

wazuh
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
anomaly-detectionanti-botcloud-security+12
17.4k10h 7m ago
wazuh/wazuhOpen-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
 dmitryflynn/netlogic
NetLogic is an advanced network analysis and cybersecurity toolkit for traffic inspection, packet analysis, and threat detection
 liam-worsley/cve-2025-32433-poc-analysis
This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 farhanashrafdev/90daysofcybersecurity
Structured 90-day cybersecurity study plan with daily tasks covering Network+, Security+, Linux, Python, traffic analysis, cloud security, and…
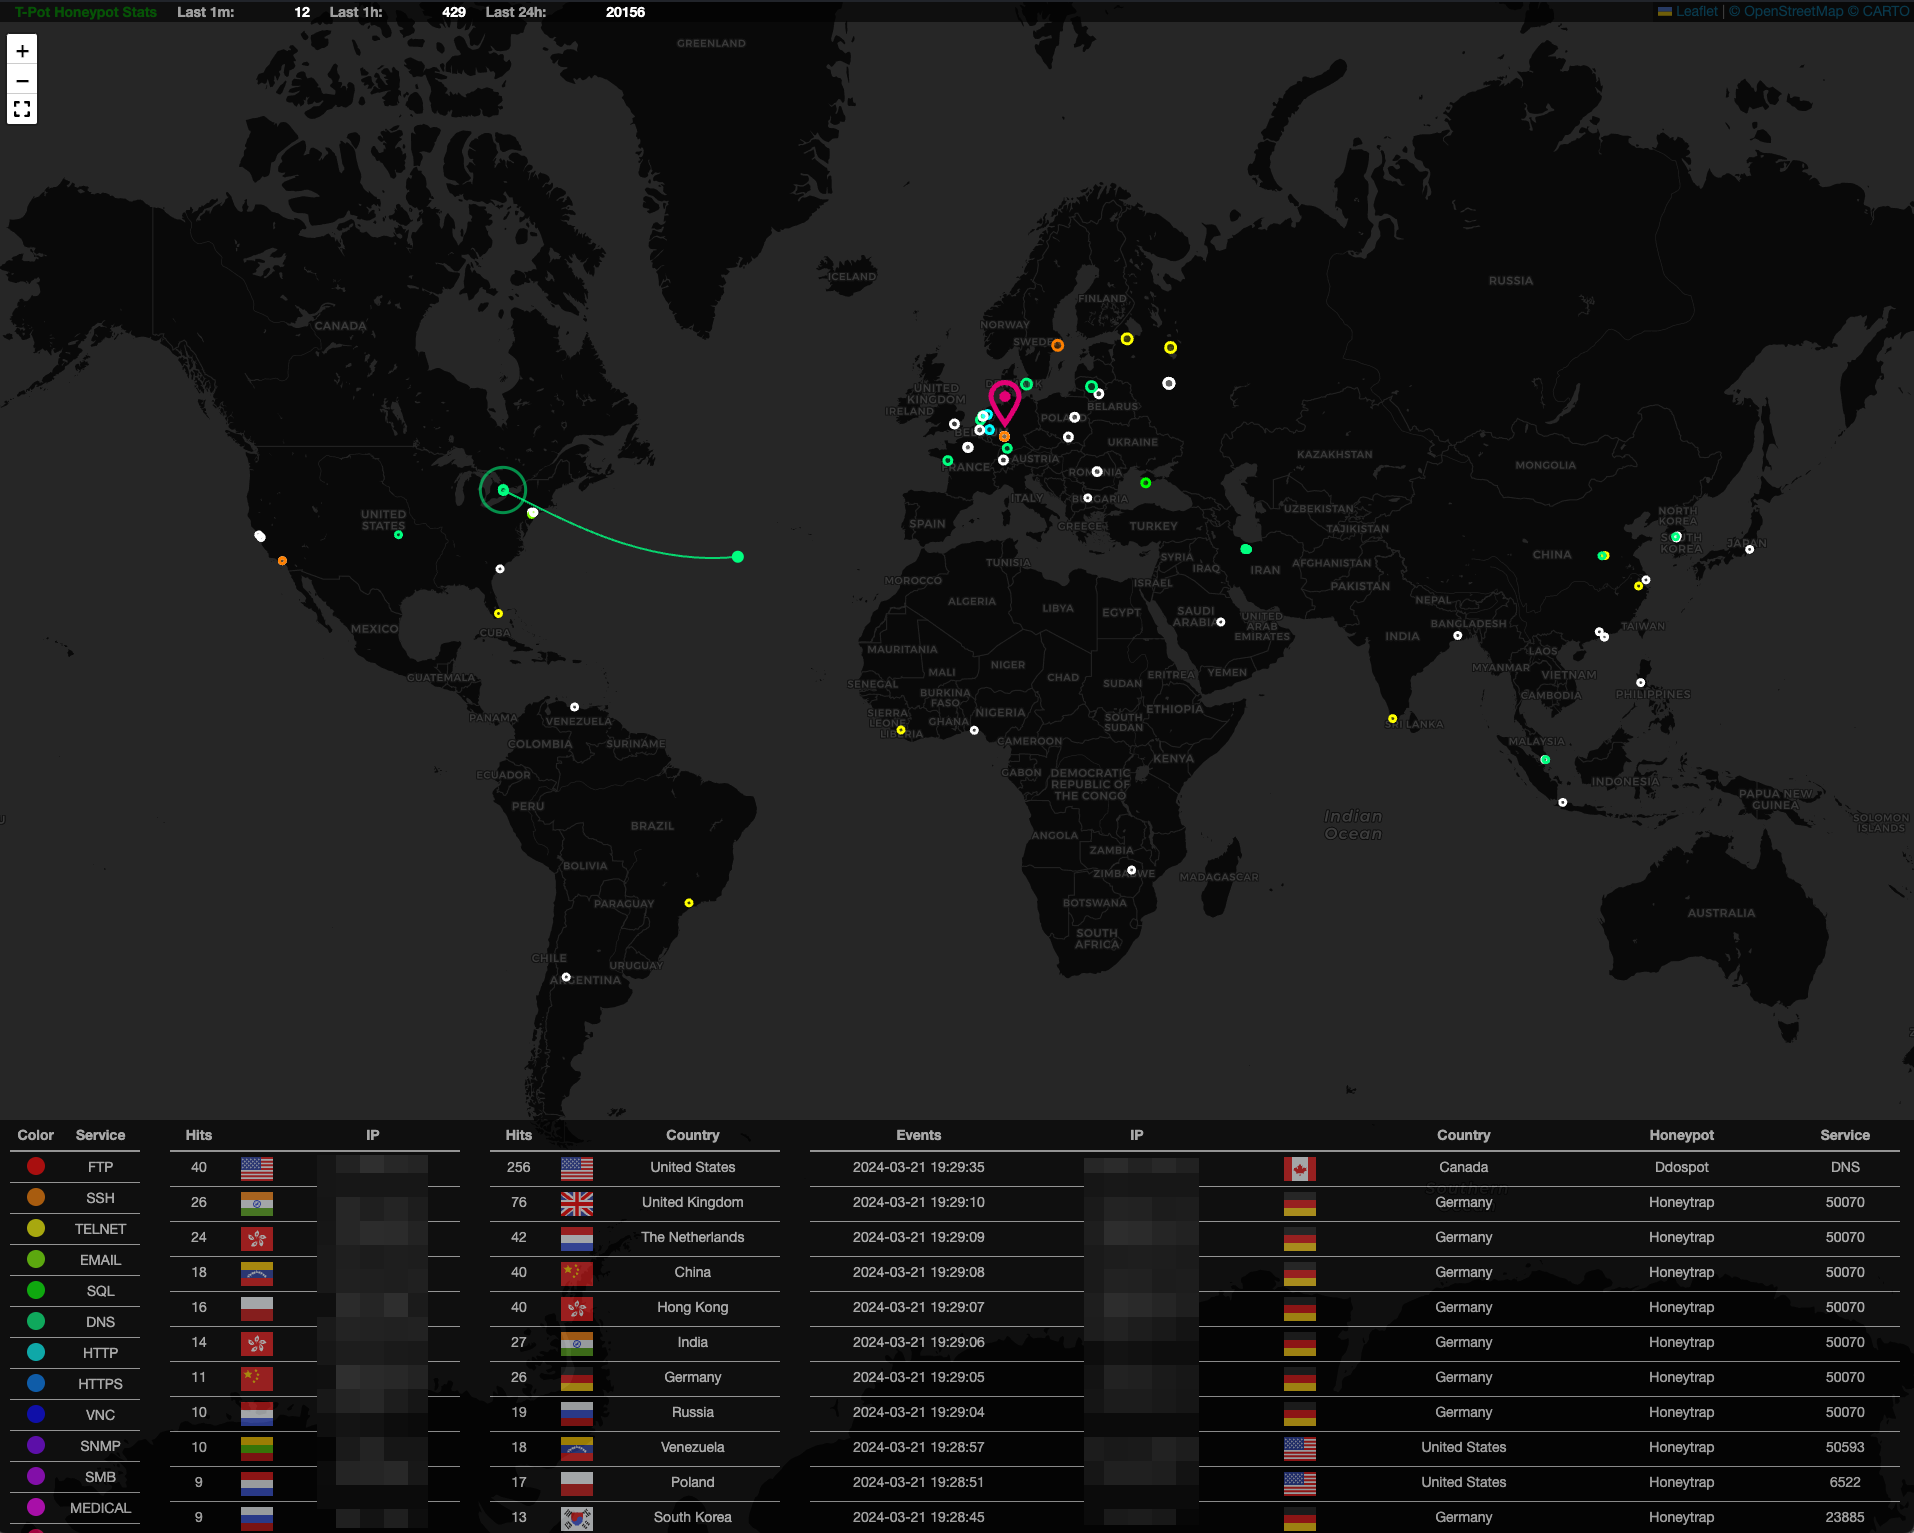 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 nfstream/nfstream
NFStream: a Flexible Network Data Analysis Framework.
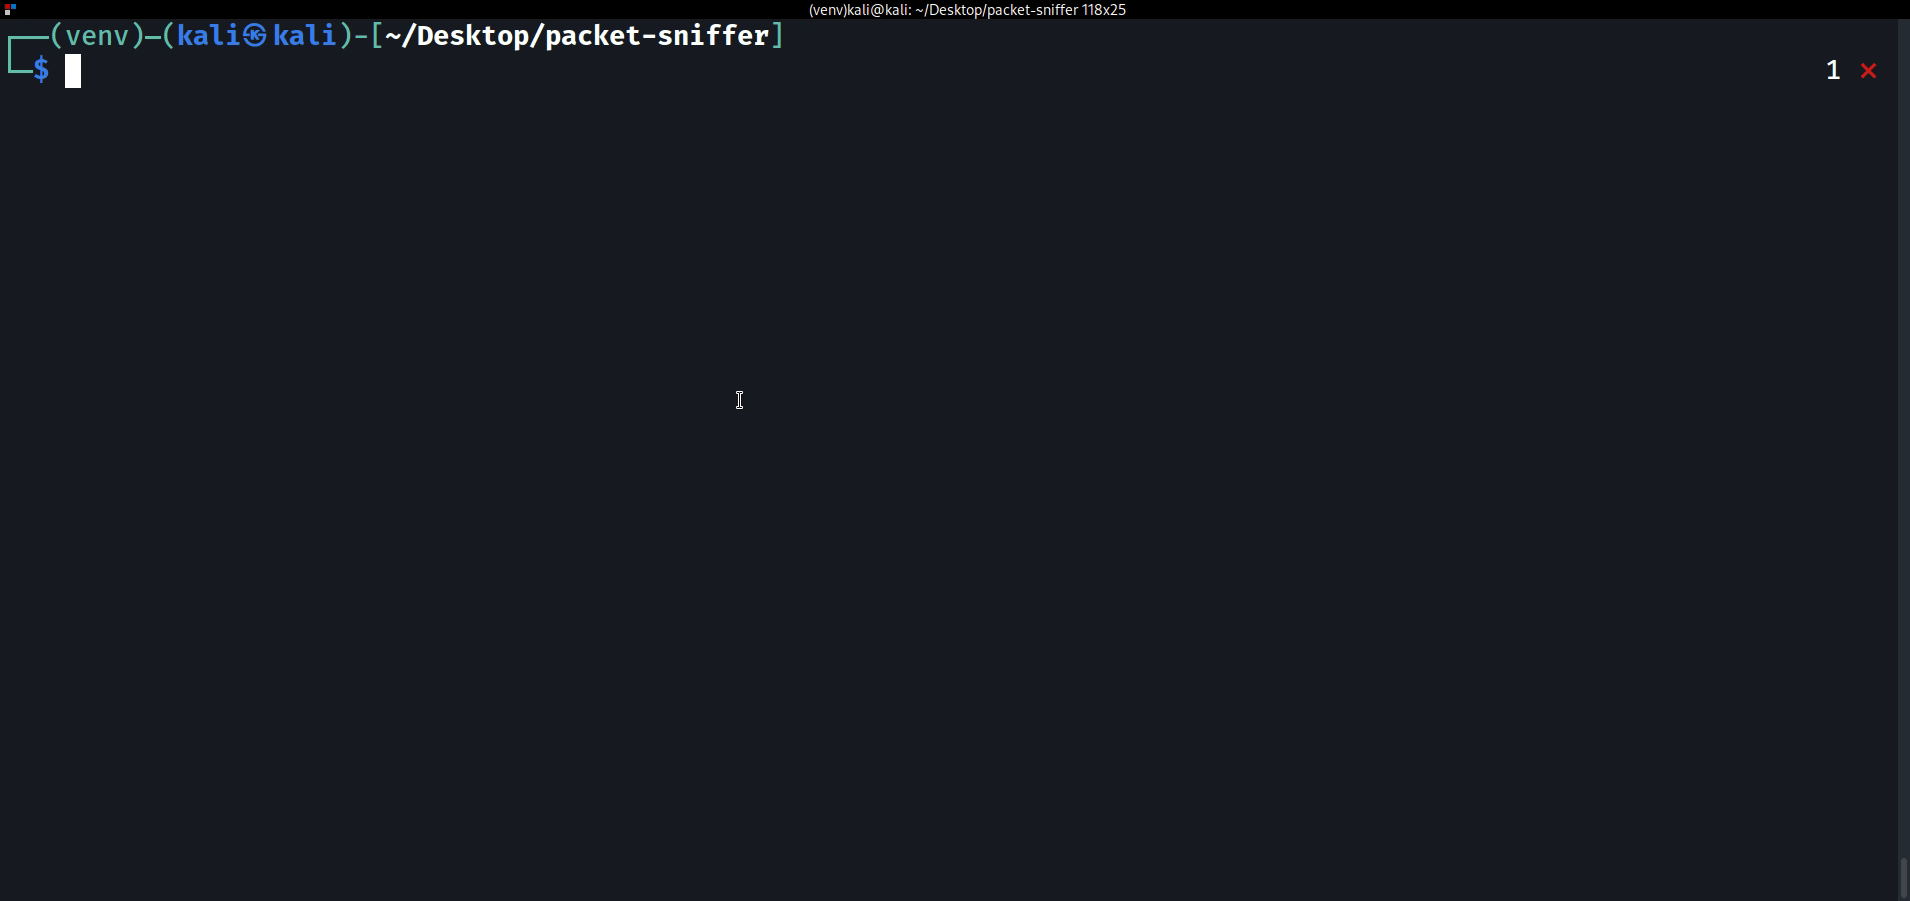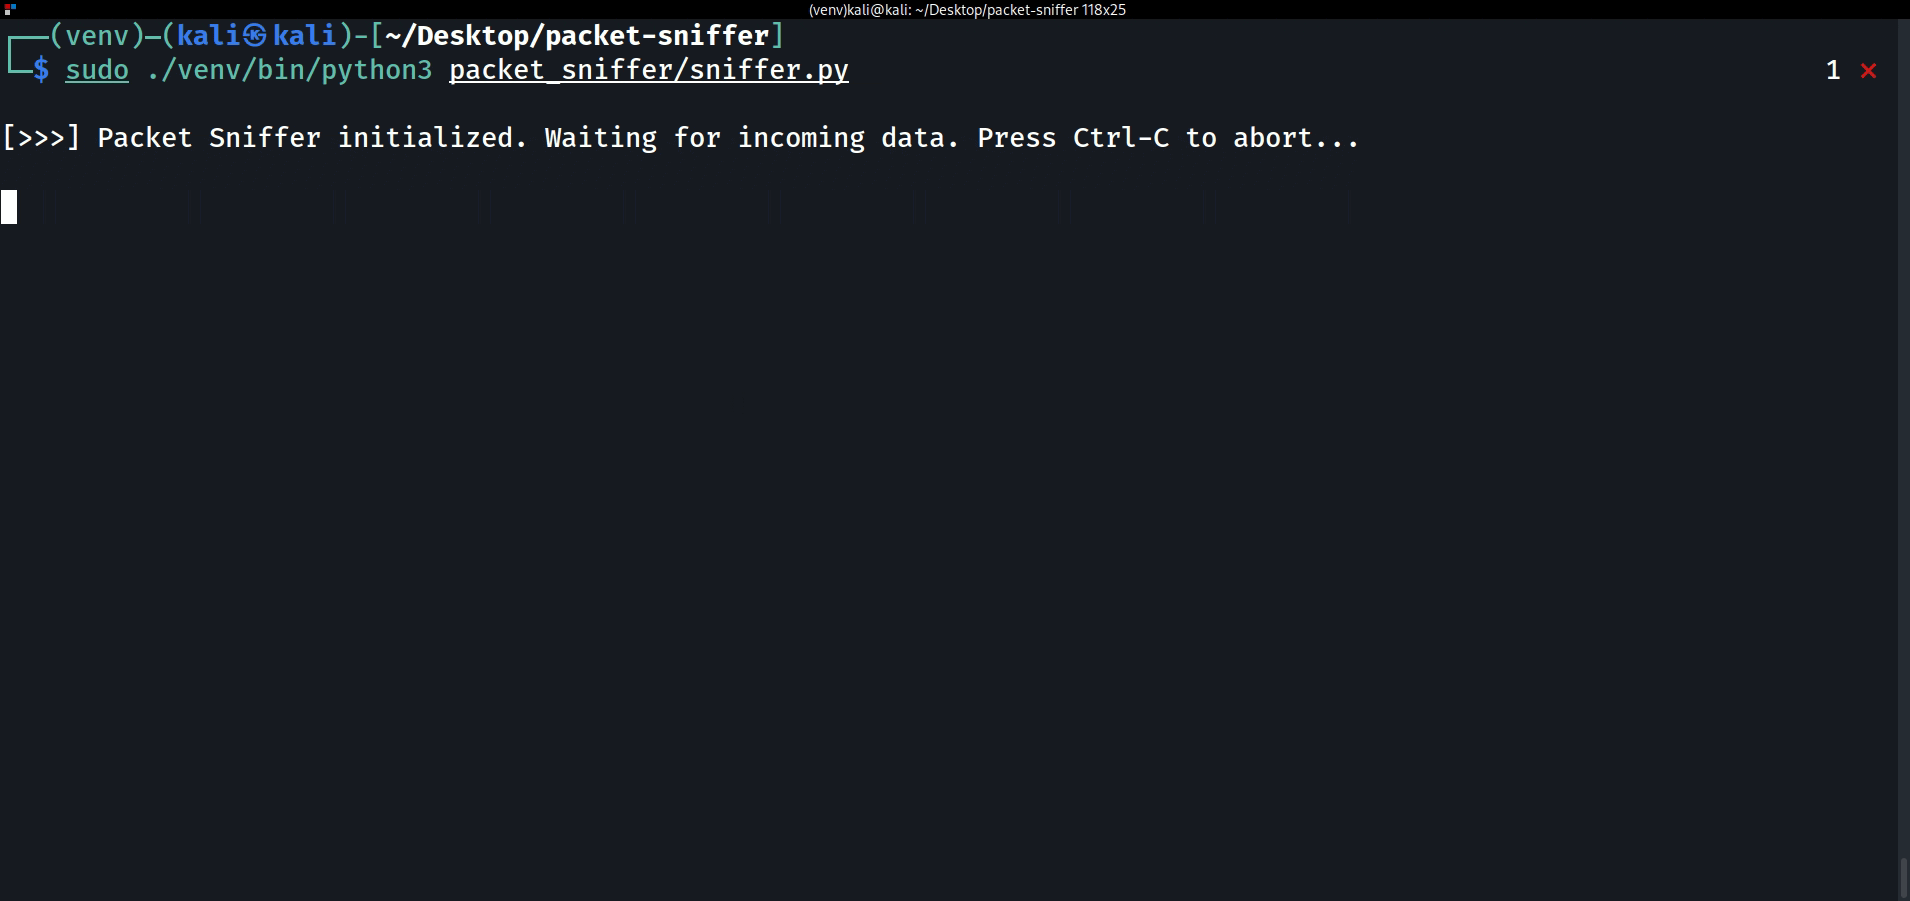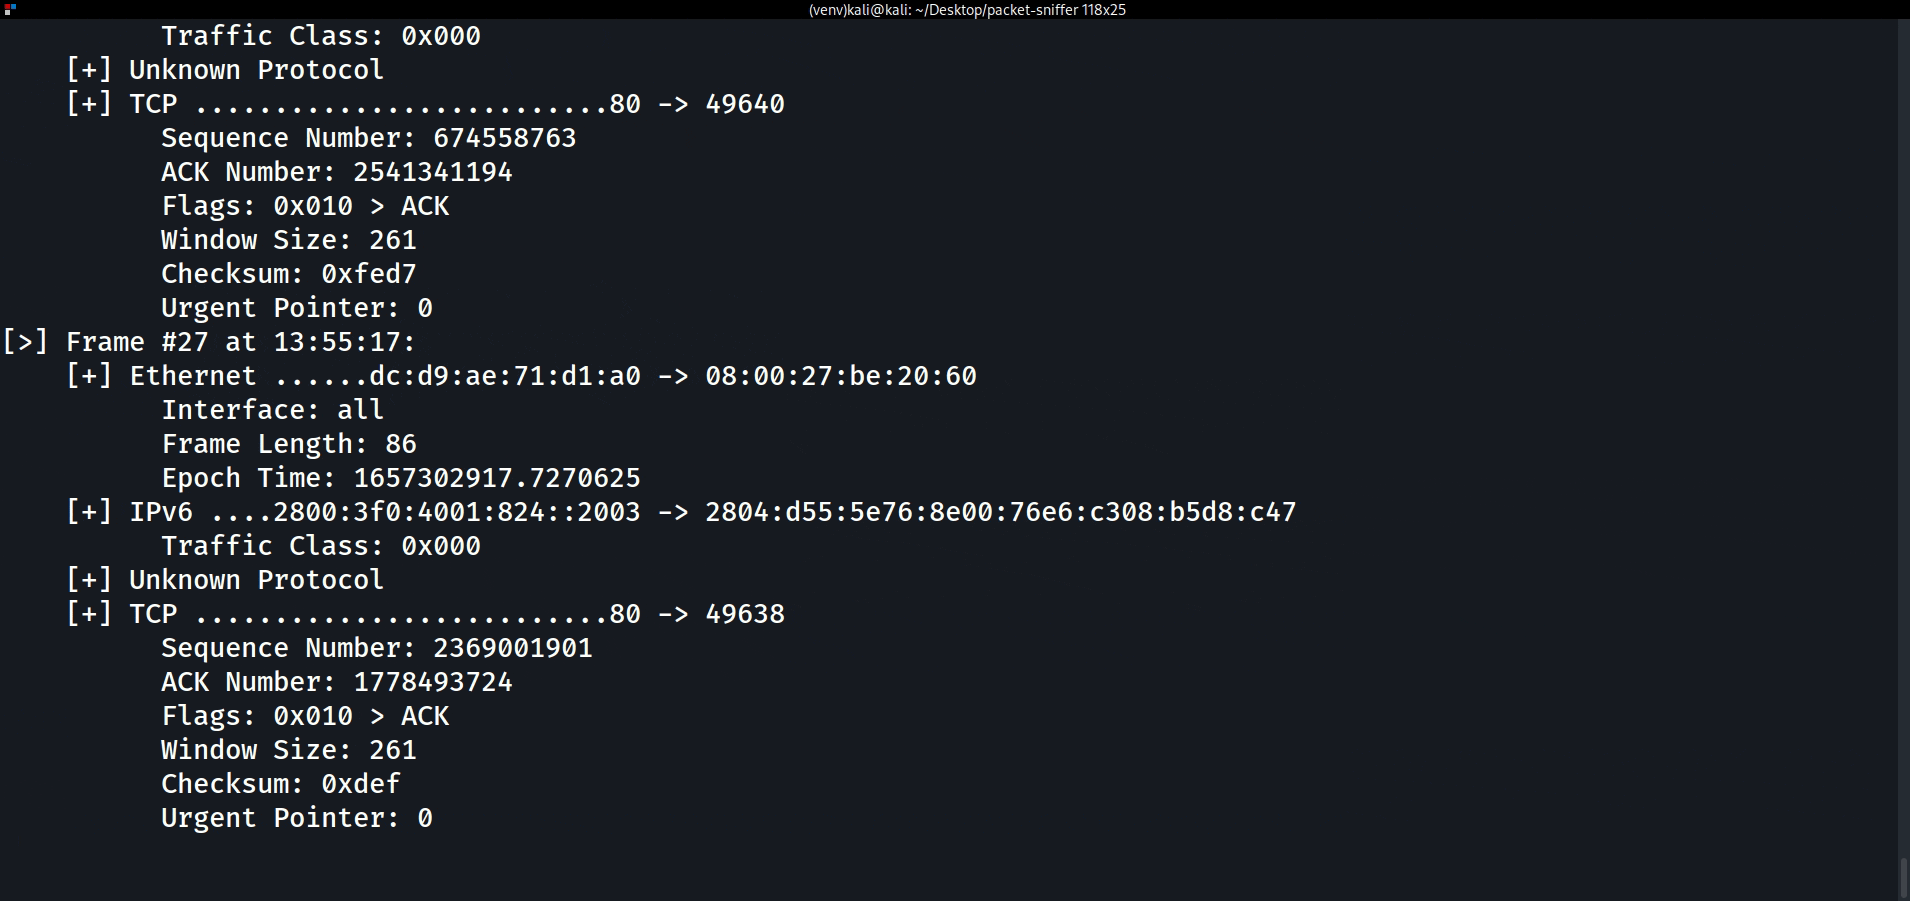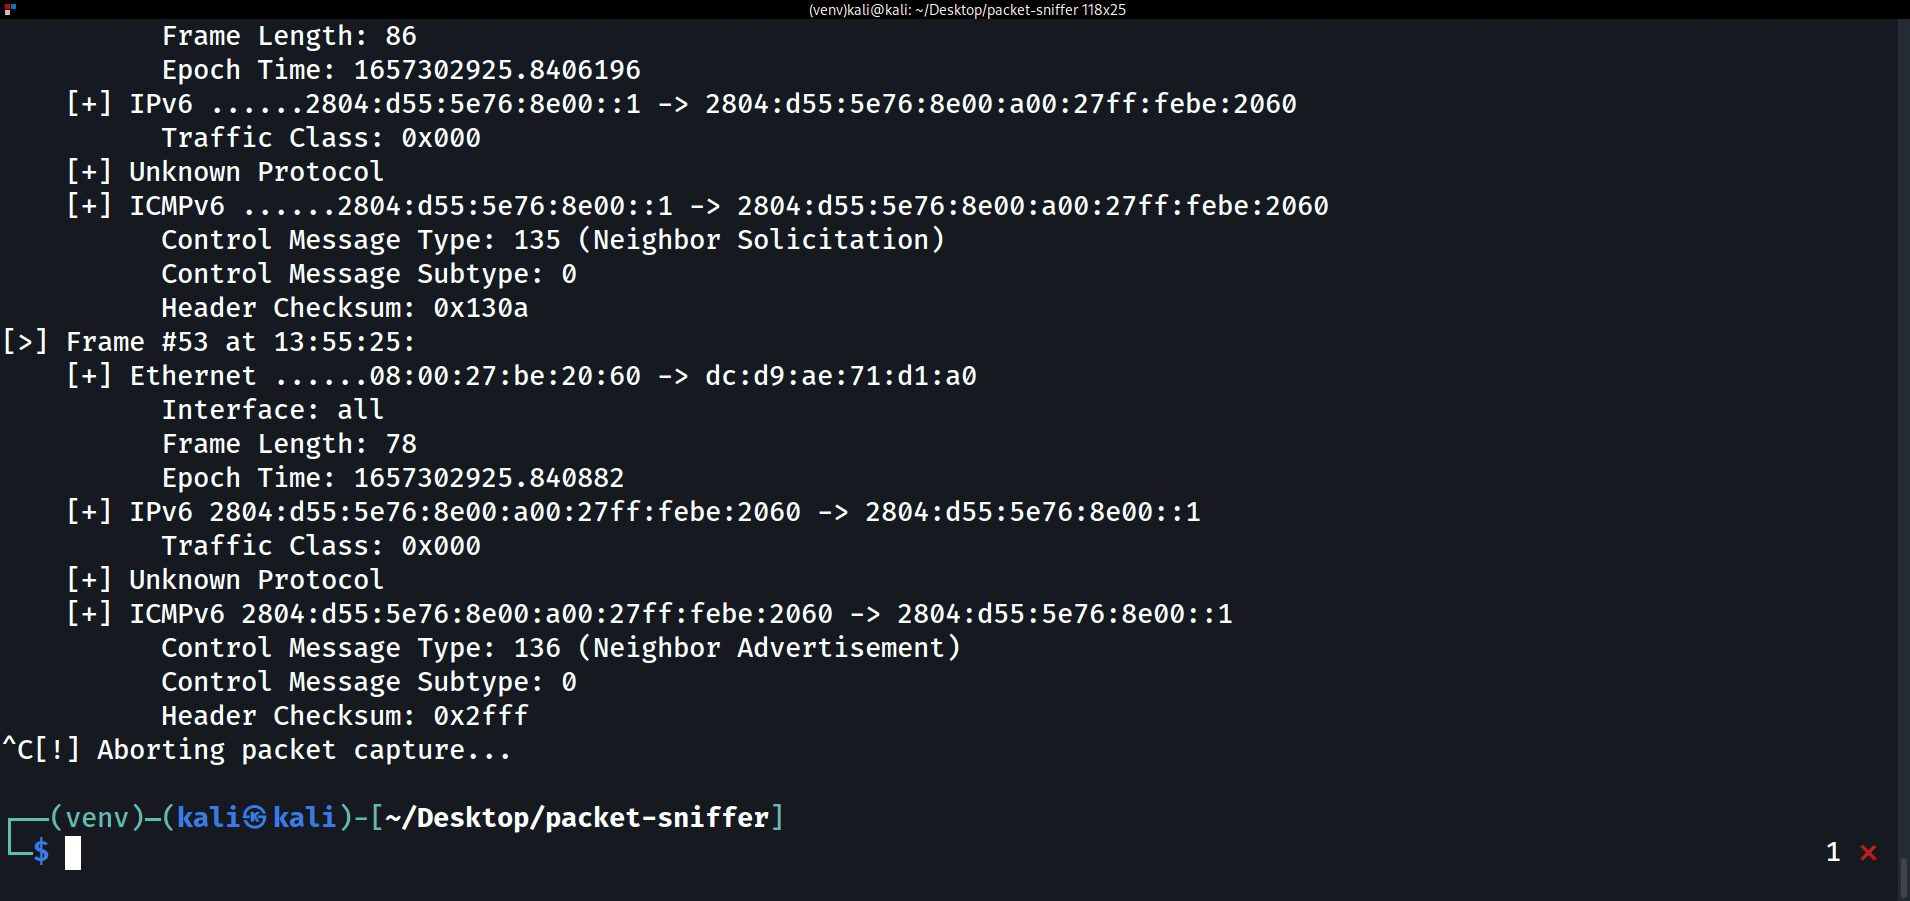 eonraider/packet-sniffer
Raw socket-based network packet sniffer that captures and disassembles TCP/IP packets from network interfaces for security analysis and educational…
 pentesteracademy/patoolkit
PA Toolkit is a collection of traffic analysis plugins focused on security
 raytheonbbn/maude-hcs
Formal modeling and analysis framework for hidden communication systems, enabling specification of covert channels, adversary models, and statistical…
 avidanmaatuk/cve-2024-38063
Educational proof-of-concept for CVE-2024-38063, a critical Windows IPv6 RCE, with technical analysis, Scapy-based crash trigger, and lab setup for…
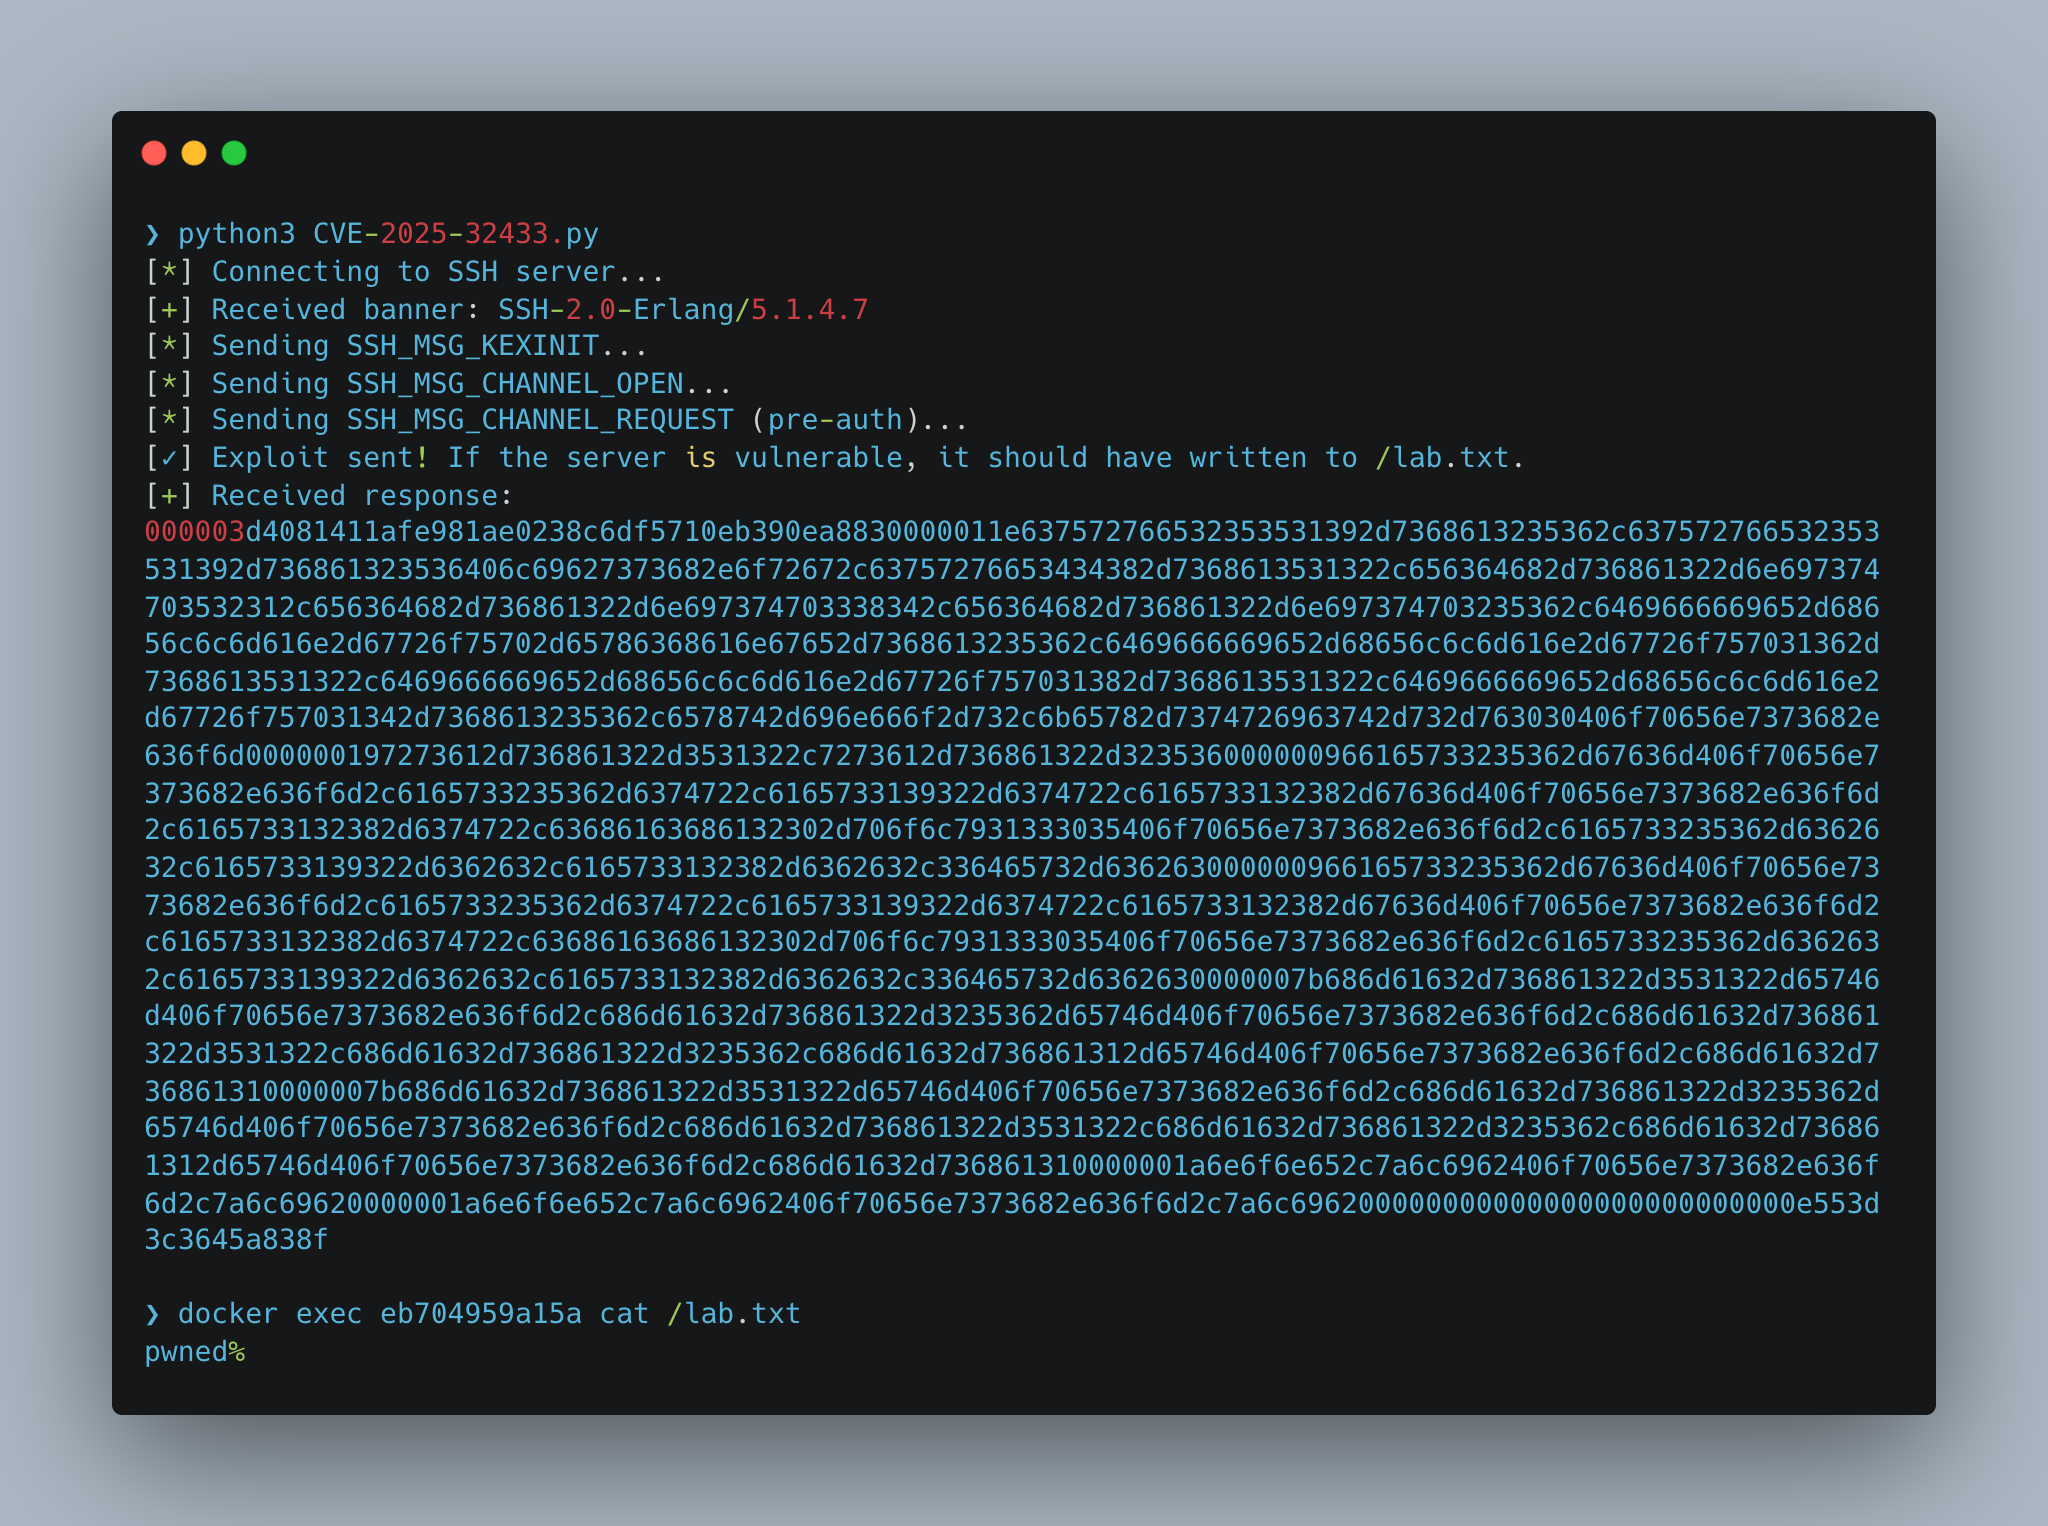 yonathanpy/cve-2025-32433.py
CVE-2025-32433 PoC – SSH Protocol Python-based PoC for controlled lab testing of SSH message handling, channel operations, and pre-auth interactions.…
 al7araziruby-jpg/cve-2024-6387-openssh-analysis
Security analysis and report of CVE-2024-6387 OpenSSH vulnerability, including vulnerability details, CVSS evaluation, and mitigation recommendations.
 kaleth4/cve-2026-33827
Technical analysis of CVE-2026-33827, a critical Windows TCP/IP RCE via race condition in IPv6/IPSec, including exploitation techniques, mitigation…
 minc-nice-100/http2-bomb-analysis-paper
HTTP/2 Bomb: HPACK indexed-reference amplification + flow-control stall. A high school student's full protocol analysis (LaTeX). CVE-2026-49975,…
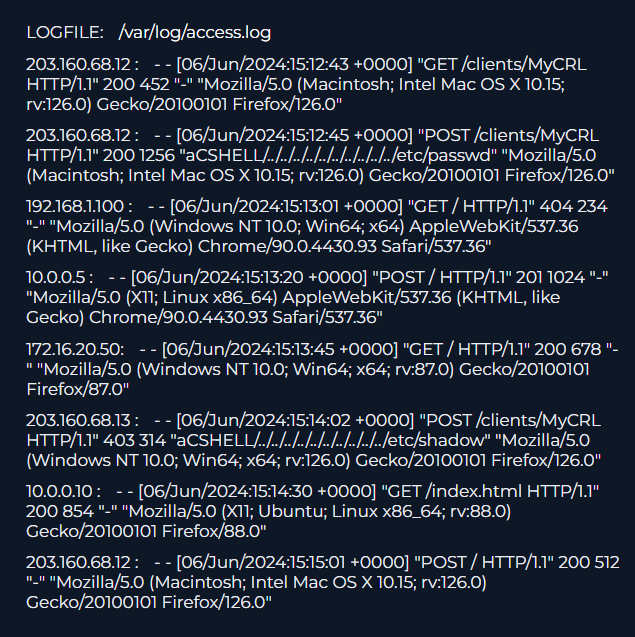 zedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…