
windows_tcpip_fuzz
 personnumber3377/windows_tcpip_fuzz
This is my attempt at fuzzing the tcpip.sys driver in windows via using scapy. This is inspired by this vulnerability here:…
binary-analysisexploitationfuzzing+2
personnumber3377/windows_tcpip_fuzzThis is my attempt at fuzzing the tcpip.sys driver in windows via using scapy. This is inspired by this vulnerability here:…
 gojue/ecapture
Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
 malwaremorghulis/sunburst
Detection for SUNBURST C2 Stage-1 using Shannon Entropy
 loosehose/silentbutdeadly
SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
 seclabresearchbv/cve-2022-34718-poc
Python-based proof-of-concept exploit for CVE-2022-34718, a remote code execution vulnerability in IPv6 on Windows, using Scapy to craft and send…
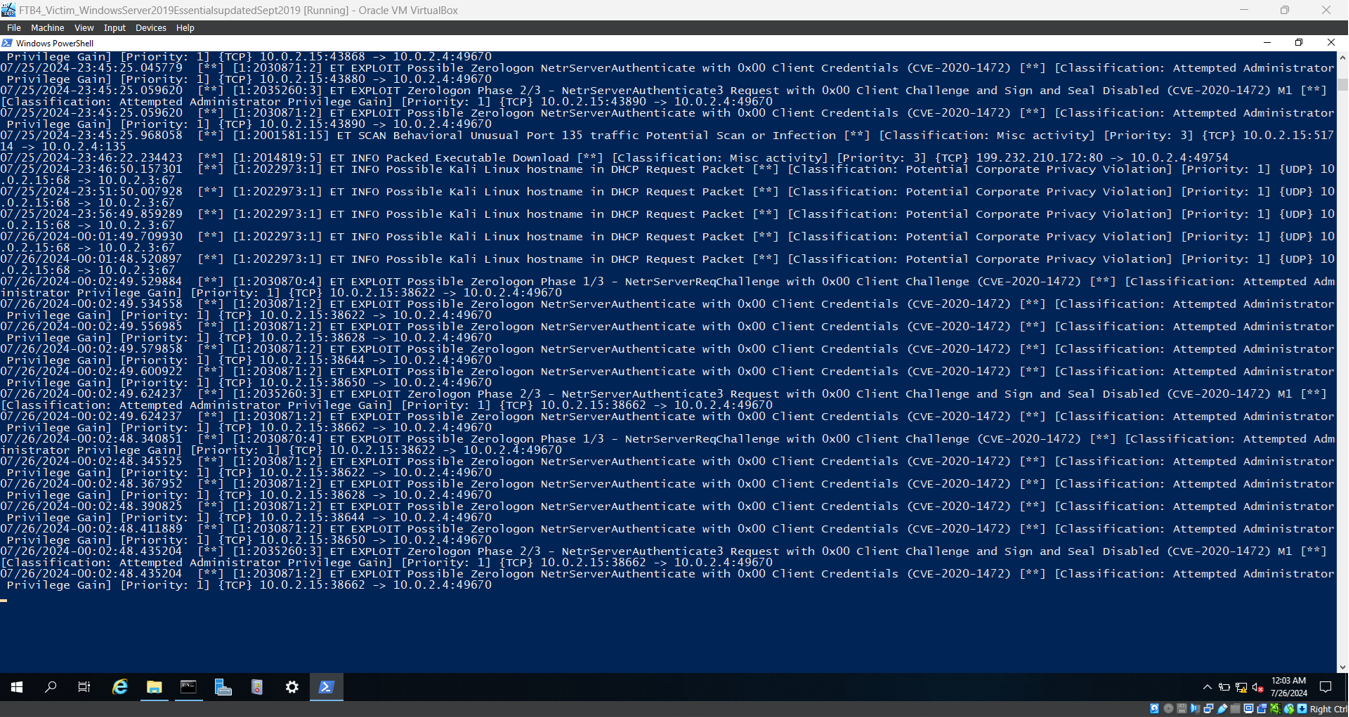 tdevworks/cve-2020-1472-zerologon-demo-detection-mitigation
Educational demo of CVE-2020-1472 (ZeroLogon) detection using Windows Event Logs and Suricata IDS, plus mitigation via Windows Updates. Includes…
 darkoperator/posh-ssh
PowerShell Module for automating tasks on remote systems using SSH
 hotcakex/harden-windows-security
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
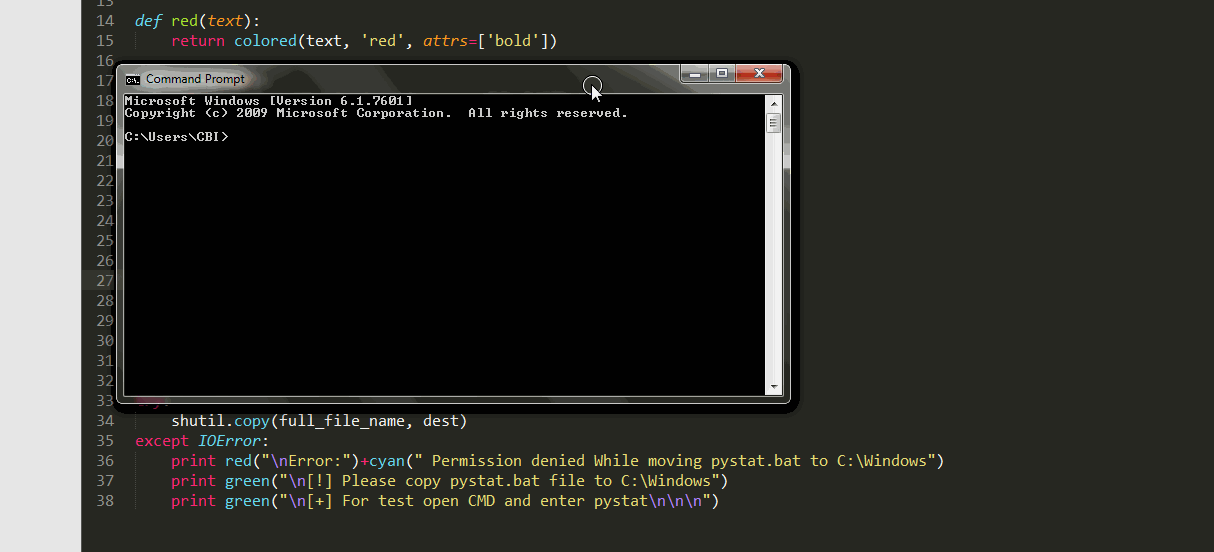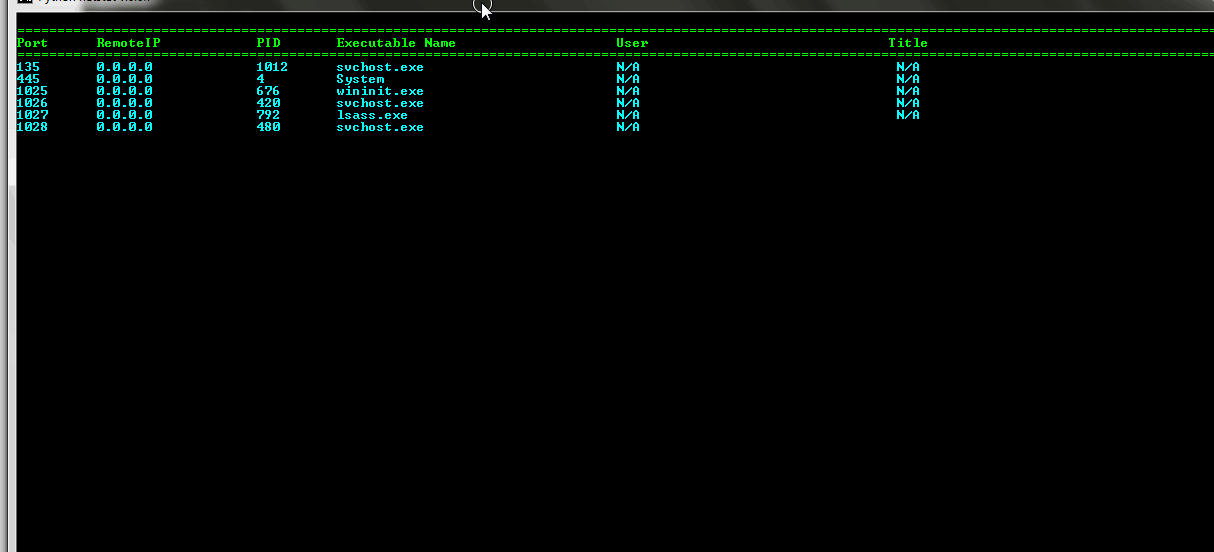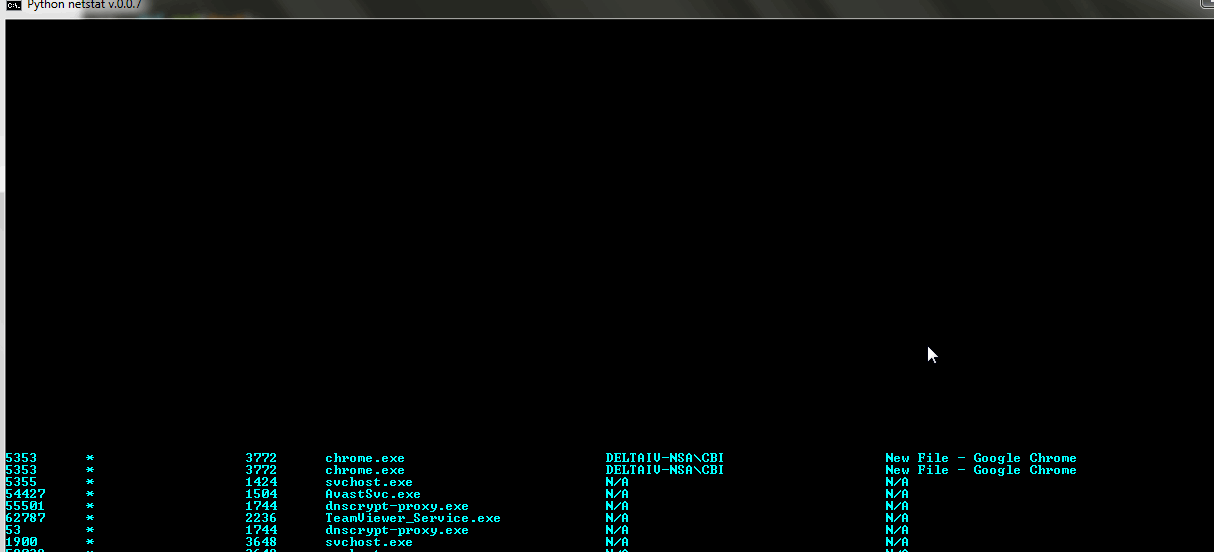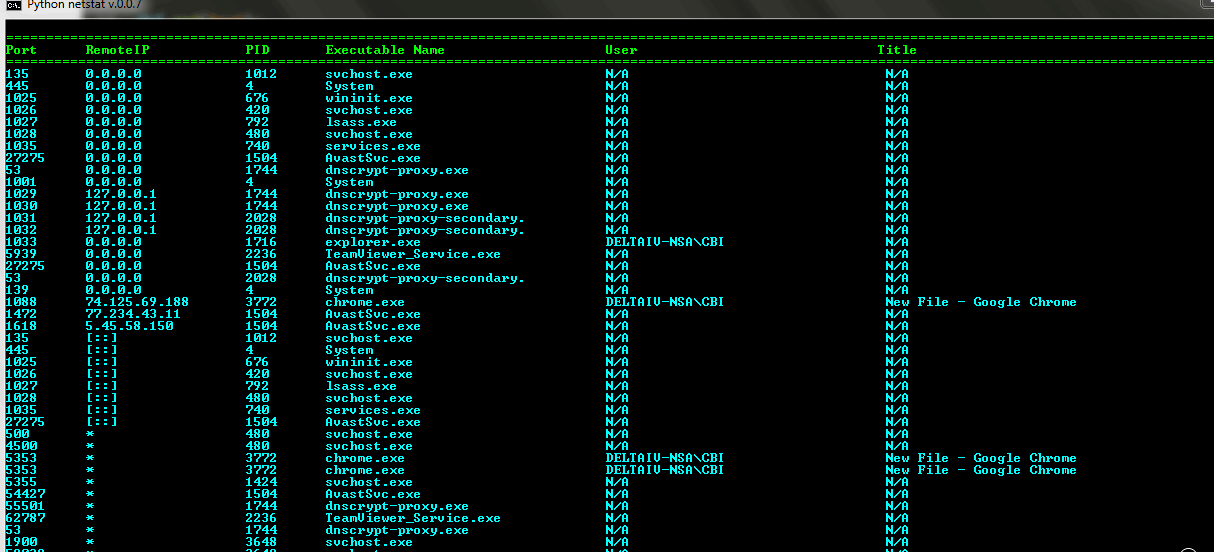 roothaxor/pystat
Advanced Netstat Using Python For Windows
 deepzec/win-portfwd
Powershell script to setup windows port forwarding using native netsh client
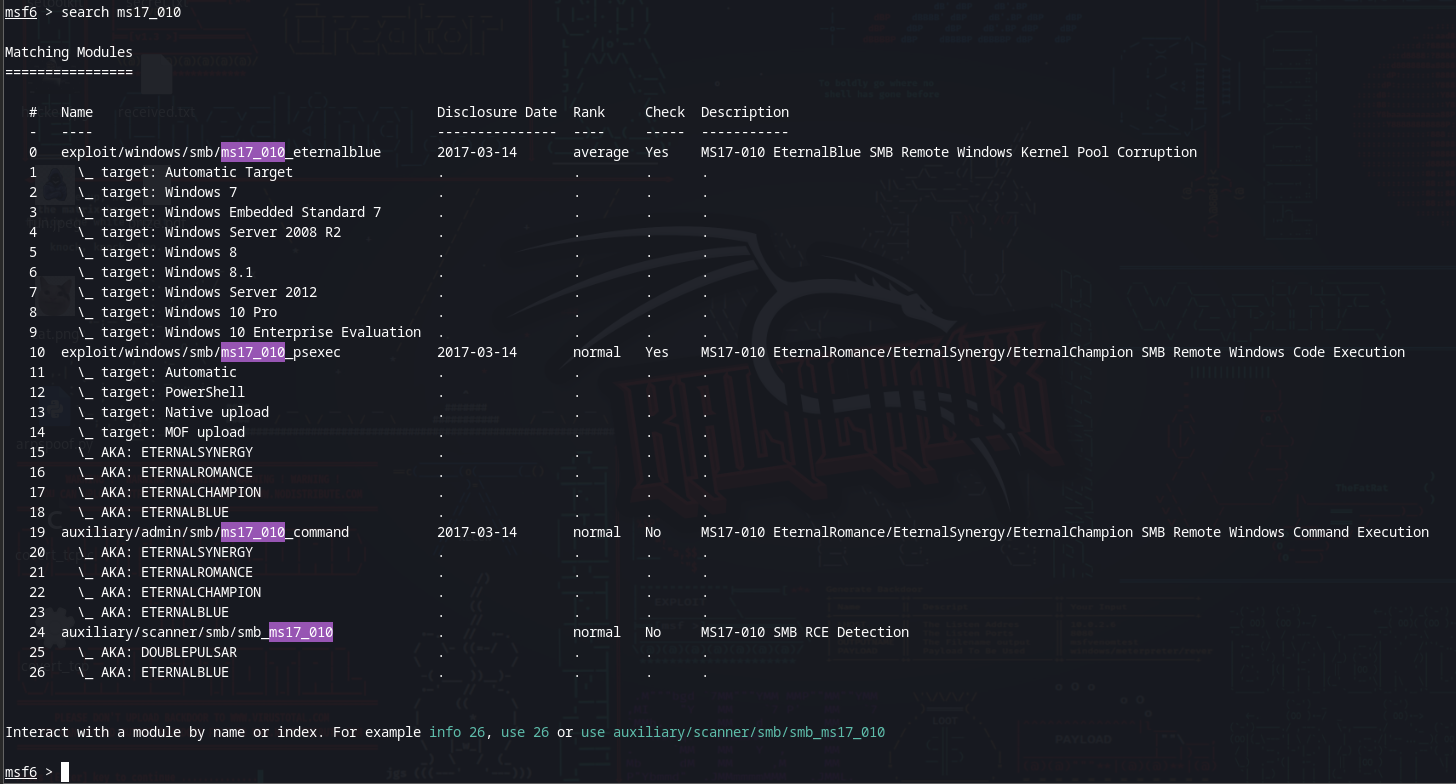 luckyman2907/smb-protocol-vulnerability_cve-2017-0144
Step-by-step lab guide demonstrating the EternalBlue exploit (CVE-2017-0144) against Windows 7 SMB protocol using Metasploit, including setup,…
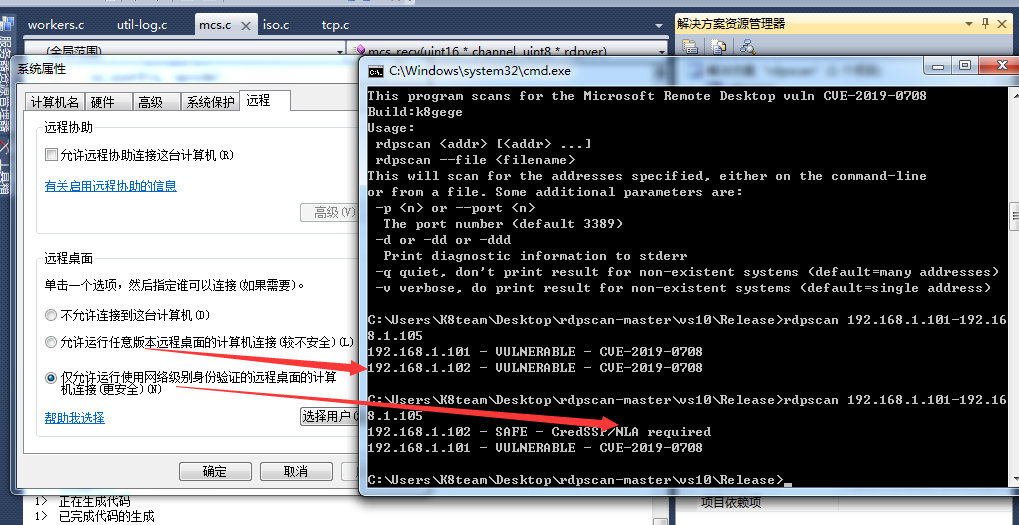 lisinan988/cve-2019-0708-scan
Batch scanner for CVE-2019-0708 (BlueKeep) RDP vulnerability with Windows and Linux support, using rdpscan and custom Cscan for mass IP range…
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.
 seguridadentrerios/cve-2026-33829
Automated Bash script to passively audit Windows assets for CVE-2026-33829 search: protocol handler vulnerability using tcpdump and SMB connection…
 dweger-scripts/cve-2024-38063-remediation
PowerShell audit script to detect missing patches for CVE-2024-38063, an IPv6 vulnerability in Windows systems, enabling rapid remediation…
 valarauco/wannafind
Simple script using nmap to detect CVE-2017-0143 MS17-010 in your network
 simeononsecurity/cve-2020-1350-fix
A registry-based workaround can be used to help protect an affected Windows server, and it can be implemented without requiring an administrator to…
 shardianlabs/ephemeralnet
A secure, decentralized P2P ephemeral network in C++. Features a custom DHT, encrypted transport, and autonomous NAT traversal using high-performance…