
 thinkst/canarytokens
Canarytokens helps track activity and actions on your network
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
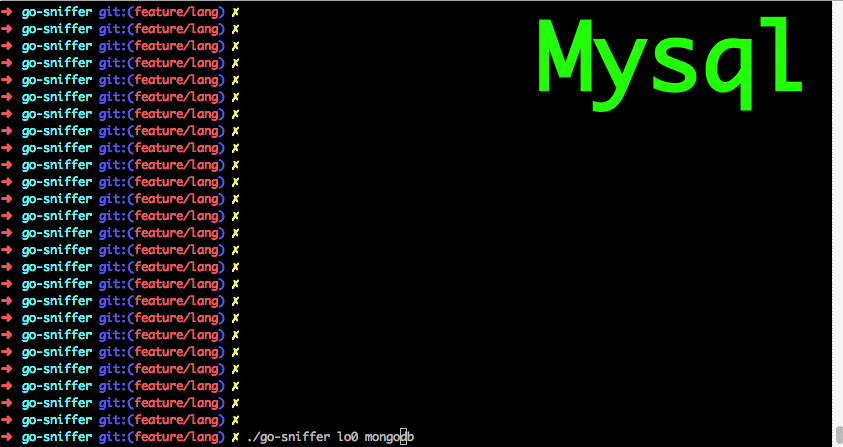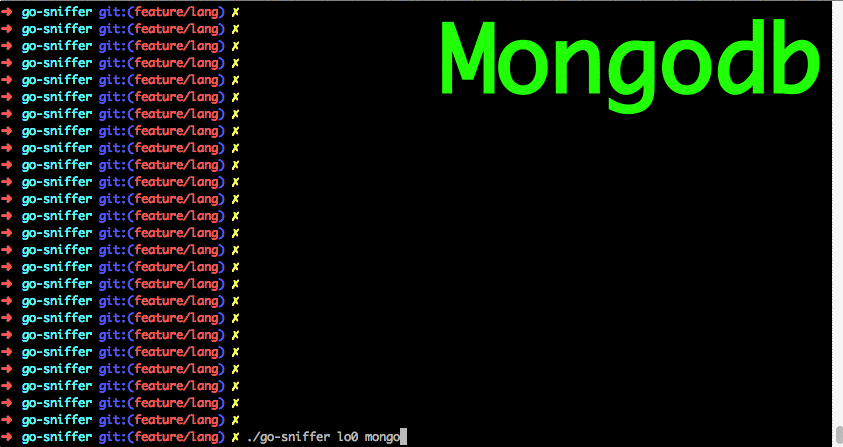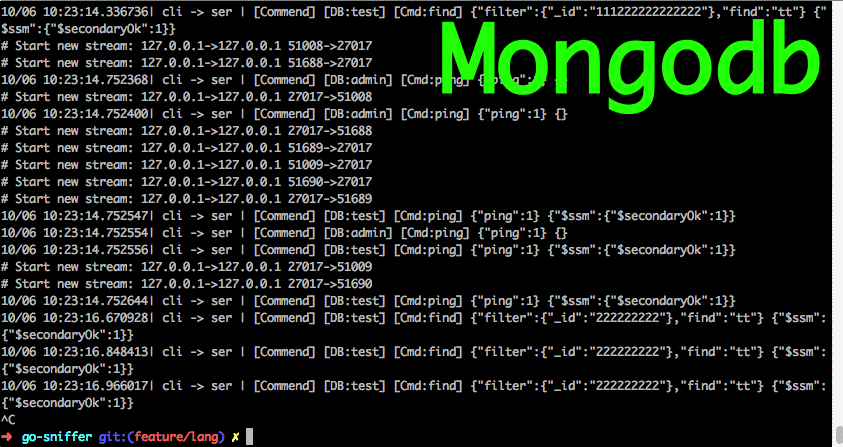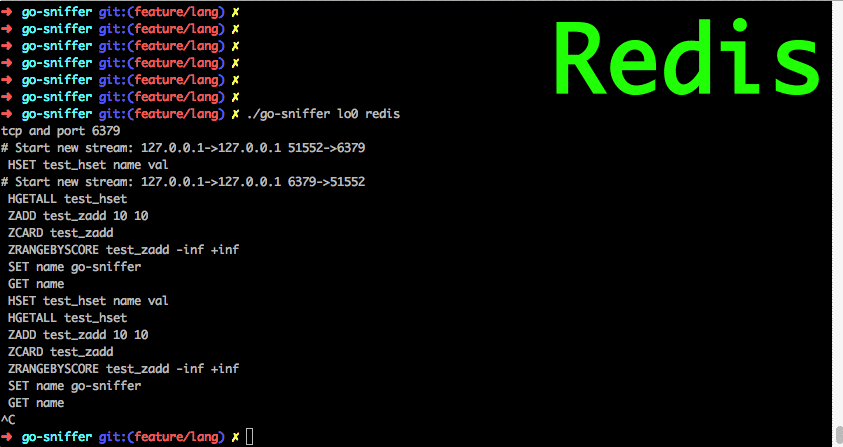 40t/go-sniffer
🔎Sniffing and parsing mysql,redis,http,mongodb etc protocol. 抓包截取项目中的数据库请求并解析成相应的语句。
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 alphasoc/flightsim
A utility to safely generate malicious network traffic patterns and evaluate controls.
 snorby/snorby
Ruby On Rails Application For Network Security Monitoring
 seccubus/seccubus
Easy automated vulnerability scanning, reporting and analysis
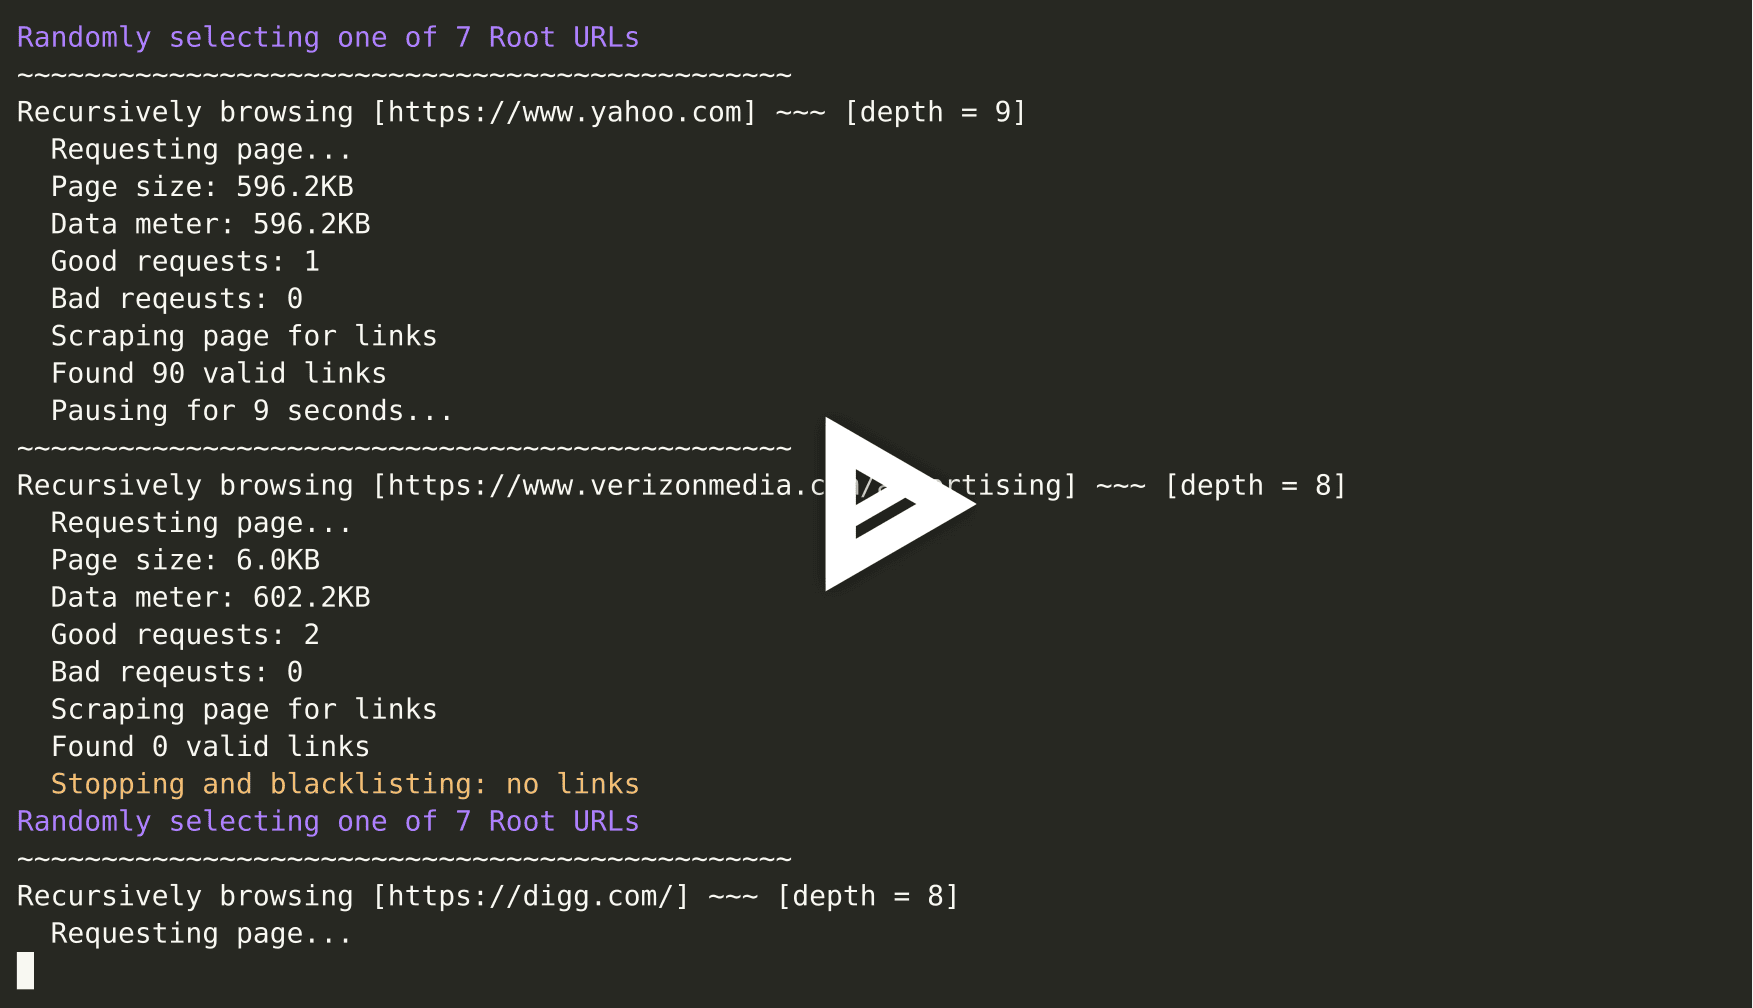 reconinfosec/web-traffic-generator
A quick and dirty HTTP/S "organic" traffic generator.
 pfq/pfq
Functional Network Framework for Multi-Core Architectures
 ugzv/ublockdnsclient
Cross-platform system DNS client for uBlockDNS with device wide ad and tracker blocking and real time filter updates.
 cyberark/ketshash
A little tool for detecting suspicious privileged NTLM connections, in particular Pass-The-Hash attack, based on event viewer logs.
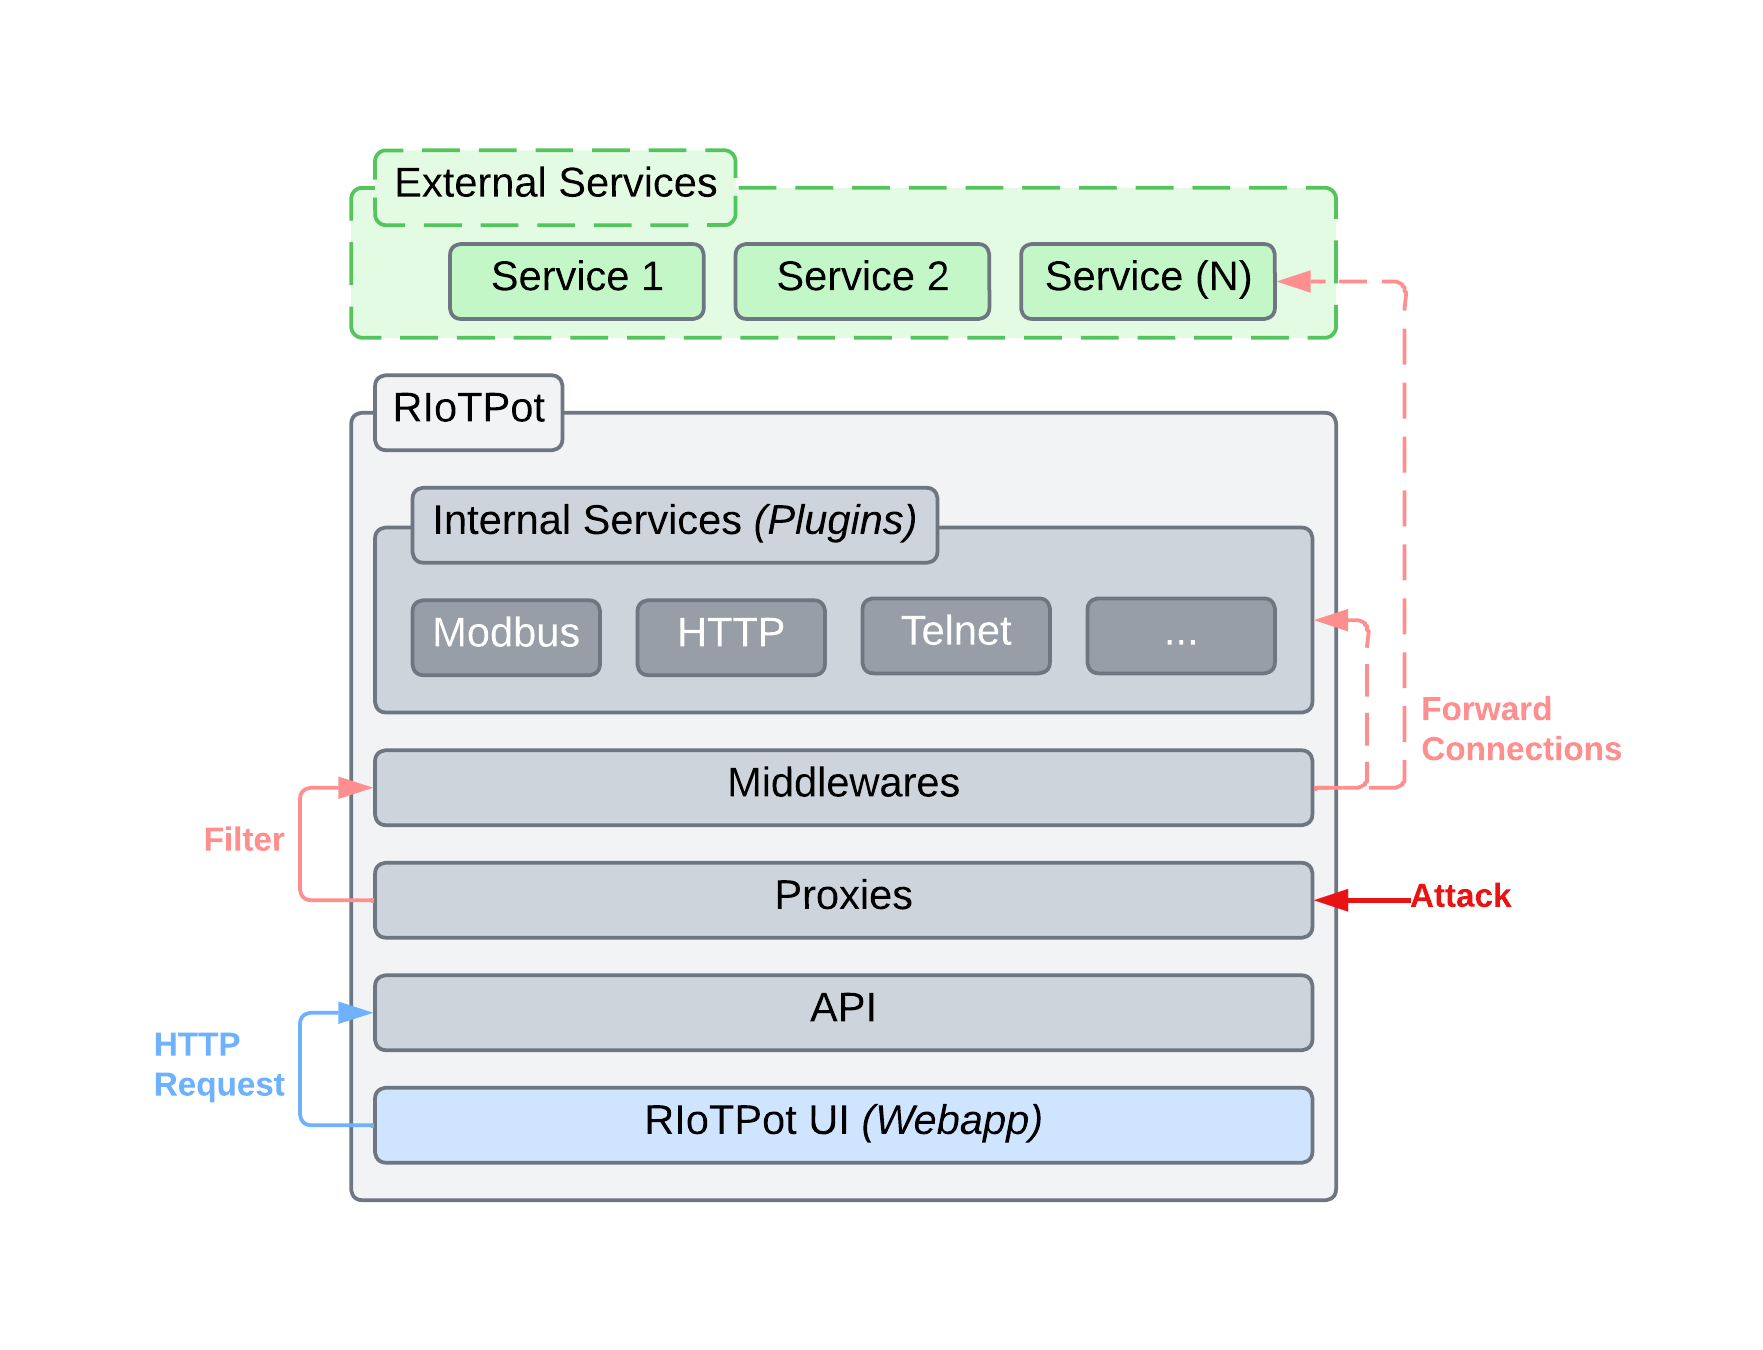 aau-network-security/riotpot
IoT and Operational Technology Honeypot
 crypt0p3g/adnullenum
One-pass anonymous Active Directory enumeration over SAMR and LSARPC — null session, no credentials, with structured reusable output.
 cbuijs/sdproxy
DNS Proxy that is simple and fast with not so simple features. Focused on routed DNS forwarding, filtering and parental control.
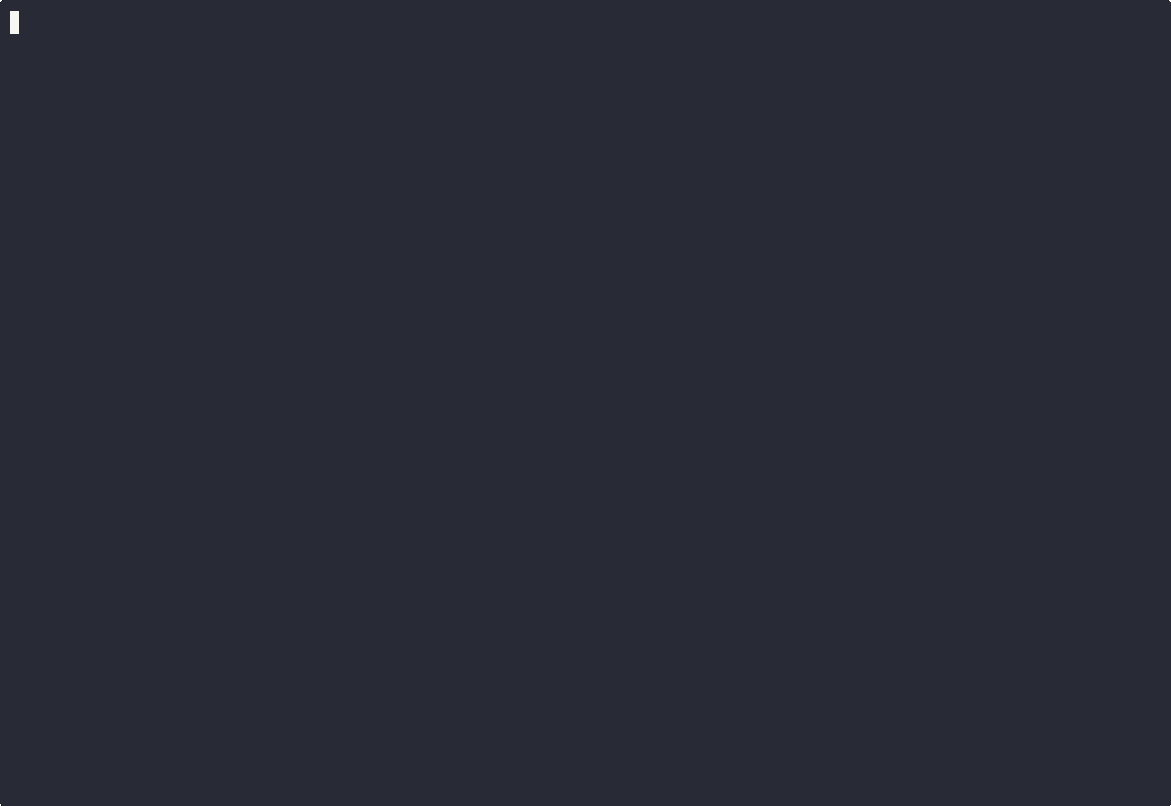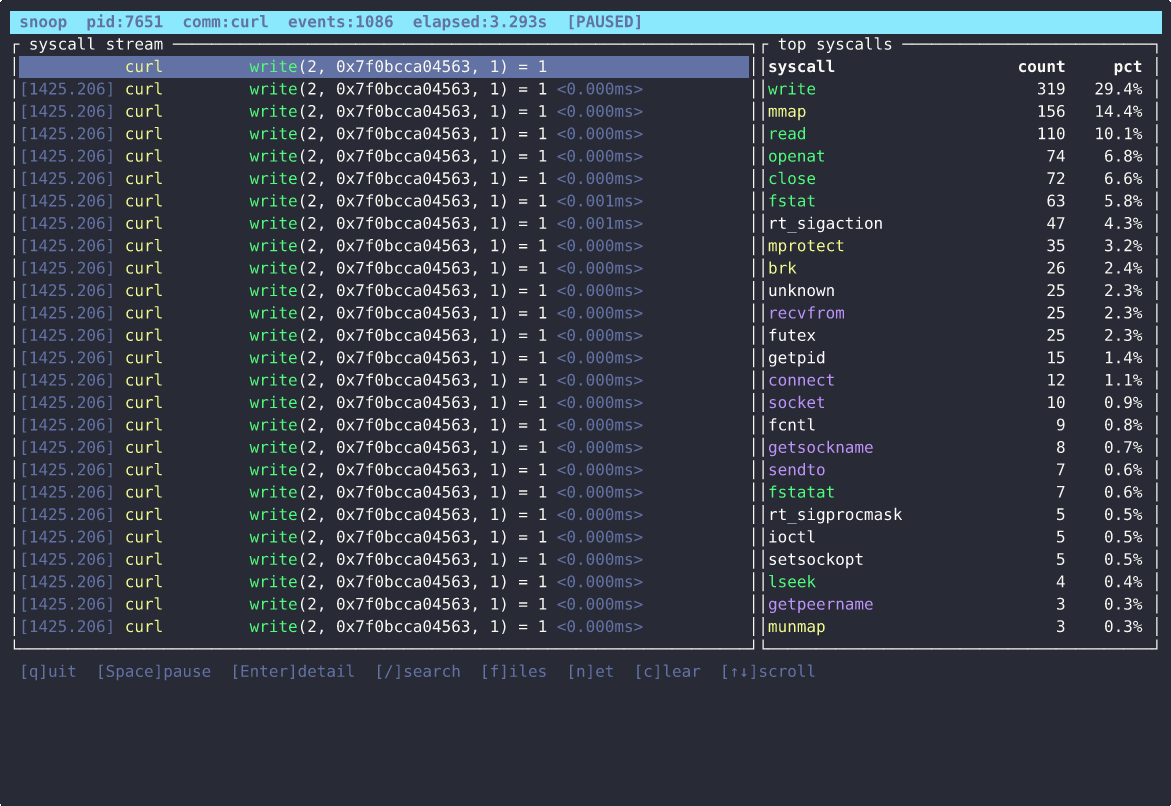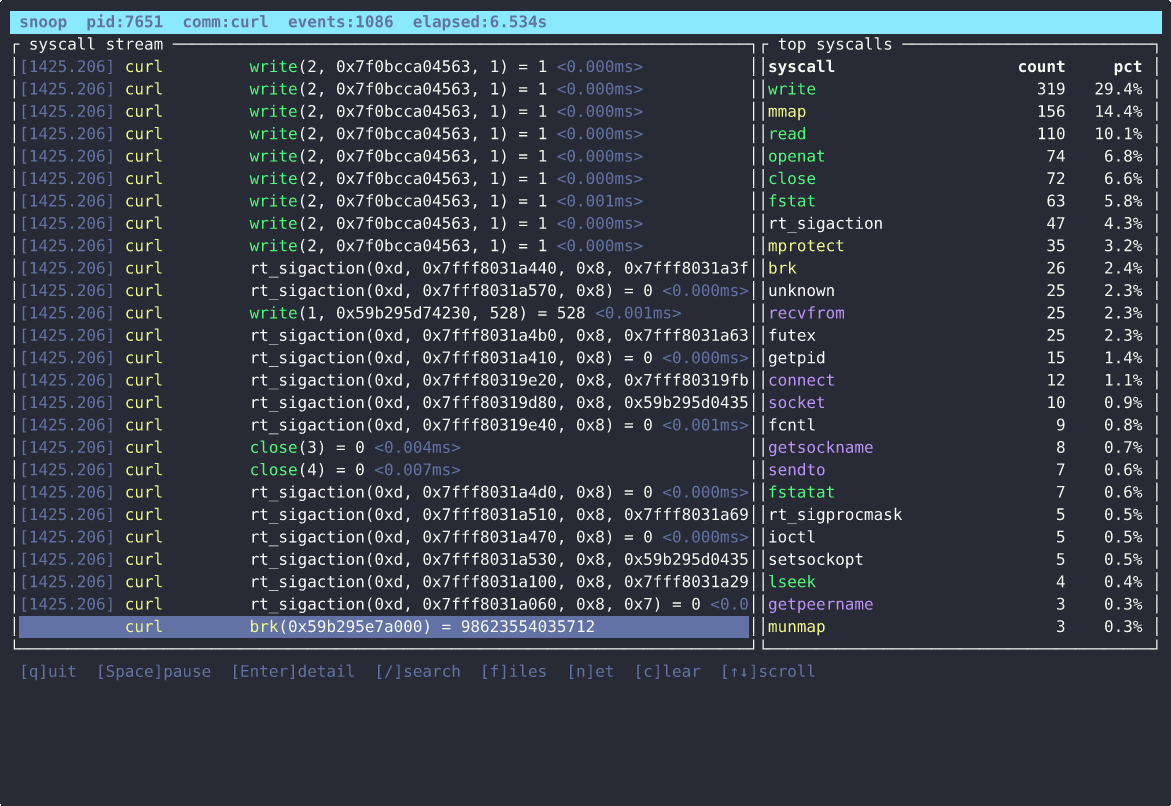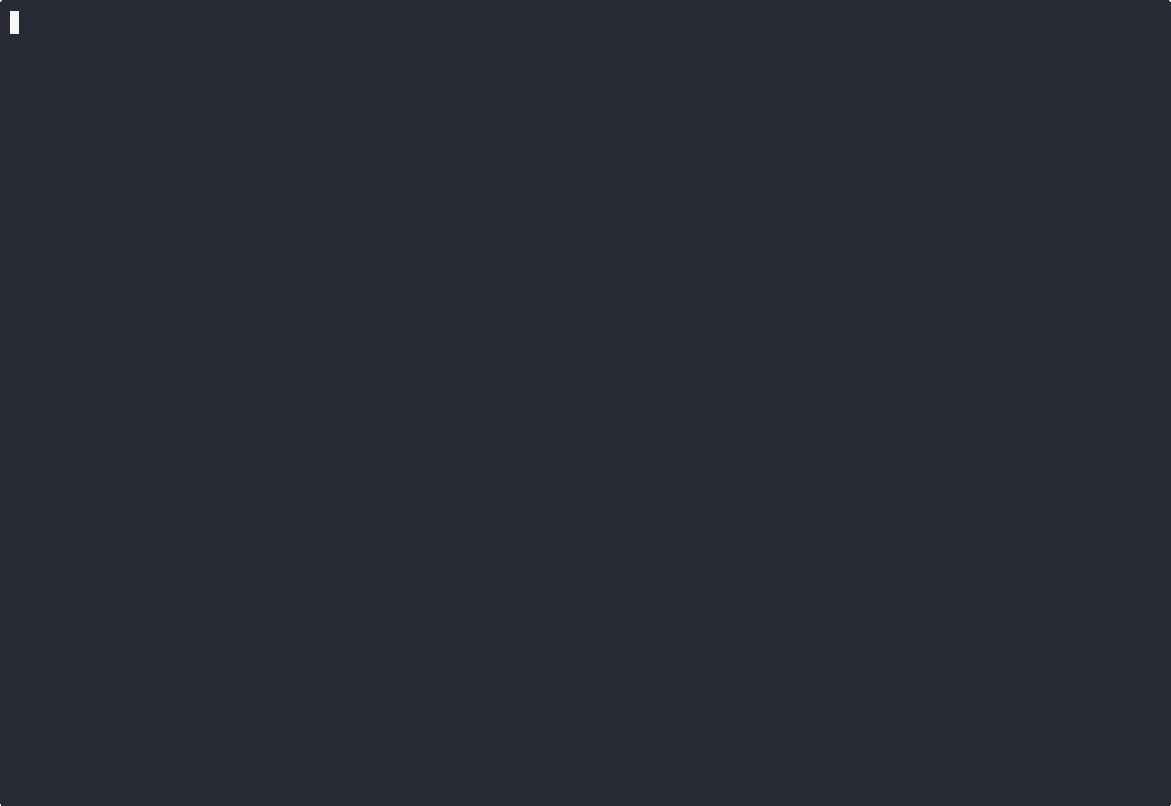 pandaadir05/snoop
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
 mister-iks/pcybox-attackgraph
Open source browser lab to build a simulated infrastructure, watch an attack move through it, and check whether your defense works.
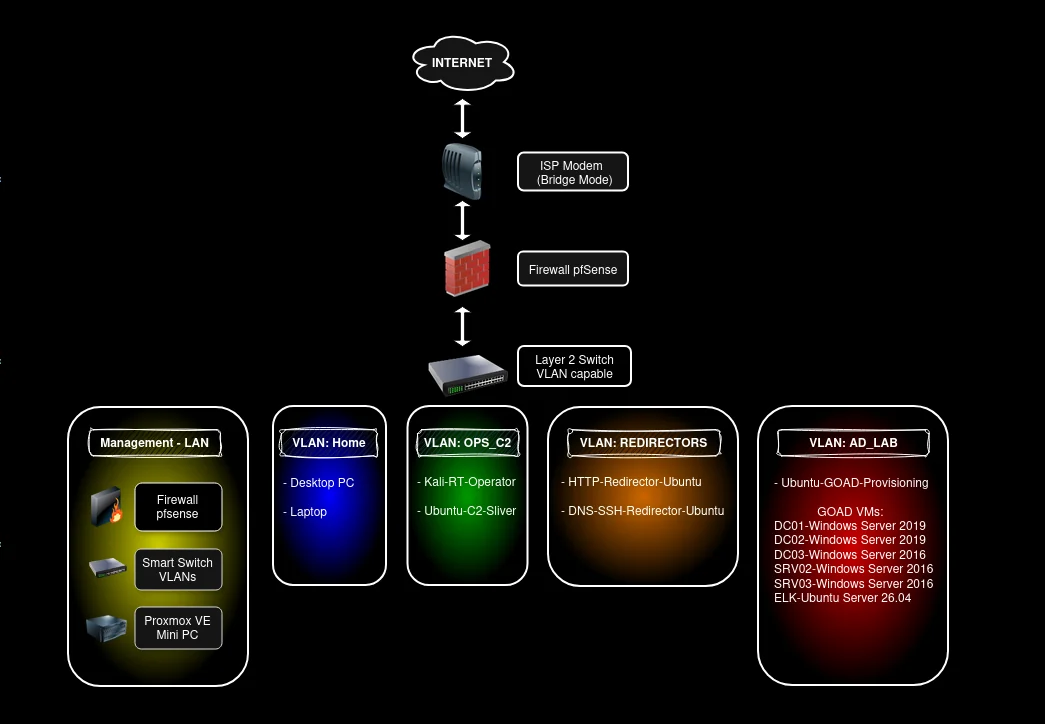 pho5nix/red-team-goad-lab-proxmox
Build guide for Red Teaming home lab. GOAD lab setup in Proxmox and pfSense, Operator/C2 and Redirectors.