

Check-vuln-CVE-2019-0708
 sugib3o/check-vuln-cve-2019-0708
Check vuln CVE 2019-0708
exploitationnetwork-securitypenetration-testing+3
7
sugib3o/check-vuln-cve-2019-0708Check vuln CVE 2019-0708
 revoltsecurities/cve-2023-20198
An Exploitation script developed to exploit the CVE-2023-20198 Cisco zero day vulnerability on their IOS routers
 nikhil1232/libssh-authentication-bypass
LibSSH Authentication Bypass CVE-2018-10933
 abraxas/cve-2026-19553-wrap-bio
Proof-of-concept lab reproducing CVE-2026-19553, where CPython ssl.SSLContext.wrap_bio() silently skips TLS hostname verification when…
 abraxas/cve-2026-105221-gist-tls
CVE-2026-105221 - gist RubyGem - High - MITM - GitHub OAuth token theft
 abraxas/ats-ipallow-method-case
Apache Traffic Server 10.2.0 - High - Remote - Privilege leftover - ip_allow method case
 abraxas/vsftpd-ssl-data-any-ticket
vsftpd 3.0.5 - High - Remote - Privilege leftover - FTPS data accepts any resumed ticket
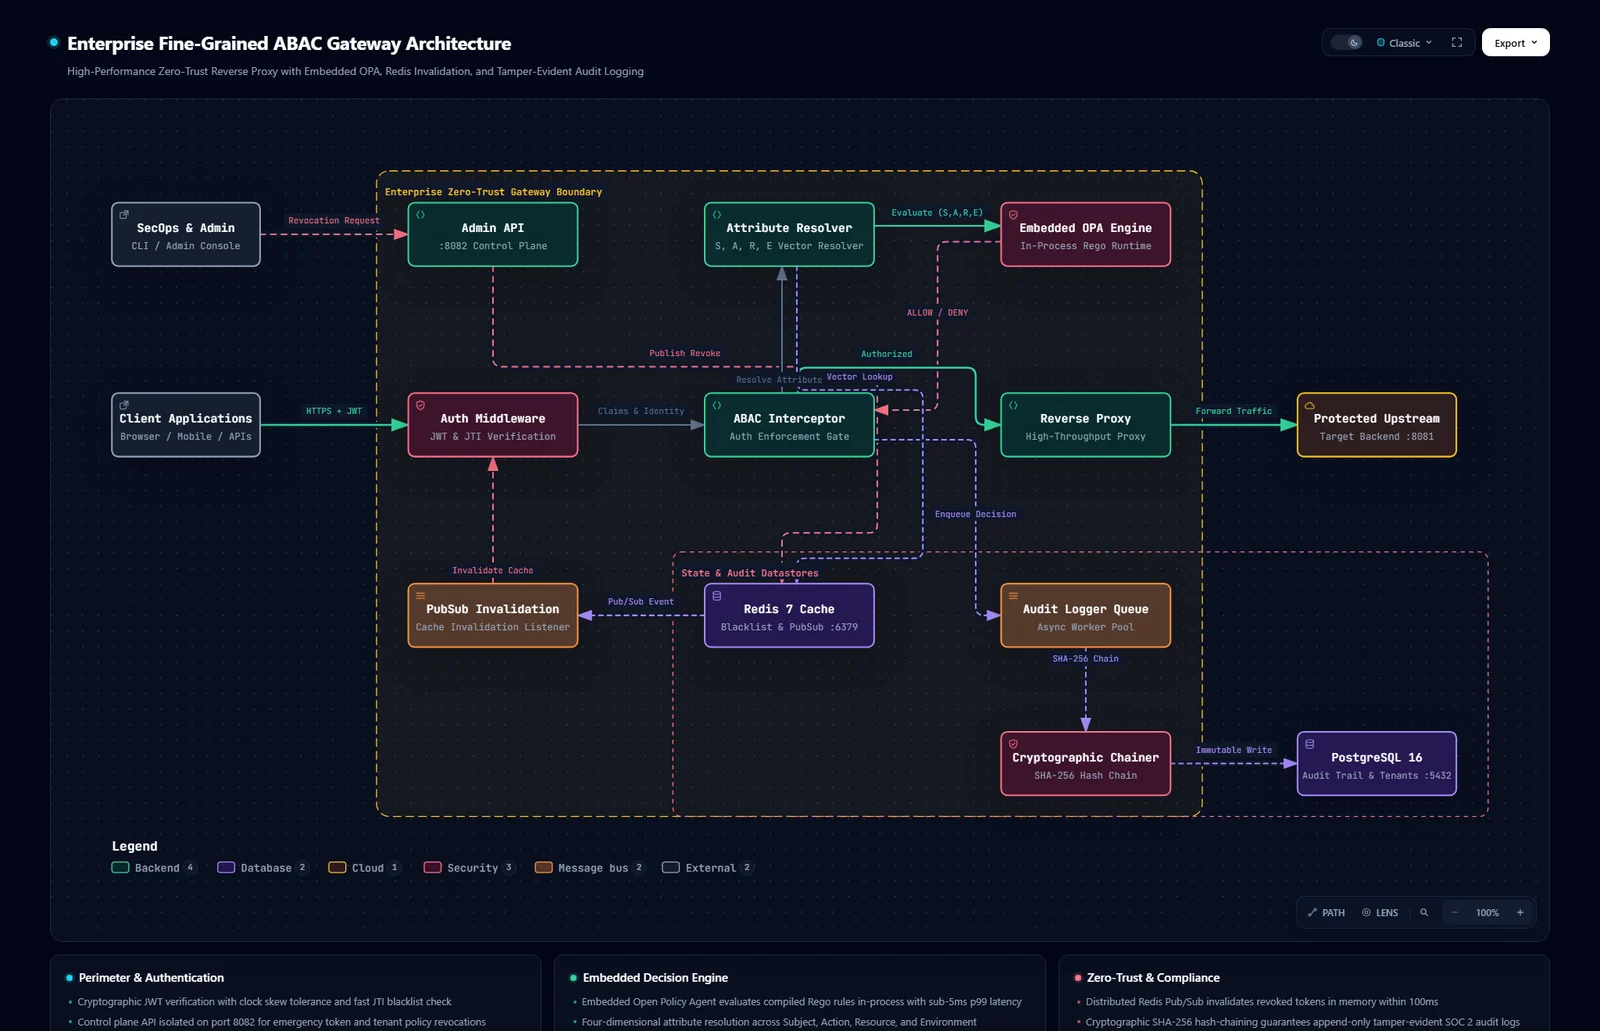
 kavryxdev-group/enterprise-abac-gateway
Zero-trust reverse proxy and ABAC authorization gateway in Go with embedded OPA policy evaluation and distributed token revocation.
 abraxas/pfsense-bsnmpd-conf
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - bsnmpd syslocation
 abraxas/opnsense-captive-lastseen-roam
OPNsense 26.7.6 - High - Remote - Network-access bypass - captive lastseen roam
 truerandom/nmap_draytek_rce
nmap script to detect CVE-2020-8515 on Draytek Devices
 tushargurav28/cve-2026-0257
Palo Alto Networks PAN-OS contains an authentication bypass caused by flaws in the GlobalProtect portal and gateway, letting attackers establish…
 balgan/cve-2026-24061
inetutils-telnetd Authentication Bypass - working
 iwallplace/cve-2026-26898-xiaomi-ssrf-hostheaderinjection
Unauthenticated SSRF in Xiaomi Mi Router 4A Gigabit Edition (firmware 3.0.24) via Host Header Injection — CVE-2026-26898
 r3verii/cve-2026-33555
One zero-byte QUIC packet is enough to desynchronize HAProxy's backend connection pool and smuggle HTTP requests across unrelated users — even users…
 harygovind/cve-2026-24061
CVE-2026-24061-PoC
 puckiestyle/cve-2024-23113
Detects CVE-2024-23113 format string vulnerability in FortiGate FGFM service via SSL connection on port 541, sending crafted payloads to verify RCE…
 emanueldosreis/nmap-cve-2023-35078-exploit
Nmap script to exploit CVE-2023-35078 - Mobile Iron Core