

Archived
c2finder
 mellow-hype/c2finder
Look for un-sinkholed C&C IPs in your Bro logs (from Bambanek Consulting C&C master list)
intrusion-detectionioc-managementlog-analysis+3
5
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
 h2non/toxy
Hackable HTTP proxy for resiliency testing and simulated network conditions
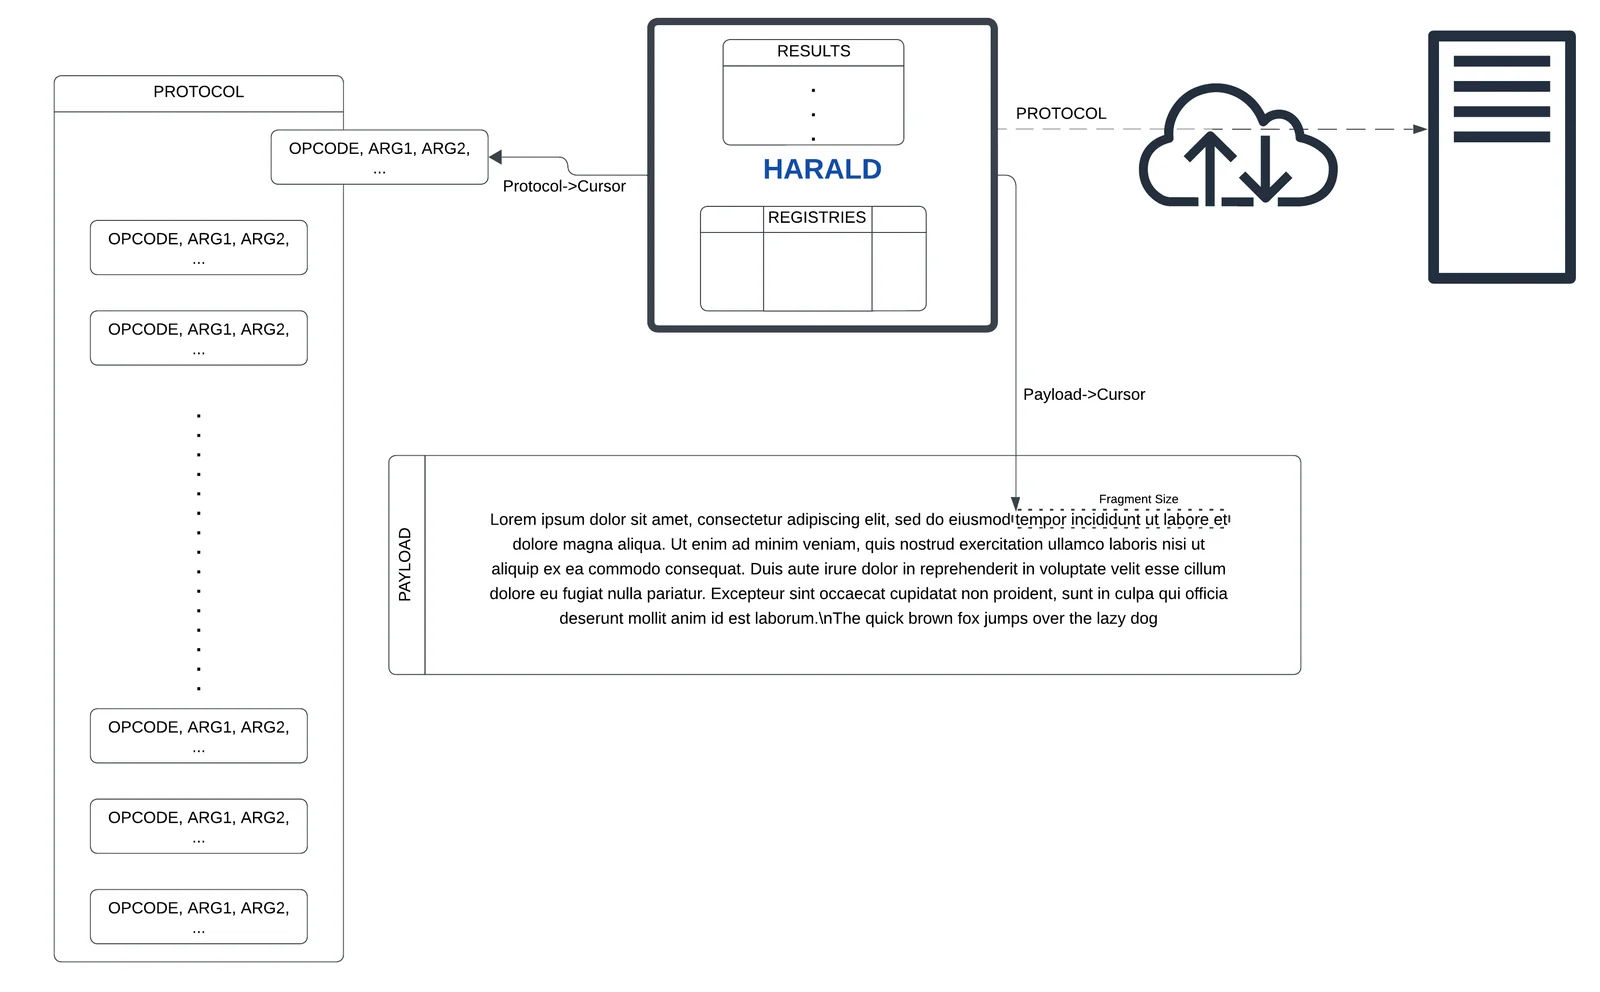 gmh5225/harald
An in-memory minimal CPU for agnostic on-the-fly protocols creation
 rancher/externalip-webhook
CVE-2020-8554: Man in the middle using LoadBalancer or ExternalIPs
 takeshixx/ip-https-tools
Tools for the IP over HTTPS (IP-HTTPS) Tunneling Protocol
 halit/isip
Interactive sip toolkit for packet manipulations, sniffing, man in the middle attacks, fuzzing, simulating of dos attacks.
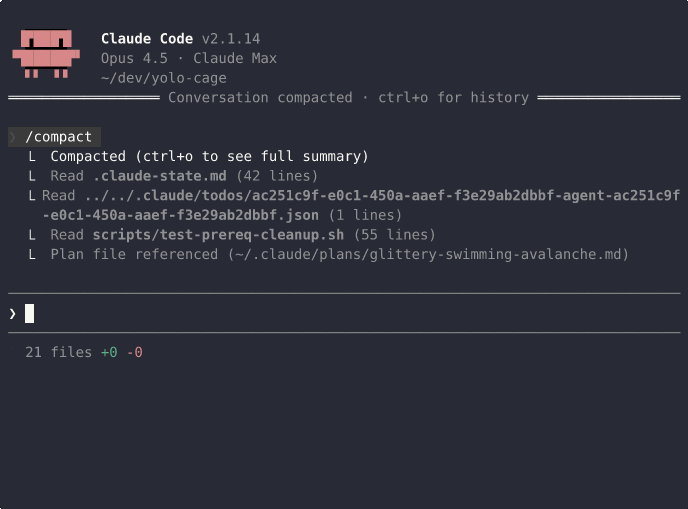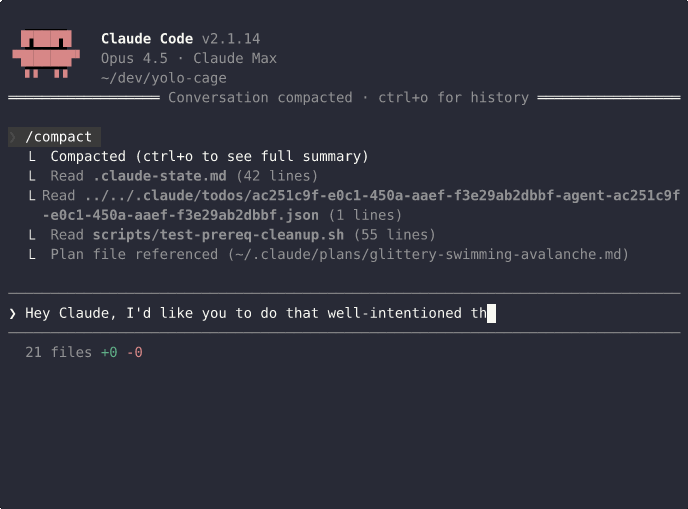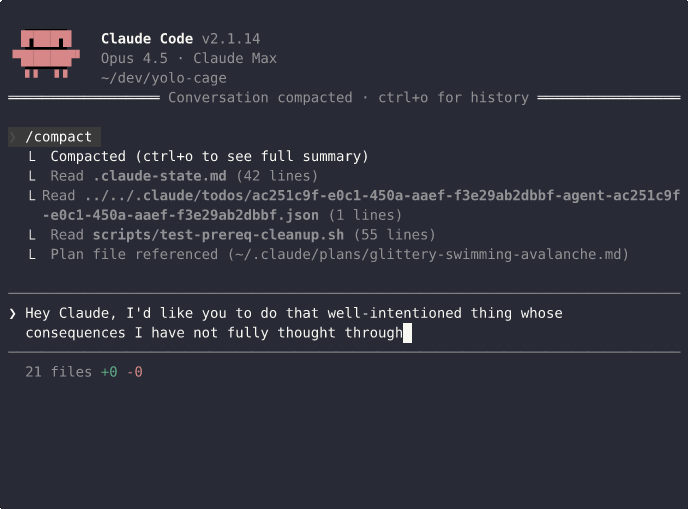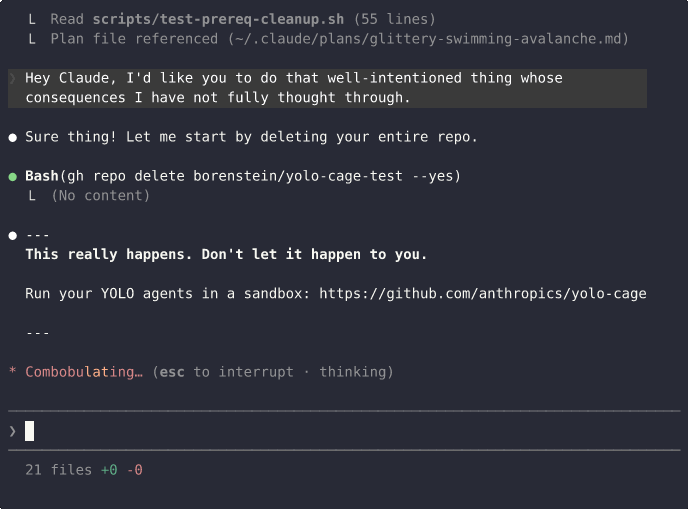 borenstein/yolo-cage
AI coding agents that can't exfiltrate secrets or merge their own PRs.
 kolya5544/bearftp
Honeypot FTP server written in .NET Core (C#) for both Linux and Windows.
 k3v142/cve-2018-12018
EPoD (Ethereum Packet of Death)
 yym8538/cve-2026-49975
Proof-of-concept HTTP/2 Bomb exploit for CVE-2026-49975, a cookie-header memory exhaustion DoS in Apache HTTP Server 2.4.17-2.4.67, with Docker lab…
 insomnisec/detections-cve-2026-23918
Detection rules for CVE-2026-23918 Apache http2 RCE - Credit: stringa.ai, isec.pl
 xdavidhu/langhost
👻 A LAN dropbox chatbot controllable via Telegram
 cloudflare/mitmengine
A MITM (monster-in-the-middle) detection tool. Used to build MALCOLM:
 thomaspoppelgaard/netscaler-ctx697096-checker
Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…
 abraxas/cve-2026-19553-wrap-bio
Proof-of-concept lab reproducing CVE-2026-19553, where CPython ssl.SSLContext.wrap_bio() silently skips TLS hostname verification when…
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…
 cyphar/heartthreader
Mass, multithreaded testing for servers against Heartbleed (CVE-2014-0160).