

LdapRelayScan
 zyn3rgy/ldaprelayscan
Check for LDAP protections regarding the relay of NTLM authentication
authenticationconfiguration-auditinginformation-gathering+5
zyn3rgy/ldaprelayscanCheck for LDAP protections regarding the relay of NTLM authentication
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 rancher/externalip-webhook
CVE-2020-8554: Man in the middle using LoadBalancer or ExternalIPs
 vishnunandan555/cordon
Run any command inside a restricted filesystem view on Linux
 horkimhab/cve-2026-68121
Proof-of-concept for CVE-2026-68121 (PPPoEject), providing a Python exploit implementation for authorized security research and lab testing.
 justmao945/mallory
HTTP/HTTPS proxy over SSH
 prowler-cloud/prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…
 opsxcq/docker-tor-hiddenservice-nginx
Easily setup a hidden service inside the Tor network
 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 byt3bl33d3r/itwasalladream
A PrintNightmare (CVE-2021-34527) Python Scanner. Scan entire subnets for hosts vulnerable to the PrintNightmare RCE
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 binarydefense/log4j-honeypot-flask
Internal network honeypot for detecting if an attacker or insider threat scans your network for log4j CVE-2021-44228
 lockness-ko/xz-vulnerable-honeypot
An ssh honeypot with the XZ backdoor. CVE-2024-3094
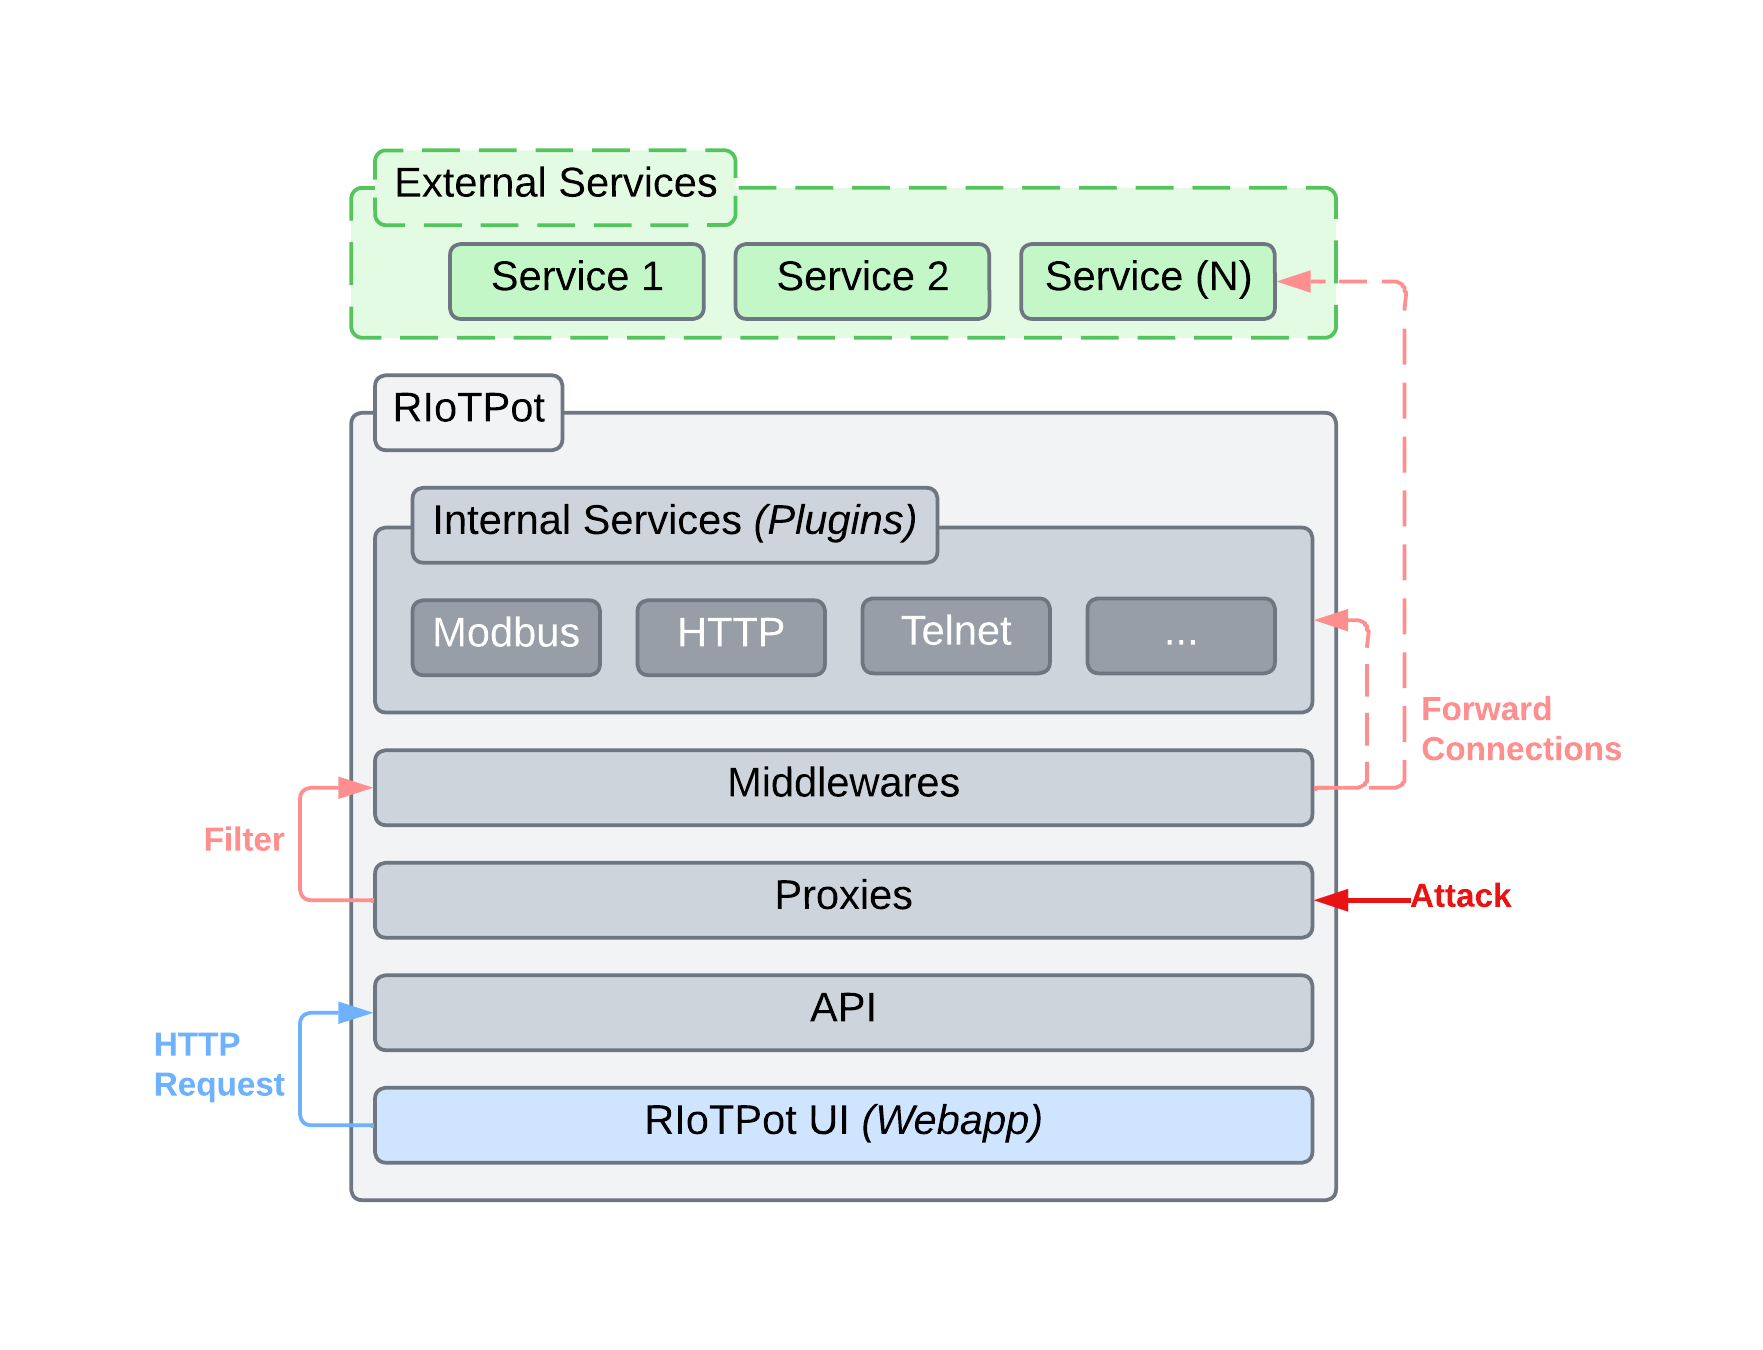 aau-network-security/riotpot
IoT and Operational Technology Honeypot
 s1ko/cve-2026-52616
Advisory and benign PoC for OS command injection in an nmap MCP server, with duplicate CVE tracking, detection guidance, and mitigation.
 regelepuma/http-2-rapid-reset-ddos
PoC for HTTP/2 Rapid Reset DDoS Vulnerability - CVE-2023-44487