
PiX-C2
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
command-and-controlnetwork-securitypacket-sniffing-analysis+3
robertdavis1/pix-c2Ping Exfiltration Command and Control (PiX-C2)
 cloudflare/mitmengine
A MITM (monster-in-the-middle) detection tool. Used to build MALCOLM:
 tranqtruong/detect-bluekeep
a simple tool to detect the exploitation of BlueKeep vulnerability (CVE-2019-0708)
 zanks08/cve-2023-44487-demo
Demo for detection and mitigation of HTTP/2 Rapid Reset vulnerability (CVE-2023-44487)
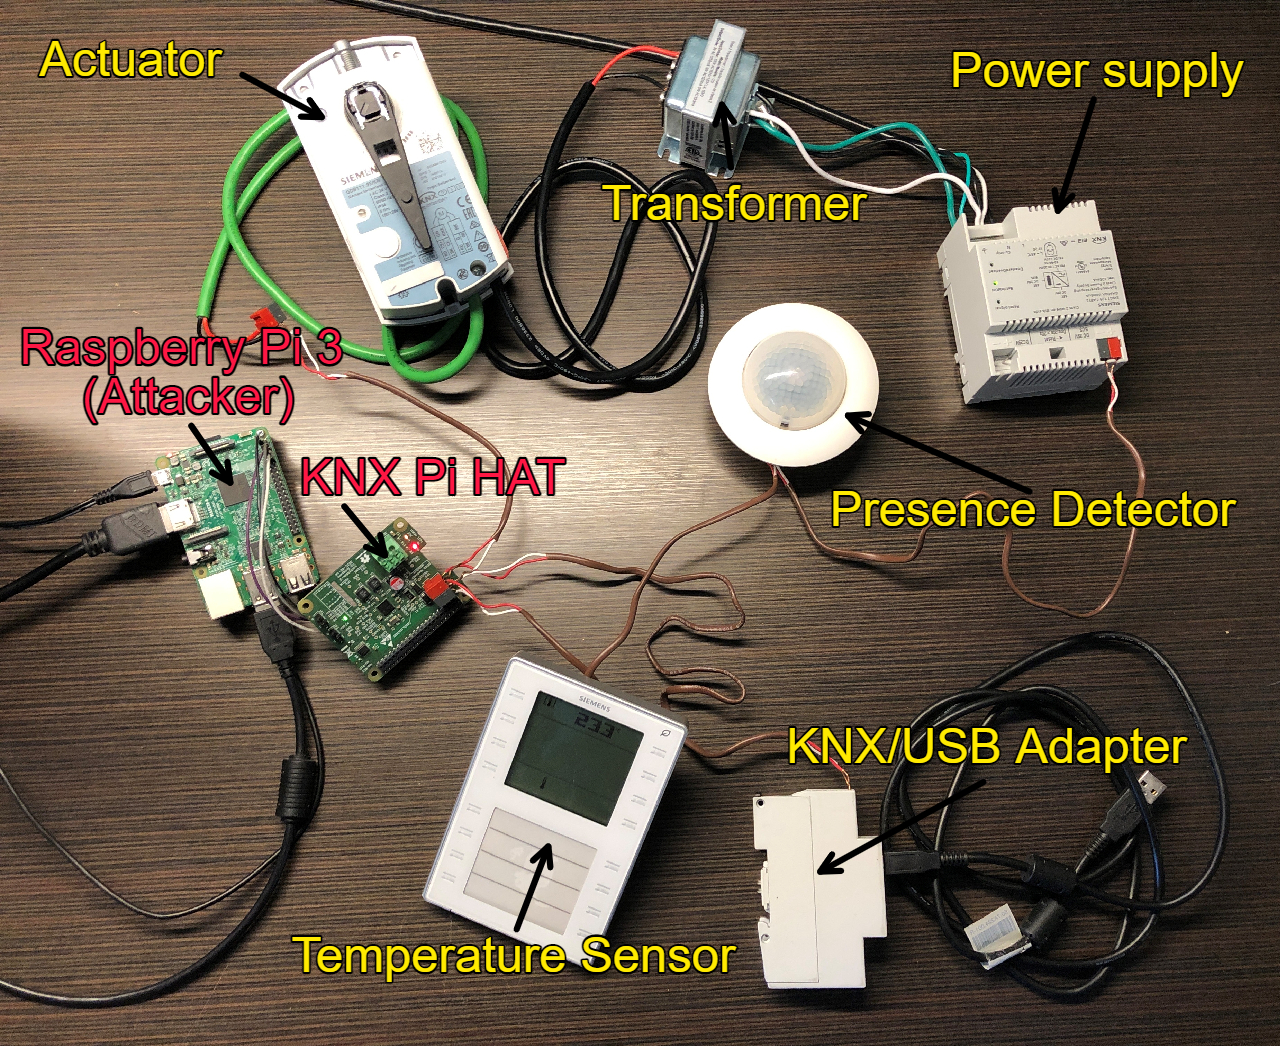 chrism09/knx-bus-dump
A tool to listen on a KNX bus via TPUART and the Calimero Project suite and to dump the data from the packets into a Wireshark-Compatible file hex…
 uthrasri/openssl_g2.5_cve-2014-3570_01
General-purpose cryptography library and SSL/TLS toolkit implementing ciphers, digests, public key algorithms, X.509 certificates, and a command-line…
 mrmtwoj/cve-2024-6387
regreSSHion is a security tool designed to test for vulnerabilities related to CVE-2024-6387, specifically focusing on SSH and remote access…
 gmh5225/deluded-openssl-3.2.0
Robust open-source toolkit implementing TLS, DTLS, and QUIC protocols with a full-strength cryptographic library, command-line tool for key…
 efforg/rayhunter
Rust tool to detect cell site simulators on an orbic mobile hotspot
 matthewclarkmay/geoip-attack-map
Cyber security geoip attack map that follows syslog and parses IPs/port numbers to visualize attackers in real time.
 gvcoder09/nodpi4android
Android proxy app that circumvents Deep Packet Inspection censorship by fragmenting TLS ClientHello packets and rewriting the TLS version to restore…
 mhils/honeyproxy
This project is now part of @mitmproxy.
 pasquini-dario/project_mantis
Project Mantis: Hacking Back the AI-Hacker; Prompt Injection as a Defense Against LLM-driven Cyberattacks
 seungsoo-lee/delta
PROJECT DELTA: SDN SECURITY EVALUATION FRAMEWORK
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
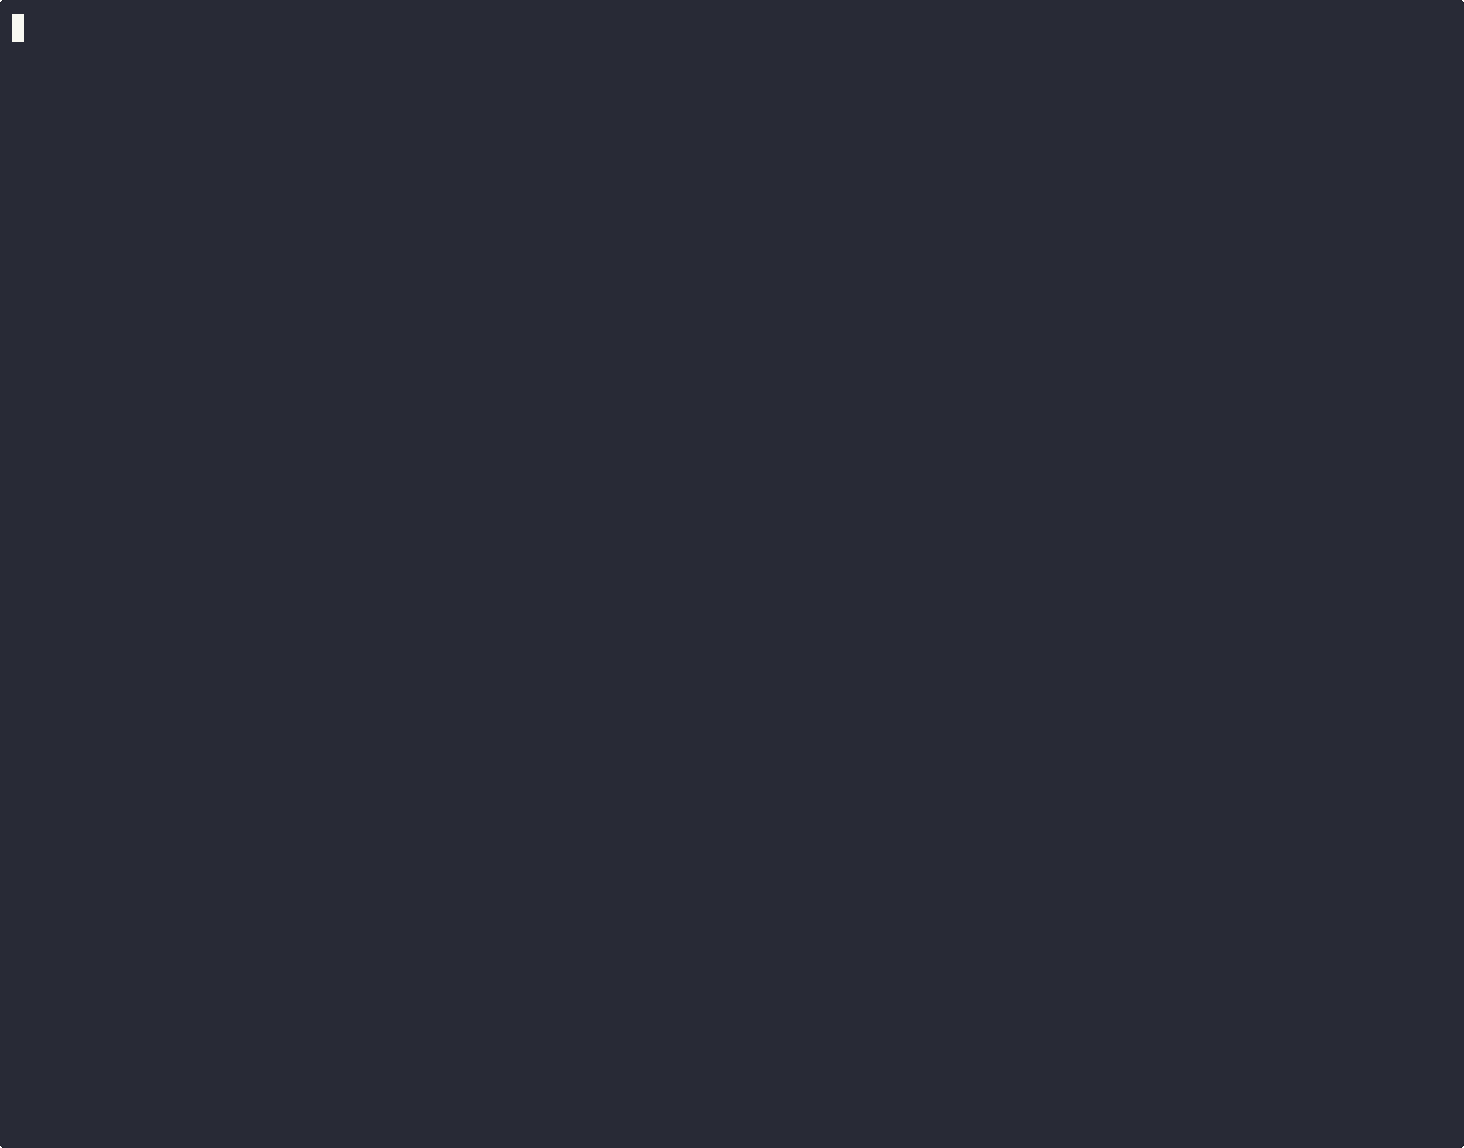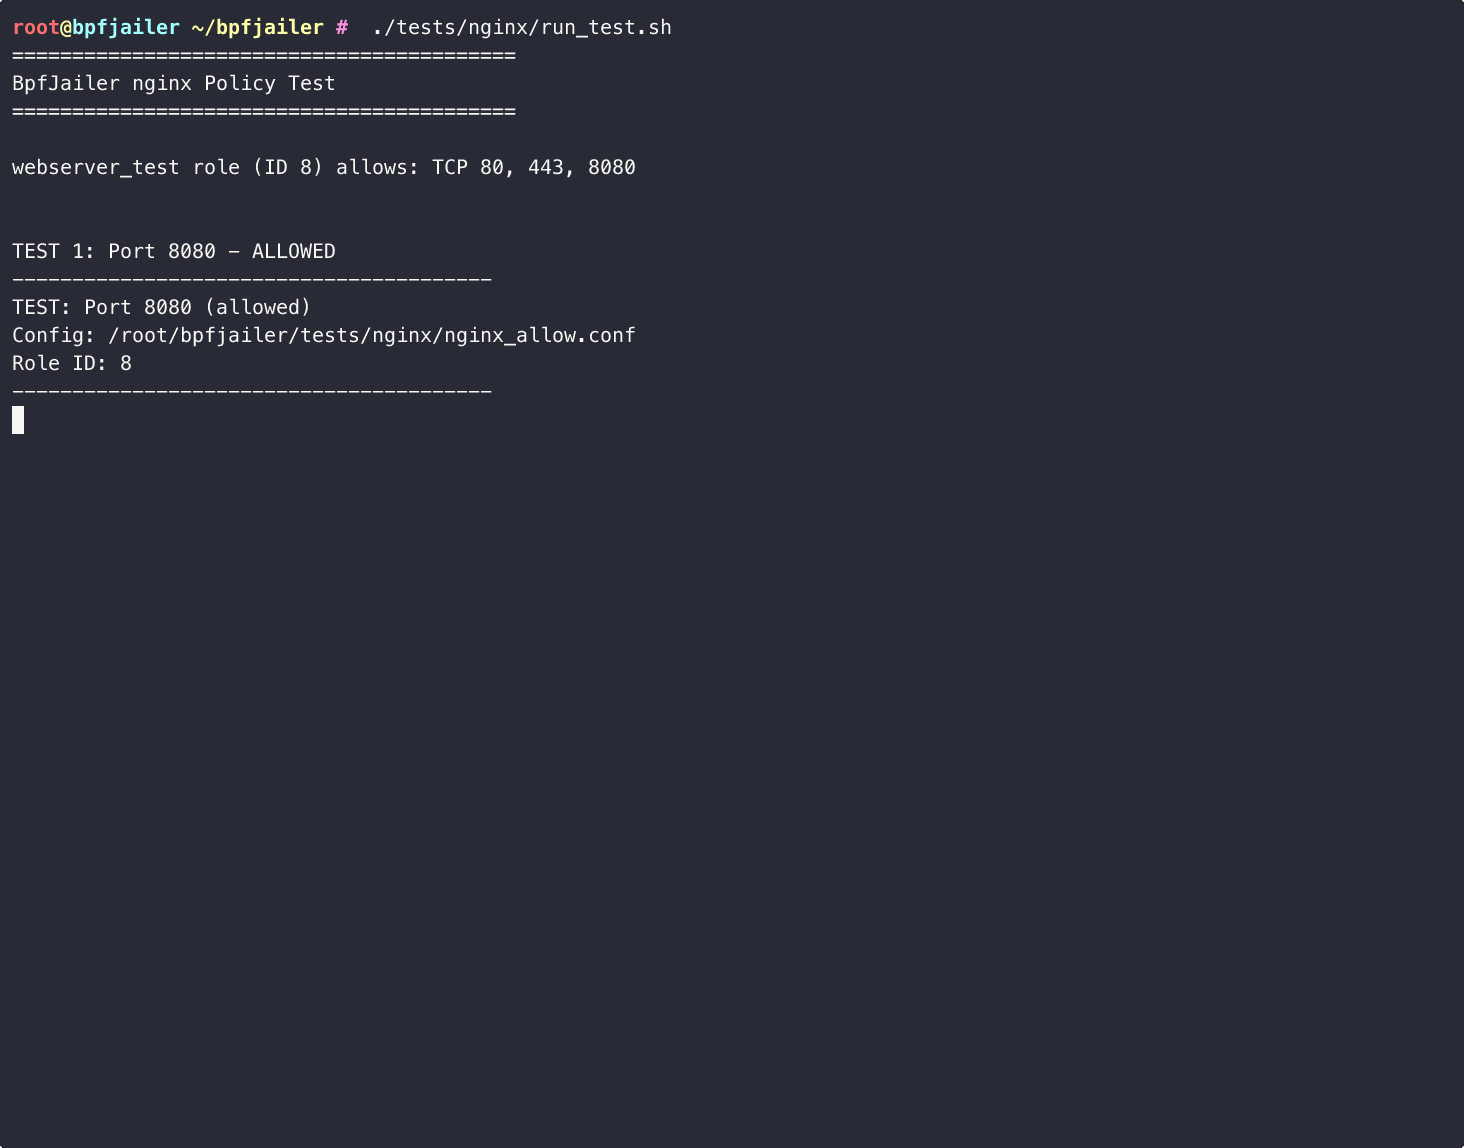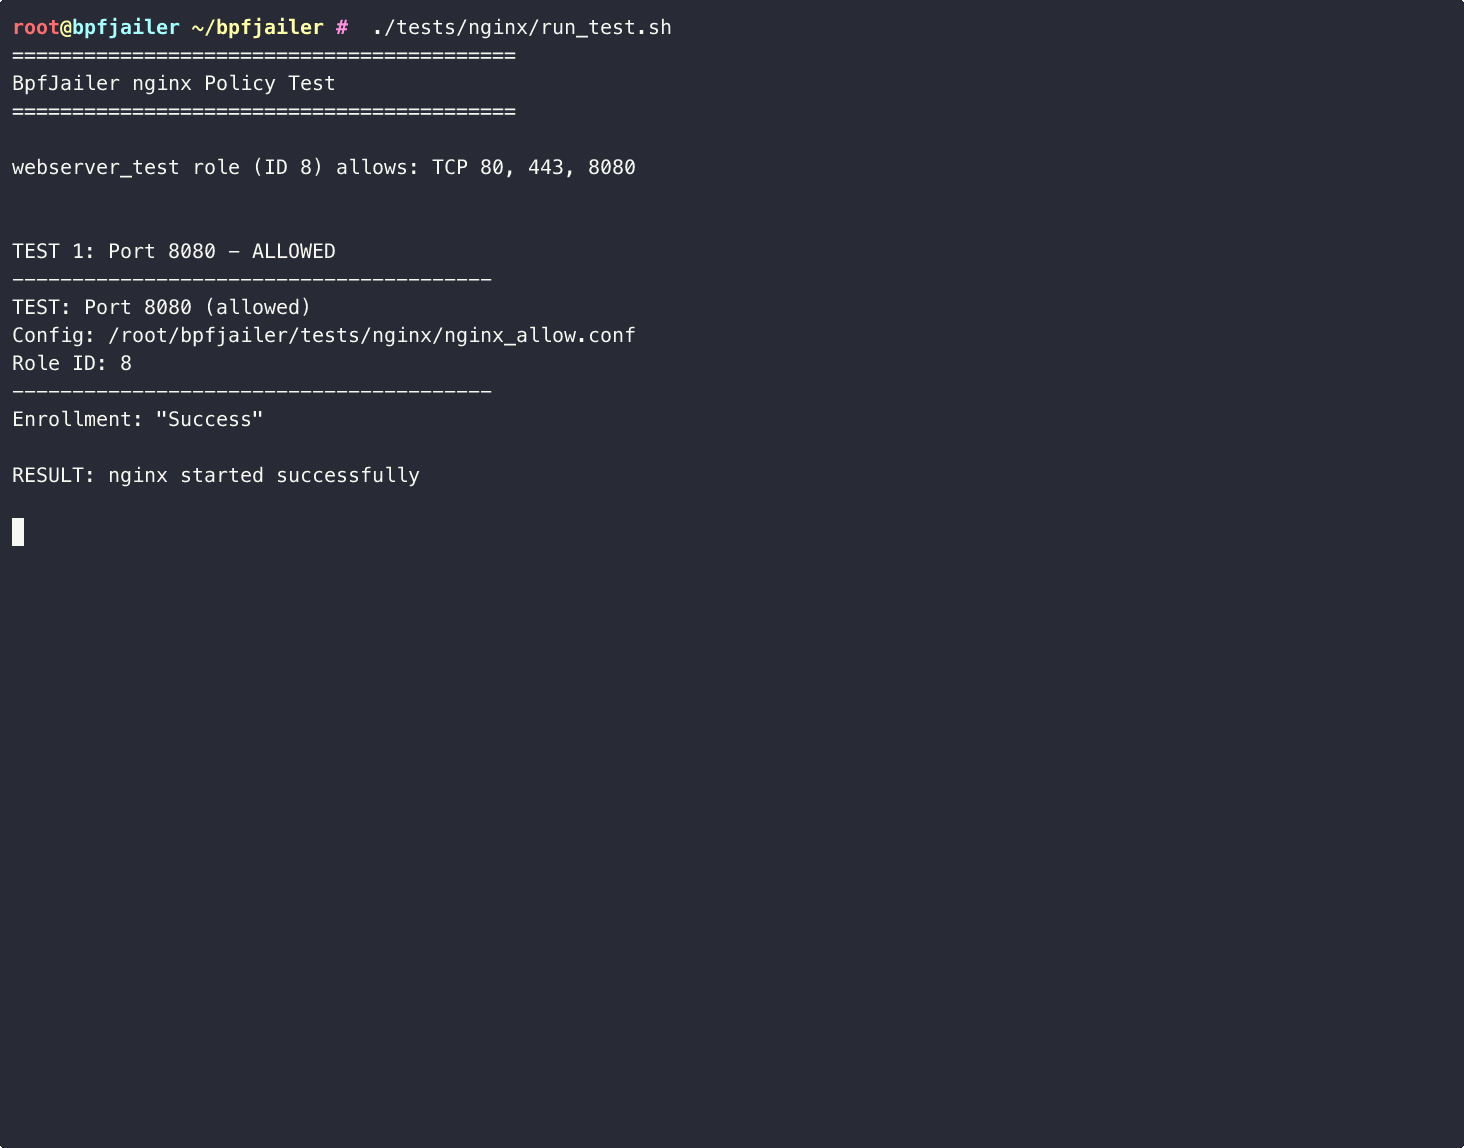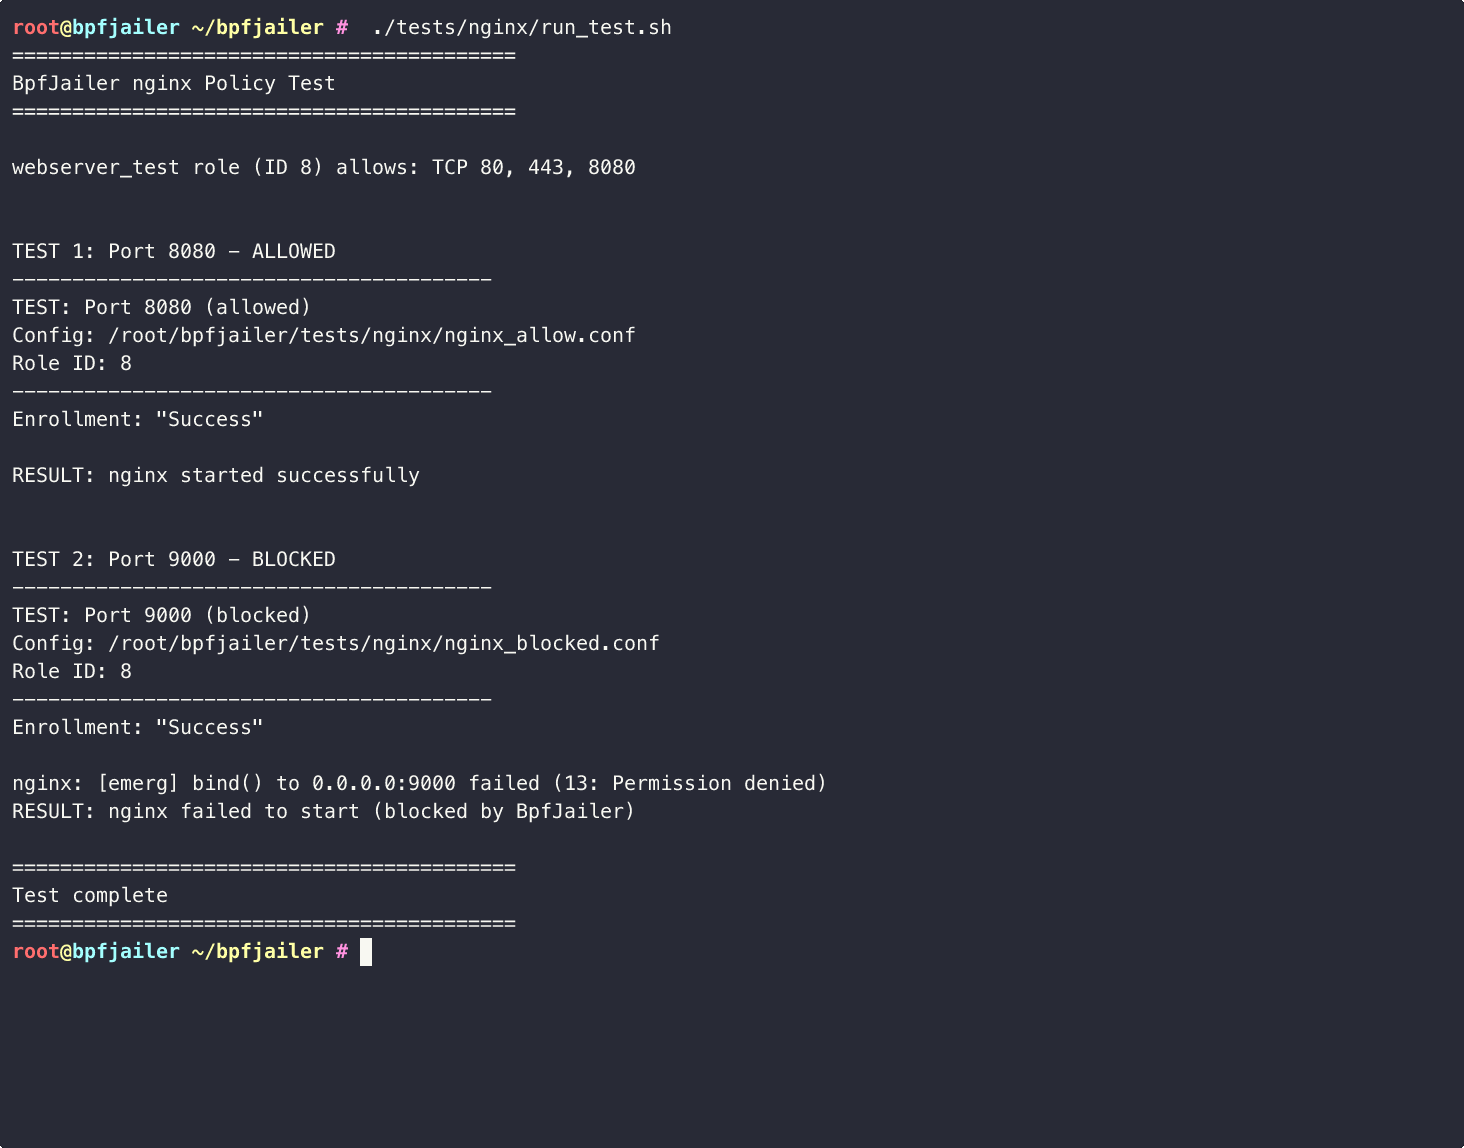 gen0sec/jailer
Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
 abbbe/sslcaudit
Automated SSL/TLS client security testing tool for detecting MITM vulnerabilities in thick clients, mobile apps, and network appliances.
 toperaproject/topera
IPv6 analysis tool: the other side