

arp-dns-attacks
 ashishraste/arp-dns-attacks
ARP spoofing, HTTP redirection, DNS spoofing and DNS forging using pcap library
dns-analysiseducationexploitation+3
31
ashishraste/arp-dns-attacksARP spoofing, HTTP redirection, DNS spoofing and DNS forging using pcap library
 ntrippar/arpwner
ARP spoofing and network packet manipulation tool for man-in-the-middle attacks, traffic interception, and LAN reconnaissance using Python and pcap.
 dtrecherel/dnsspoof
A DNS spoofer tool written in Python3.
 strozfriedberg/badsamba
This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
 priyankvadaliya/hack-captive-portal
This script helps to pass through the captive portals in public Wi-Fi networks. It hijacks IP and MAC from somebody who is already connected and…
 yosangwon/arp-dns-spoof
Sample code for DNS spoofing with ARP poisoning.
 kamorin/dhcpig
DHCP exhaustion script written in python using scapy network library
 baptisterajaut/radmin-vpn-linux
Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss
 firehol/firehol
iptables-based stateful firewall with human-friendly configuration and optional QoS (FireQOS) for bandwidth management.
 mirage/qubes-mirage-firewall
Minimal unikernel firewall for QubesOS that filters network traffic, implements NAT, and communicates via Qubes DB and qrexec.
 k4yt3x/scutum
Linux Automatic ARP (TCP / UDP / ICMP) Firewall

 halildeniz/macmaster
Advanced Network Interface Management and Monitoring
 freeradius/freeradius-server
High-performance multi-protocol AAA server for RADIUS, DHCPv4/v6, DNS, TACACS+, and VMPS, centralizing network authentication, authorization, and…
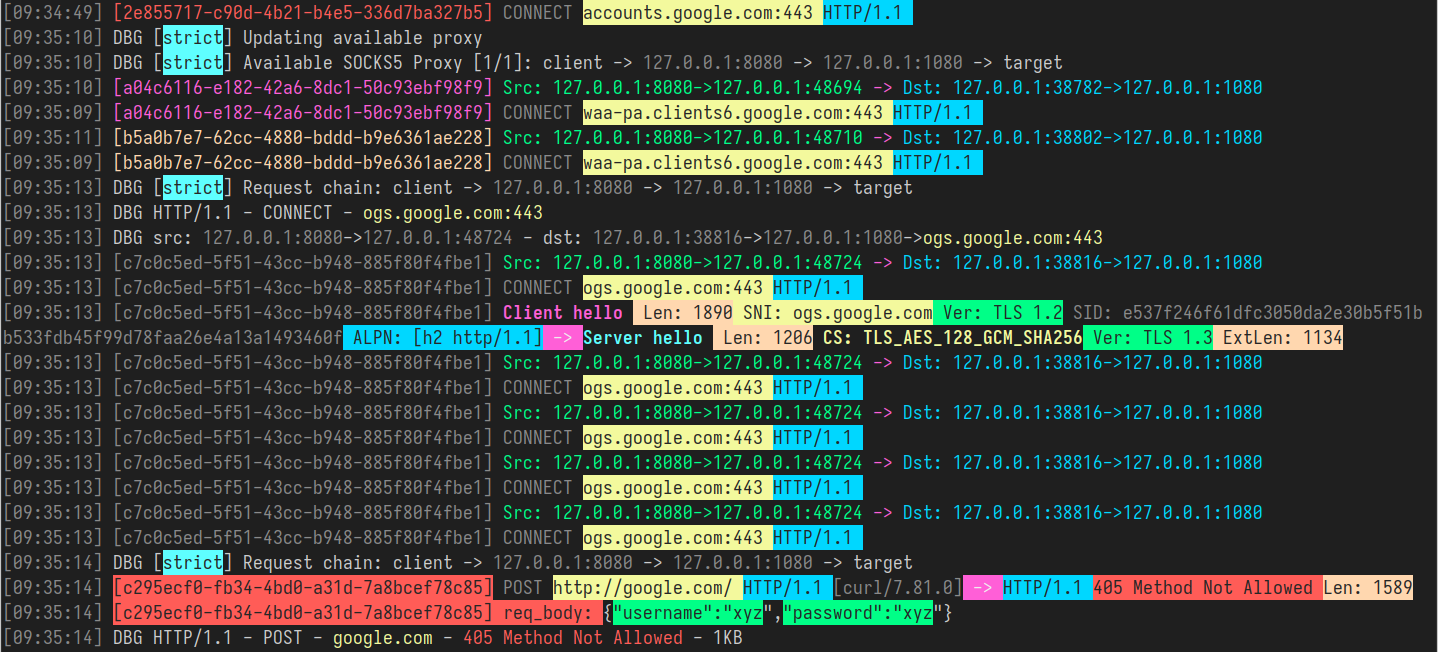 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.
 kevin-robertson/inveighzero
.NET IPv4/IPv6 machine-in-the-middle tool for penetration testers
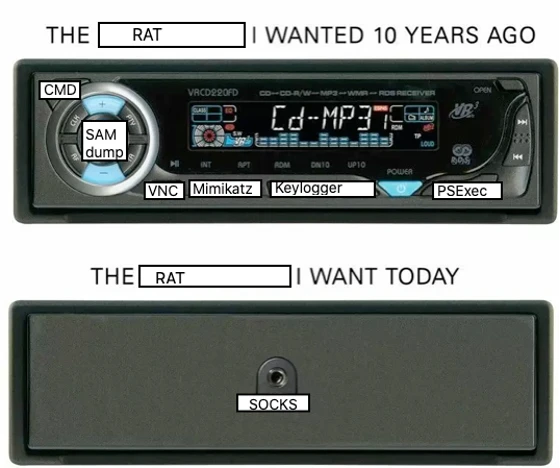 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…