CiscoSpectreTakeover
 plyrthn/ciscospectretakeover
A POC chain exploit using the recent Cisco SMP exploit (CVE-2017-6736) to chain into Spectre (CVE-2017-5753 and CVE-2017-5715)
exploitationnetwork-securitypenetration-testing+2
plyrthn/ciscospectretakeoverA POC chain exploit using the recent Cisco SMP exploit (CVE-2017-6736) to chain into Spectre (CVE-2017-5753 and CVE-2017-5715)
 klairmanraj/multi-vlan-enterprise-network-vulnerability-assessment
Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…
 evilsocket/bettercap
DEPRECATED, bettercap developement moved here: https://github.com/bettercap/bettercap
 check-risk-waf/check-risk-waf
Reverse-proxy web application firewall with WAF, anti-bot and anti-DDoS protection at L3/L4/L7, custom rules, rate limiting, geo/IP filtering and…
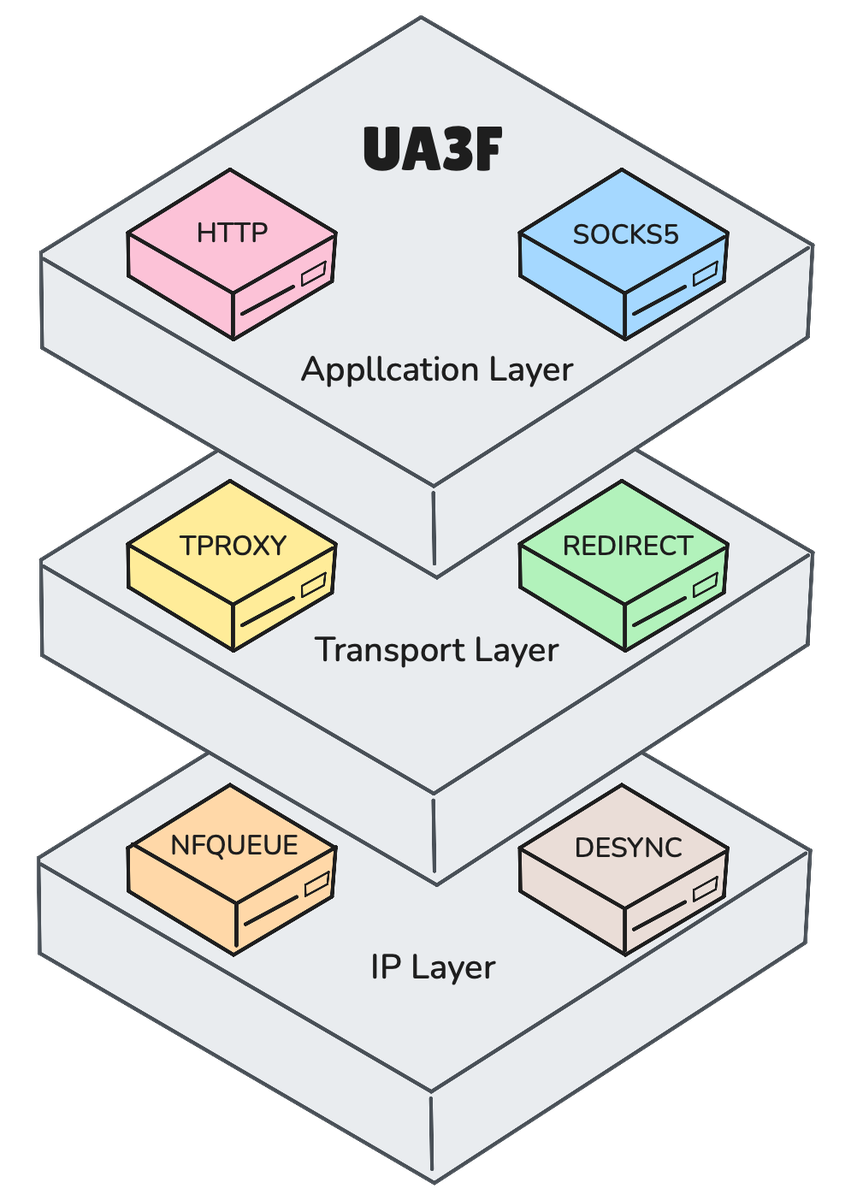 sunbk201/ua3f
Transparent HTTP(S) rewriting proxy supporting HTTP, SOCKS5, TPROXY, REDIRECT and NFQUEUE modes with HTTPS MitM, rule-based header/body rewriting and…
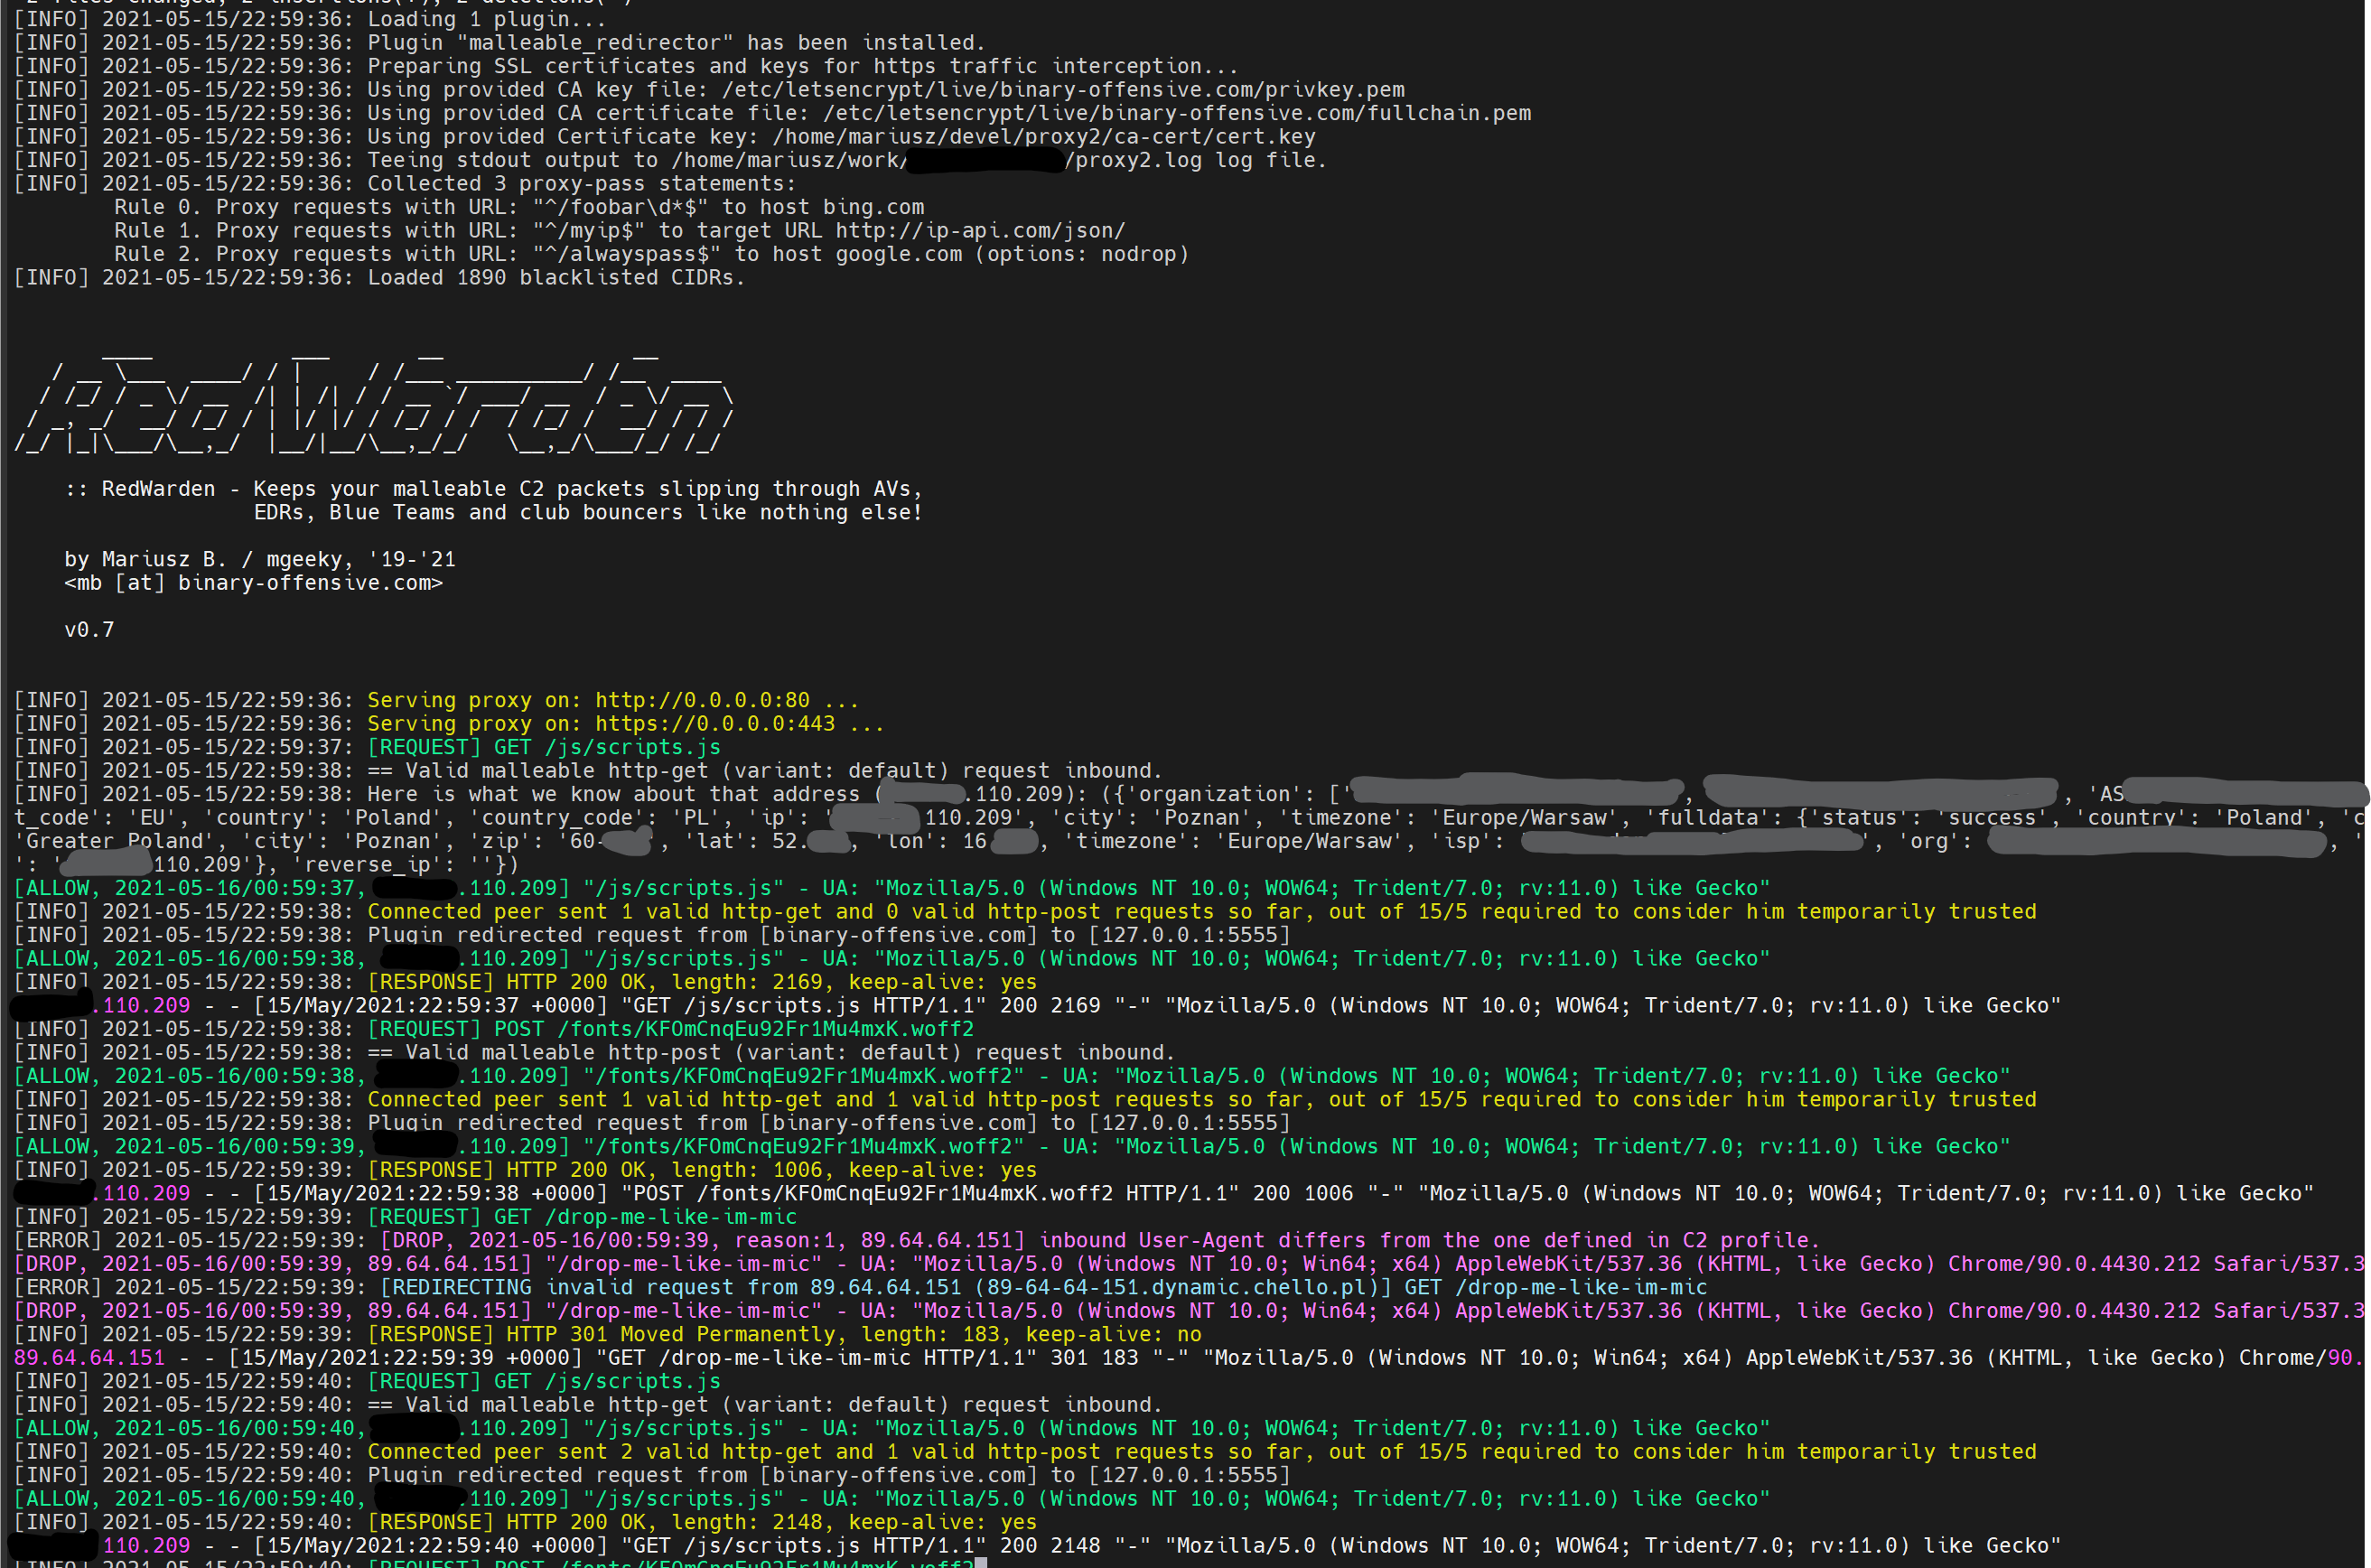 mgeeky/redwarden
Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation
 abraxas/ats-ipallow-method-case
Apache Traffic Server 10.2.0 - High - Remote - Privilege leftover - ip_allow method case
 yili-soc/vm-homelab-log4shell-assessment
Full-lifecycle vulnerability management on a live Log4Shell (CVE-2021-44228) target — scan, manual exploitation, network detection, and remediation…
 fevar54/cve-2026-20245---cisco-sd-wan-privilege-escalation-exploit
**Este código es SOLO para fines educativos y pruebas de seguridad autorizadas.**