vedas-signatures
 arpsyndicate/vedas-signatures
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs
curated-resourcesdefensive-toolsintrusion-detection+8
23
arpsyndicate/vedas-signaturesVEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
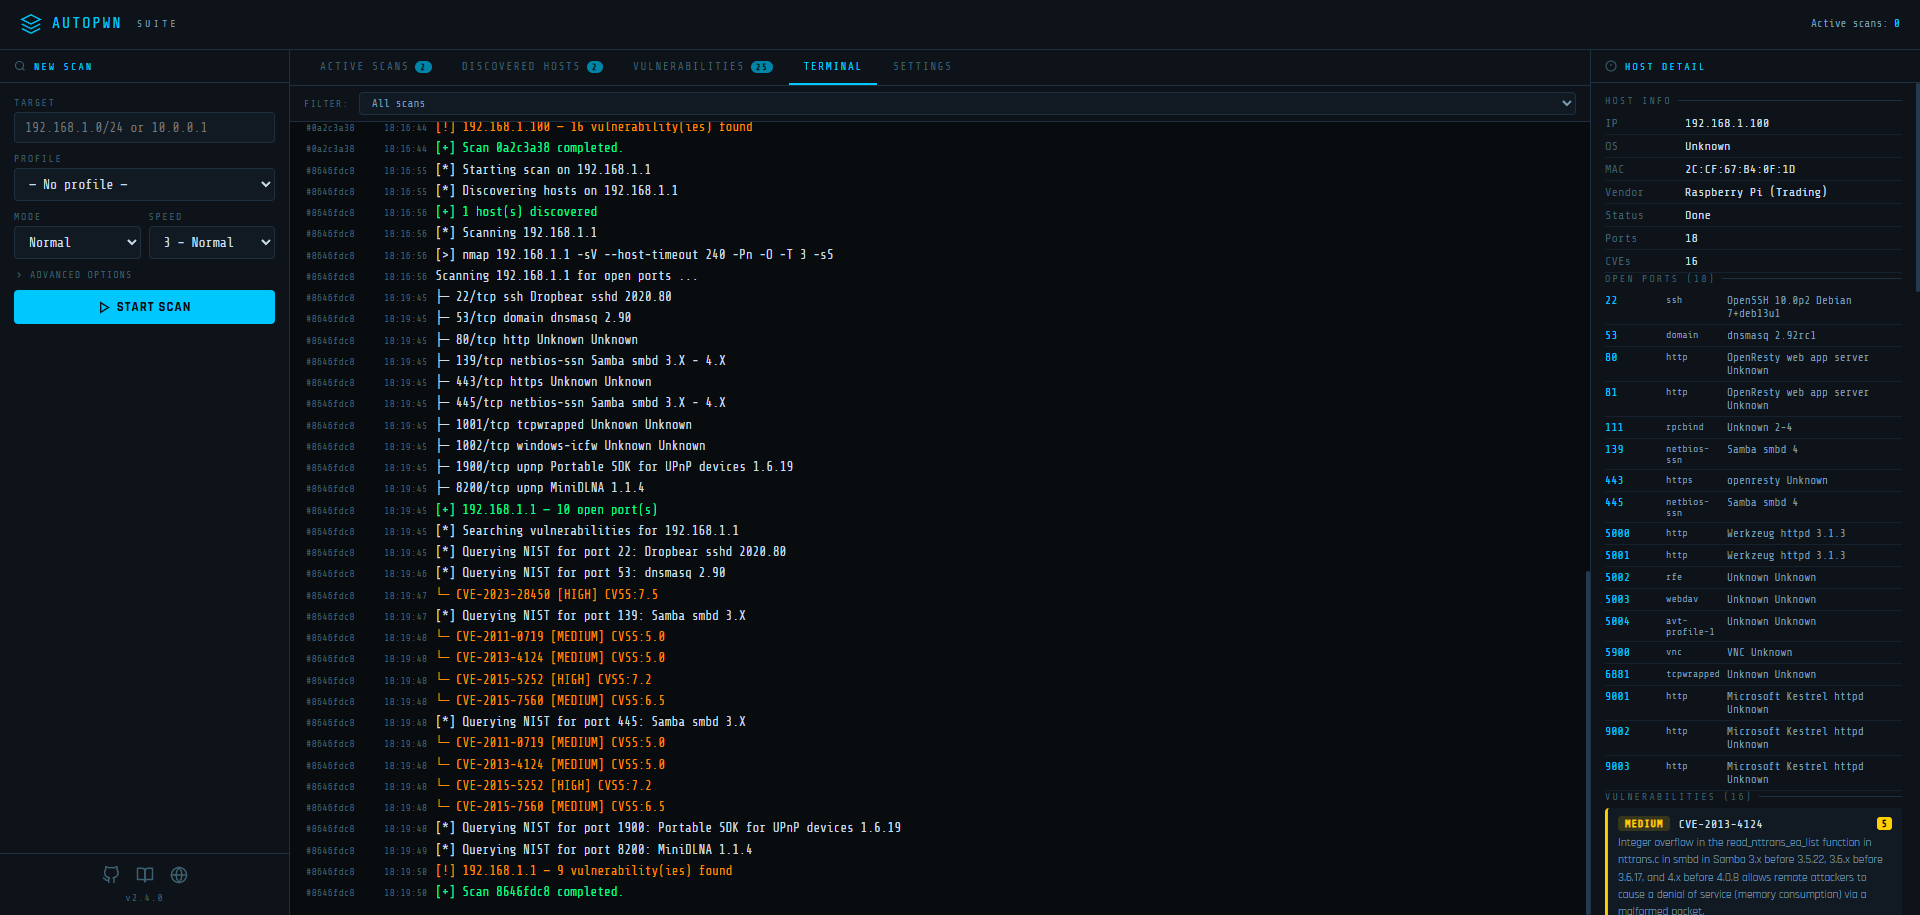 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 abraxas/vsftpd-ssl-data-any-ticket
vsftpd 3.0.5 - High - Remote - Privilege leftover - FTPS data accepts any resumed ticket
 abraxas/vsftpd-deny-file-brace-child
vsftpd 3.0.5 - High - Remote - Privilege leftover - brace deny_file misses .private/secret
 abraxas/spark-rpc-stream-unauth
Apache Spark 4.2.0 - High - Remote - File read - unauth RPC StreamRequest File join
 abraxas/pfsense-qinq-parent-if
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - QinQ parent-if ifconfig
 abraxas/opnsense-captive-lastseen-roam
OPNsense 26.7.6 - High - Remote - Network-access bypass - captive lastseen roam
 abraxas/cve-2026-19553-wrap-bio
Proof-of-concept lab reproducing CVE-2026-19553, where CPython ssl.SSLContext.wrap_bio() silently skips TLS hostname verification when…
 abraxas/cve-2026-105221-gist-tls
CVE-2026-105221 - gist RubyGem - High - MITM - GitHub OAuth token theft
 blessedrebus/krawl
Krawl is a customizable, lightweight, cloud-native web deception server and anti-crawler that creates fake web applications with low-hanging…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 d0rb/shellscope
Defensive exposure auditor for Plex2Shell and php2shell — find your own before they find you.
 infat0x/cve-2026-24061
Proof-of-concept exploit for Telnet NEW-ENVIRON authentication bypass vulnerability (CVE-2026-24061). Allows unauthorized access to vulnerable Telnet…
 abraxas/pfsense-bsnmpd-conf
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - bsnmpd syslocation
 abraxas/ats-ipallow-method-case
Apache Traffic Server 10.2.0 - High - Remote - Privilege leftover - ip_allow method case
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88772
Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.