

 umputun/reproxy
Lightweight edge HTTP(S) server and reverse proxy with automatic SSL, Docker/Consul discovery, per-route authentication, rate limiting, and…
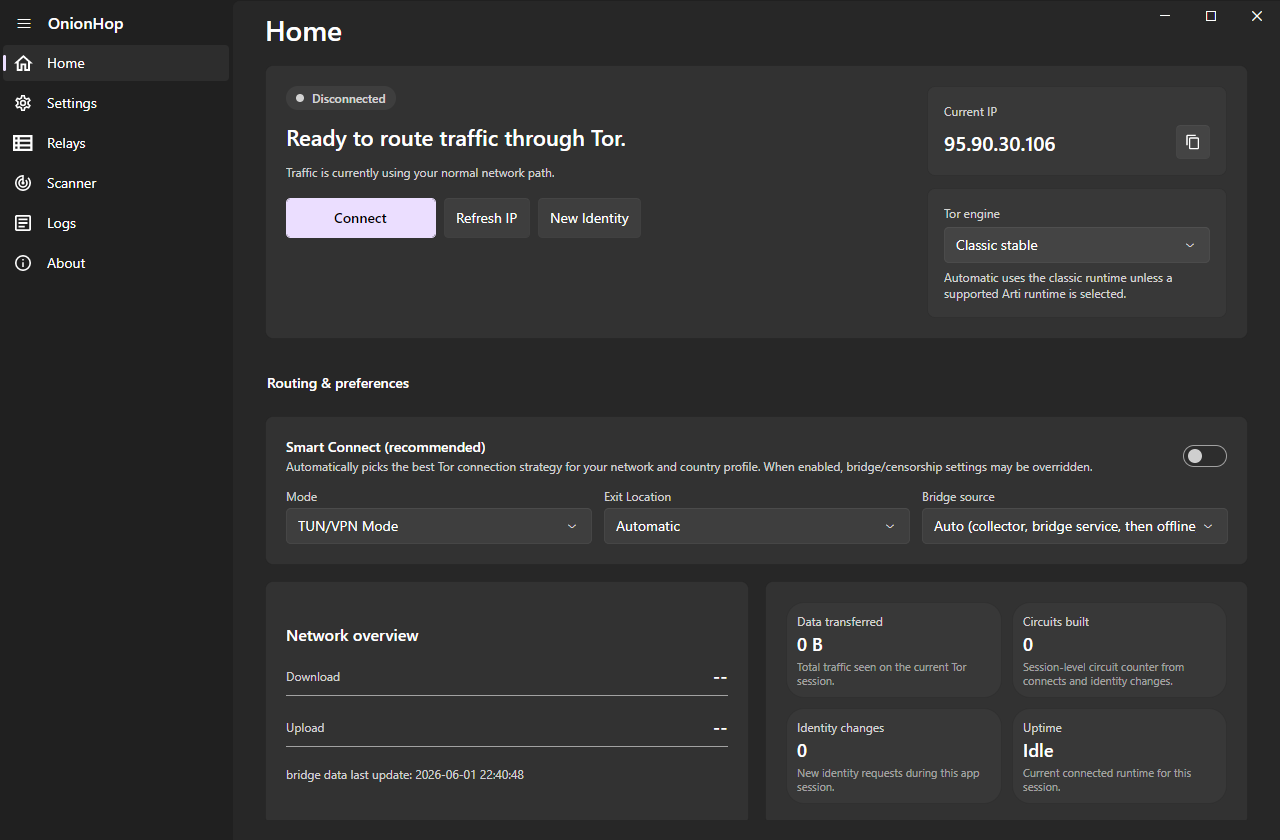 center2055/onionhop
Privacy-first Desktop app that routes your traffic through Tor - Anonymous browsing made simple
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
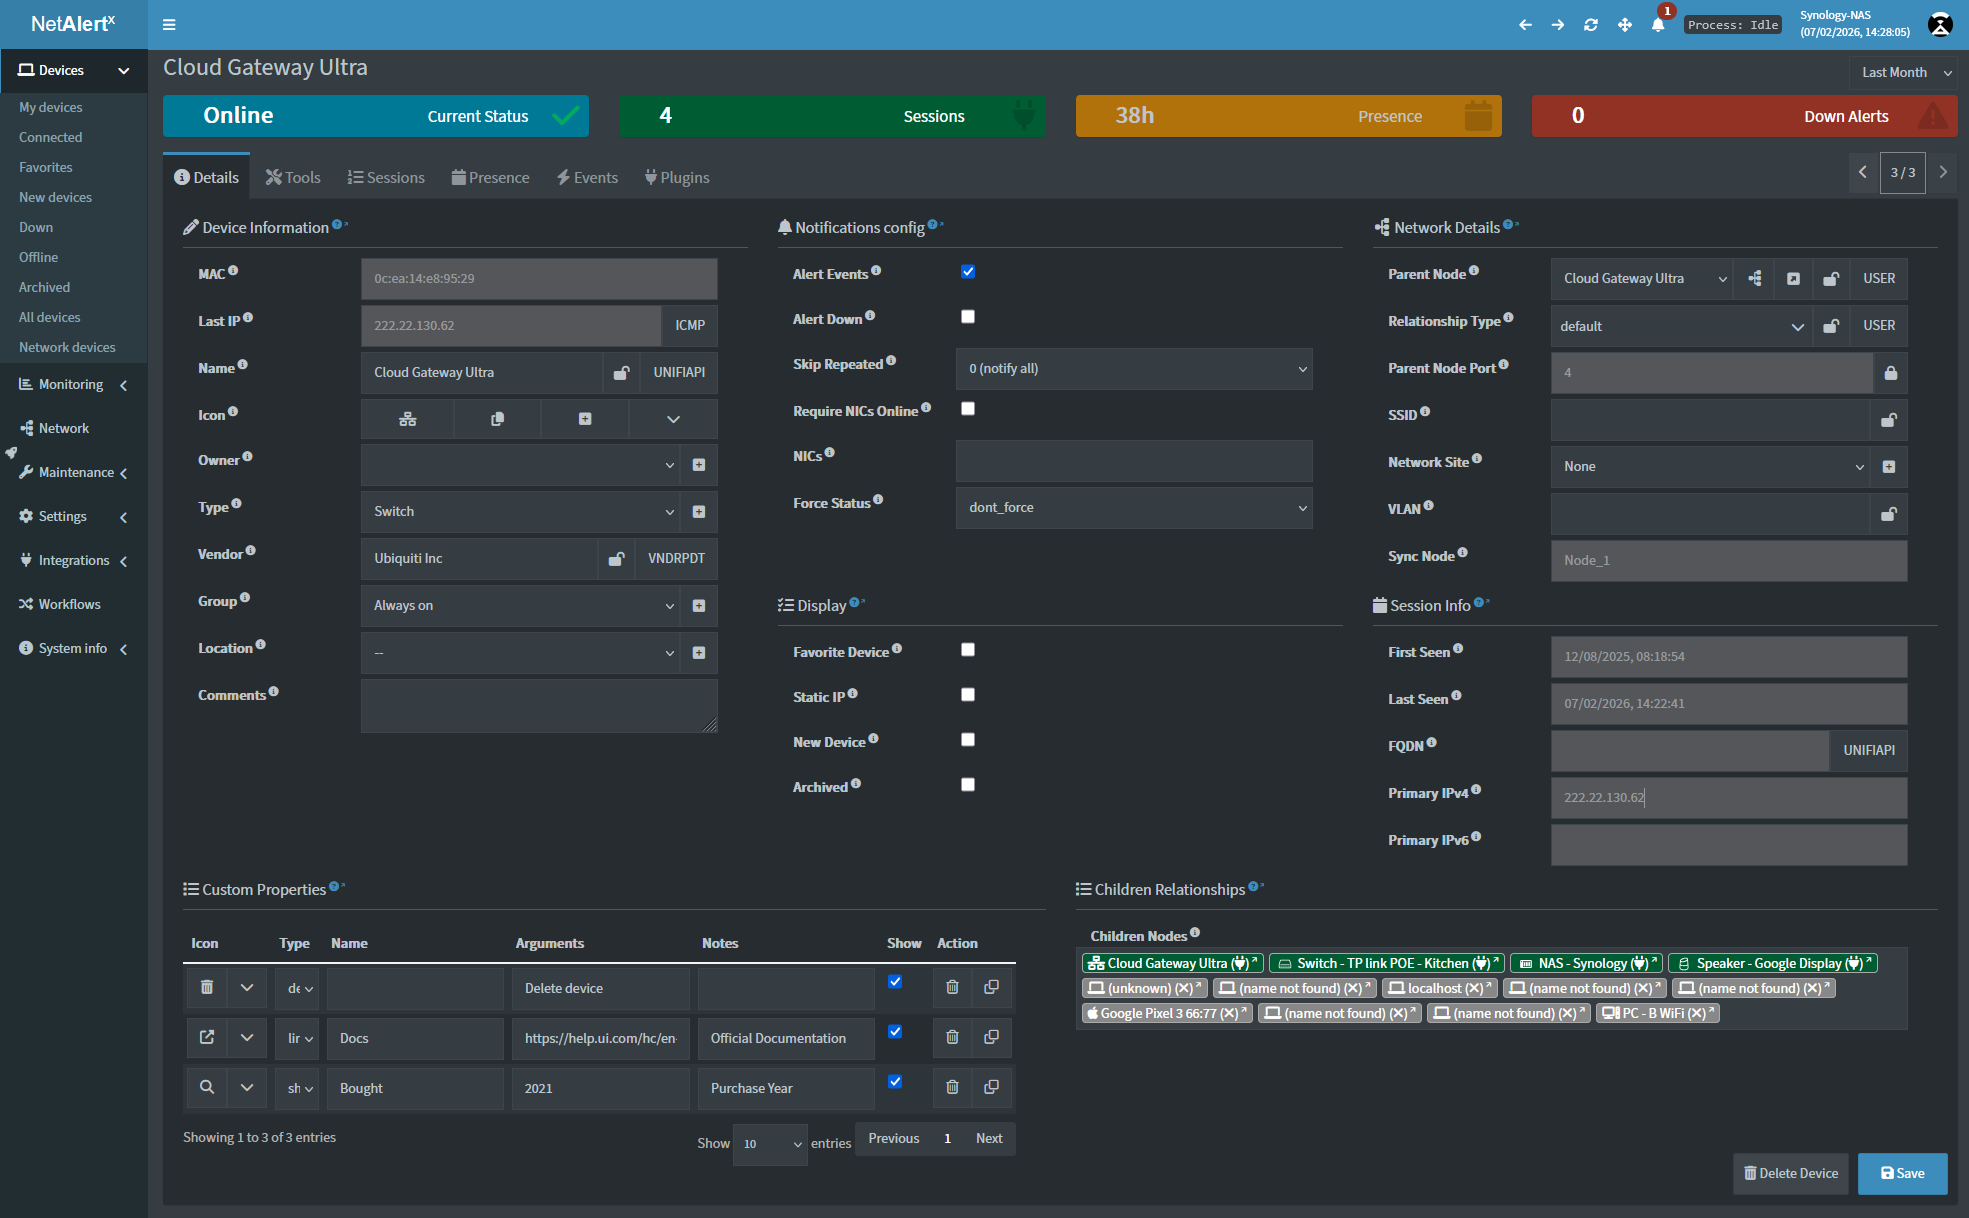 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 ntop/pf_ring
High-speed packet processing framework
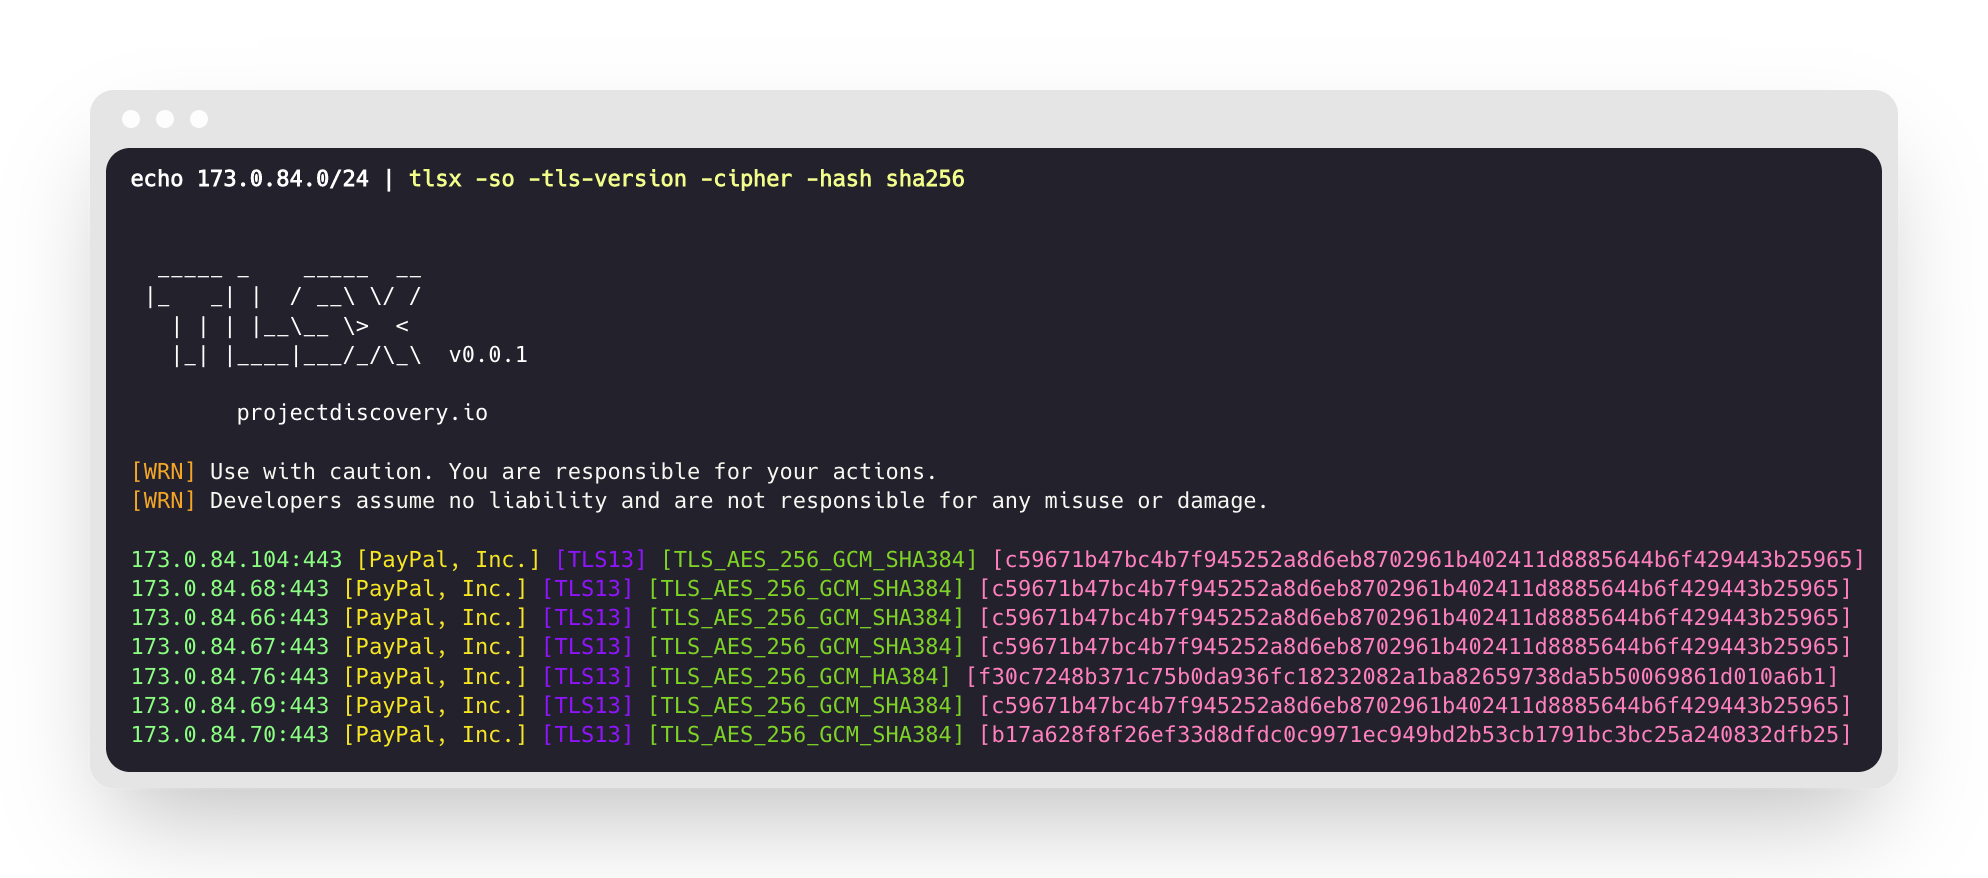 projectdiscovery/tlsx
Fast and configurable TLS grabber focused on TLS based data collection.
 aix567/c-a-s
C.A.S-Exploit — Python-based security research and proof-of-concept toolkit for CVE-2017-5689 (Intel AMT authentication bypass), featuring Shodan…
 ullaakut/nmap
Idiomatic Go library for invoking a network scanner binary, enabling host discovery, port scanning, service/OS detection, and scripted vulnerability…
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…
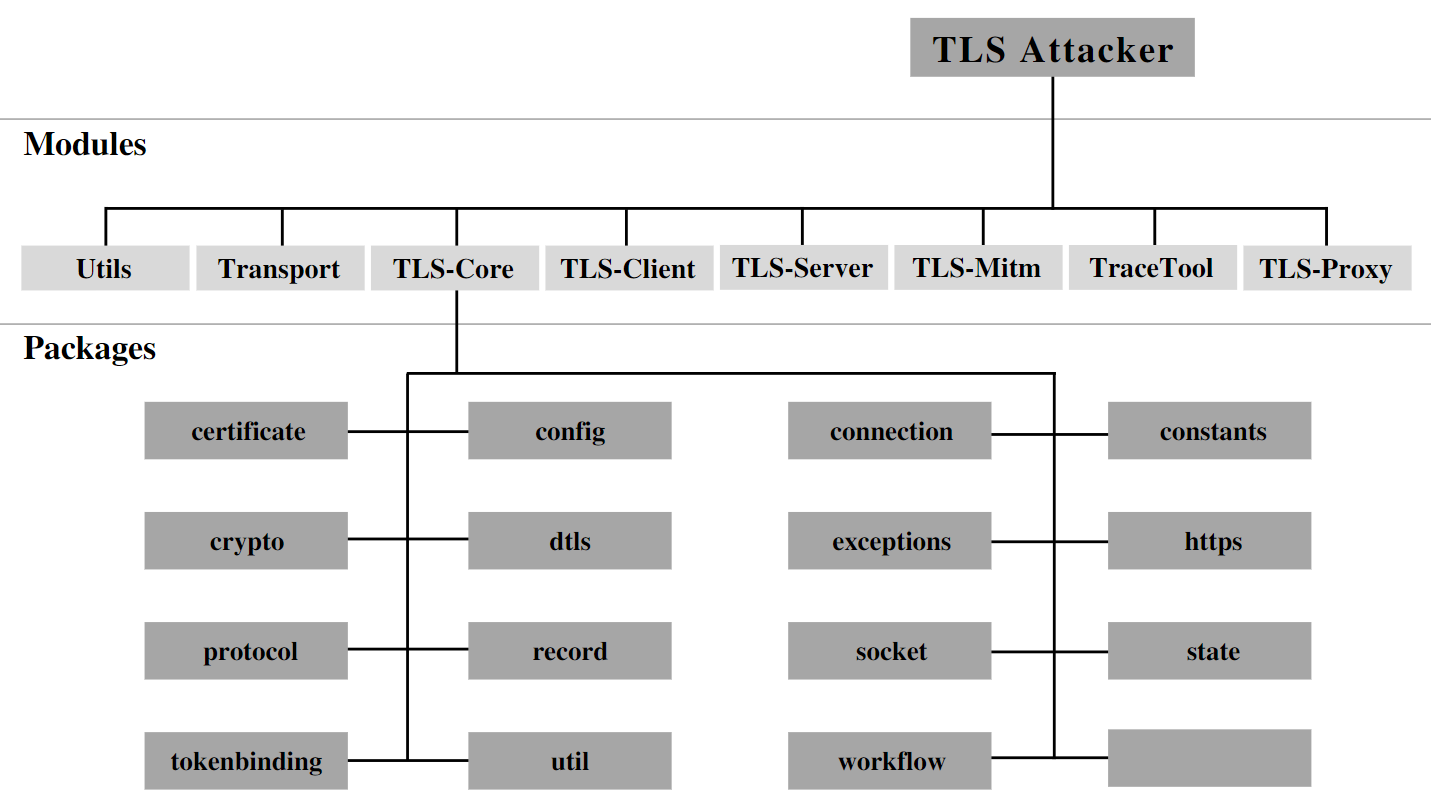 tls-attacker/tls-attacker
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
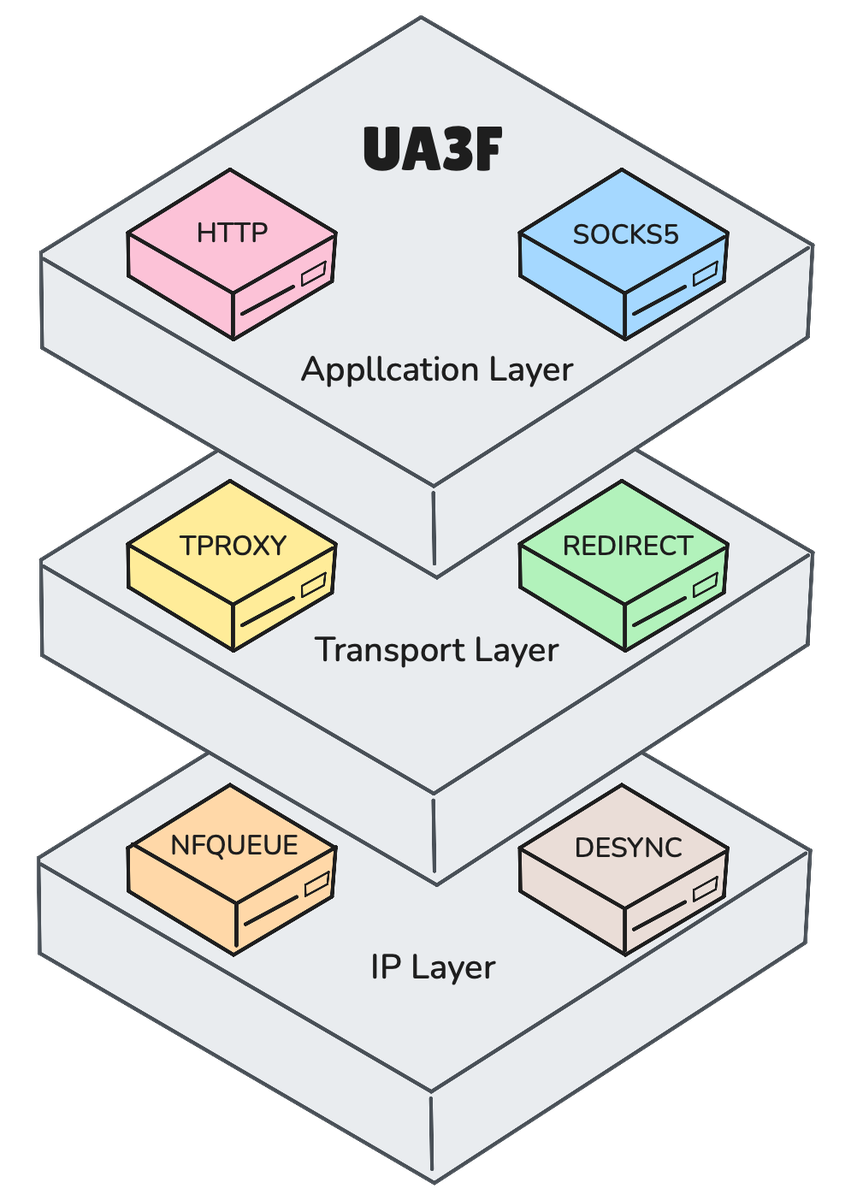 sunbk201/ua3f
Transparent HTTP(S) rewriting proxy supporting HTTP, SOCKS5, TPROXY, REDIRECT and NFQUEUE modes with HTTPS MitM, rule-based header/body rewriting and…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 m0vi0/pacmap
Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
 hunt-benito/the-same-key-opens-every-box-cve-2026-71960-hard-coded-jwt-secret-in-cudy-wr3000-mesh-mqtt
PoC toolkit that unpacks router firmware, decrypts device secrets, forges JWT tokens, and exploits CVE-2026-71960/71961 to take over Cudy WR3000 mesh…