
Docker IPsec VPN Server
 hwdsl2/docker-ipsec-vpn-server
Docker-based IPsec VPN server supporting IPsec/L2TP, Cisco IPsec, and IKEv2 with automatic credential generation and multi-platform client…
encryption-decryption-toolsnetwork-security
hwdsl2/docker-ipsec-vpn-serverDocker-based IPsec VPN server supporting IPsec/L2TP, Cisco IPsec, and IKEv2 with automatic credential generation and multi-platform client…

 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 objective-see/lulu
Open-source macOS firewall that monitors and controls network connections, blocking unauthorized outbound and inbound traffic with per-application…
 al7araziruby-jpg/cve-2024-6387-openssh-analysis
Security analysis and report of CVE-2024-6387 OpenSSH vulnerability, including vulnerability details, CVSS evaluation, and mitigation recommendations.
 mda1r/cve-2026-31278
CVE write-up for Active Directory credential exposure vulnerability in Suprema BioStar 2
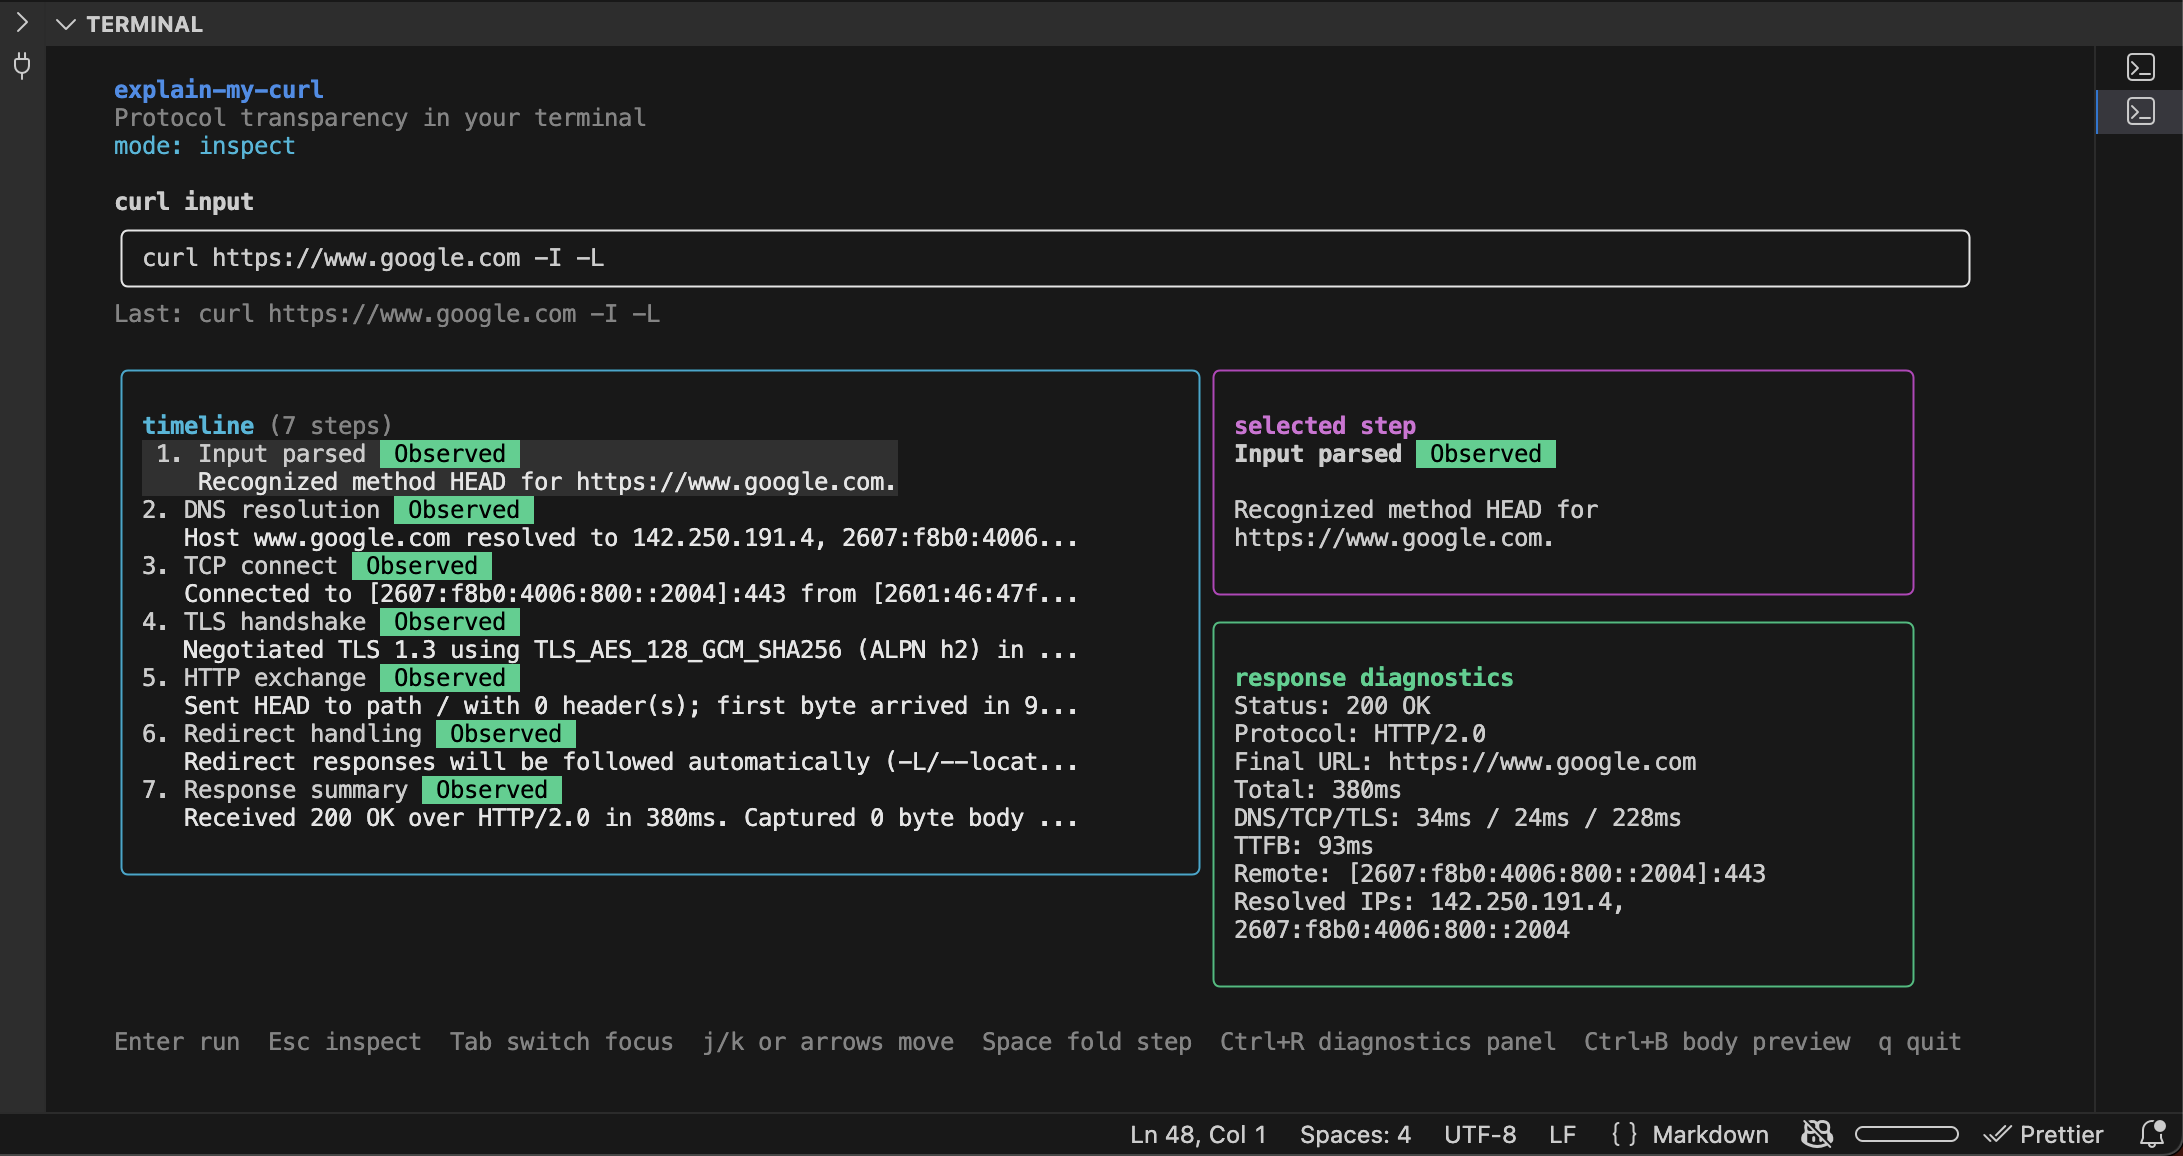 akgitrepos/explain-my-curl
Takes a curl command and explains DNS/TLS/HTTP details step-by-step
 buzz075/cve-2026-24061
Deep technical analysis and scanner for CVE-2026-24061, a critical authentication bypass in GNU InetUtils telnetd, including exploit chain, PoC, and…
 mkultra6969/anysniff
AnySniff is a tool for monitoring TCP connections of processes like AnyDesk on Windows. It uses the CVE-2024-52940 vulnerability to track open…
 ebrasha/abdal-anydesk-remote-ip-detector
CVE-2024-52940 - A zero-day vulnerability in AnyDesk's "Allow Direct Connections" feature, discovered and registered by Ebrahim Shafiei (EbraSha),…
 redteampentesting/watchguard-sso-client
Client Implementation for the WatchGuard SSO Agent Protocol used for Security Research (CVE-2024-6592, CVE-2024-6593, CVE-2024-6594)
 password123456/ssl-certificate-expiry-date-checker
Scans SSL/TLS certificates for expiry dates, issuer details, and OCSP status. Sends notifications via webhook, Telegram, or Slack. Supports proxy per…
 ruppde/scan_cve-2020-29583
Scanner for Zyxel products which are potentially vulnerable due to an undocumented user account (CVE-2020-29583)
 xdldcg/bash-tls-reneg-attack
A bash script that attempts to flood a server with TLS renegotiations by using the openssl client. See CVE-2011-1473 and CVE-2011-1473 for details.