oxo
 ostorlab/oxo
Modular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
devsecopsmobile-securitynetwork-security+3
5804h 21m ago
ostorlab/oxoModular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 ssc-ict-innovatie/nl-kat-coordination
Modular network scanning framework that integrates diverse tools and external databases to detect vulnerabilities and configuration errors, producing…
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
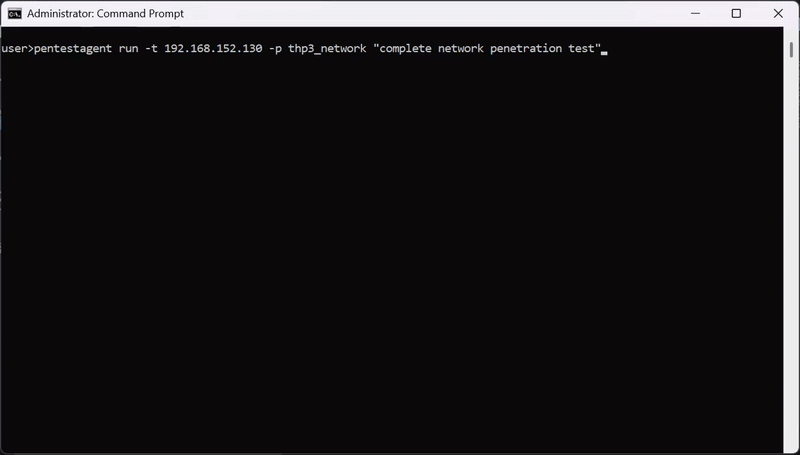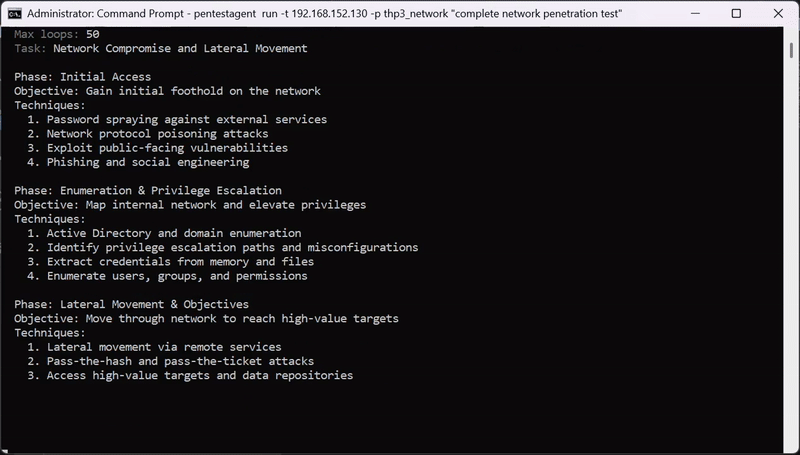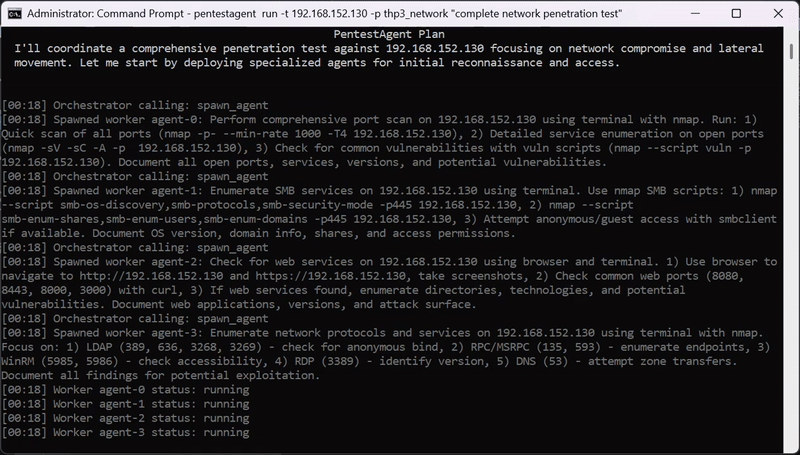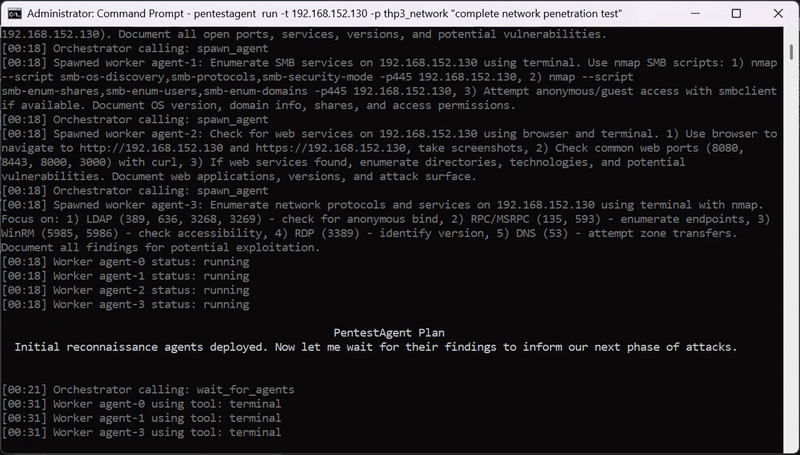 gh05tcrew/pentestagent
AI agent framework for black-box security testing with autonomous multi-agent orchestration, built-in pentesting tools, and MCP integration for bug…
 ull0a/cve-2026-50751
Bypass de autenticación por certificado en la VPN Remote-Access de Check Point (IKEv1).
 e4zyy/project-cve-2026-50751
IKEv1 VPN scanners, attempts a Check Point authentication-bypass exploit, and includes internal network scanning and reverse-shell features.
 mahmoud-sadder/airstrike
AirStrike is an advanced wireless security assessment framework designed to simplify and enhance Wi-Fi penetration testing through an integrated,…
 0xjessie21/wp2shell-checker
WordPress Core Unauthenticated RCE (CVE-2026-63030, CVE-2026-60137)
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 codextf2/openmalleablec2
Open Source Implementation of Cobalt Strike's Malleable C2
 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
 azhariramadhan/cve-2026-39047
Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…
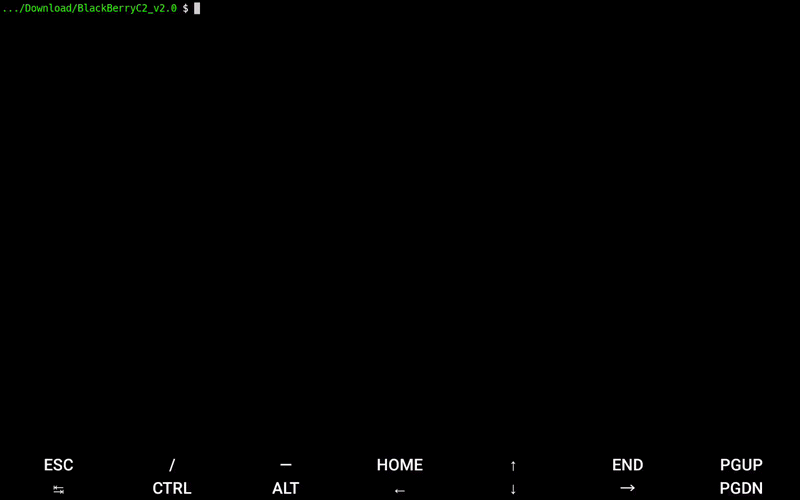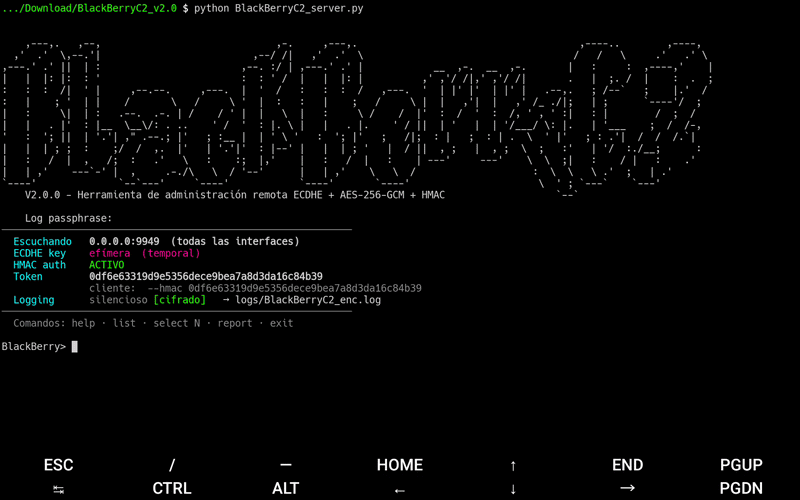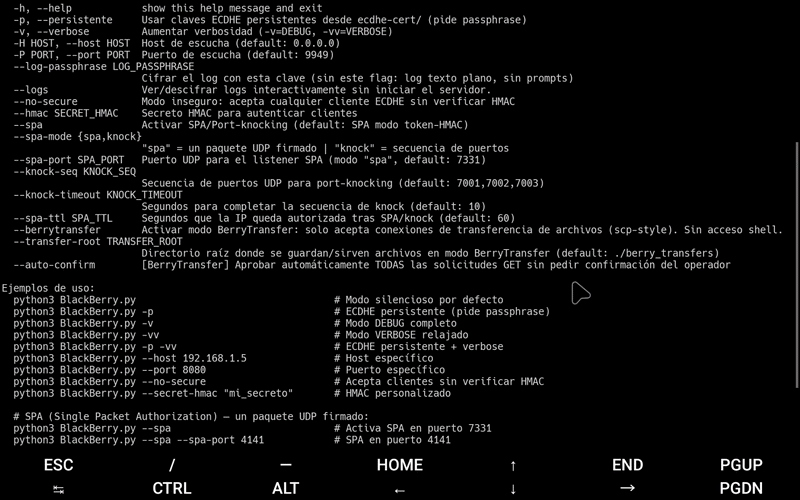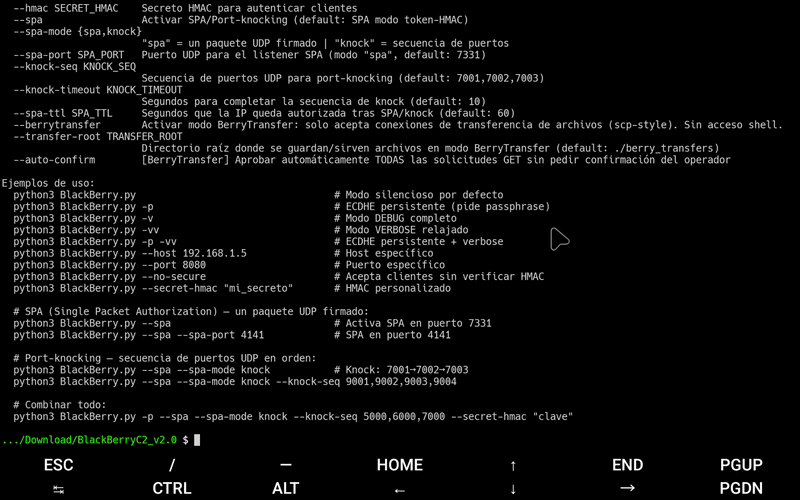 dereeqw/blackberryc2
Encrypted command‑and‑control (C2) research framework for cybersecurity education, red team labs, and secure client‑server communication experiments.