
CVE-2024-38063
 avidanmaatuk/cve-2024-38063
Educational proof-of-concept for CVE-2024-38063, a critical Windows IPv6 RCE, with technical analysis, Scapy-based crash trigger, and lab setup for…
binary-exploitationeducationexploitation+3
2
avidanmaatuk/cve-2024-38063Educational proof-of-concept for CVE-2024-38063, a critical Windows IPv6 RCE, with technical analysis, Scapy-based crash trigger, and lab setup for…
 al7araziruby-jpg/cve-2024-6387-openssh-analysis
Security analysis and report of CVE-2024-6387 OpenSSH vulnerability, including vulnerability details, CVSS evaluation, and mitigation recommendations.
 sxmpl3/cve-2024-21762-safe-check
Safe, non-intrusive scanner that detects FortiOS SSL VPN out-of-bounds write vulnerability (CVE-2024-21762) by comparing normal and chunked HTTP POST…
 oseasfr/scanner_cve_openssh
Scanner para identificação de servidores com softwares SSH possivelmente vulnerável às CVEs CVE-2024-6387 e CVE-2023-48795.
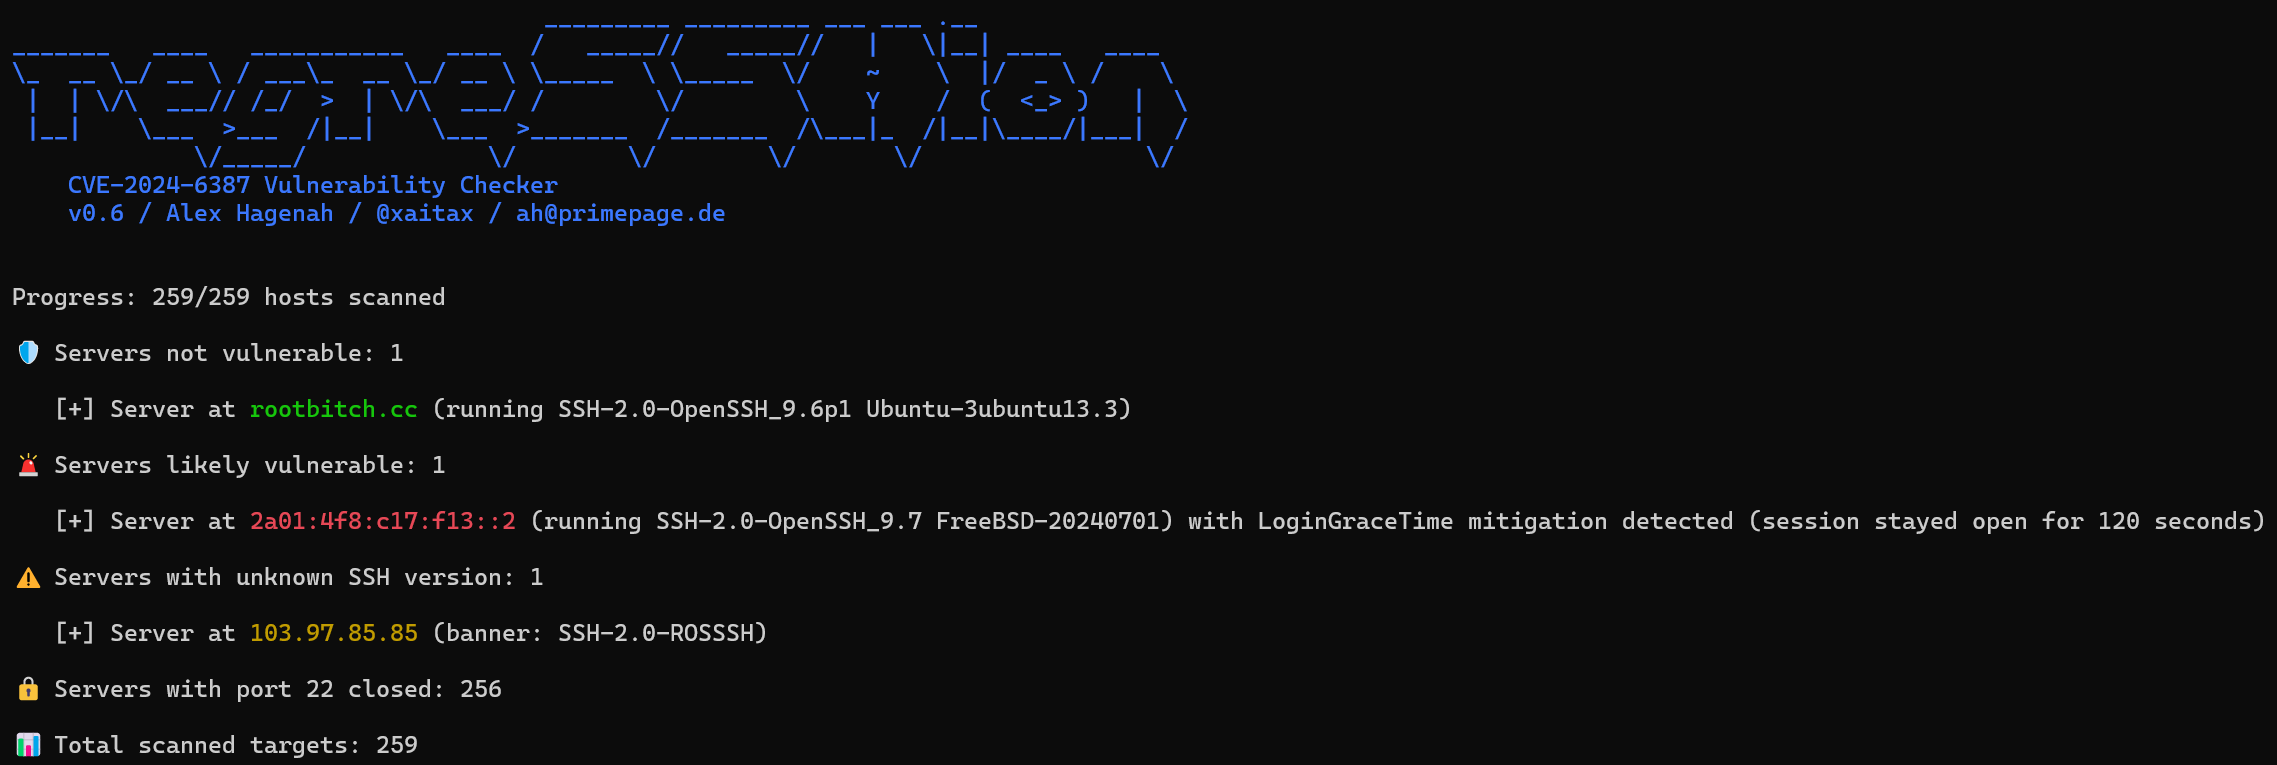 xaitax/cve-2024-6387_check
CVE-2024-6387_Check is a lightweight, efficient tool designed to identify servers running vulnerable versions of OpenSSH
 minhpham123456789/poc-cve-2024-23113
A proof of concept for CVE 2024 23113 inspired by WatchTowr's article.
 jimi2x/dirtycups
UDP-based scanner for CVE-2024-47176 that validates CUPS vulnerability by creating a local socket listener and triggering target responses.
 rohitmalik7/cve-2024-38063-detection-mitigation-system
End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…
 nonosticisiguzo-command/nmap-scan-results
Found 200+ vulnerabilities on scanme.nmap.org including CVE-2023-38408 (9.8 critical)
 doux-x/cve-2024-6387-analysis
CVE-2024-6387 OpenSSH 信号竞争漏洞(regreSSHion)分析报告及检测脚本
 salma-essaoud/cve-cvss--cve-2024-38063-ipv6-tcp-ip-remote-code-execution-analysis
Technical analysis and PoC demonstration of CVE-2024-38063, an IPv6 TCP/IP remote code execution vulnerability in Windows, including root cause, lab…
 sallocinavalcante/lab-smb-responder-cve-2024-21413
Laboratorio criado para PenTest da Vuln CVE 2024-214113(MONIKER LINK).
 aytackalinci/cve-2024-47176
Vulnerability Scanner for CUPS: CVE-2024-47176
 themehackers/cve-2024-38063
CVE-2024-38063 is a critical security vulnerability in the Windows TCP/IP stack that allows for remote code execution (RCE)
 forceea001/cve-2024-40898-ssl-bypass-detection
This Python script is a Proof-of-Concept (PoC) scanner for detecting the vulnerability CVE-2024-40898, which affects Apache HTTP Server’s SSL…
 gpotter2/cve-2024-20674
Exploit for CVE-2024-20674: Kerberos mutual authentication bypass via logic bug in client-side U2U TGT-REP handling. Enables unauthenticated network…
 deauther890/cve-2024-54772
Python-based exploit for CVE-2024-54772 enabling username enumeration on MikroTik RouterOS versions v6.43 through v7.17.2 using wordlist or…
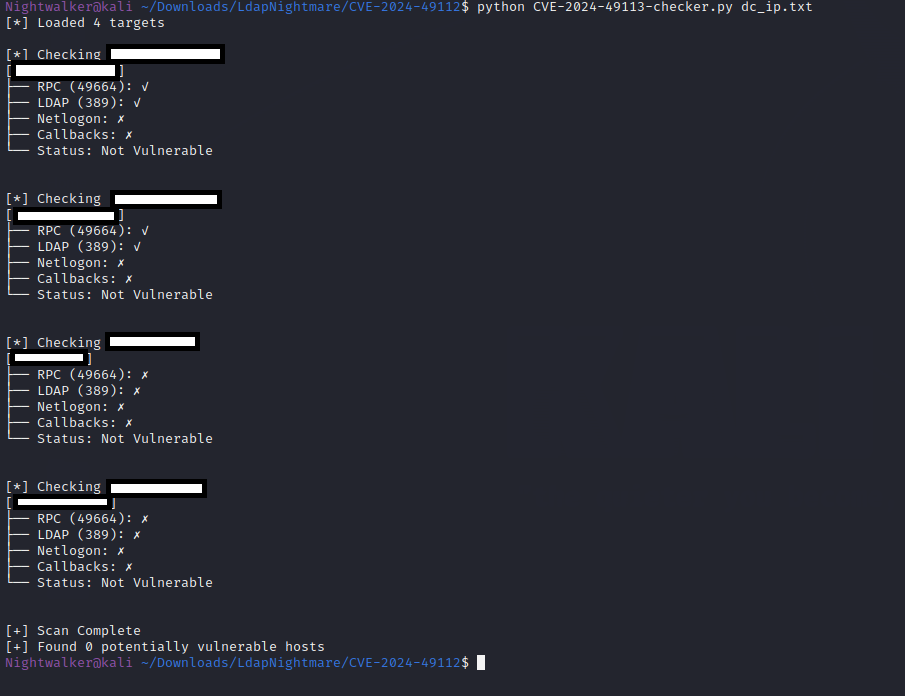 barcrange/cve-2024-49113-checker
Checks if a system is potentially vulnerable to CVE-2024-49113 (LDAP Nightmare) by testing RPC connectivity, LDAP ports, Netlogon service, and LDAP…