
tenzir
 tenzir/tenzir
Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…
incident-responselog-analysisnetwork-security+1
769
tenzir/tenzirCollect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
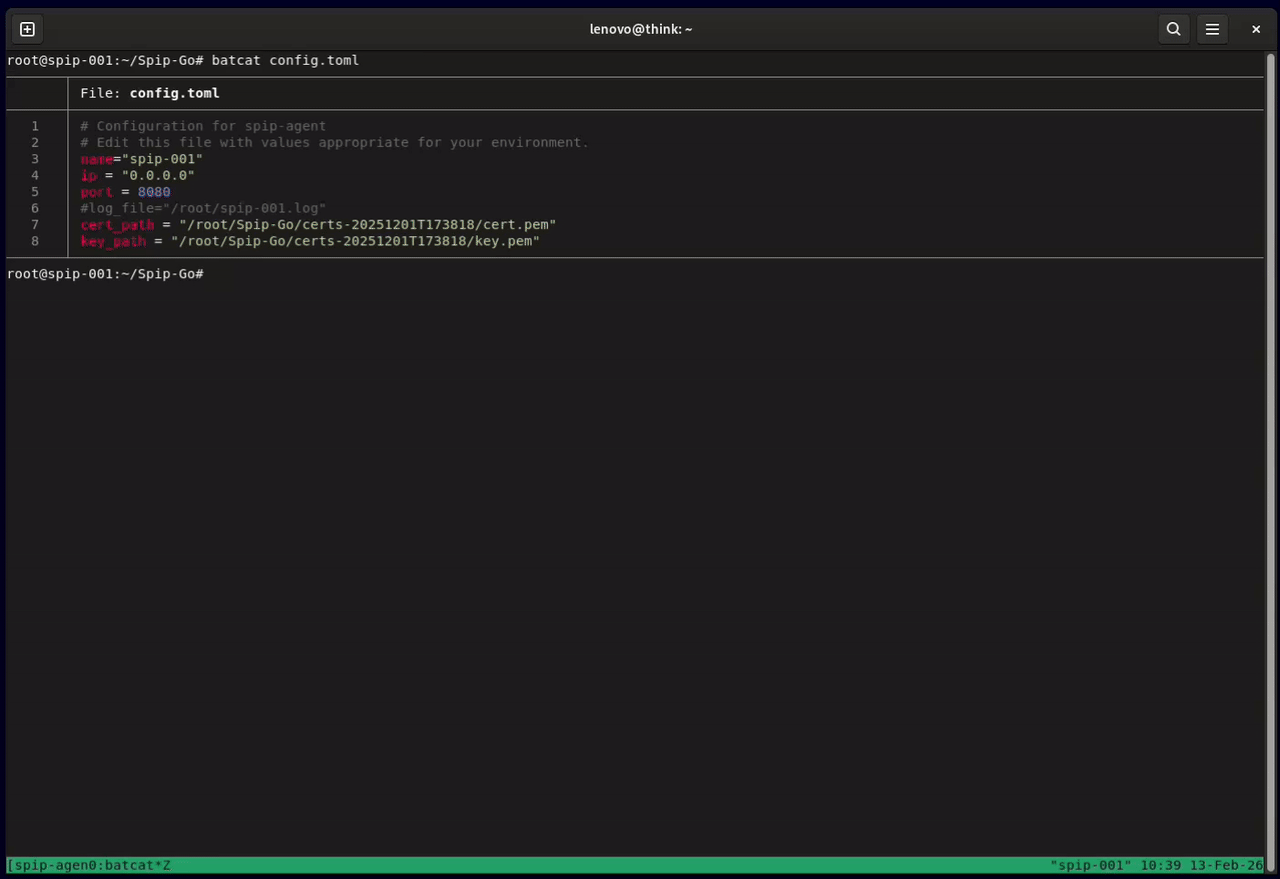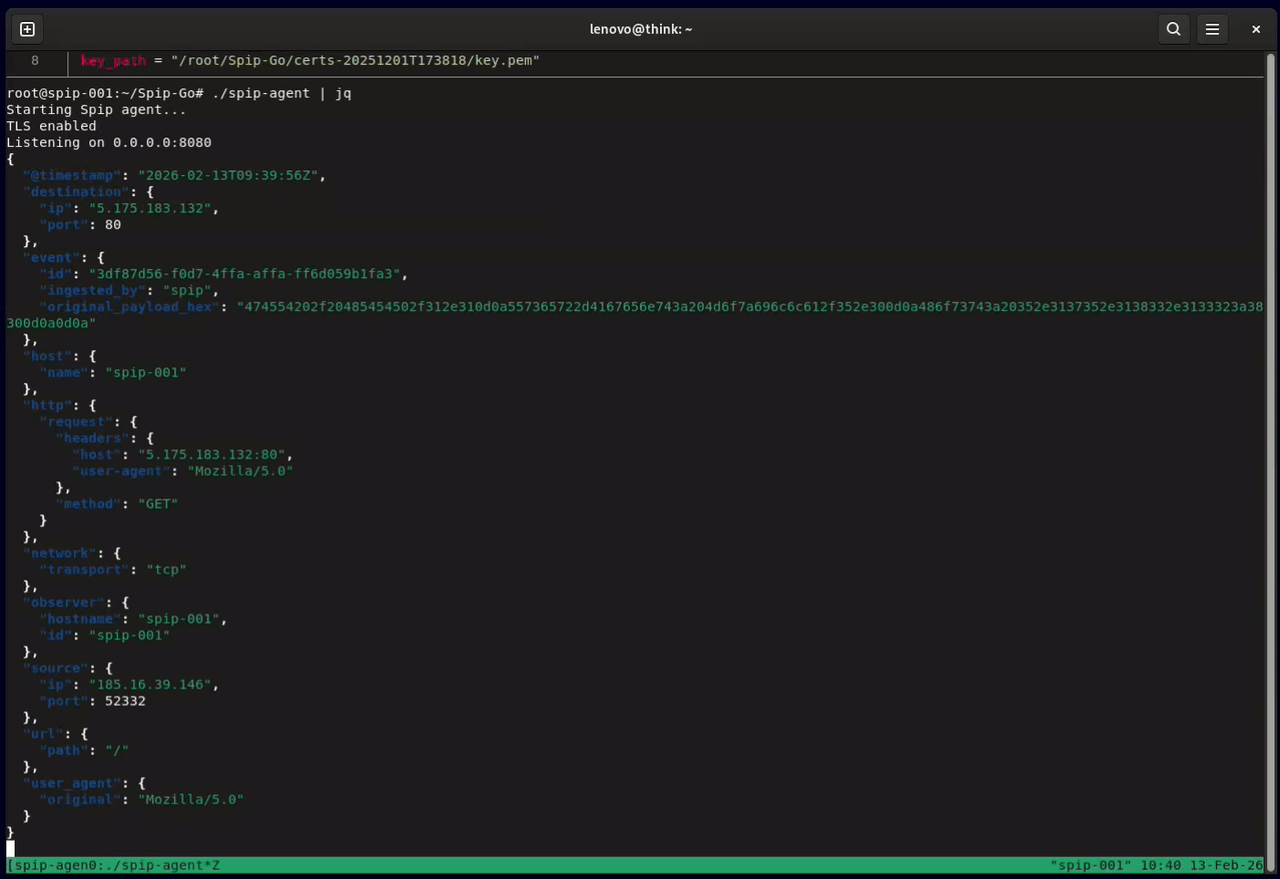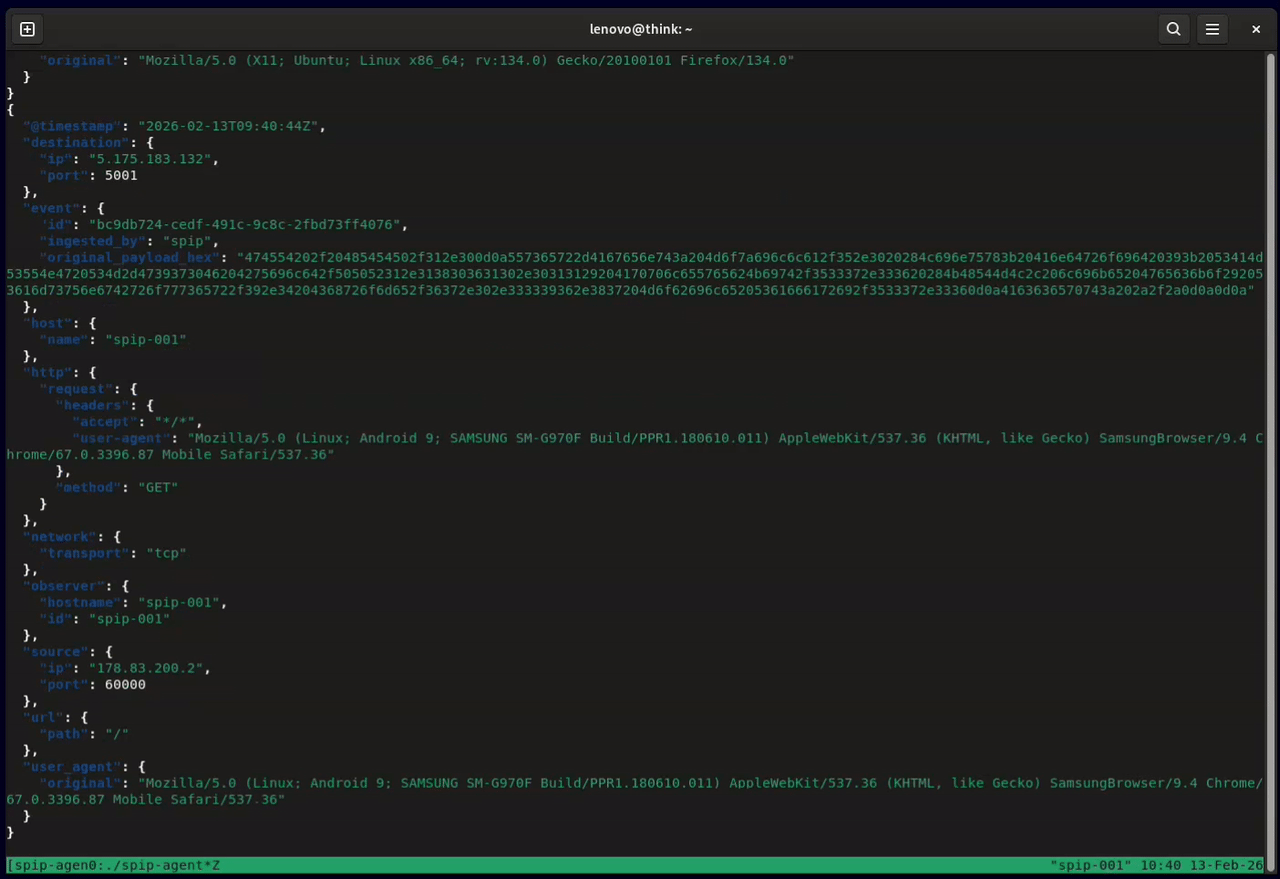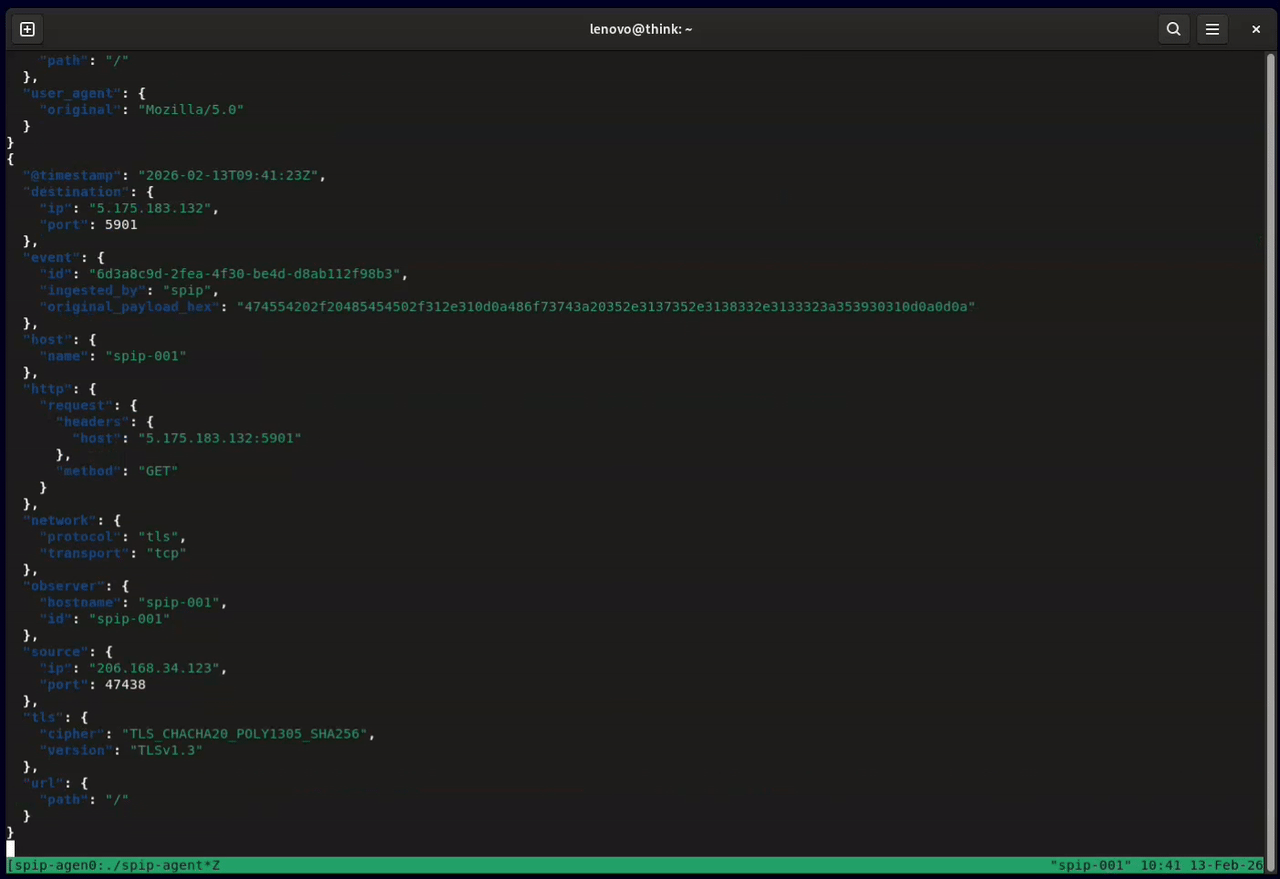 honeylabshq/spip-go
Spip network sensor written in Go
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
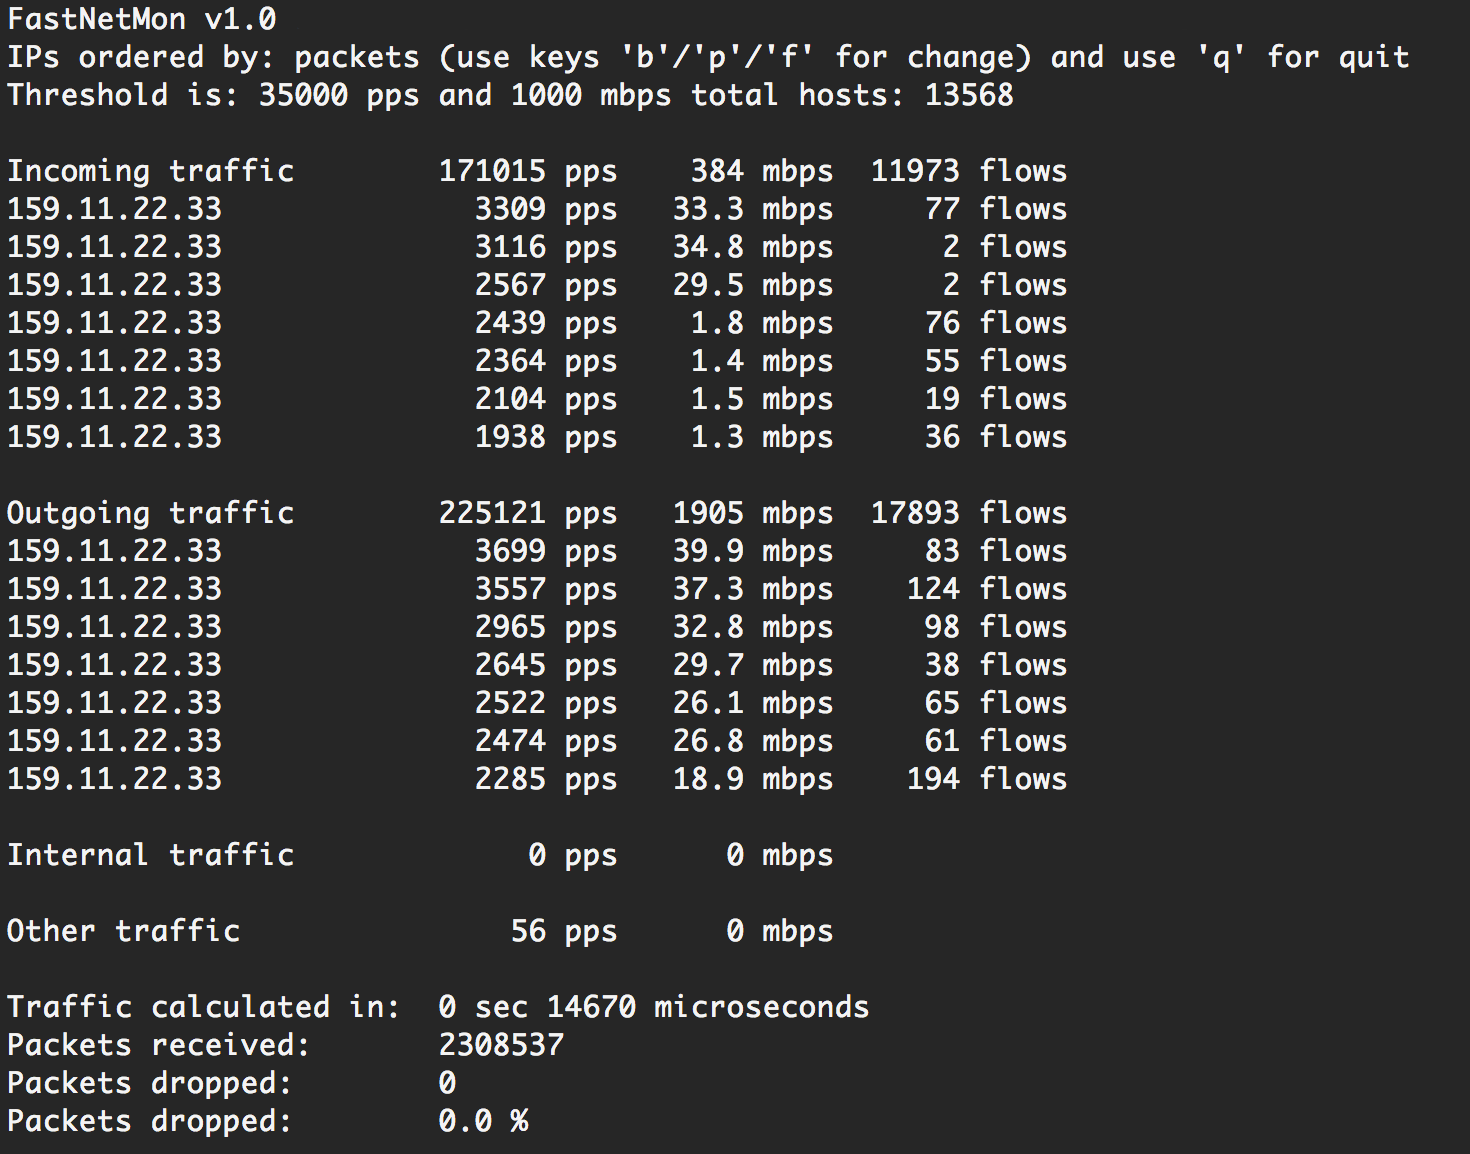 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 drb-ra/c2intelfeeds
Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…
 corelight/ecs-logstash-mappings
Mapping Corelight or Zeek data to Elastic Common Schema logs
 drduh/macos-security-and-privacy-guide
Curated macOS security and privacy guide with practical instructions for threat modeling, disk encryption, firewall configuration, secure…
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 0xajstrike/opcuatrap
High-interaction OPC UA honeypot for ICS/SCADA — multi-profile (oil & gas, water, power grid), live process simulation, per-session threat scoring,…
 gagaltotal/cve-2026-mikrotik-poc
MikroTik RouterOS PoC Collection - CVE-2026-86060 - CVE-2026-67279 - CVE-2026-67276 RouterOS SSH
 dshield-isc/dshield
Installs and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to…
 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
 fox-it/cisco-ios-xe-implant-detection
Cisco IOS XE implant scanning & detection (CVE-2023-20198, CVE-2023-20273)
 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…