

artillery
 trustedsec/artillery
Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
anomaly-detectiondefensive-toolshardware-iot-security+5
339
trustedsec/artilleryOpen-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
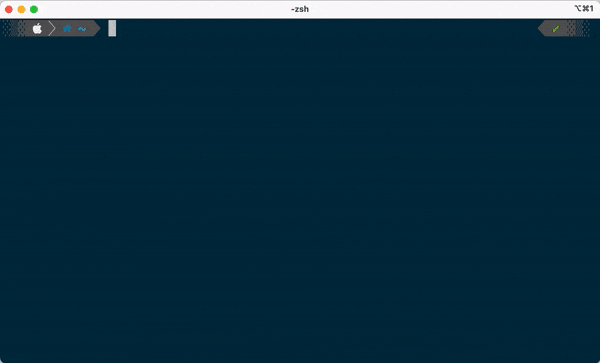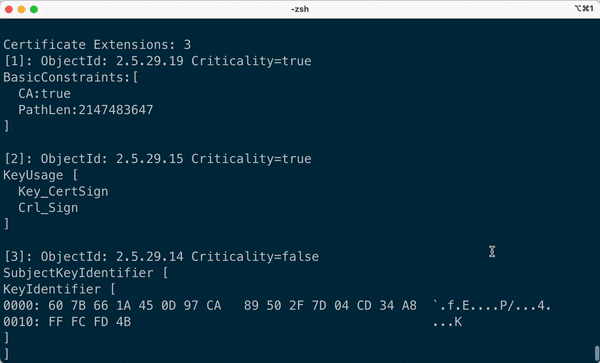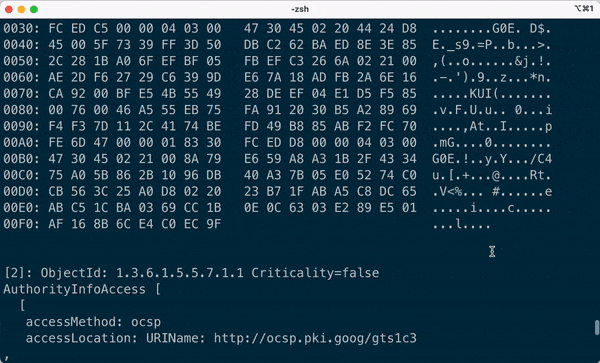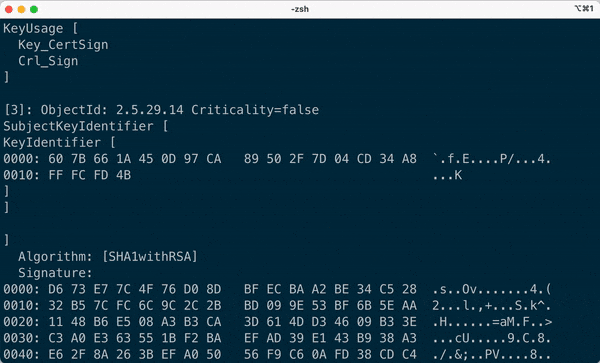 hakky54/certificate-ripper
🔐 A CLI tool to extract server certificates
 bojanisc/quicmap
quicmap is a simple yet quic (!) QUIC protocol scanner
 pghook/cve-2018-10933_scanner
Scans single or multiple IPs for libssh servers vulnerable to CVE-2018-10933, displaying geolocation of vulnerable hosts.
 musalbas/heartbleed-masstest
Multi-threaded tool for scanning many hosts for CVE-2014-0160.
 r4tw1z/cve-2024-6387
This script, created by R4Tw1z, is designed to scan IP addresses to check if they are running a potentially vulnerable version of OpenSSH. The tool…
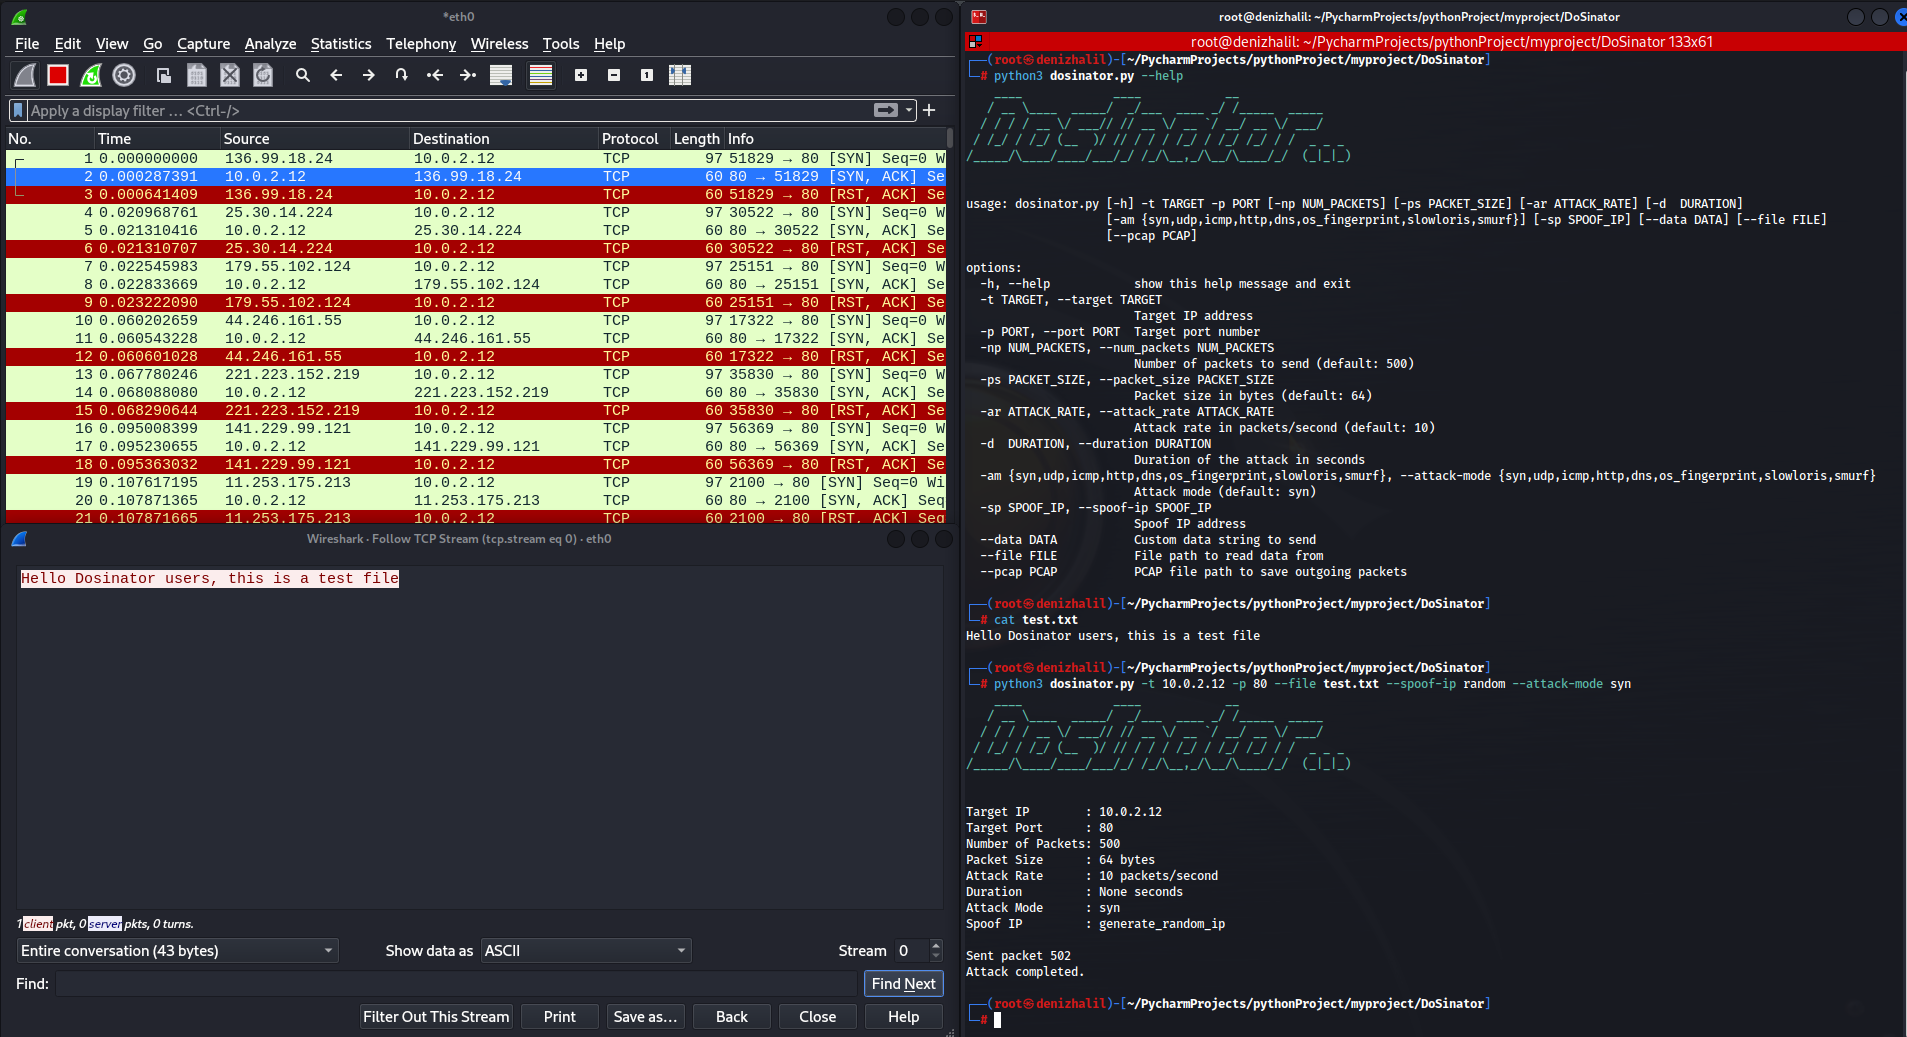 halildeniz/dosinator
DoSinator is a powerful Denial of Service (DoS) testing tool developed in Python.
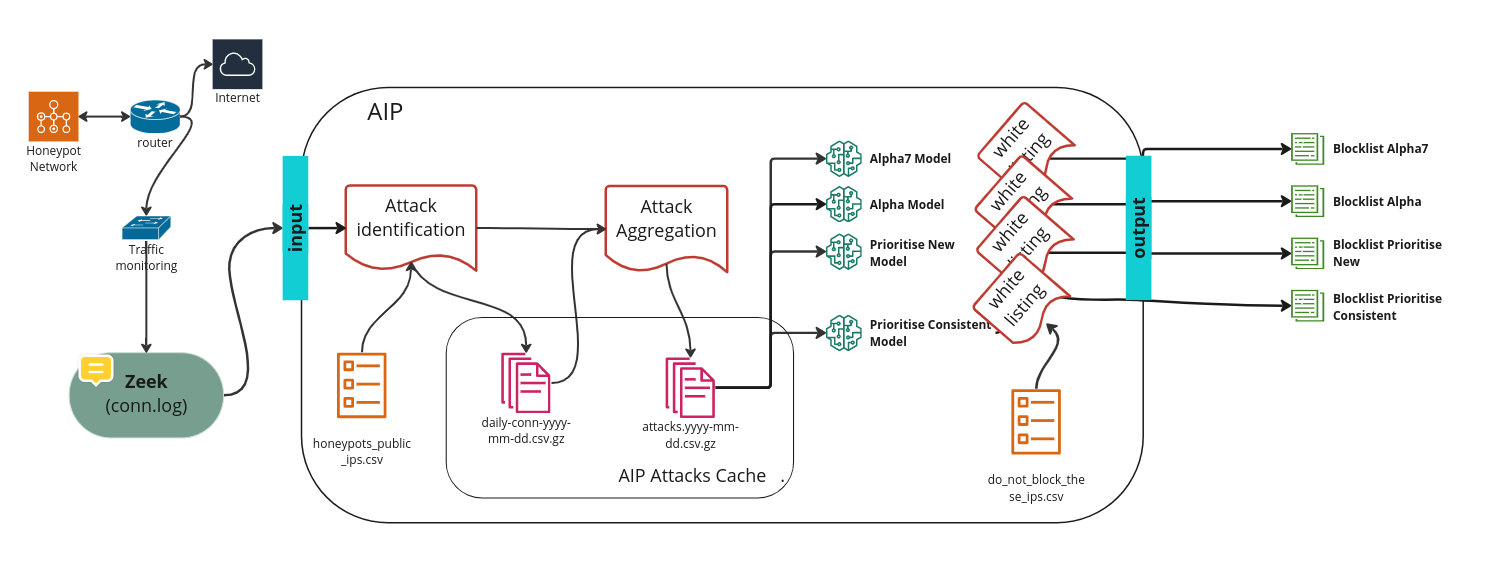 stratosphereips/aip
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…
 the-tcpdump-group/libpcap
System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
 identity-threat-labs/cve-2024-6387-vulnerability-checker
This Python script checks for the CVE-2024-6387 vulnerability in OpenSSH servers. It supports multiple IP addresses, URLs, CIDR ranges, and ports.…
 devarshishimpi/cve-2024-6387-check
Fast, efficient, and reliable detection for the regreSSHion exploit. Scan multiple targets in seconds with zero dependencies.
 karammahmad/cve-2021-40113
CVE documentation repository detailing unauthenticated remote vulnerabilities in Cisco Catalyst PON Series Switches ONT, including default credential…
 cybersecurityworks553/cve-2022-3602-and-cve-2022-3786
Python-based scanner that detects OpenSSL 3.0.0-3.0.6 servers vulnerable to CVE-2022-3602 and CVE-2022-3786 by checking client authentication…
 wiis0n/zerologon_cve-2020-1472
POC for checking multiple hosts for Zerologon vulnerability
 aytackalinci/cve-2024-47176
Vulnerability Scanner for CUPS: CVE-2024-47176
 sensepost/det
(extensible) Data Exfiltration Toolkit (DET)
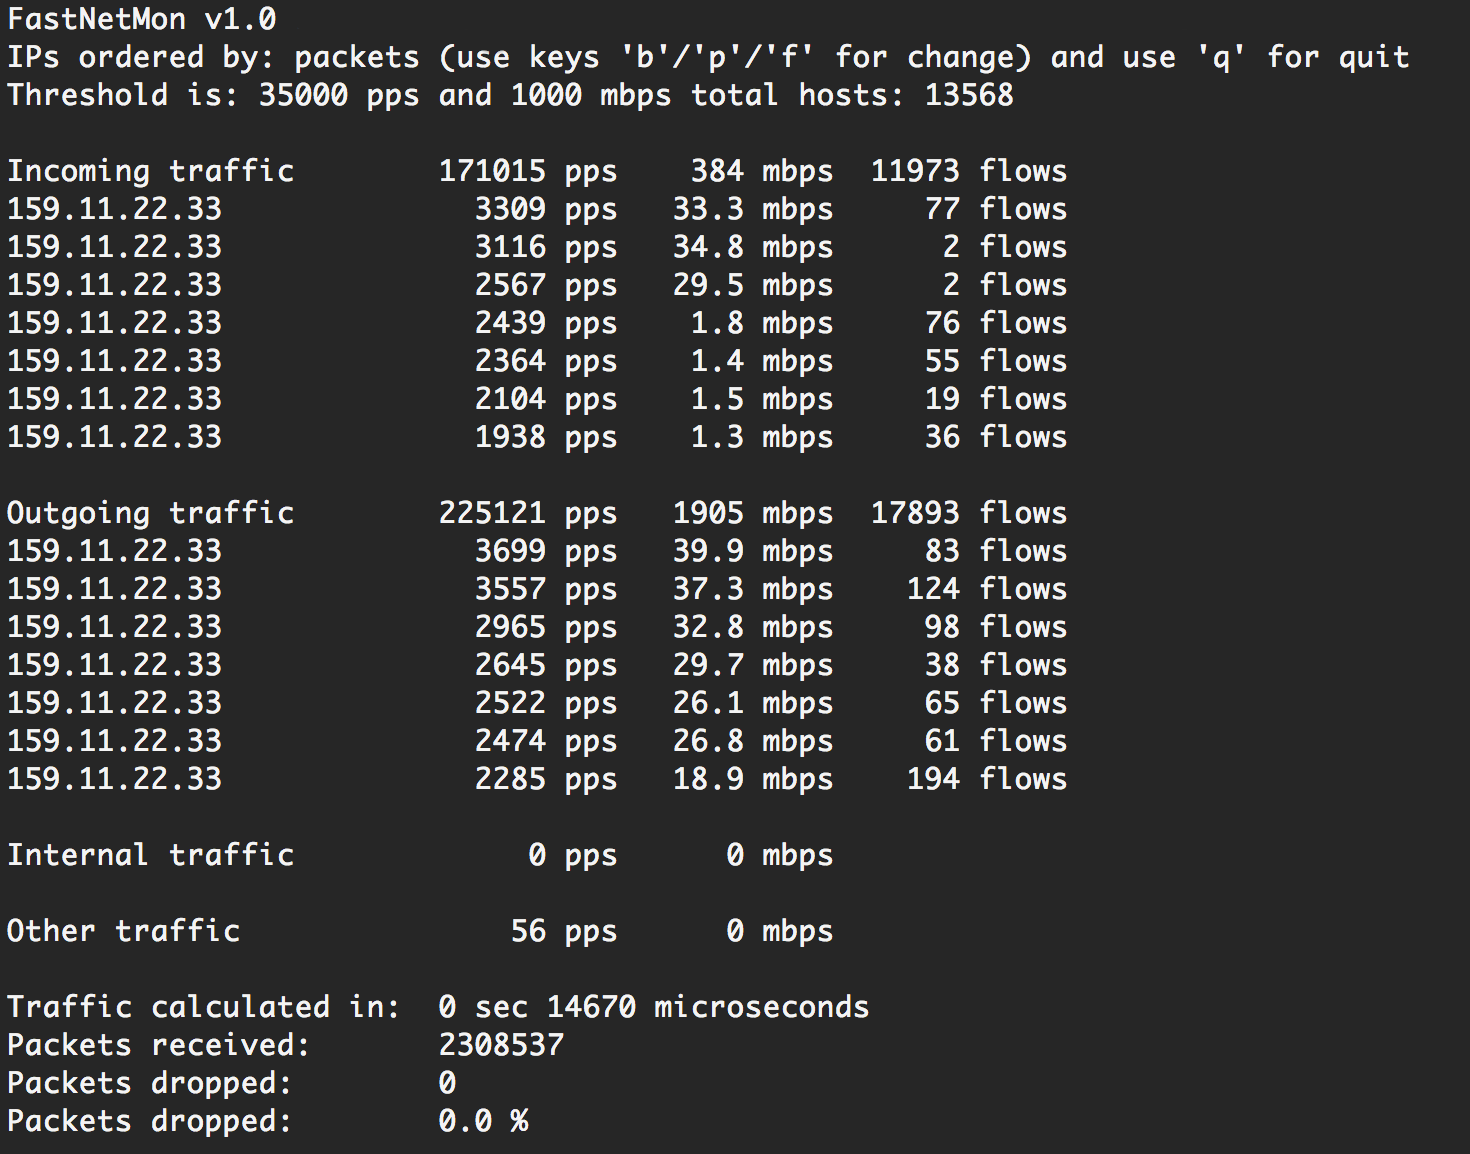 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support