
spookyssl-pcaps
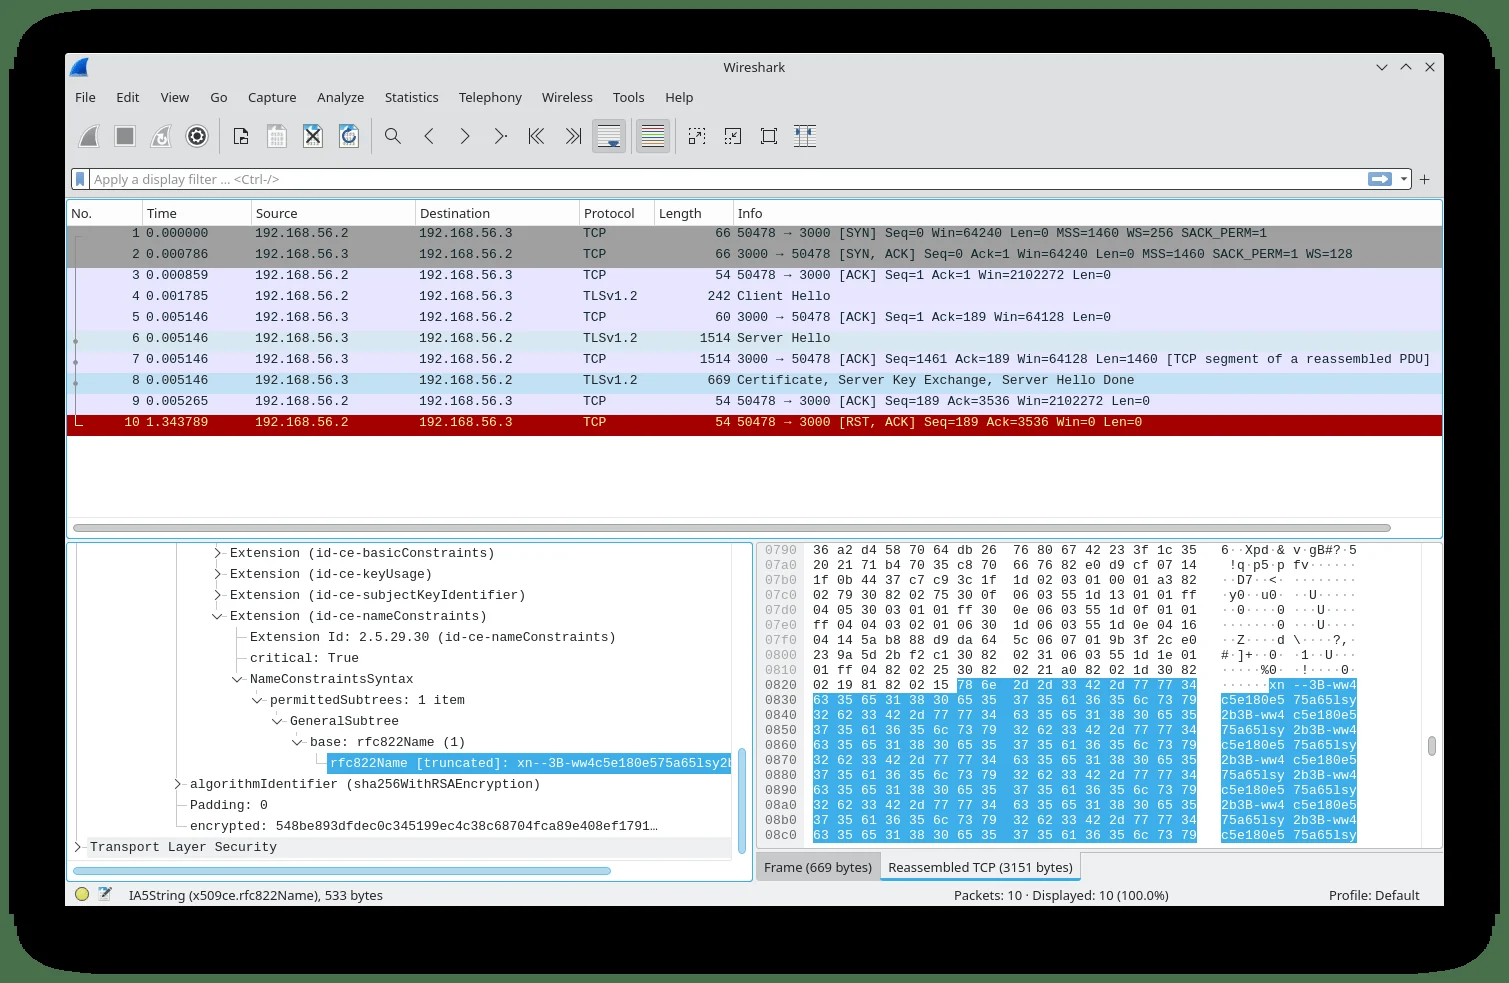
PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…

PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…

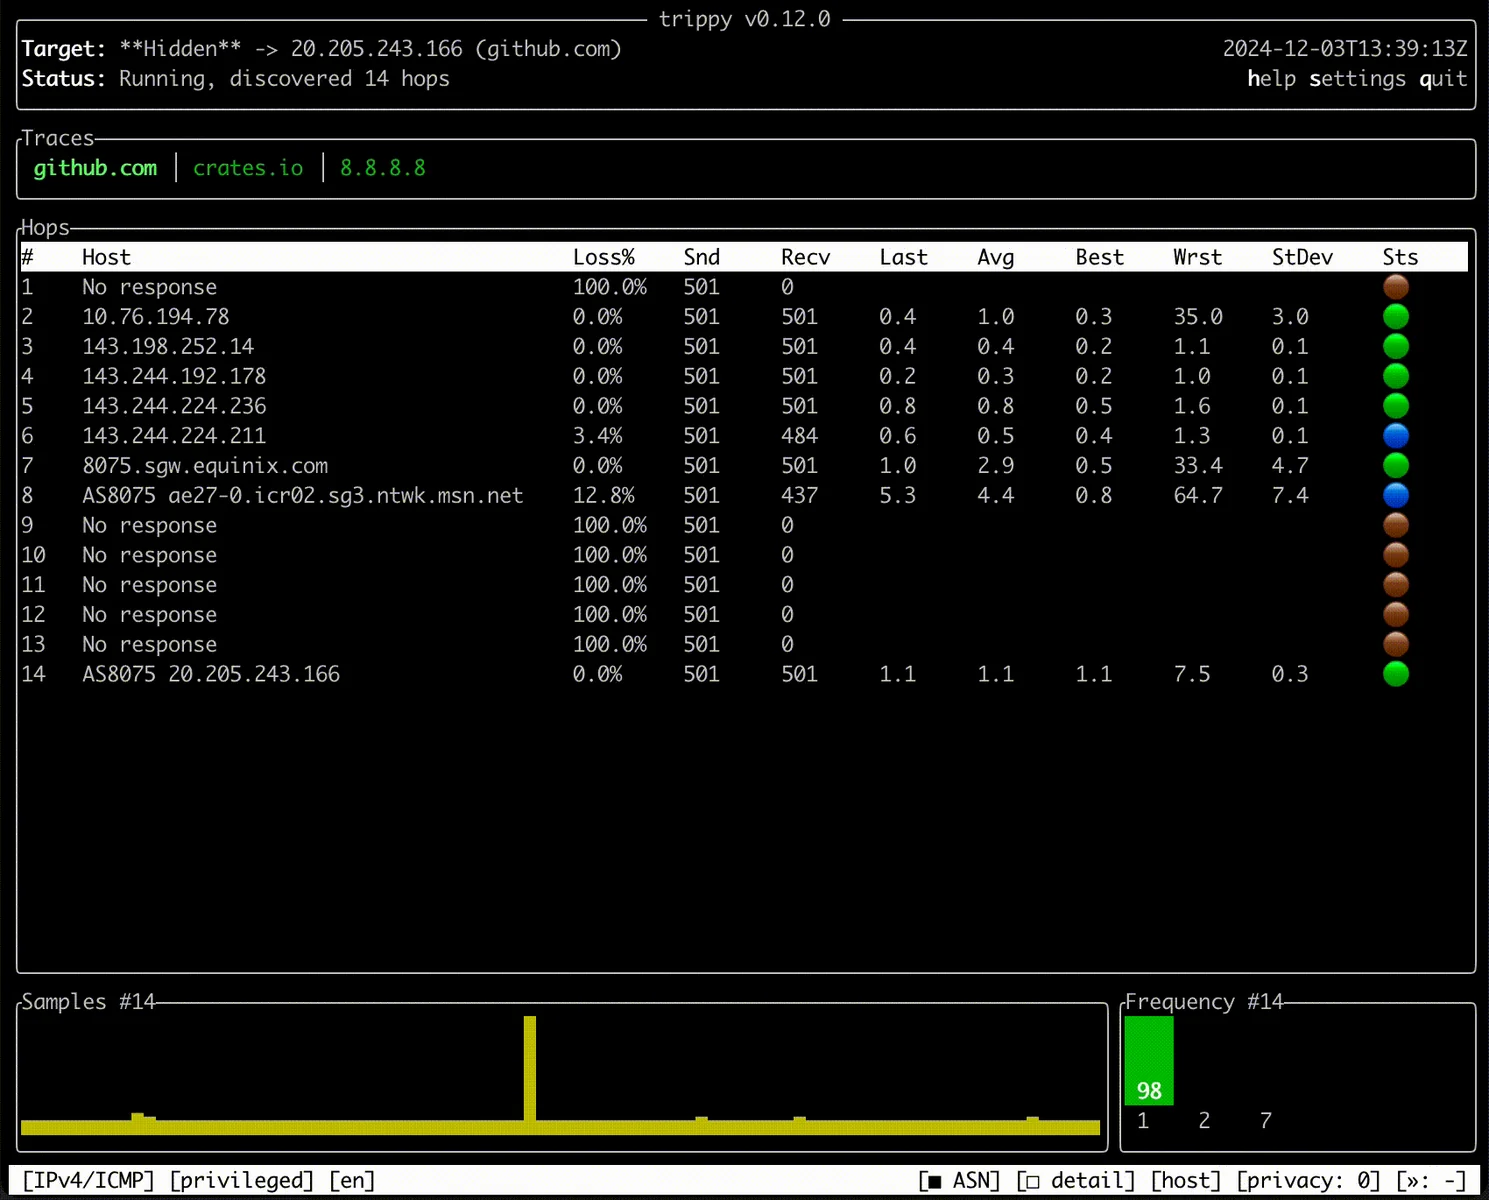
A network diagnostic tool combining traceroute and ping for analyzing network paths, latency, and packet loss with an interactive terminal UI.

Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)

Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…

Scans internet-exposed cPanel/WHM instances for CVE-2026-41940 authentication bypass, probing HTTPS on port 2087 and matching response markers to…

One zero-byte QUIC packet is enough to desynchronize HAProxy's backend connection pool and smuggle HTTP requests across unrelated users — even users…

Quick and Simple Scripts to Scan for Vulnerable Servers and Packet Level Monitors

Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…

Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…

Provides packet processing capabilities for Go

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…

Pre-auth PoC for CVE-2026-41089 Netlogon CLDAP stack overflow via UDP/389, triggering LSASS crash/DC reboot. Includes exploit script, root-cause…

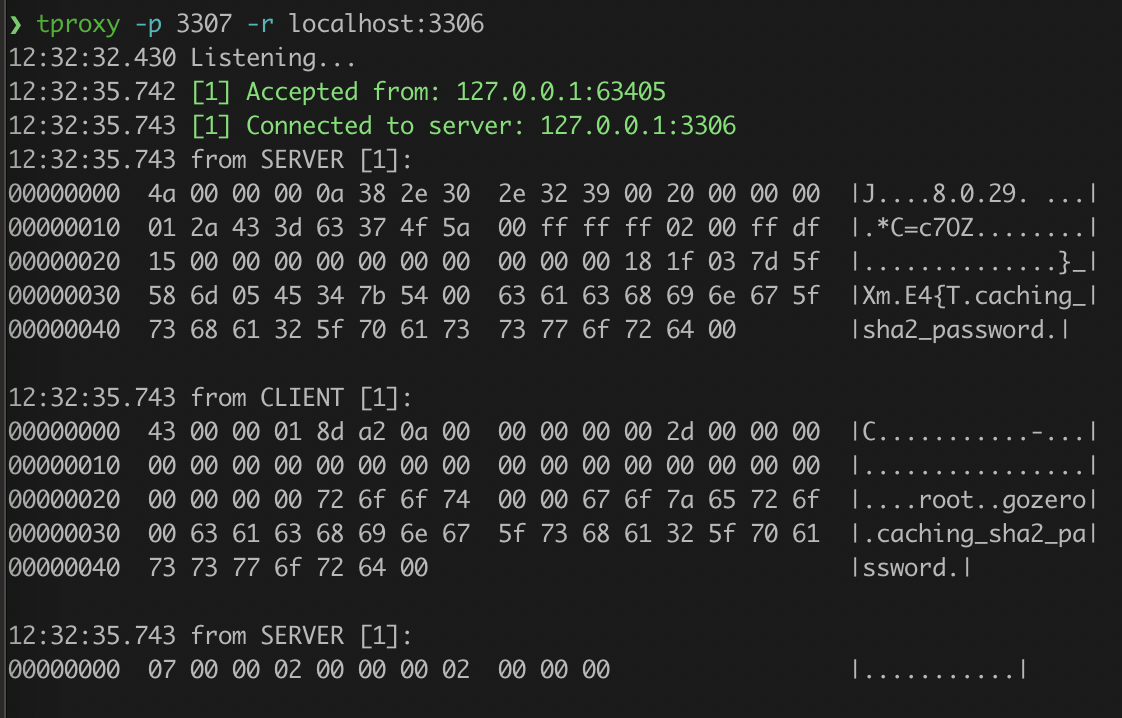
A cli tool to proxy and analyze TCP connections.


teamcity teamcity-CVE-2026-63077 exploitation pcap

Educational Python PoC for a QUIC address-validation bypass that triggers handshake amplification, including vulnerable server simulation and attack…

My Aircrack-ng contribution with Thomas d'Otreppe