
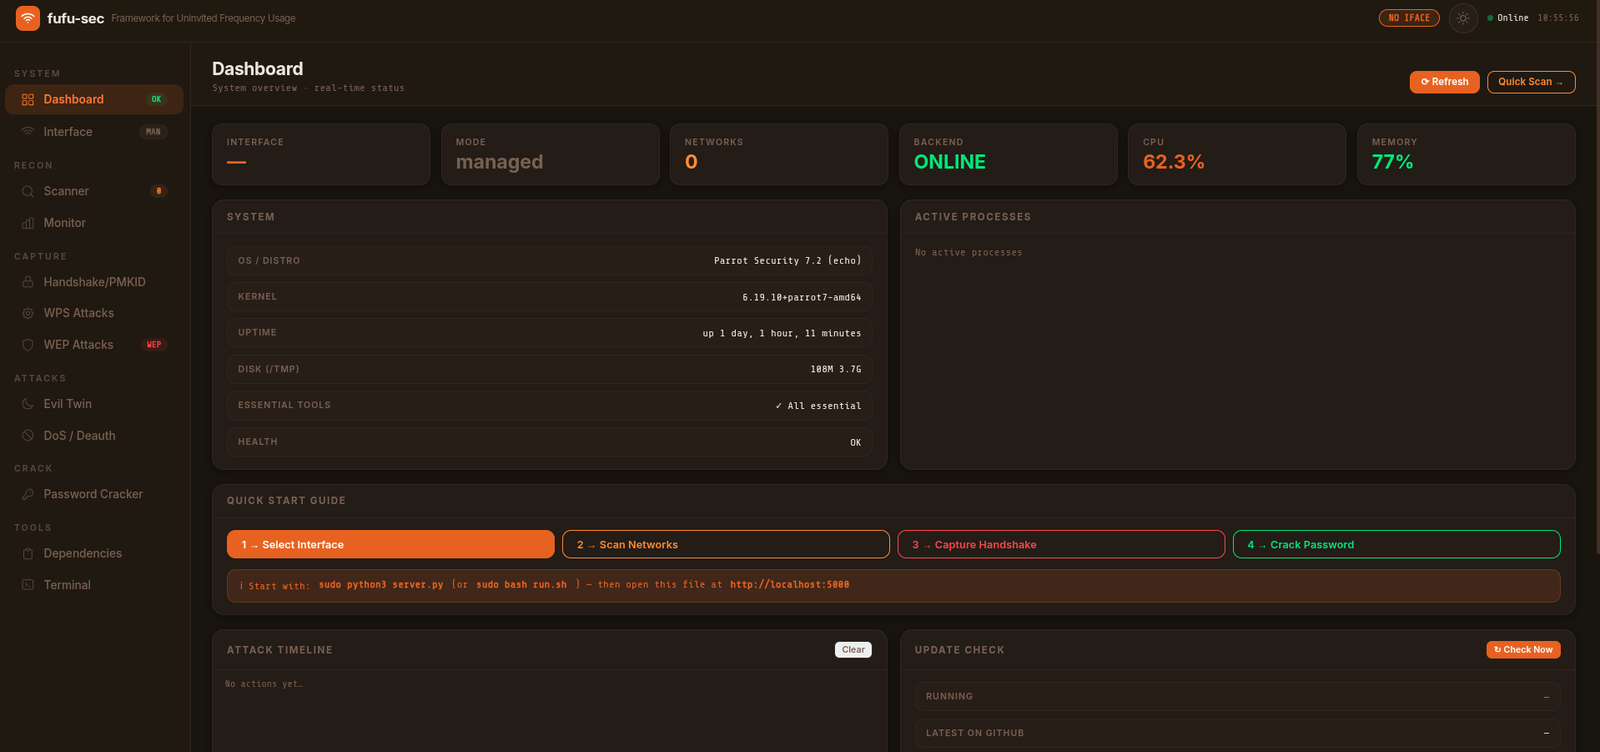
fufu-sec
 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
exploitationnetwork-securitypassword-attacks+4
kyllr-qwen/fufu-secFramework for Uninvited Frequency Usage
 toouch67/cve-2026-1459-poc
POC for the CVE-2026-1459 which payload changes root SSH password.
 manio/mtpass
MikroTik Password Recovery Tool
 nccgroup/cisco-snmp-enumeration
Automated Cisco SNMP Enumeration, Brute Force, Configuration Download and Password Cracking
 1n3/supermicro-password-scanner
Supermicro IPMI/BMC Cleartext Password Scanner
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 joeblacksecurity/sshusernamebruter-sshub
Fully functional script for brute forcing SSH and trying credentials - CVE-2018-15473
 sinichi449/python-mikrotikloginexploit
PoC of CVE-2018-14847 Mikrotik Vulnerability using simple script
 jaarden/cve-2024-22894
Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…
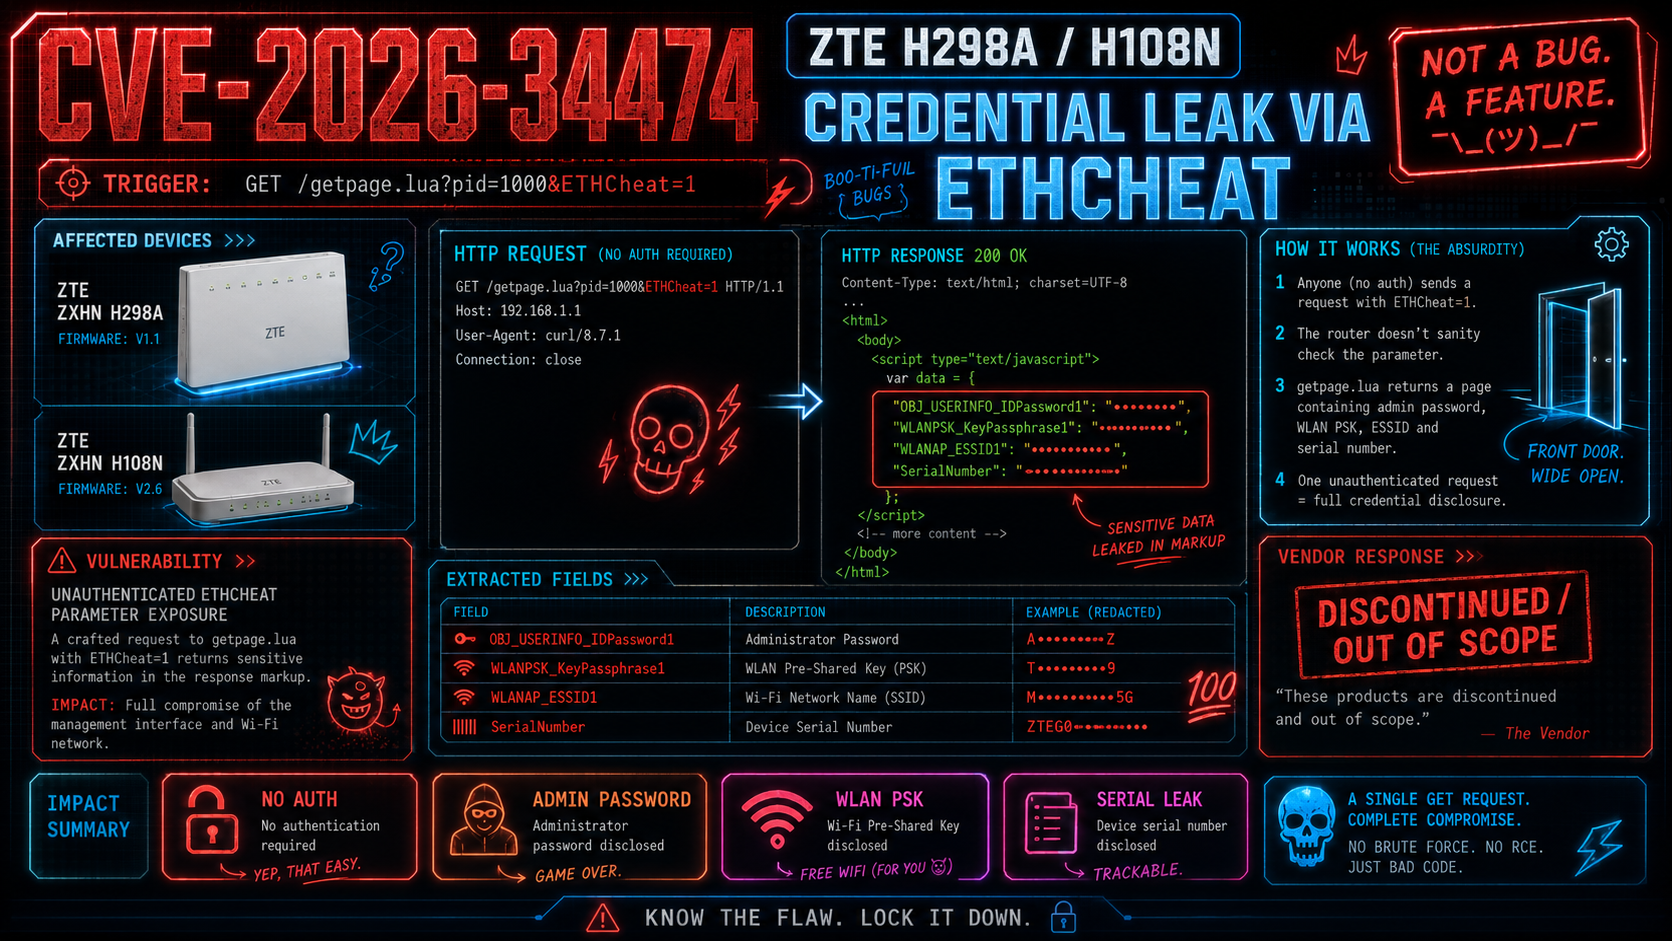 minanagehsalalma/cve-2026-34474-zte-h298a-h108n-sensitive-data-exposure
CVE-2026-34474: unauthenticated ETHCheat=1 requests leak the admin password and Wi-Fi PSK from ZTE H298A/H108N routers.
 x3roxismygood/cve-2012-1803
Critical vulnerability in Siemens RuggedCom ROS devices allowing attackers to derive a hidden factory account password from the device MAC address…
 mauricelambert/passwordssniffer
This module sniff username and password of unprotected protocols.
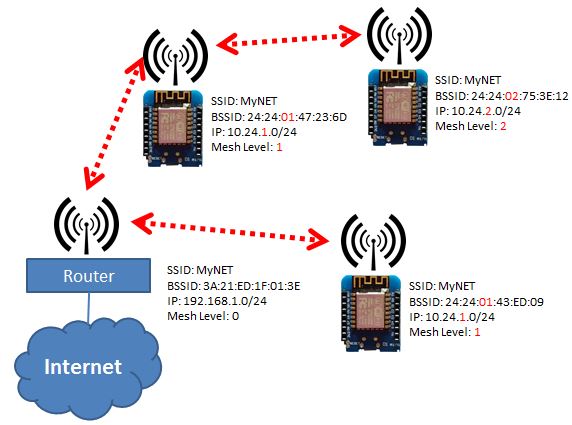 martin-ger/esp_wifi_repeater
A full functional WiFi NAT Router (and now also a WiFi Repeater)
 jptr218/openssh_dos
Proof-of-concept exploit for CVE-2016-6515, crashing OpenSSH servers via oversized password payloads that exhaust CPU resources during hash…
 hacker30468/mikrotik-router-hack
Proof-of-concept exploit for CVE-2018-14847 (MikroTik WinBox vulnerability) enabling arbitrary file read and plaintext password extraction via TCP/IP…
 arturo-b-cmu/cve-2016-20012
Python script for SSH username enumeration using timing-based analysis to identify valid accounts on a target server.
 itzmetanjim/cve-2026-8697
Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…