ddos-reduction-system

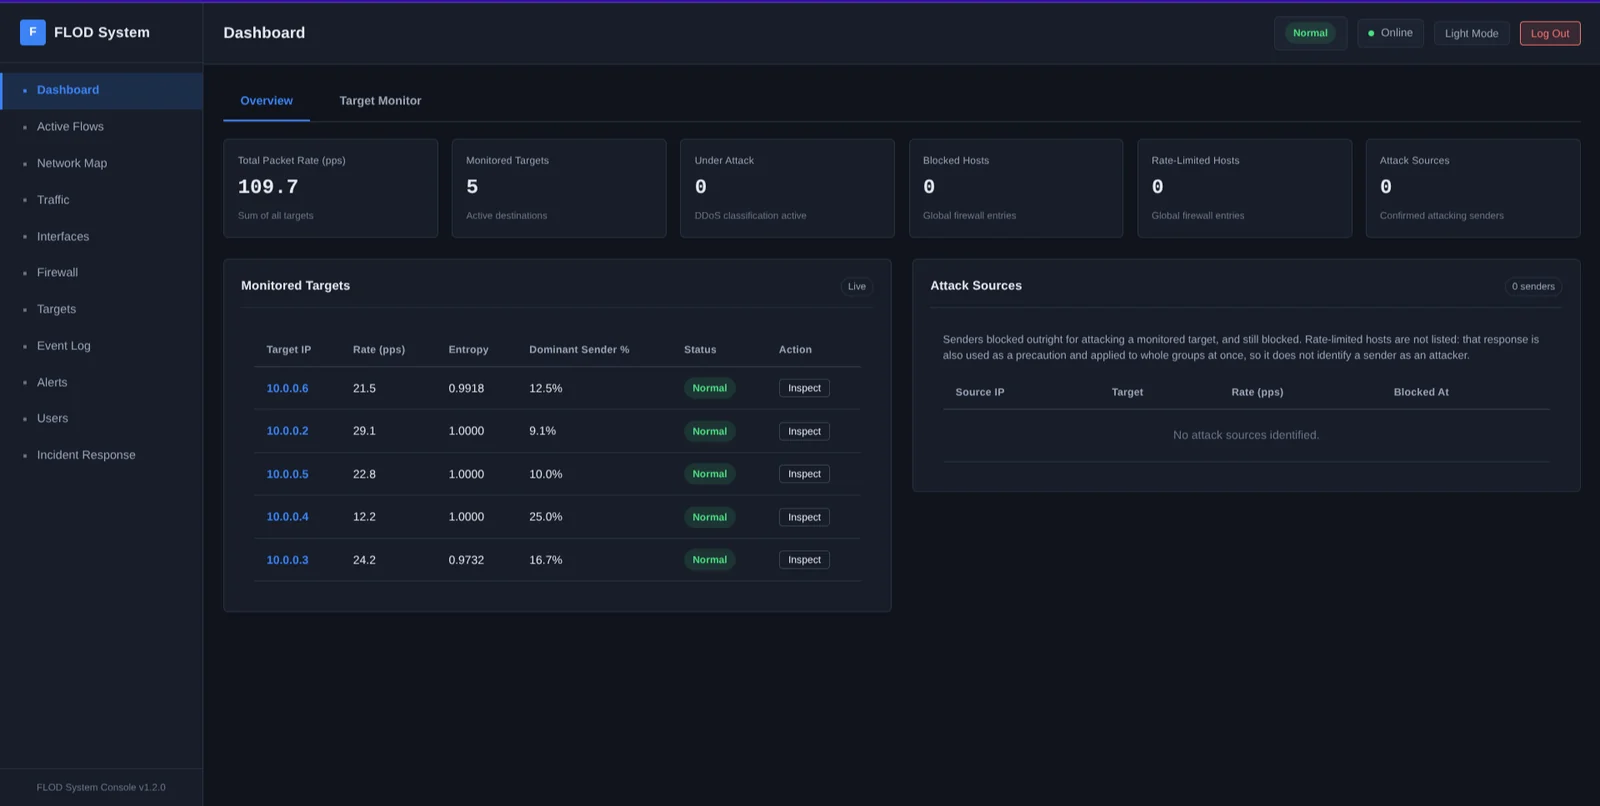
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…

Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…

Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.

Does This Look Like An Honeypot? (DTLLAH) Multi-protocol CLI that fingerprints whether a target IP behaves like an honeypot — using Honeyscore,…

Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…

Detection and mitigation research lab for CVE-2023-23397 using network and endpoint security telemetry.

Cross-platform command-line tools for configuring WireGuard VPN tunnels, offering key generation, peer management, and quick interface setup via wg…

Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…

A delicious, but malicious SSL-VPN server 🌮

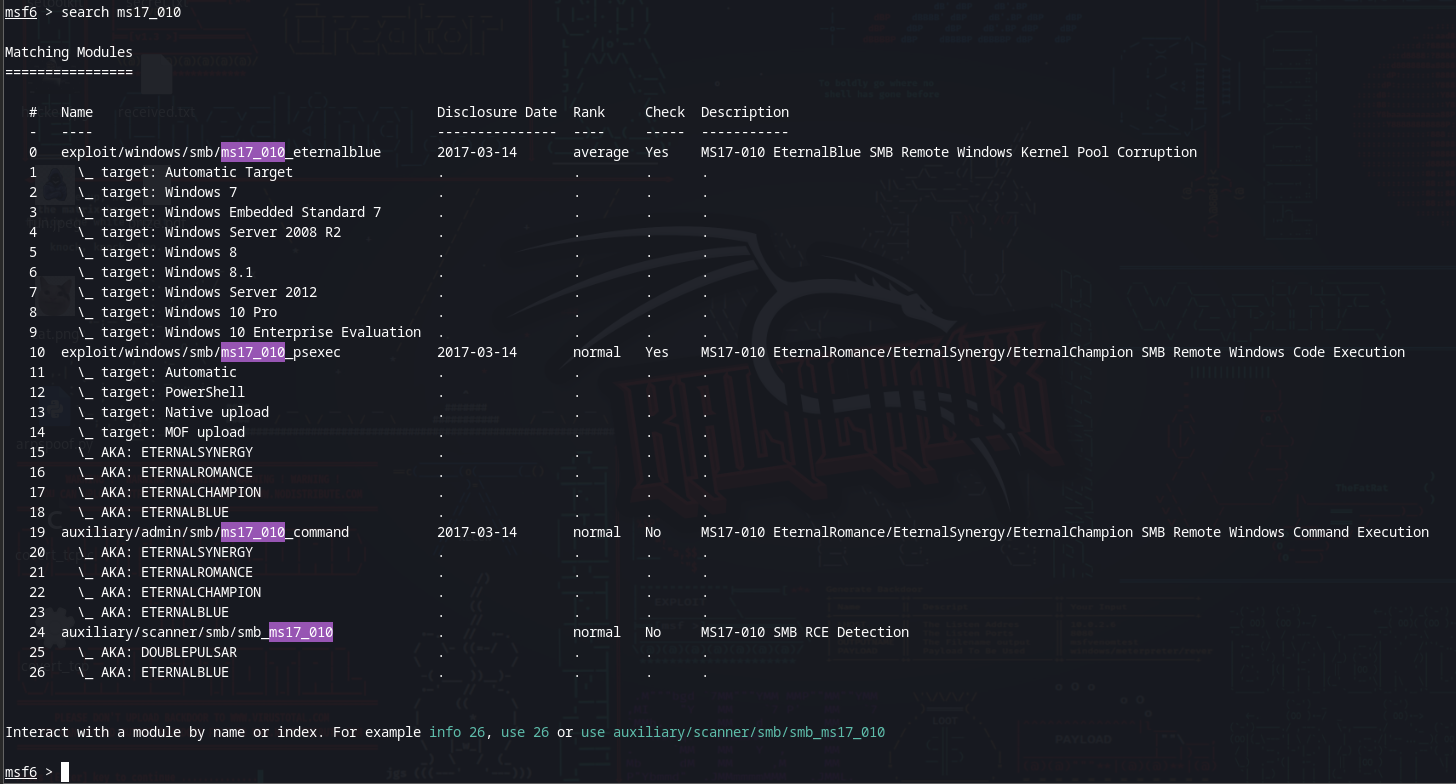
Step-by-step lab guide demonstrating the EternalBlue exploit (CVE-2017-0144) against Windows 7 SMB protocol using Metasploit, including setup,…

Detects NTLM relay attacks via PetitPotam exploit using Zeek, distinguishing successful and unsuccessful attempts by analyzing DCERPC return codes.

Free tool to connect private networks securely using encryption (AES/ChaCha20) with TLS authentication, supporting multi-platform remote access and…

Detection for SUNBURST C2 Stage-1 using Shannon Entropy

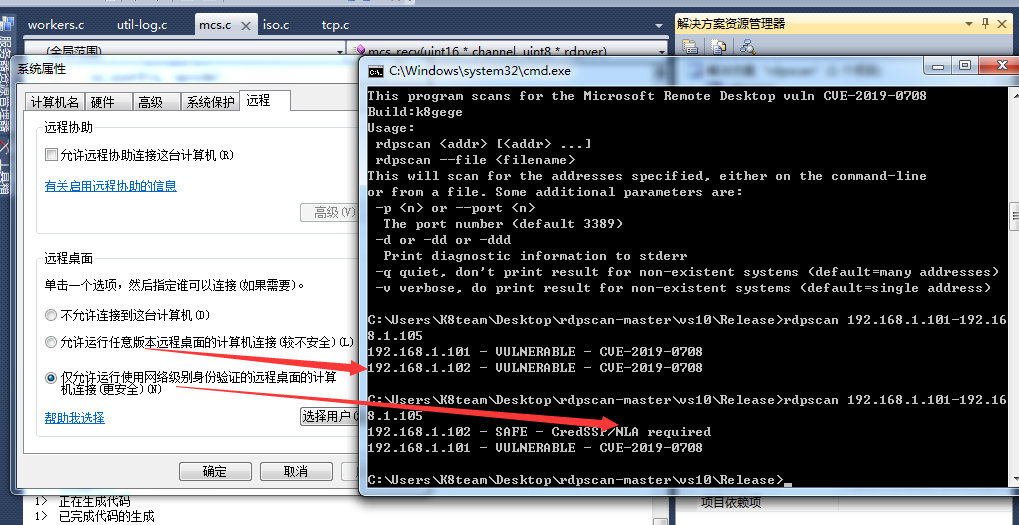
Batch scanner for CVE-2019-0708 (BlueKeep) RDP vulnerability with Windows and Linux support, using rdpscan and custom Cscan for mass IP range…

Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.

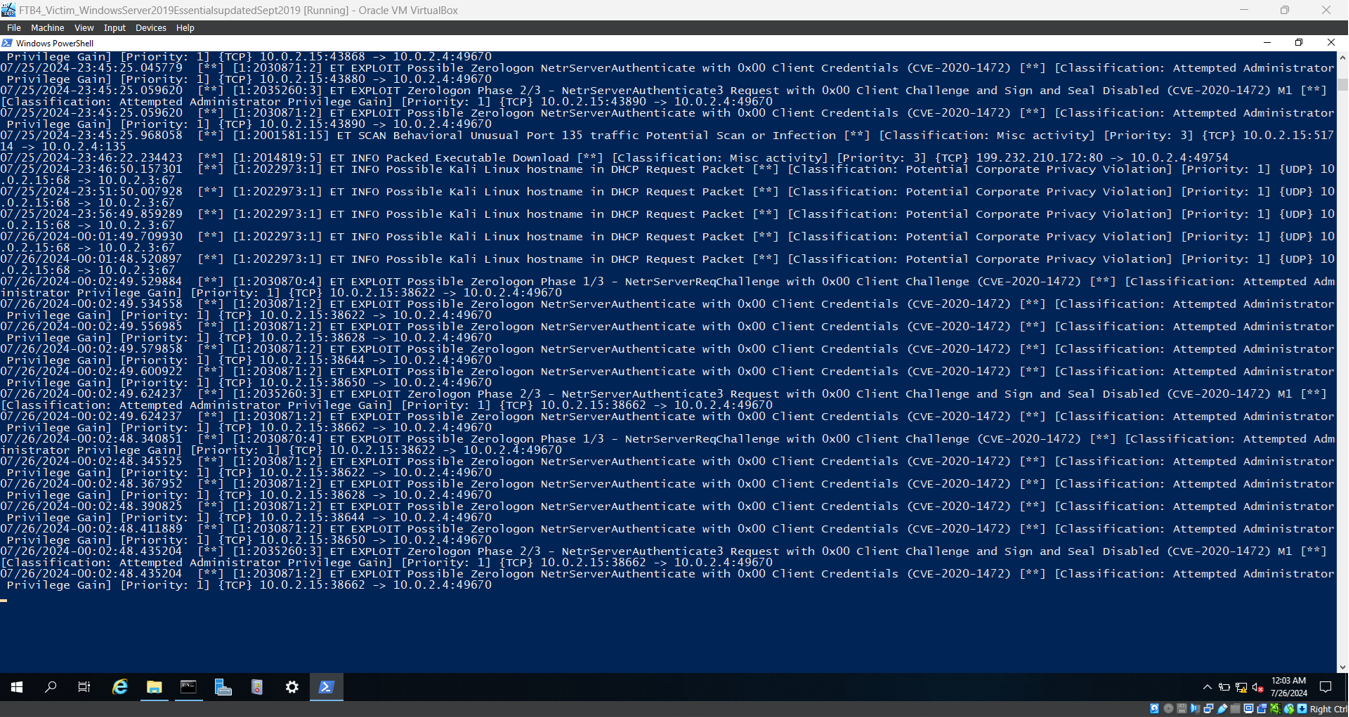
Educational demo of CVE-2020-1472 (ZeroLogon) detection using Windows Event Logs and Suricata IDS, plus mitigation via Windows Updates. Includes…

Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…

This is my attempt at fuzzing the tcpip.sys driver in windows via using scapy. This is inspired by this vulnerability here:…

Simple script using nmap to detect CVE-2017-0143 MS17-010 in your network