Open-Source-Threat-Intel-Feeds

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

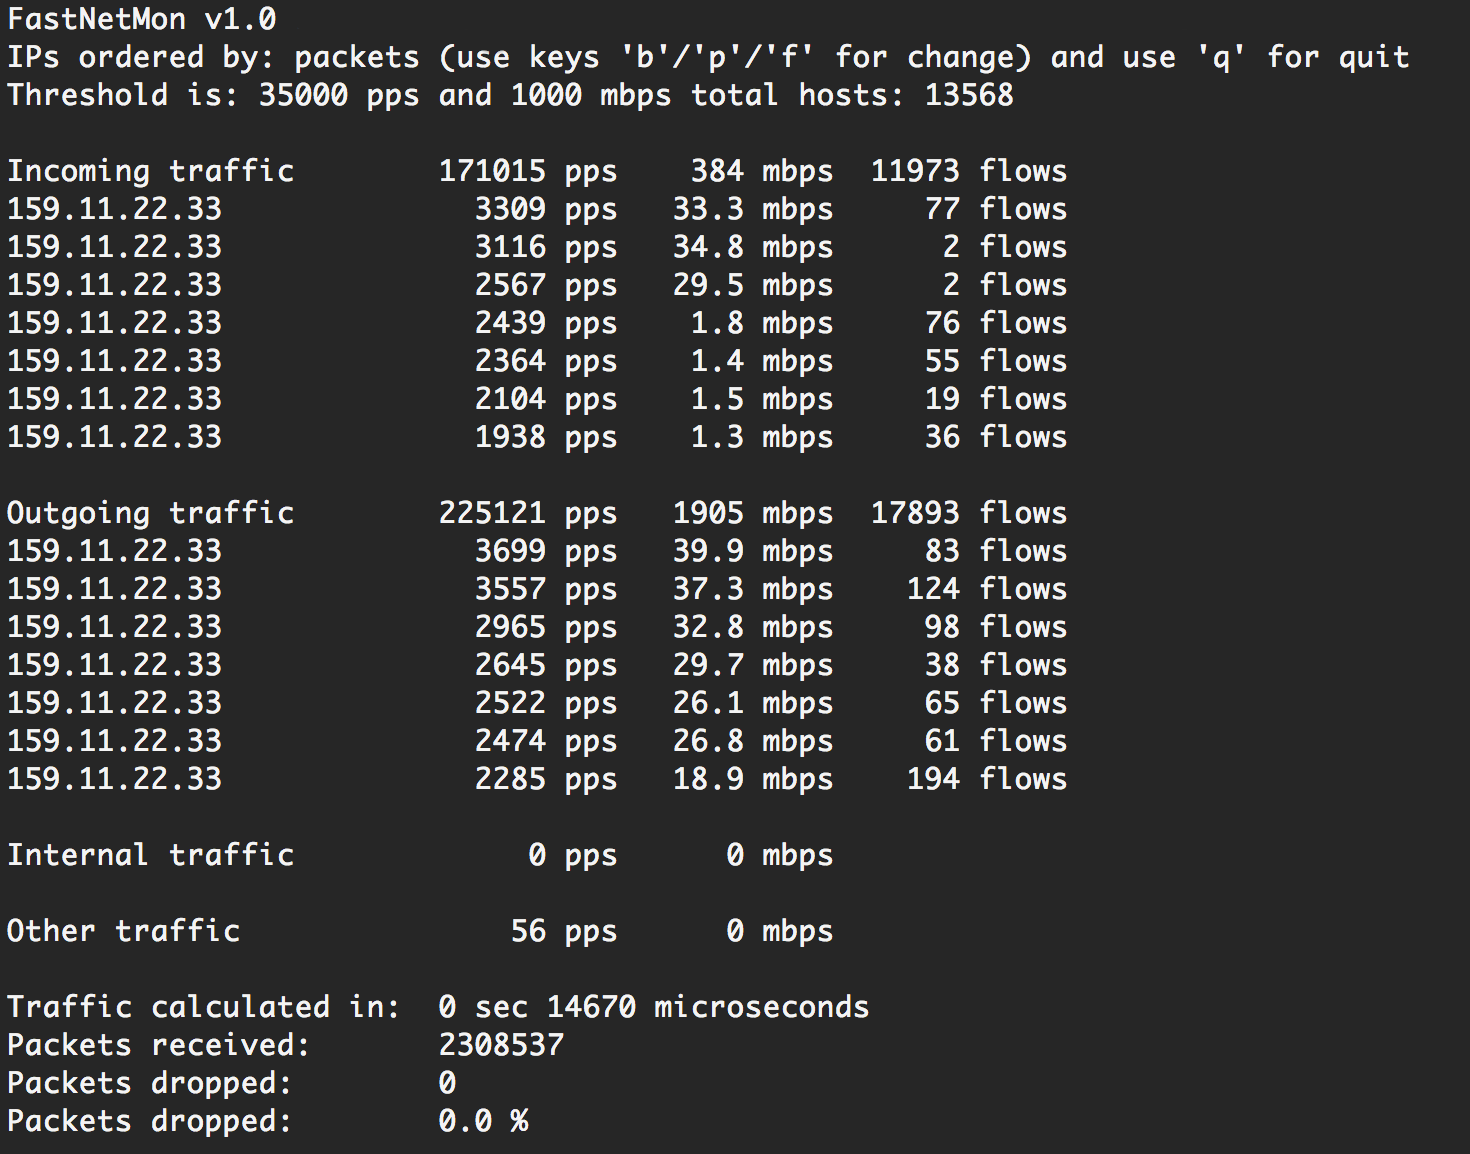
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support

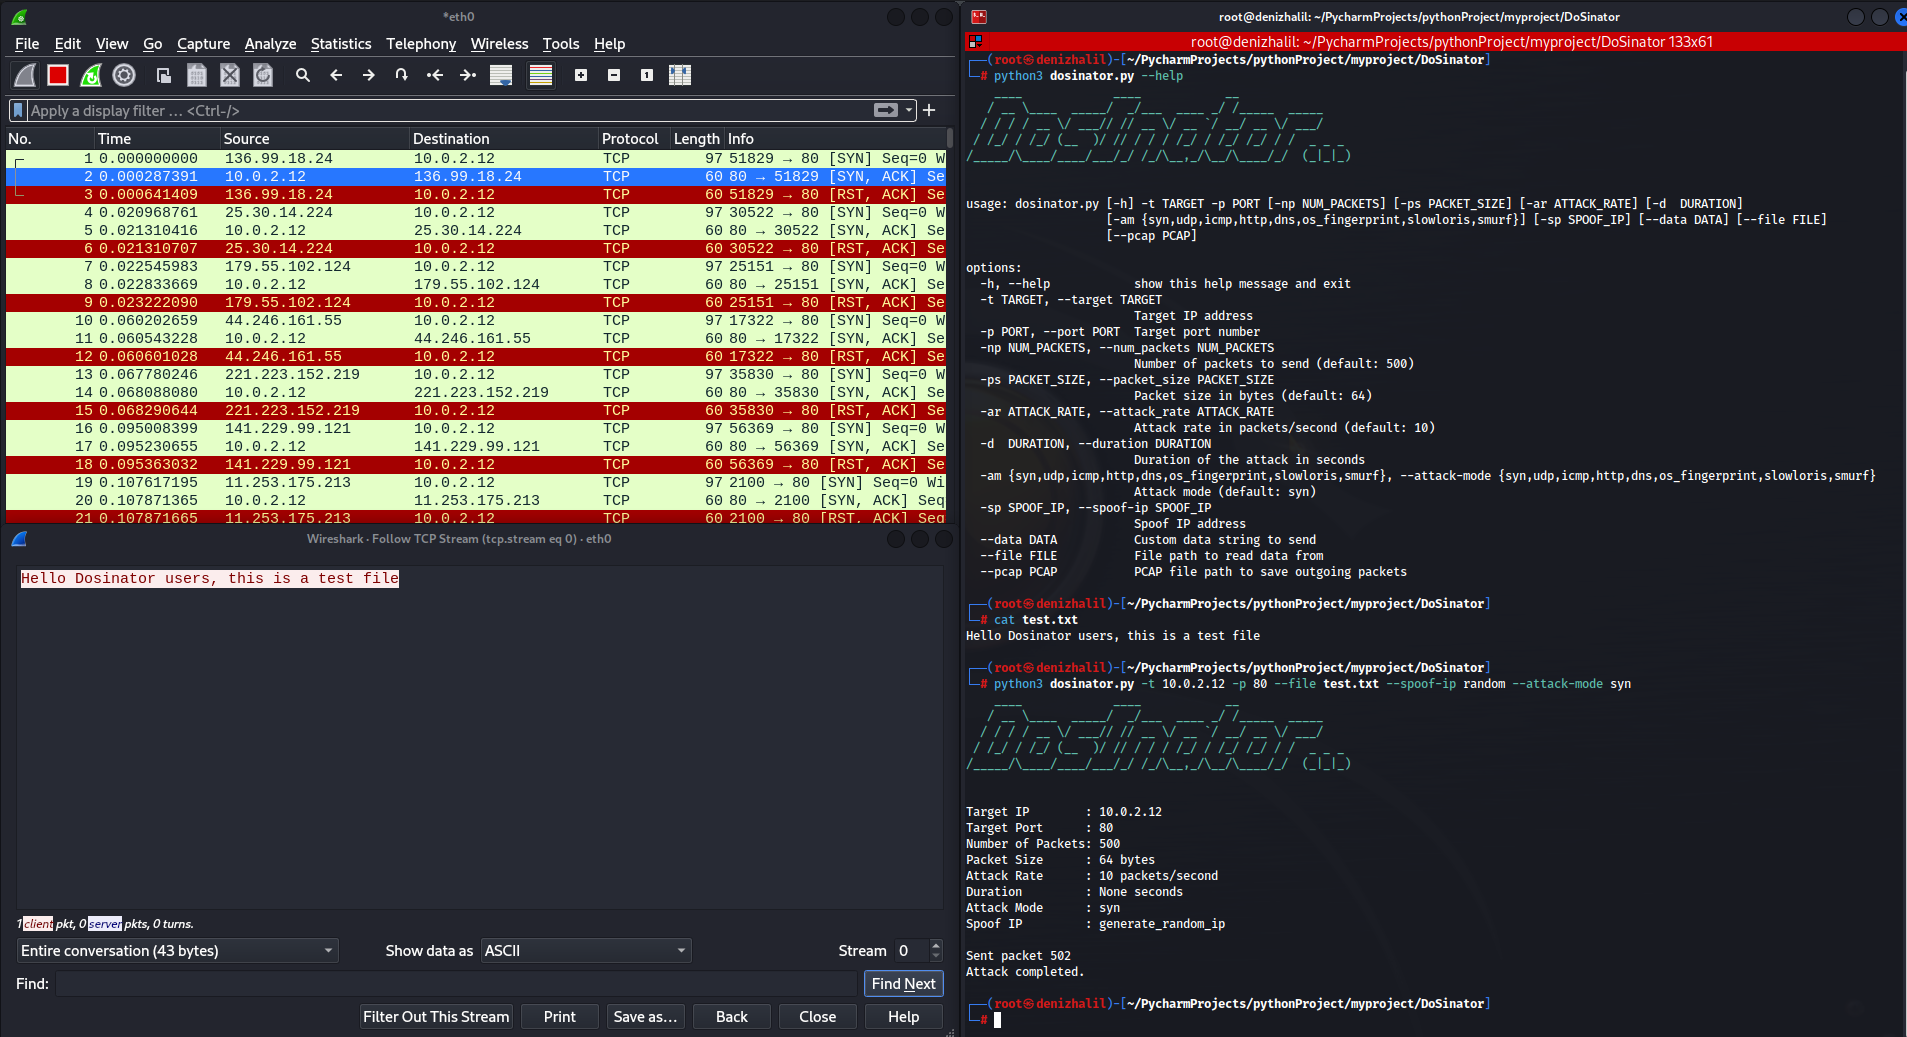
DoSinator is a powerful Denial of Service (DoS) testing tool developed in Python.

(extensible) Data Exfiltration Toolkit (DET)

Fast, efficient, and reliable detection for the regreSSHion exploit. Scan multiple targets in seconds with zero dependencies.

🔐 A CLI tool to extract server certificates

System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…

Multi-protocol honeypot simulator supporting 50+ network services with deep interaction, TCP/UDP/ICMP logging, JA3 fingerprinting, and virtual…

quicmap is a simple yet quic (!) QUIC protocol scanner

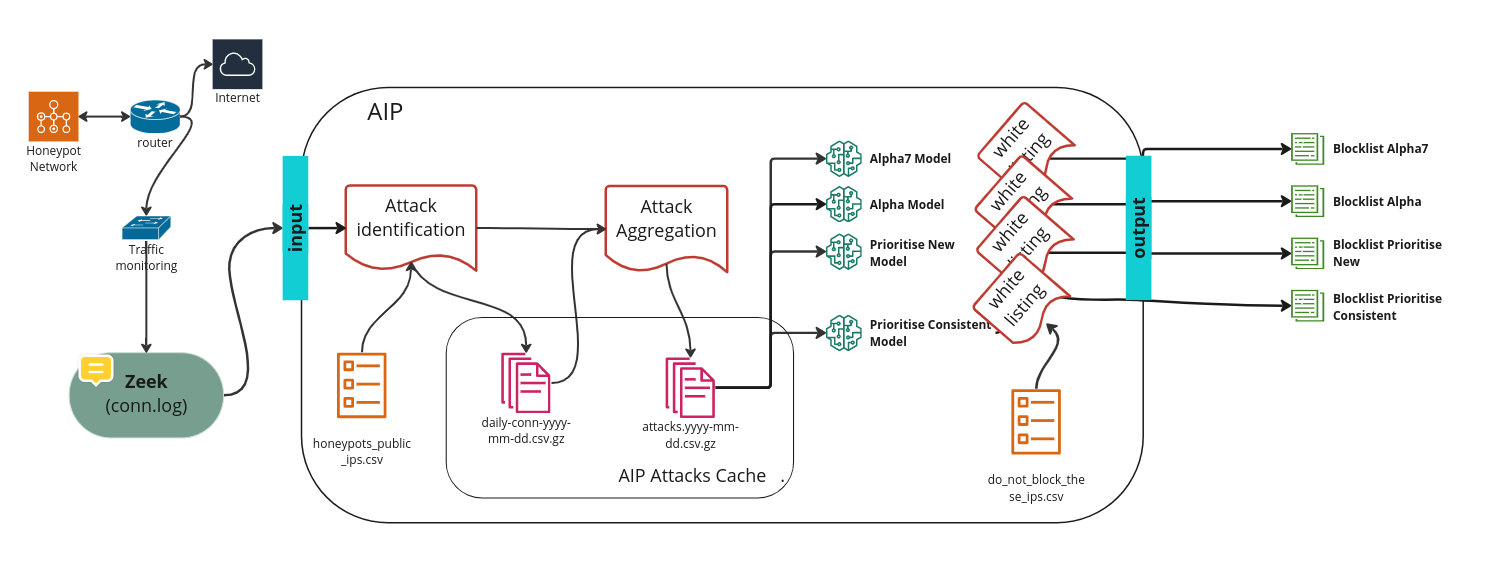
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…

Multi-threaded tool for scanning many hosts for CVE-2014-0160.

This script, created by R4Tw1z, is designed to scan IP addresses to check if they are running a potentially vulnerable version of OpenSSH. The tool…

Amplify network visibility from multiple POV of other hosts

This Python script checks for the CVE-2024-6387 vulnerability in OpenSSH servers. It supports multiple IP addresses, URLs, CIDR ranges, and ports.…

POC for checking multiple hosts for Zerologon vulnerability

Python-based scanner that detects OpenSSL 3.0.0-3.0.6 servers vulnerable to CVE-2022-3602 and CVE-2022-3786 by checking client authentication…

Vulnerability Scanner for CUPS: CVE-2024-47176

CVE documentation repository detailing unauthenticated remote vulnerabilities in Cisco Catalyst PON Series Switches ONT, including default credential…