

kubeshark
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
ai-securitycloud-infrastructure-securitycloud-security+9
12.1k
kubeshark/kubesharkeBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 cilium/cilium
eBPF-based Networking, Security, and Observability
 ntop/ndpi
Open Source Deep Packet Inspection Software Toolkit
 ory/oathkeeper
A cloud native Identity & Access Proxy / API (IAP) and Access Control Decision API that authenticates, authorizes, and mutates incoming HTTP(s)…
 nameles-org/nameles
Open source entropy based invalid traffic detection and pre-bid filtering.
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
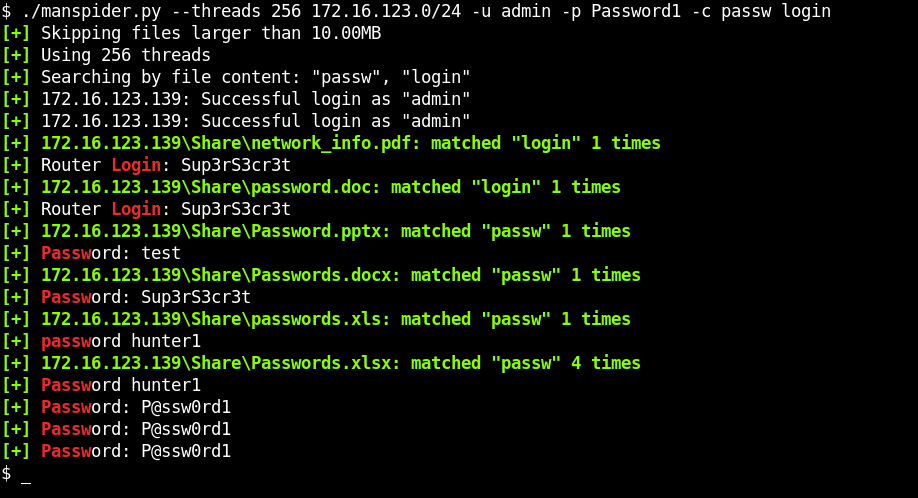 blacklanternsecurity/manspider
Spider entire networks for juicy files sitting on SMB shares. Search filenames or file content - regex supported!
 kismetwireless/kismet
Github mirror of official Kismet repository
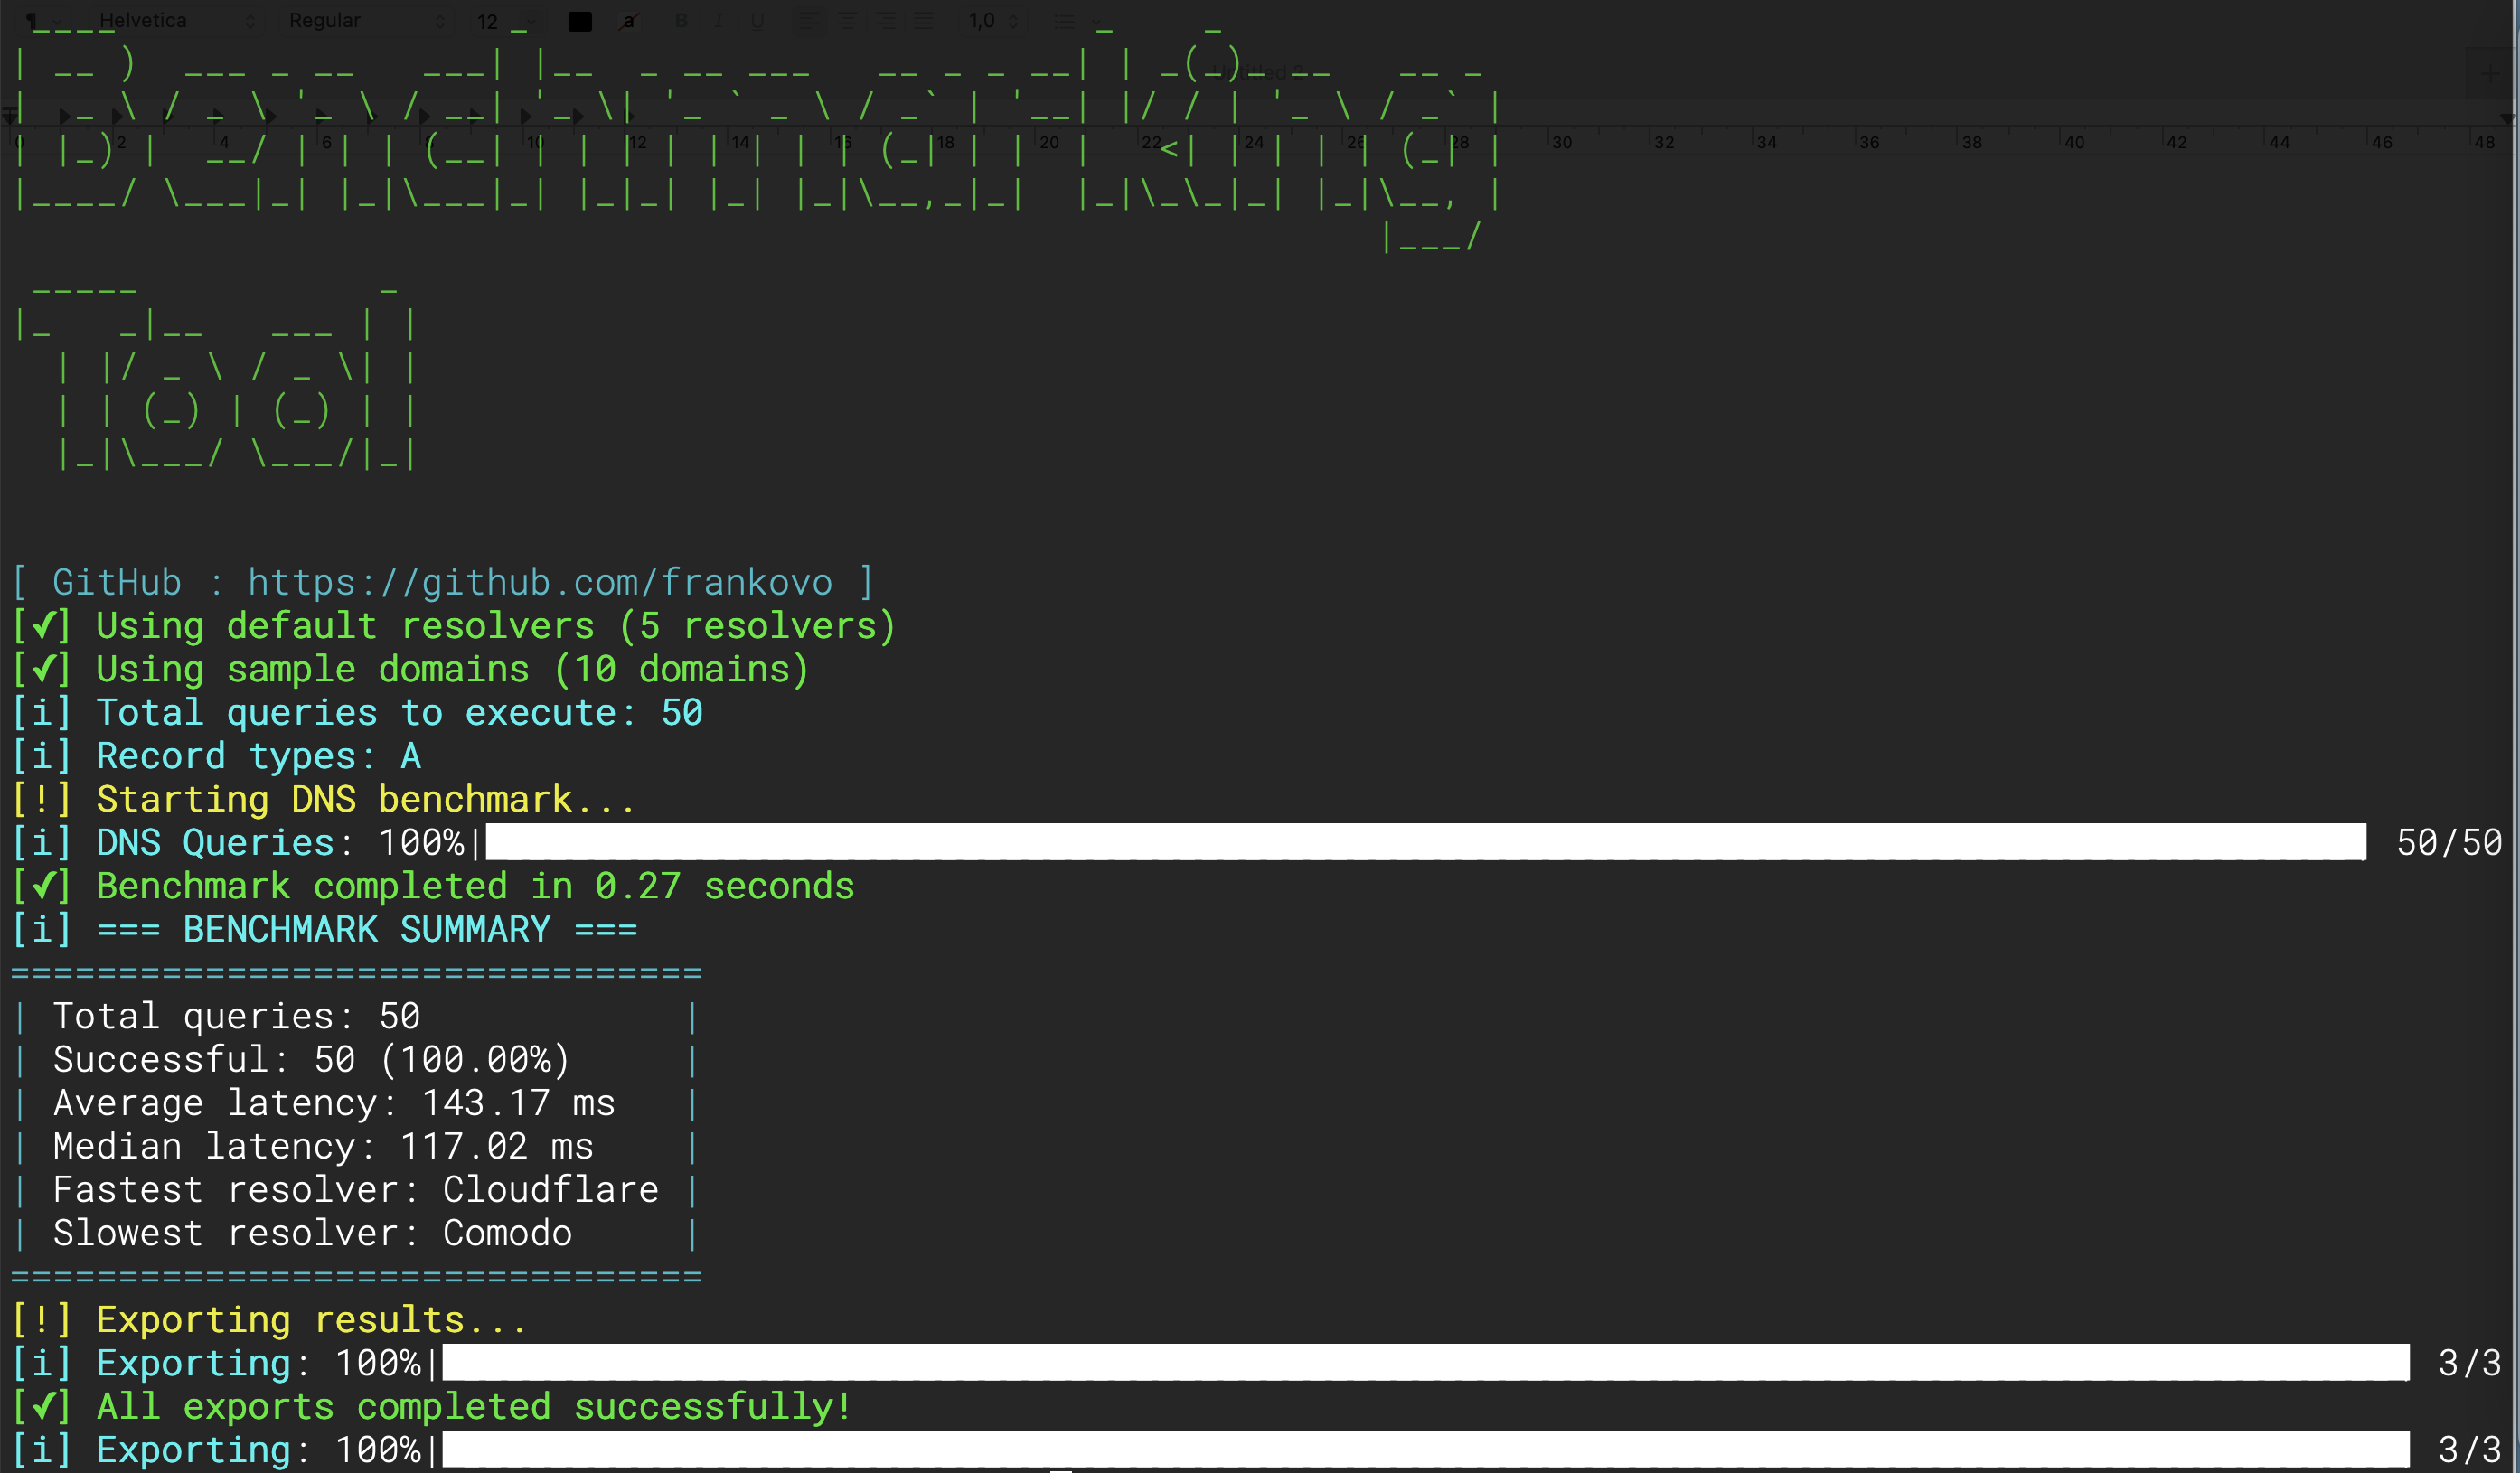 net-benchmark/dns-benchmark-tool
Fast, comprehensive DNS performance testing with DNSSEC validation, DoH/DoT support, and enterprise features
 kismetwireless/kismet-docs
Documentation repository for Kismet, a wireless network detector, sniffer, and intrusion detection system. Includes guides, configuration references,…
 stealyourcode/cve-2019-1663
Docs on the Vulnerability CVE-2019-1663 (Cisco Routers)