

 redcode-labs/coldfire
Golang malware development library
 cybersecurityworks553/cve-2021-1675_printnightmare
Scanner to detect Windows Print Spooler RCE vulnerability (CVE-2021-1675) across single IPs, IP lists, or CIDR ranges using Python.
 haishanzheng/cve-2019-0708-generate-hosts
CIDR-based host discovery tool that uses nmap to identify Windows machines with open port 3389 (RDP), reducing target IPs for CVE-2019-0708…
 eesshq/cve-2017-0144---etneralblue-ms17-010-remote-code-execution
Step-by-step guide to exploiting MS17-010 EternalBlue vulnerability on Windows Server 2008 R2, including reconnaissance, exploitation,…
 sethwhy/bluedoor
Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…
 dsp-testing/cve-2018-13797
Cross-platform Node.js library to retrieve MAC addresses per network interface on Linux, macOS, and Windows, with async and sync APIs.
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 rustdesk/rustdesk
An open-source remote desktop application designed for self-hosting, as an alternative to TeamViewer.
 zux0x3a/0xsp-mongoose
a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…
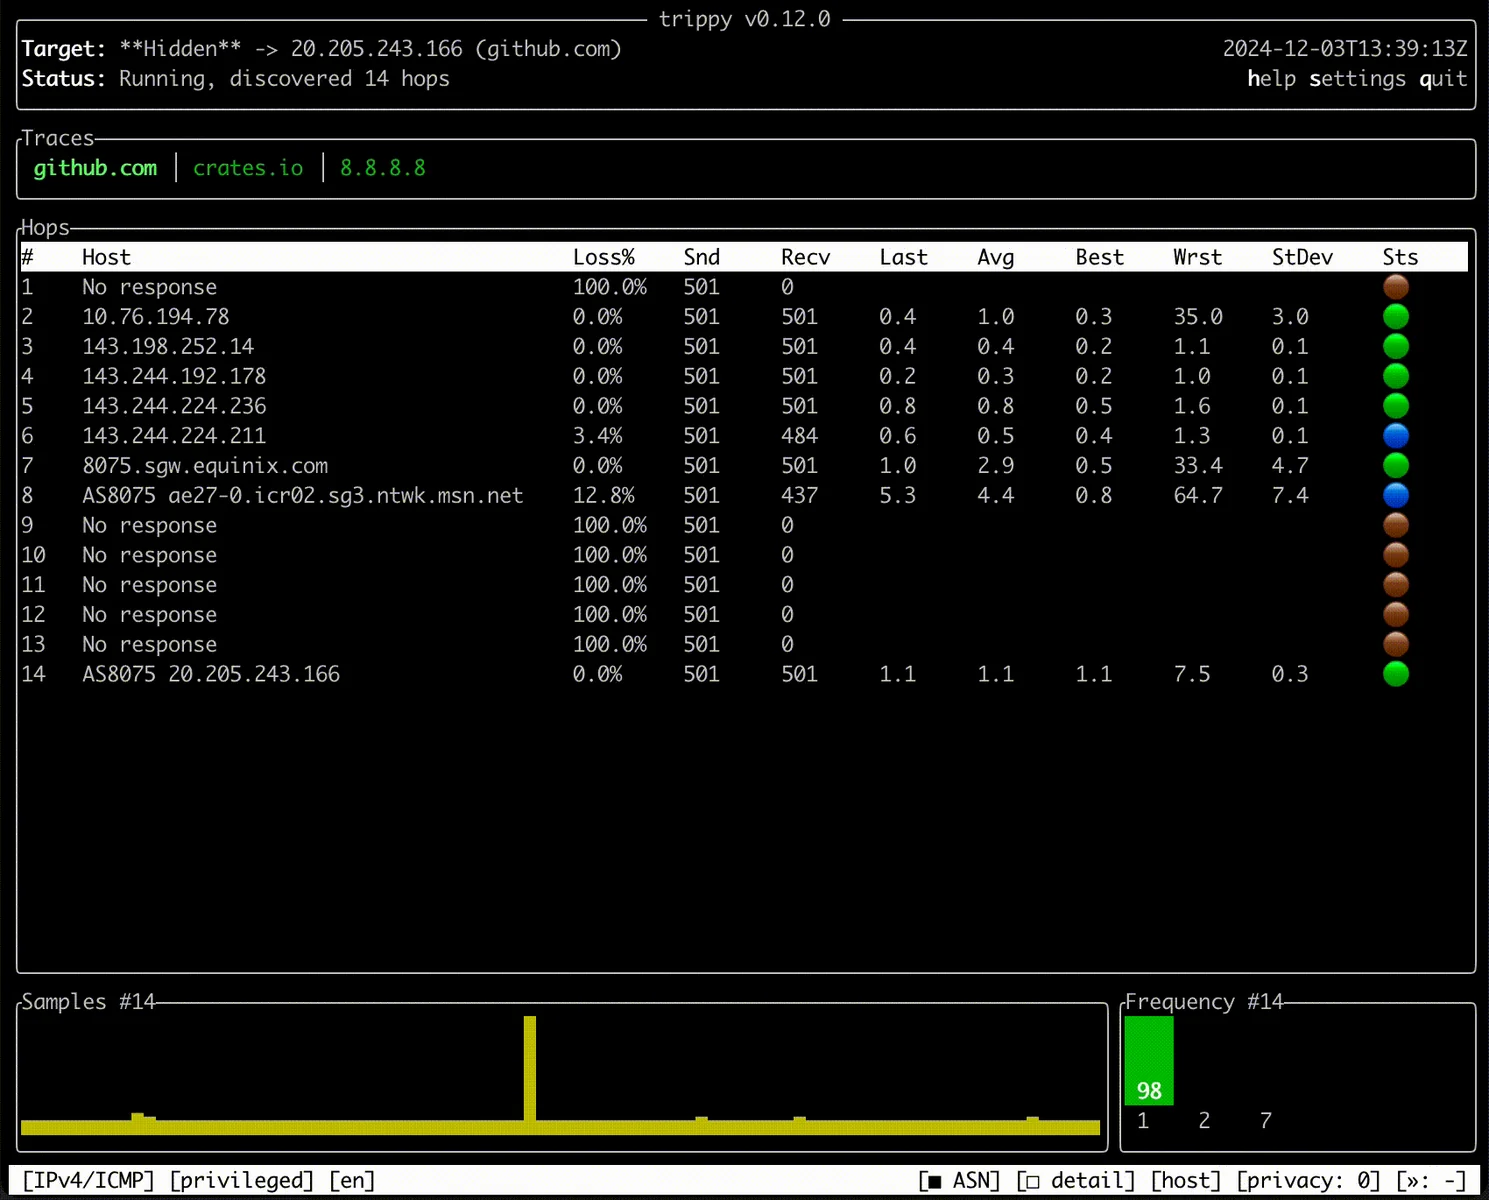 fujiapple852/trippy
A network diagnostic tool combining traceroute and ping for analyzing network paths, latency, and packet loss with an interactive terminal UI.
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 p0dalirius/sharehound
A python tool to map the access rights of network shares into a BloodHound OpenGraphs easily
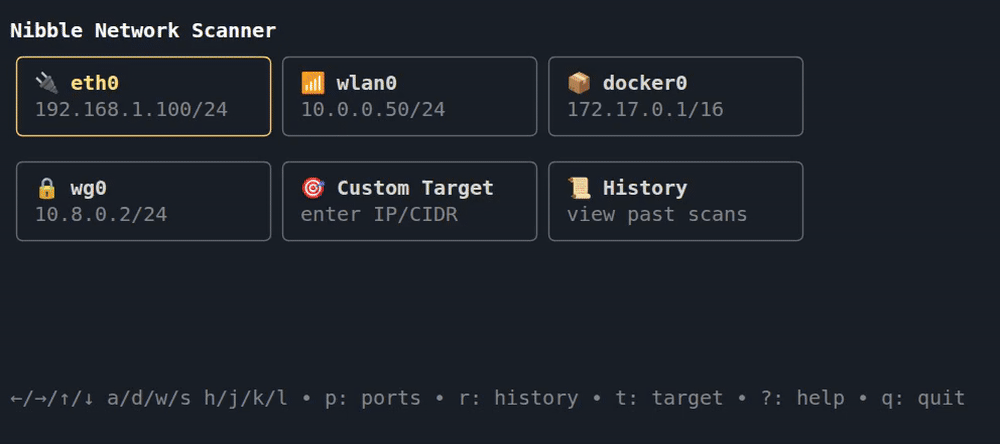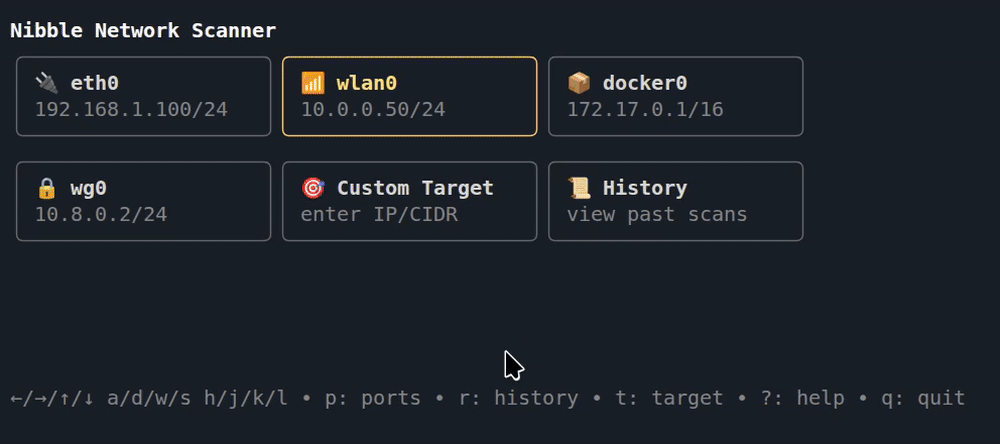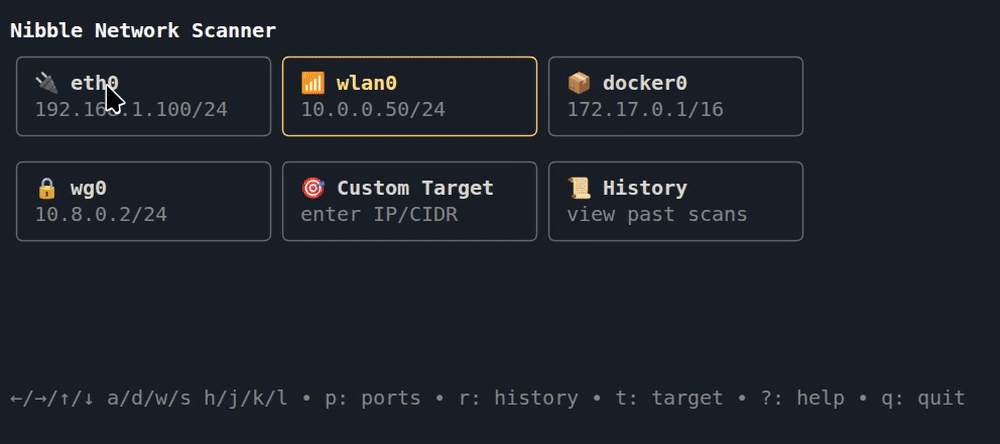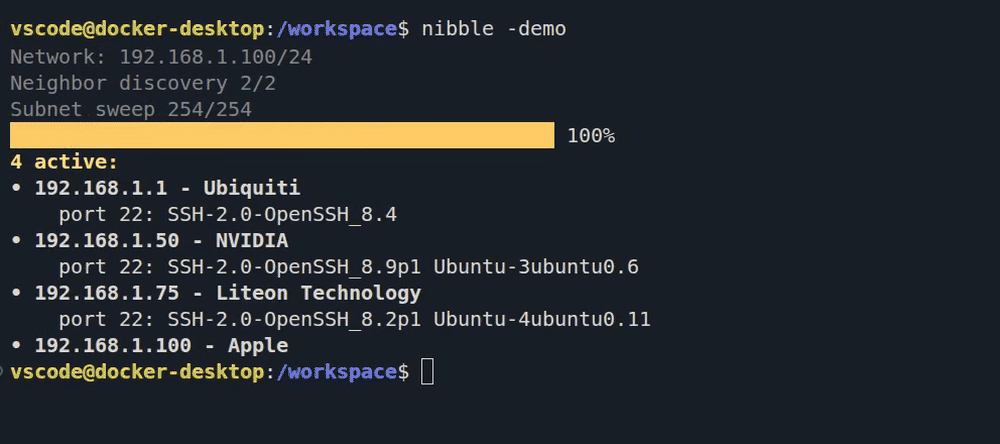 backendsystems/nibble
easy to use network scanner, with a clickable tui interface
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 jasondrawdy/forerunner
Fast and extensible network scanning library featuring multithreading, ping probing, and scan fetchers.
 injectionmethod/windows-zte-loader
Windows ZTE Loader CVE-2014-2321 Requires ZMAP For Windows Or BigEar
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…