ivre
 ivre/ivre
Network recon framework. Build your own, self-hosted and fully-controlled alternatives to Shodan / ZoomEye / Censys and GreyNoise, run your Passive…
dns-analysisinformation-gatheringnetwork-mapping+4
4.2k
ivre/ivreNetwork recon framework. Build your own, self-hosted and fully-controlled alternatives to Shodan / ZoomEye / Censys and GreyNoise, run your Passive…
 trustedsec/hardcidr
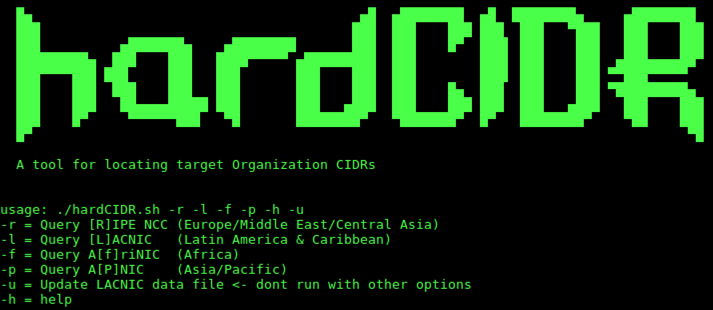
Bash script for passive reconnaissance that queries RIRs and BGP route servers to discover target organization netblocks, ASNs, and CIDR ranges…
 haruu77g/phantomprint
Passive hybrid fingerprinting engine — identify hosts without sending a single packet
 s0md3v/smap
a drop-in replacement for Nmap powered by shodan.io
 evilsocket/spycast
A crossplatform mDNS enumeration tool.
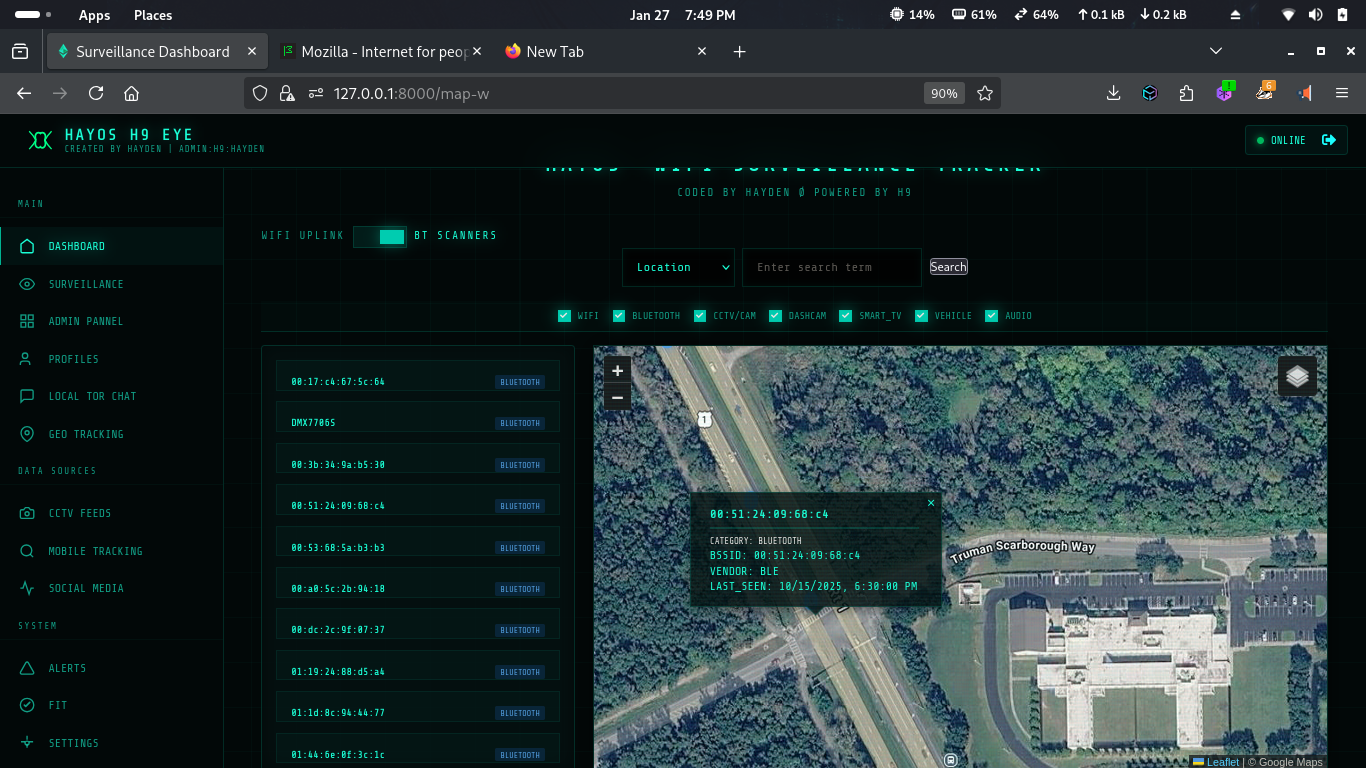 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…

 jankoboy88/higernes
a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 vqkro/higernes
a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…