
ConMachi
 nccgroup/conmachi
Container Blackbox Security Auditing Tool: enumerates security configuration from within the target container
cloud-infrastructure-securityconfiguration-auditingcontainer-security+4
106
nccgroup/conmachiContainer Blackbox Security Auditing Tool: enumerates security configuration from within the target container
 bojanisc/quicmap
quicmap is a simple yet quic (!) QUIC protocol scanner
 jhaddix/awsscrape
A tool to scrape the AWS ranges looking for a keyword in SSL certificate data.
 reddyyz/astsu
A network scanner tool, developed in Python 3 using scapy.
 xcodeon1/ssh-killv2
SSH brute-force tool targeting jailbroken iPhones with default 'alpine' password, featuring network scanning, wordlist-based cracking, and file…
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…

 al14s/rawr
Rapid Assessment of Web Resources
 raskrebs/sonar
CLI tool for inspecting and managing services listening on localhost ports
 evilsocket/spycast
A crossplatform mDNS enumeration tool.
 jevalenciap/iptodomain
This tool extract domains from IP address based in the information saved in virustotal.

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
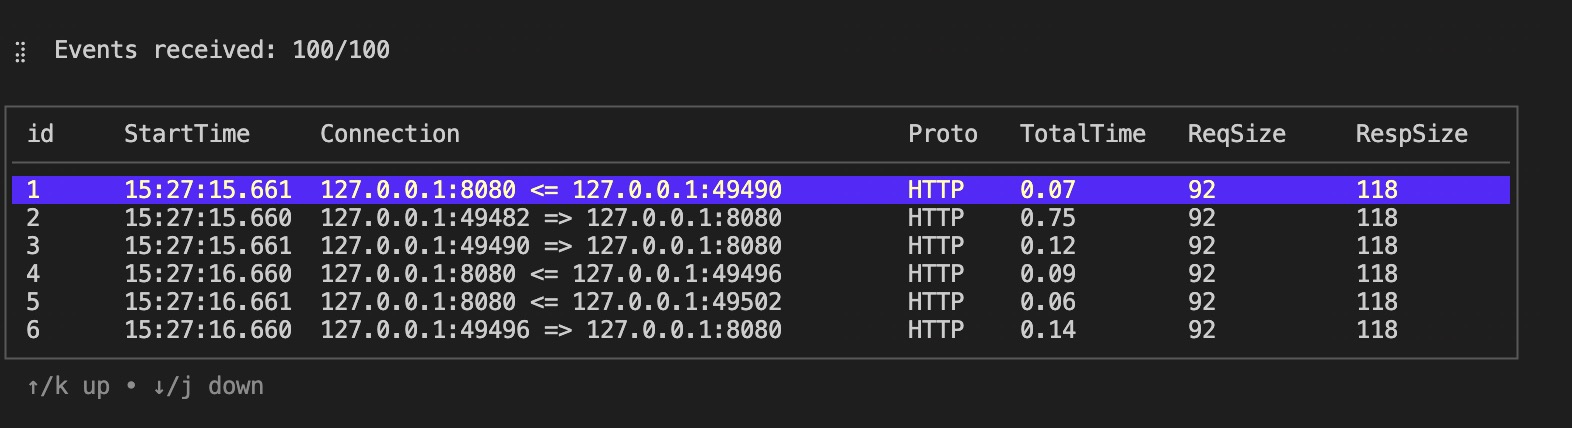 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
 nccgroup/cloud_ip_ranges
Identify IP addresses owned by public cloud providers
 dsp-testing/cve-2018-13797
Cross-platform Node.js library to retrieve MAC addresses per network interface on Linux, macOS, and Windows, with async and sync APIs.
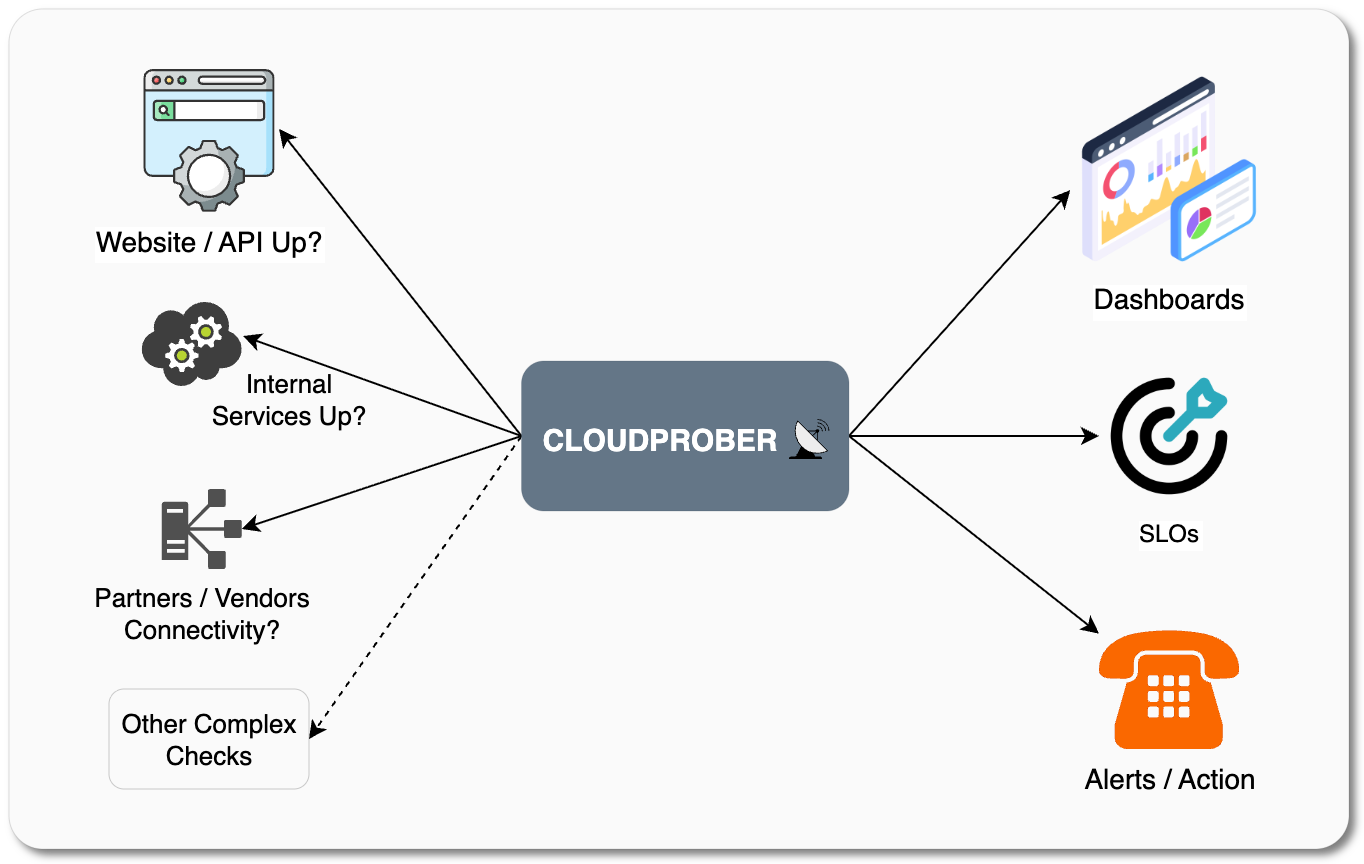 cloudprober/cloudprober
An active monitoring software to detect failures before your customers do.
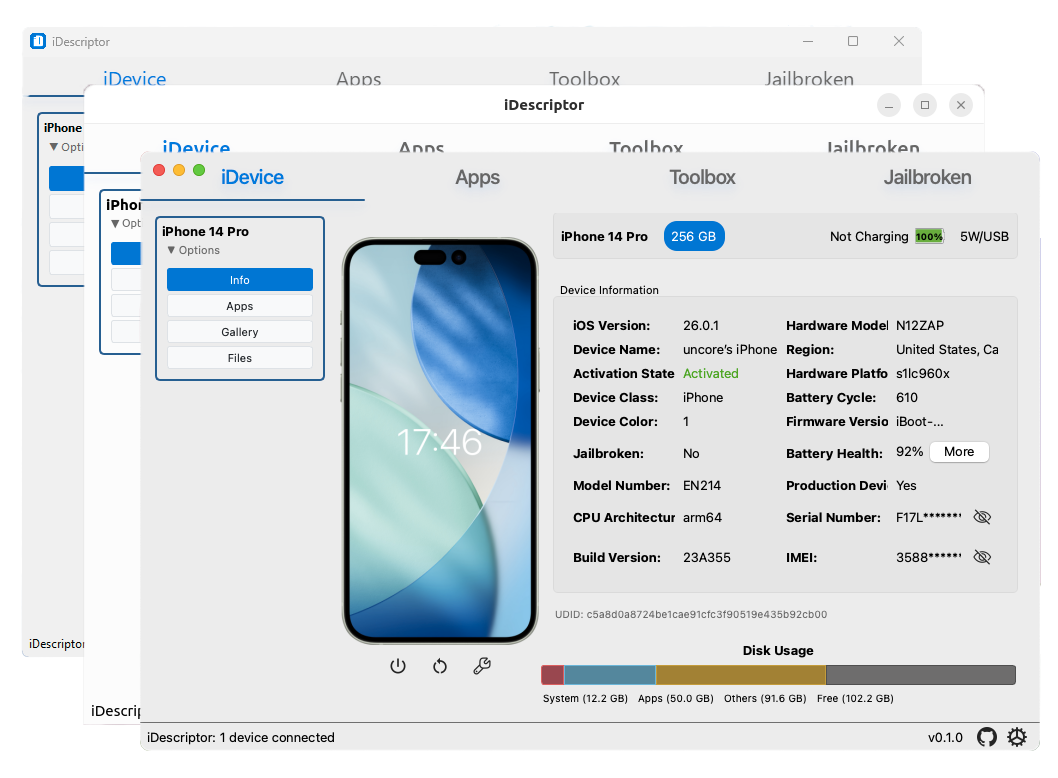 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 tjnull/cygor
An modular asset discovery framework written in python to automate the repeating manual work
 vig9610/exploiting-samba-on-metasploitable-2
Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…