
sdwan-harvester
 sdnewhop/sdwan-harvester
🌐 Automatically enumerate and fingerprint SD-WAN nodes on the internet
information-gatheringnetwork-mappingosint+4
49
sdnewhop/sdwan-harvester🌐 Automatically enumerate and fingerprint SD-WAN nodes on the internet
 escape-technologies/awesome-attack-surface-management
A curated collection of tools, techniques, frameworks, and learning resources focused on Attack Surface Management (ASM).
 projectdiscovery/naabu-action
A fast port scanner written in go with a focus on reliability and simplicity.
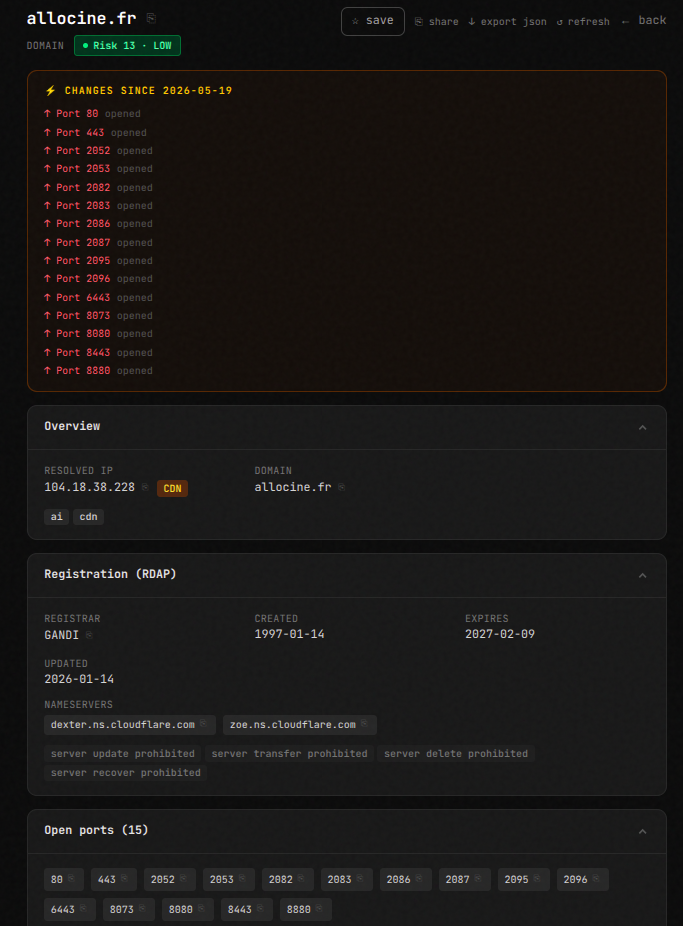 teycir/seekyou
OSINT intelligence on any IP, domain, or ASN
 enenumxela/ps.sh
A bash script that automates port scanning on specified target host(s). The aim of the scripts is reducing scan time, increasing scan efficiency and…
 eesshq/cve-2017-0144---etneralblue-ms17-010-remote-code-execution
Step-by-step guide to exploiting MS17-010 EternalBlue vulnerability on Windows Server 2008 R2, including reconnaissance, exploitation,…
 qkaiser/awind-research
This repository holds interesting bits and pieces related to research I performed on wireless presentation devices manufactured by Awindinc and…
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
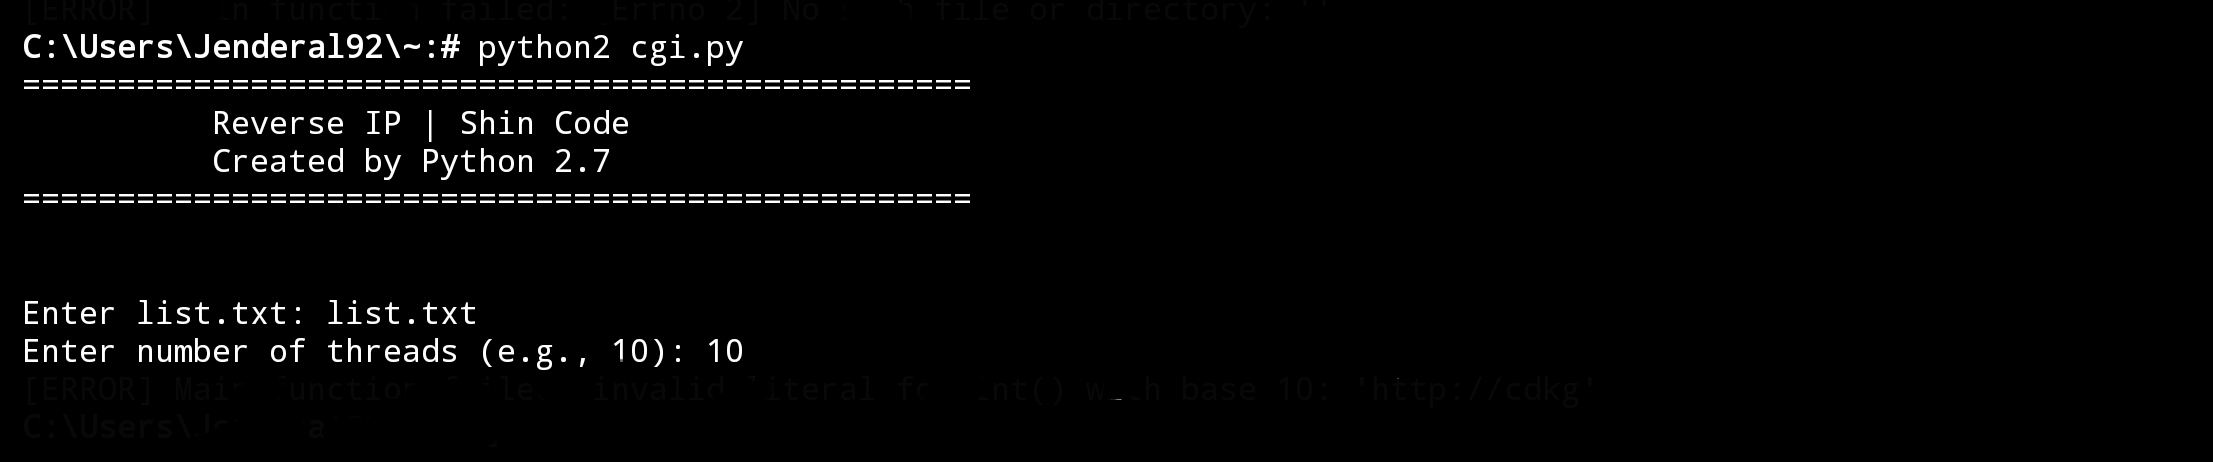 jenderal92/reverse-ip-new-api
This tool is used to perform reverse IP lookups— searching for all domains hosted on one IP address.
 sethwhy/bluedoor
Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…
 rinaliyeva/metasploitable2-vsftpd-exploitation
Project: vsFTPd 2.3.4 backdoor exploitation (CVE-2011-2523) on Metasploitable 2.
 masjohncook/netsec-project
Script of Network Security Project - Attack on CVE-2021-22555
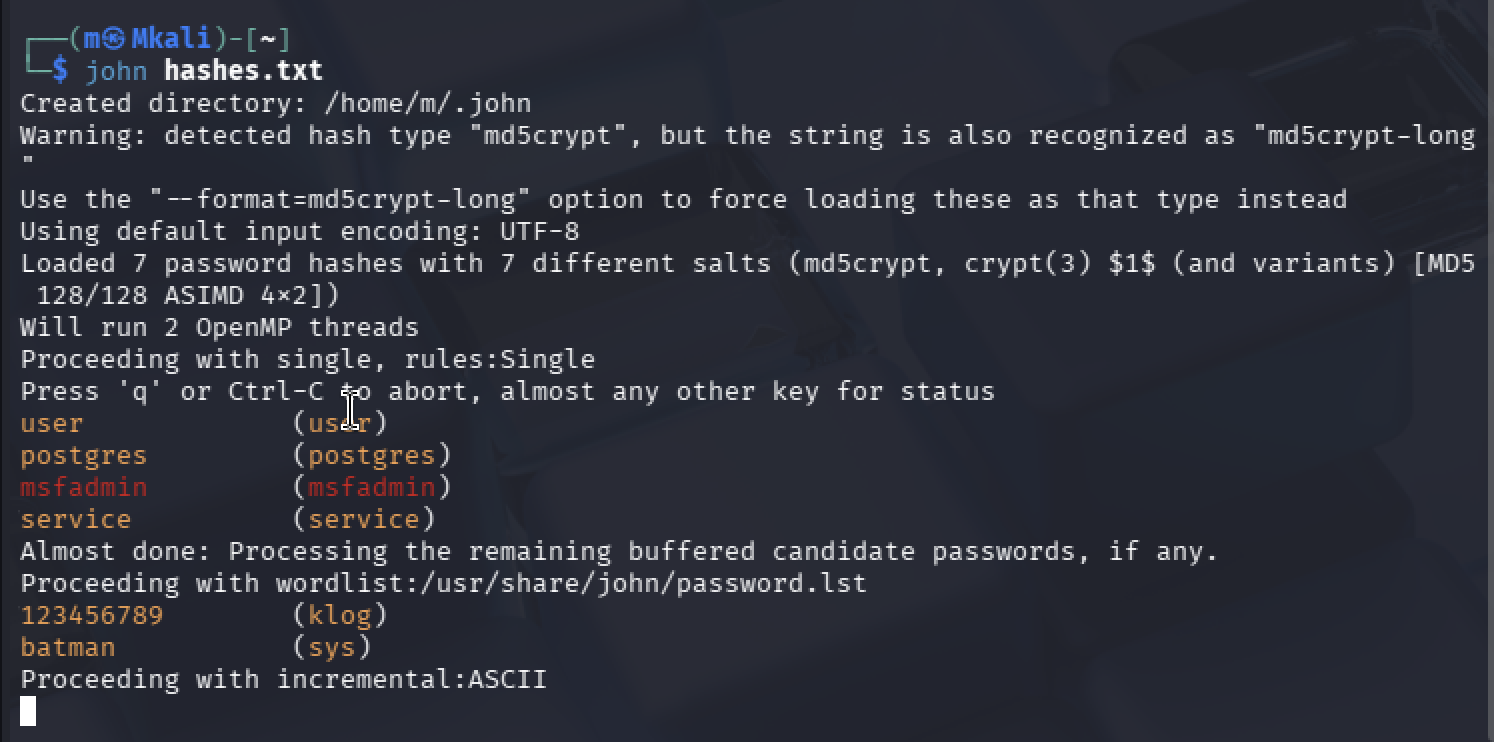 mirza-22144/vulnerability-assessment-exploitation-lab
Full-lifecycle penetration test of a legacy Linux environment (Metasploitable 2) emulated on Apple Silicon. Demonstrating network reconnaissance, RCE…
 dsp-testing/cve-2018-13797
Cross-platform Node.js library to retrieve MAC addresses per network interface on Linux, macOS, and Windows, with async and sync APIs.
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.
 neweracracker/loic
Deprecated - Low Orbit Ion Cannon - An open source network stress tool, written in C#. Based on Praetox's LOIC project. USE ON YOUR OWN RISK. WITHOUT…
 projectdiscovery/dnsprobe
DNSProb is a tool built on top of retryabledns that allows you to perform multiple dns queries of your choice with a list of user supplied resolvers.
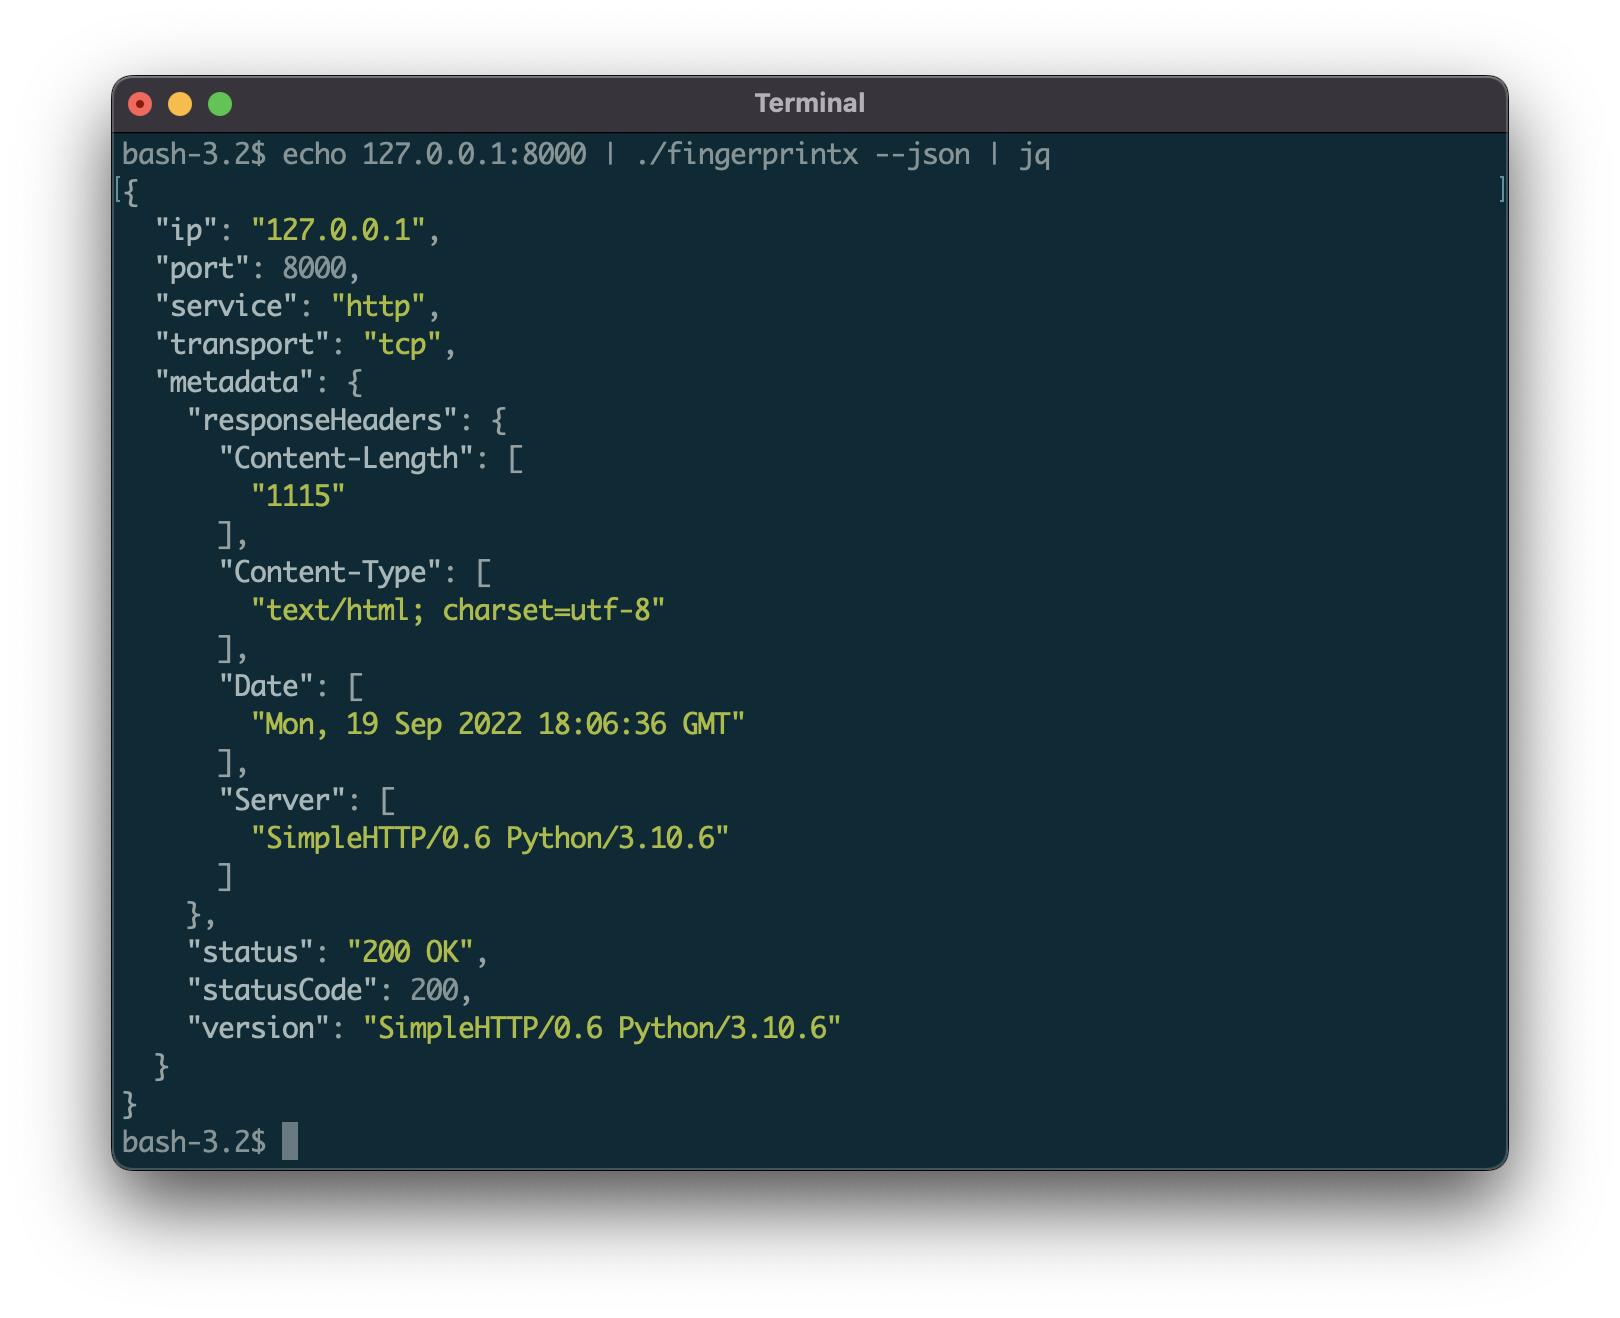 praetorian-inc/fingerprintx
Standalone utility for service discovery on open ports!