

bettercap
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
bluetooth-securitydata-exfiltrationfingerprint-spoofing+16
19.8k
bettercap/bettercapThe Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 sdnewhop/sdwan-harvester
:globe_with_meridians: Automatically enumerate and fingerprint SD-WAN nodes on the internet
 sabri-zaki/easy_hack
Hack the World using Termux
 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
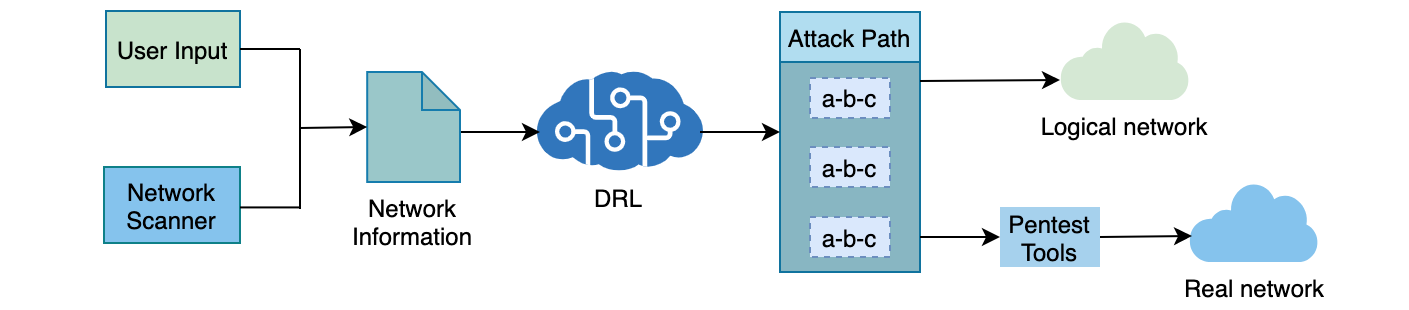 crond-jaist/autopentest-drl
AutoPentest-DRL: Automated Penetration Testing Using Deep Reinforcement Learning
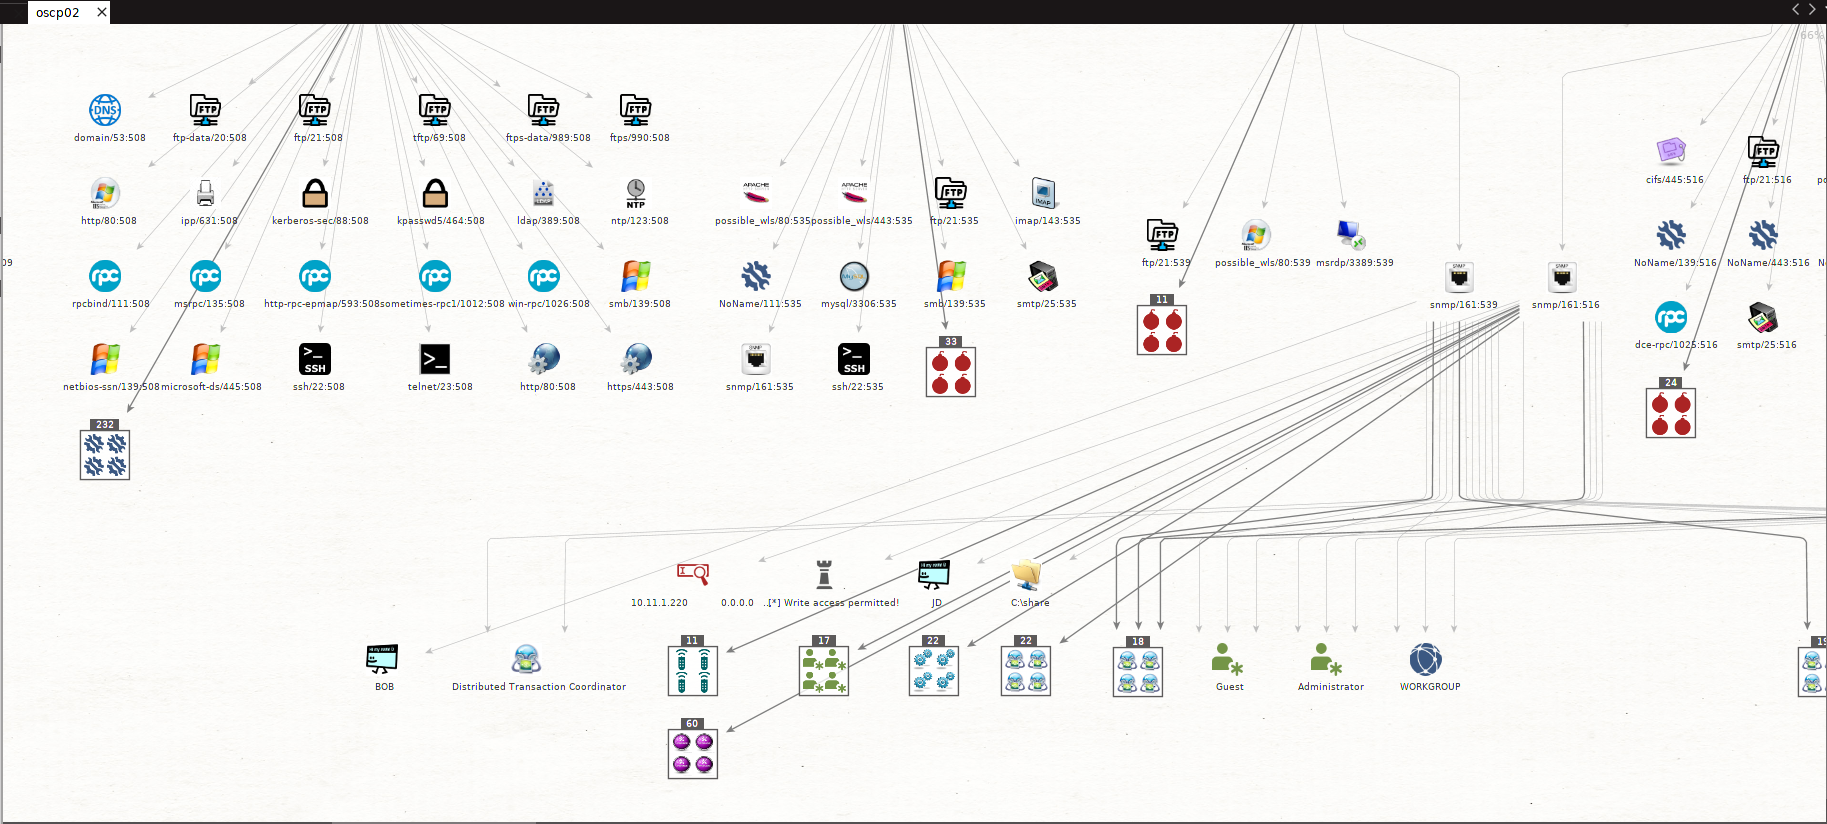 shizzz477/msploitego
Pentesting suite for Maltego based on data in a Metasploit database
 morpheuslord/nmap-api
RESTful API wrapping Nmap for automated network scanning, port detection, service enumeration, and vulnerability analysis with optional AI-powered…
 alexanderortizscript/evillcode
Herramienta de auditoría y análisis de redes para Kali Linux.
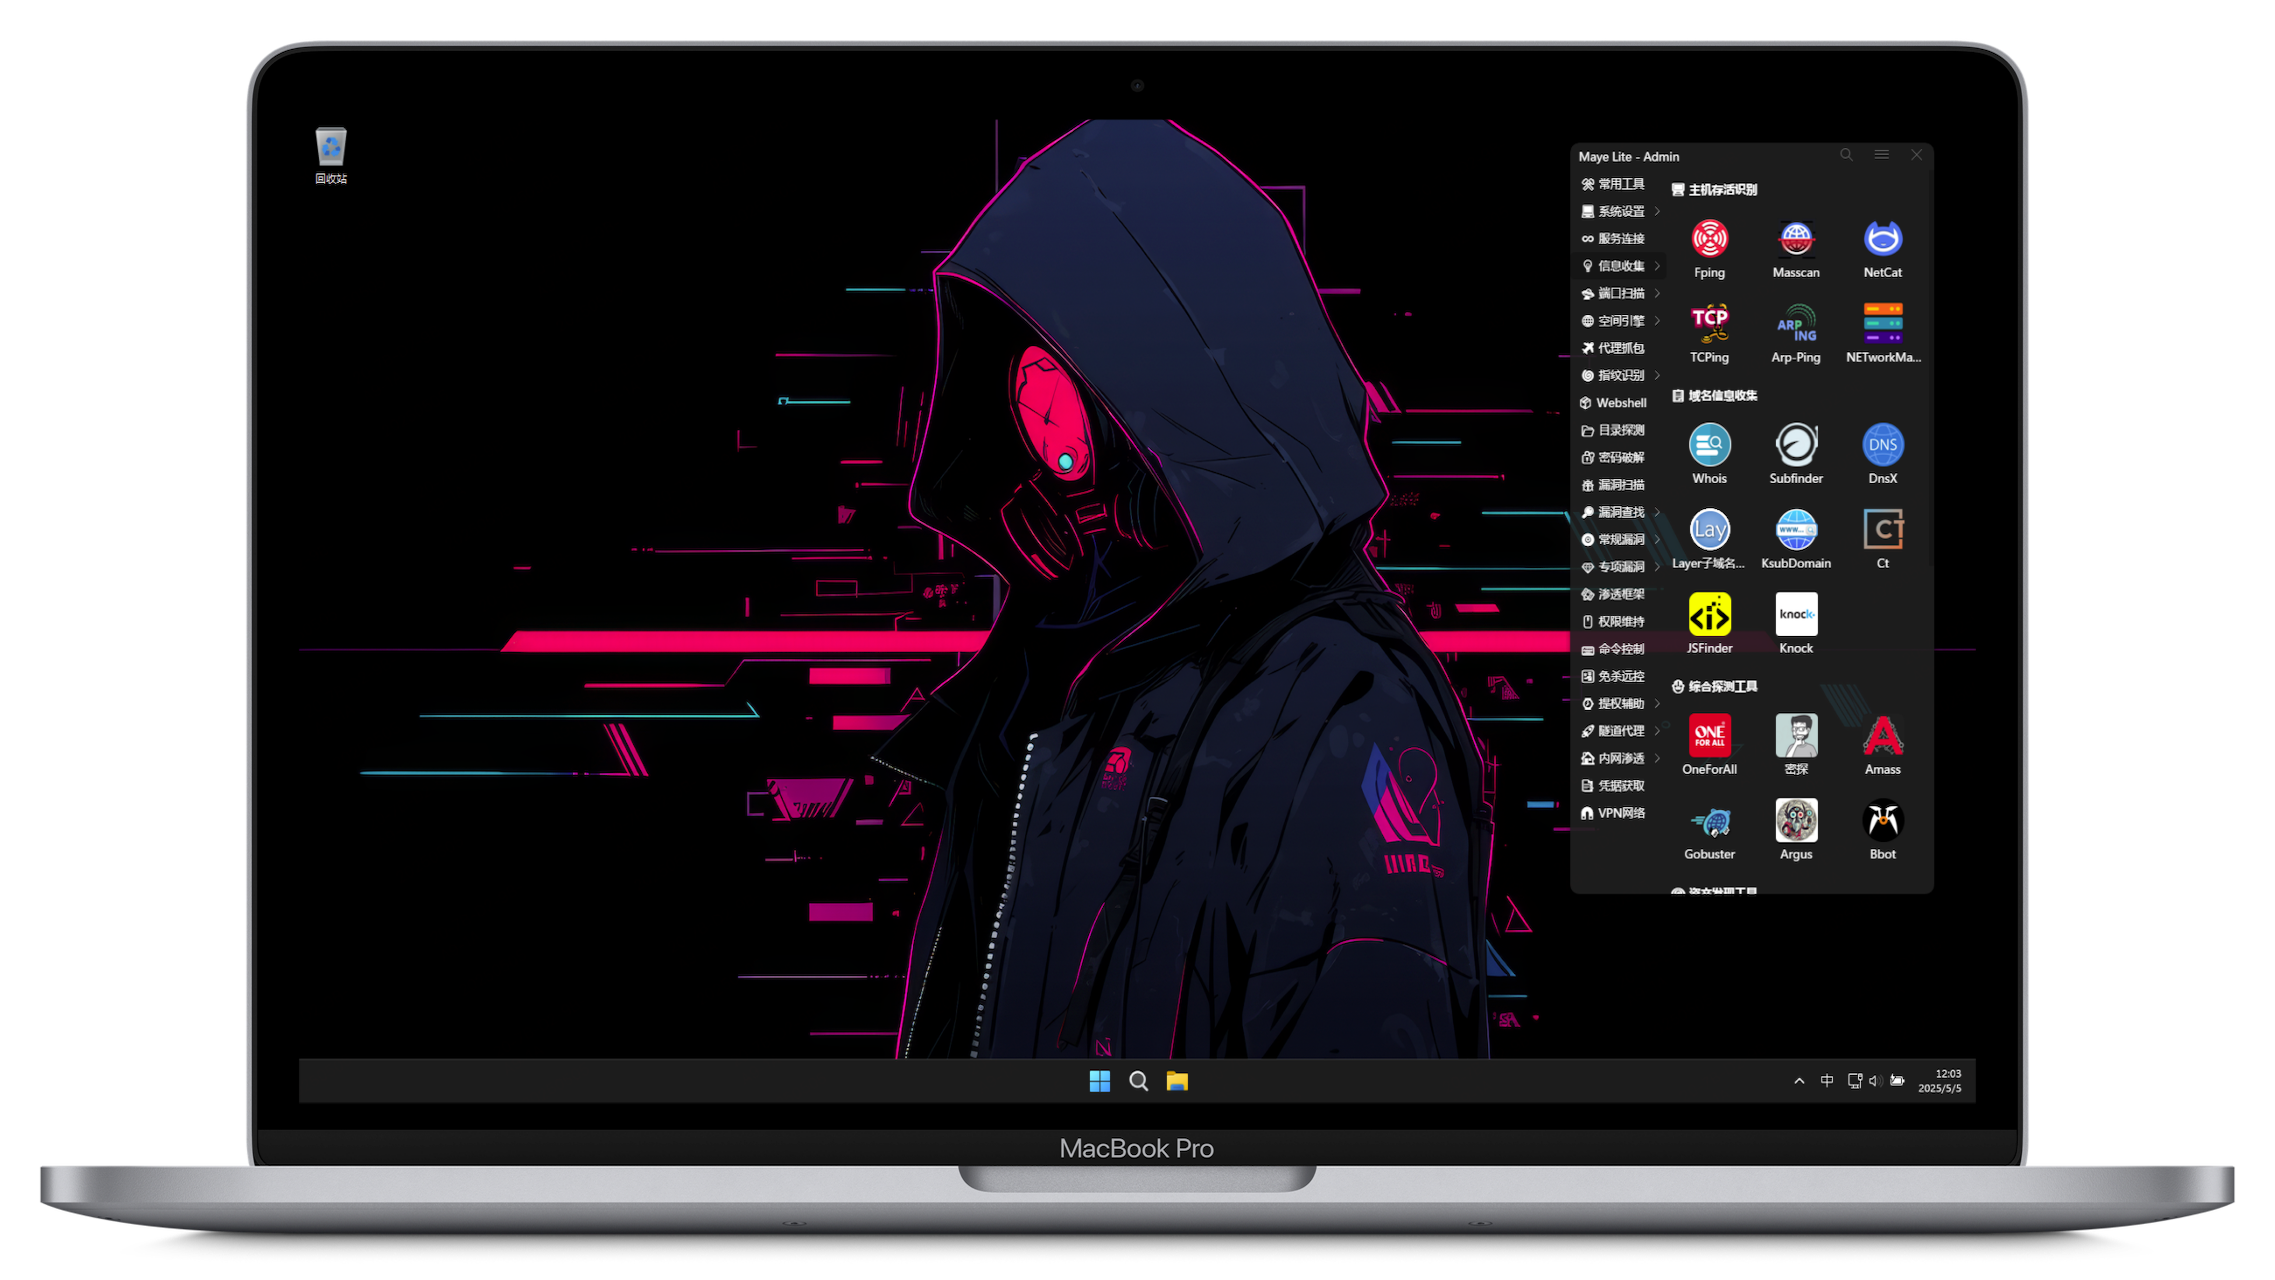 arch3rpro/pentest-windows
⚔️Windows11 Penetration Suite Toolkit 🔰 The First Windows Penetration Testing Environment on Mac M Chips
 eartoearoak/rtlsdr-scanner
A cross platform Python frequency scanning GUI for the OsmoSDR rtl-sdr library
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
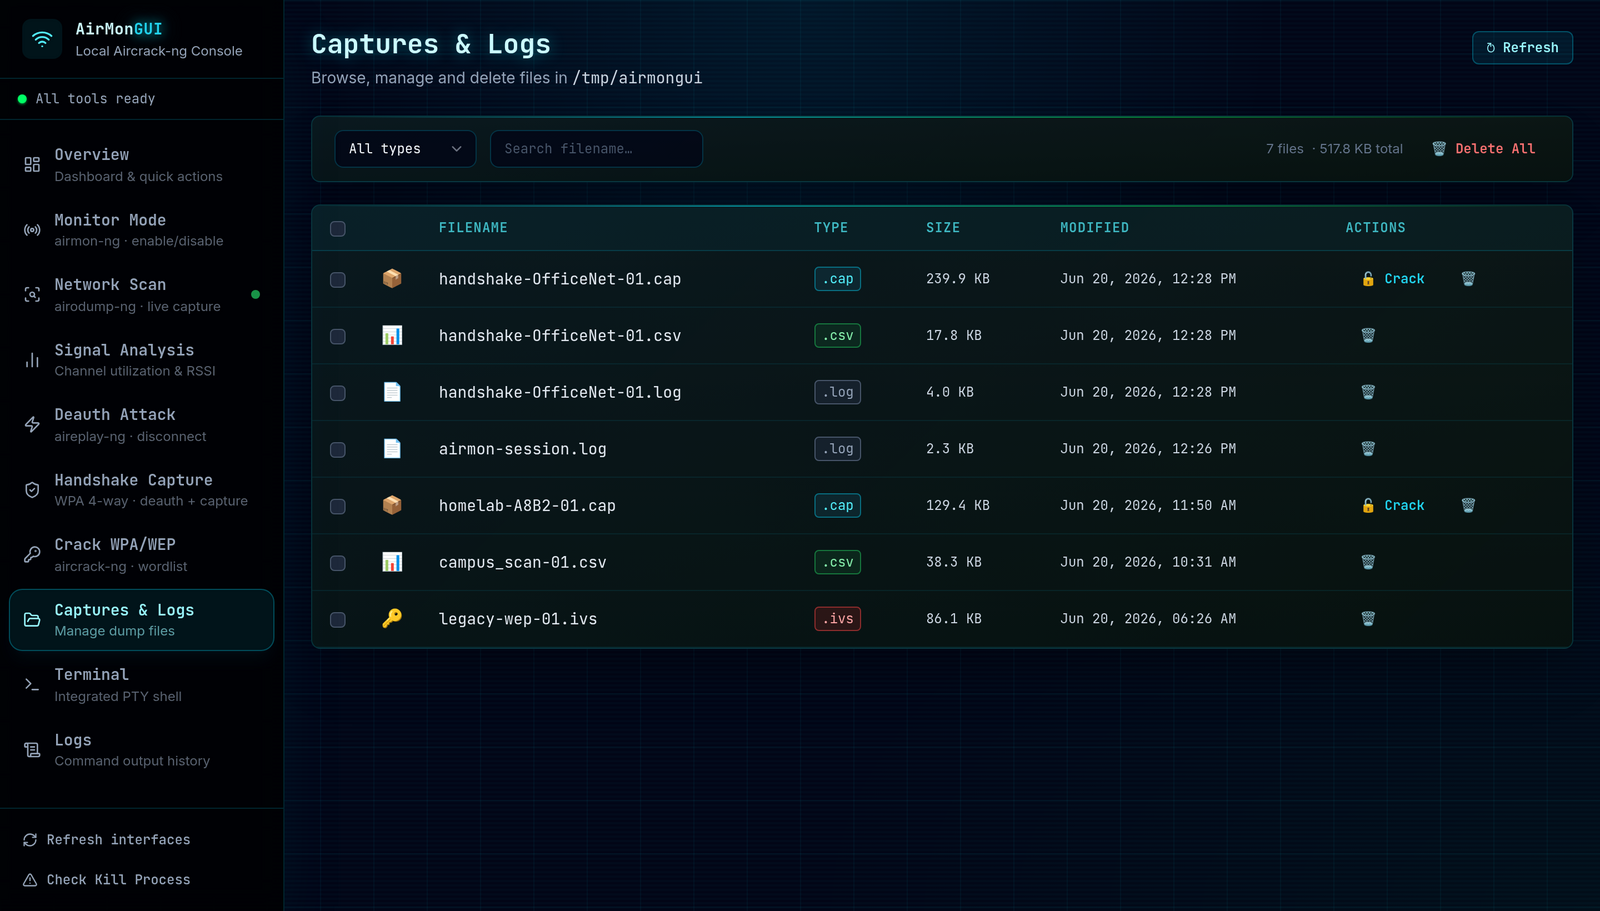 elhart05/airmongui
A locally-hosted GUI for the aircrack-ng wireless auditing suite.
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 sethwhy/bluedoor
Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…
 bitburner/ivre-wizard
An interactive wizard front end for IVRE to make creating scans to the database easier.
 hackhermind-pixel/vulnerable-lab-exploitation
A hands-on project demonstrating the setup of virtual security lab, network reconnaissance, and exploitation of CVE-2012-1823.
 vig9610/exploiting-samba-on-metasploitable-2
Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…