
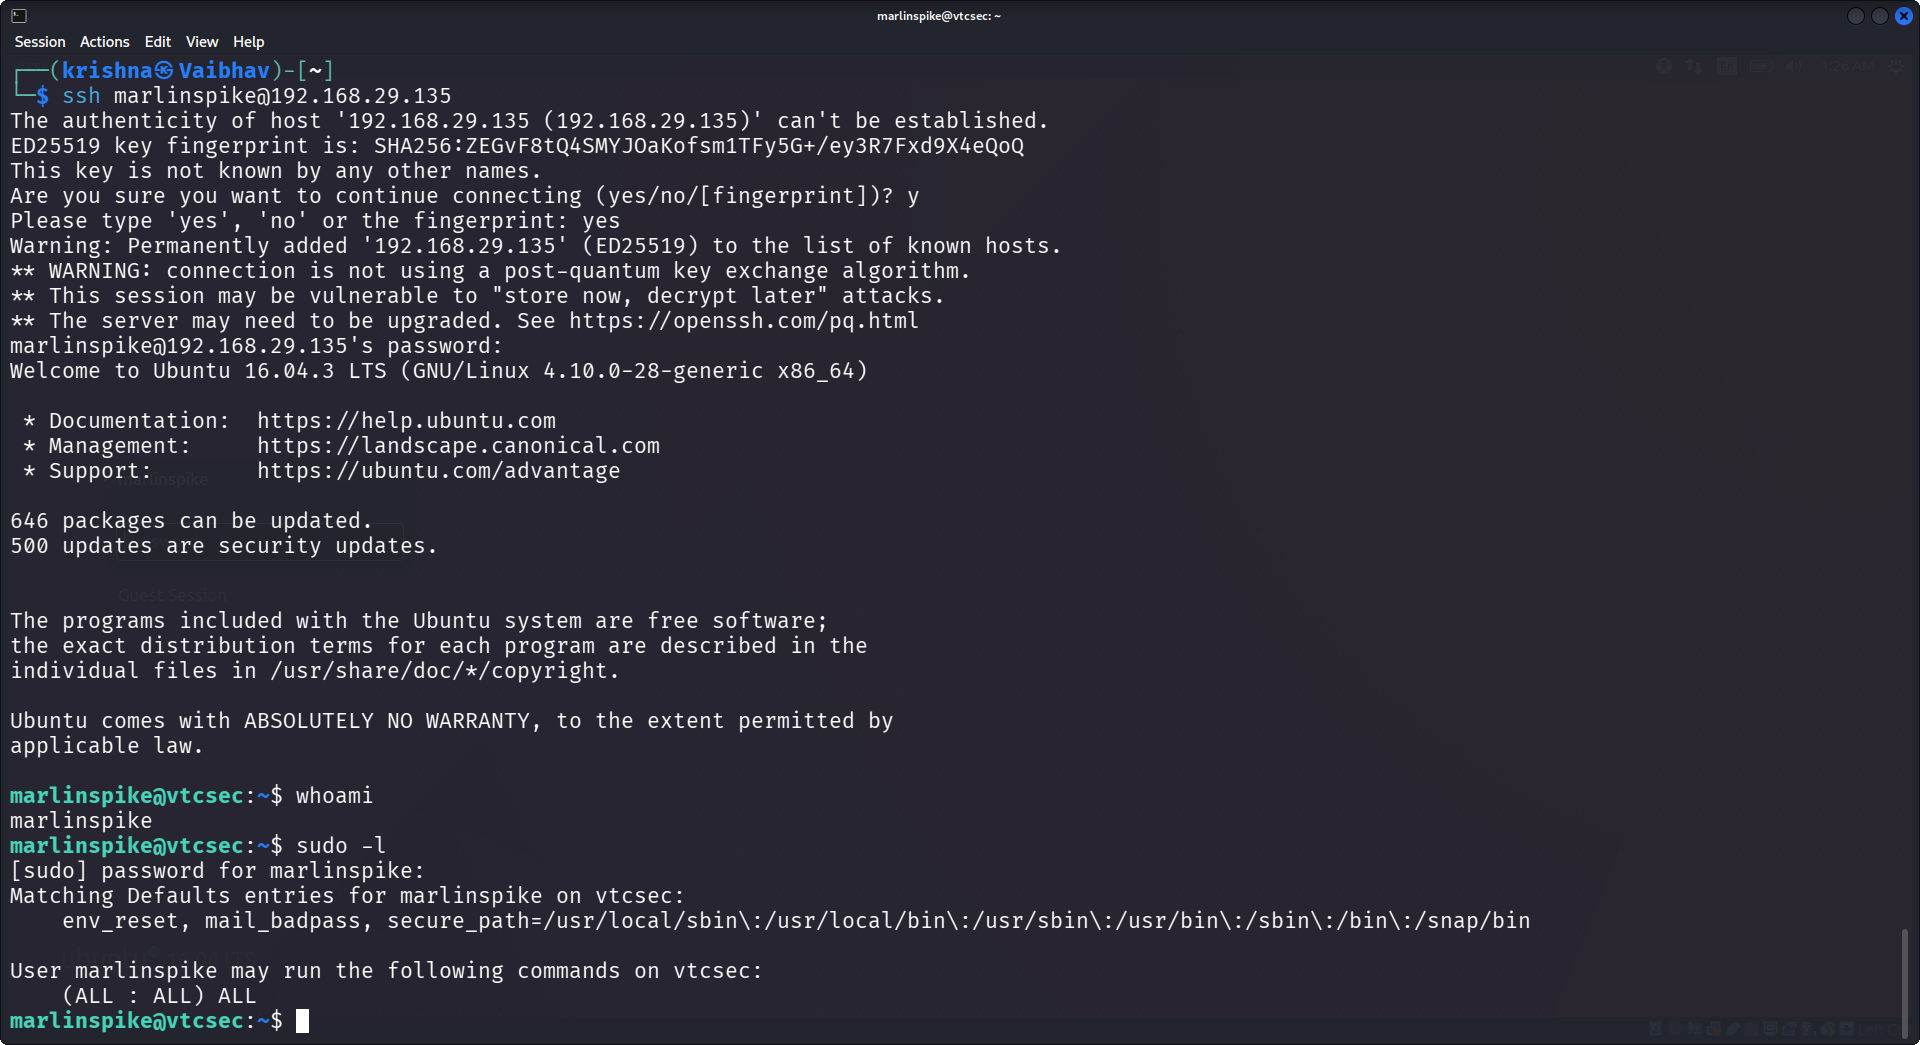
ubuntu-privesc-lab
 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
educationexploitationlabs-practice+8
vaibhavkrishna12004/ubuntu-privesc-labFull penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
 h3x0v3rl0rd/autonmap
Automated Nmap scanning script for Hack The Box, streamlining port enumeration and reconnaissance during penetration testing.
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
 cro-thehacker/v1ew-s0urce
Python-based penetration testing framework and reconnaissance toolkit offering port scanning, information gathering, and network scanning modules for…
 sabri-zaki/easy_hack
Hack the World using Termux
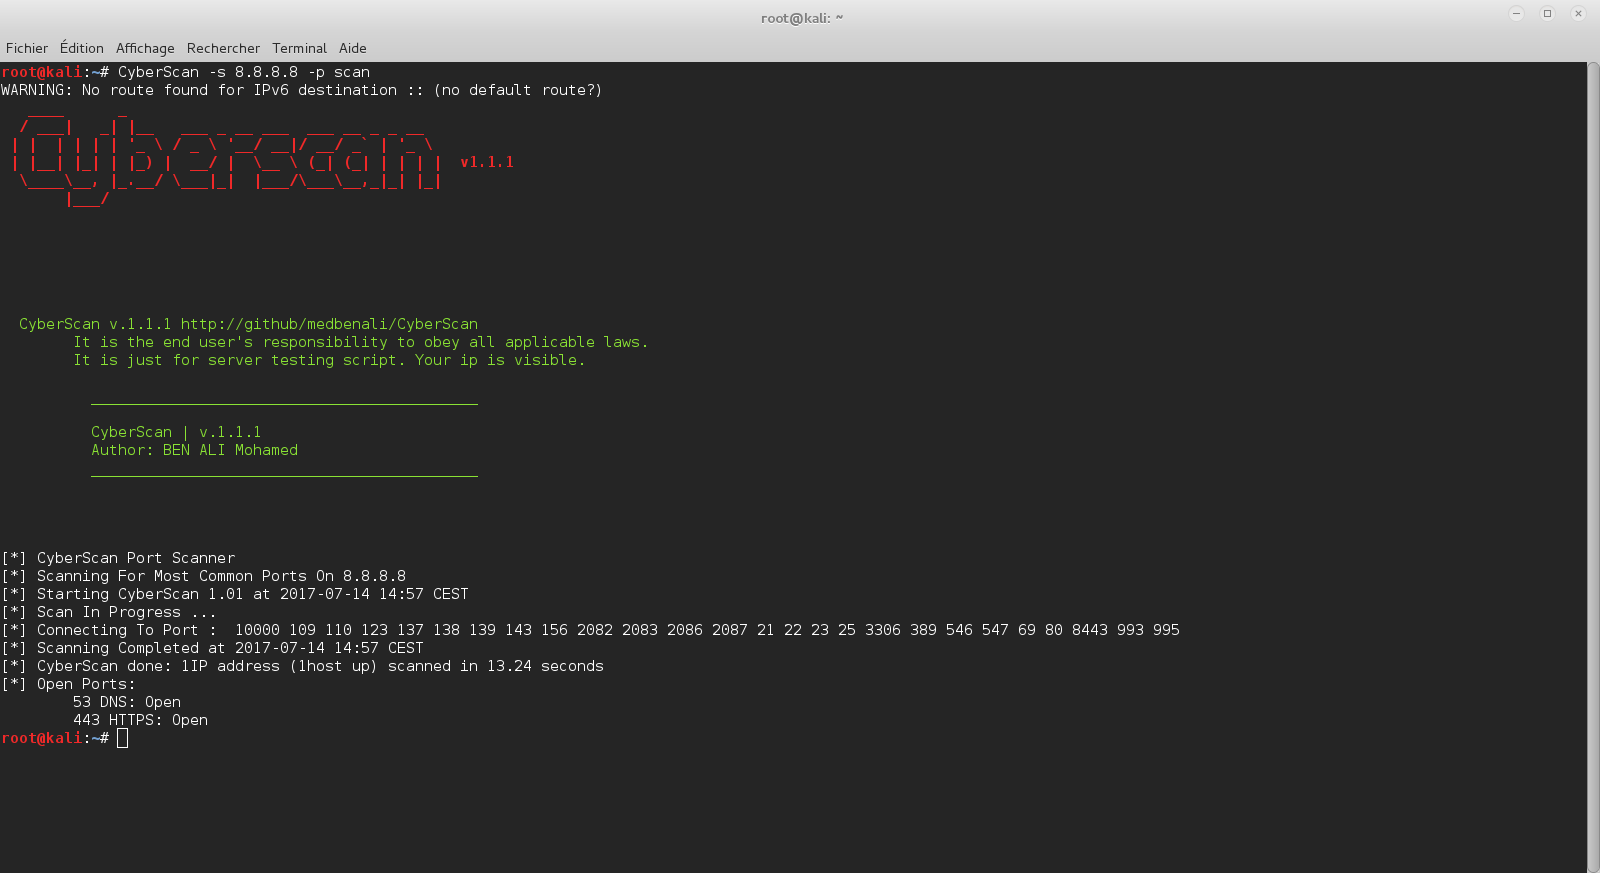 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 r3vn/badkarma
network reconnaissance toolkit
 sigploiter/gtscan
The Nmap Scanner for Telco
 blindfuzzy/lhf
A modular recon tool for pentesting
 jonnyhightower/neet
Neet - Network Enumeration and Exploitation Tool
 bishopfox/cirro
Creating attacks paths across management and data planes
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 hackhermind-pixel/vulnerable-lab-exploitation
A hands-on project demonstrating the setup of virtual security lab, network reconnaissance, and exploitation of CVE-2012-1823.
 rinaliyeva/metasploitable2-vsftpd-exploitation
Project: vsFTPd 2.3.4 backdoor exploitation (CVE-2011-2523) on Metasploitable 2.
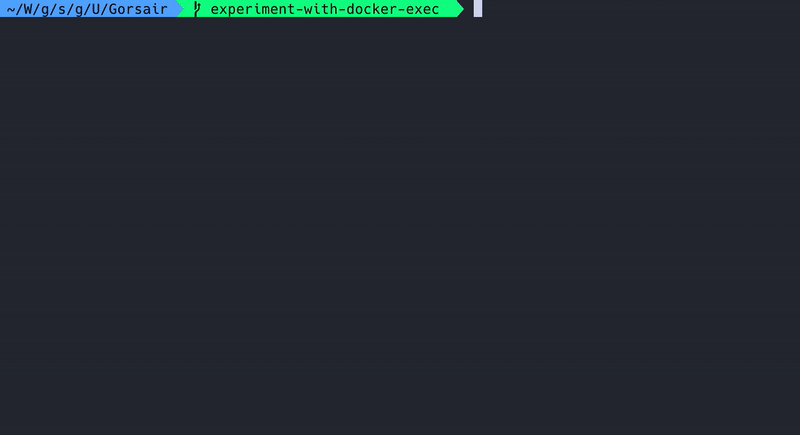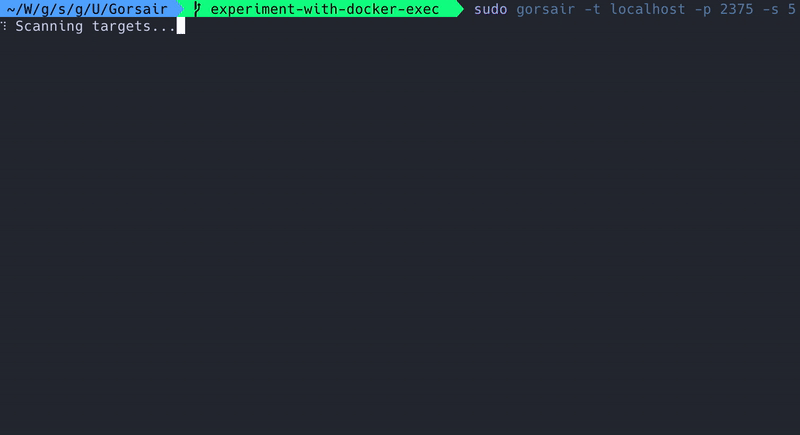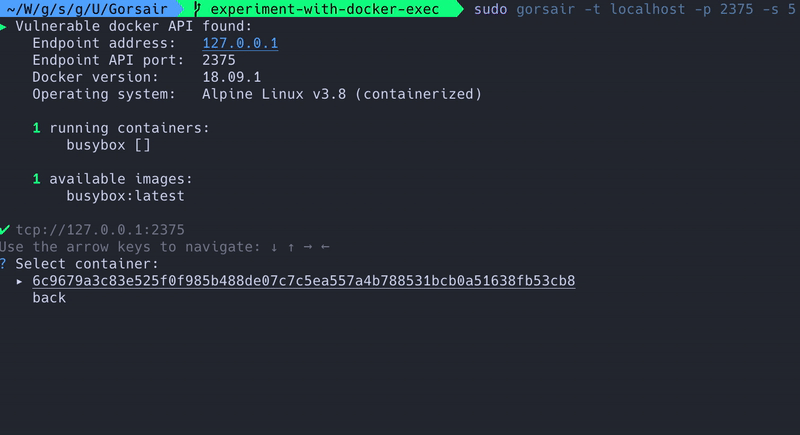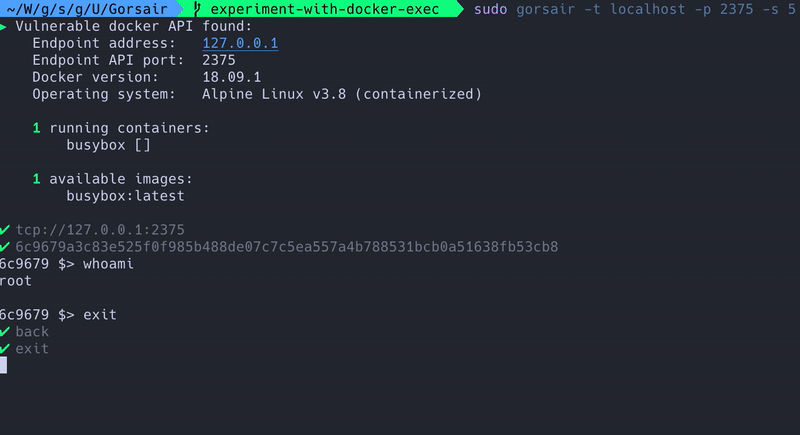 ullaakut/gorsair
Gorsair gives root access on remote docker containers that expose their APIs
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…