

zeek
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
anomaly-detectionanti-botdefensive-tools+14
zeek/zeekZeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 davidhavoc/ayaflow
A high-performance, eBPF-based network traffic analyzer written in Rust.
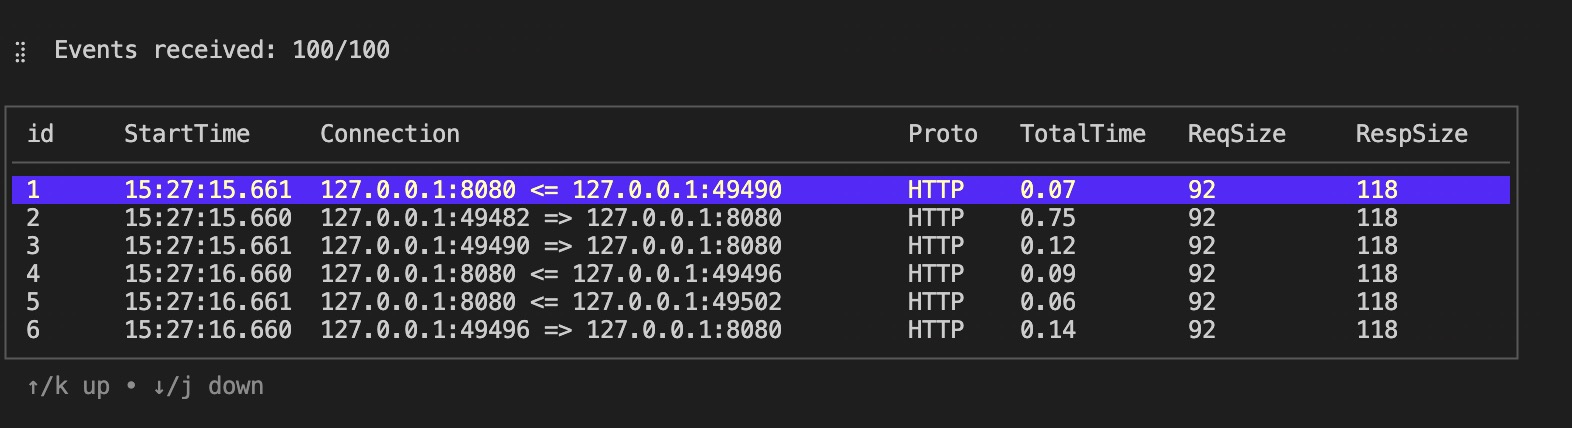 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
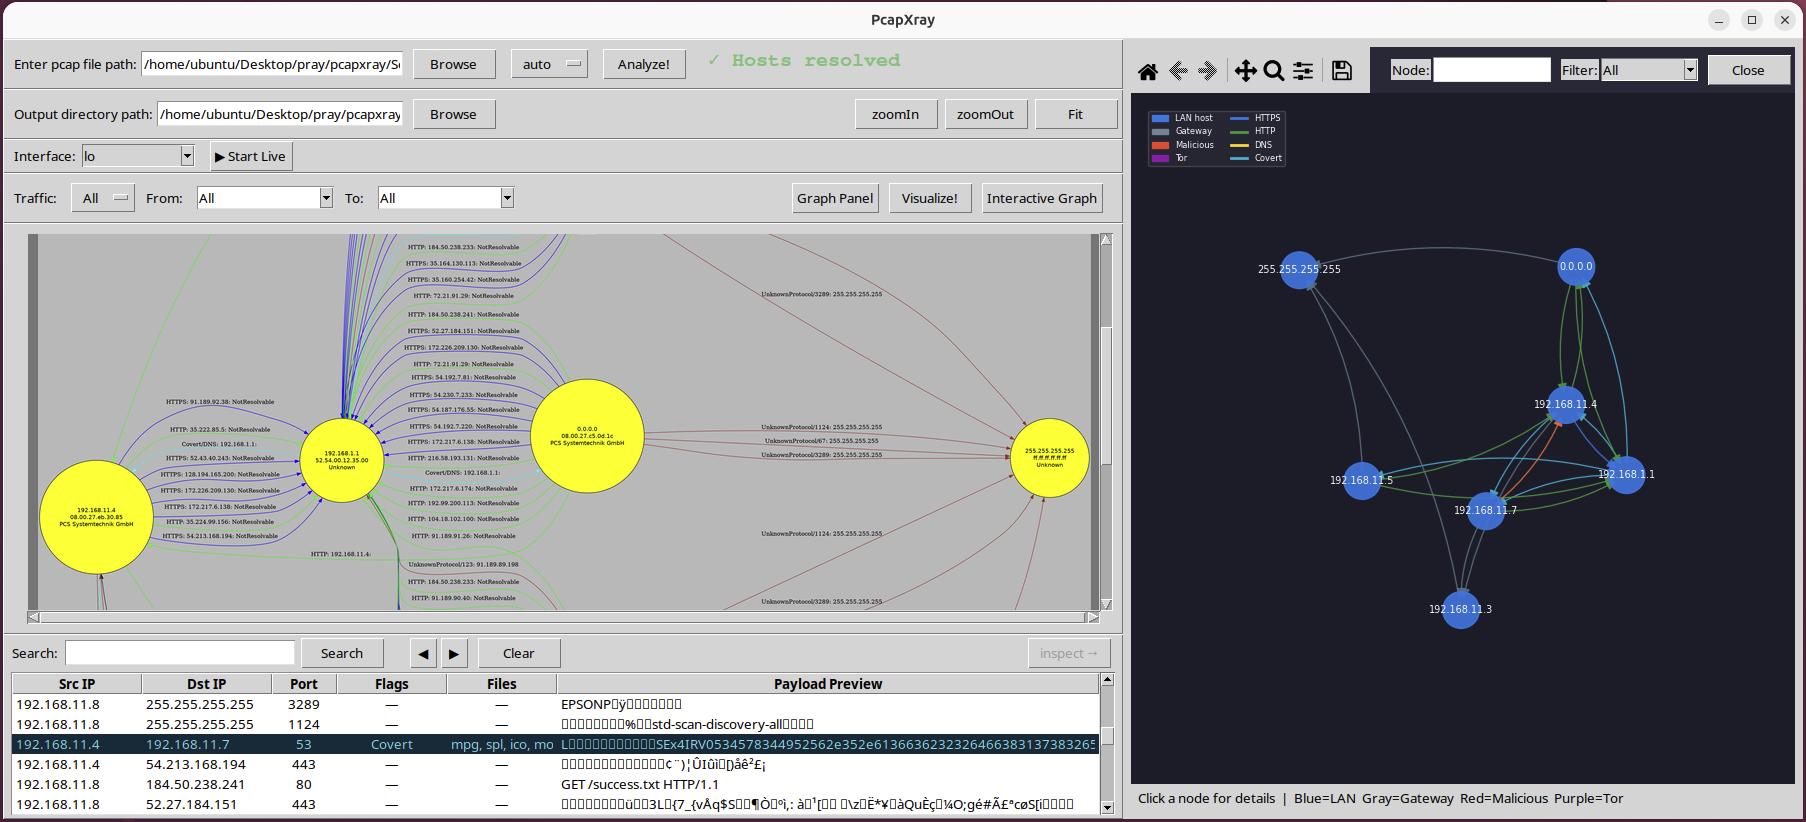 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
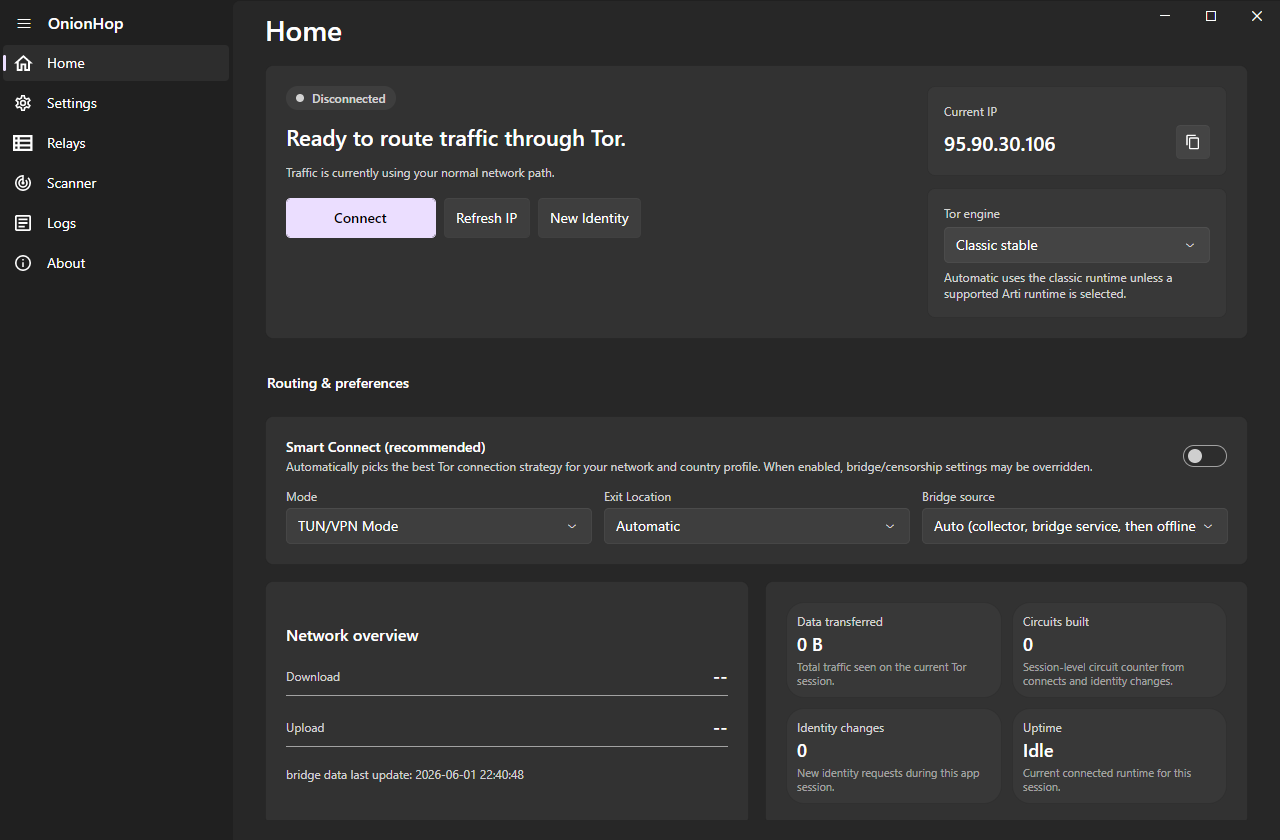 center2055/onionhop
Privacy-first Desktop app that routes your traffic through Tor - Anonymous browsing made simple
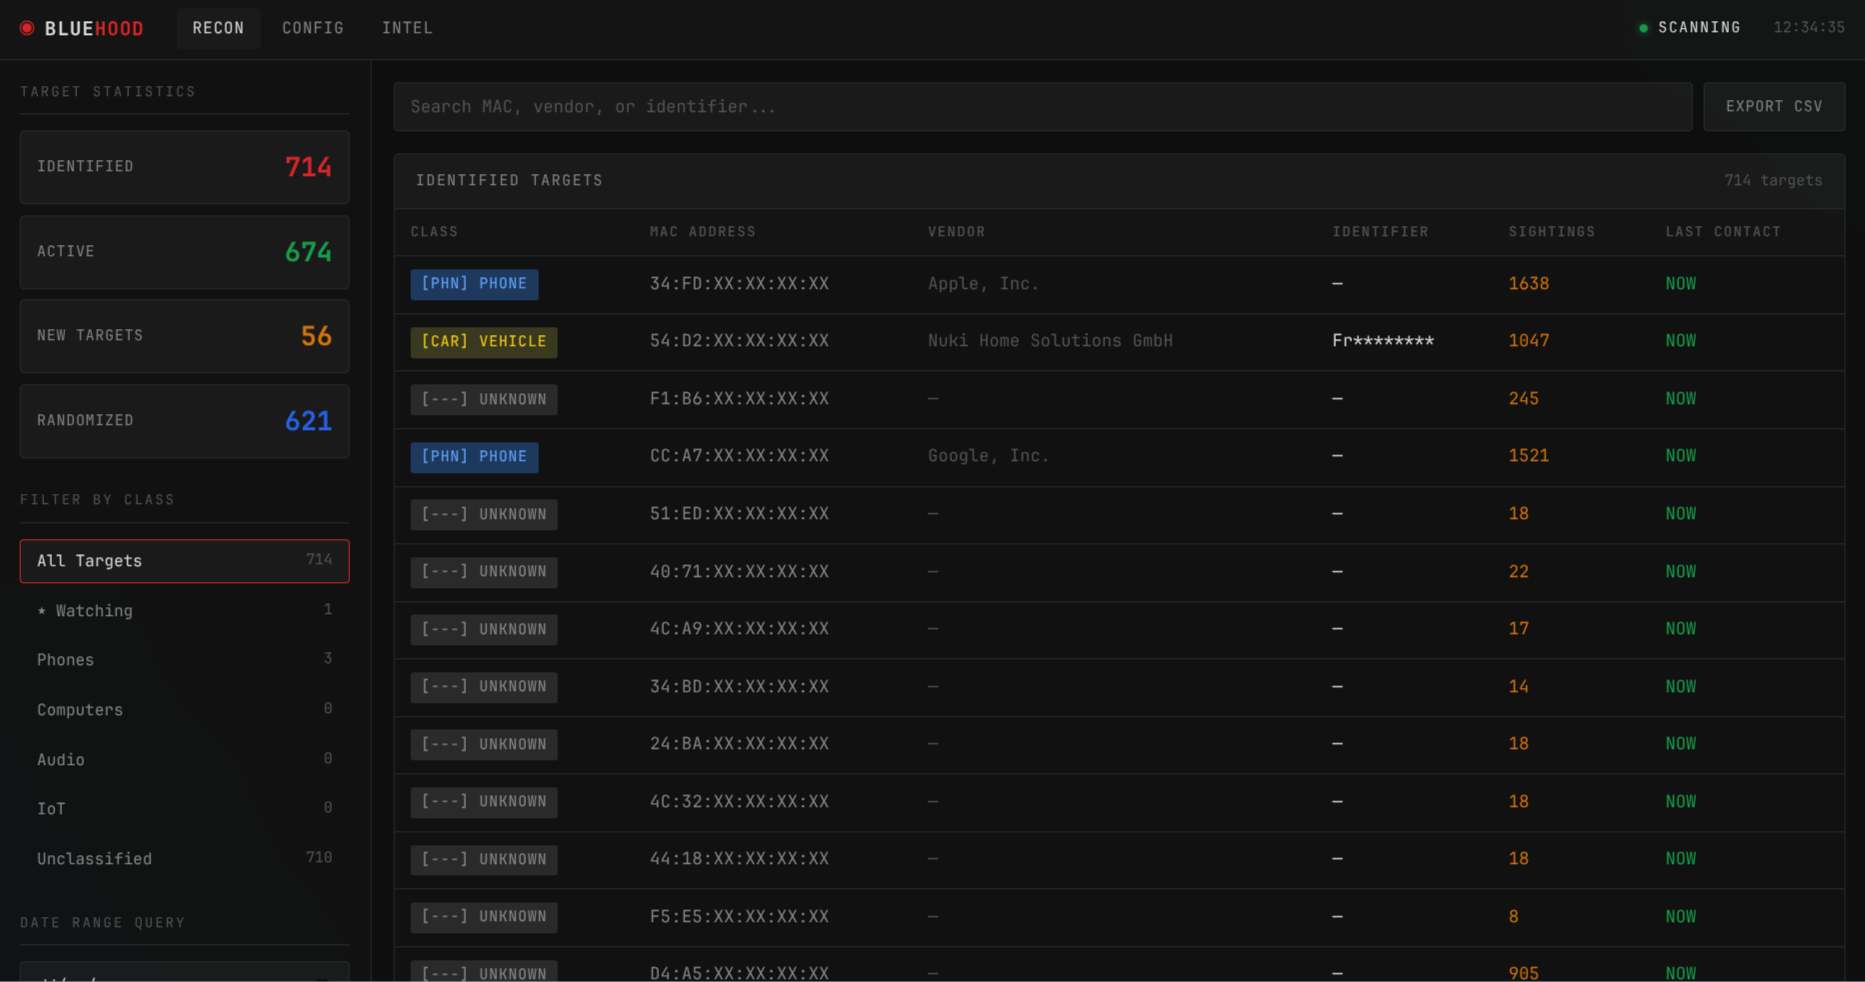 dannymcc/bluehood
Monitor your local neighbourhood's bluetooth activity
 m0vi0/pacmap
Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
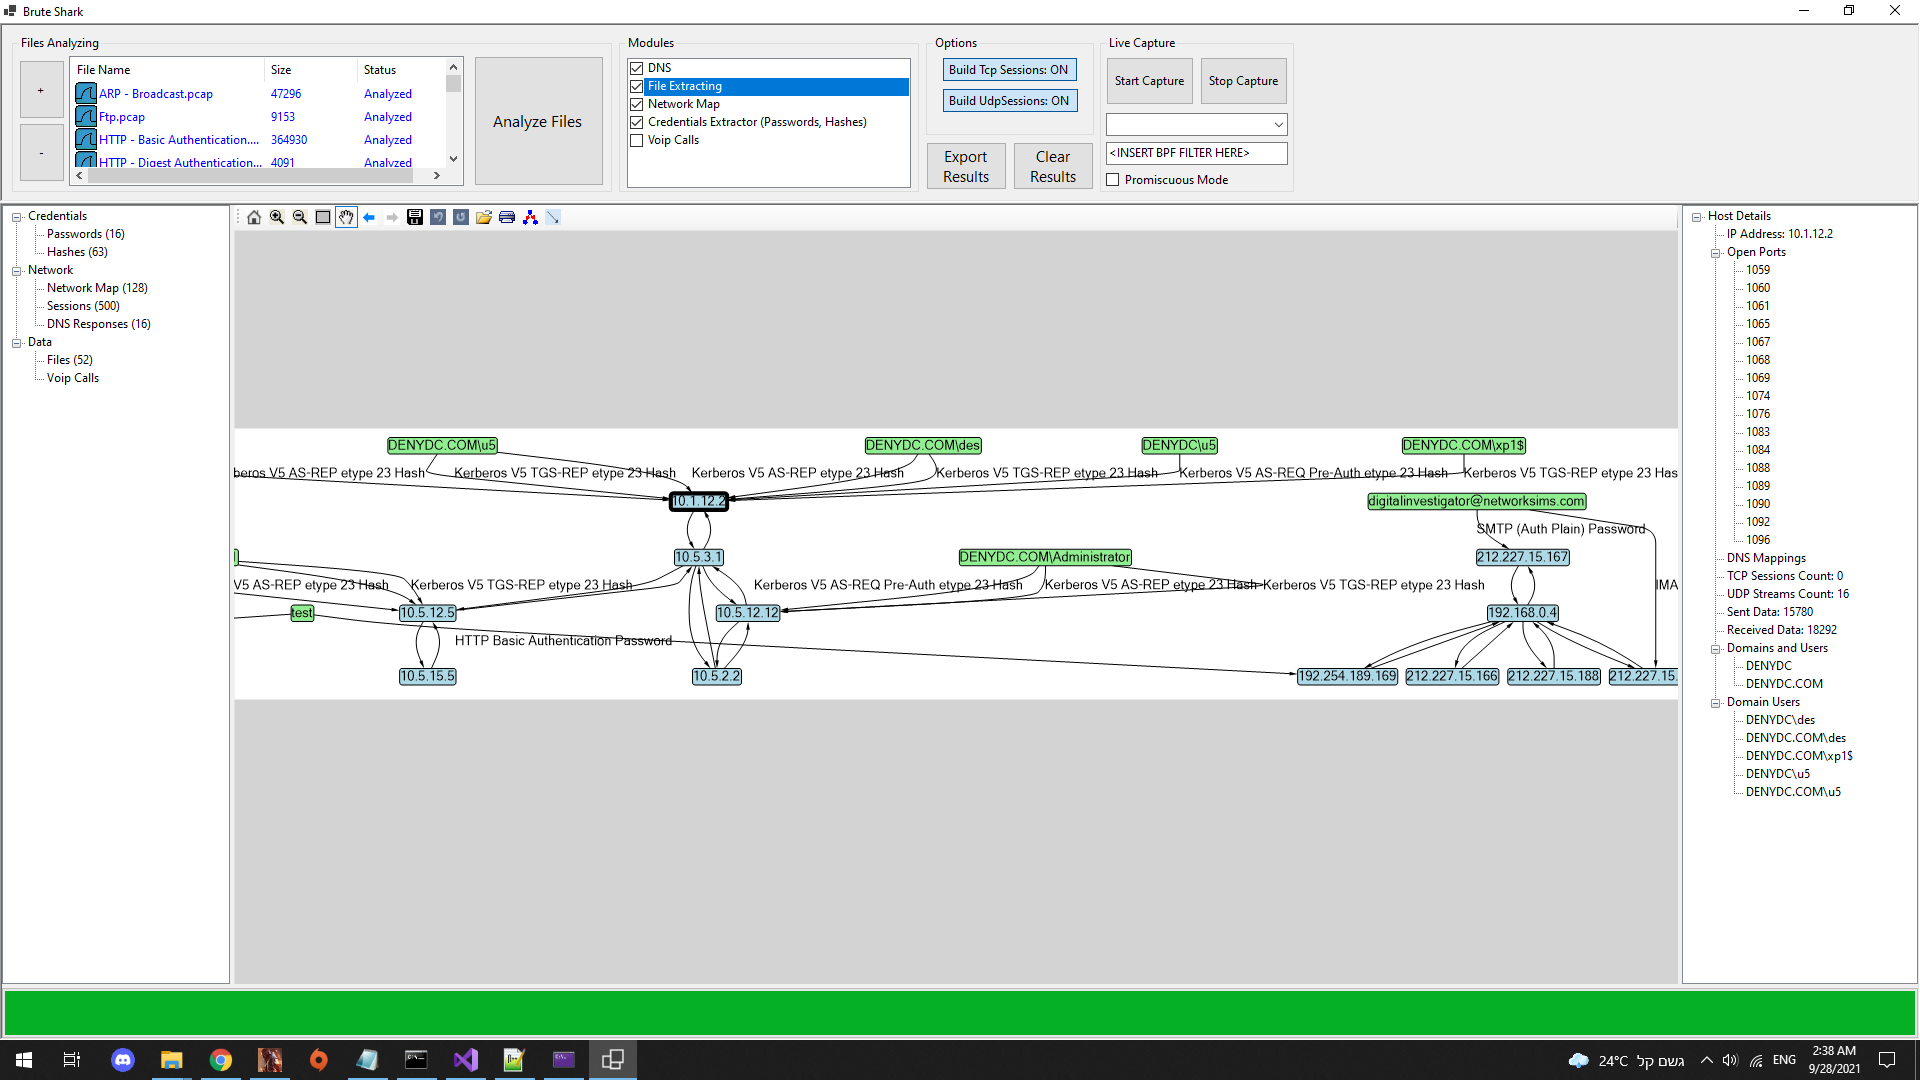
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
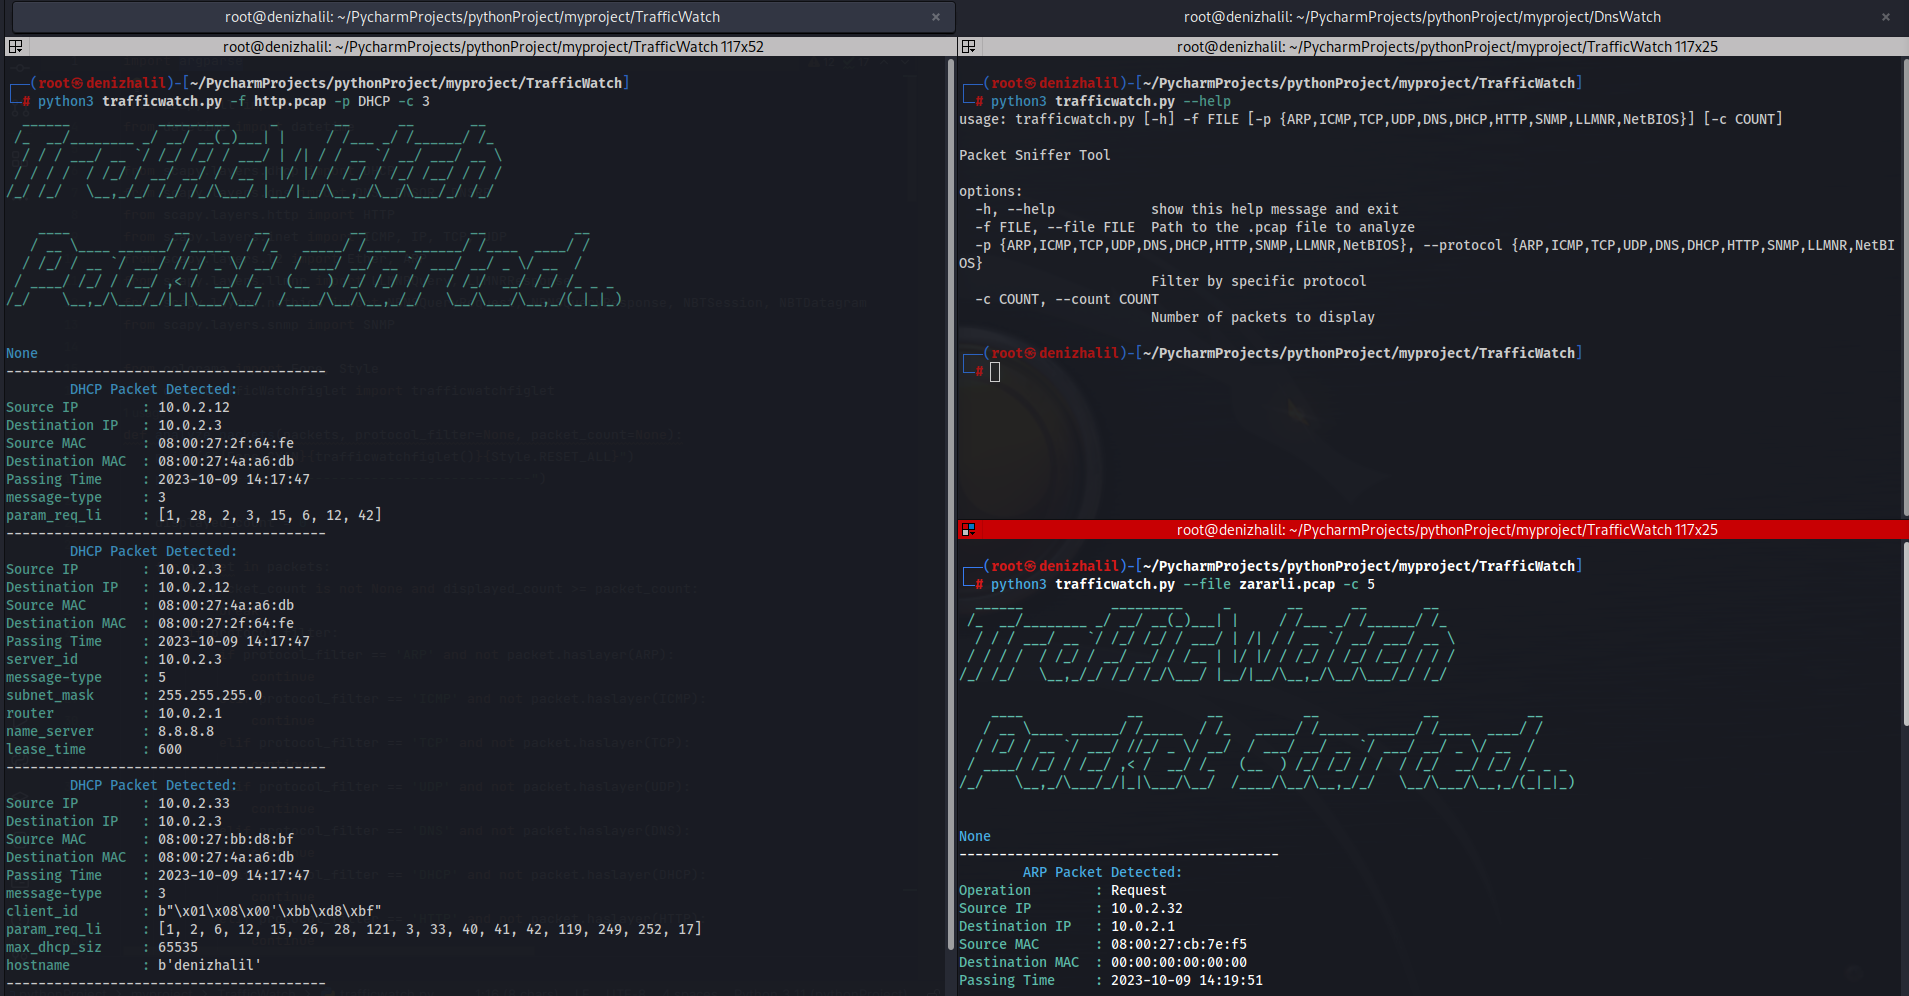 halildeniz/trafficwatch
PCAP-based packet sniffer and analyzer supporting ARP, ICMP, TCP, UDP, DNS, DHCP, HTTP, SNMP, LLMNR, and NetBIOS protocol inspection with filtering…
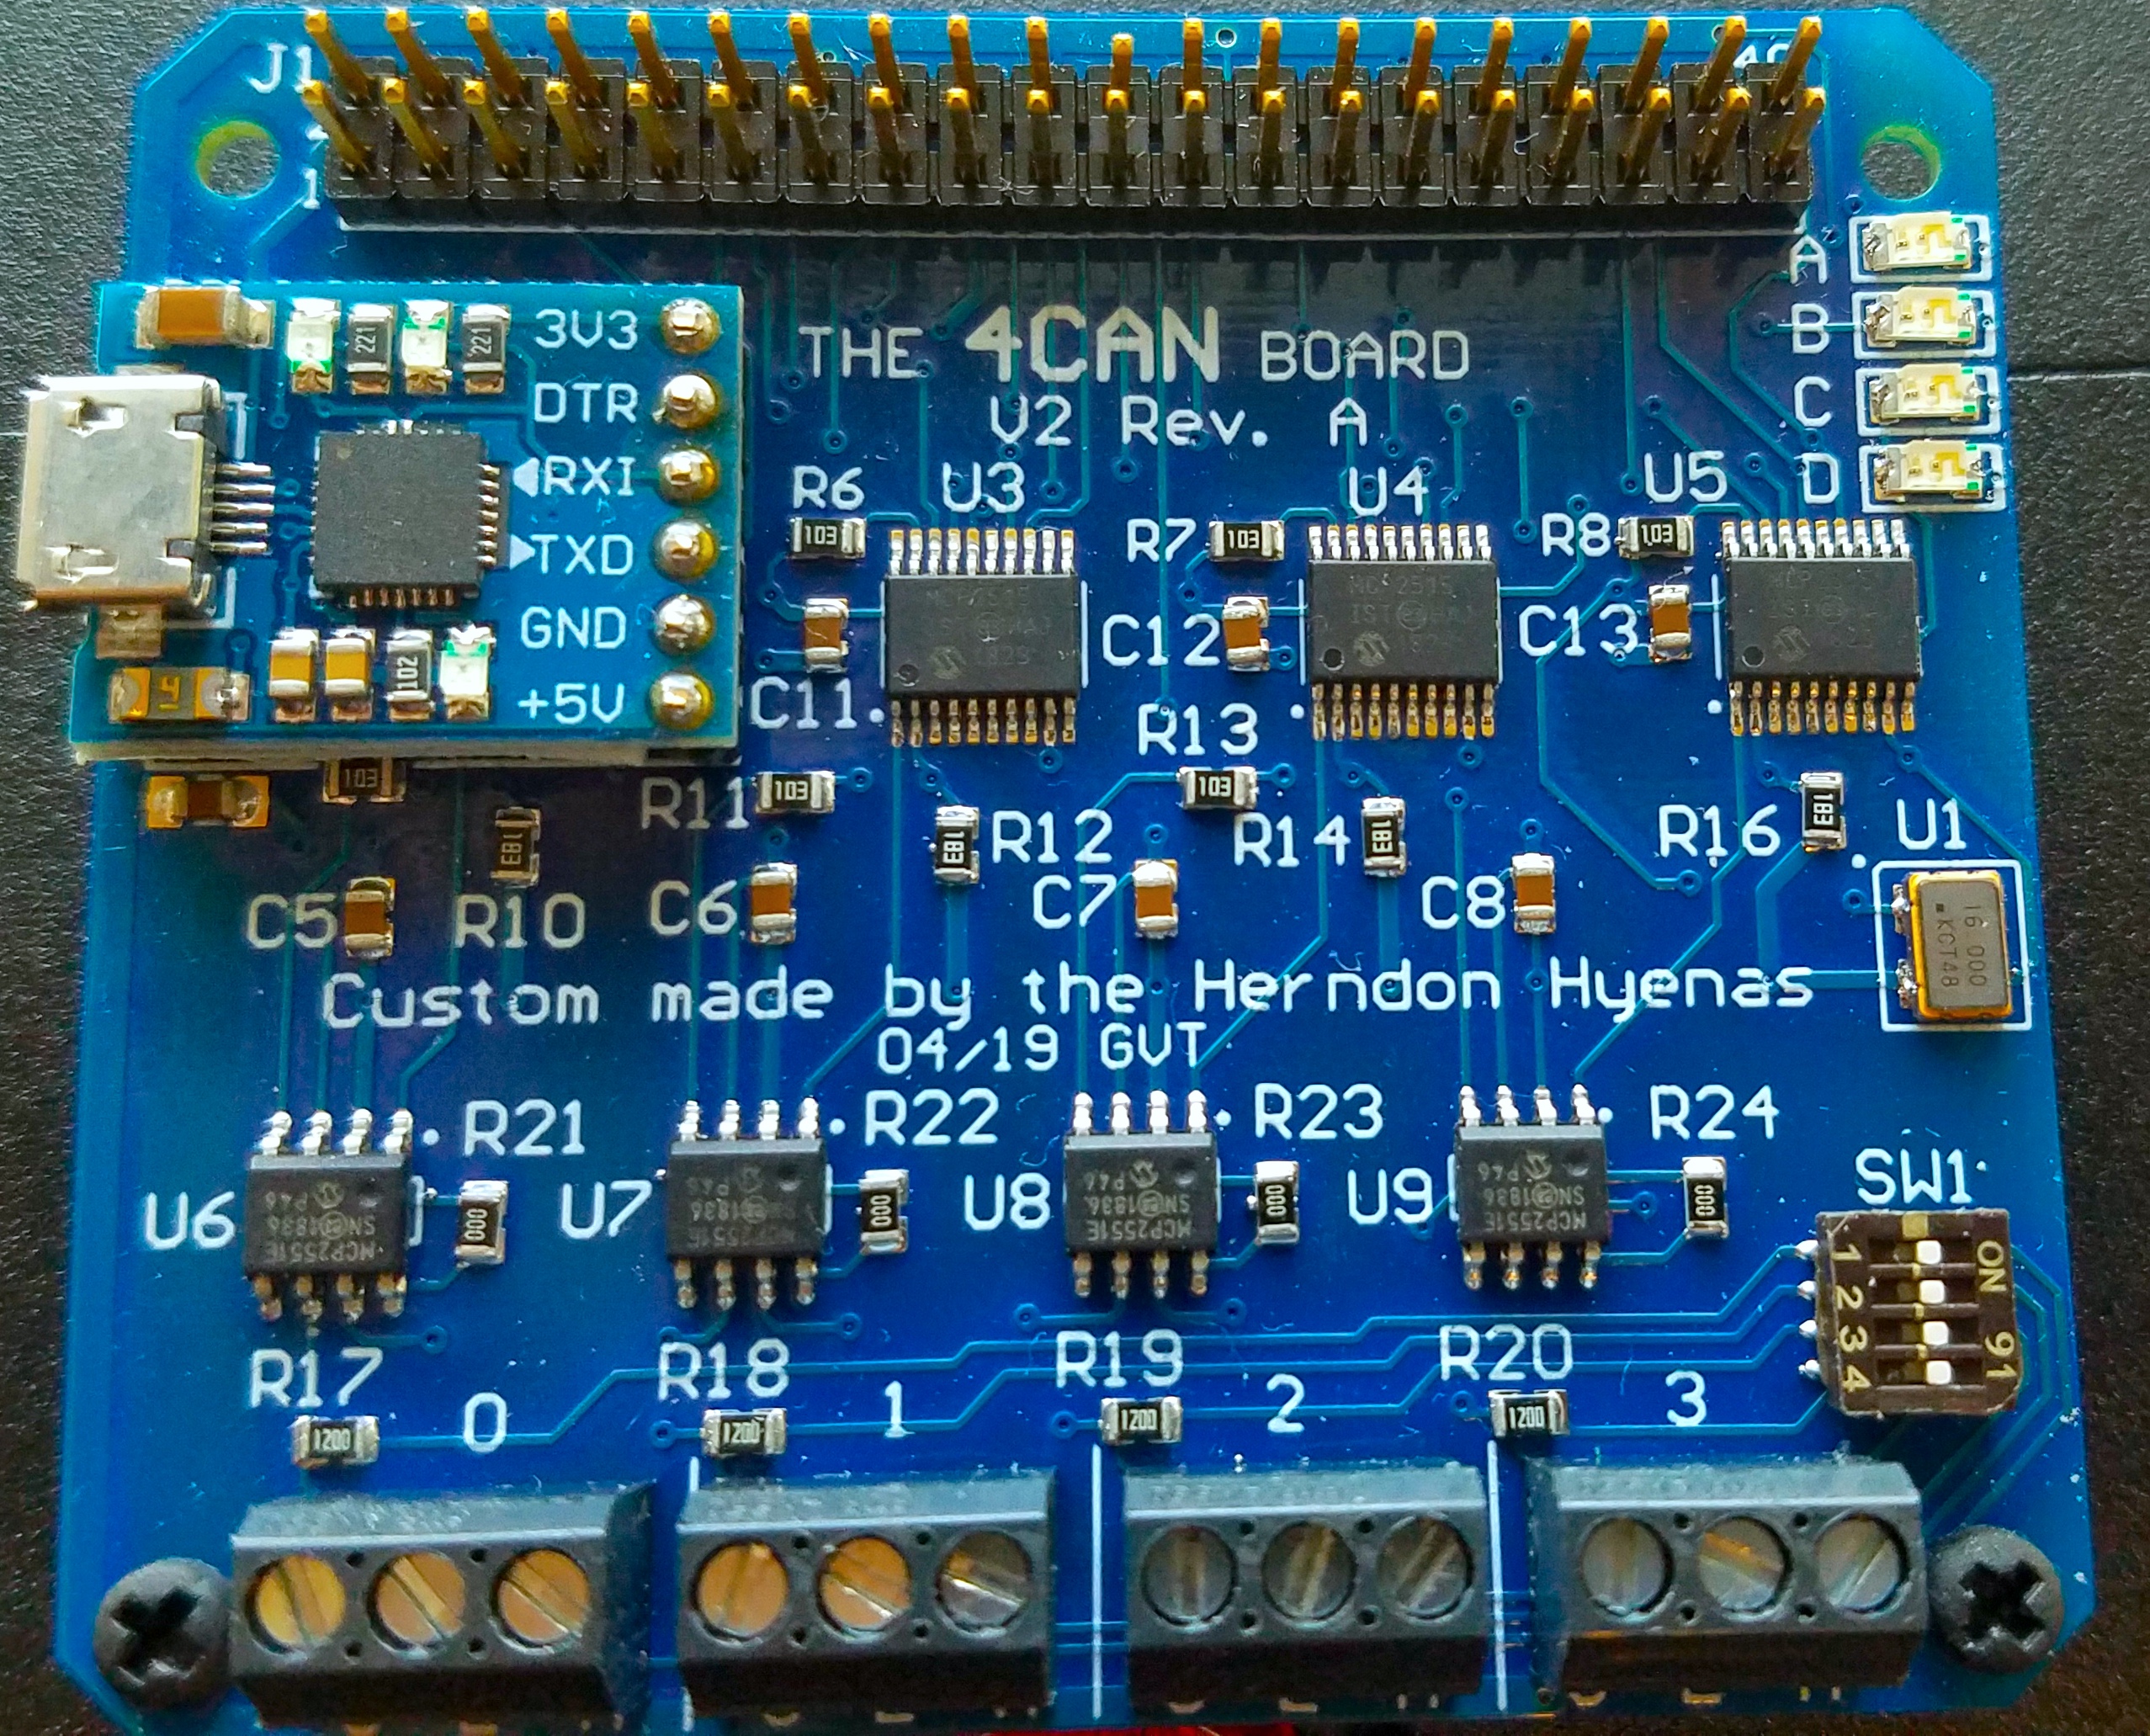 alexdetrano/4can
Open-source Raspberry Pi HAT providing 4 CAN interfaces for automotive bus testing, CAN-in-the-middle attacks, and simultaneous multi-bus traffic…
 lsecqt/portforwarder
TCP Port Forwarding Utility on C