
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
64 results
BlueFish preview

BlueFish

GitHubemrekybs/bluefish

Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
forensicsincident-responseinformation-gathering+2
20
5 months ago
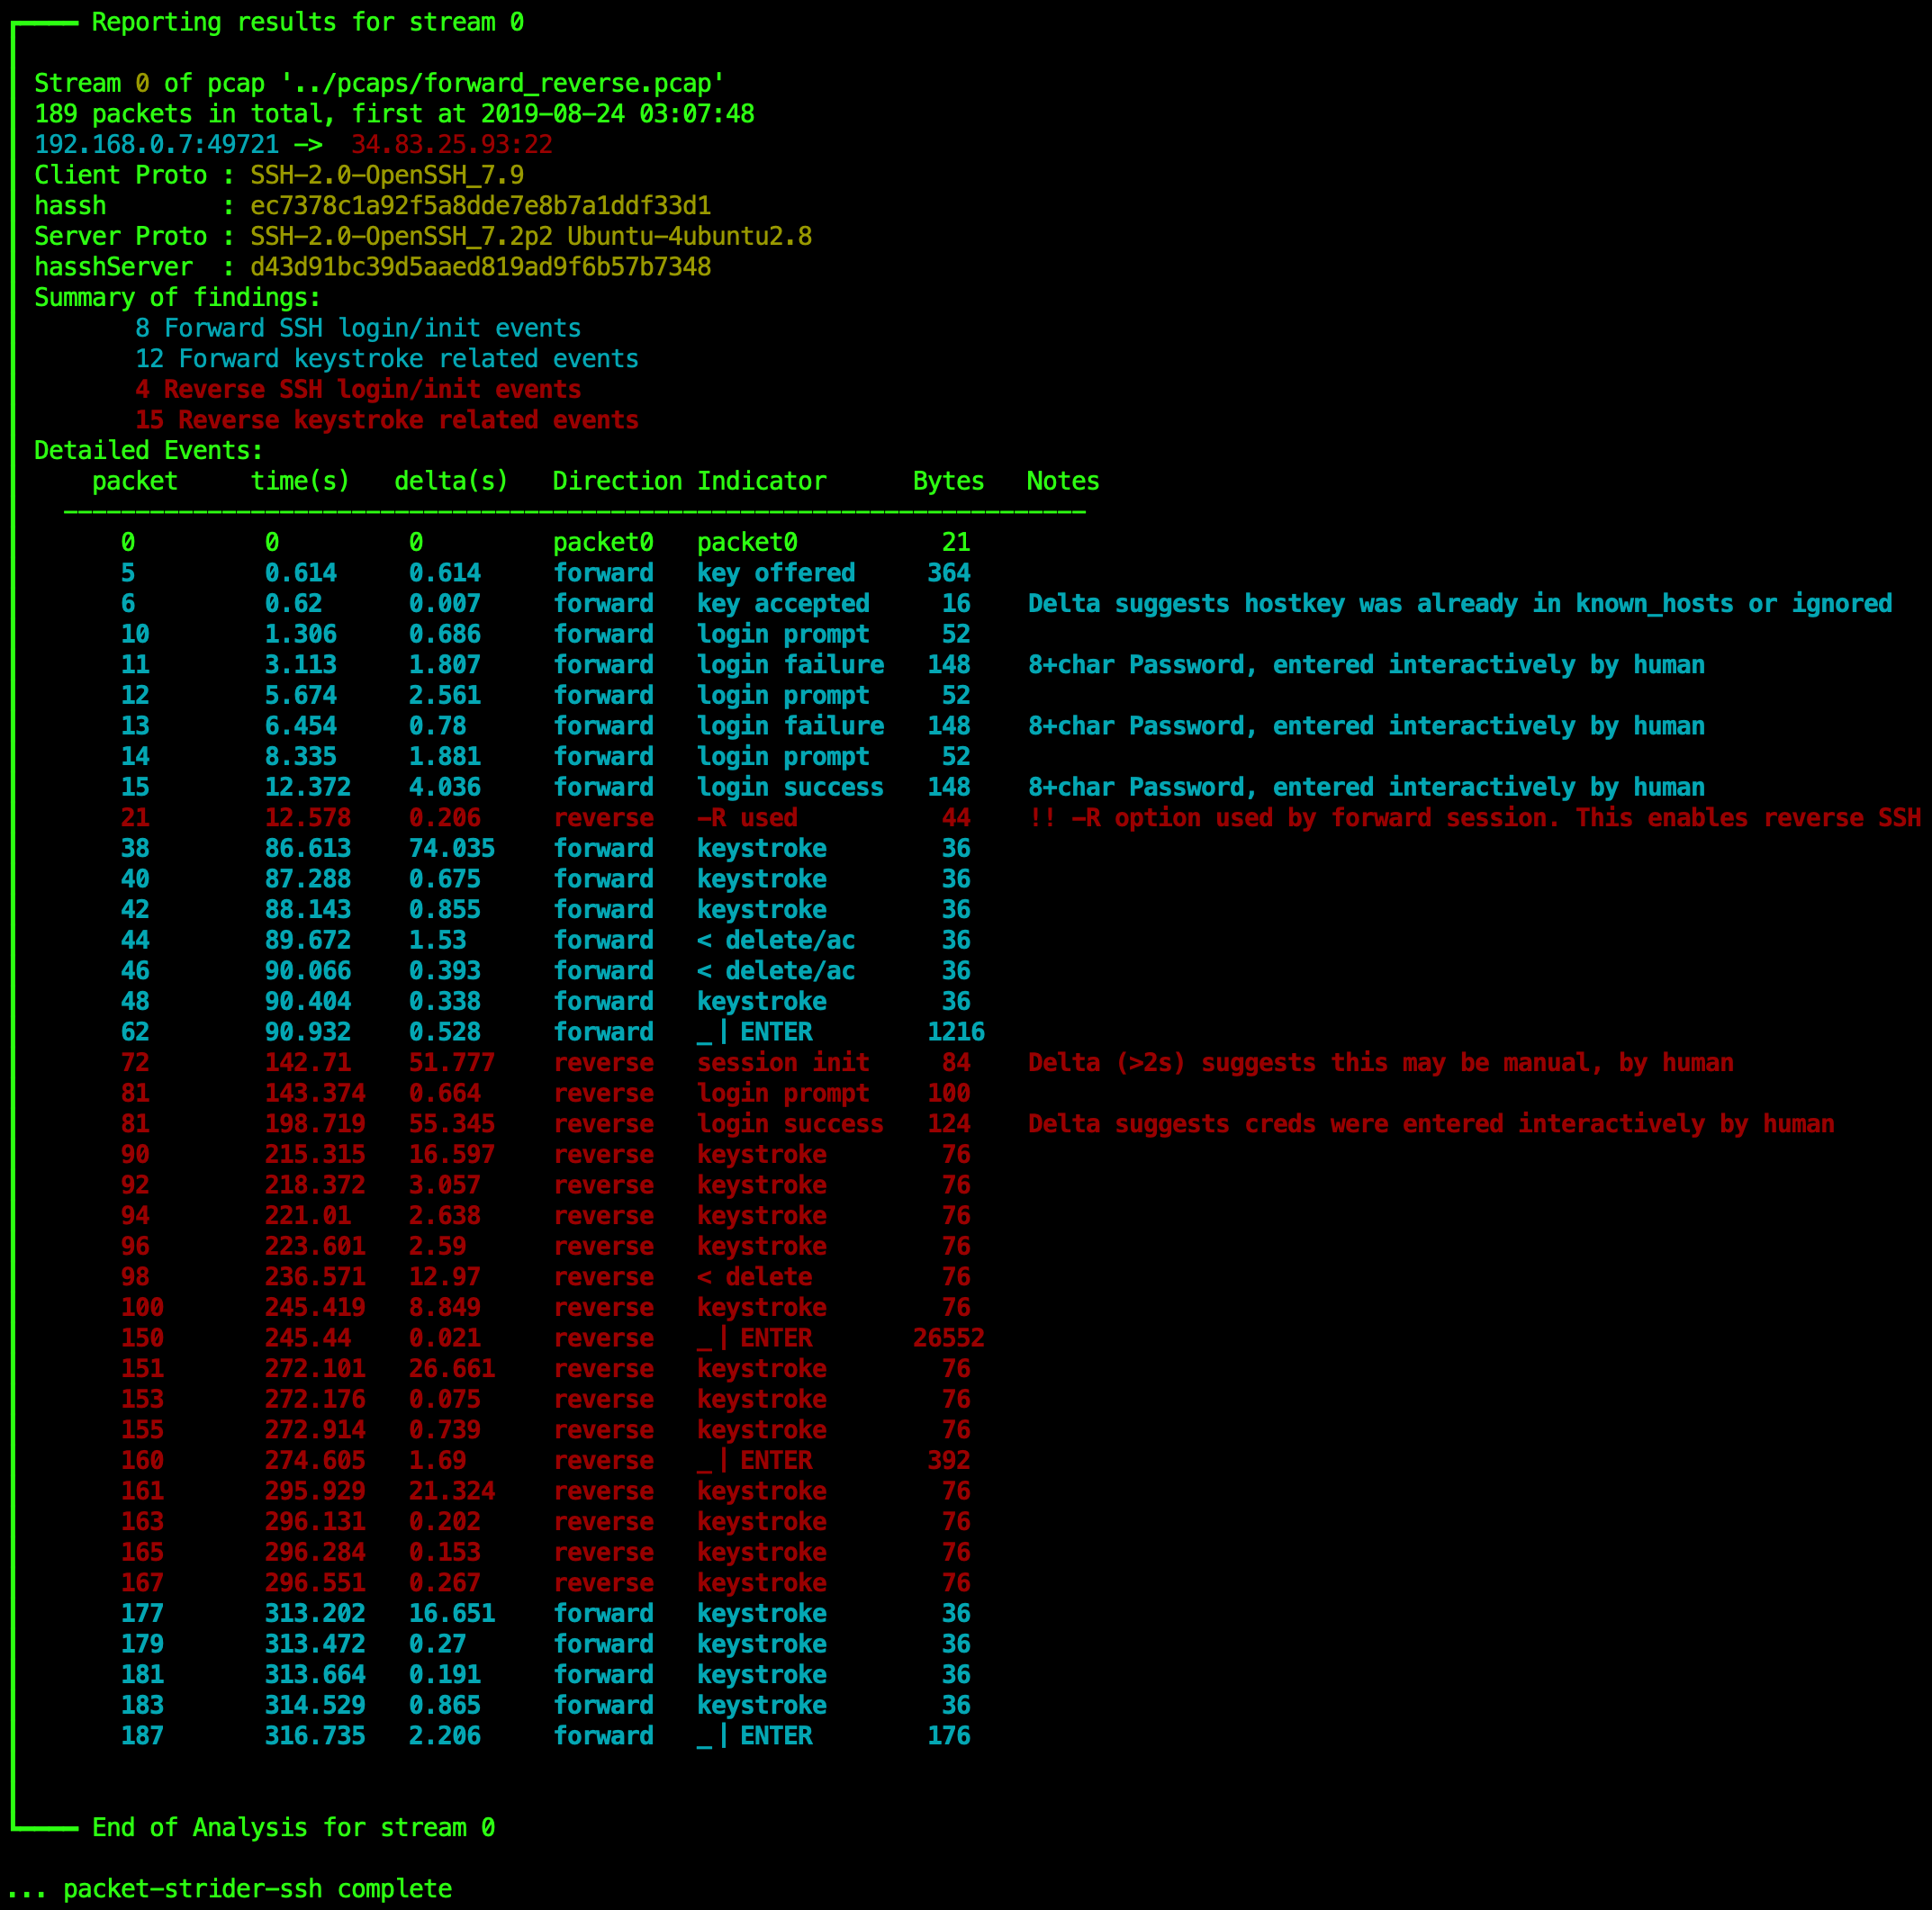
packetStrider preview

packetStrider

GitHubbenjeems/packetstrider

A network packet forensics tool for SSH

anomaly-detectionforensicsintrusion-detection+5
2556 years ago
caronte preview

caronte

GitHubeciavatta/caronte

A tool to analyze the network flow during attack/defence Capture the Flag competitions
ctfforensicsnetwork-forensics+1
6514 years ago
Bryobio preview

Bryobio

GitHubemrekybs/bryobio

It was developed to speed up the processes of SOC Analysts during analysis
forensicsinformation-gatheringnetwork-forensics+3
485 months ago
drovorub-hunt preview

drovorub-hunt

GitHubinsane-forensics/drovorub-hunt

A tool to assist with network-based hunting for GRU's Drovorub malware c2

incident-responseintrusion-detectionmalware-analysis+3
256 years ago
IpGeo preview

IpGeo

GitHubz4l4mi/ipgeo

Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
information-gatheringnetwork-forensicsosint+1
1323 years ago
Blue-Team-Notes preview

Blue-Team-Notes

GitHubpurp1ew0lf/blue-team-notes

You didn't think I'd go and leave the blue team out, right?
curated-resourcesdigital-forensicseducation+5
1.8k5 days ago
Dshell preview

Dshell

GitHubusarmyresearchlab/dshell

Dshell is a network forensic analysis framework.
digital-forensicsdns-analysisforensics+3
5.5k2 years ago
detux preview

detux

GitHubdetuxsandbox/detux

The Multiplatform Linux Sandbox

dynamic-analysis-sandboxingforensicsmalware-analysis+1
2668 years ago
CovenantDecryptor preview

CovenantDecryptor

GitHubnaacbin/covenantdecryptor

Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…

command-and-controlcryptographydigital-forensics+4
372 years ago
NetworkAssessment preview

NetworkAssessment

GitHubhalildeniz/networkassessment

NetworkAssessment: Network Compromise Assessment Tool

dns-analysisforensicsintrusion-detection+4
952 years ago
An-Integrated-Wireless-Network-Forensic-Analysis-Framework preview

An-Integrated-Wireless-Network-Forensic-Analysis-Framework

GitHubbenadia/an-integrated-wireless-network-forensic-analysis-framework

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
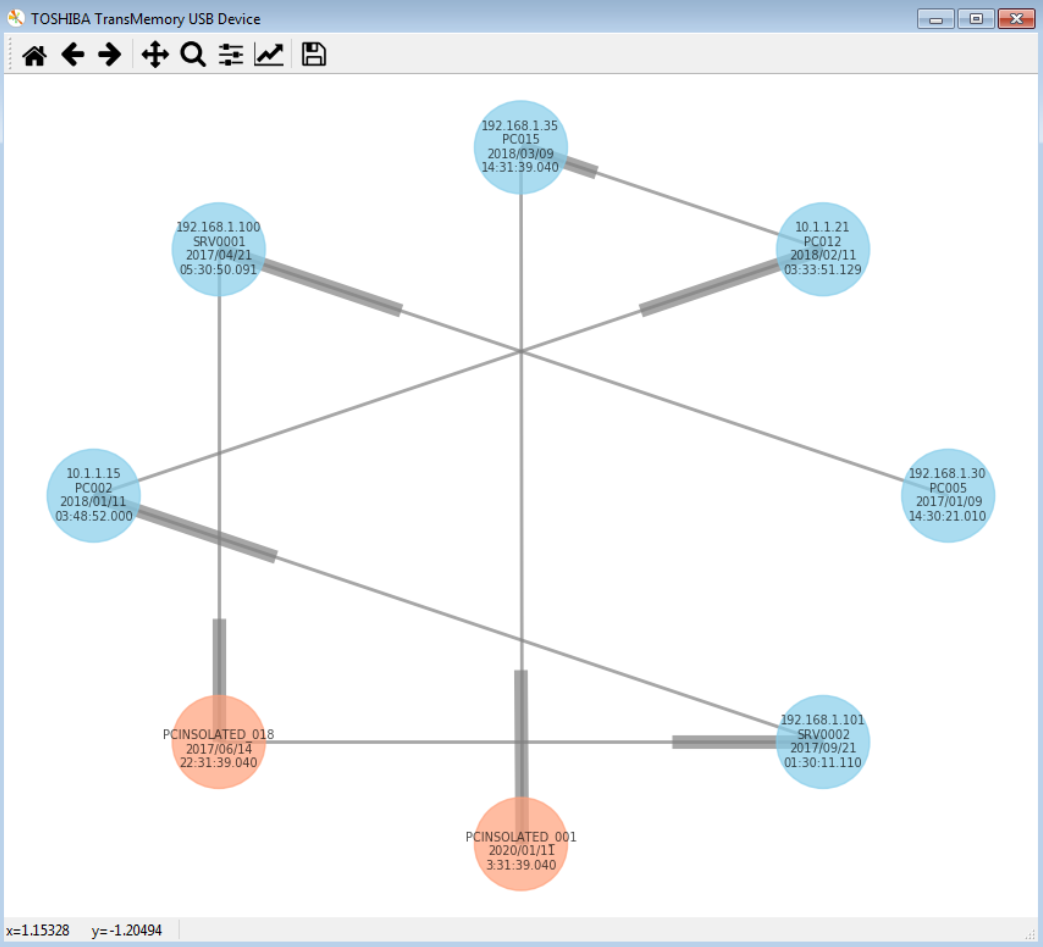
digital-forensicsforensicsnetwork-forensics+2
68 years ago
HiddenNetworks-Python preview

HiddenNetworks-Python

GitHubtelefonica/hiddennetworks-python

USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
digital-forensicsforensicsinformation-gathering+2
386 years ago
game-of-kingshot-re preview

game-of-kingshot-re

GitHubkdbugk/game-of-kingshot-re

Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…
android-securitybinary-analysisdynamic-analysis-sandboxing+5
314 months ago
wireshark-forensics-plugin preview

wireshark-forensics-plugin

GitHubrjbhide/wireshark-forensics-plugin

Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
digital-forensicsforensicsnetwork-forensics+3
1024 years ago
DFIR-LABS preview

DFIR-LABS

GitHubazr43lkn1ght/dfir-labs

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
ctfdigital-forensicsdisk-forensics+6
5859 months ago
QCSuper preview

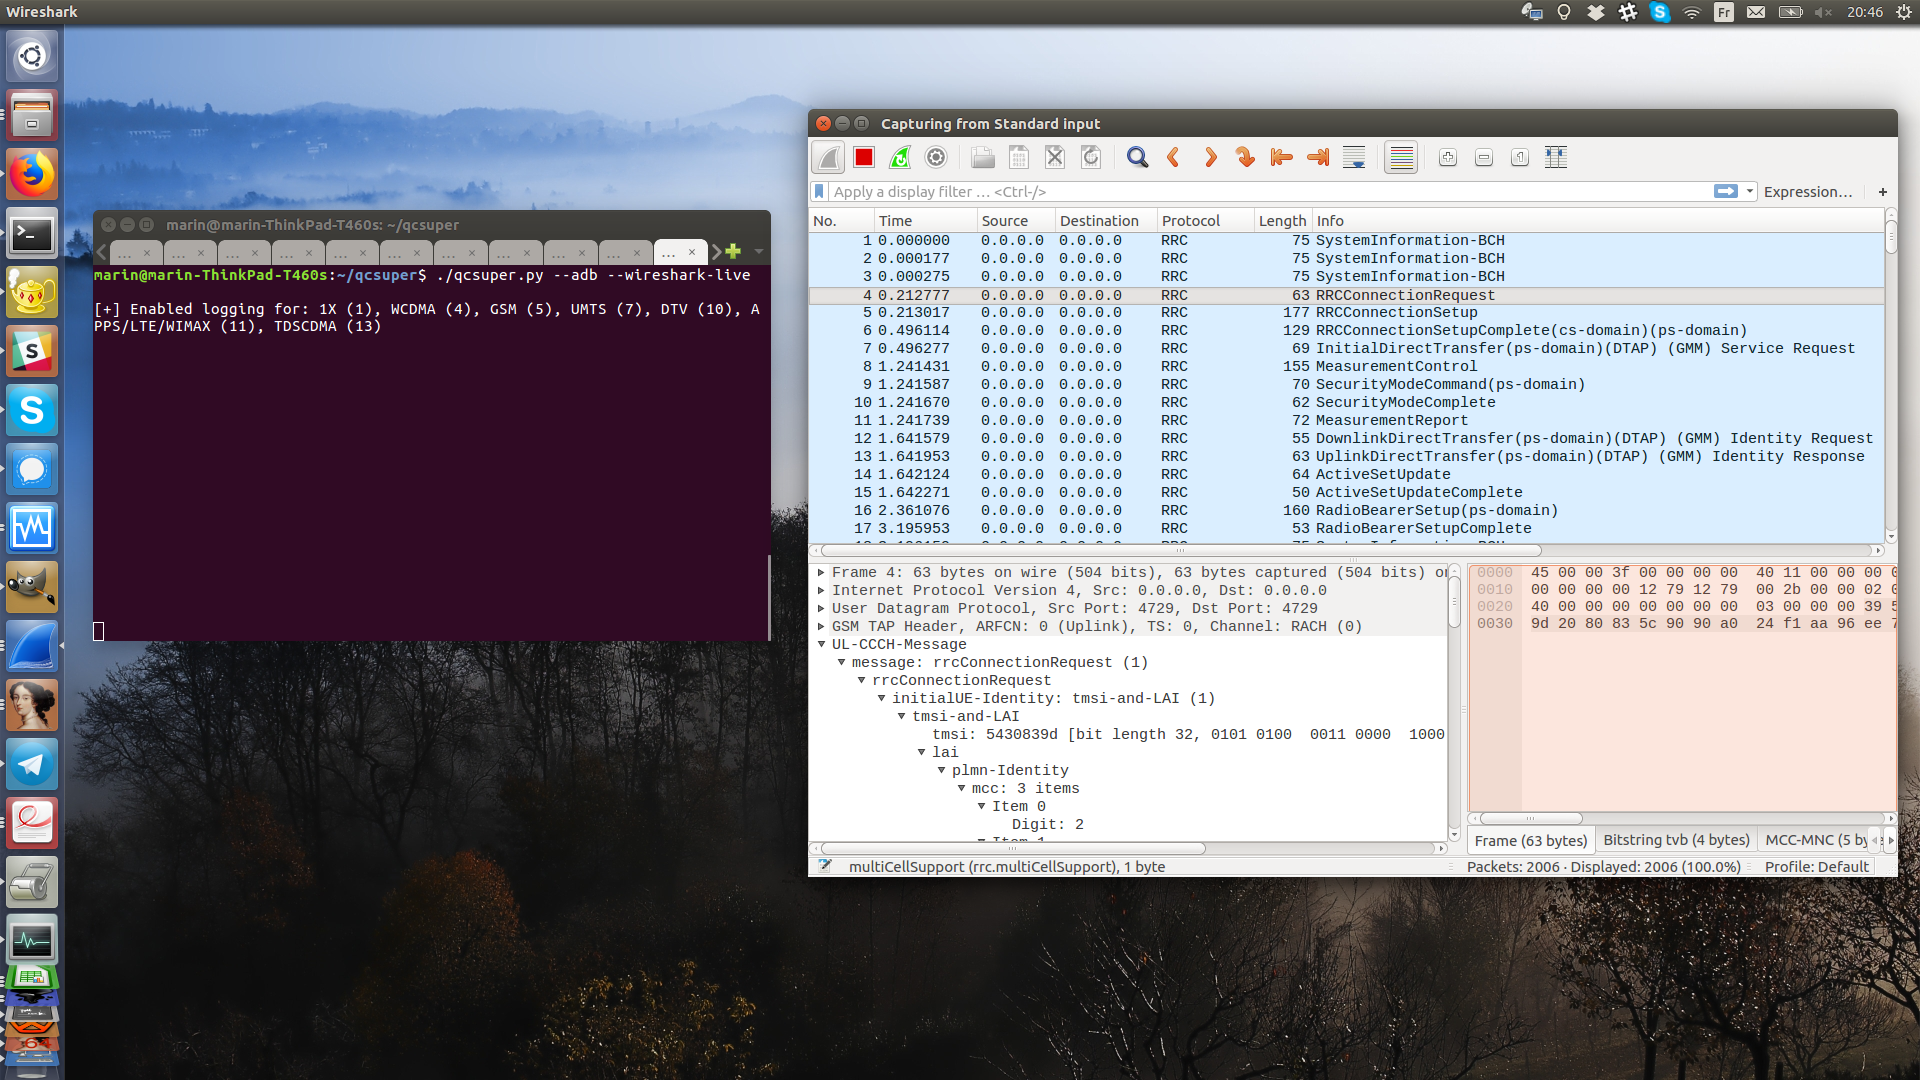
QCSuper

GitHubp1sec/qcsuper

QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
embedded-systems-securitymemory-forensicsmobile-forensics+4
1.6k1 month ago
PcapXray preview

PcapXray

GitHubsrixivas/pcapxray

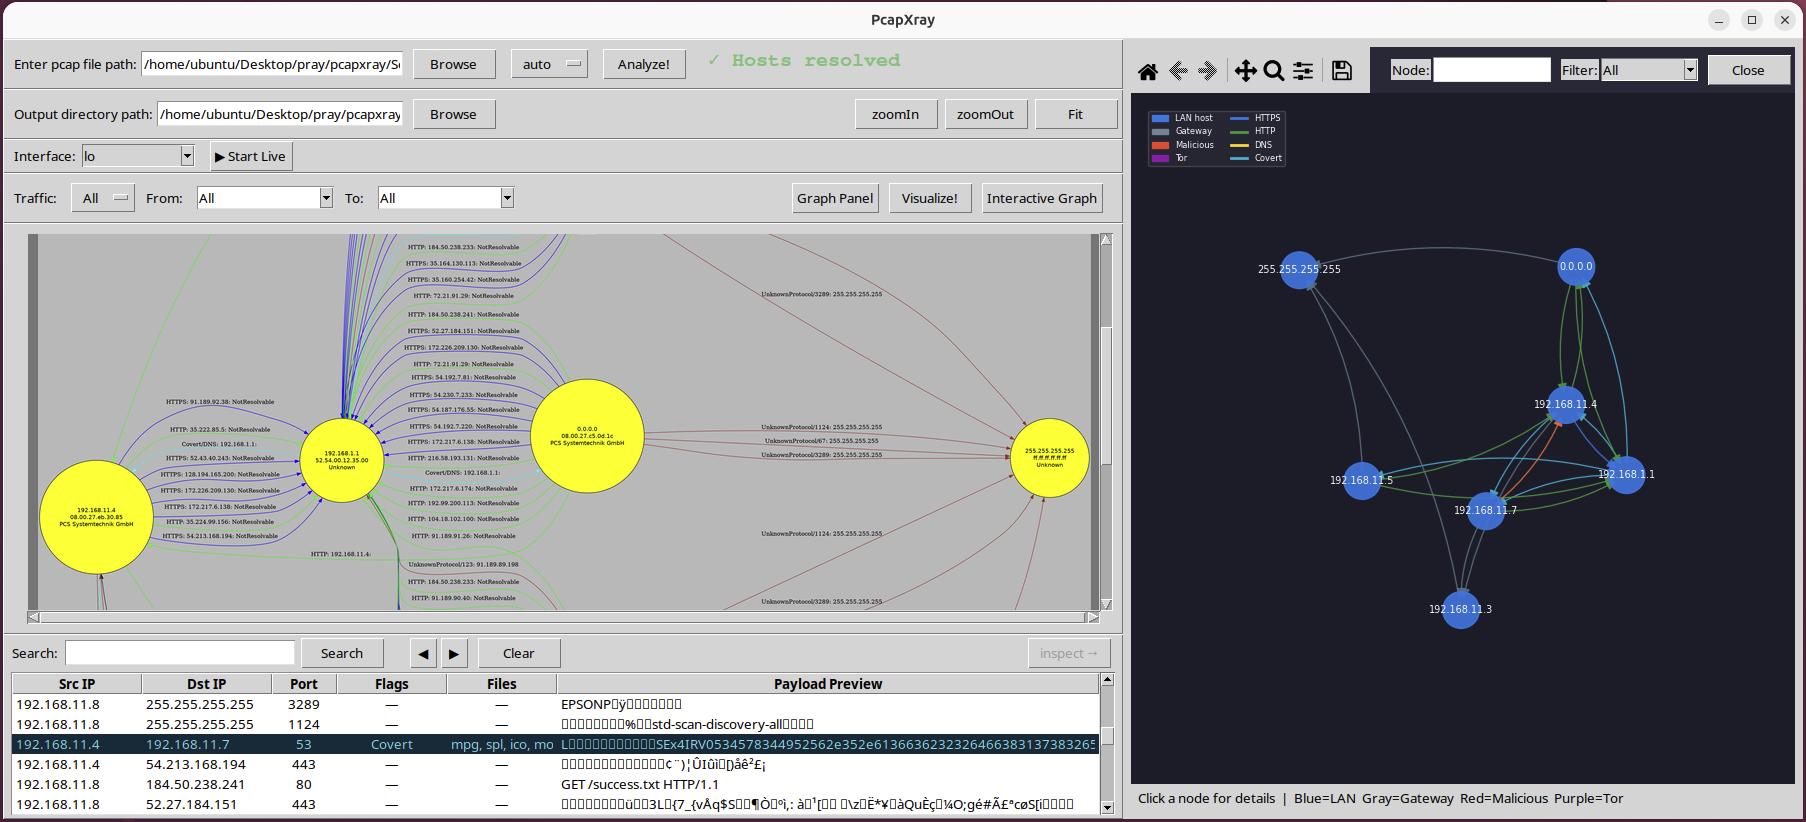
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…

ctfdns-analysiseducation+7
1.9k4 months ago
Previous1234Next