

Qu1cksc0pe
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
android-securitydynamic-analysis-sandboxingforensics+4
cyb3rmx/qu1cksc0peAll-in-One malware analysis tool.
 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 eciavatta/caronte
A tool to analyze the network flow during attack/defence Capture the Flag competitions
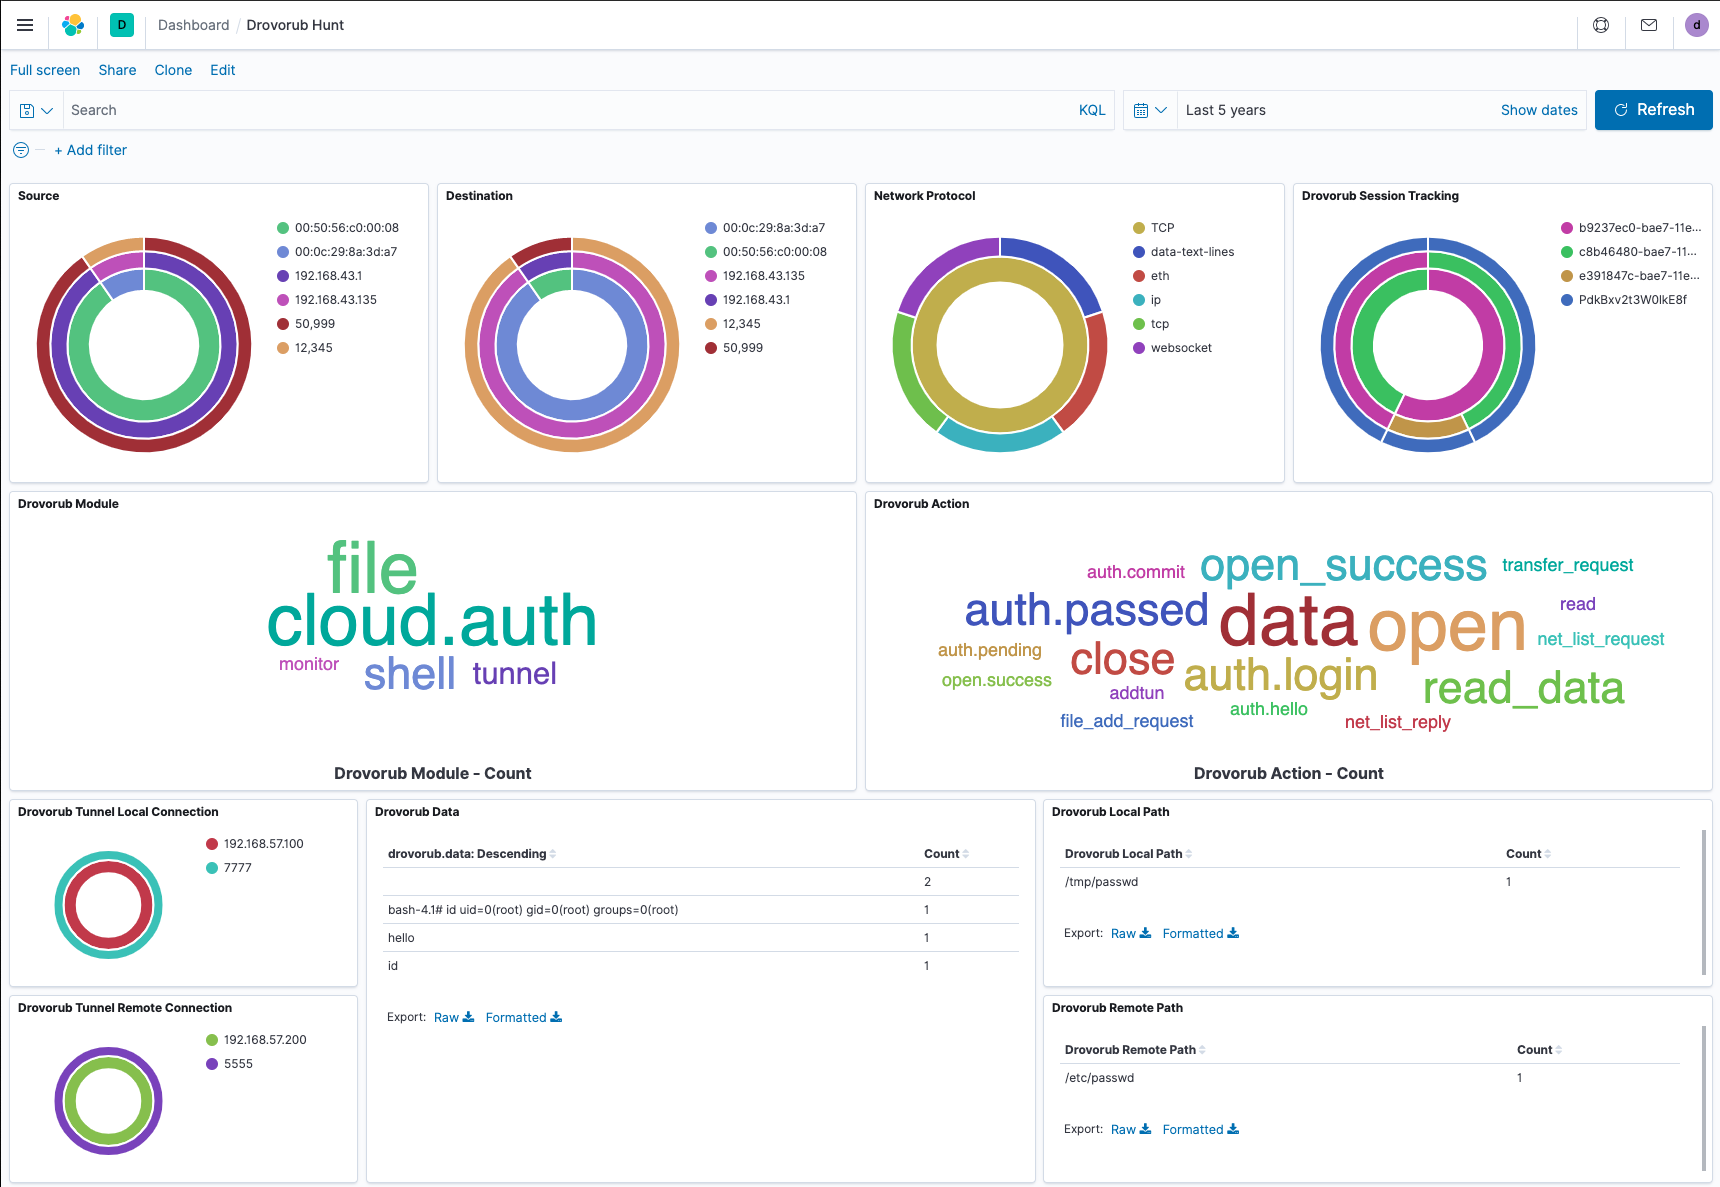 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
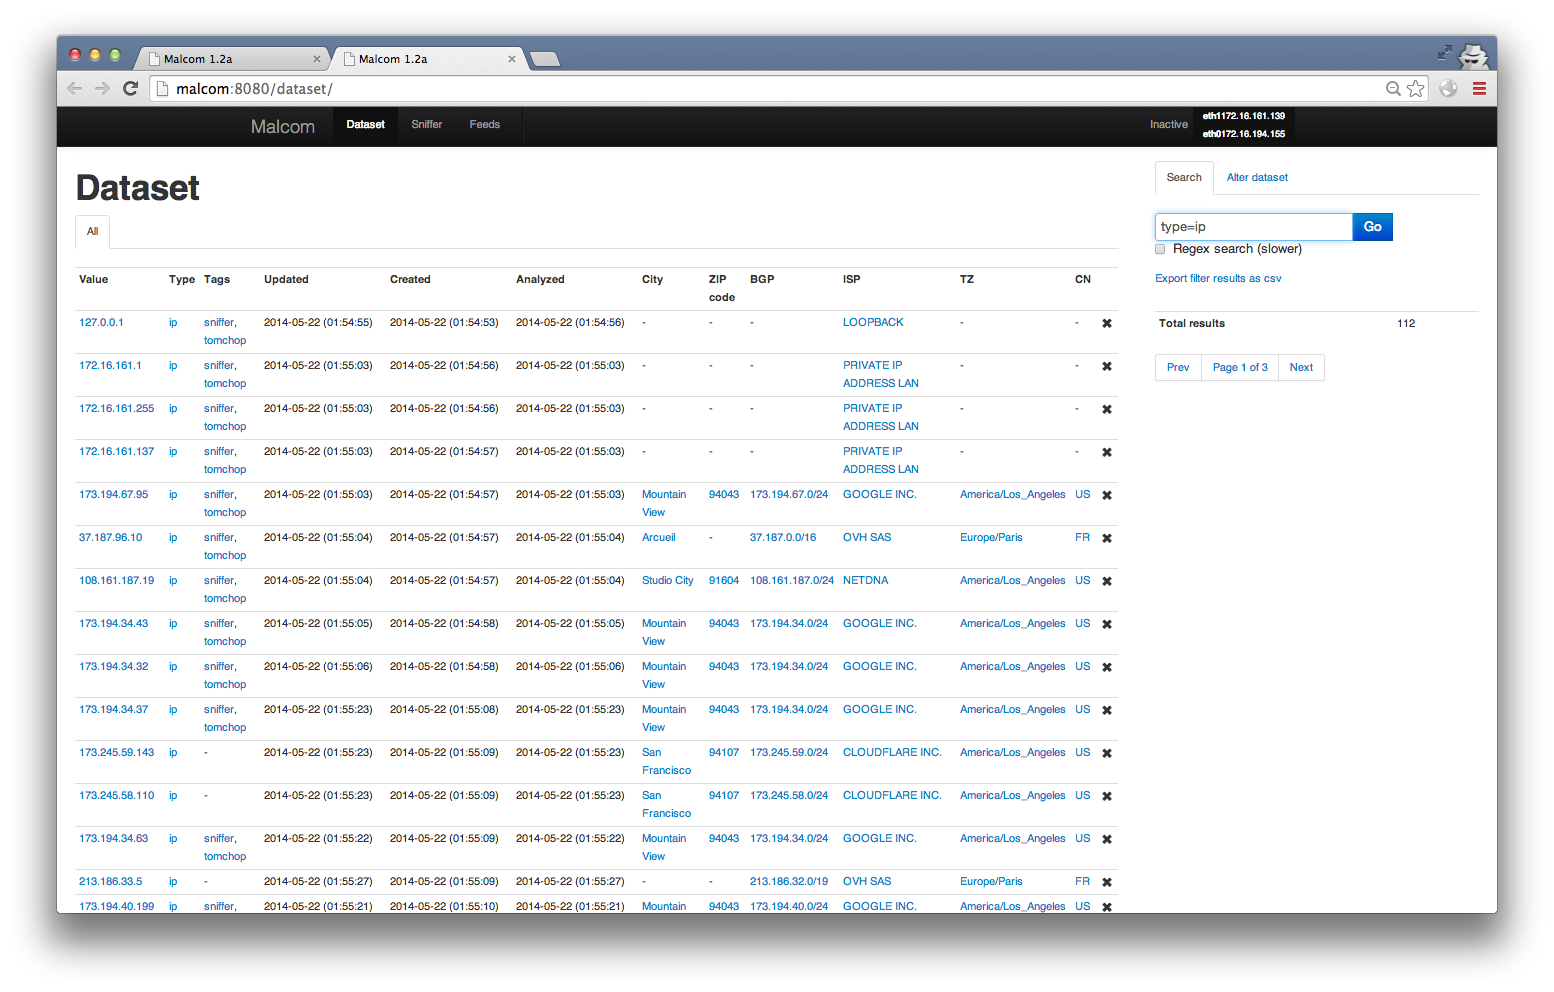 tomchop/malcom
Malcom - Malware Communications Analyzer
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
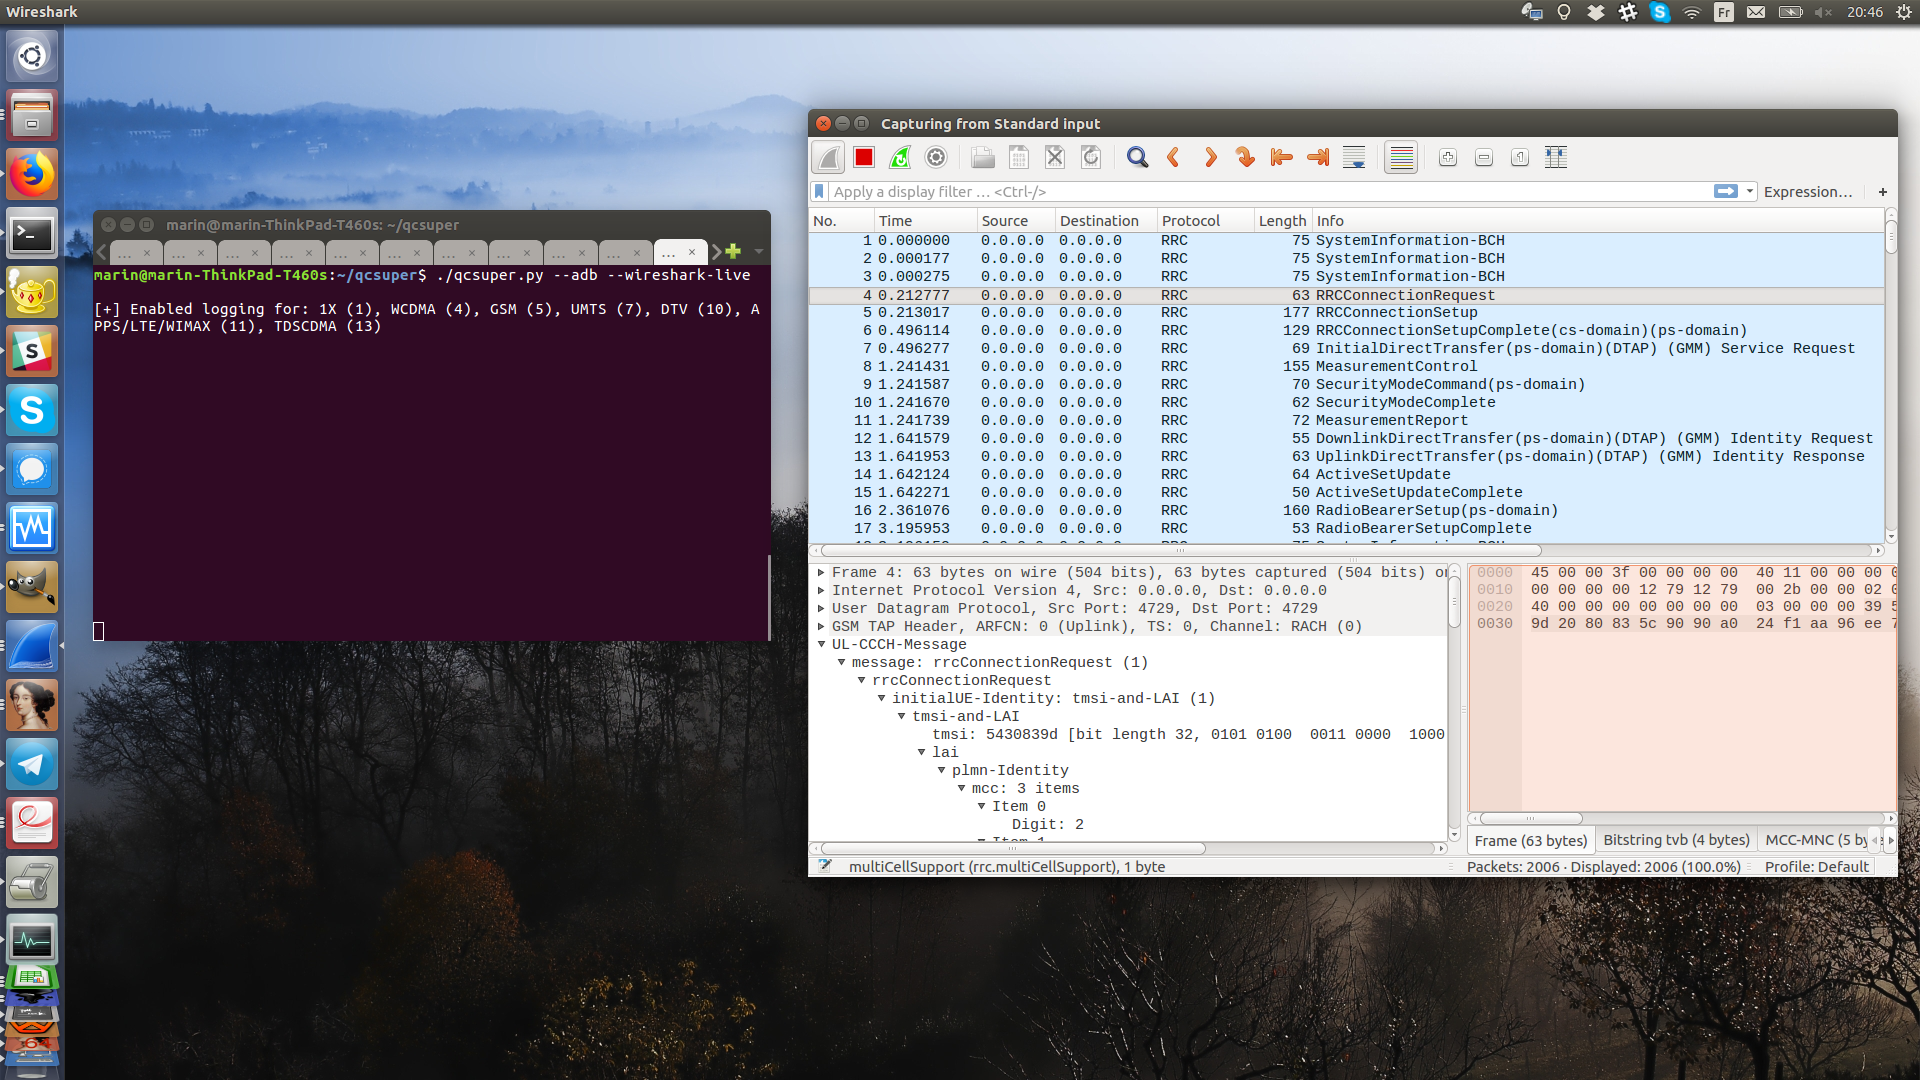 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
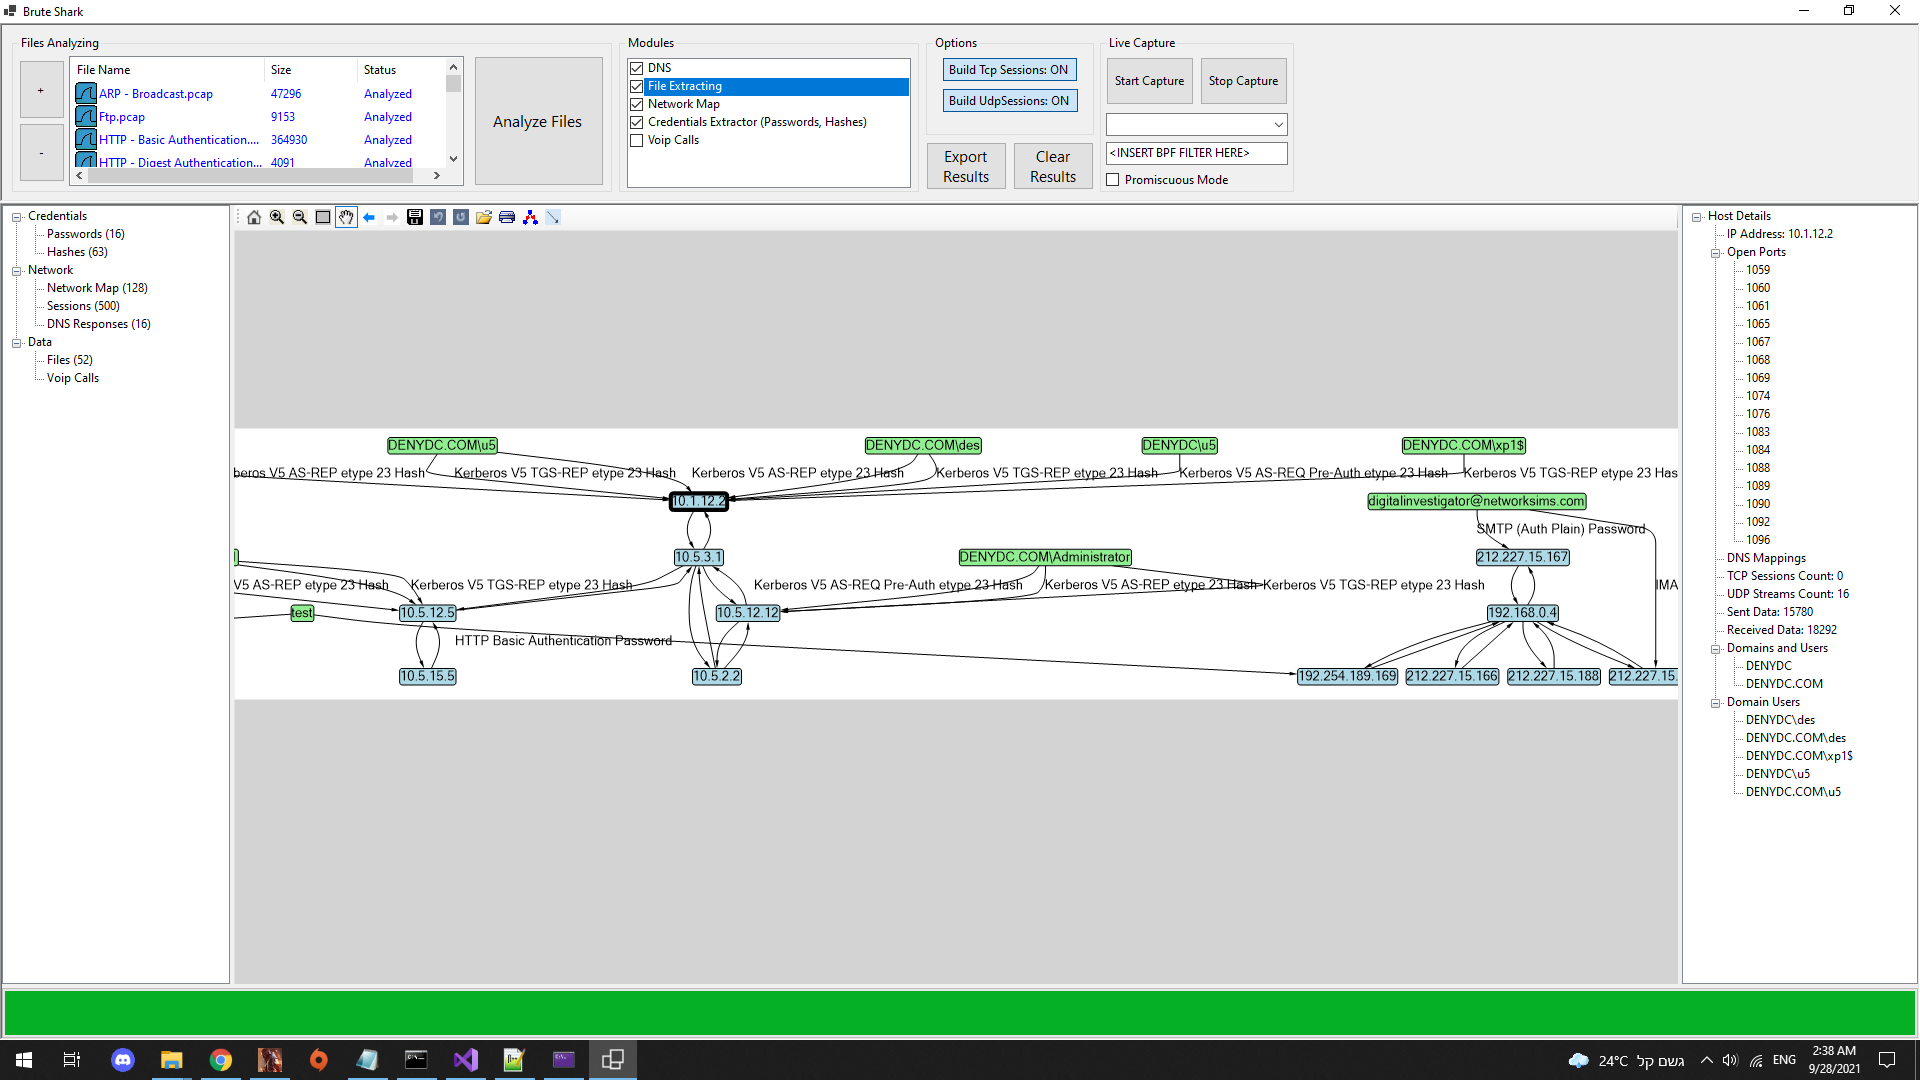
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
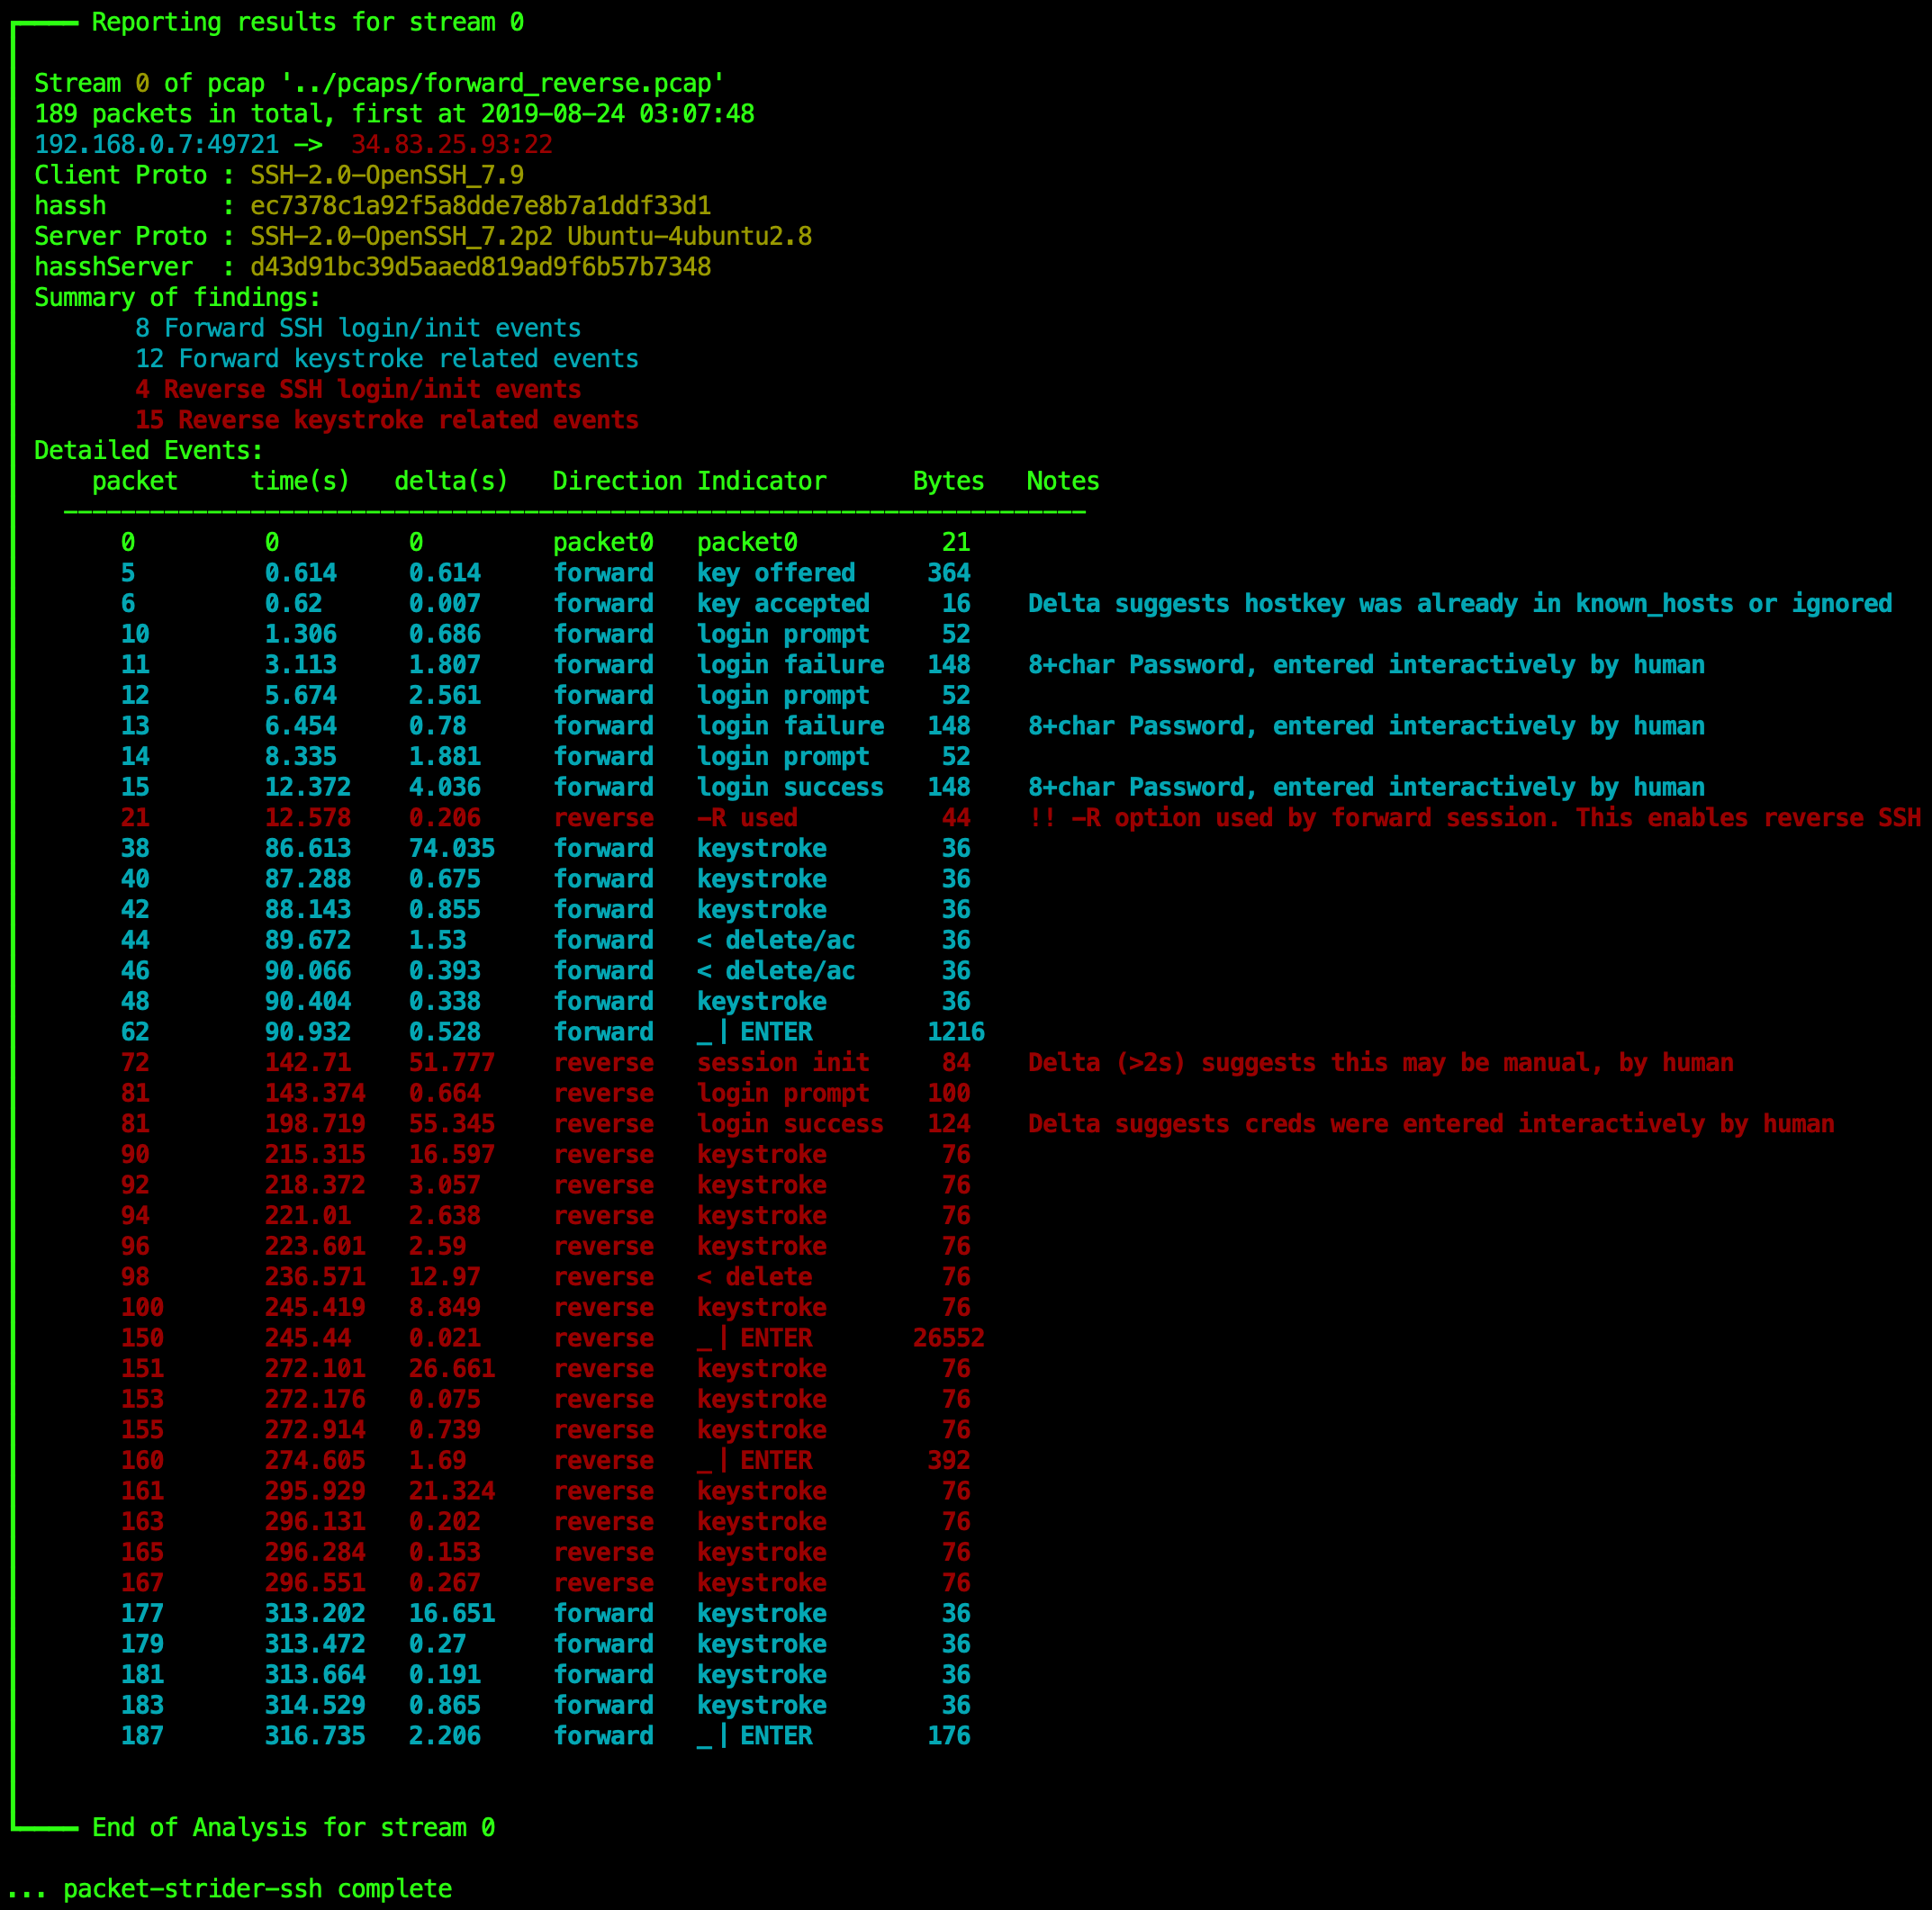 benjeems/packetstrider
A network packet forensics tool for SSH
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
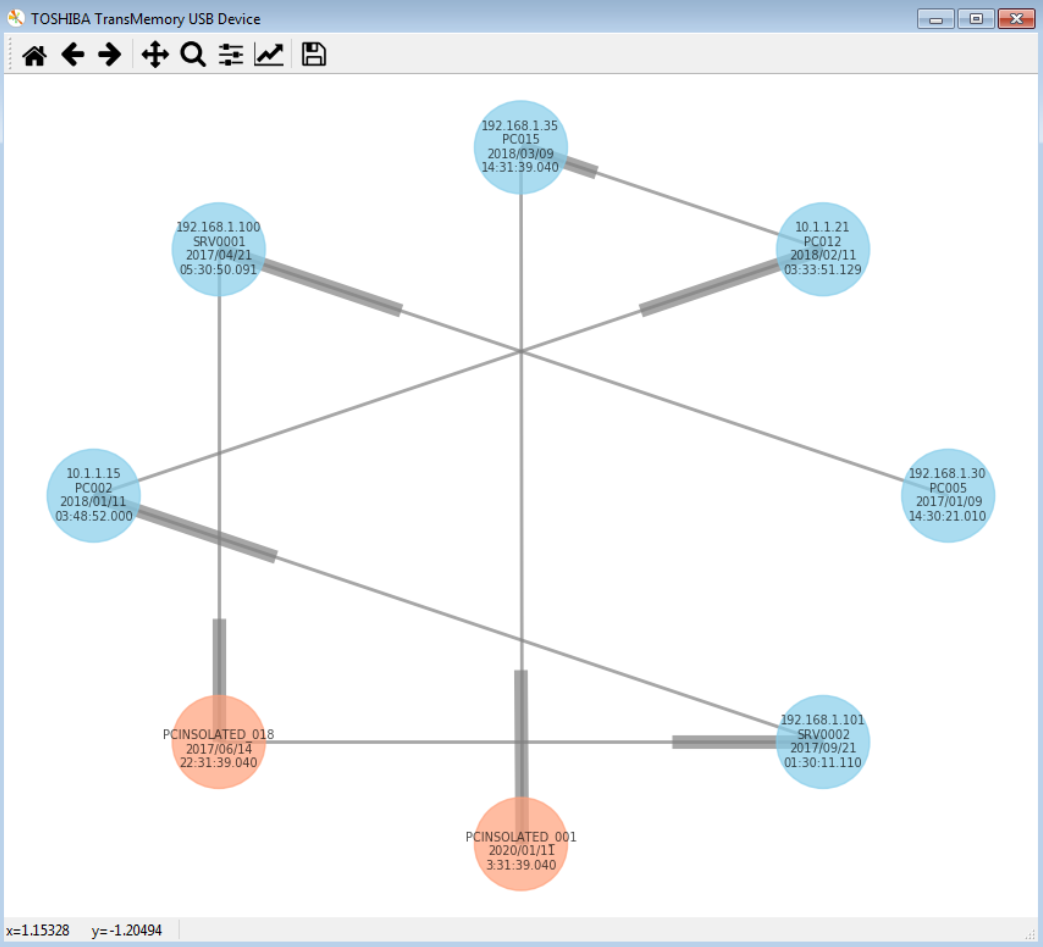 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
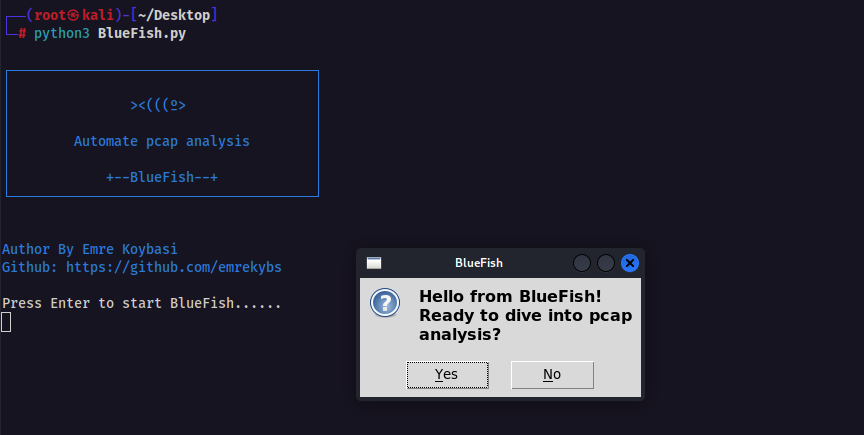 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files

 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 simsong/bulk_extractor
This is the development tree. Production downloads are at: