
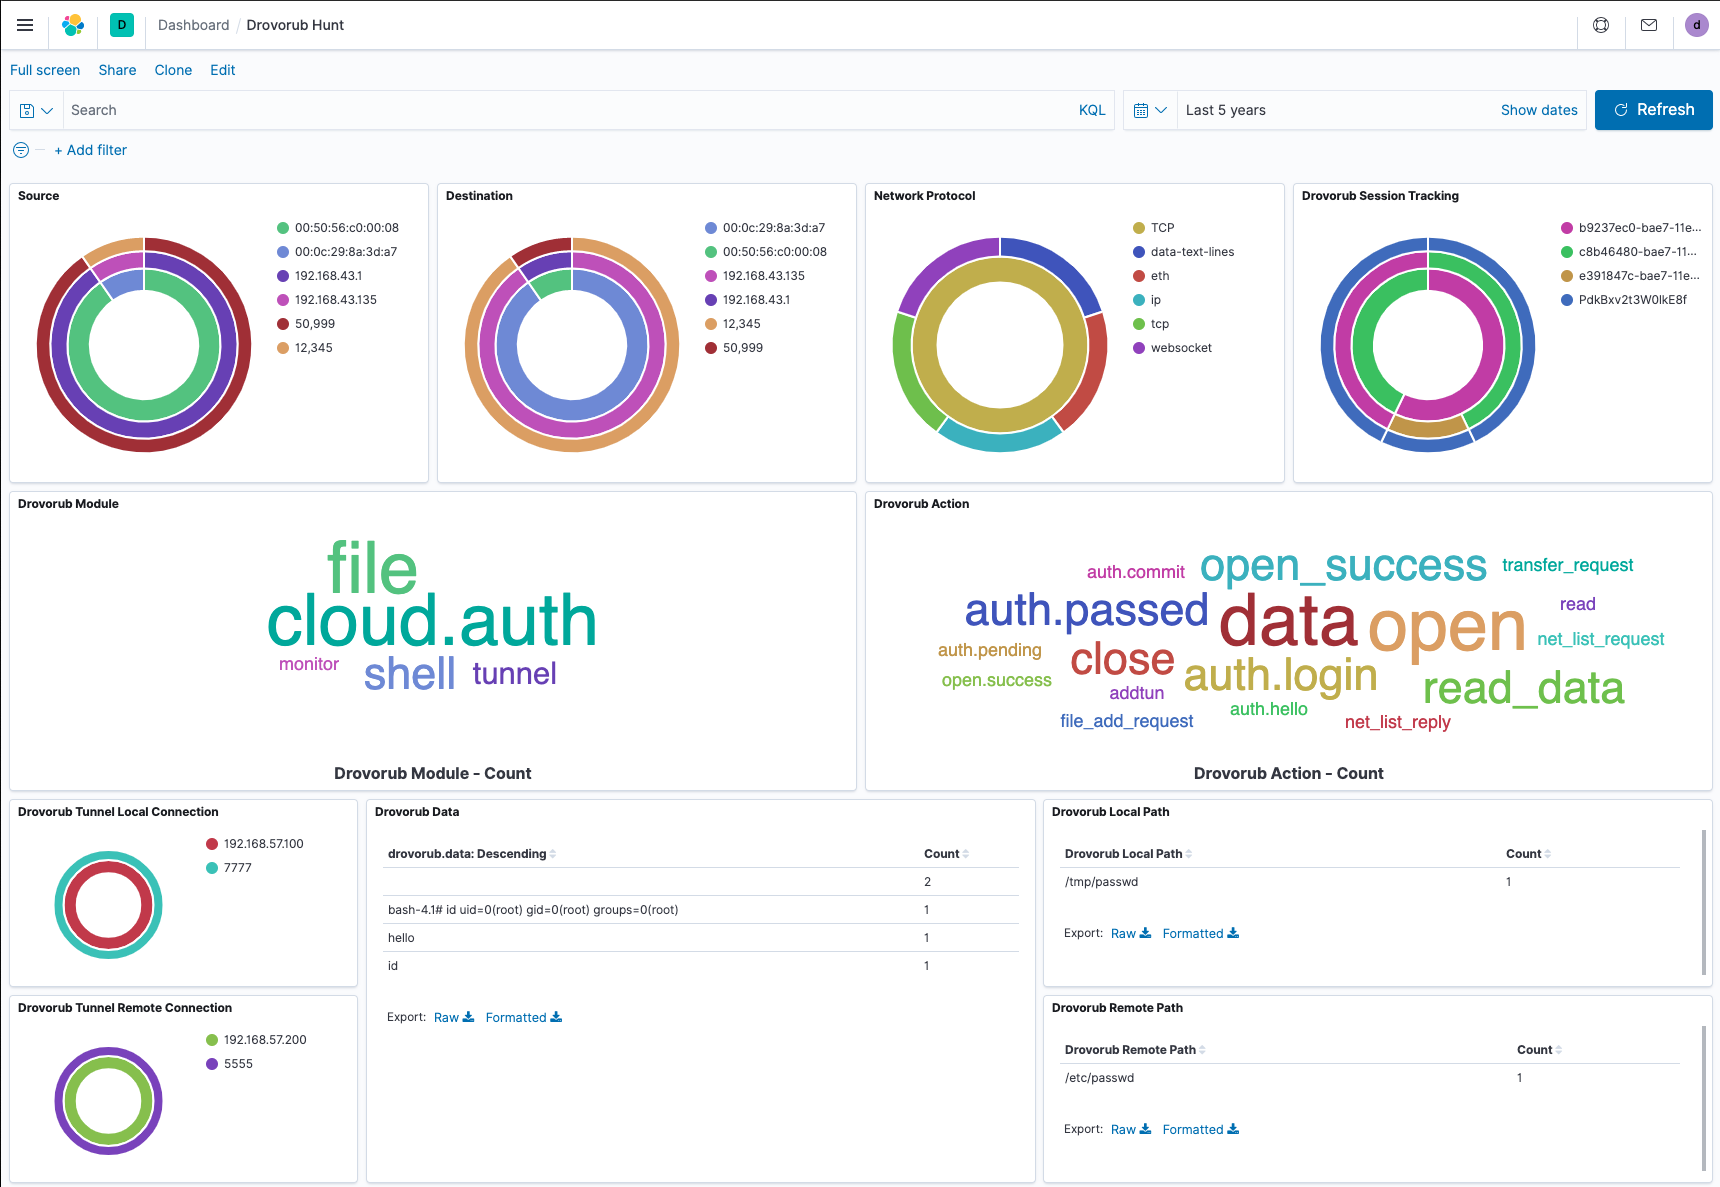
drovorub-hunt
 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
incident-responseintrusion-detectionmalware-analysis+3
25
insane-forensics/drovorub-huntA tool to assist with network-based hunting for GRU's Drovorub malware c2
 z4l4mi/ipgeo
Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
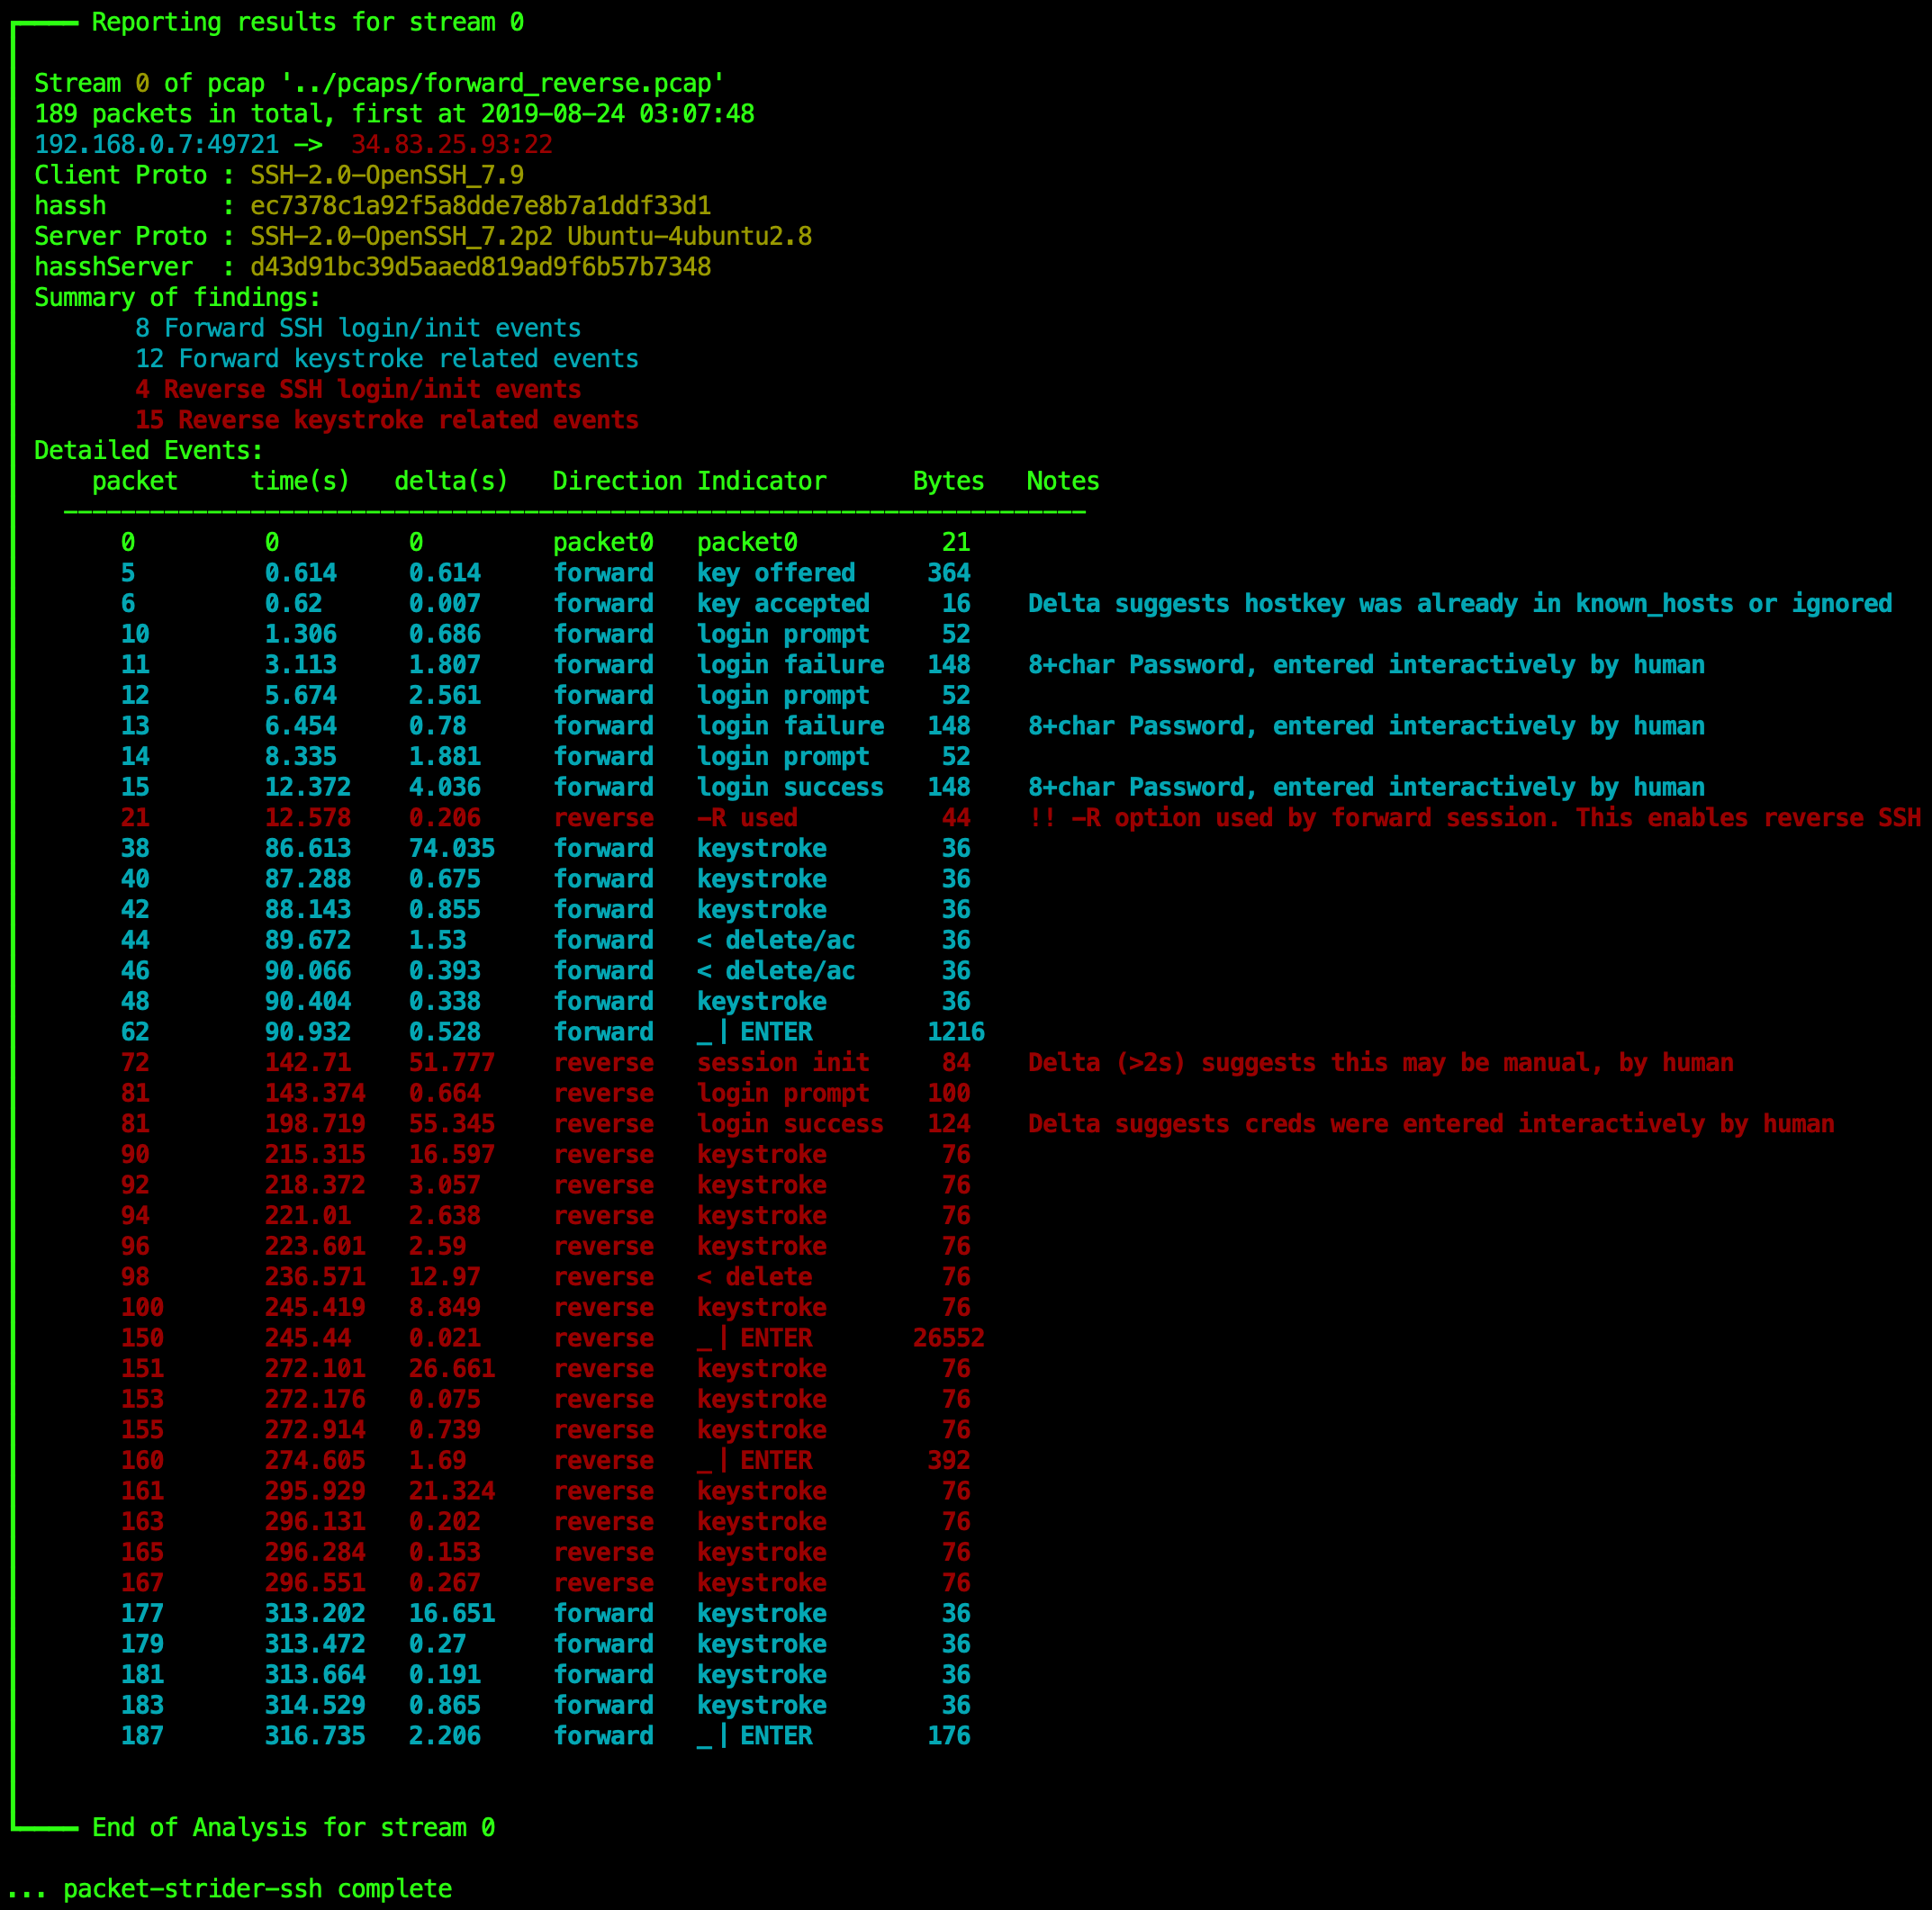 benjeems/packetstrider
A network packet forensics tool for SSH
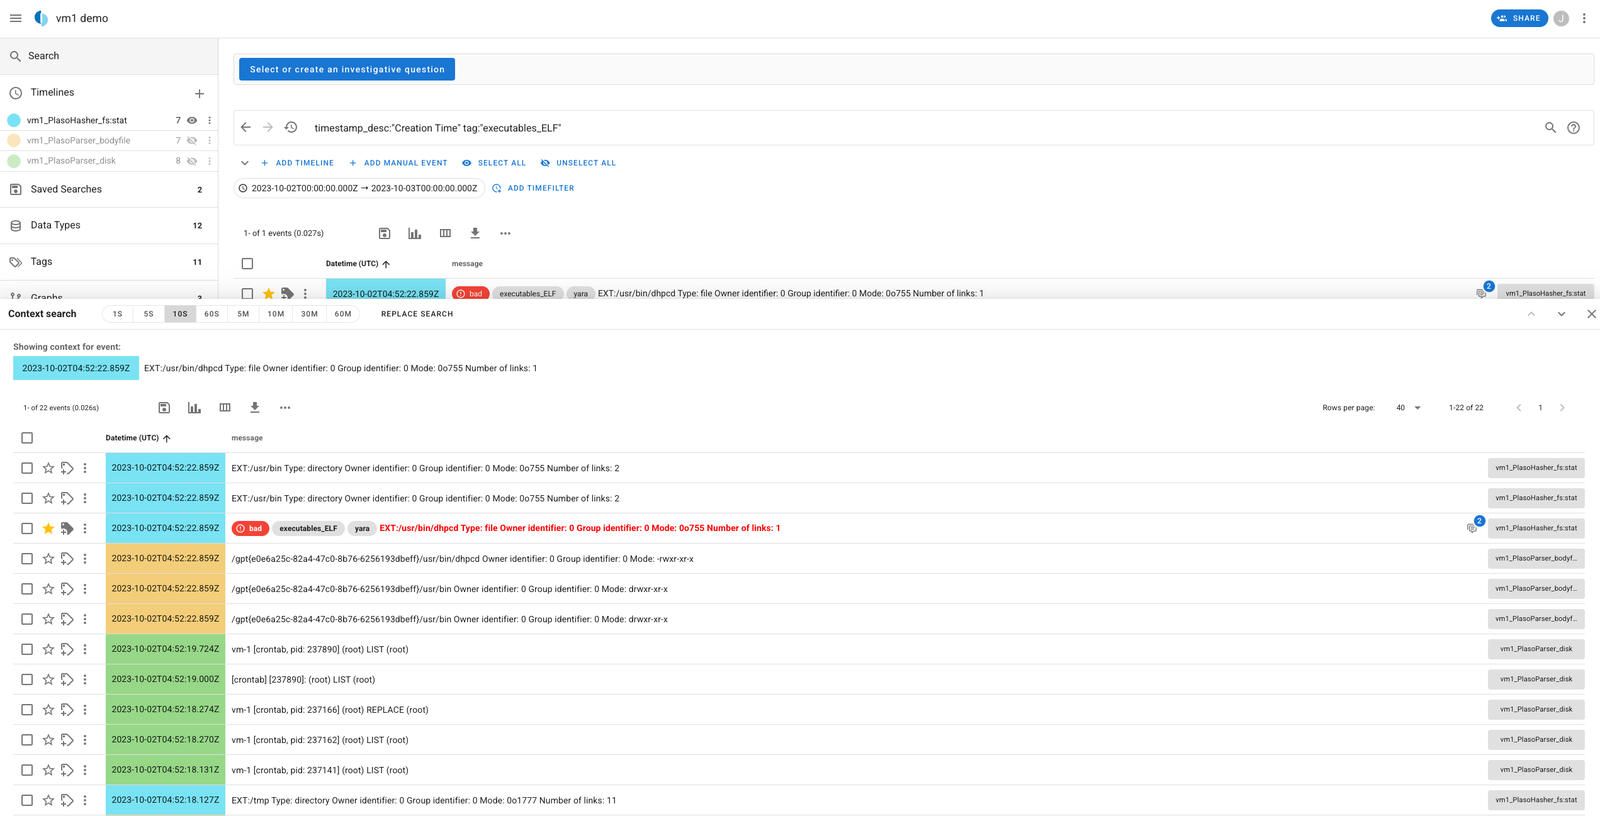 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
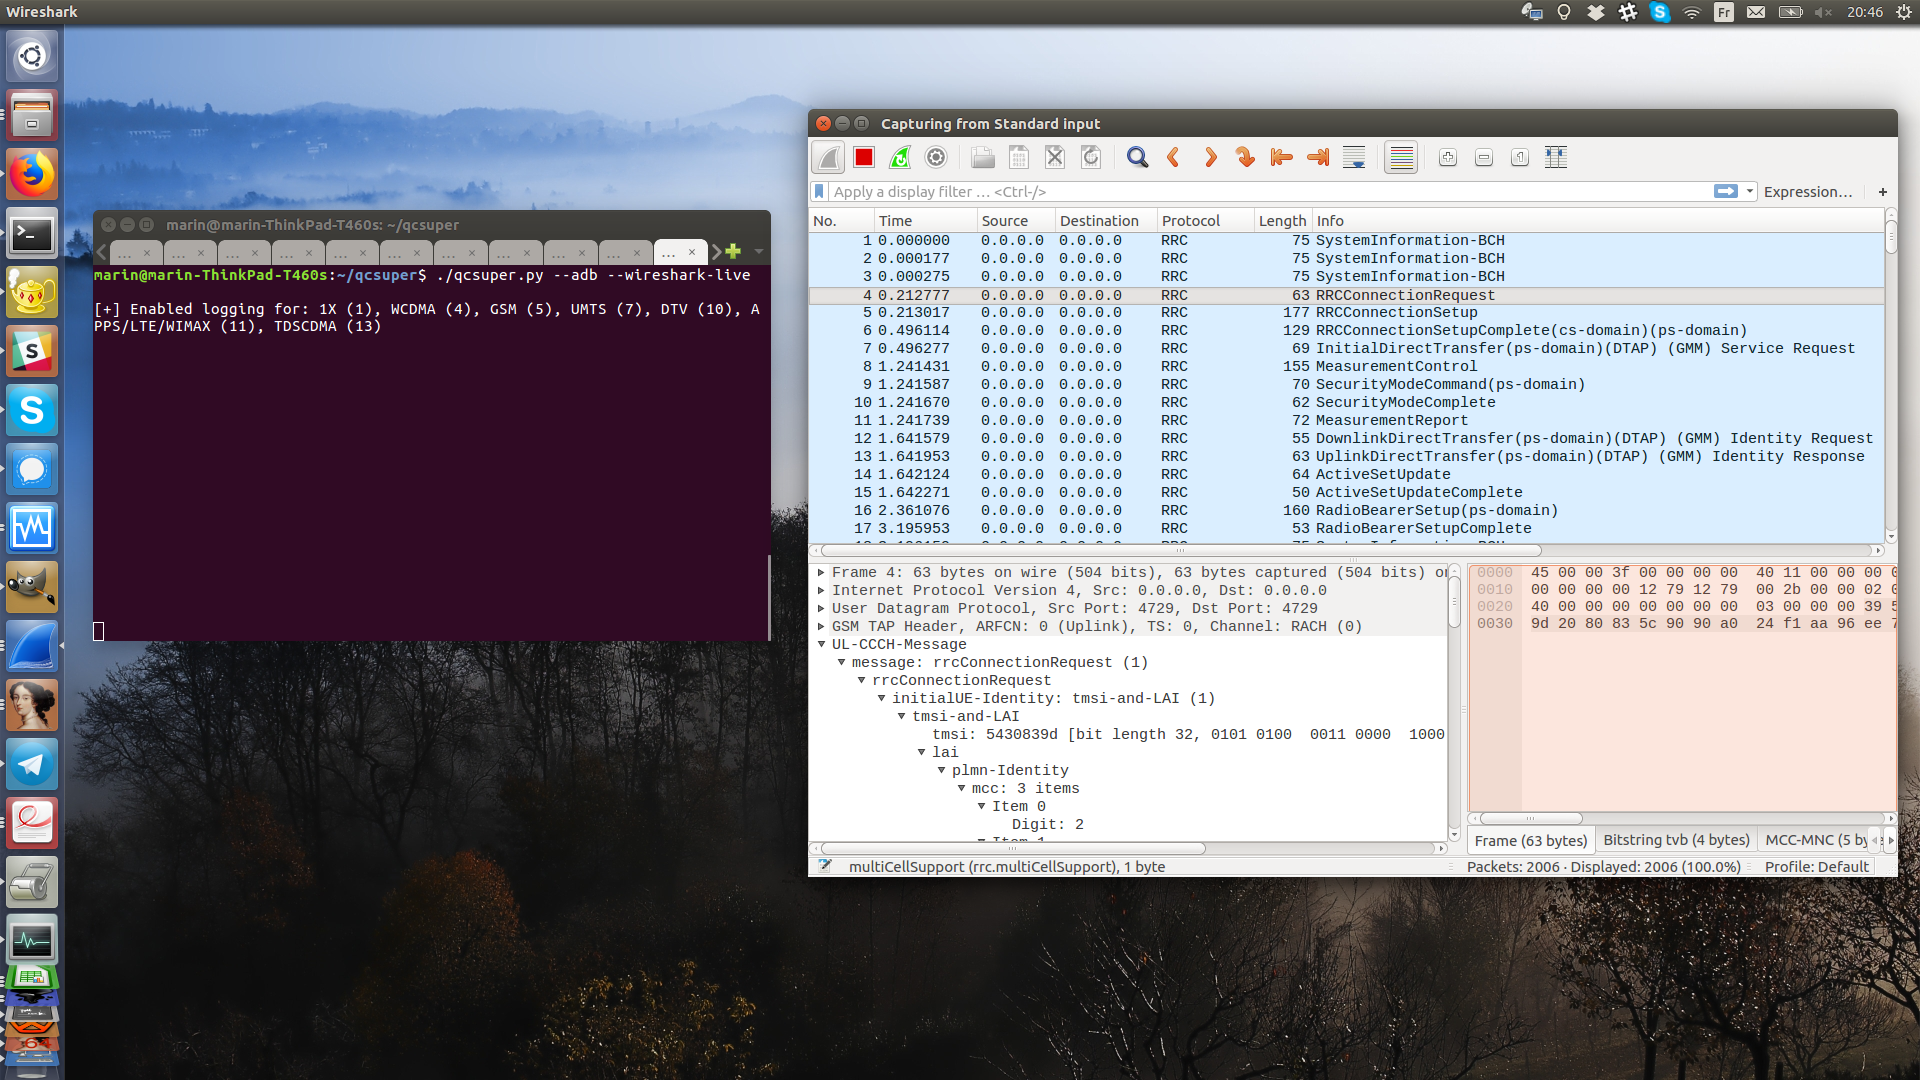 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 eciavatta/caronte
A tool to analyze the network flow during attack/defence Capture the Flag competitions
 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…

 omriher/captipper
Malicious HTTP traffic explorer
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
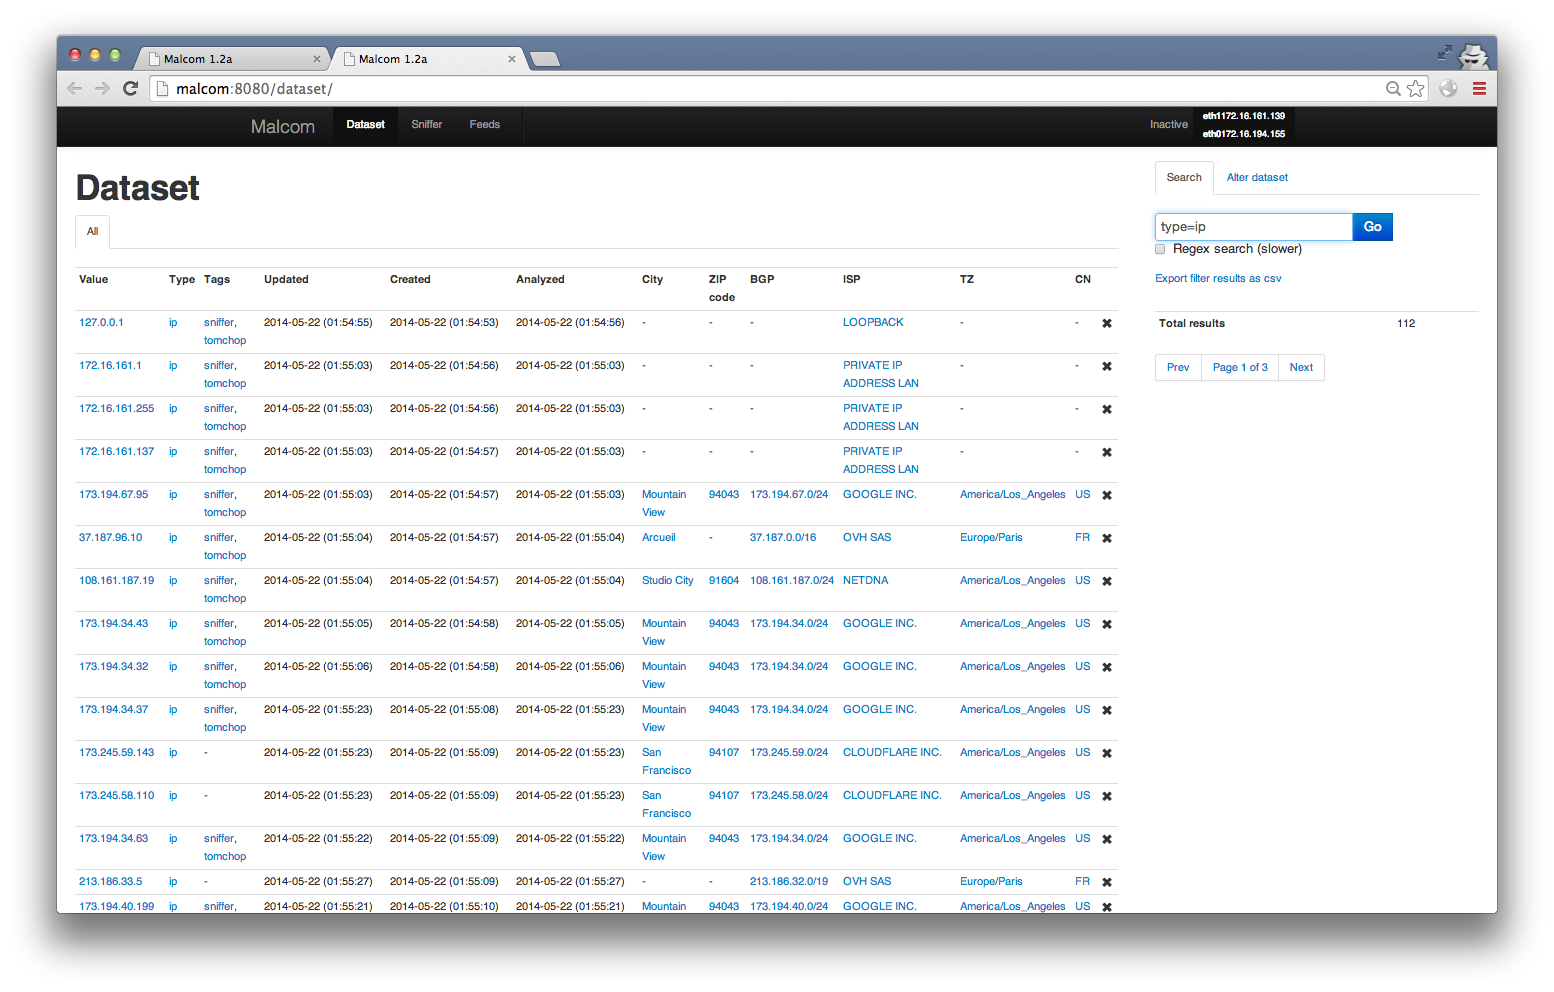 tomchop/malcom
Malcom - Malware Communications Analyzer
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files