

netsniff-ng
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
network-forensicsnetwork-mappingnetwork-security+4
1.4k
netsniff-ng/netsniff-ngA Swiss army knife for your daily Linux network plumbing.
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 gosecure/pyrdp
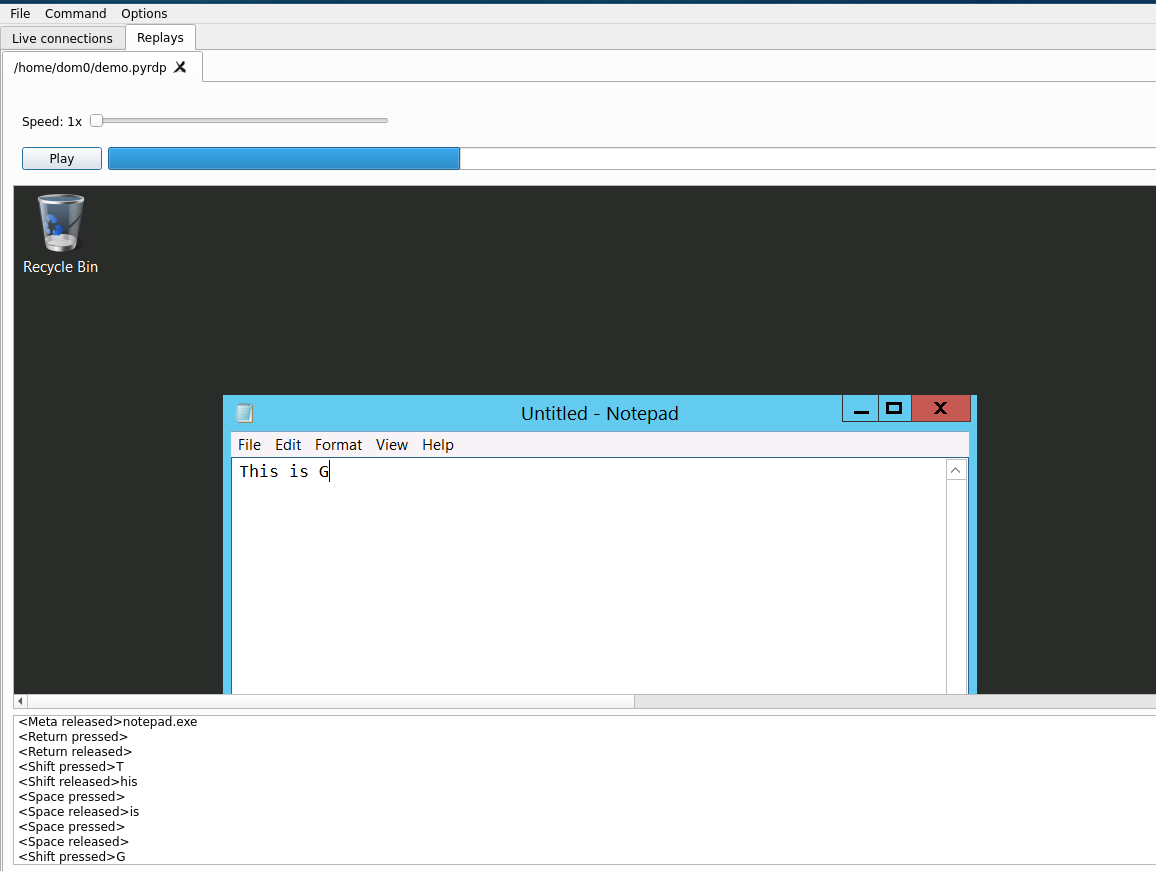
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
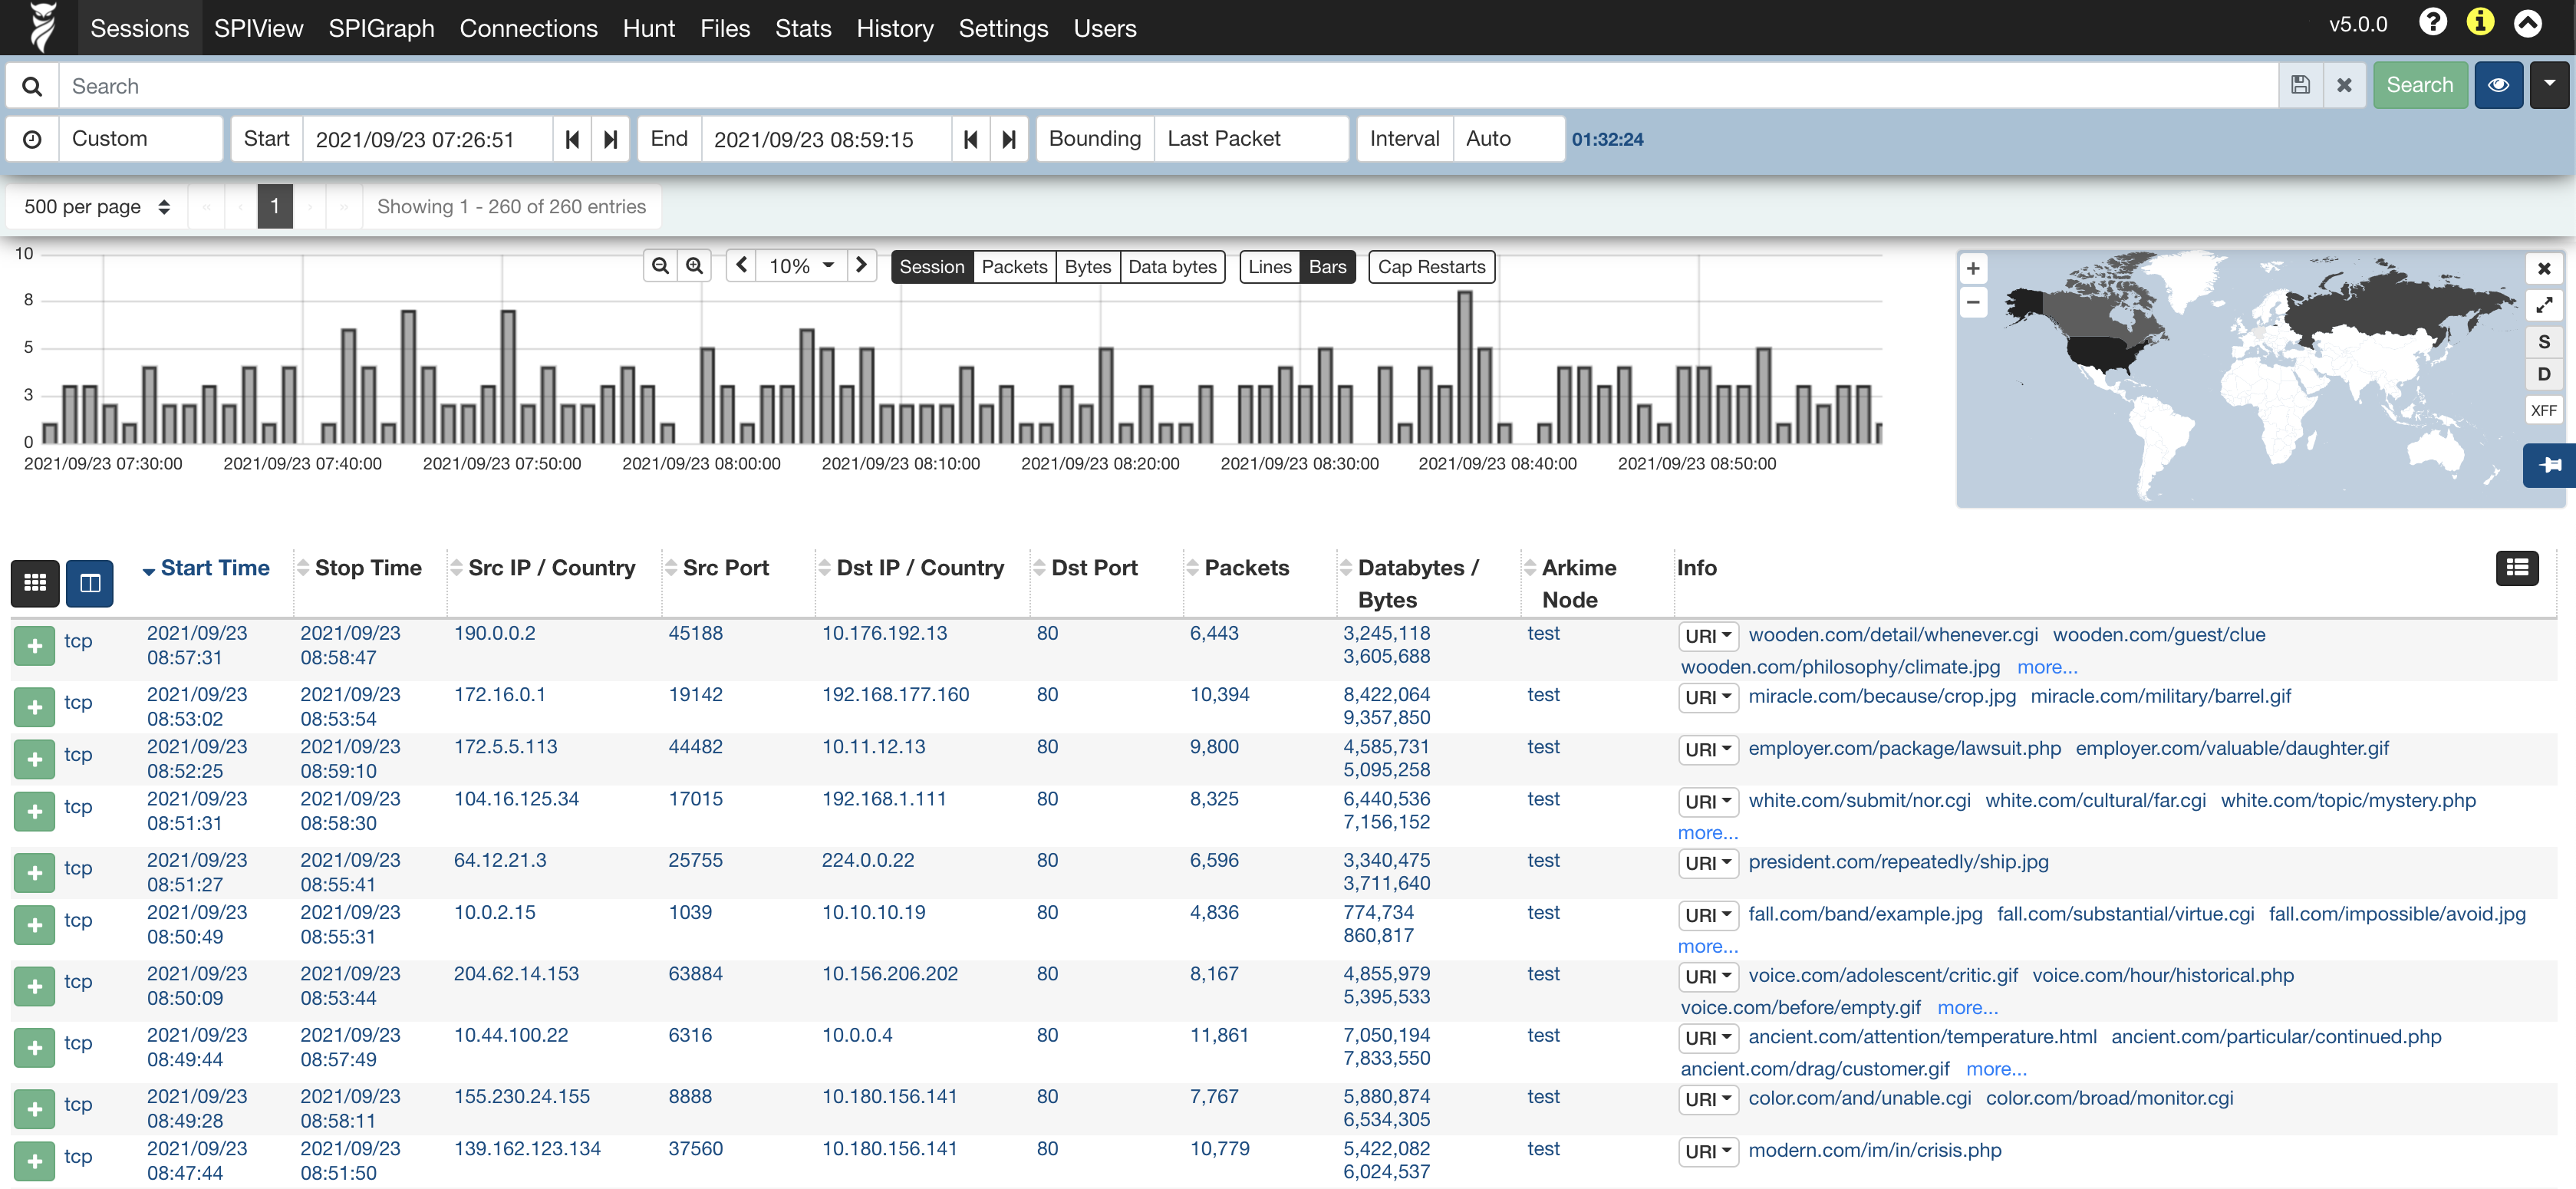 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
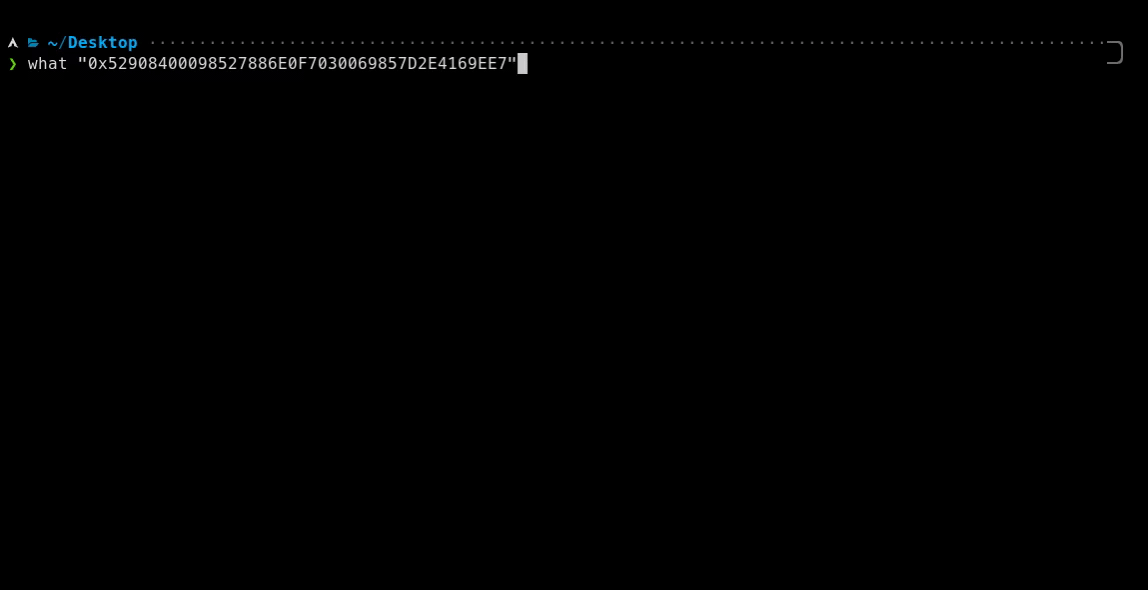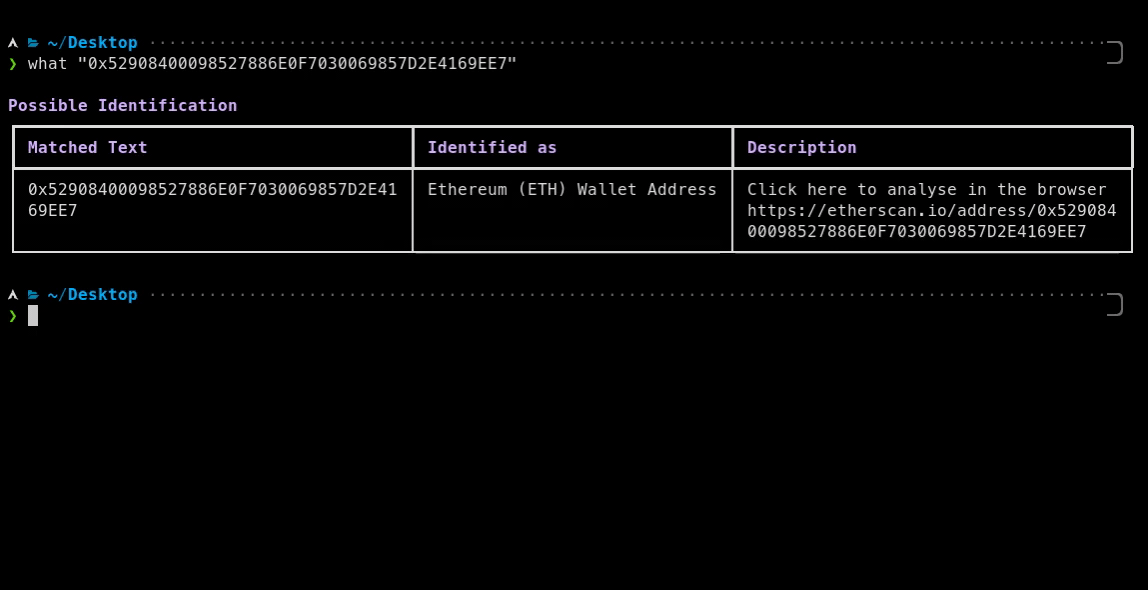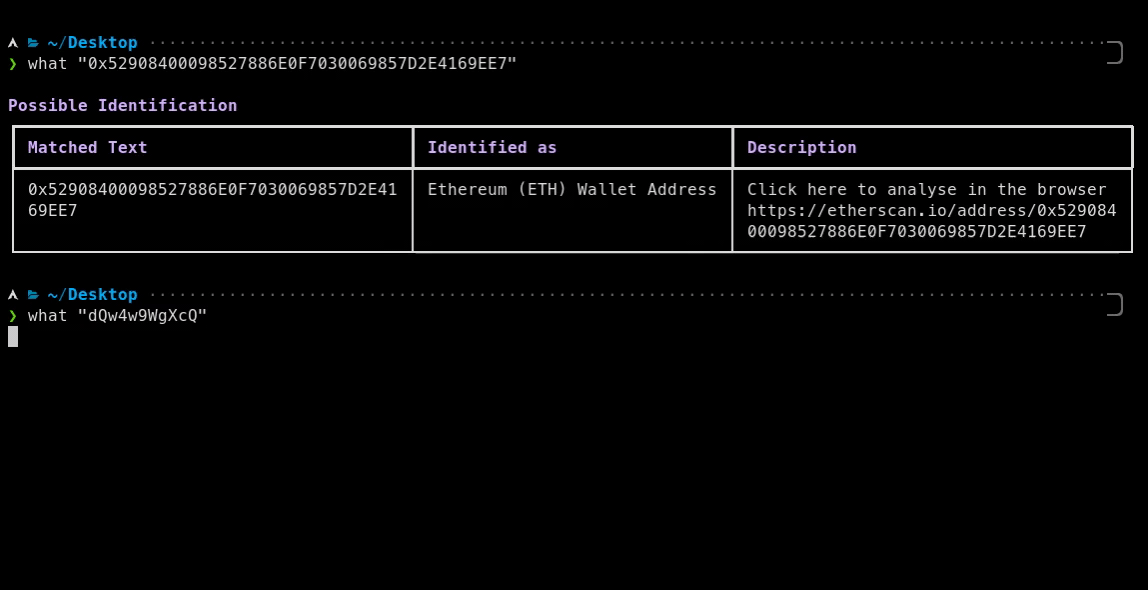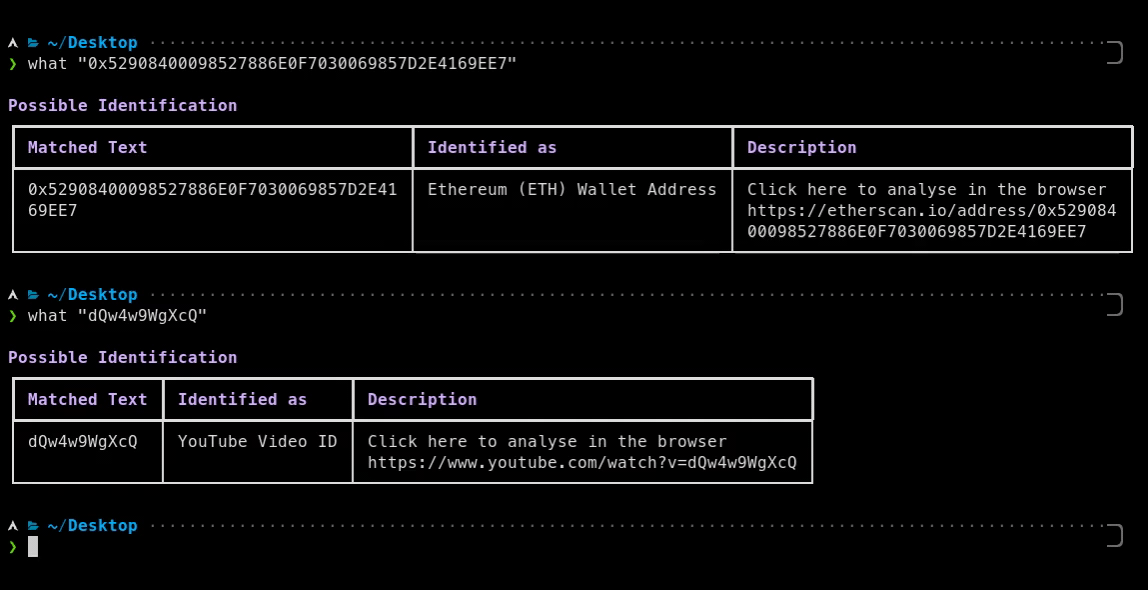 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
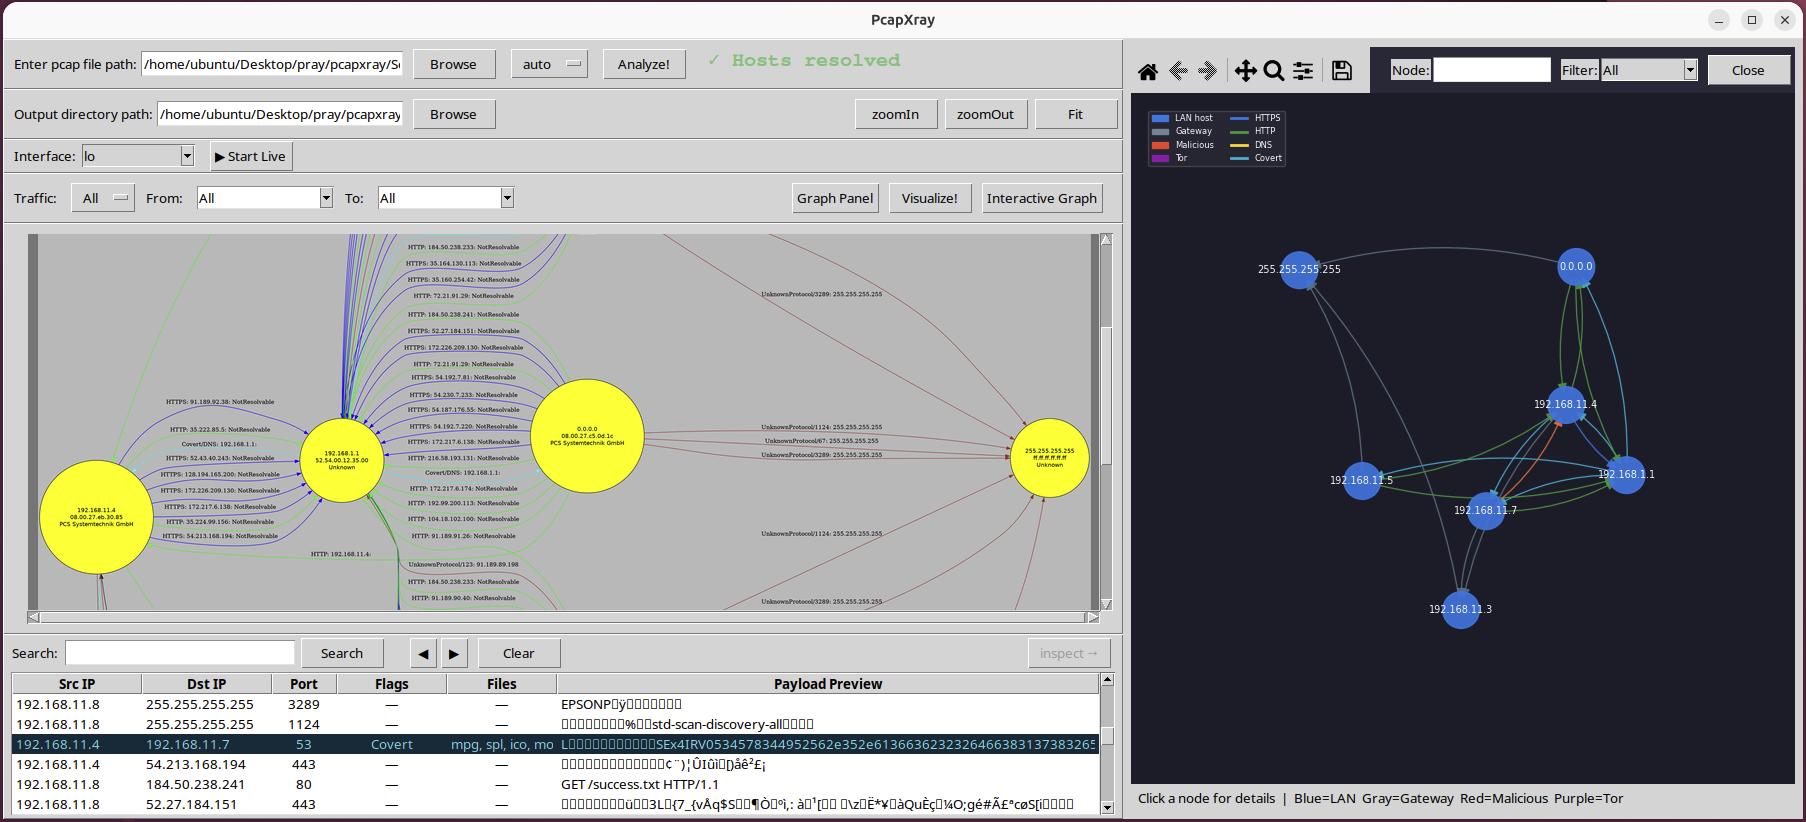 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring

 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards