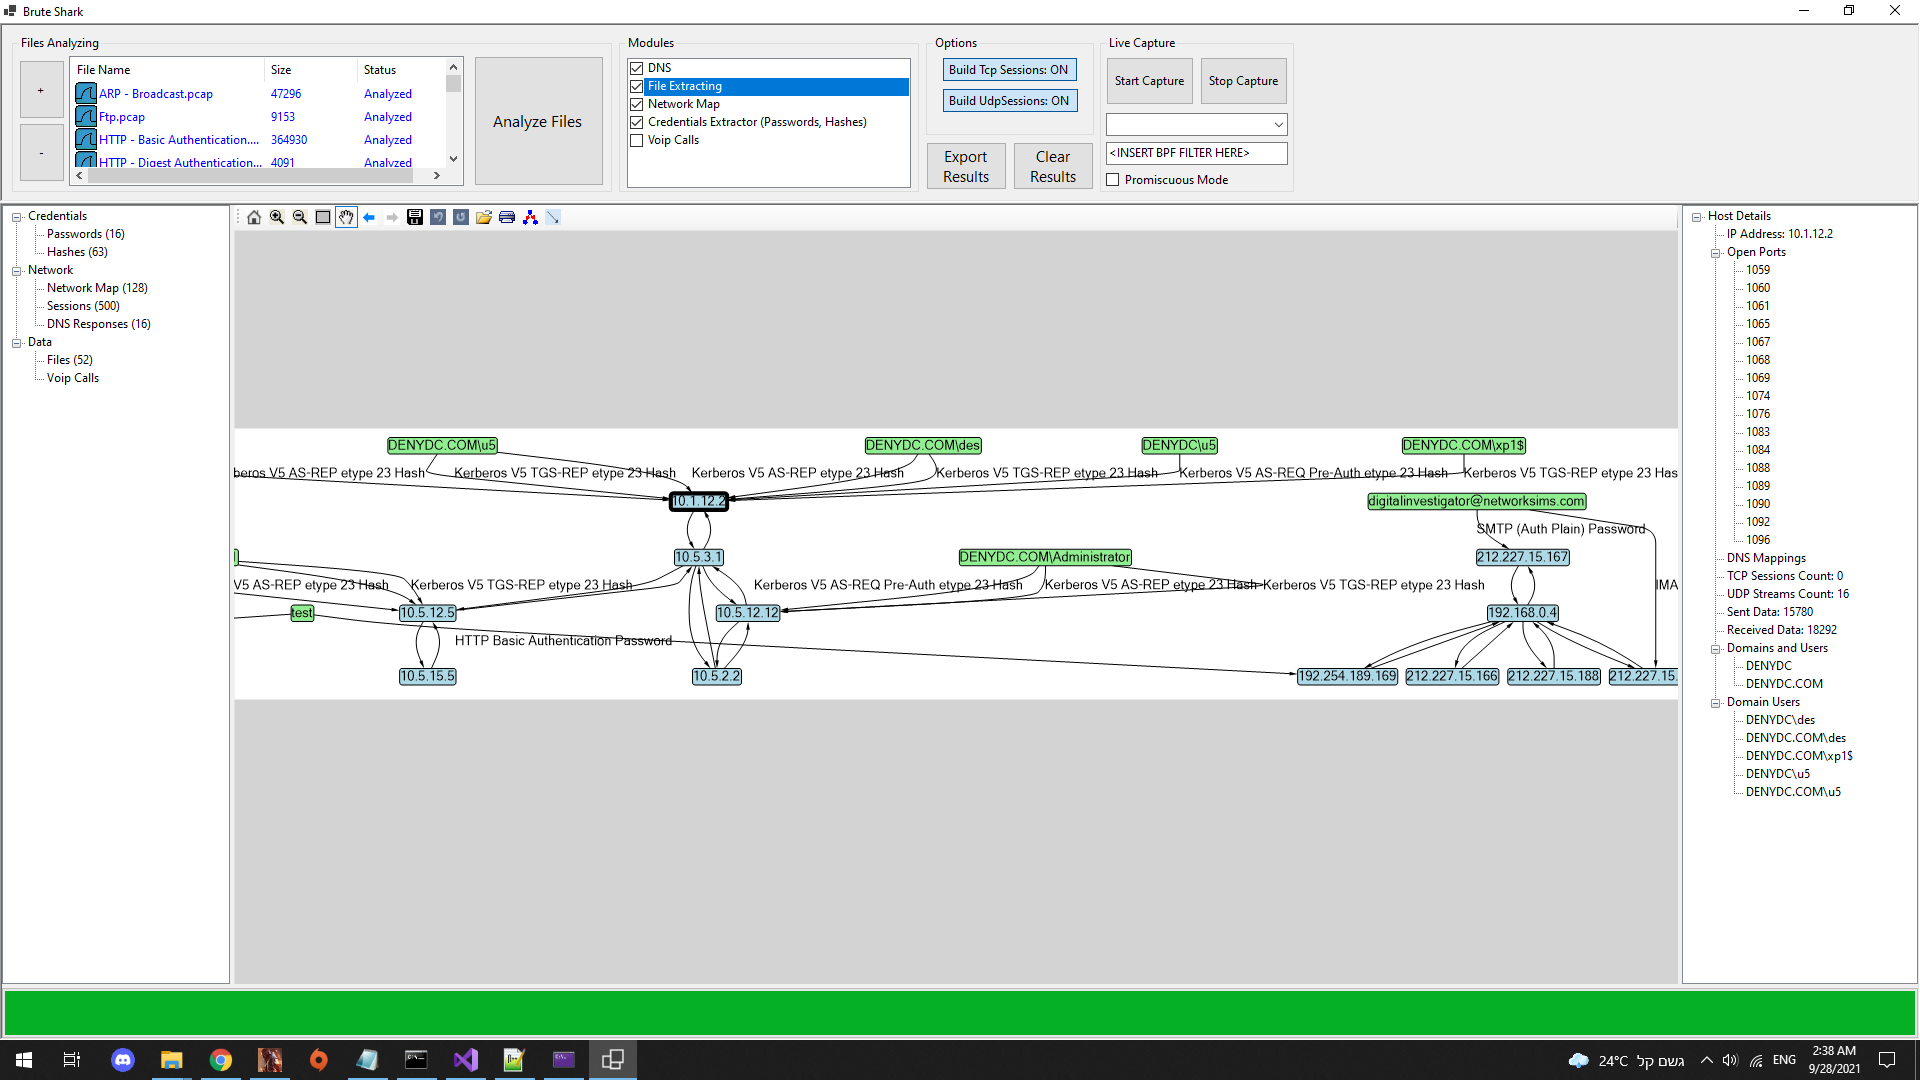
ltm
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
debuggersdigital-forensicsdisk-forensics+7
25
agent-hellboy/ltmltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
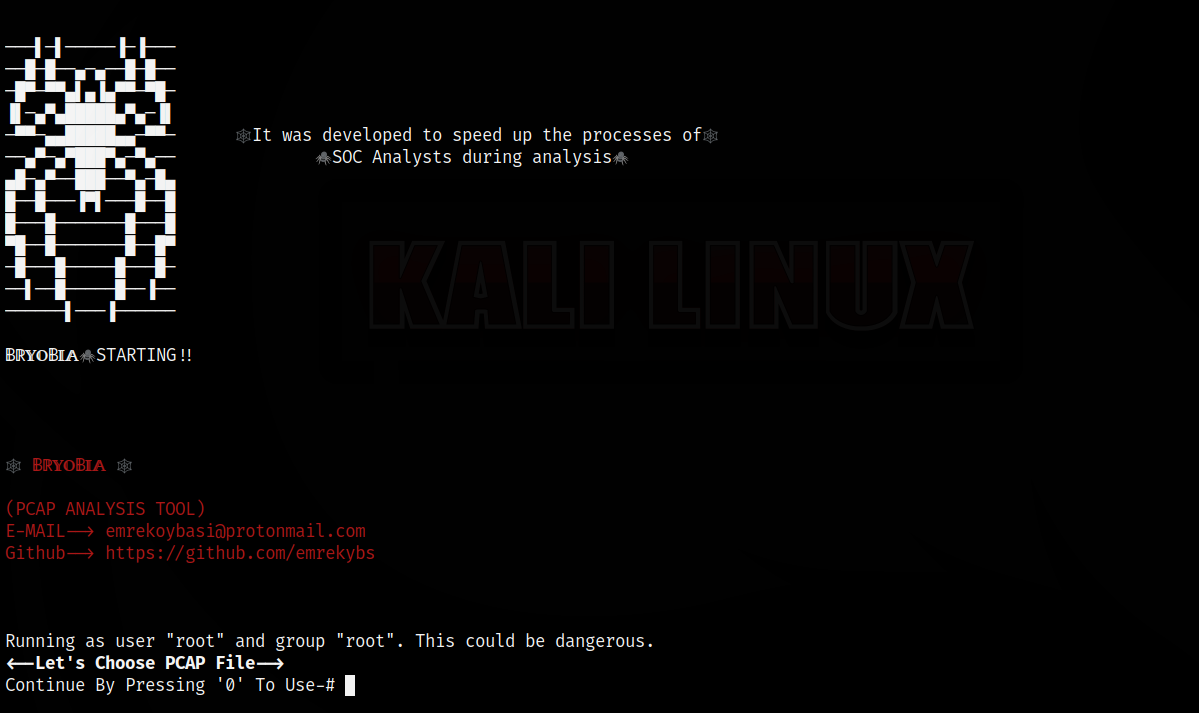 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
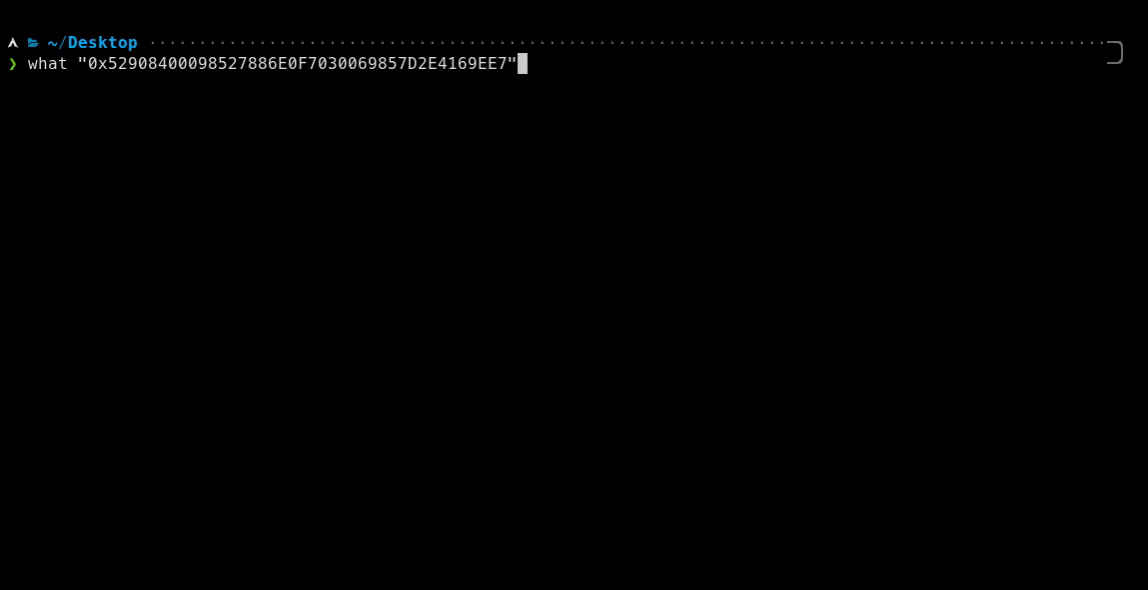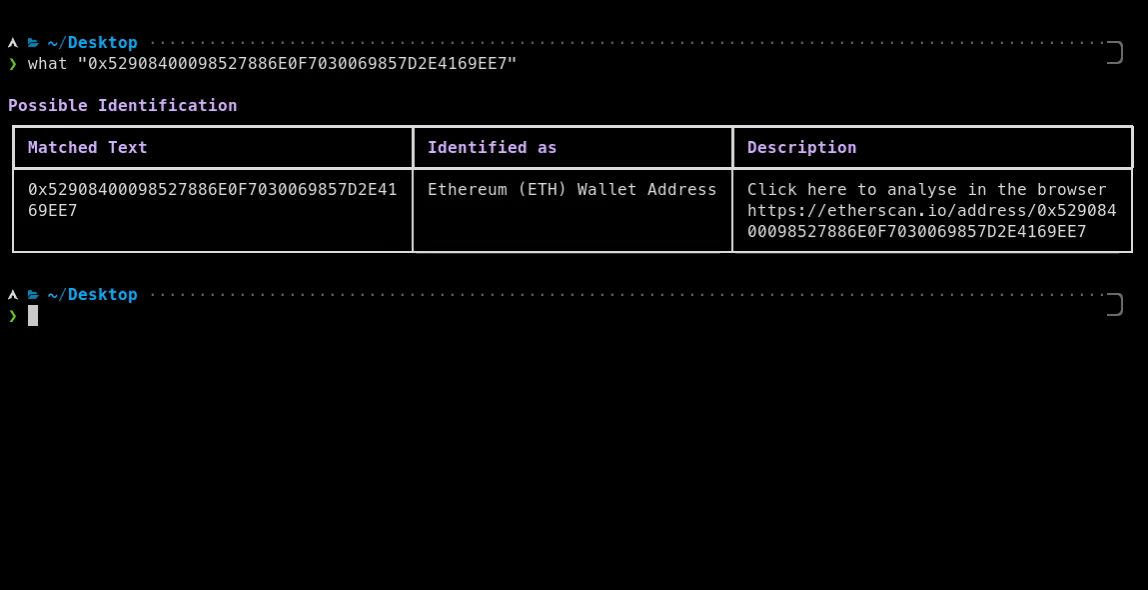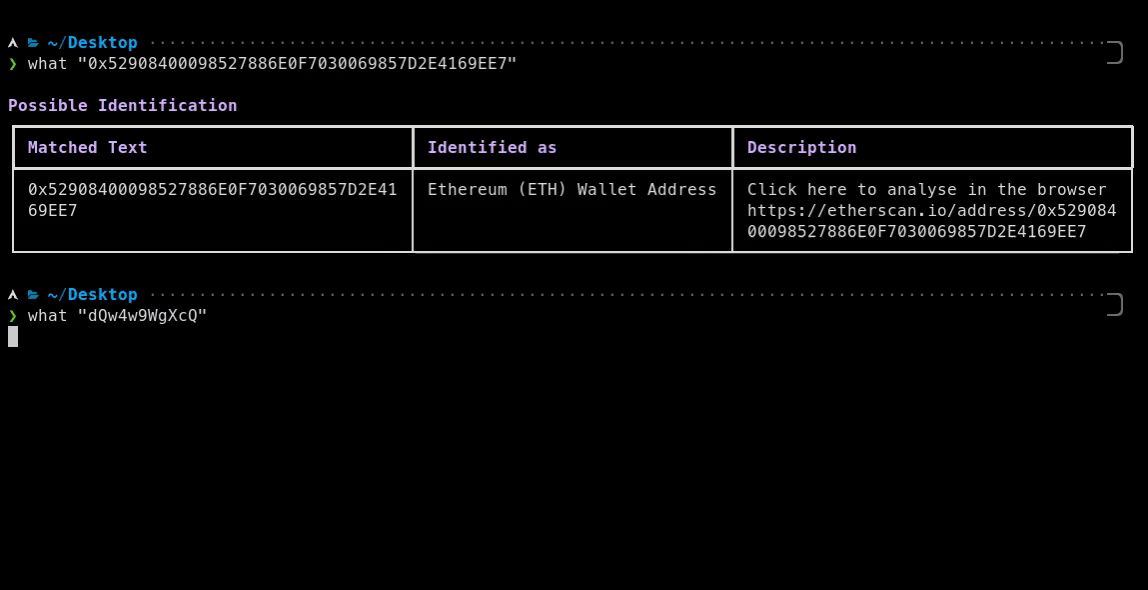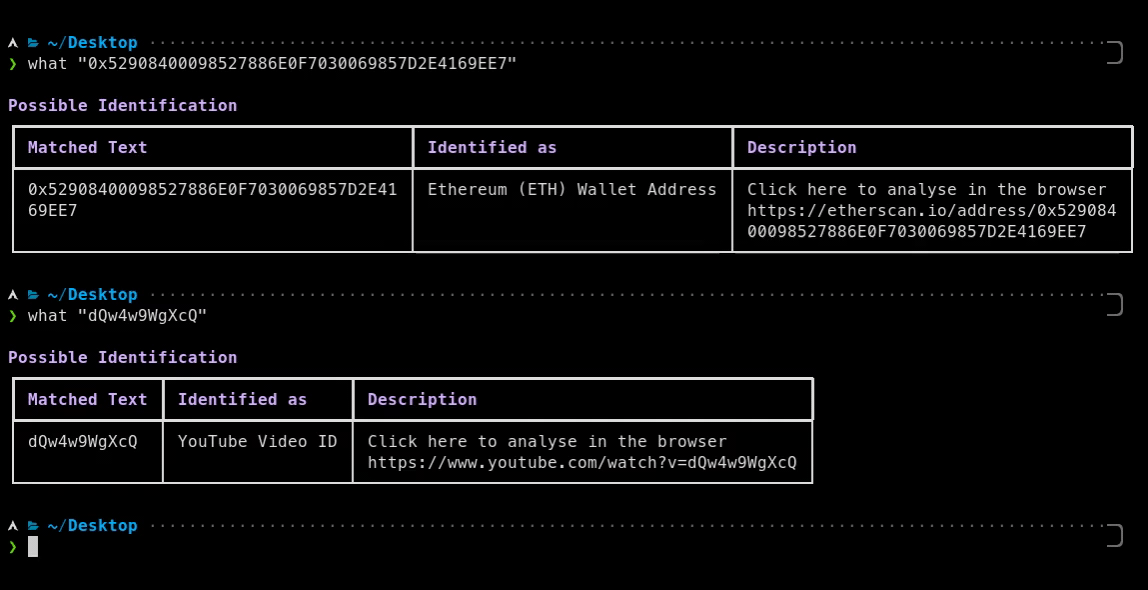 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
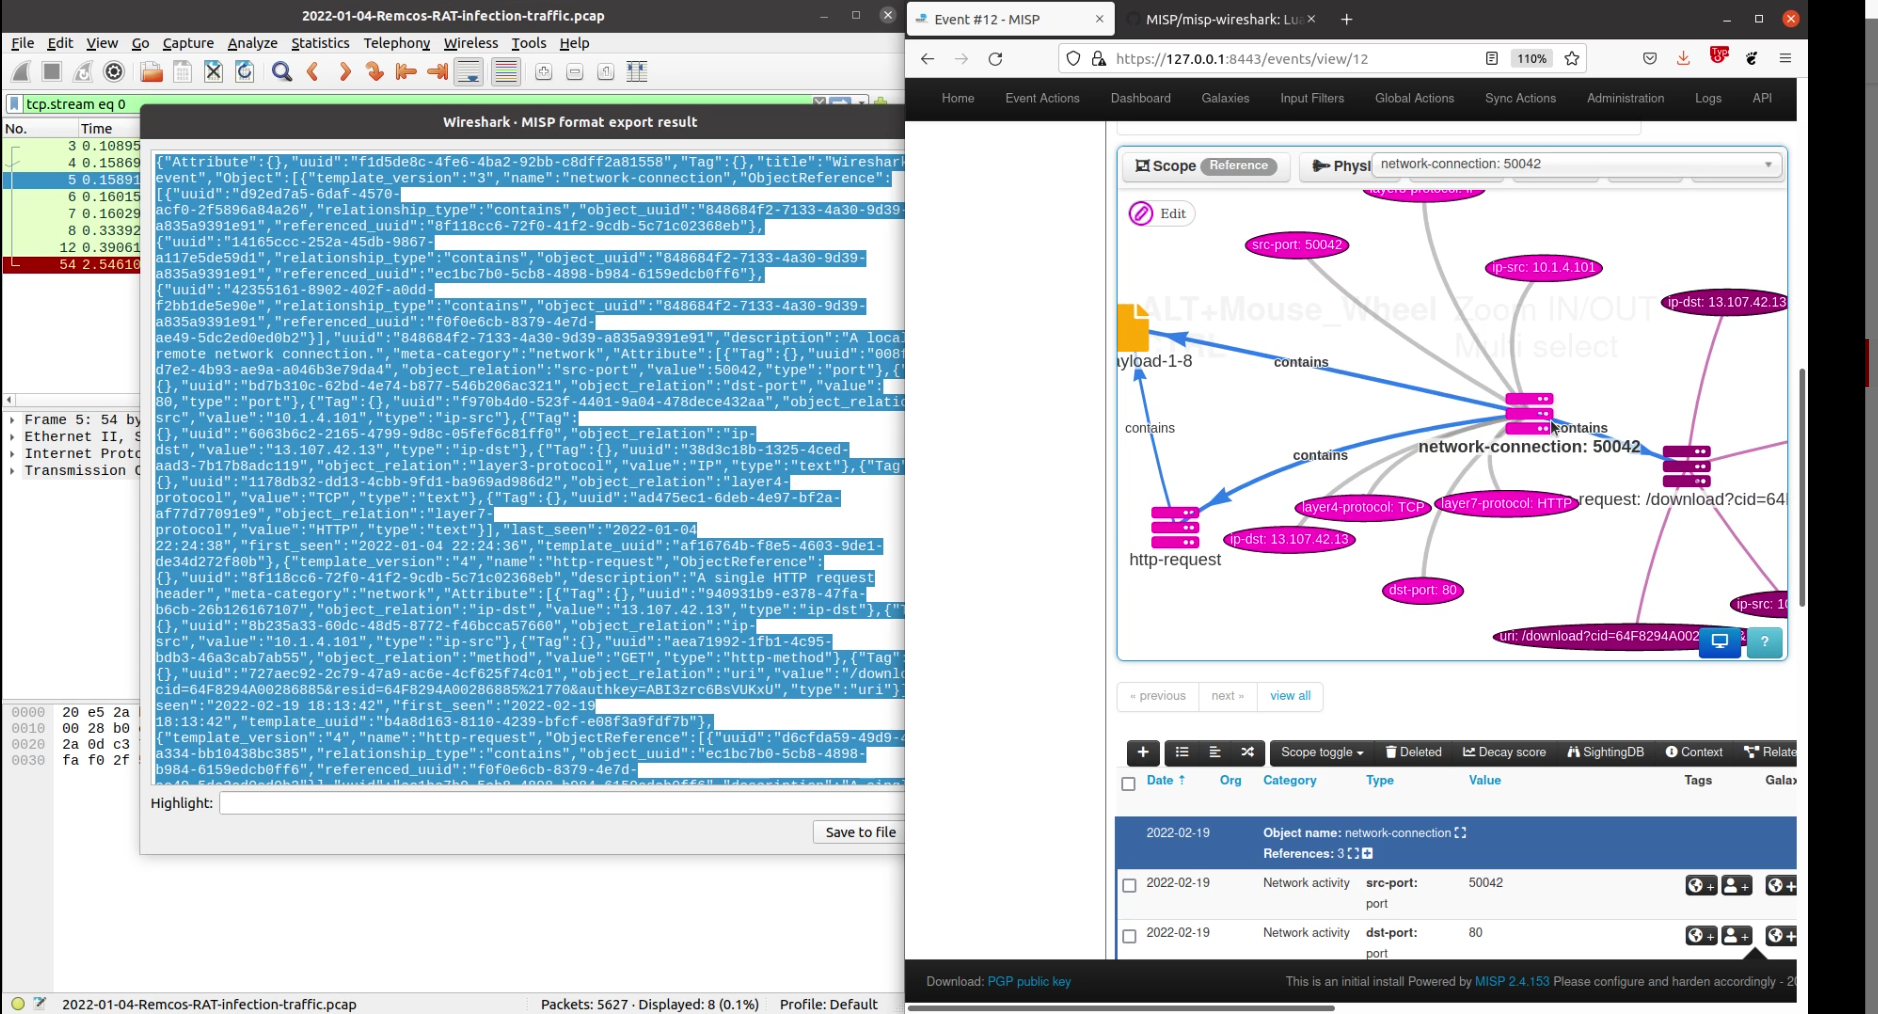 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
 benadia/an-integrated-wireless-network-forensic-analysis-framework
This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
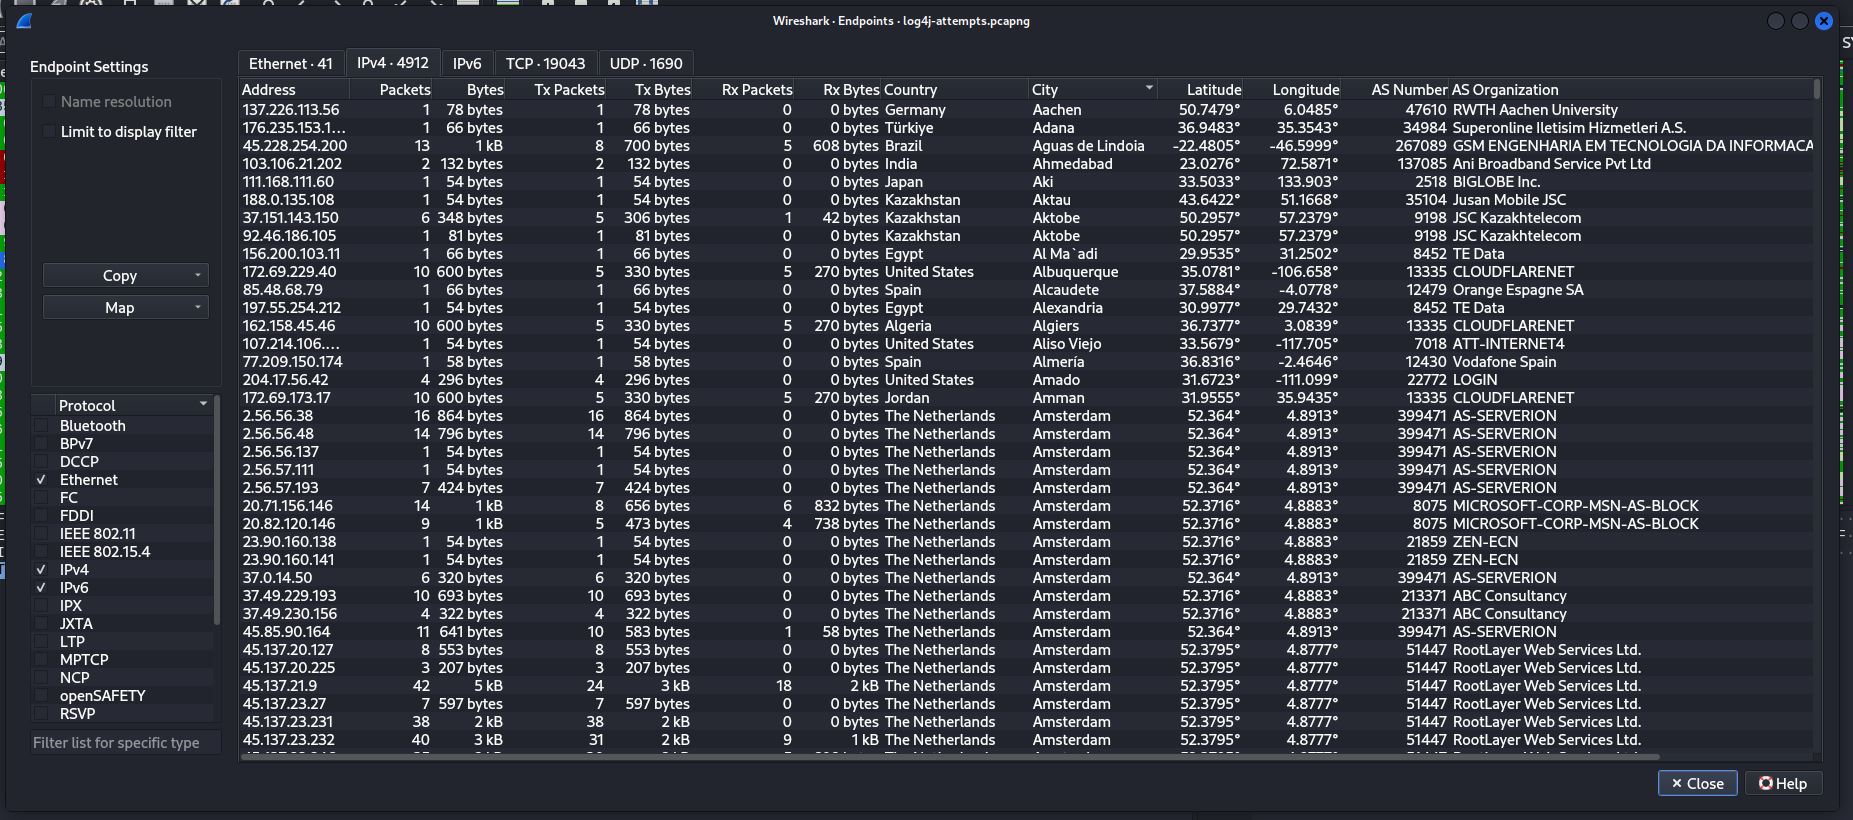 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…