
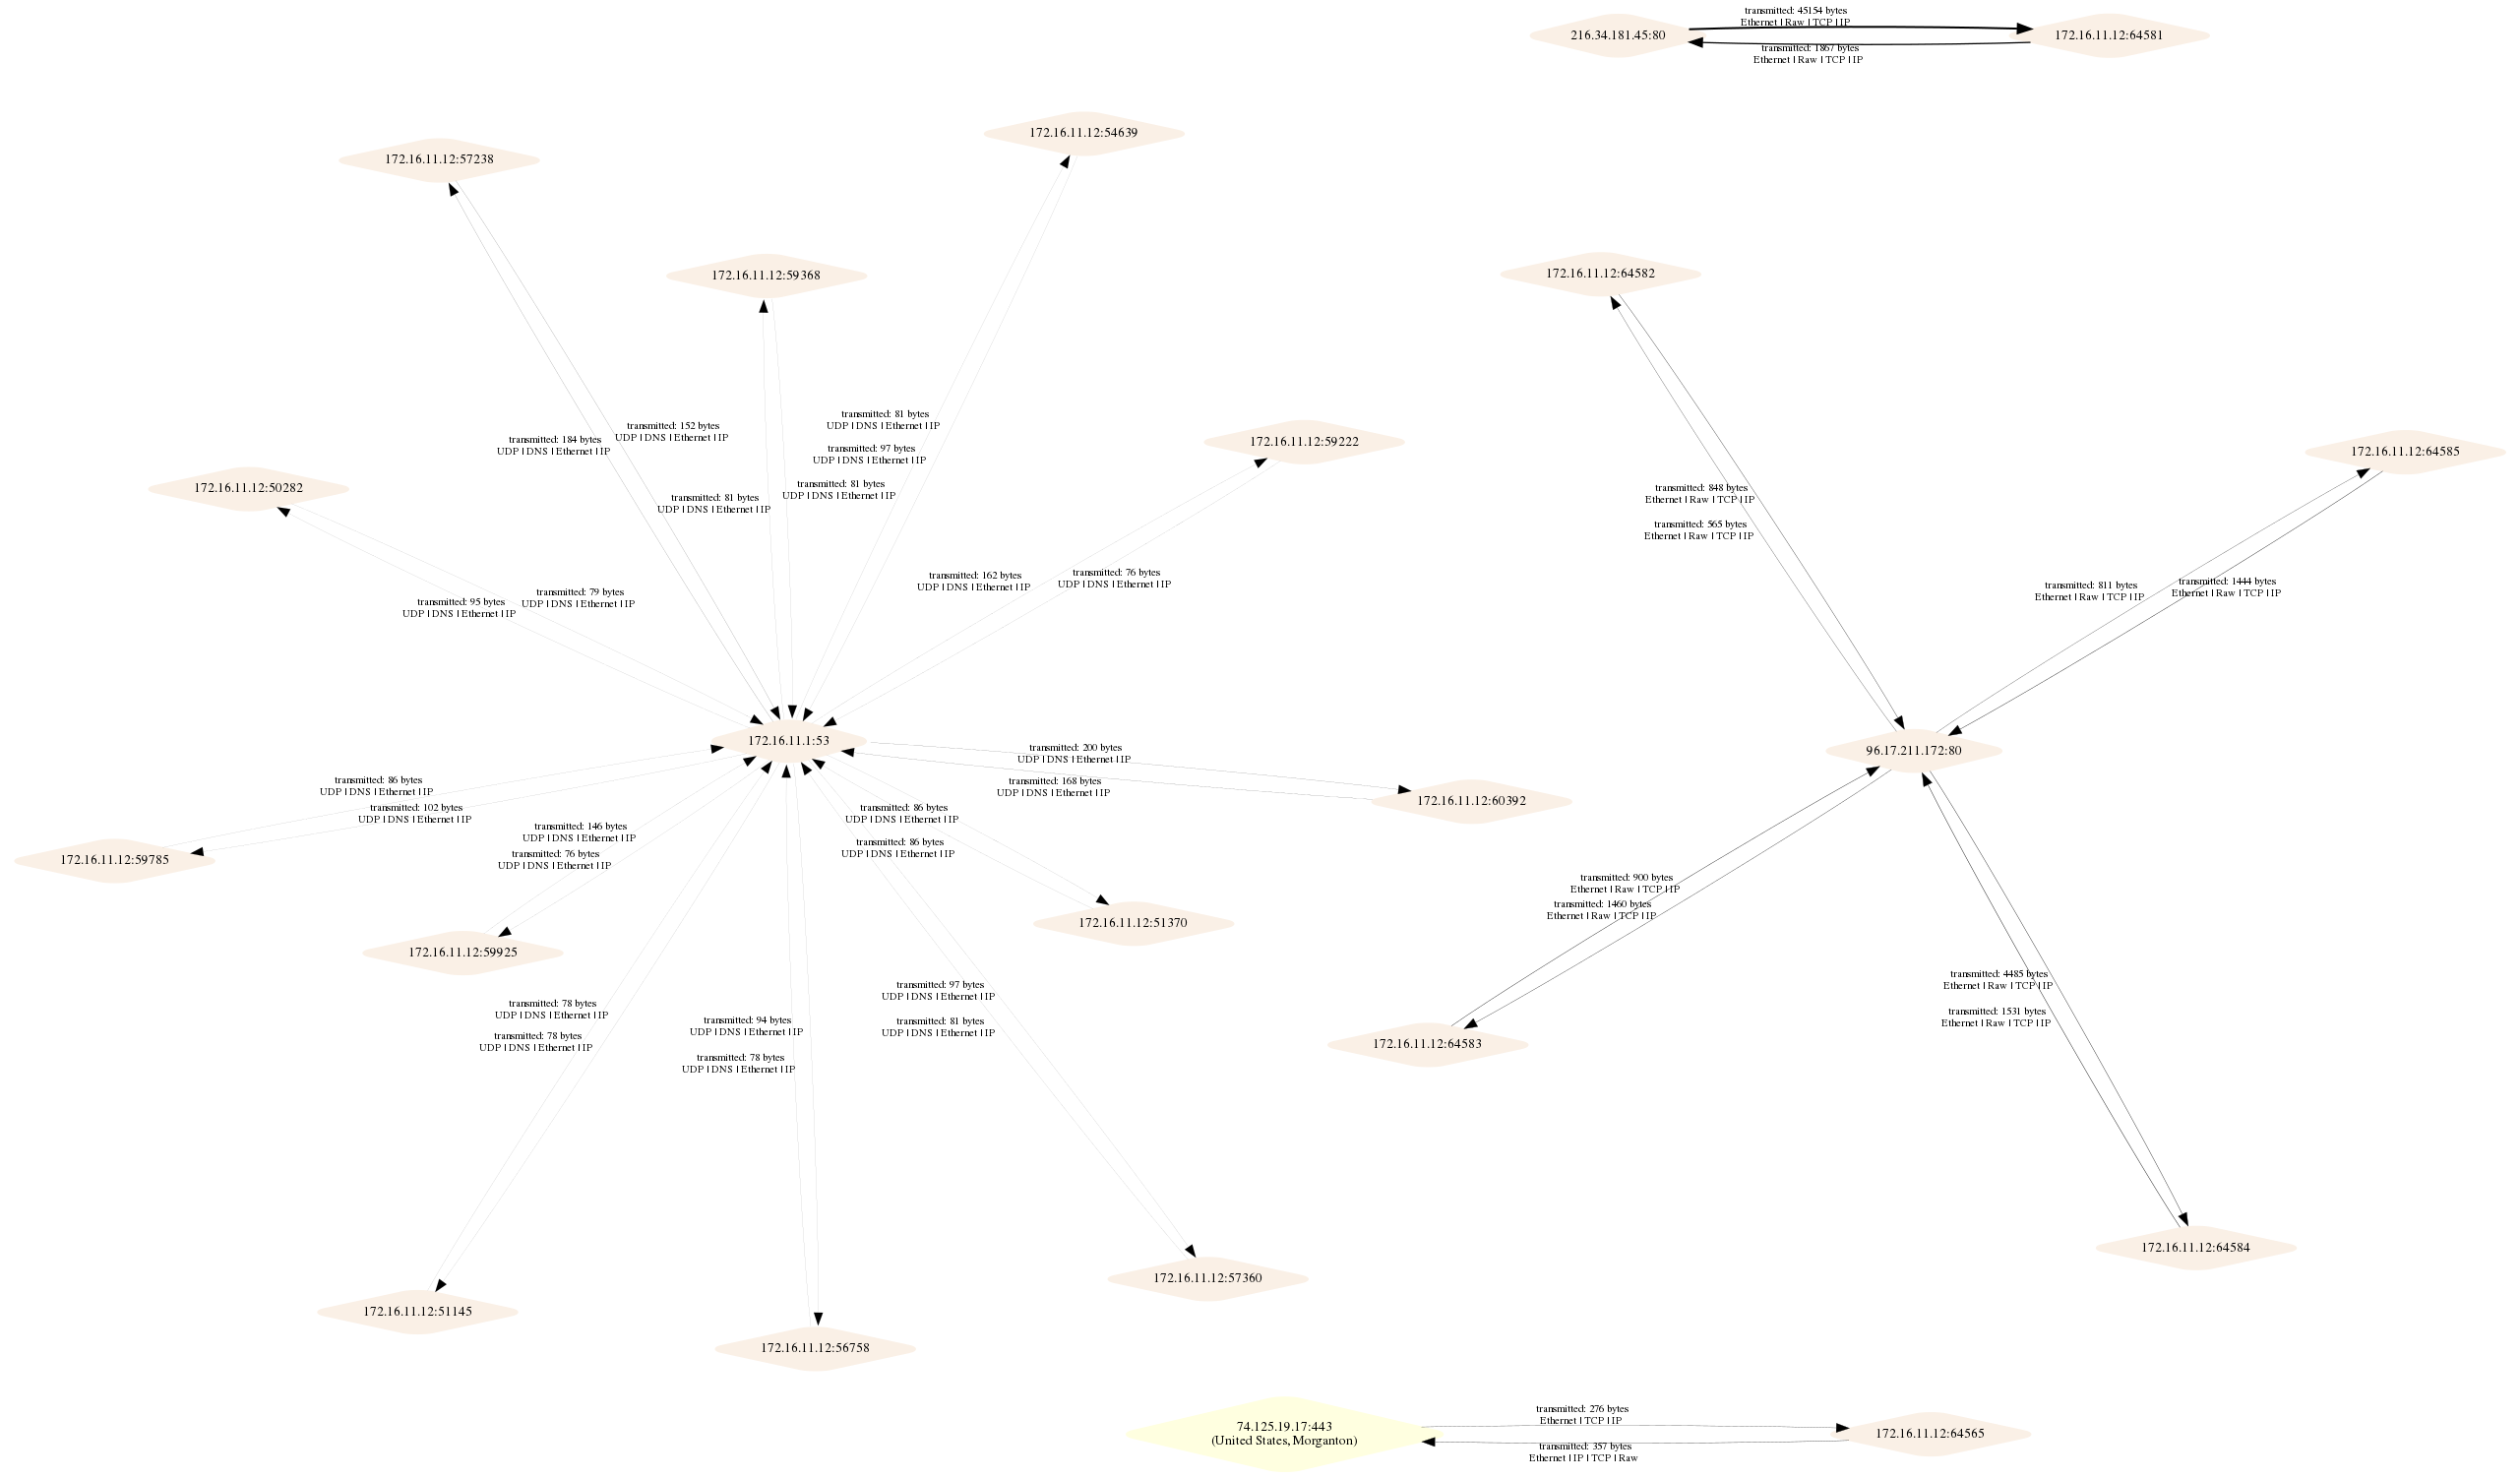
PcapViz
 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
information-gatheringnetwork-forensicsnetwork-mapping+1
360
1ultimat3/pcapvizVisualize network topologies and collect graph statistics based on pcap files

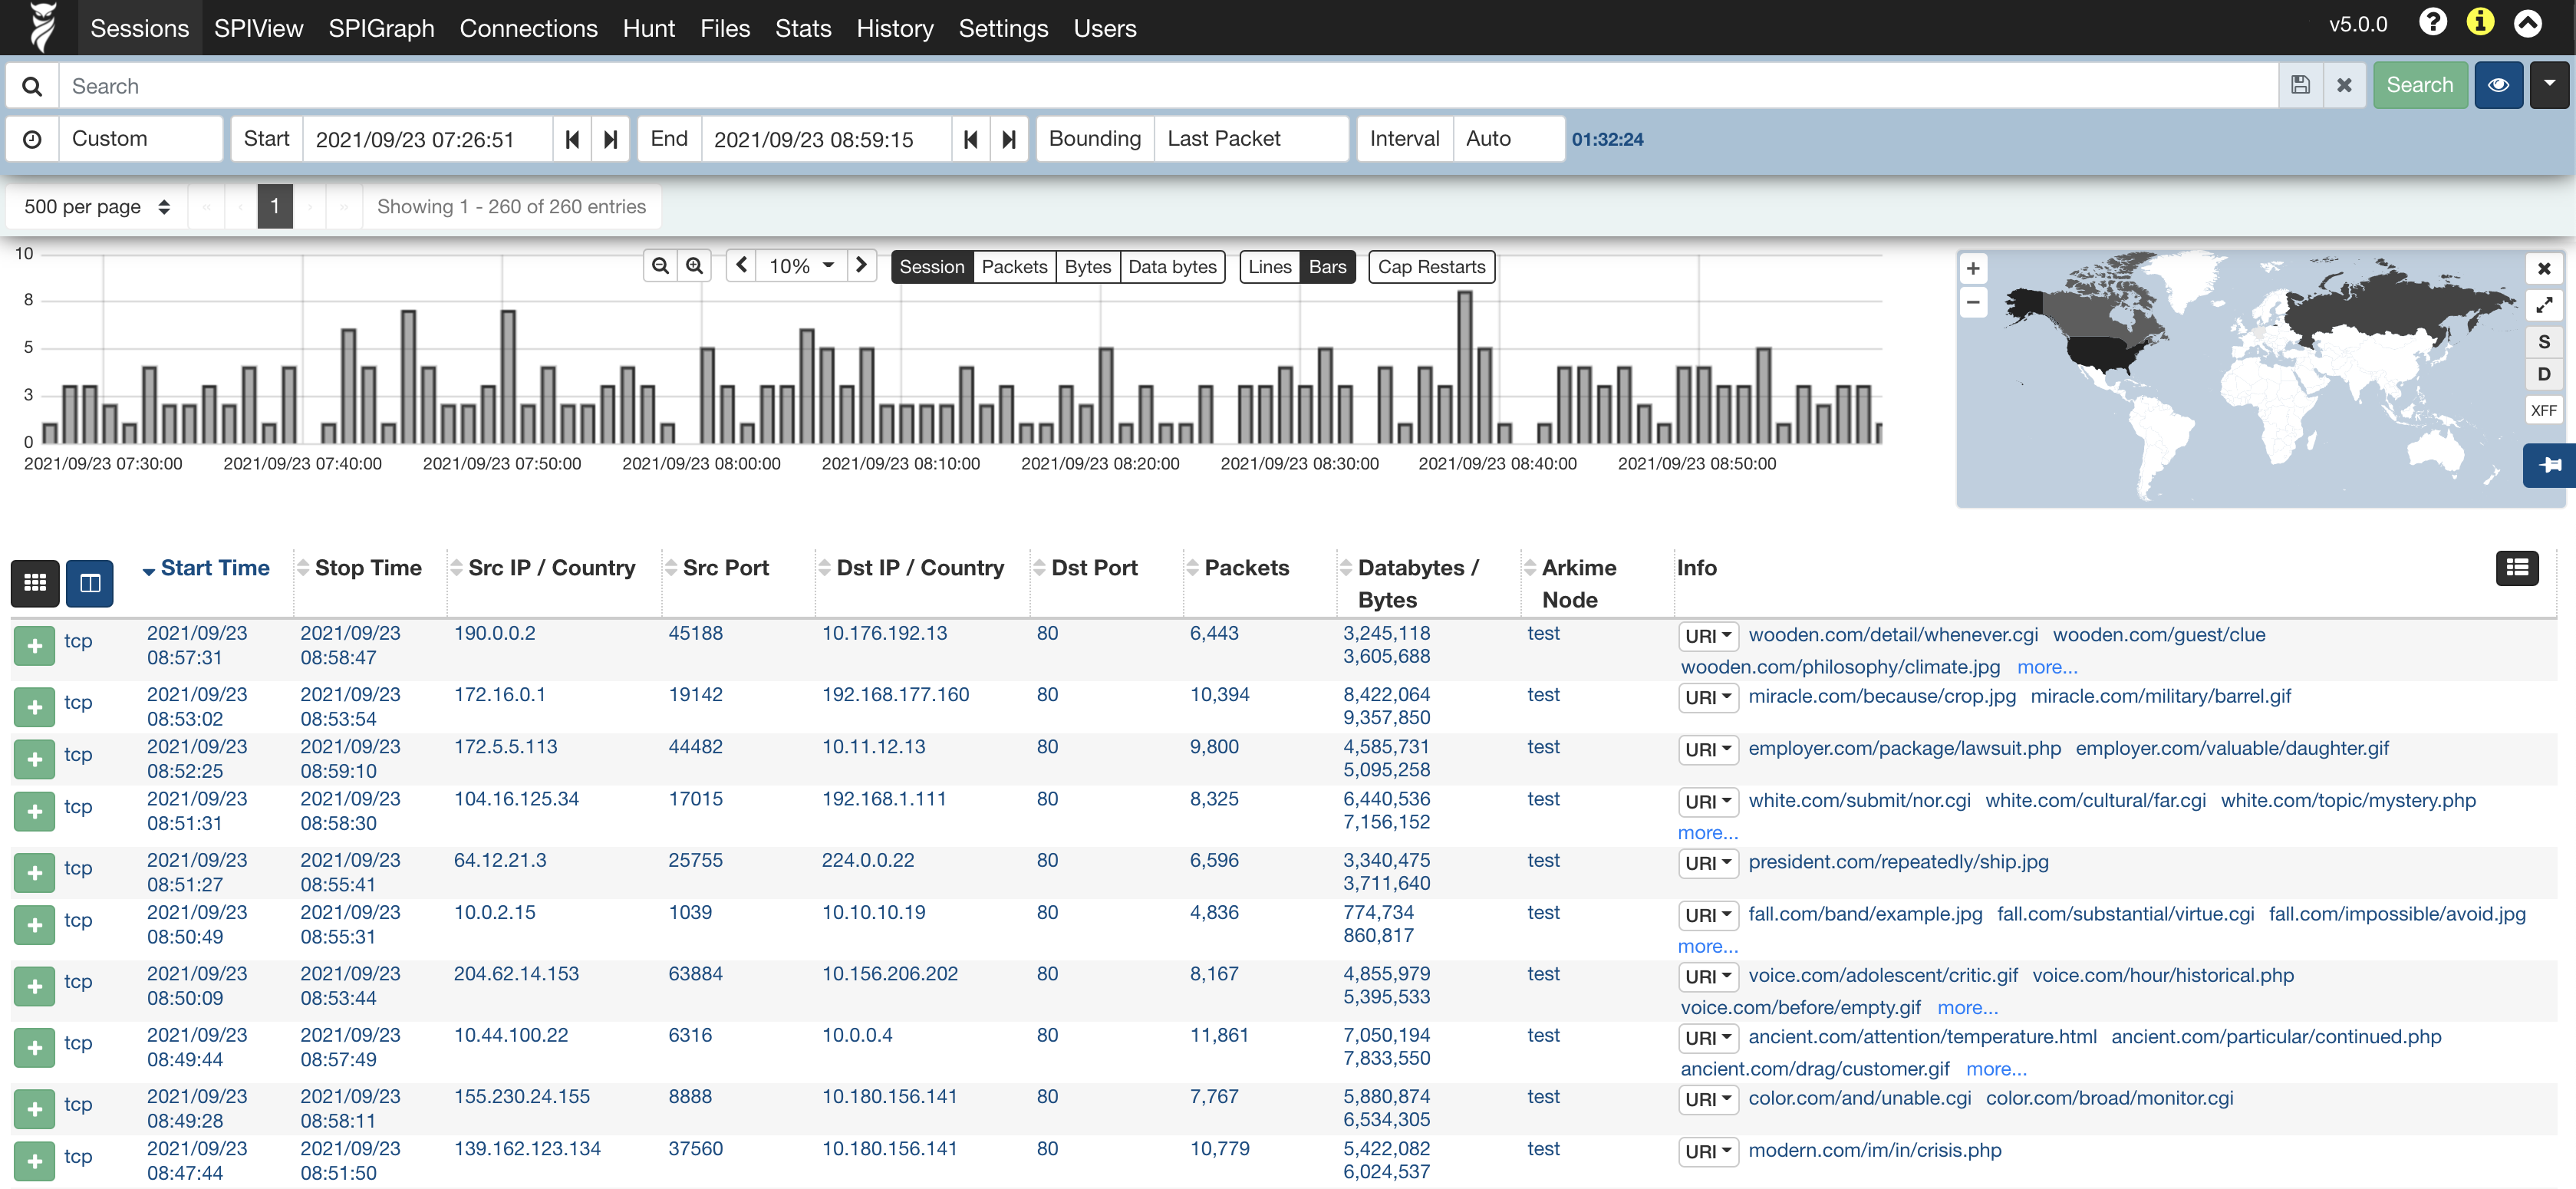 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 z4l4mi/ipgeo
Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
 azizaltuntas/network-analysis-tools
Pcap (capture file) Analysis Toolkit(v.1)
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
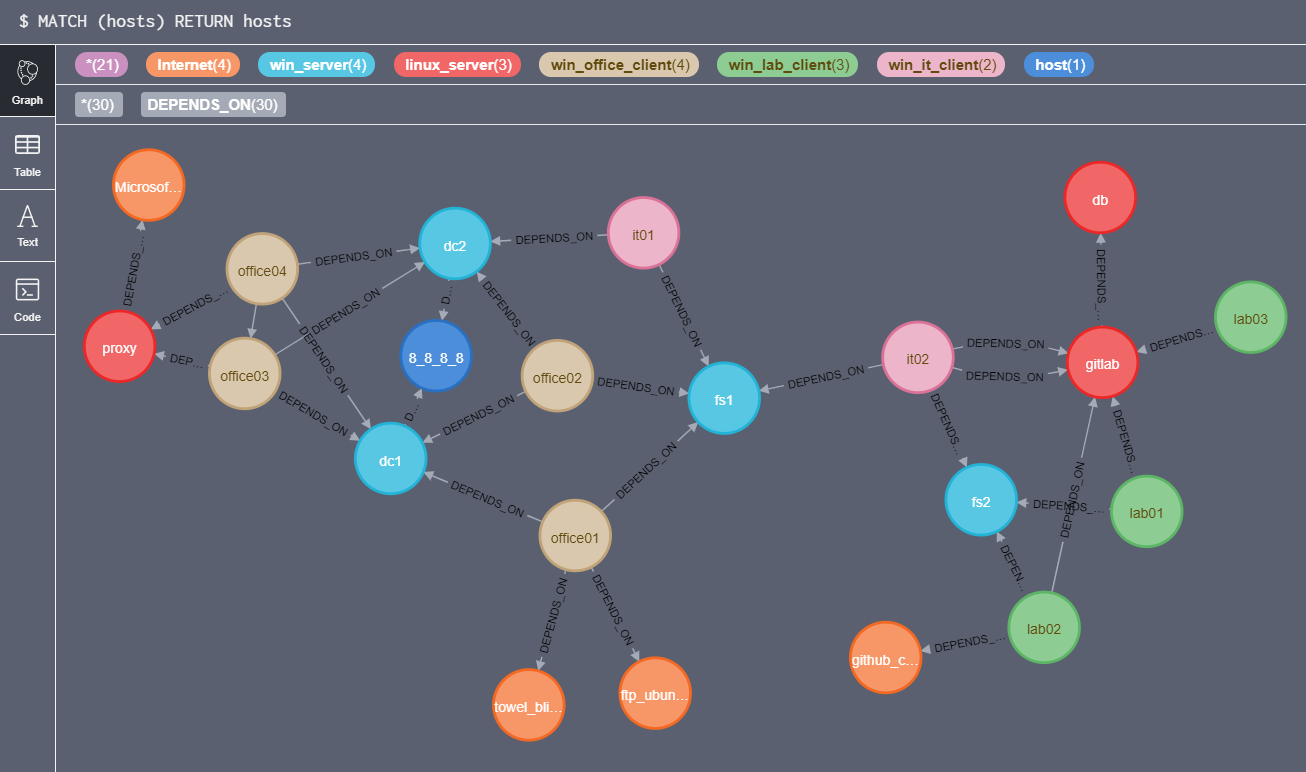 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines
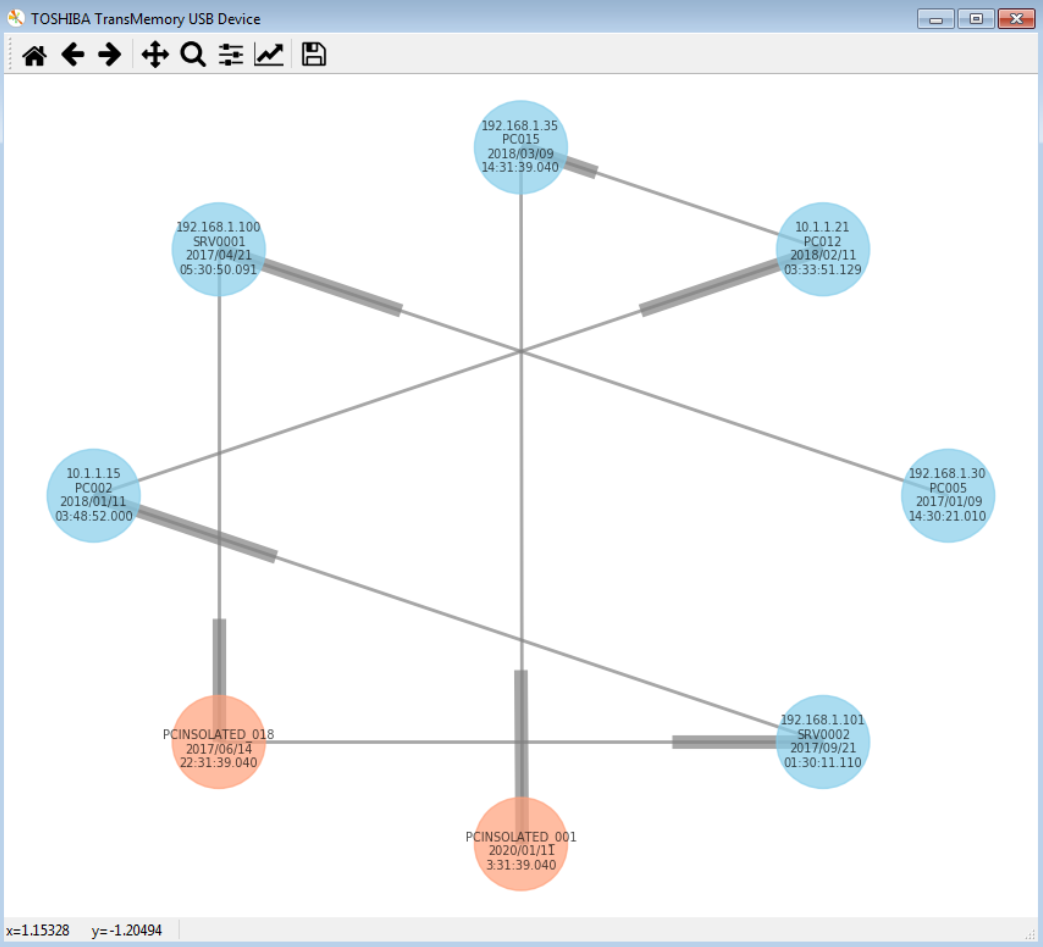 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 synacktiv/pcapan
A pcap capture analysis helper
 corelight/zeek-spicy-stun
A Zeek STUN protocol analyzer based on Spicy.