
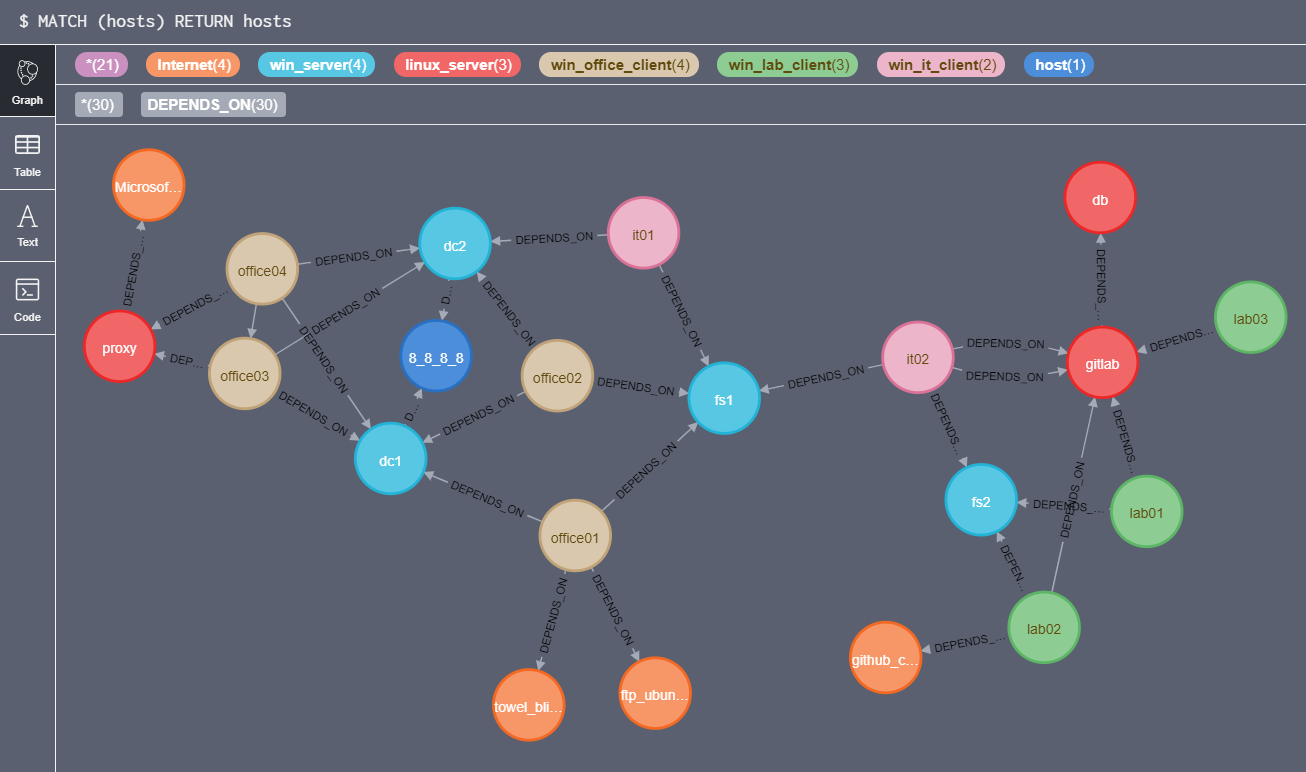
netstat2neo4j
 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines
information-gatheringlog-analysisnetwork-forensics
trinitor/netstat2neo4jcreate cypher create statements for neo4j out of netstat files from multiple machines
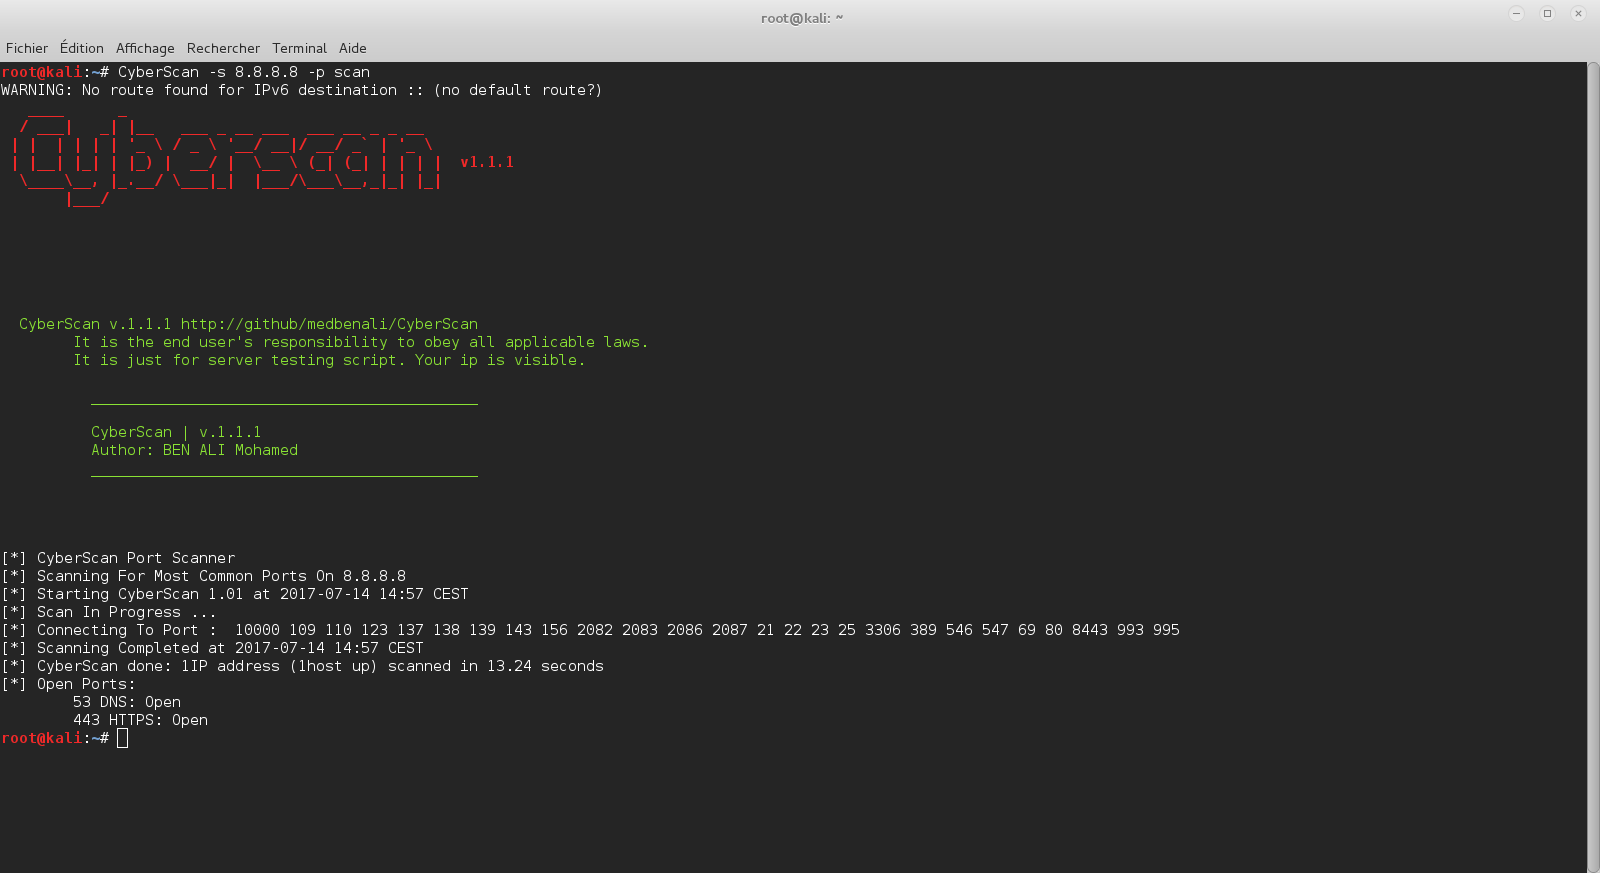 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 z4l4mi/ipgeo
Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
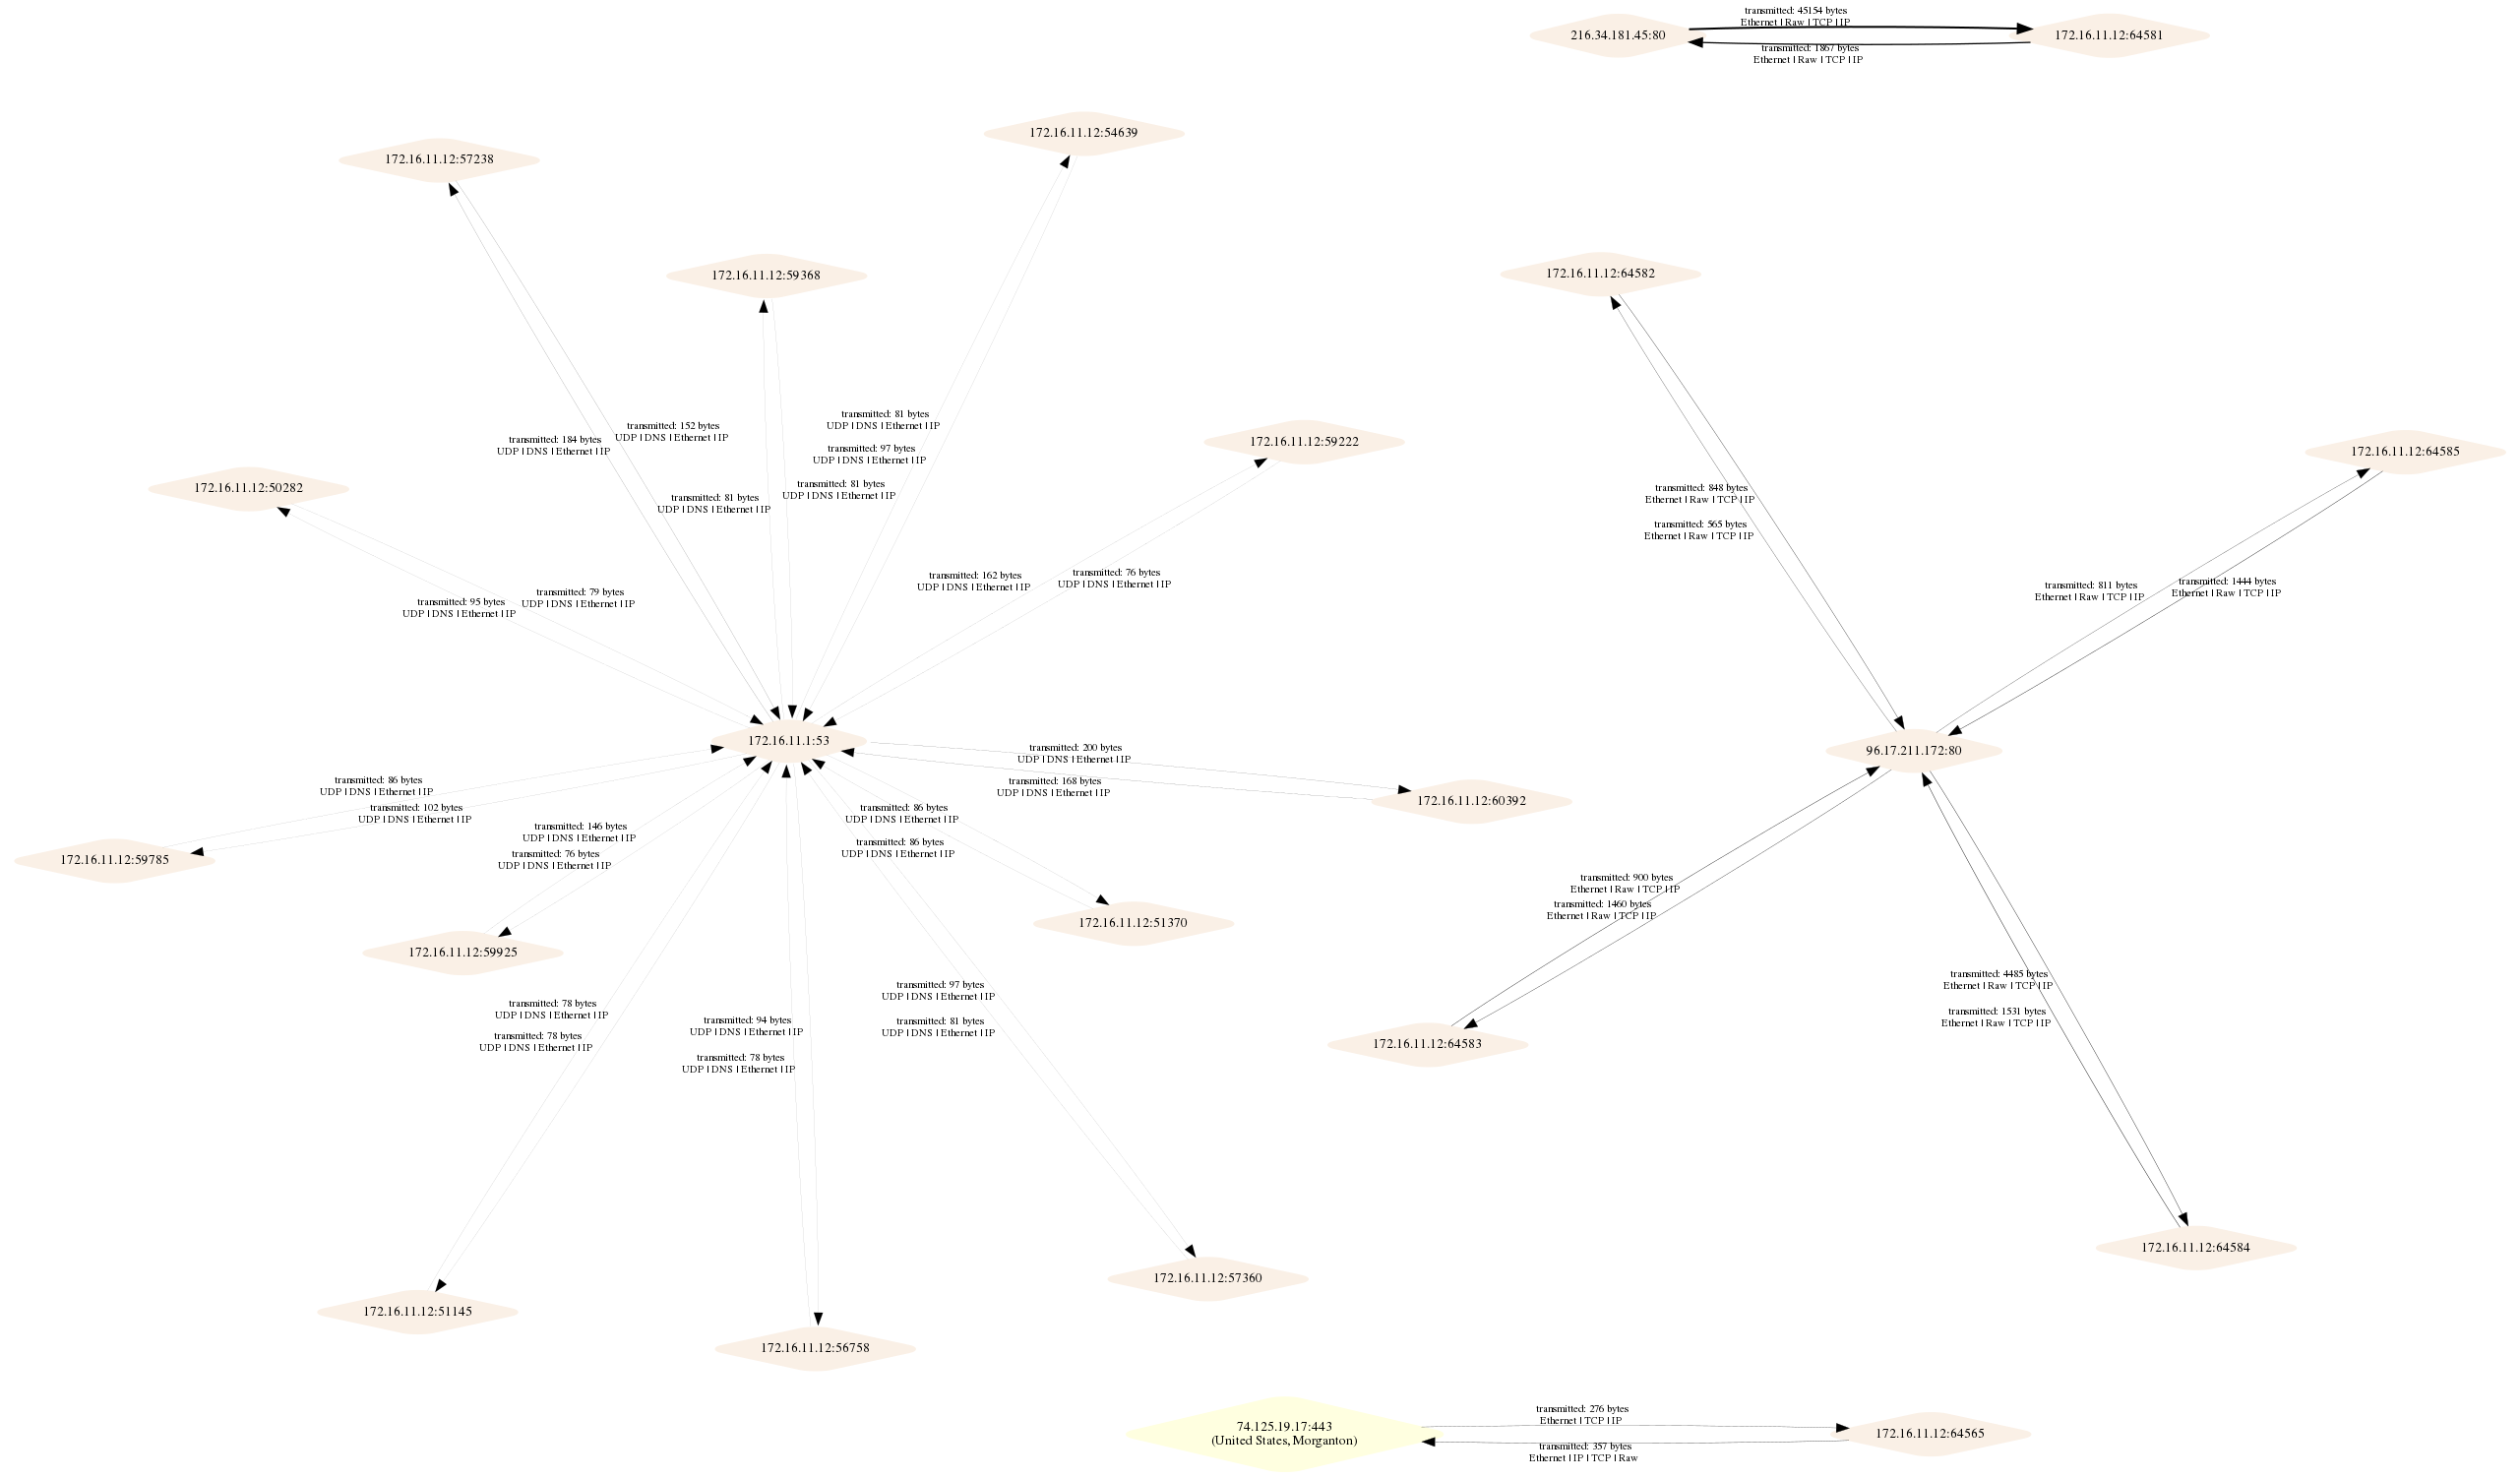 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 cristianzsh/forensictools
Collection of forensic tools
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 benadia/an-integrated-wireless-network-forensic-analysis-framework
This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
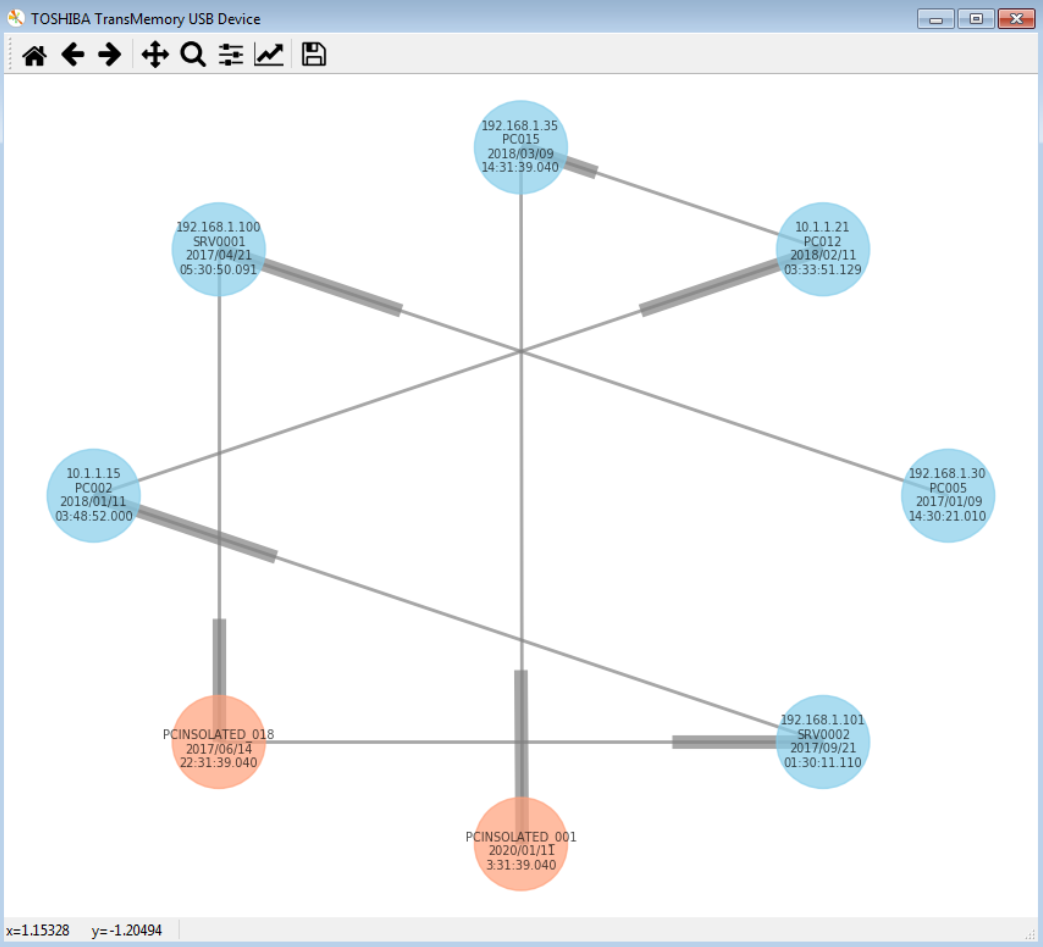 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
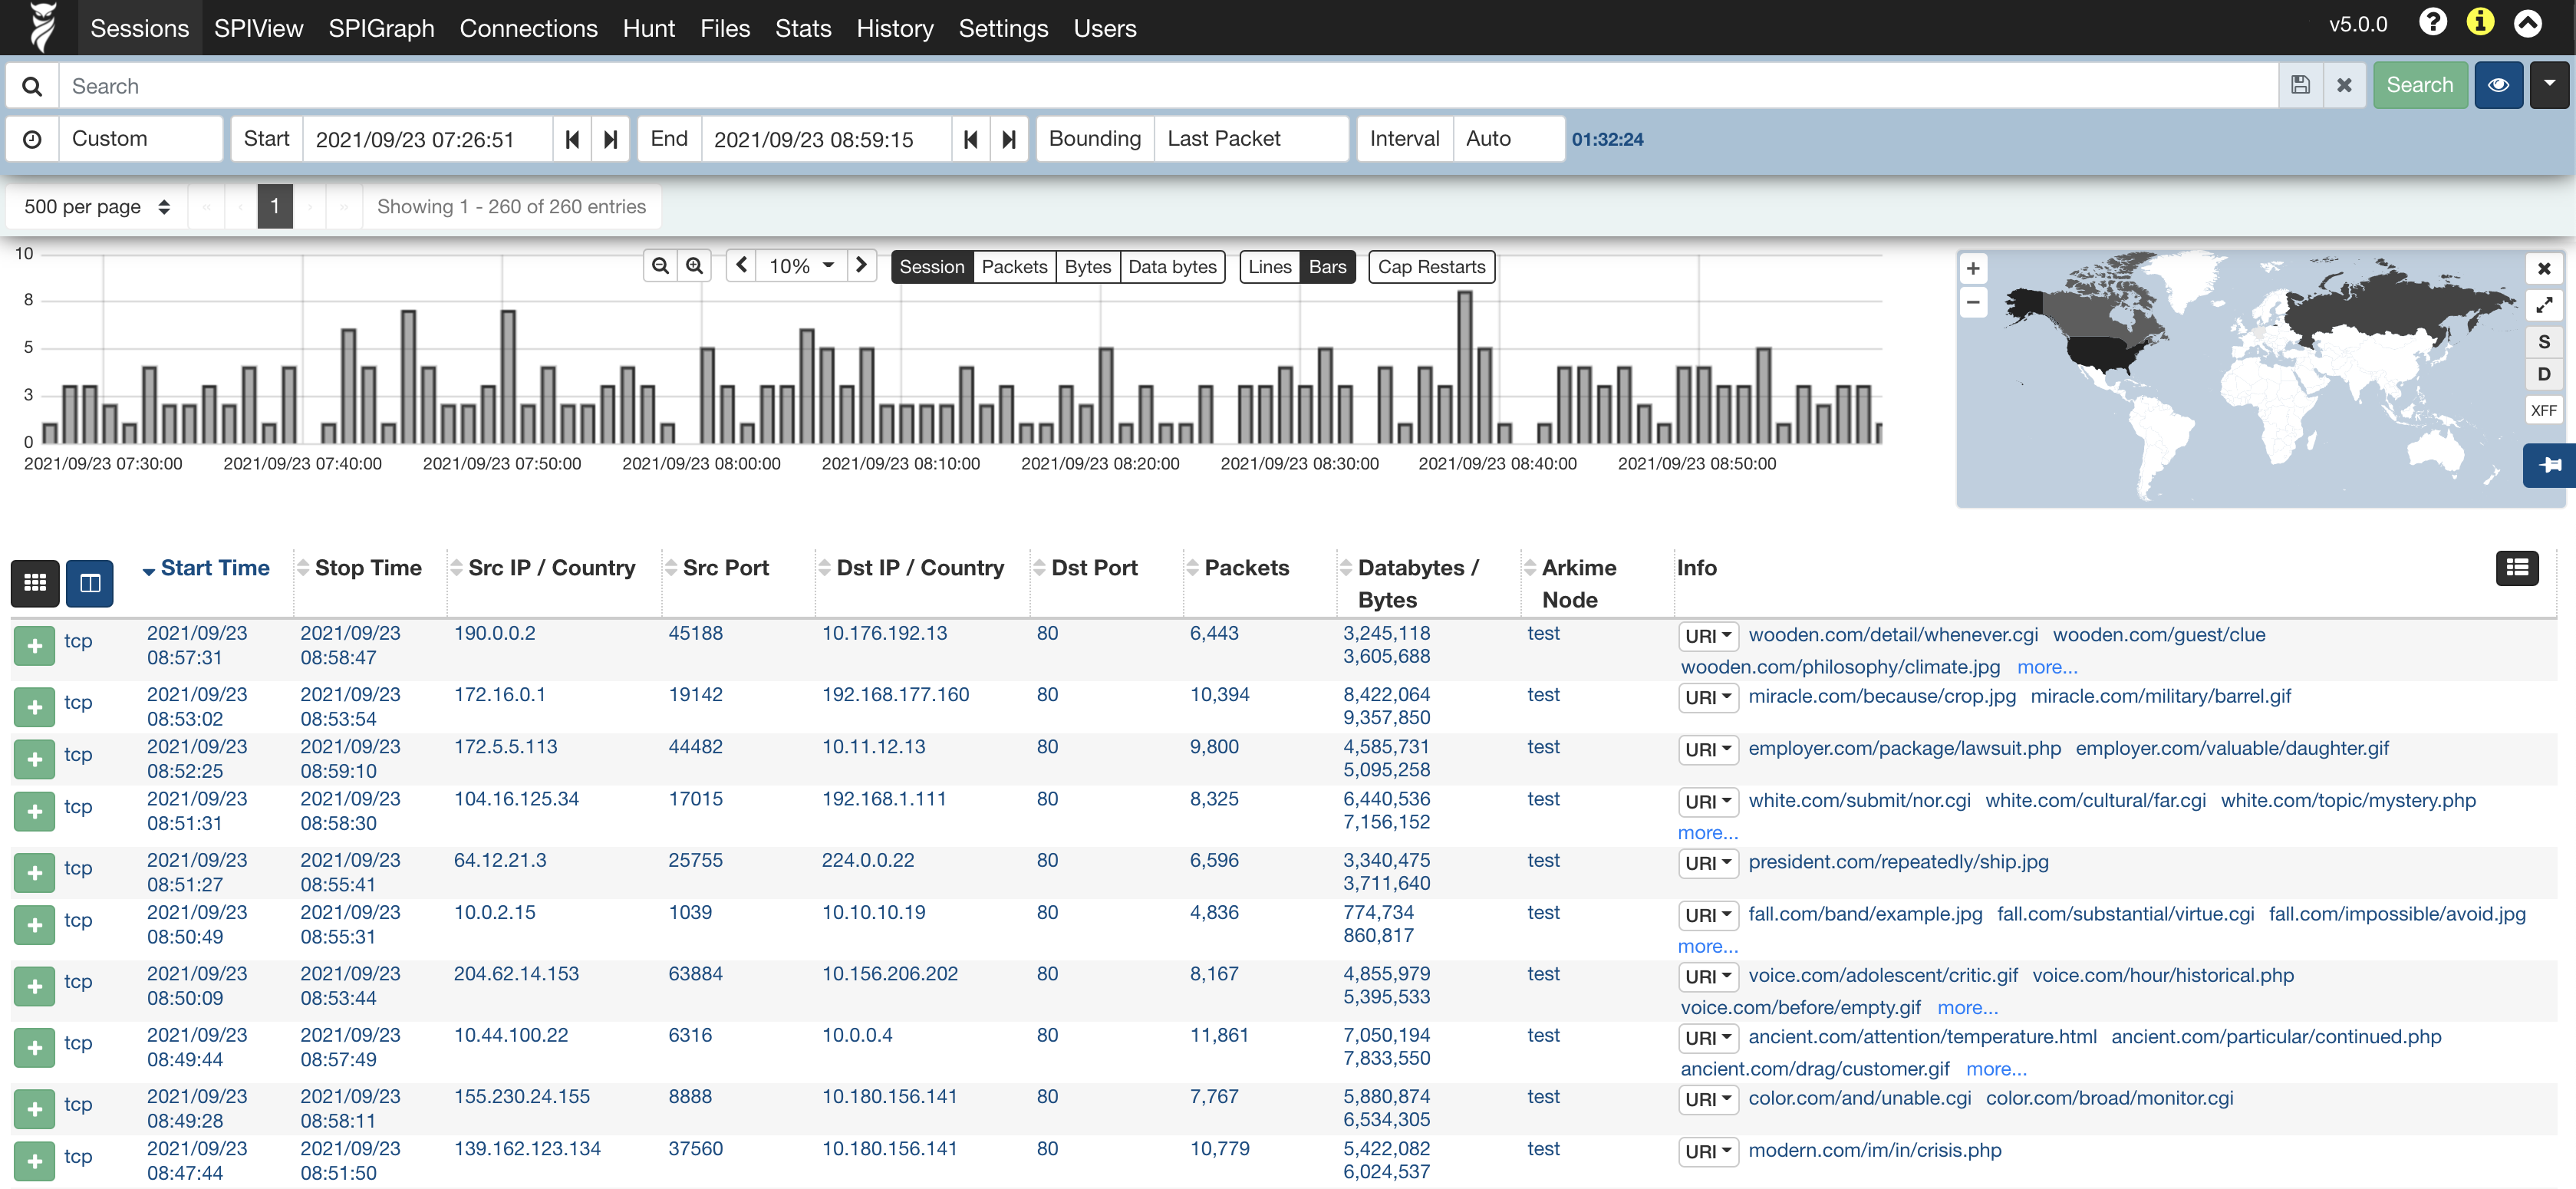 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 azizaltuntas/network-analysis-tools
Pcap (capture file) Analysis Toolkit(v.1)
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
 synacktiv/pcapan
A pcap capture analysis helper
 corelight/zeek-spicy-stun
A Zeek STUN protocol analyzer based on Spicy.