
ramnit_traffic_parser
 nao-sec/ramnit_traffic_parser
Parsing Ramnit's traffic
command-and-controldigital-forensicsforensics+3
48 years ago
nao-sec/ramnit_traffic_parserParsing Ramnit's traffic
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
 naacbin/covenantdecryptor
Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…
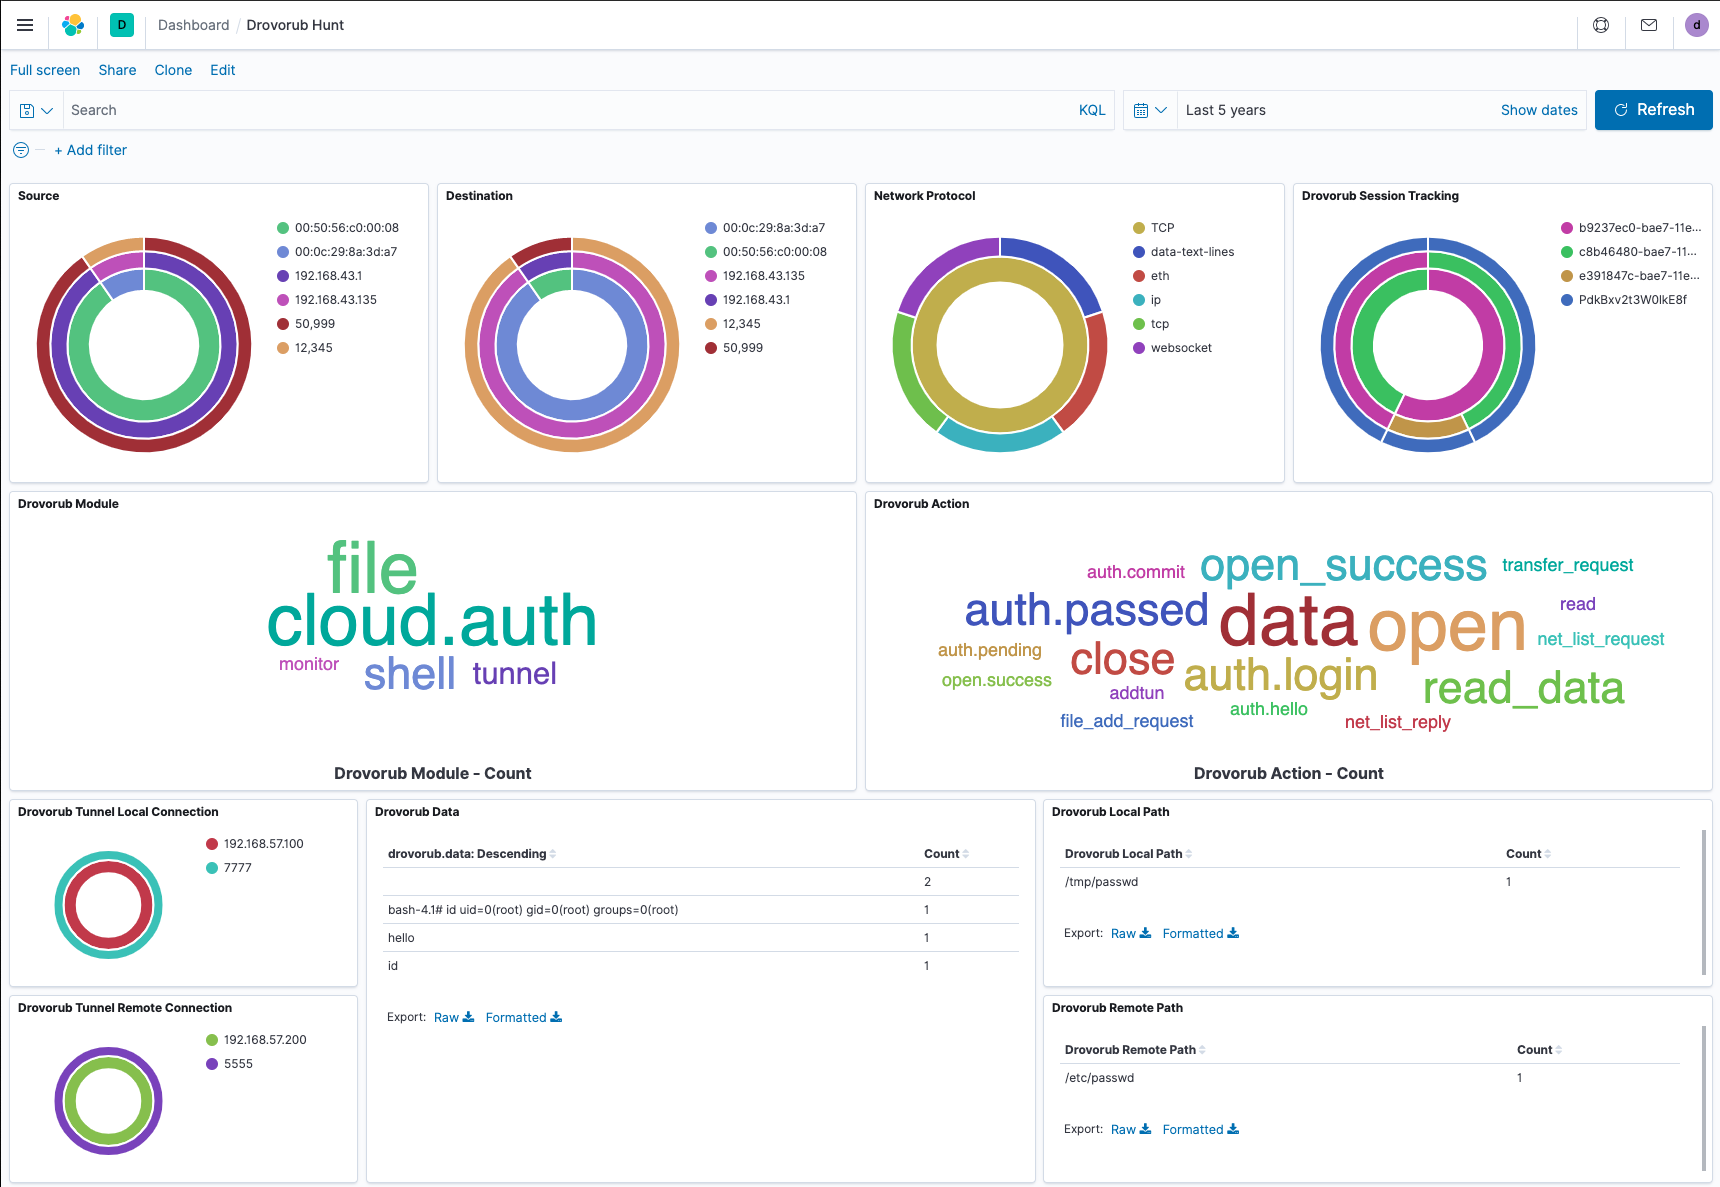 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
 fox-it/dissect.cobaltstrike
Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
 watchtowrlabs/citrix-netscaler-cve-2026-88771-iocs
Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 jhatchi/nexacorp-dfir-inc-2026-001
DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 corelight/zeek-netsupport-detector
A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.
 ahmed-tarek22752/rce-cve-2017-0199-detection-analysis
This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…
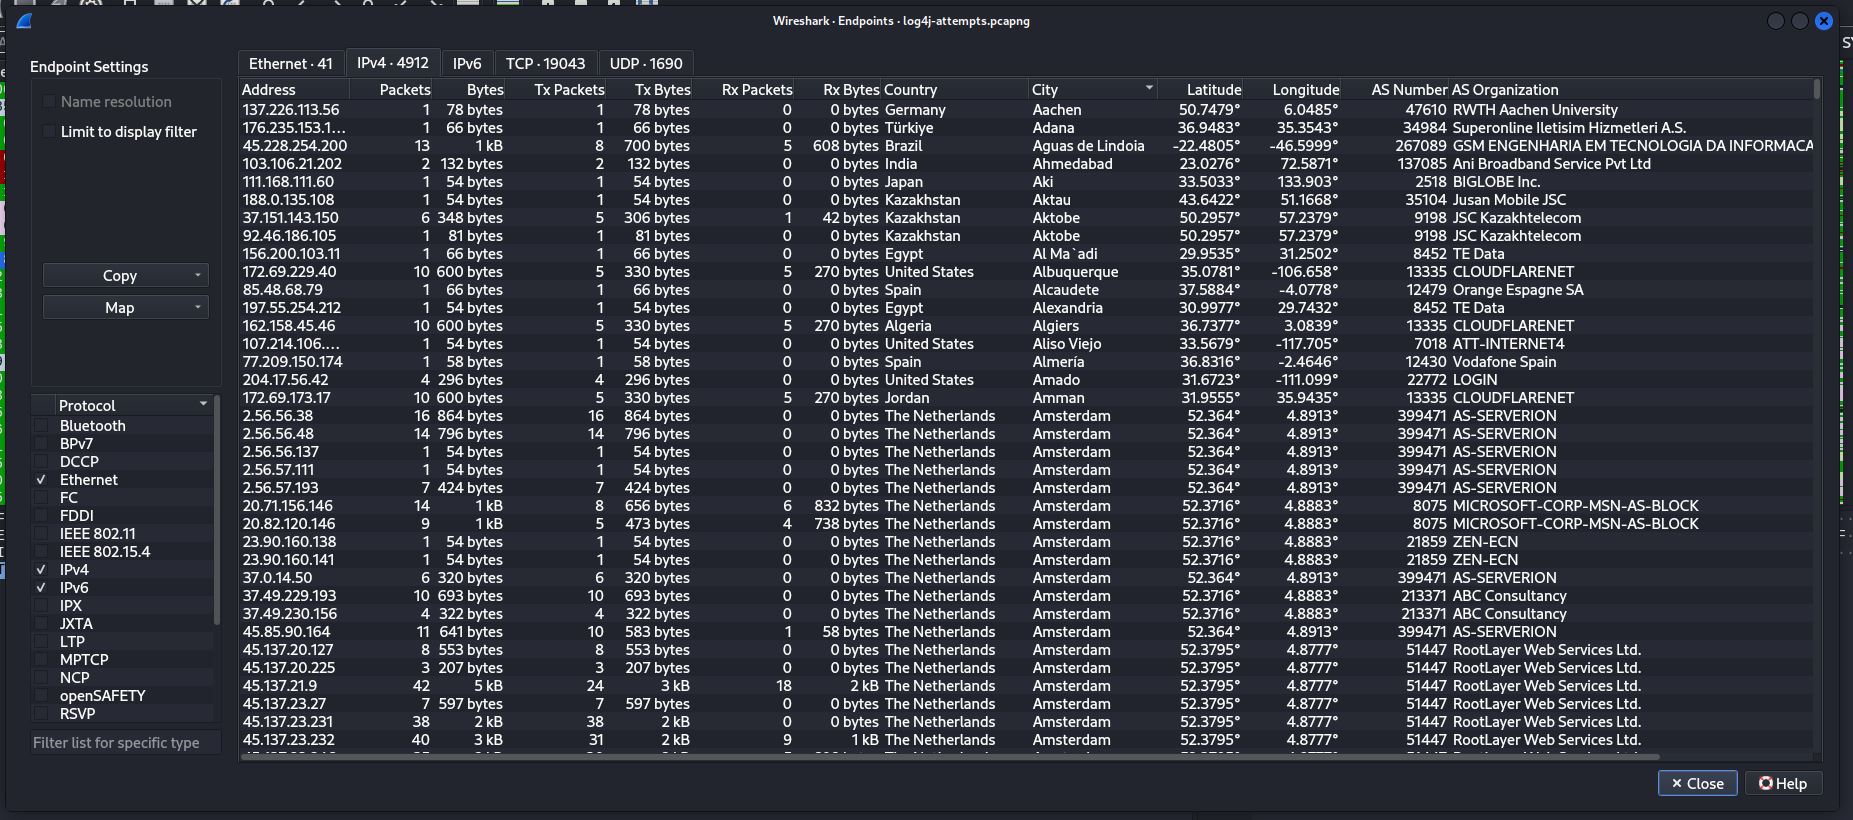 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 aelshimony-cloud/openwire-cve-2023-46604-investigation
Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…
 blackoclock/xls-to-dbatloader-or-guloader-for-agenttesla-variant
CVE-2017-0199 XLS --> HTA --> VBS --> STEGANOGRAPHY --> DBATLOADER/GULOADER STYLE MALWARE