

scripts
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
digital-forensicsforensicsincident-response+5
clausing/scriptsCollection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
 nccgroup/mortimer
A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.
 cristianzsh/forensictools
Collection of forensic tools
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
 awakecoding/wireshark-rdp
Wireshark RDP resources
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 benadia/an-integrated-wireless-network-forensic-analysis-framework
This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
 watchtowrlabs/citrix-netscaler-cve-2026-88771-iocs
Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…
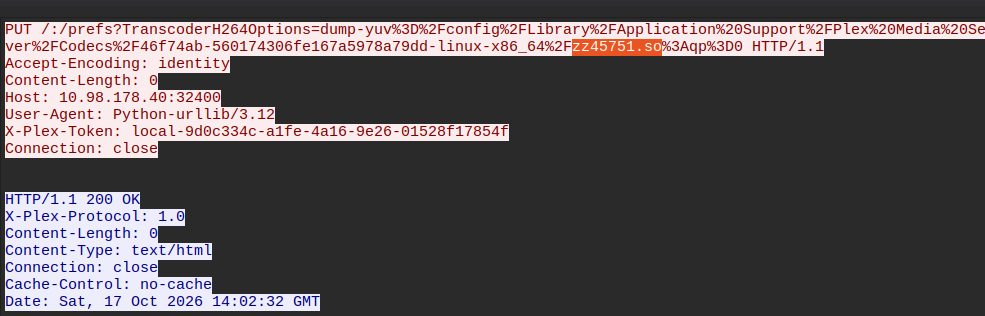 boredhackerblog/plex2shell_pcap
Packet capture artifacts of plex2shell exploitation against Plex, including lab and in-the-wild traffic, for building and validating detection…
 aelshimony-cloud/openwire-cve-2023-46604-investigation
Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…
 google/stenographer
Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those…
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
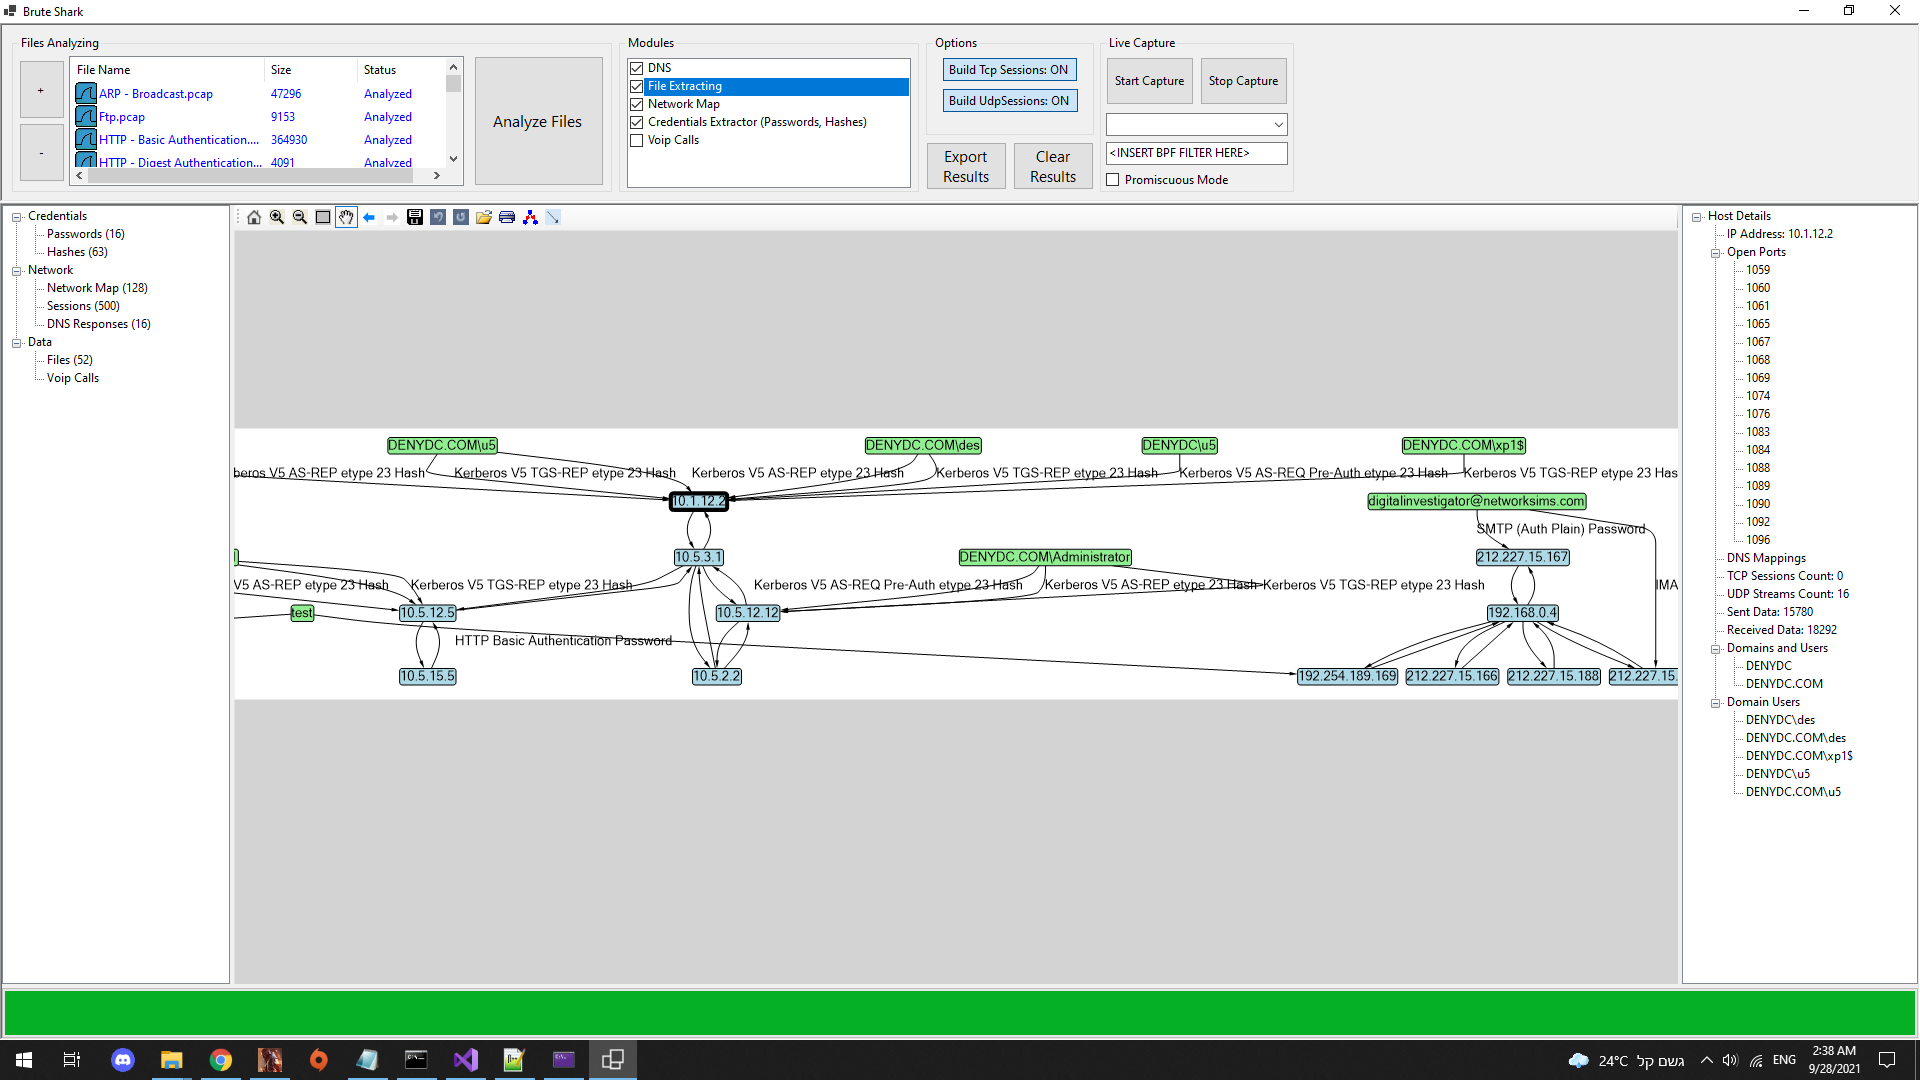
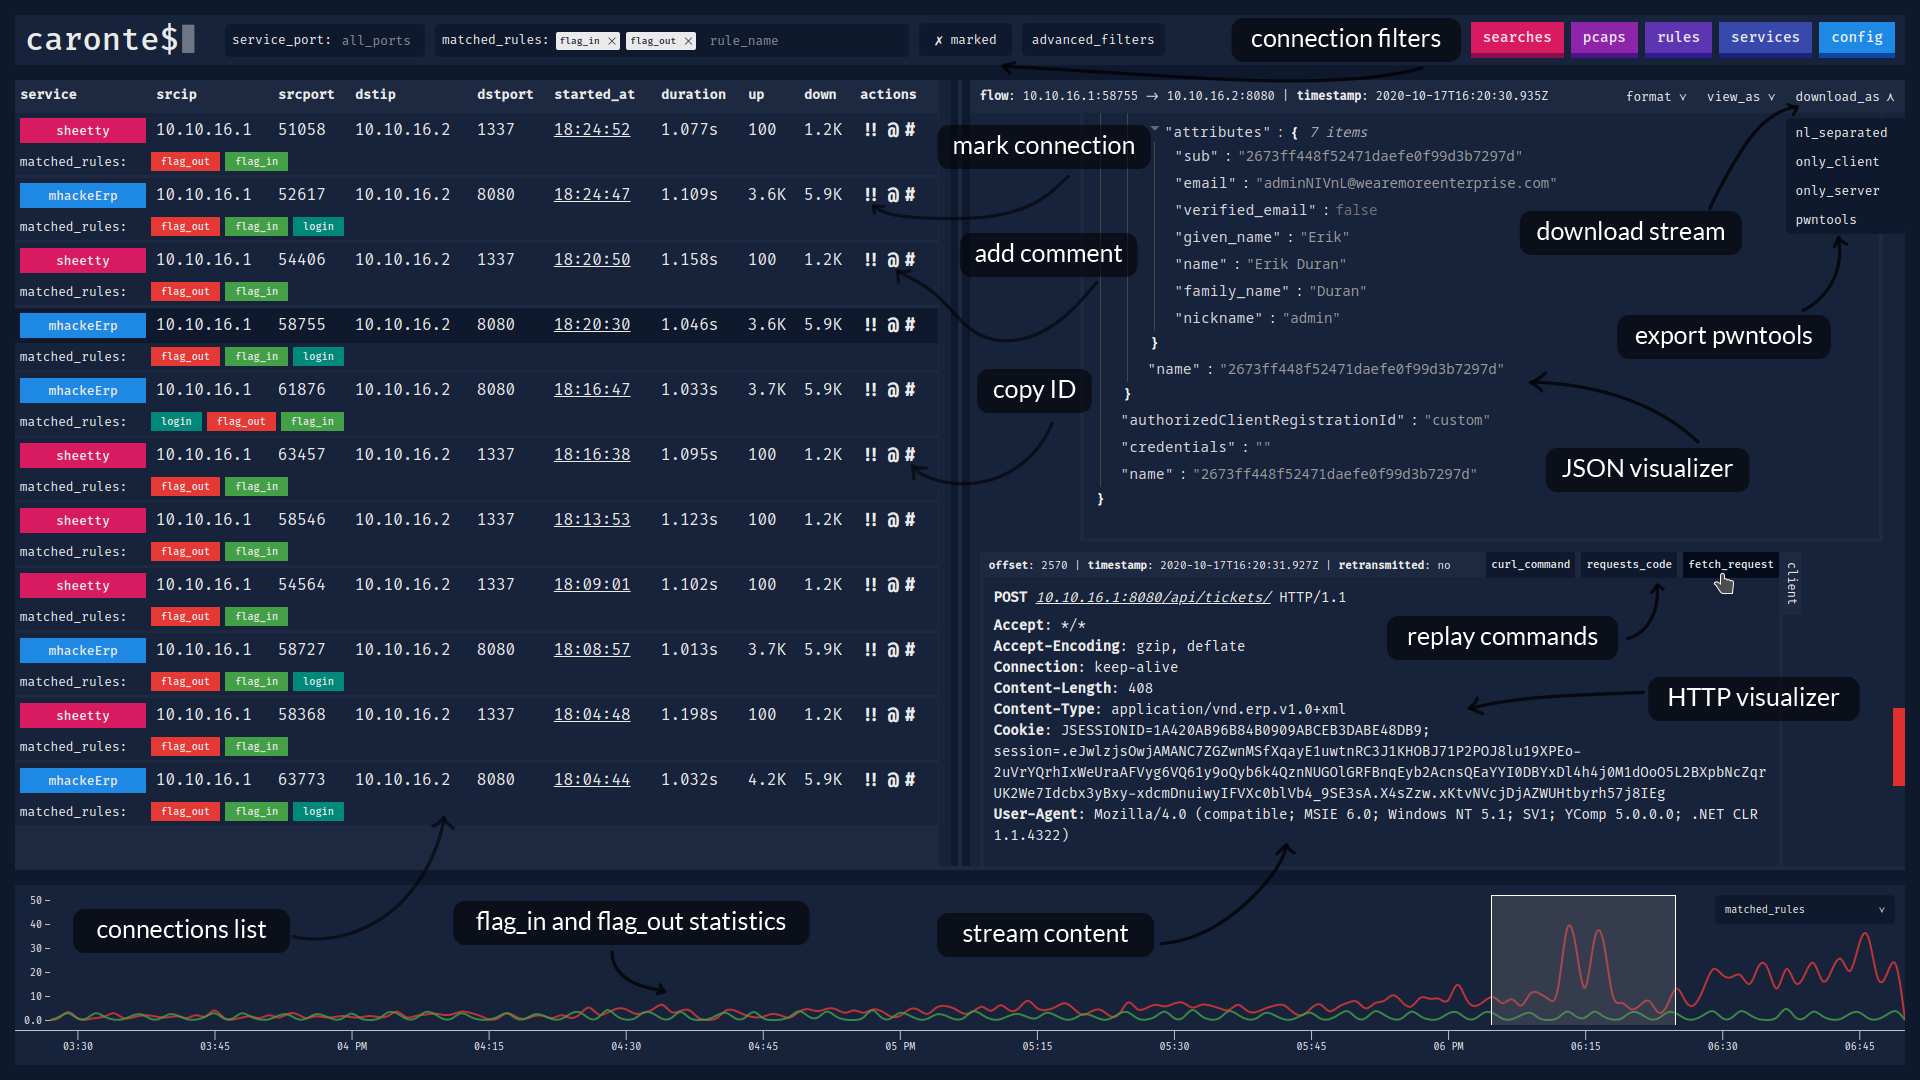 eciavatta/caronte
A tool to analyze the network flow during attack/defence Capture the Flag competitions