Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
127 results
zeek-netsupport-detector preview

zeek-netsupport-detector

GitHubcorelight/zeek-netsupport-detector

A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.
command-and-controldefensive-toolsintrusion-detection+3
2
11 months ago
windows-malware-behavioral-analysis preview

windows-malware-behavioral-analysis

GitHub0x0allenace/windows-malware-behavioral-analysis

Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
digital-forensicsdynamic-analysis-sandboxingeducation+8
1 month ago
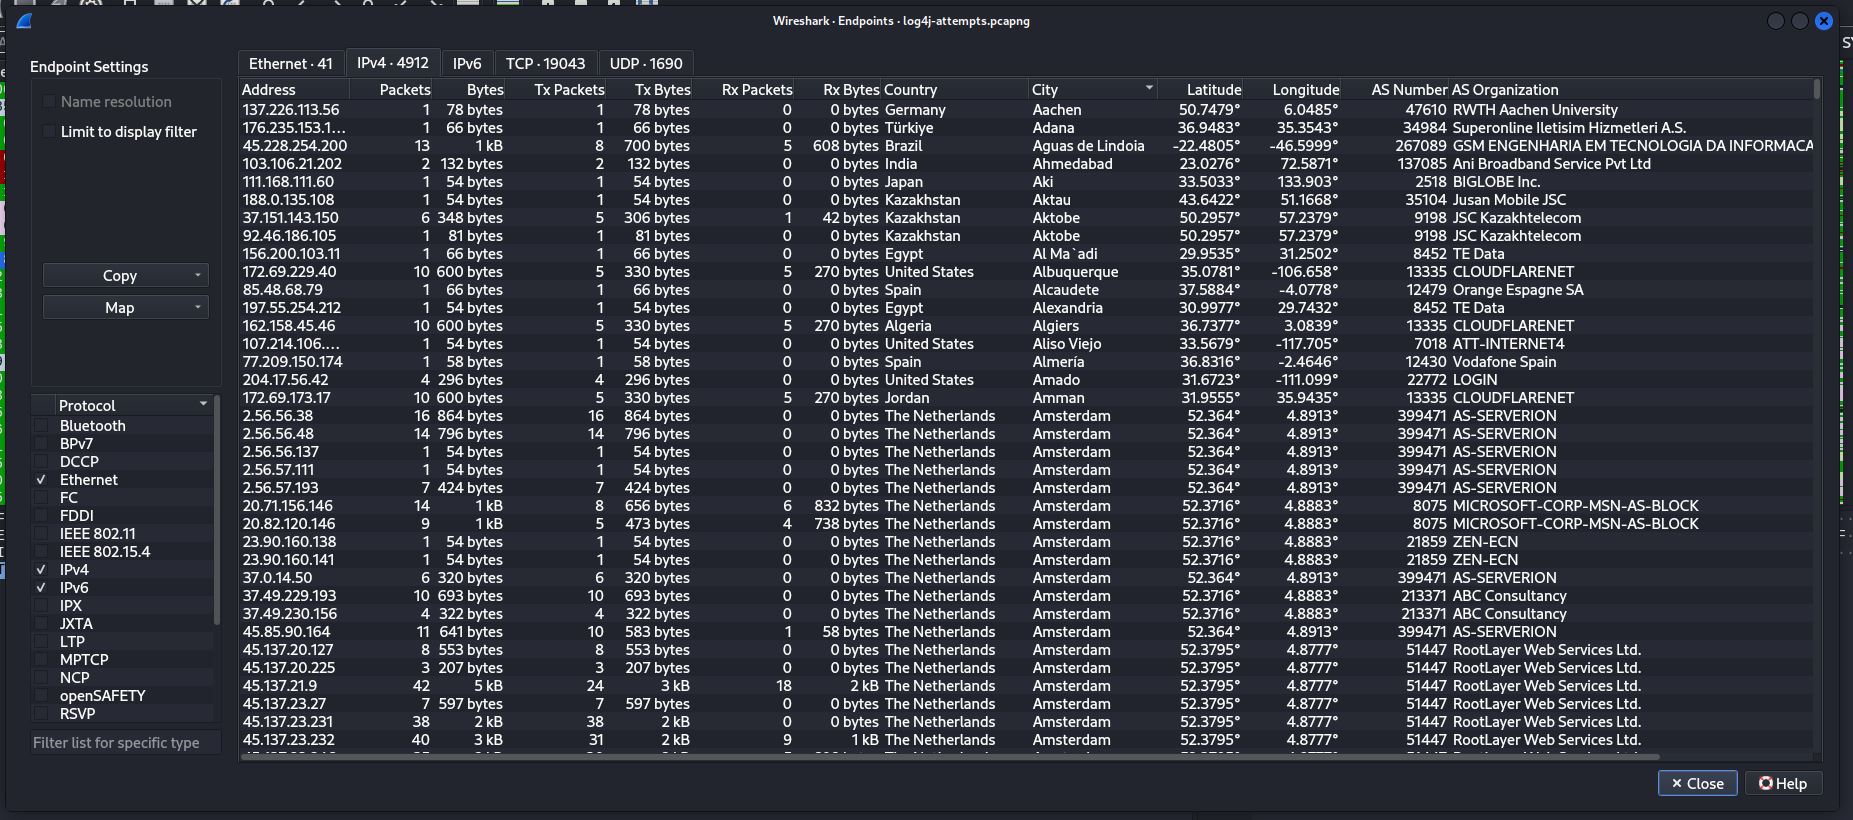
Wireshark preview

Wireshark

GitHubkirkdjohnson/wireshark

Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
command-and-controldigital-forensicseducation+9
32 years ago
OpenWire-CVE-2023-46604-Investigation preview

OpenWire-CVE-2023-46604-Investigation

GitHubaelshimony-cloud/openwire-cve-2023-46604-investigation

Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…

command-and-controldigital-forensicsexploitation+7
2 months ago
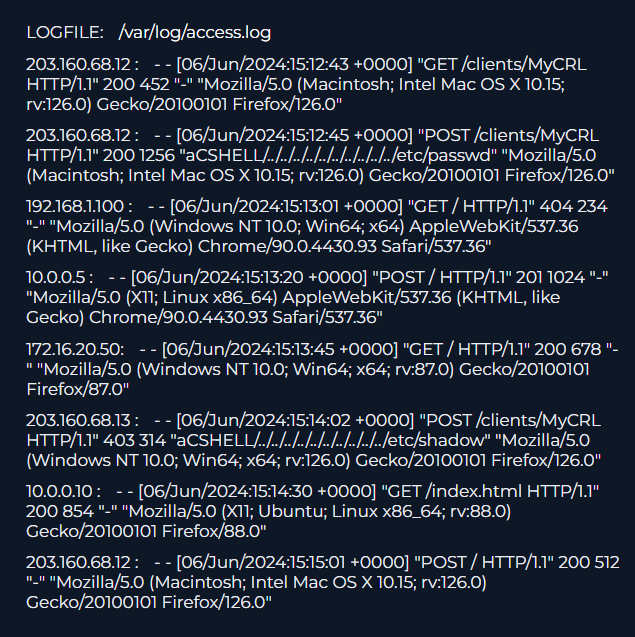
NexaCorp-DFIR-INC-2026-001 preview

NexaCorp-DFIR-INC-2026-001

GitHubjhatchi/nexacorp-dfir-inc-2026-001

DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…
digital-forensicseducationincident-response+6
2 months ago
Incident-Analysis-Response-Check-Point-Security-Gateway-CVE-2024-24919-LFI-Exploitation preview

Incident-Analysis-Response-Check-Point-Security-Gateway-CVE-2024-24919-LFI-Exploitation

GitHubzedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation

Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
digital-forensicseducationincident-response+7
11 month ago
XLS-to-DBatLoader-or-GuLoader-for-AgentTesla-variant preview

XLS-to-DBatLoader-or-GuLoader-for-AgentTesla-variant

GitHubblackoclock/xls-to-dbatloader-or-guloader-for-agenttesla-variant

CVE-2017-0199 XLS --> HTA --> VBS --> STEGANOGRAPHY --> DBATLOADER/GULOADER STYLE MALWARE
command-and-controldigital-forensicsexploitation+4
6 months ago
dfir-malware-investigation preview

dfir-malware-investigation

GitHubsuyash-r-k/dfir-malware-investigation

Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
digital-forensicseducationincident-response+9
7 months ago
aiengine preview

aiengine

Bitbucketcamp0/aiengine

AIEngine is a next generation interactive/programmable Python/Ruby/Java/Lua and Go NIDS (Network intrusion detection system).

anomaly-detectiondefensive-toolsdns-analysis+5
3 years ago
Network-Filesystem-Forensics preview

Network-Filesystem-Forensics

GitHubgilberto47831/network-filesystem-forensics

Reports on post-exploitation on honeypot exploiting vulnerable wu-ftpd (CVE-2001-0550)
digital-forensicsforensicsnetwork-forensics+2
4 years ago
CAPEsolo preview

CAPEsolo

GitHubcapesandbox/capesolo

Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
defensive-toolsdynamic-analysis-sandboxingforensics+7
2822h 34m ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
debuggersdigital-forensicsdisk-forensics+7
252 months ago
CAPEv2 preview

CAPEv2

GitHubkevoreilly/capev2

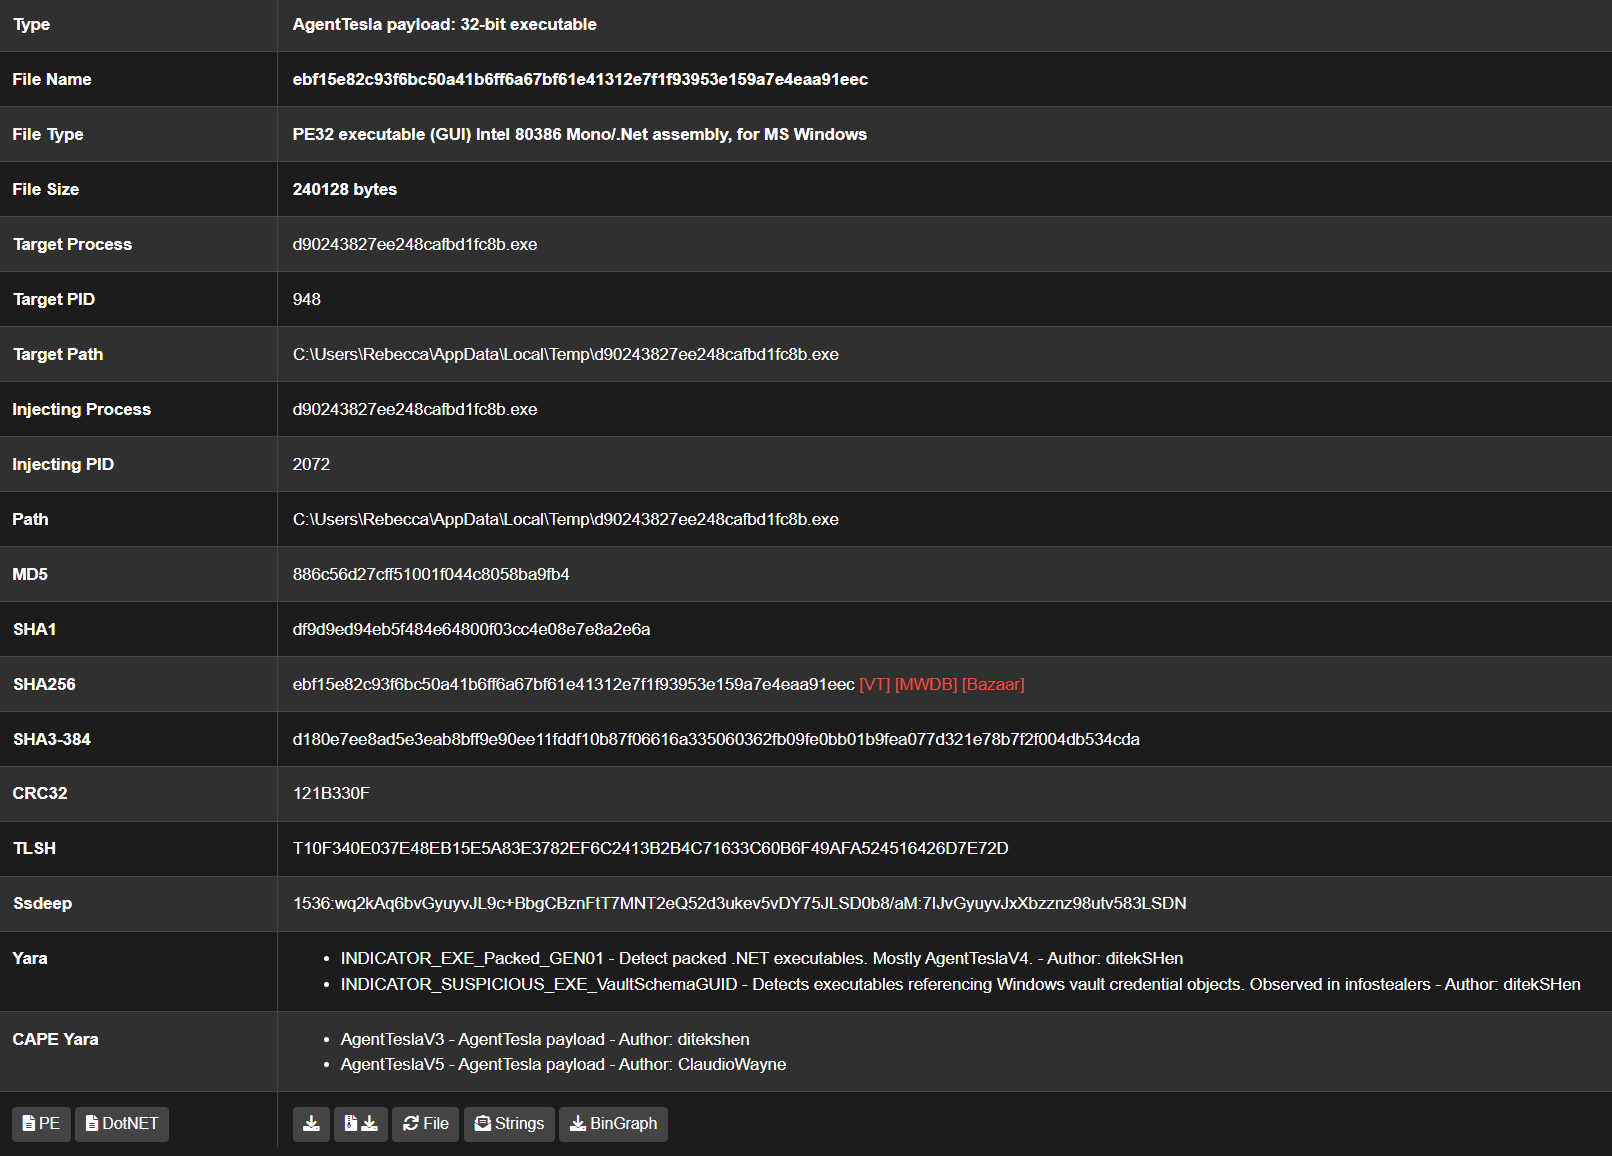
Malware Configuration And Payload Extraction
debuggersdynamic-analysis-sandboxingeducation+6
3.5k1 day ago
digital-forensics-lab preview

digital-forensics-lab

GitHubfrankwxu/digital-forensics-lab

Free hands-on digital forensics labs for students and faculty
ai-securityctfdigital-forensics+9
3.0k12h 45m ago
pyrdp preview

pyrdp

GitHubgosecure/pyrdp

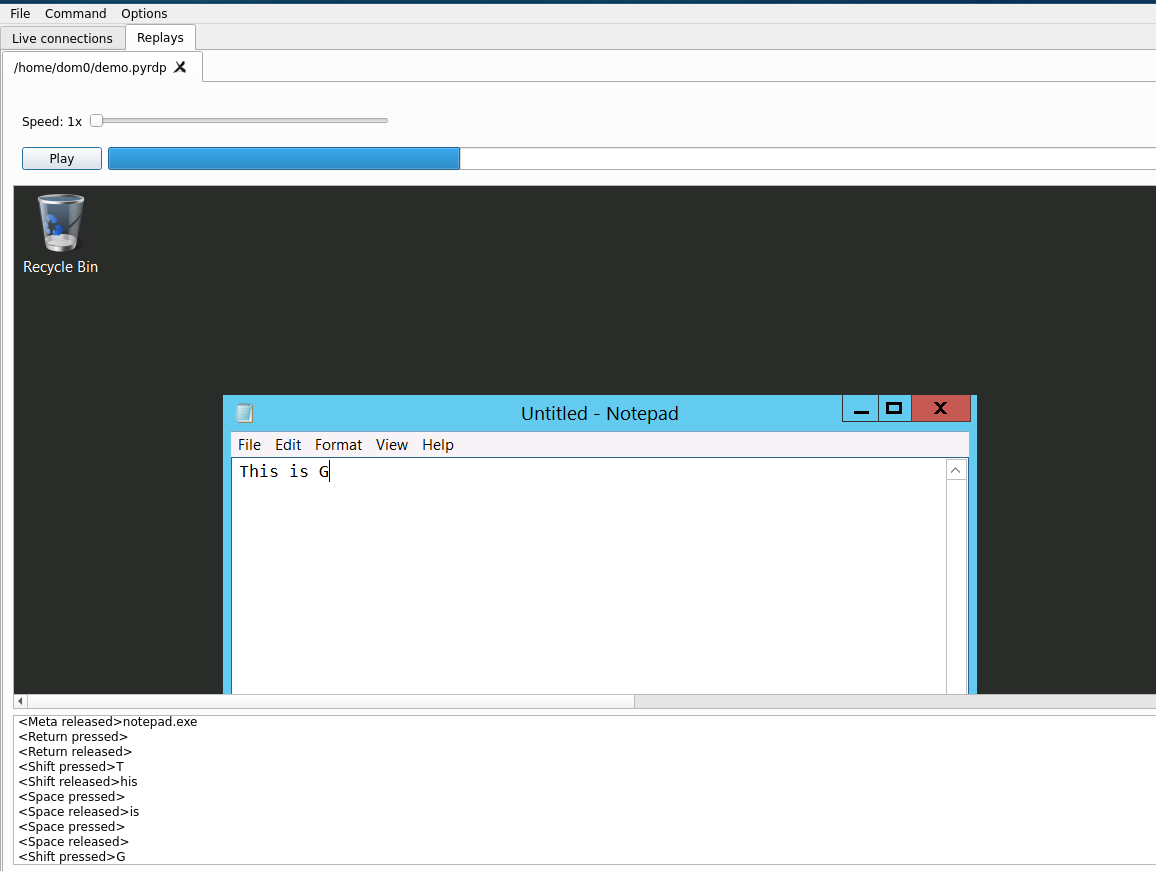
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
ctfeducationexploitation+9
1.8k4 months ago
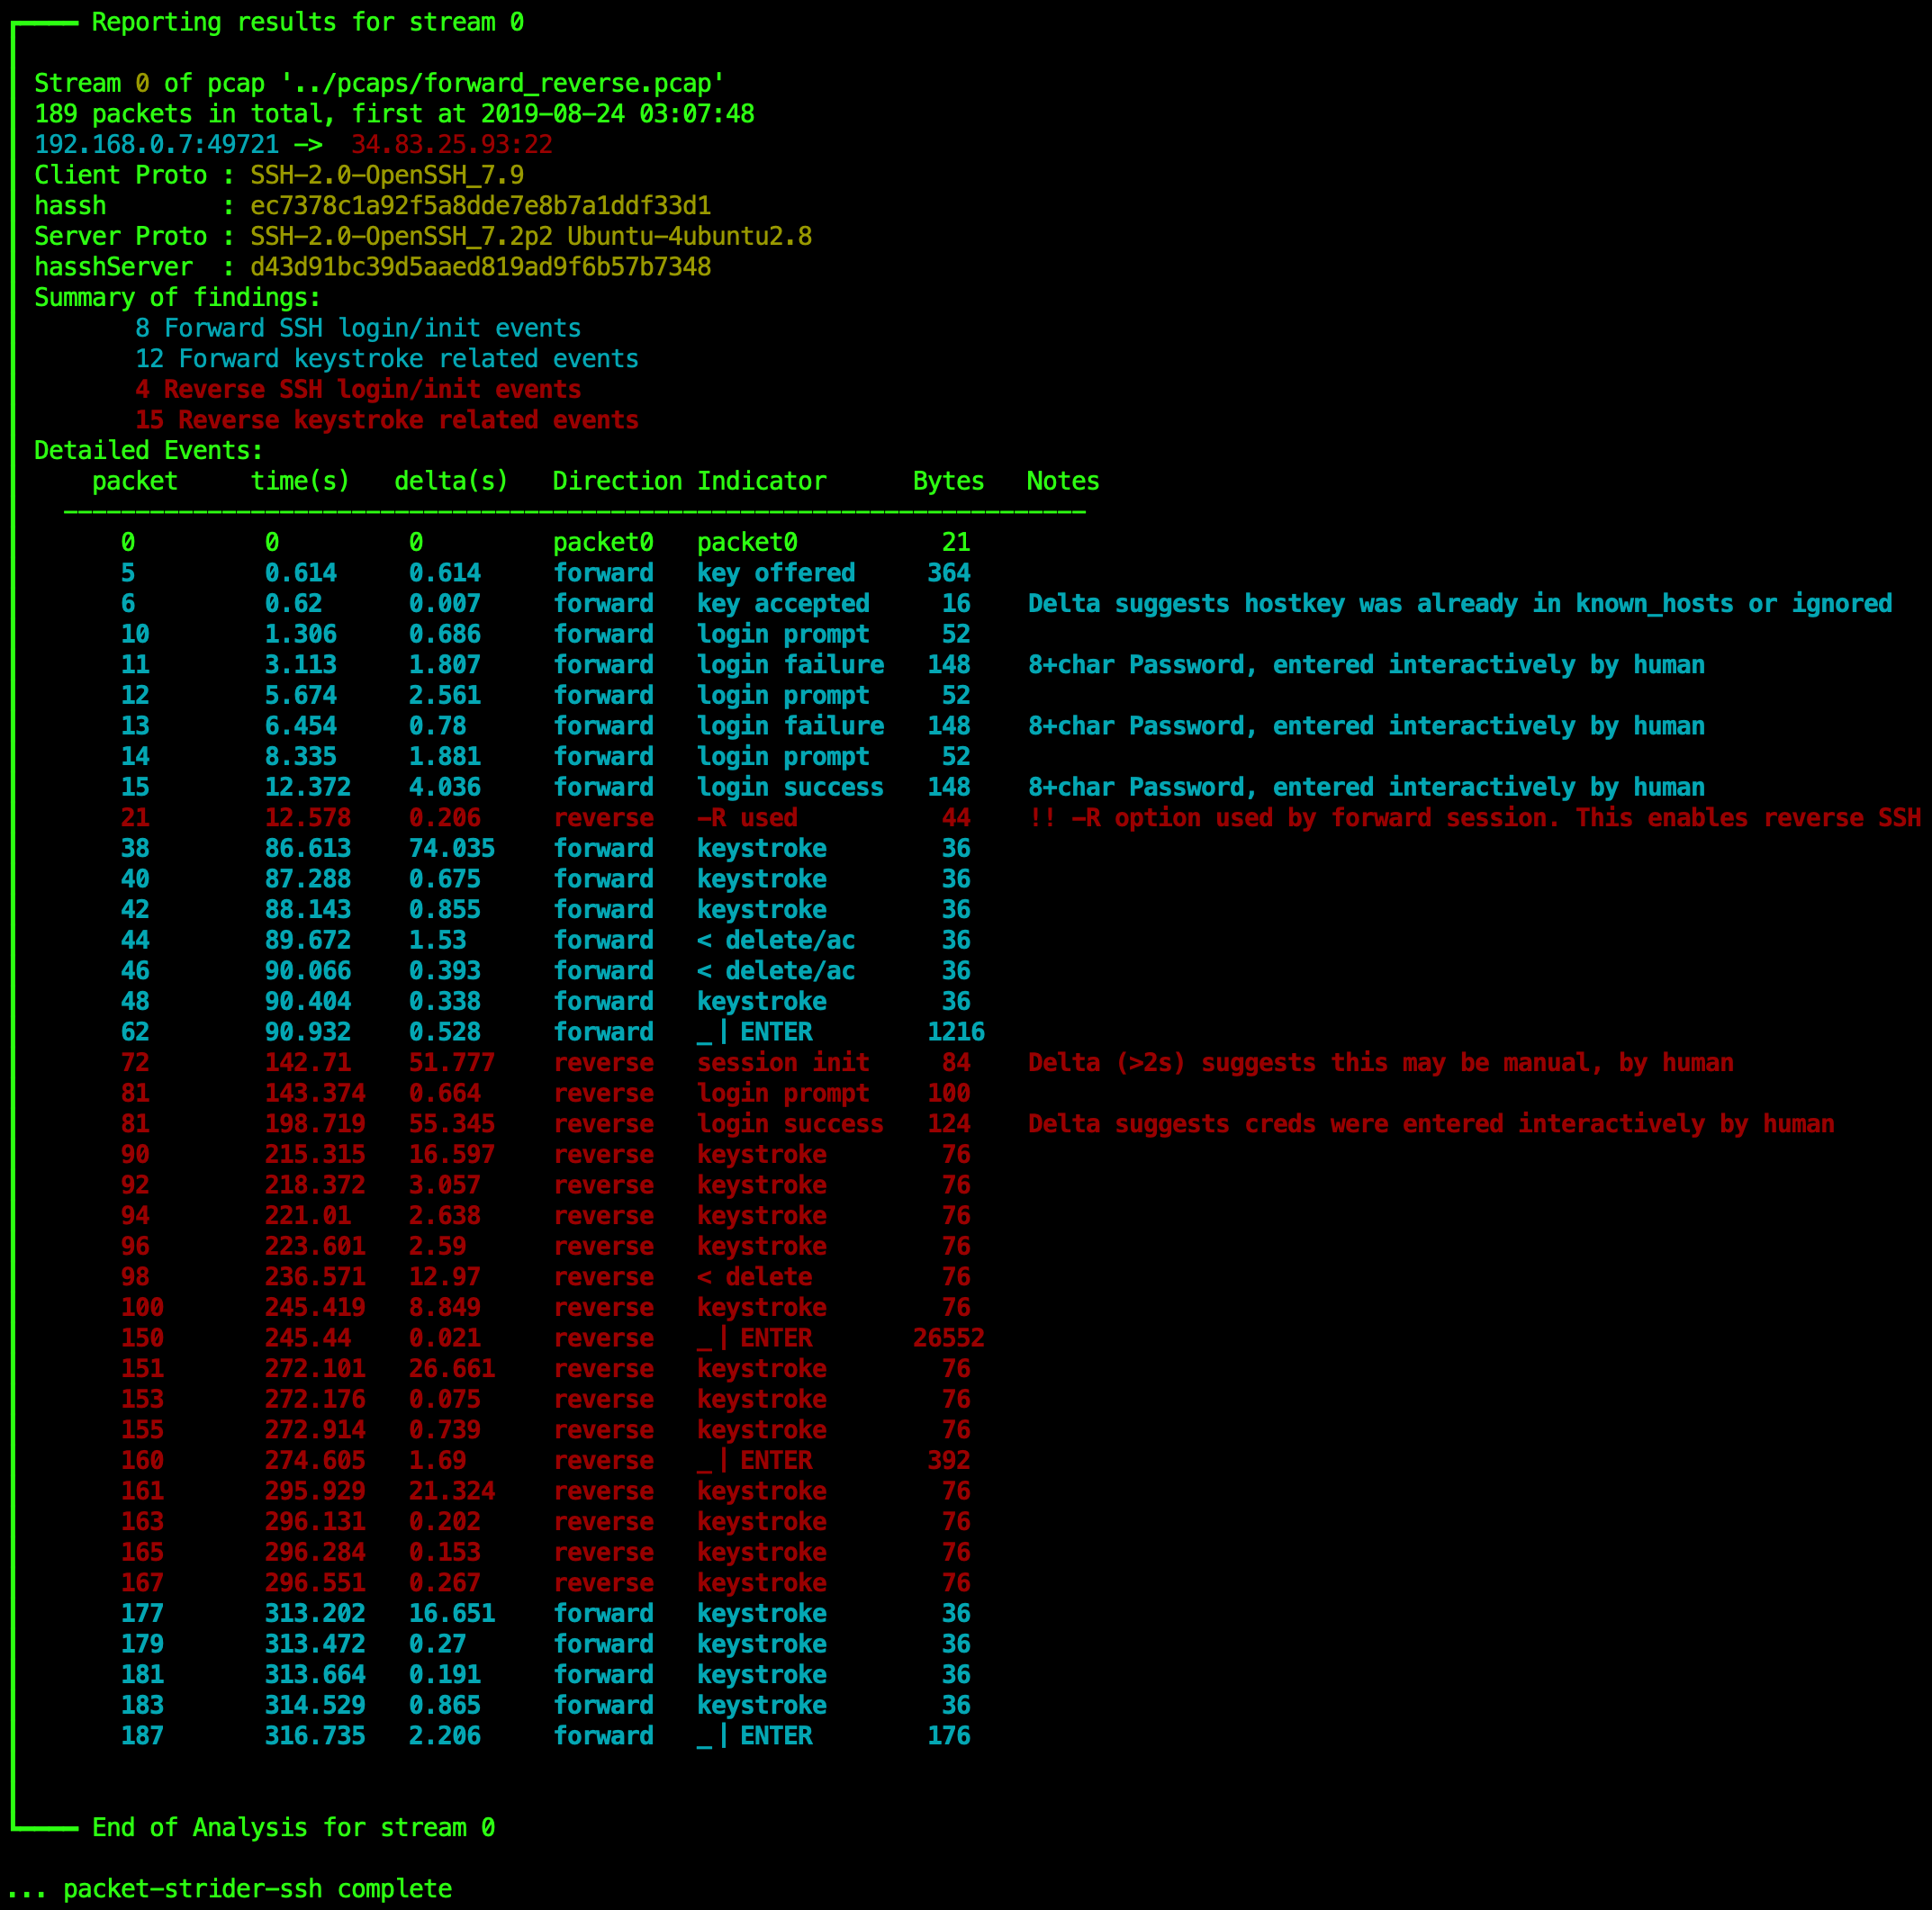
packetStrider preview

packetStrider

GitHubbenjeems/packetstrider

A network packet forensics tool for SSH

anomaly-detectionforensicsintrusion-detection+5
2556 years ago
DC30-Badge-Challenge-Writeup preview

DC30-Badge-Challenge-Writeup

GitHubkybr-git/dc30-badge-challenge-writeup

Writeup for the DEF CON 30 badge challenge
ctfcurated-resourcesdigital-forensics+3
724 years ago
security-writeups preview

security-writeups

GitHubalzeaty1/security-writeups

CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.

ctfeducationlabs-practice+5
1 month ago
Previous1…678Next