
dns_watchdog_windows2
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
anomaly-detectiondefensive-toolsdns-analysis+5
microlaser/dns_watchdog_windows2PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 camp0/aiengine
AIEngine is a next generation interactive/programmable Python/Ruby/Java/Lua and Go NIDS (Network intrusion detection system).
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
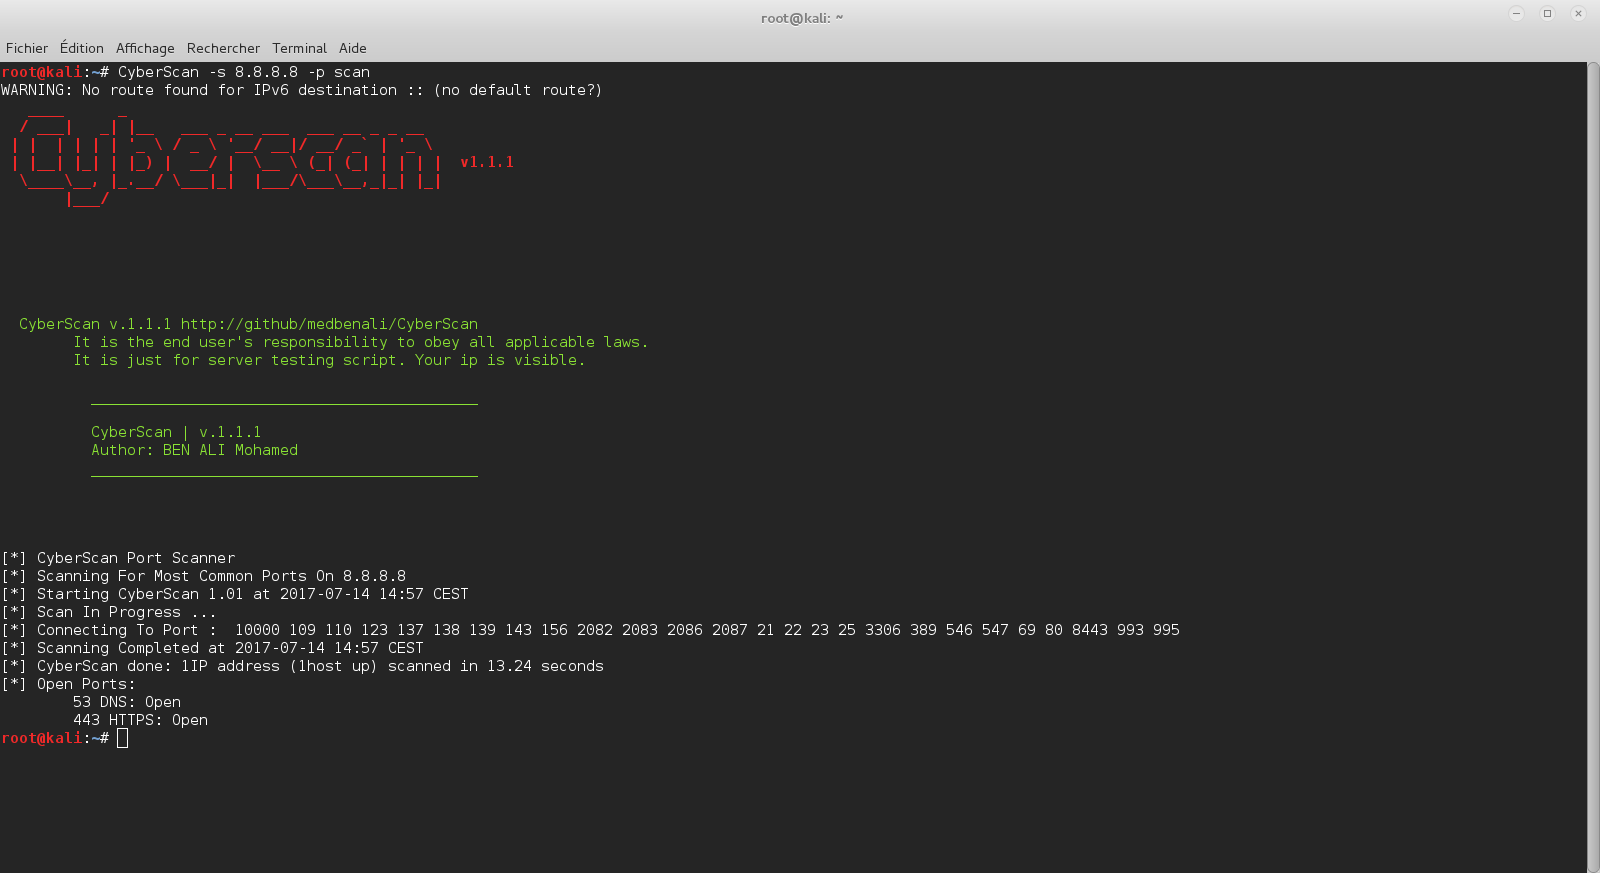 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
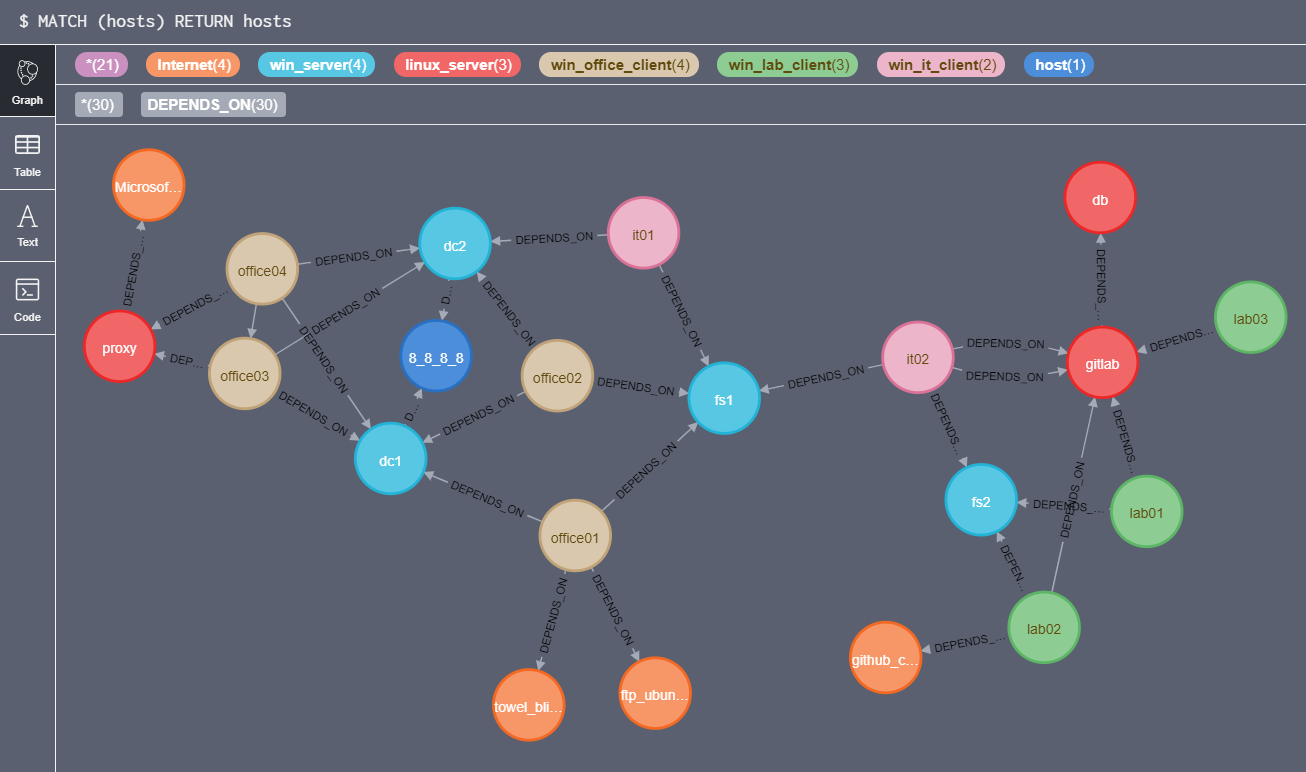 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines
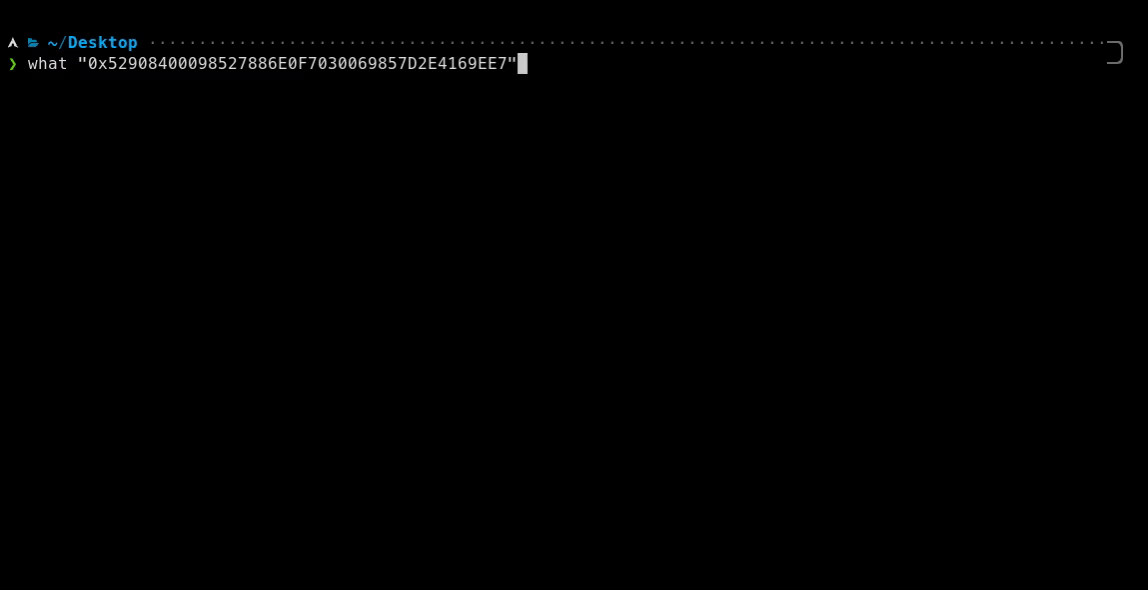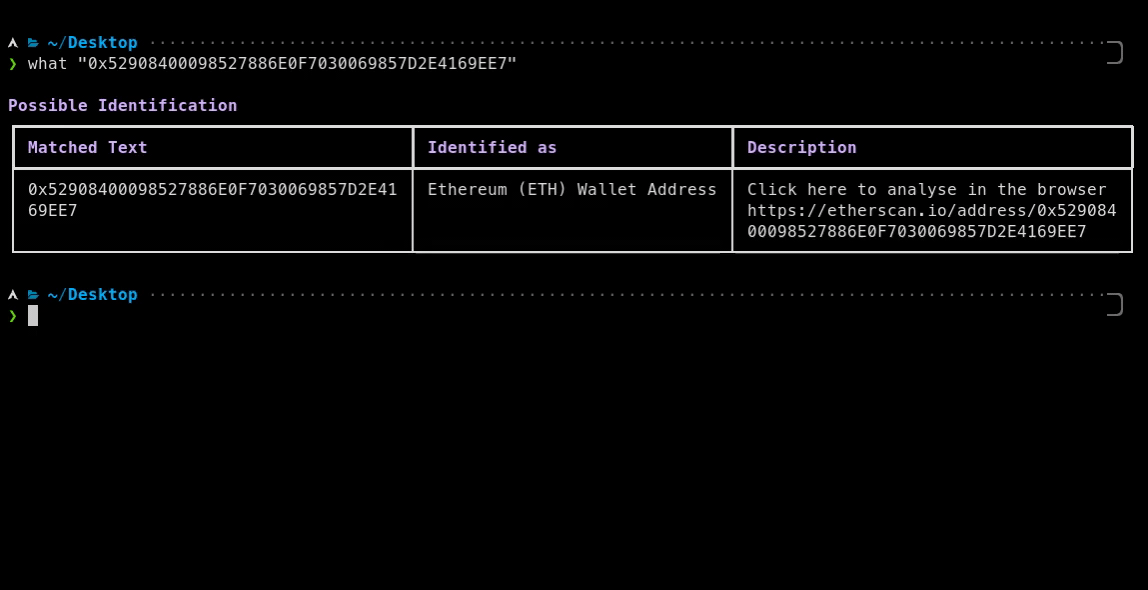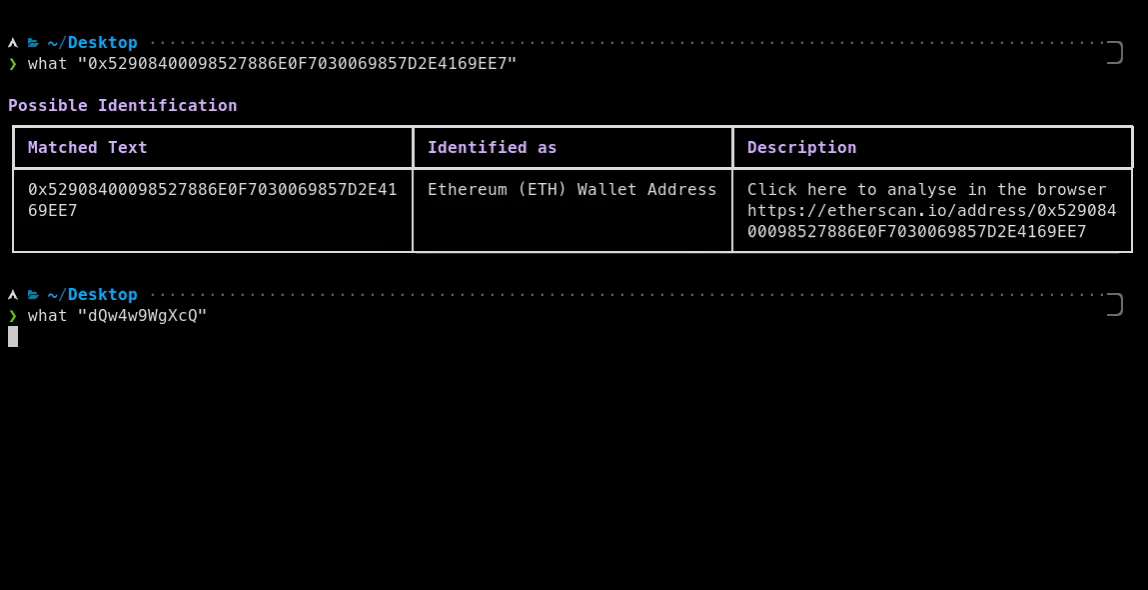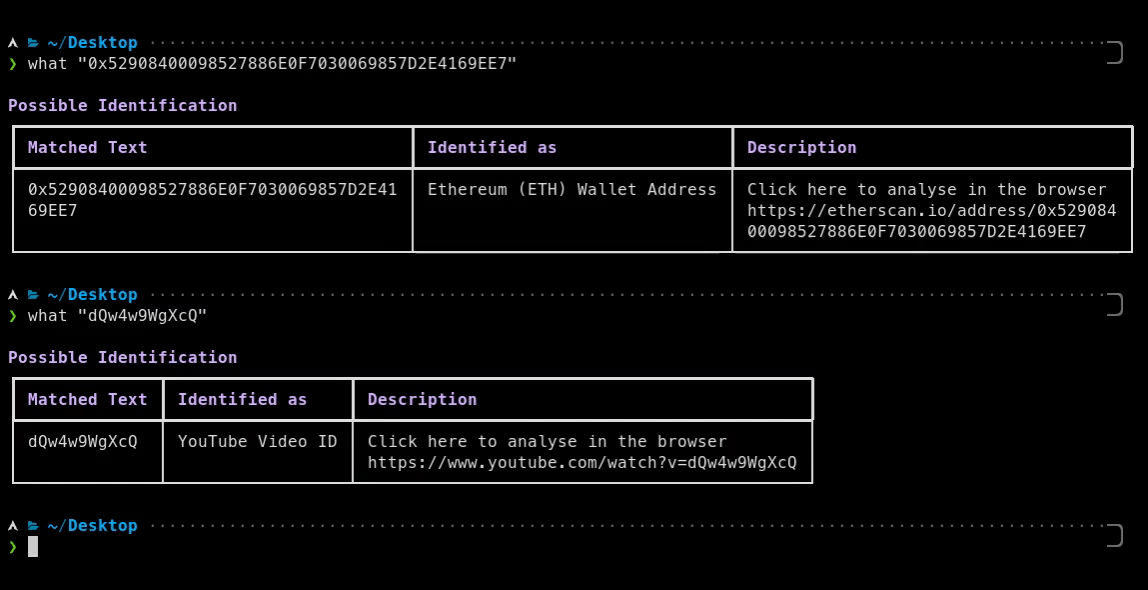 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
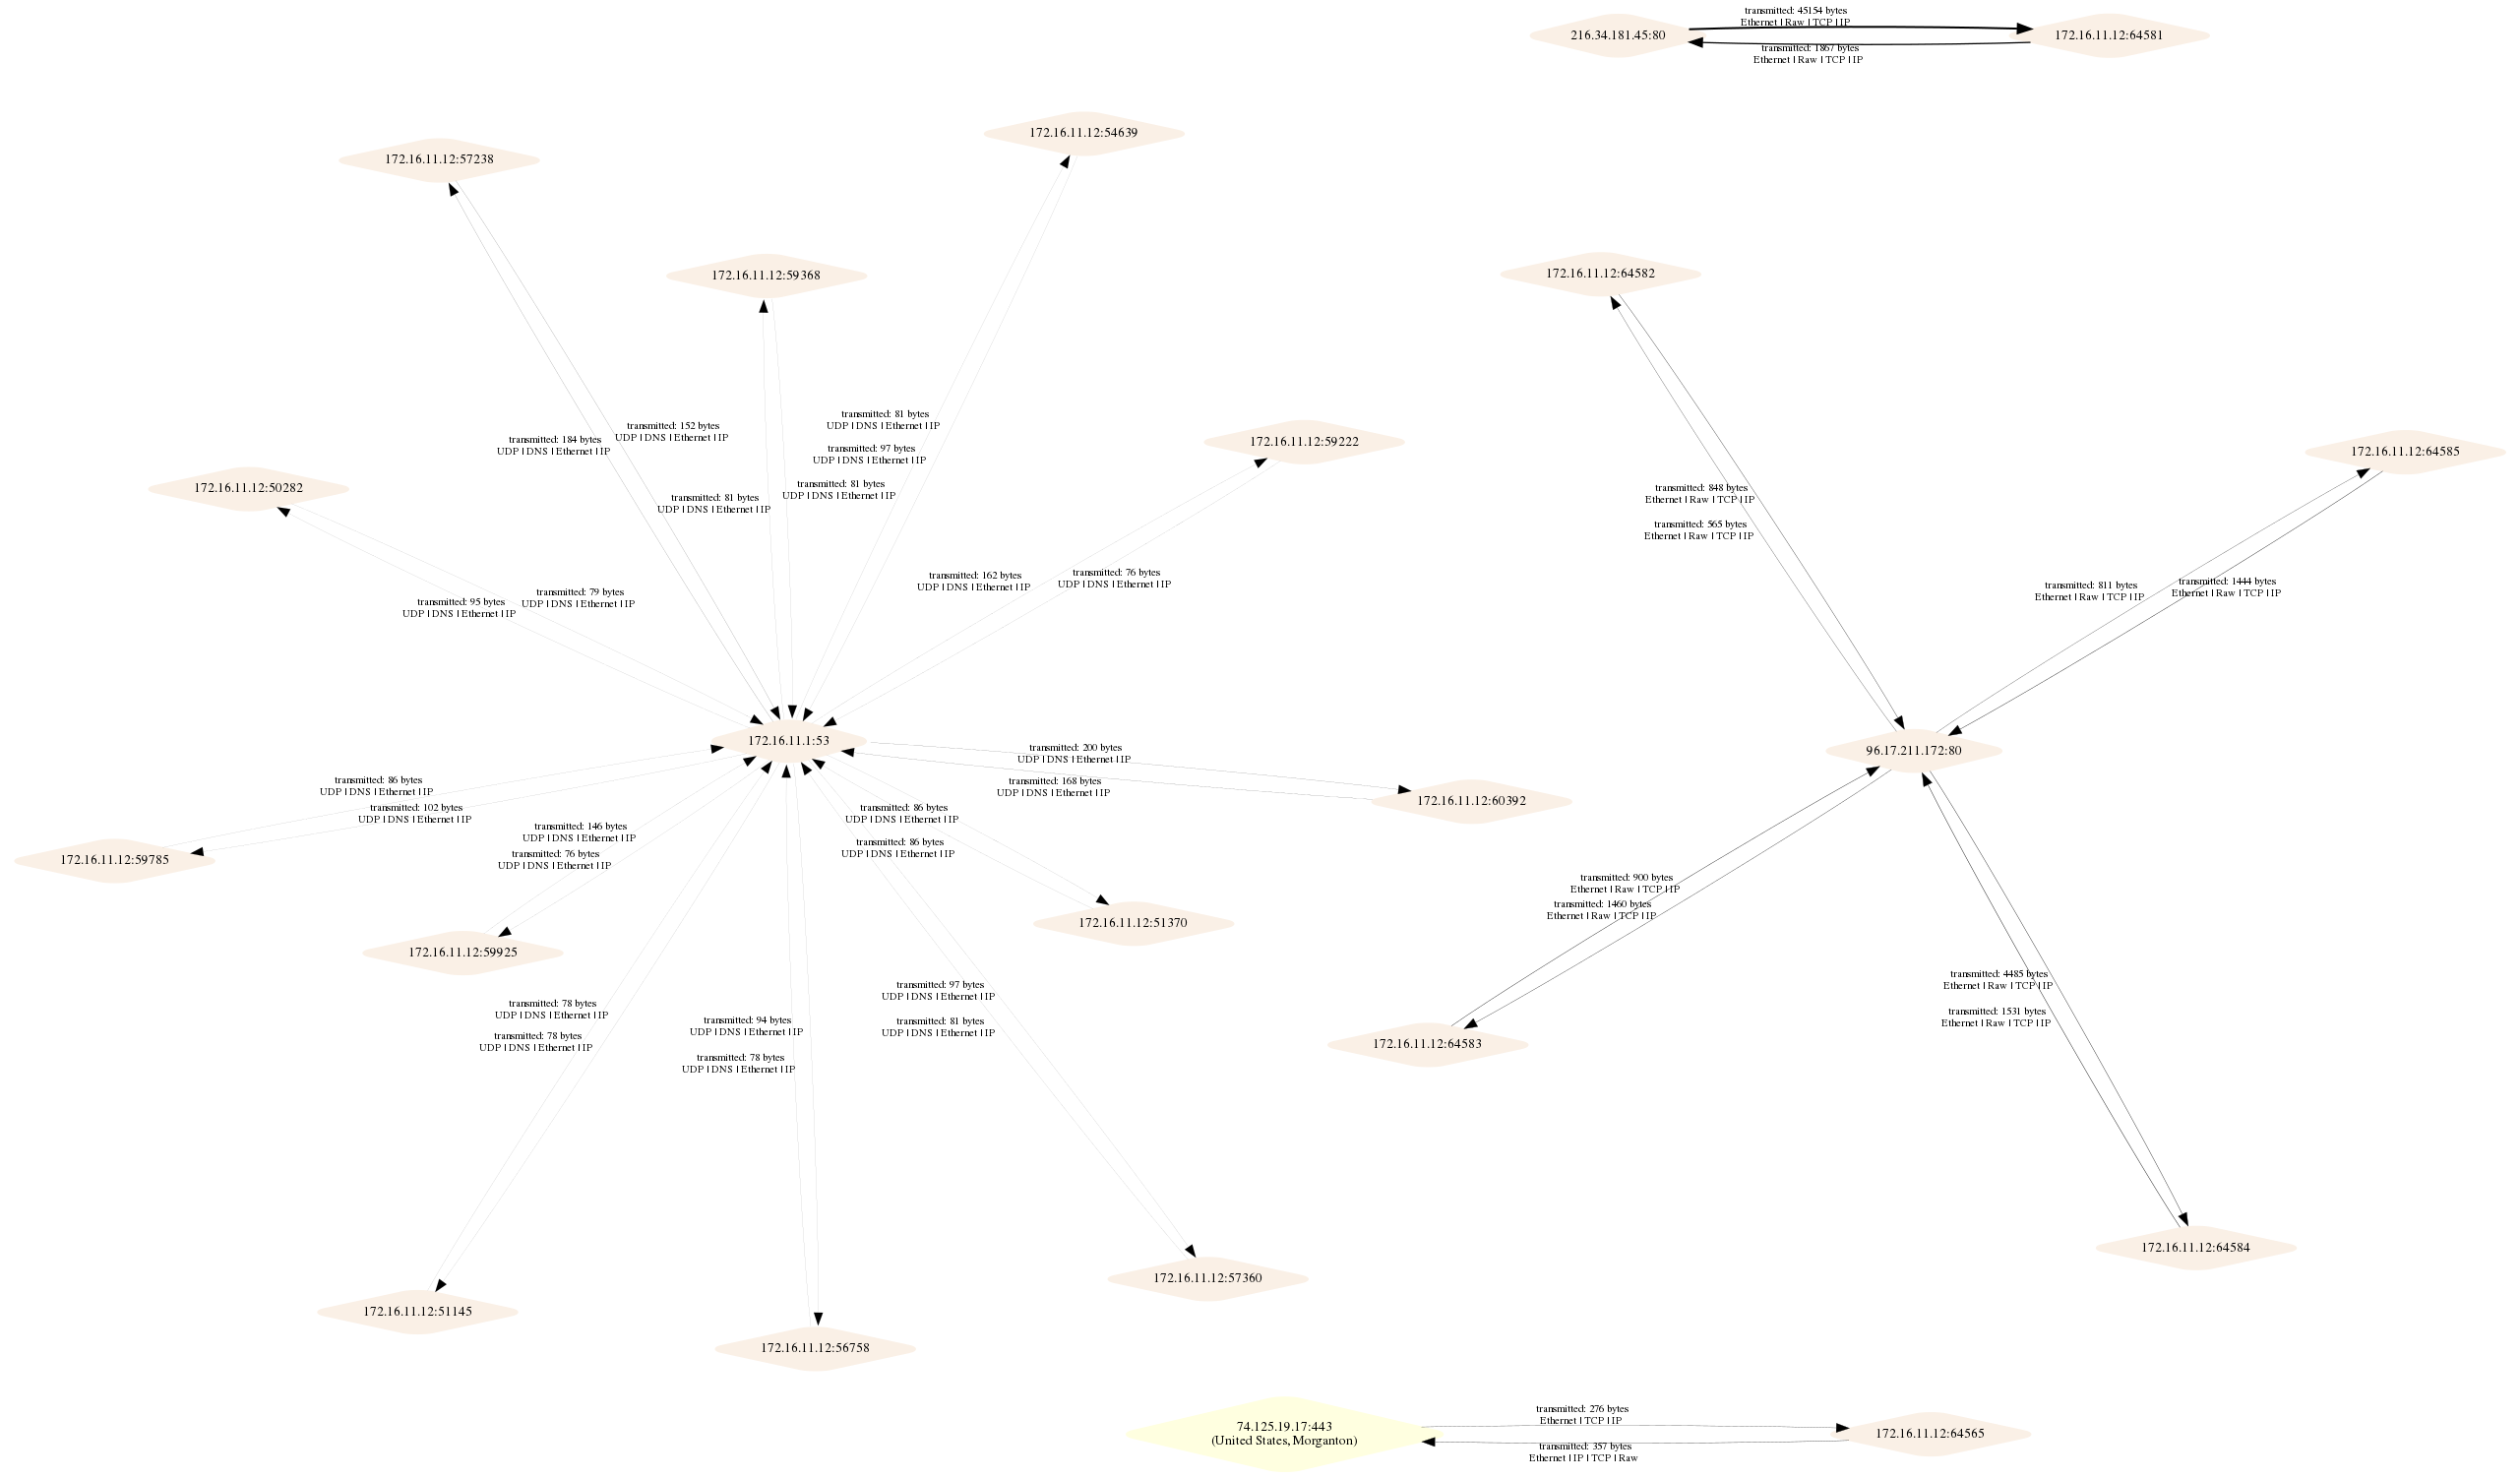 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
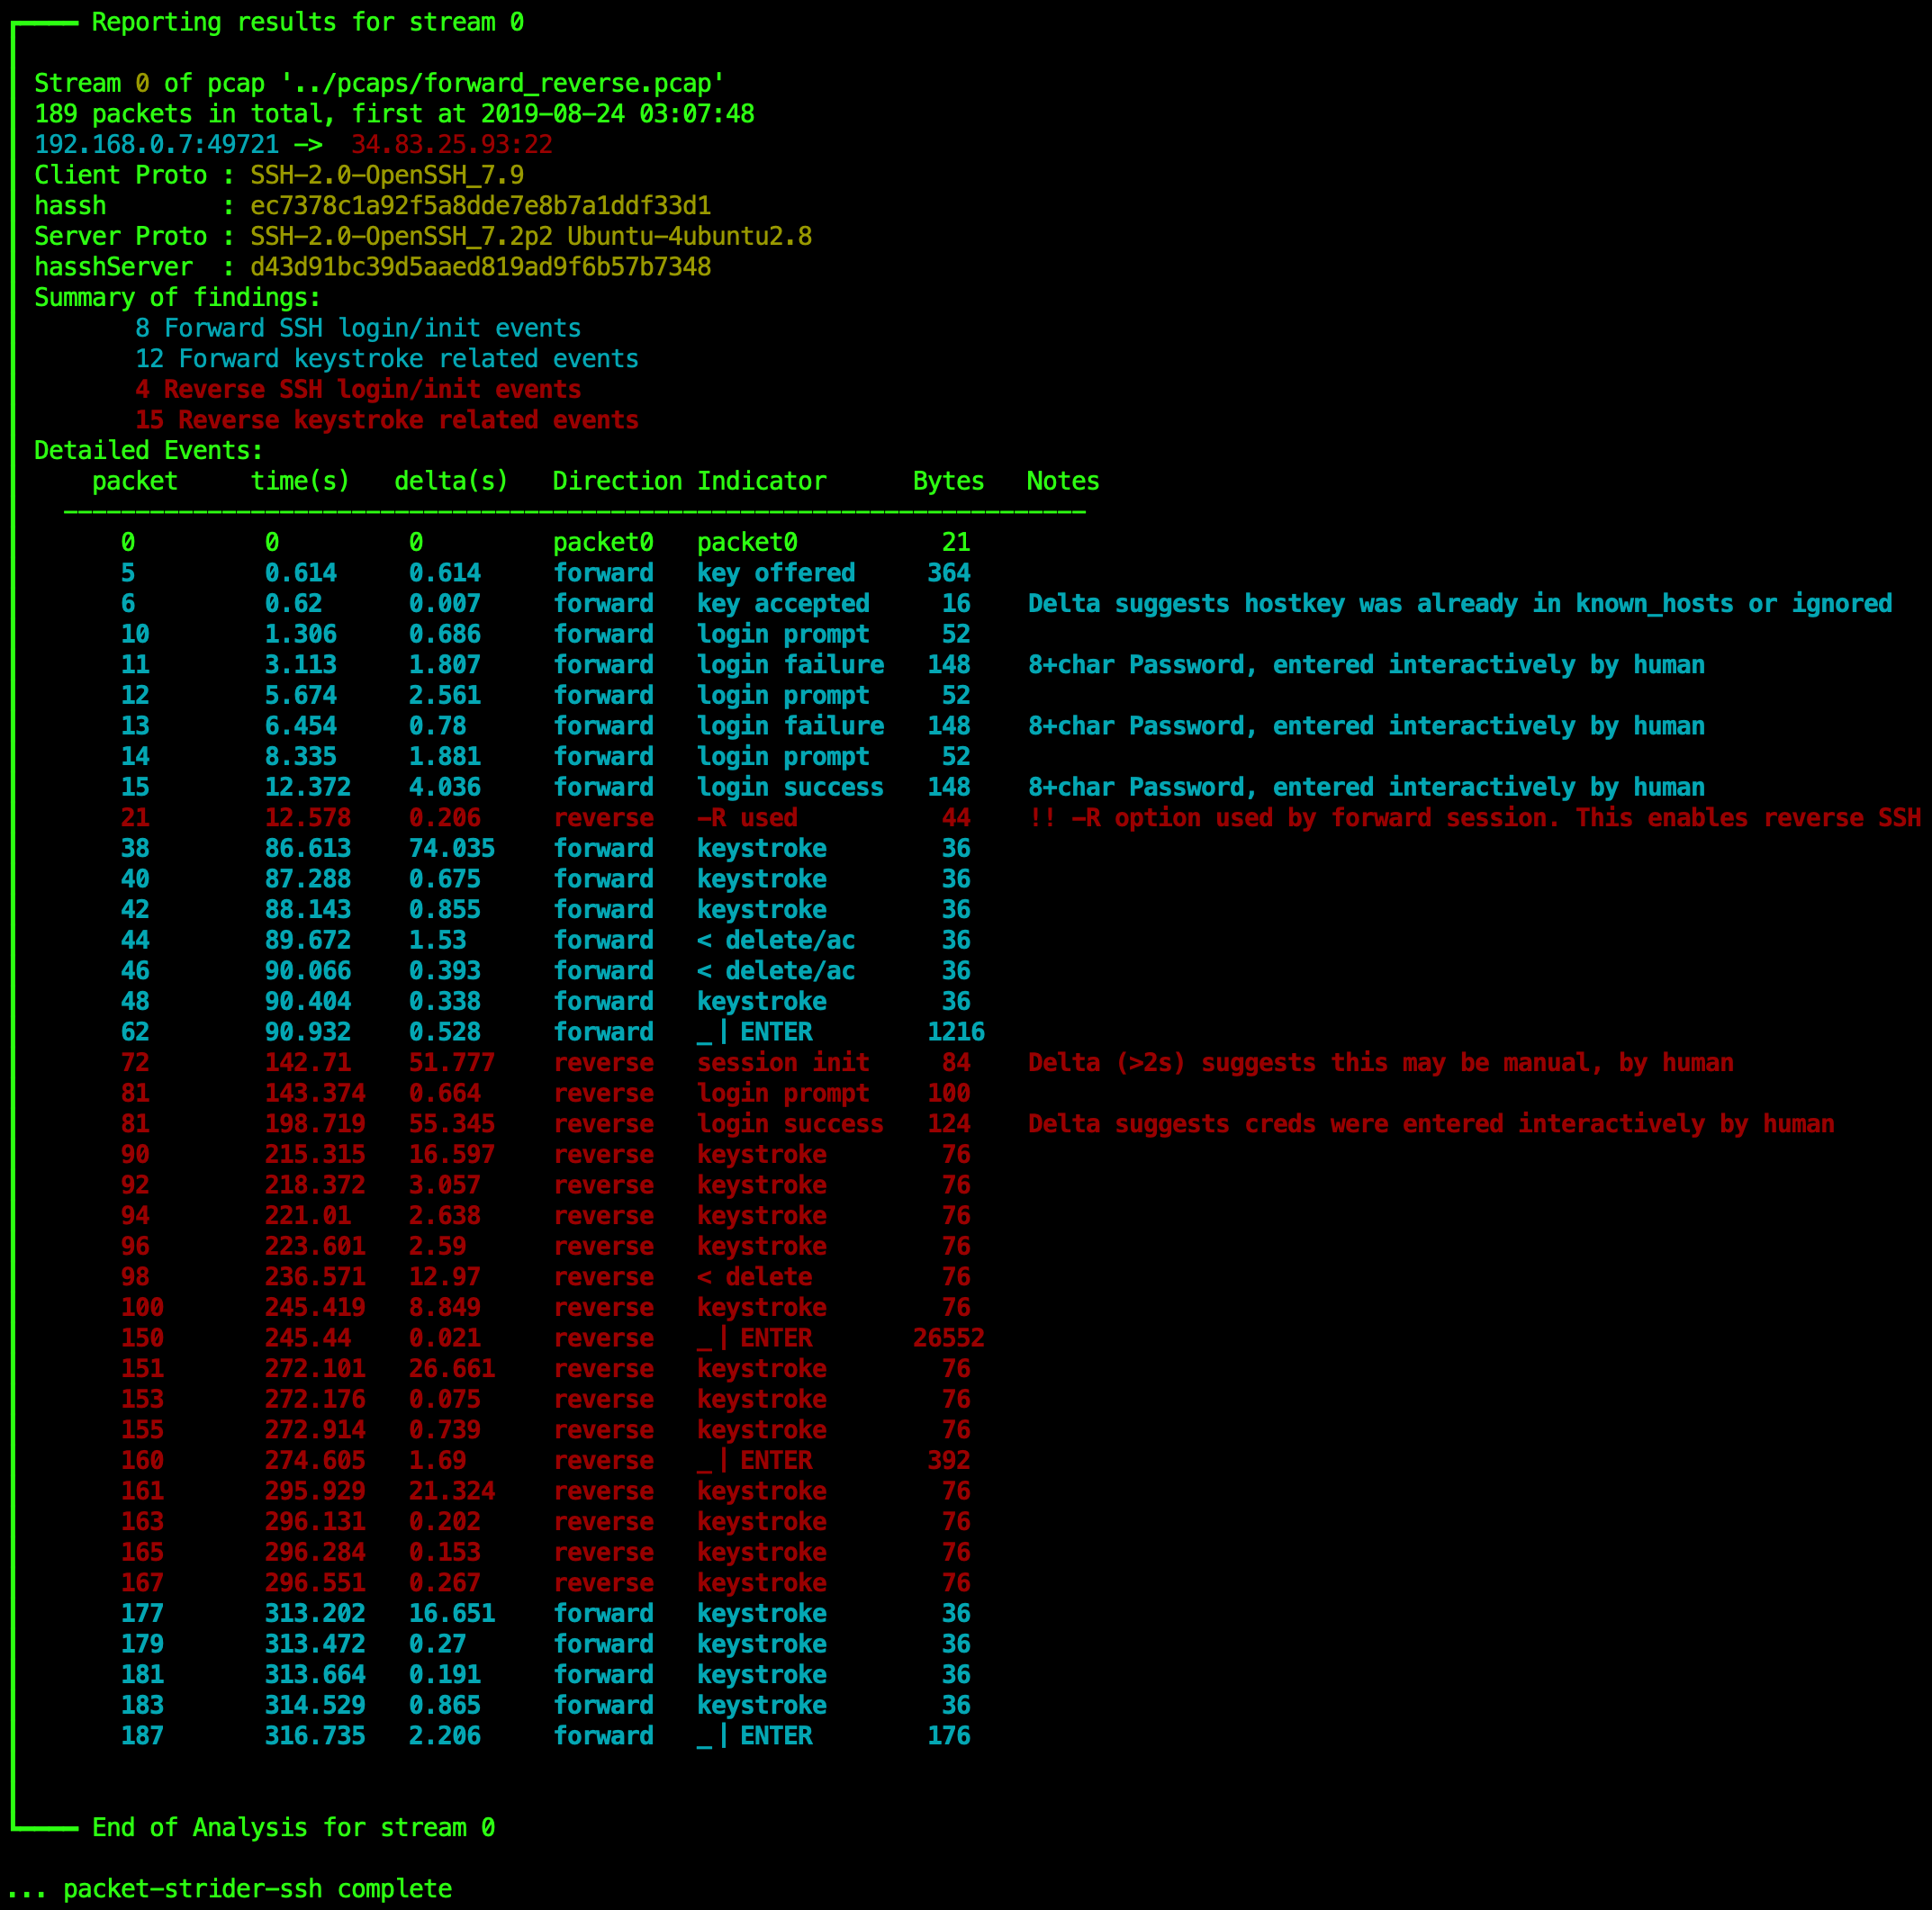 benjeems/packetstrider
A network packet forensics tool for SSH
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
 kybr-git/dc30-badge-challenge-writeup
Writeup for the DEF CON 30 badge challenge
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
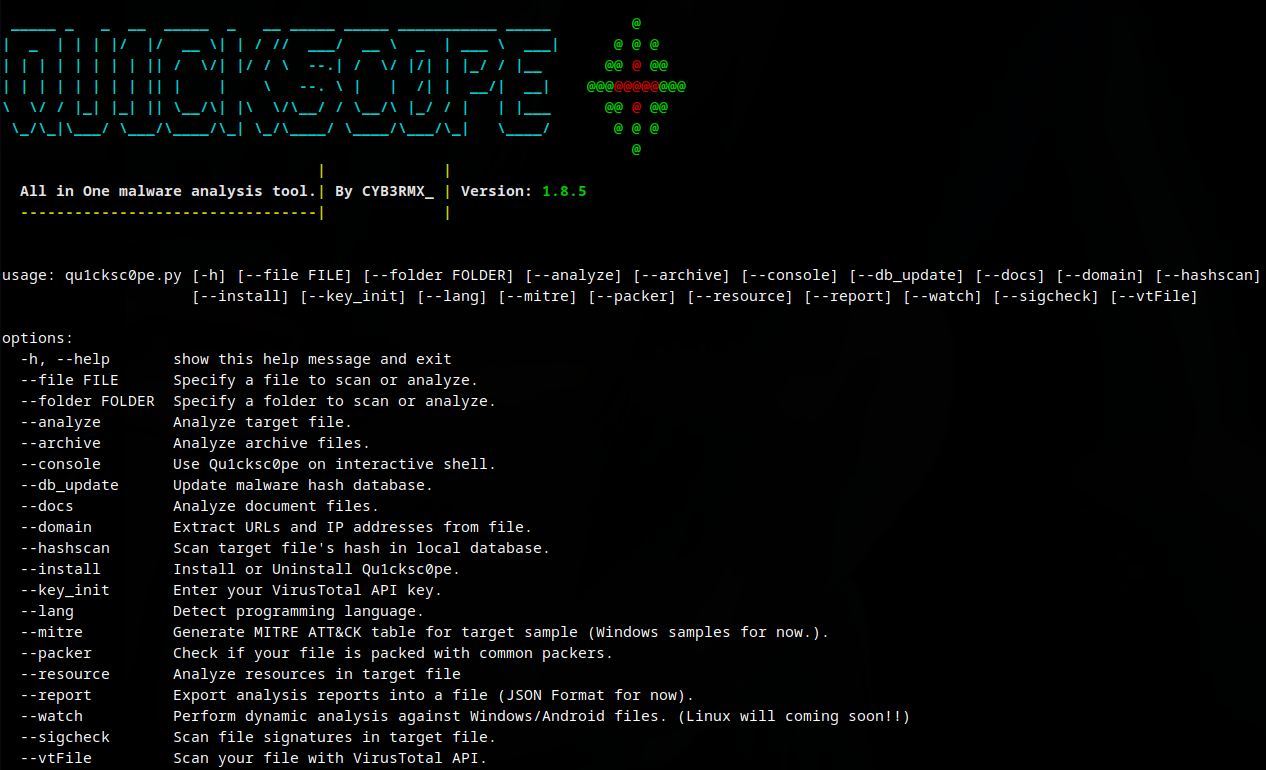 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 detuxsandbox/detux
The Multiplatform Linux Sandbox
 corelight/zeek-spicy-stun
A Zeek STUN protocol analyzer based on Spicy.