
Android-Projector-C2-Malware
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
android-securitycommand-and-controldigital-forensics+9
23
kavan00/android-projector-c2-malwareBreakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
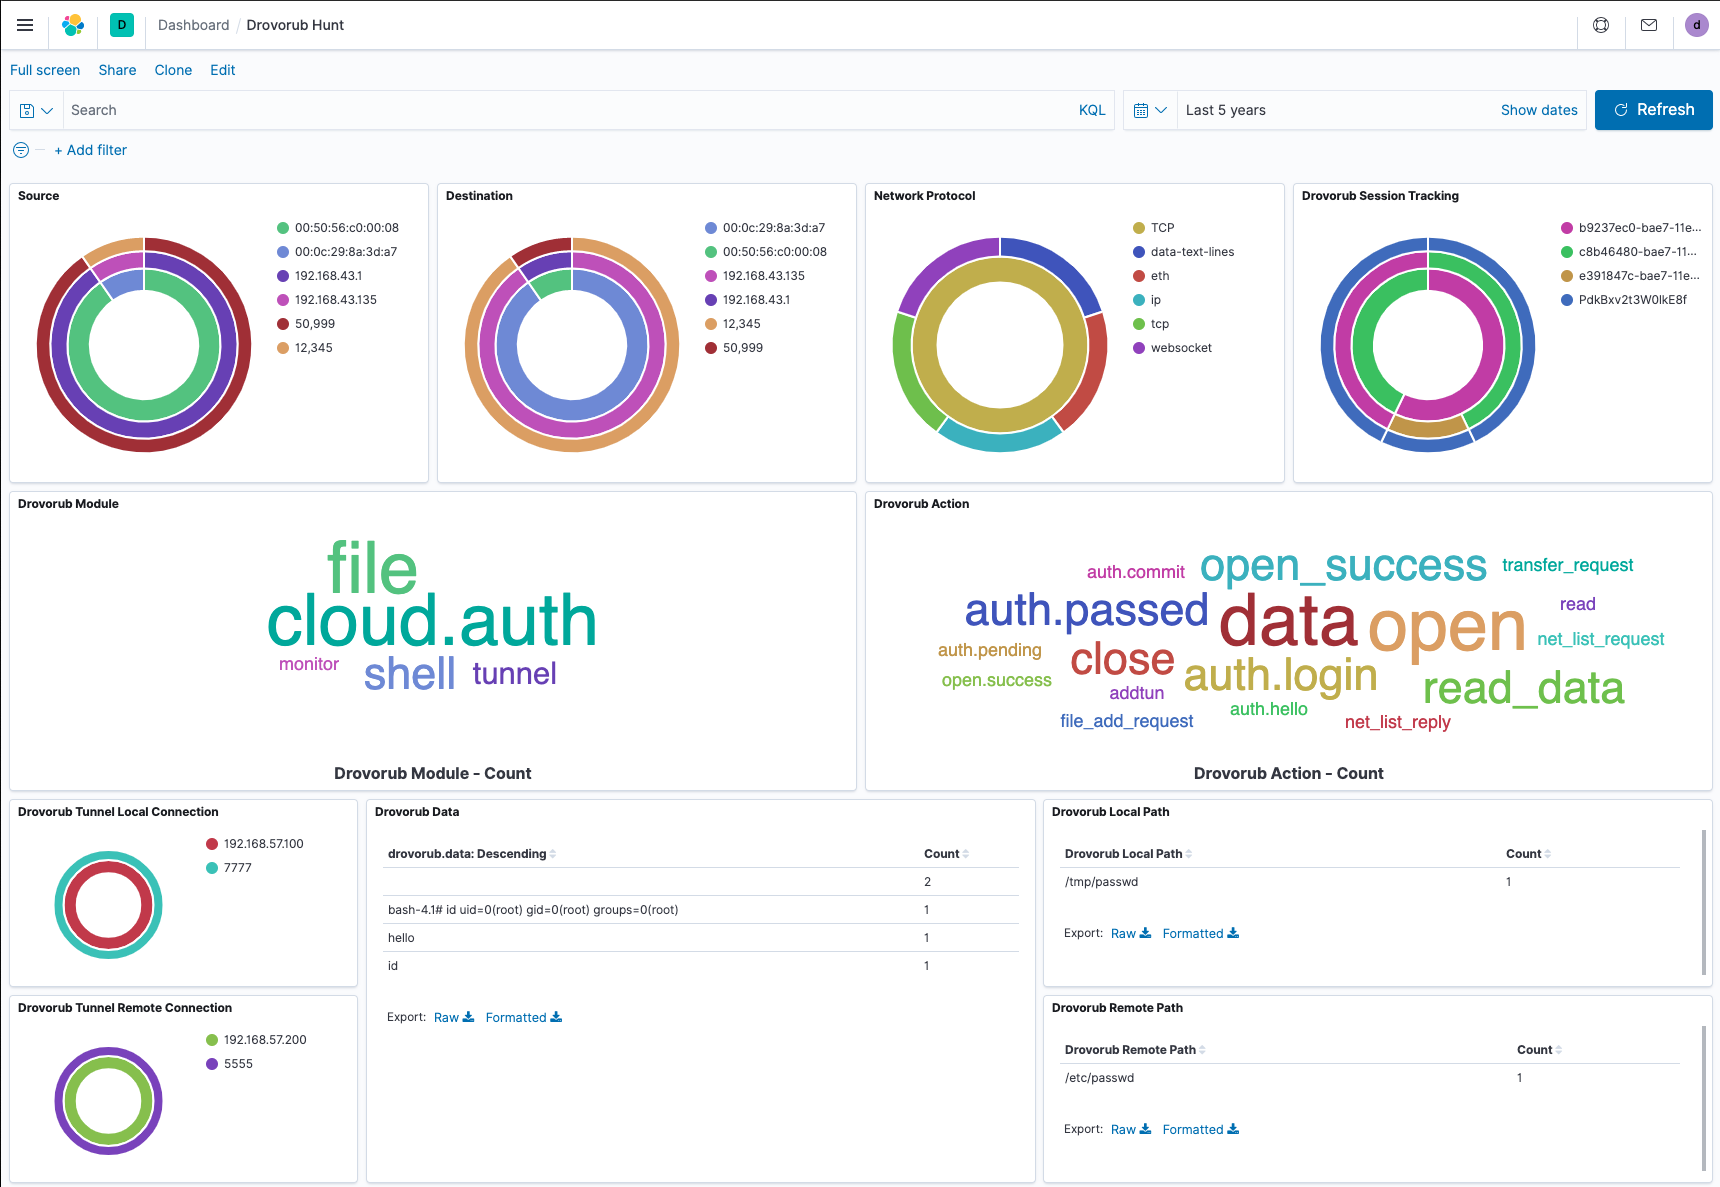 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 corelight/zeek-quic
Bro analyzer that detects Google's QUIC protocol

 nccgroup/baskerville
Selective protocol extractor from PCAPs or interfaces
 nao-sec/ramnit_traffic_parser
Parsing Ramnit's traffic
 jhatchi/nexacorp-dfir-inc-2026-001
DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…
 stevehenderson/lab_xz_backdoor
Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)
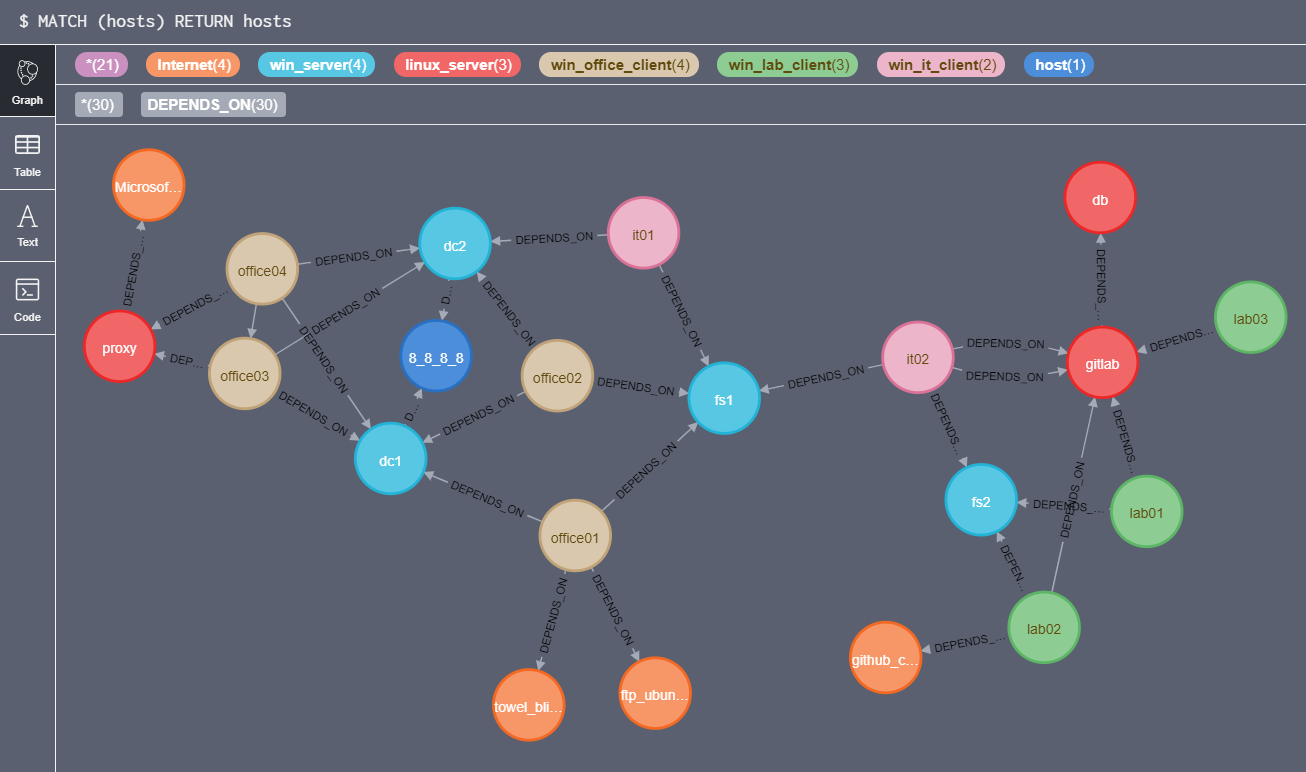 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines


 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
 google/gopacket
Provides packet processing capabilities for Go
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.