
Hodometer
 gary23w/hodometer
A single-file native Windows tray application (C, Win32, no runtime) that shows exactly which program is sending and receiving bytes and to which…
defensive-toolsdns-analysisforensics+5
1
gary23w/hodometerA single-file native Windows tray application (C, Win32, no runtime) that shows exactly which program is sending and receiving bytes and to which…
 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management
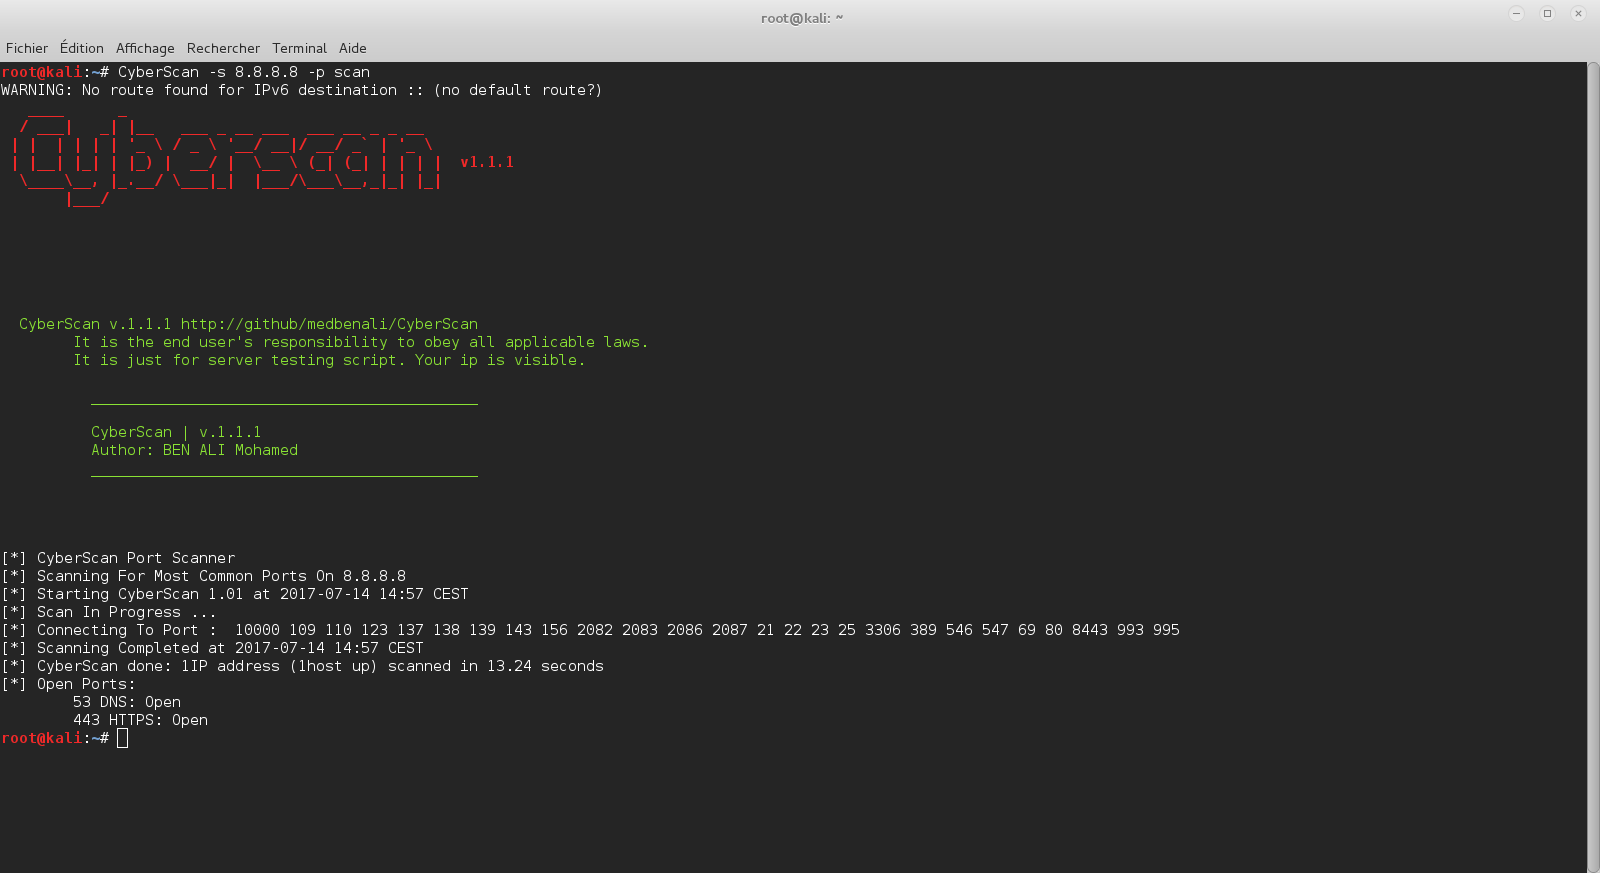 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
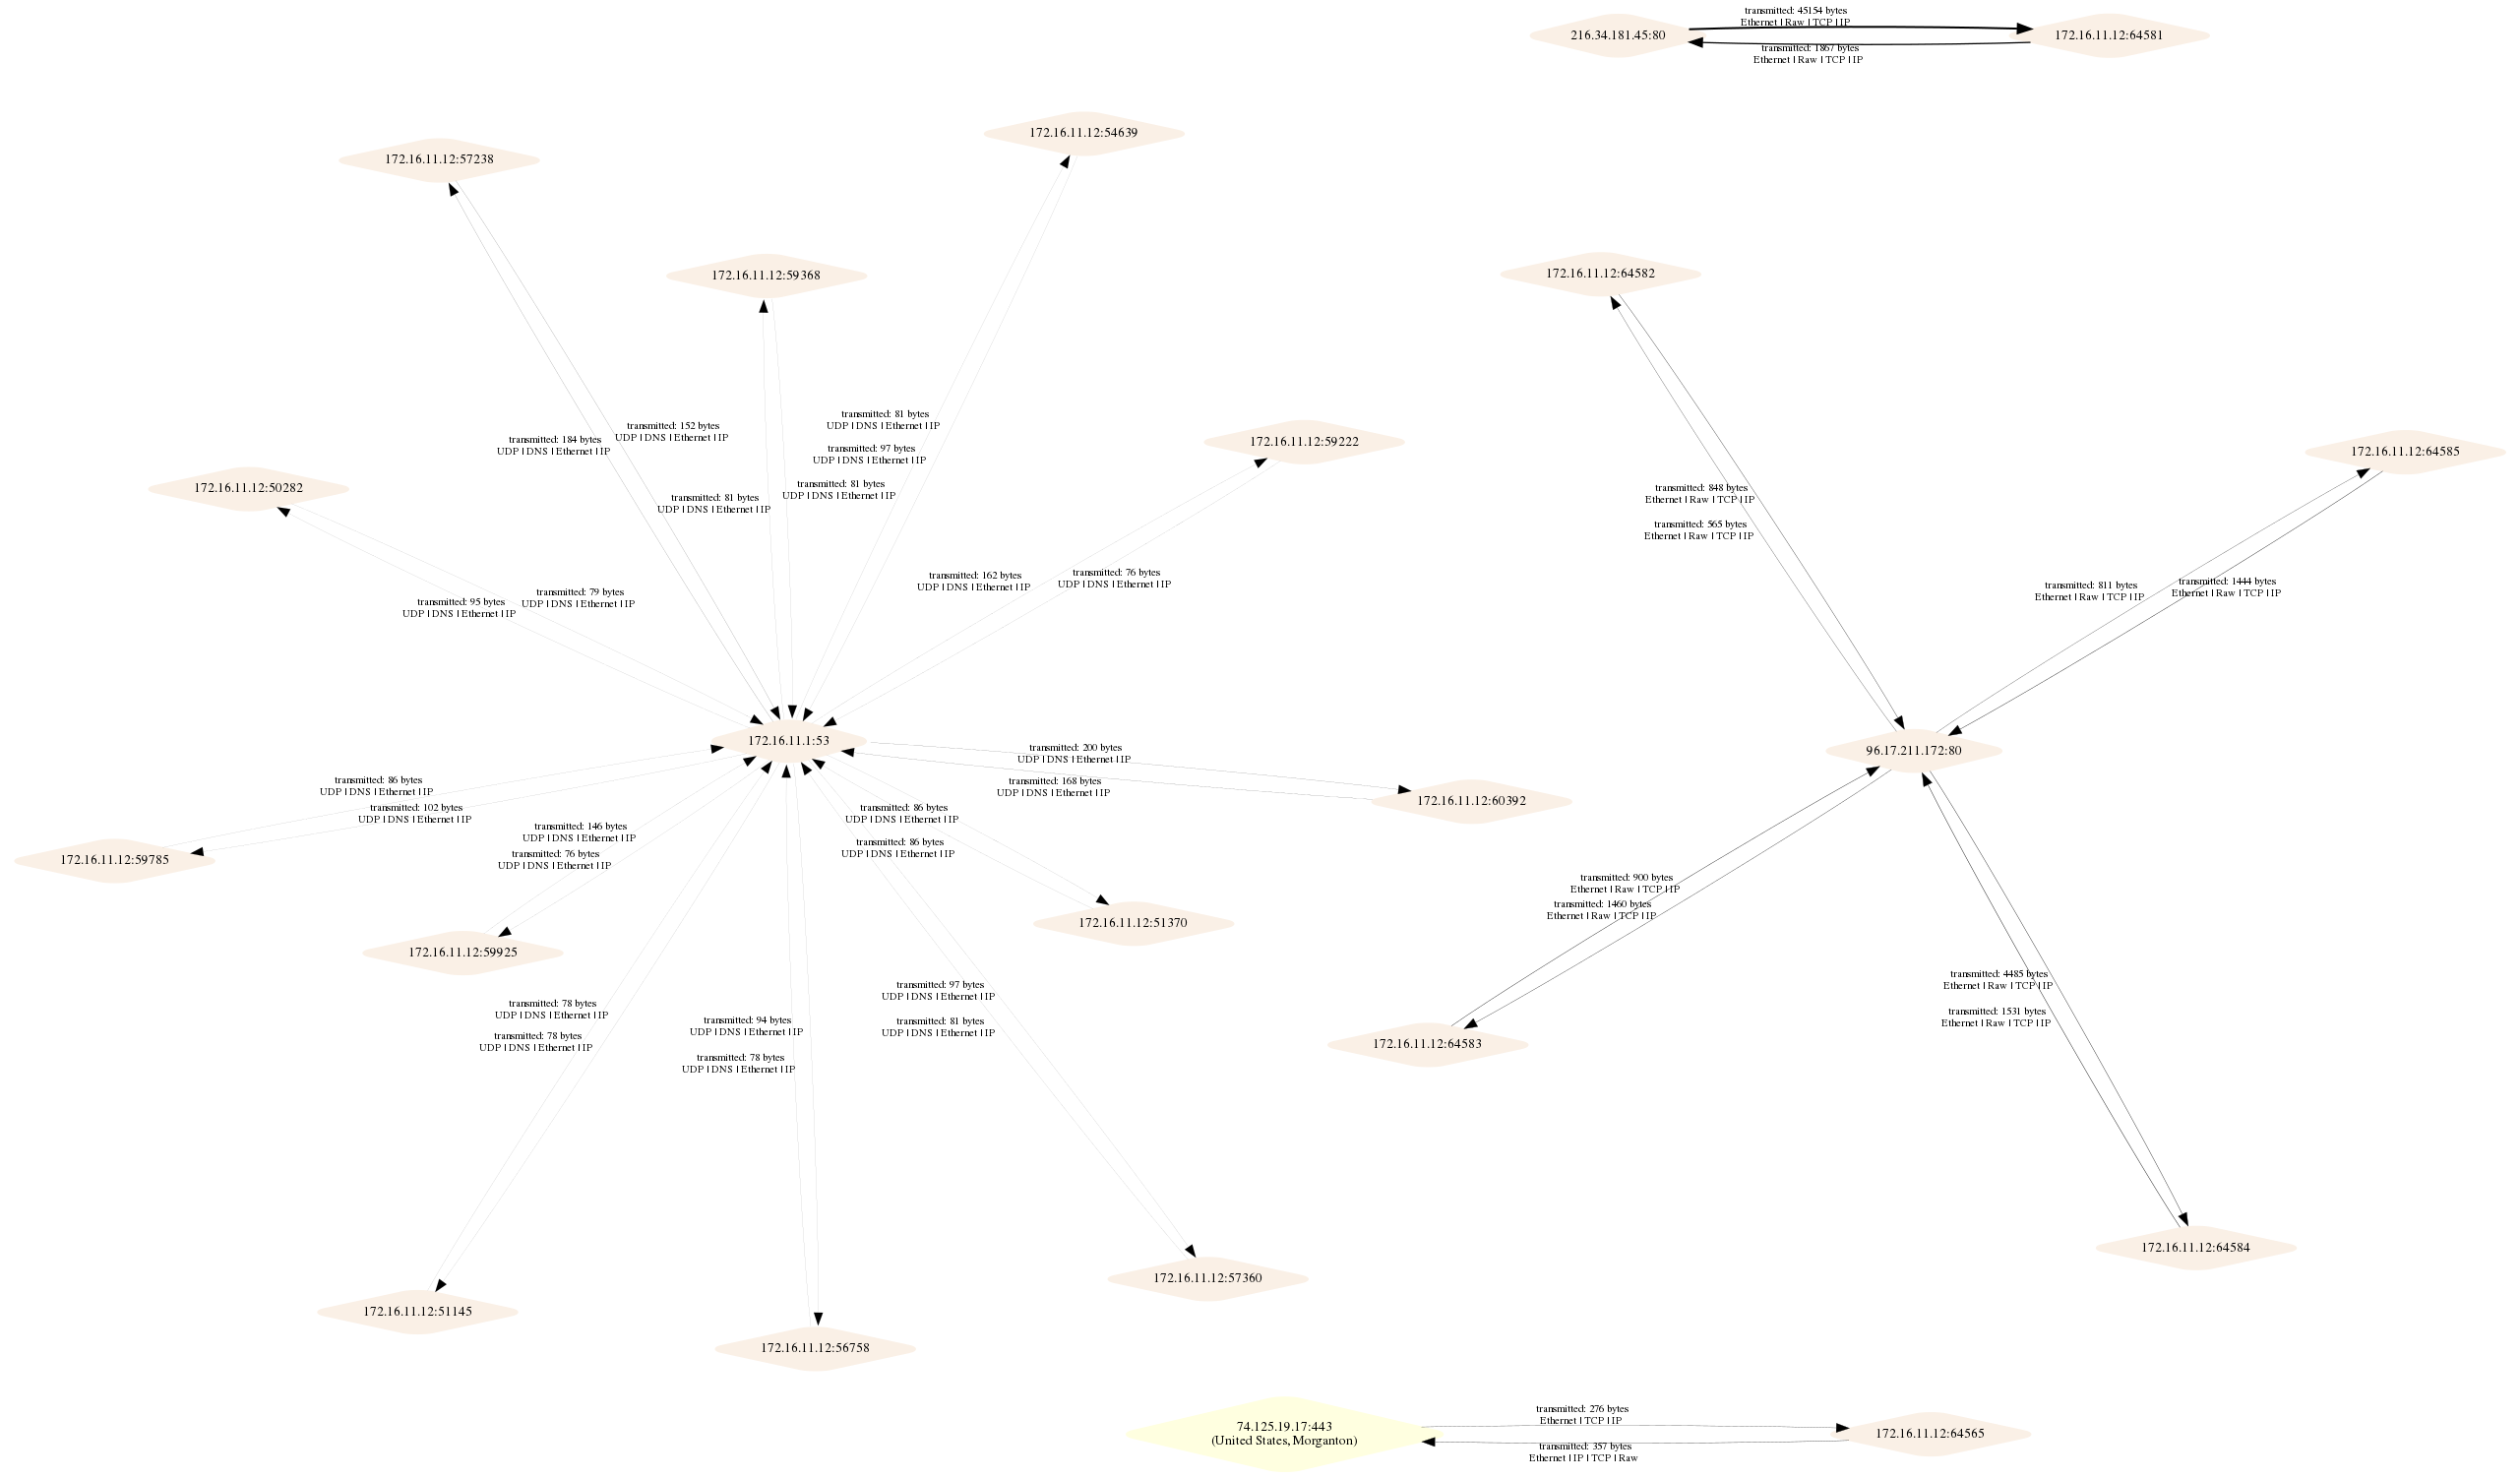 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 z4l4mi/ipgeo
Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
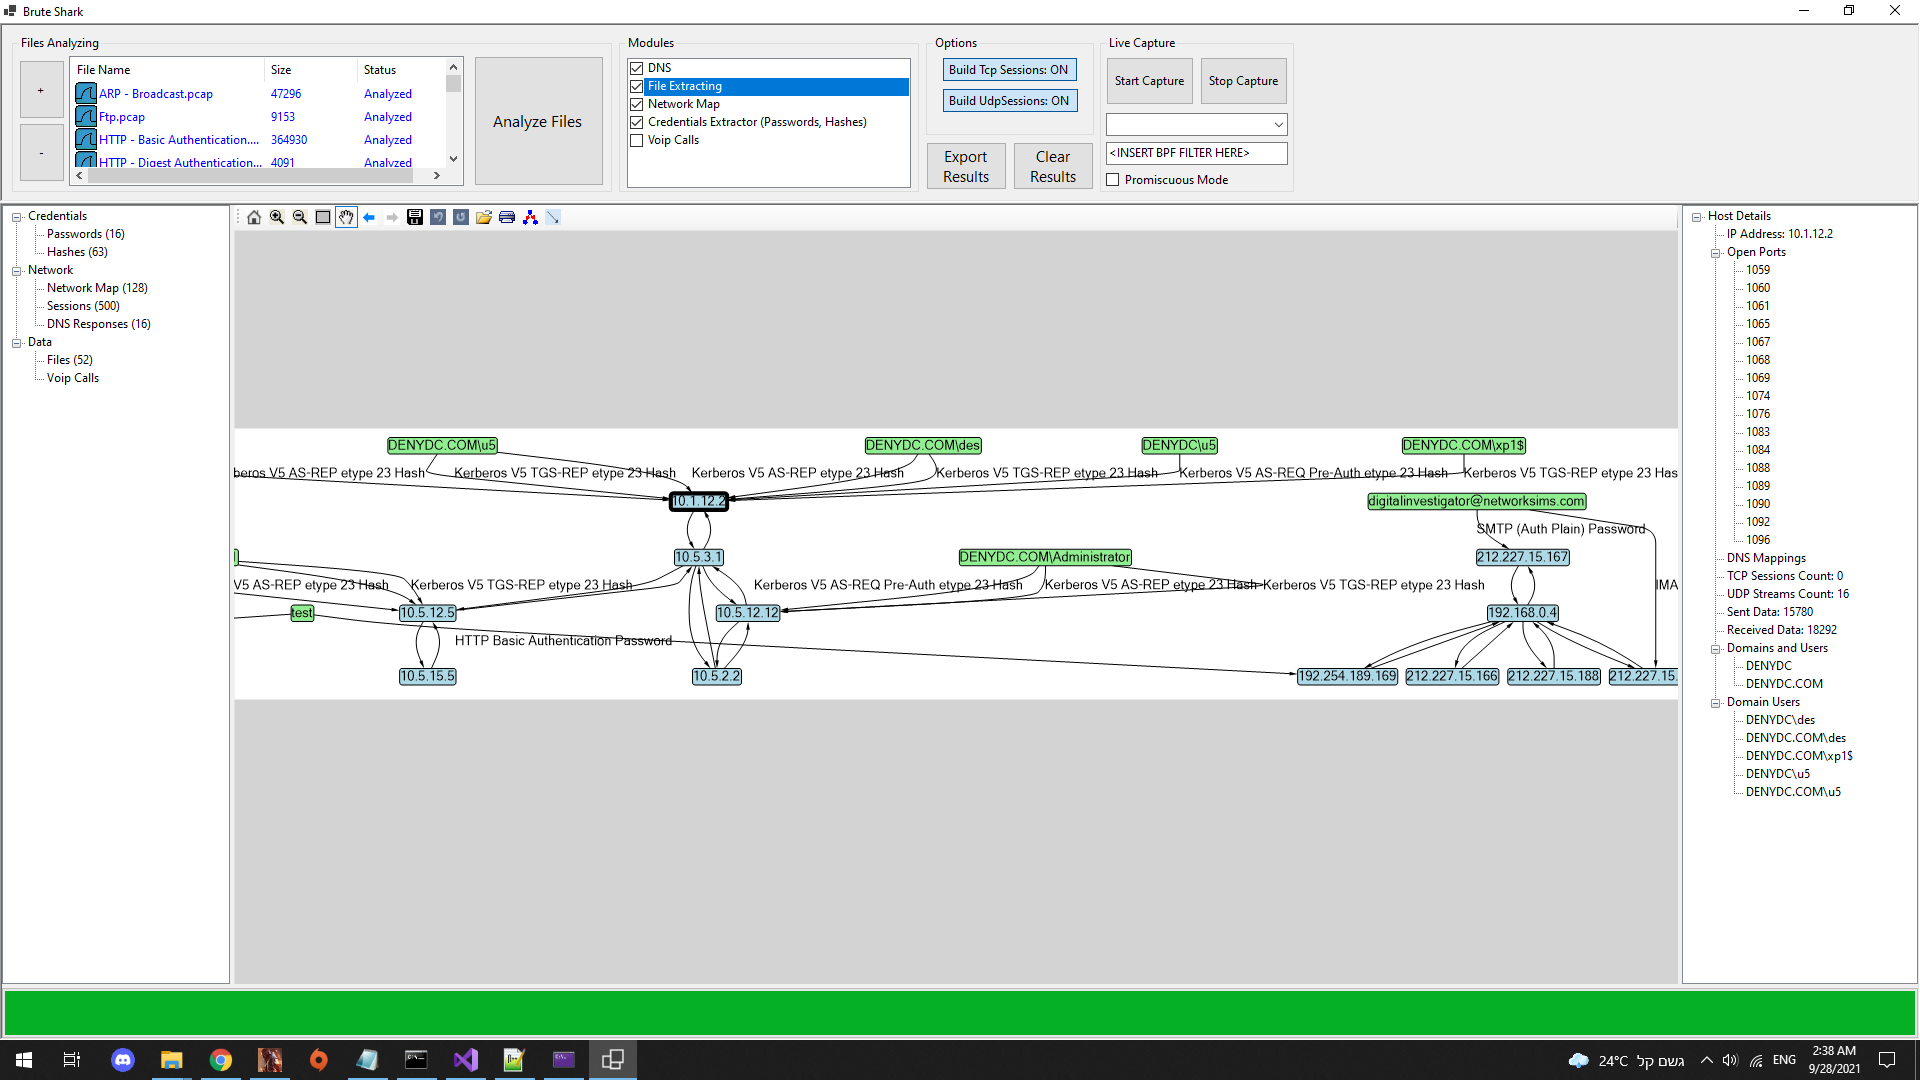
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 omriher/captipper
Malicious HTTP traffic explorer
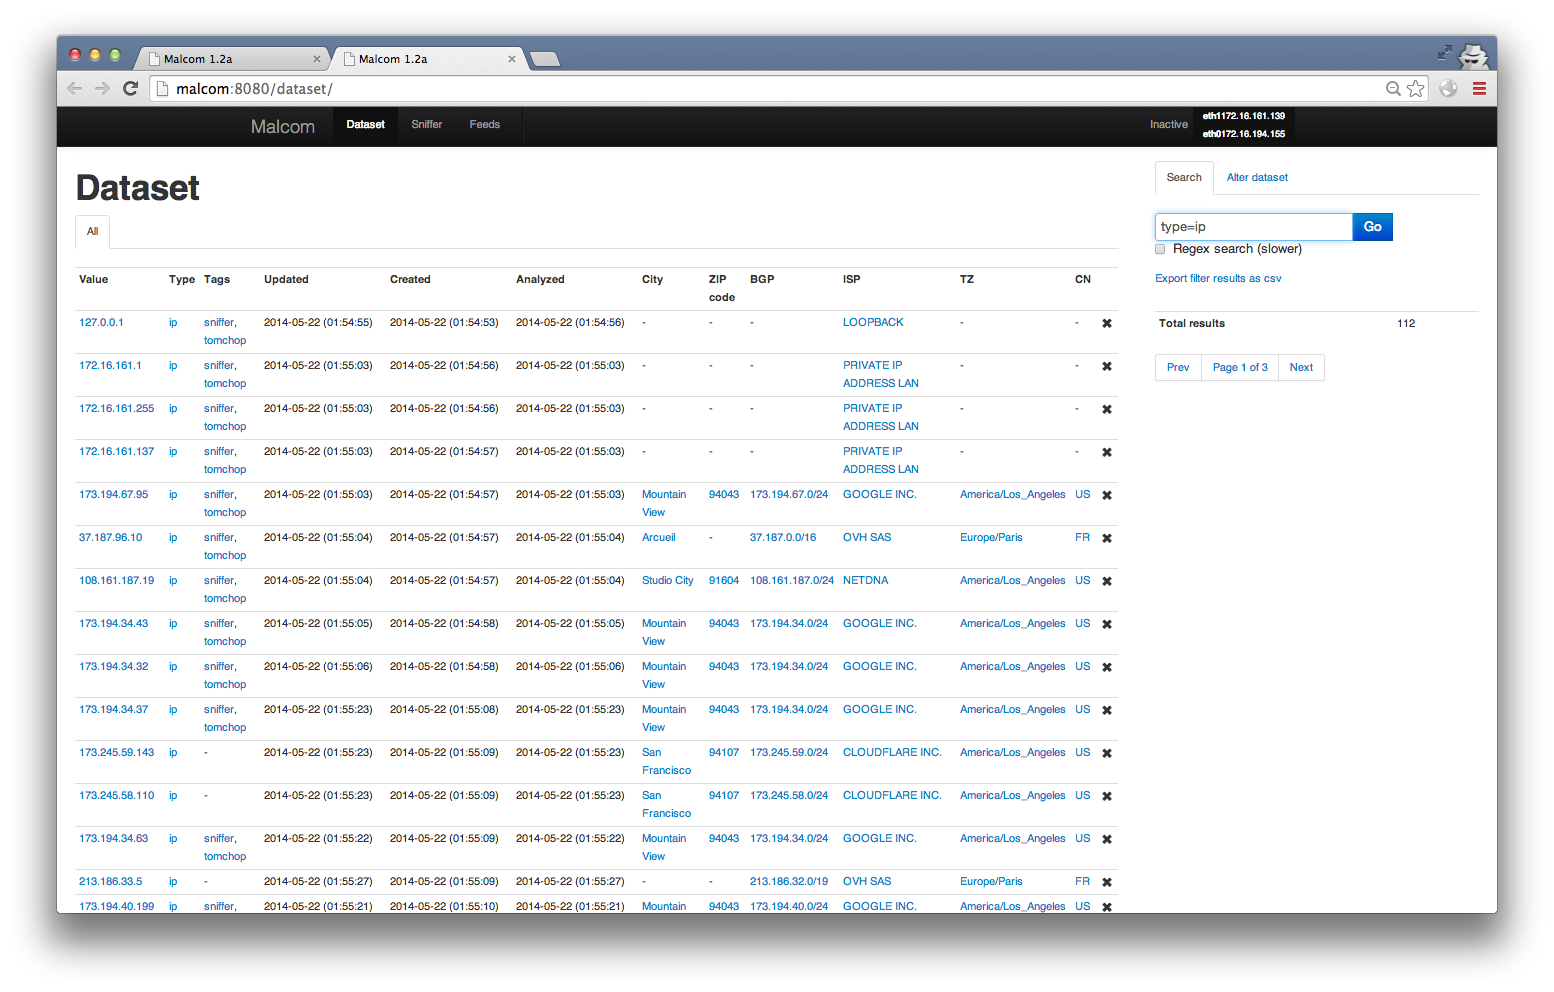 tomchop/malcom
Malcom - Malware Communications Analyzer
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 detuxsandbox/detux
The Multiplatform Linux Sandbox
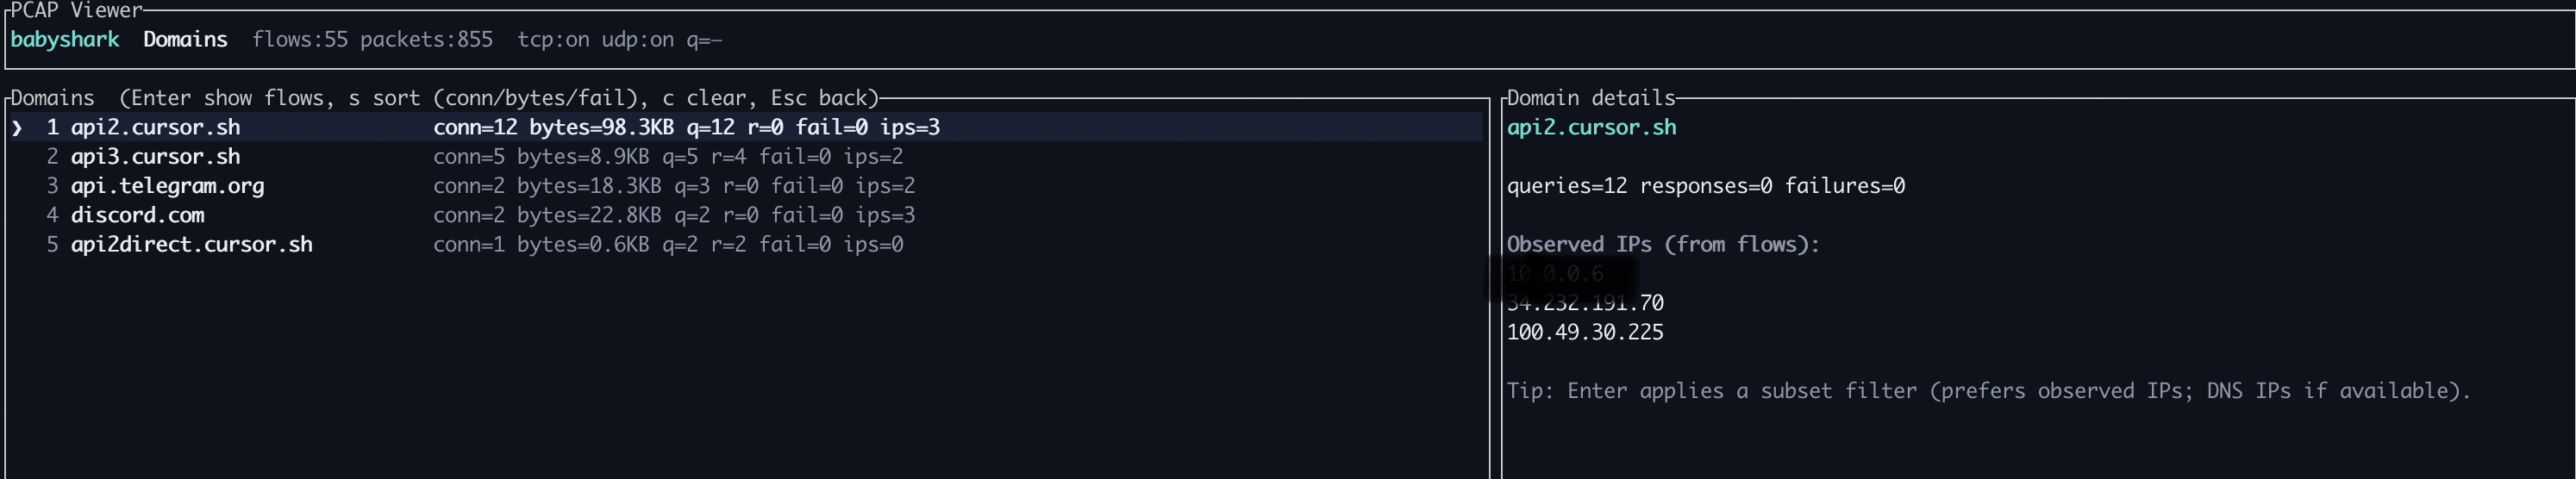 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 anssi-fr/dfir4vsphere
Powershell module for VMWare vSphere forensics
 nccgroup/pcap-burp
Pcap importer for Burp