

zeek
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
anomaly-detectionanti-botdefensive-tools+14
zeek/zeekZeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 omriher/captipper
Malicious HTTP traffic explorer
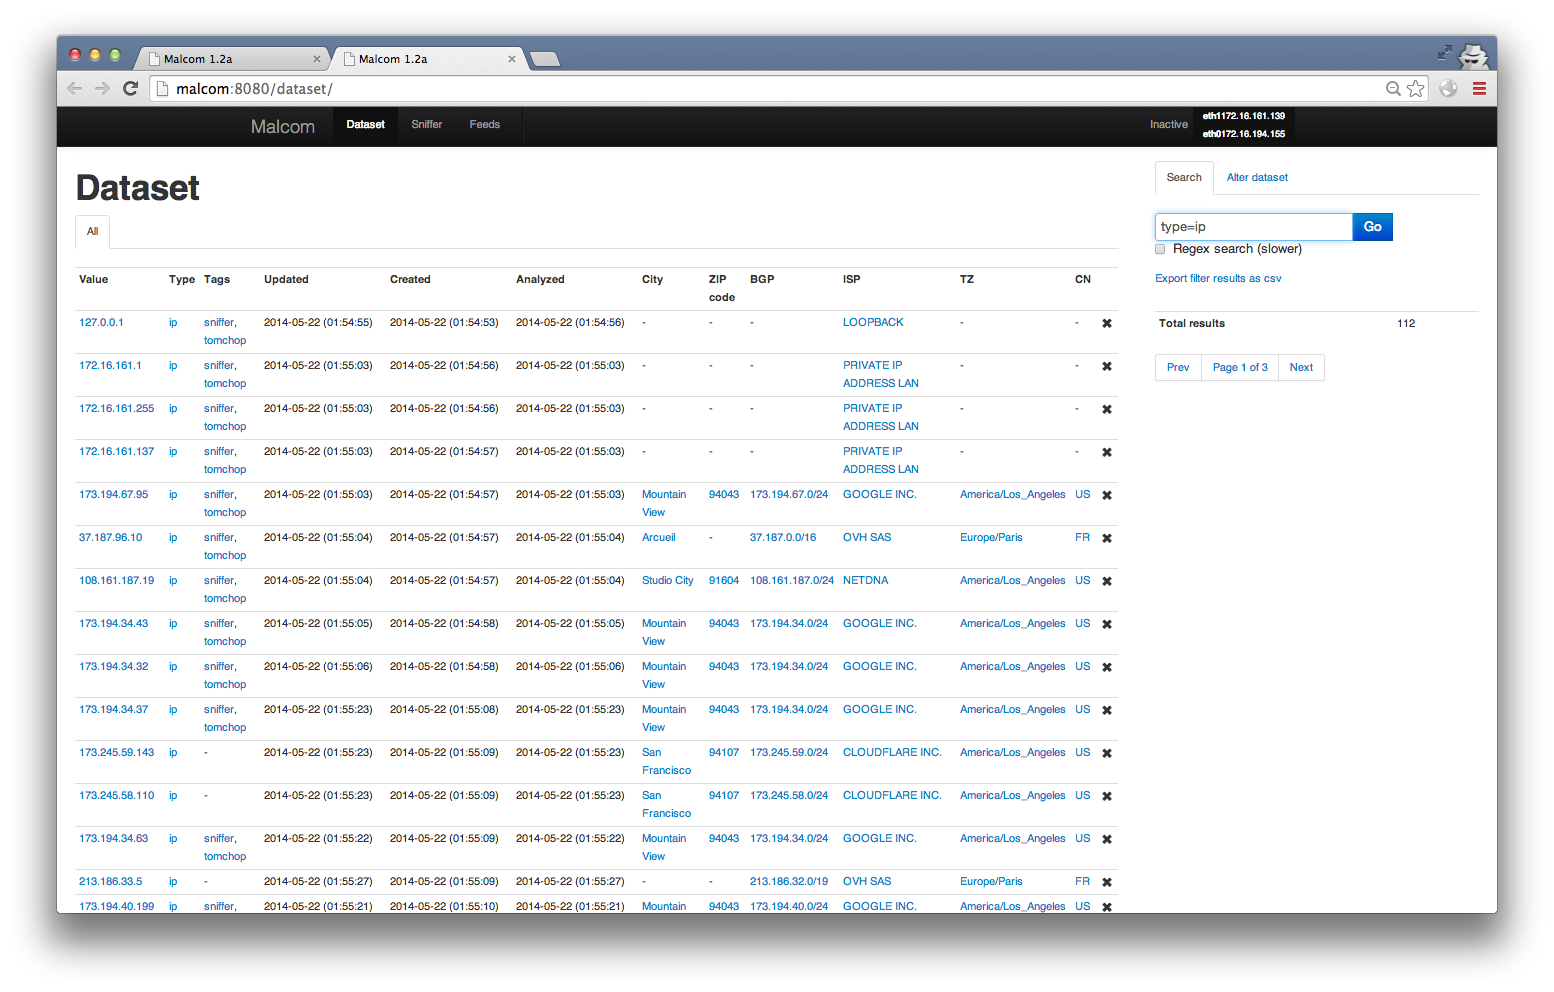 tomchop/malcom
Malcom - Malware Communications Analyzer
 detuxsandbox/detux
The Multiplatform Linux Sandbox
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
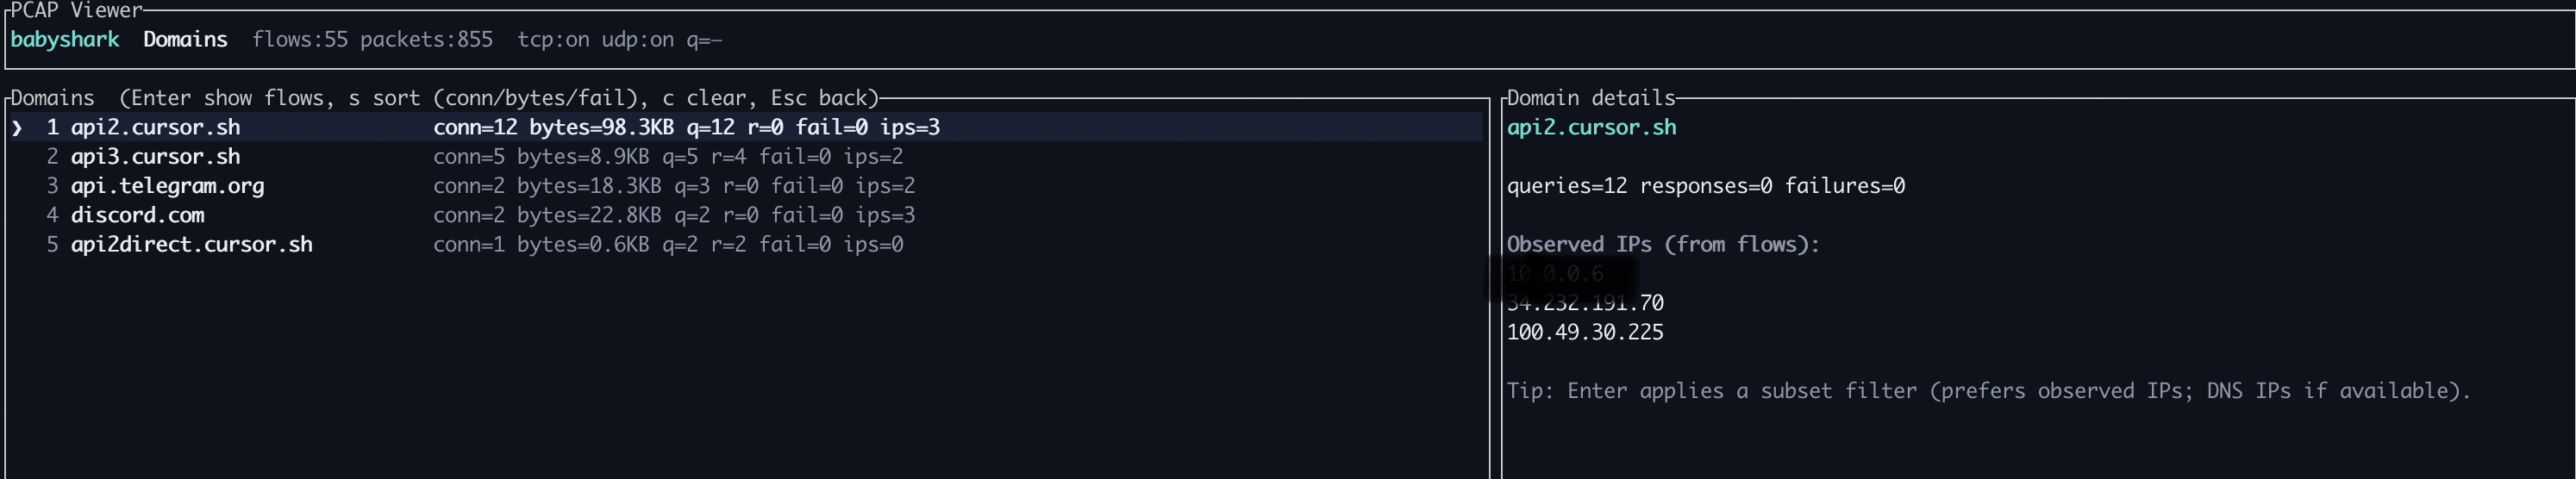 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 anssi-fr/dfir4vsphere
Powershell module for VMWare vSphere forensics
 nccgroup/pcap-burp
Pcap importer for Burp
 leonward/openfpc
OpenFPC, Open Source Full Packet Capture
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
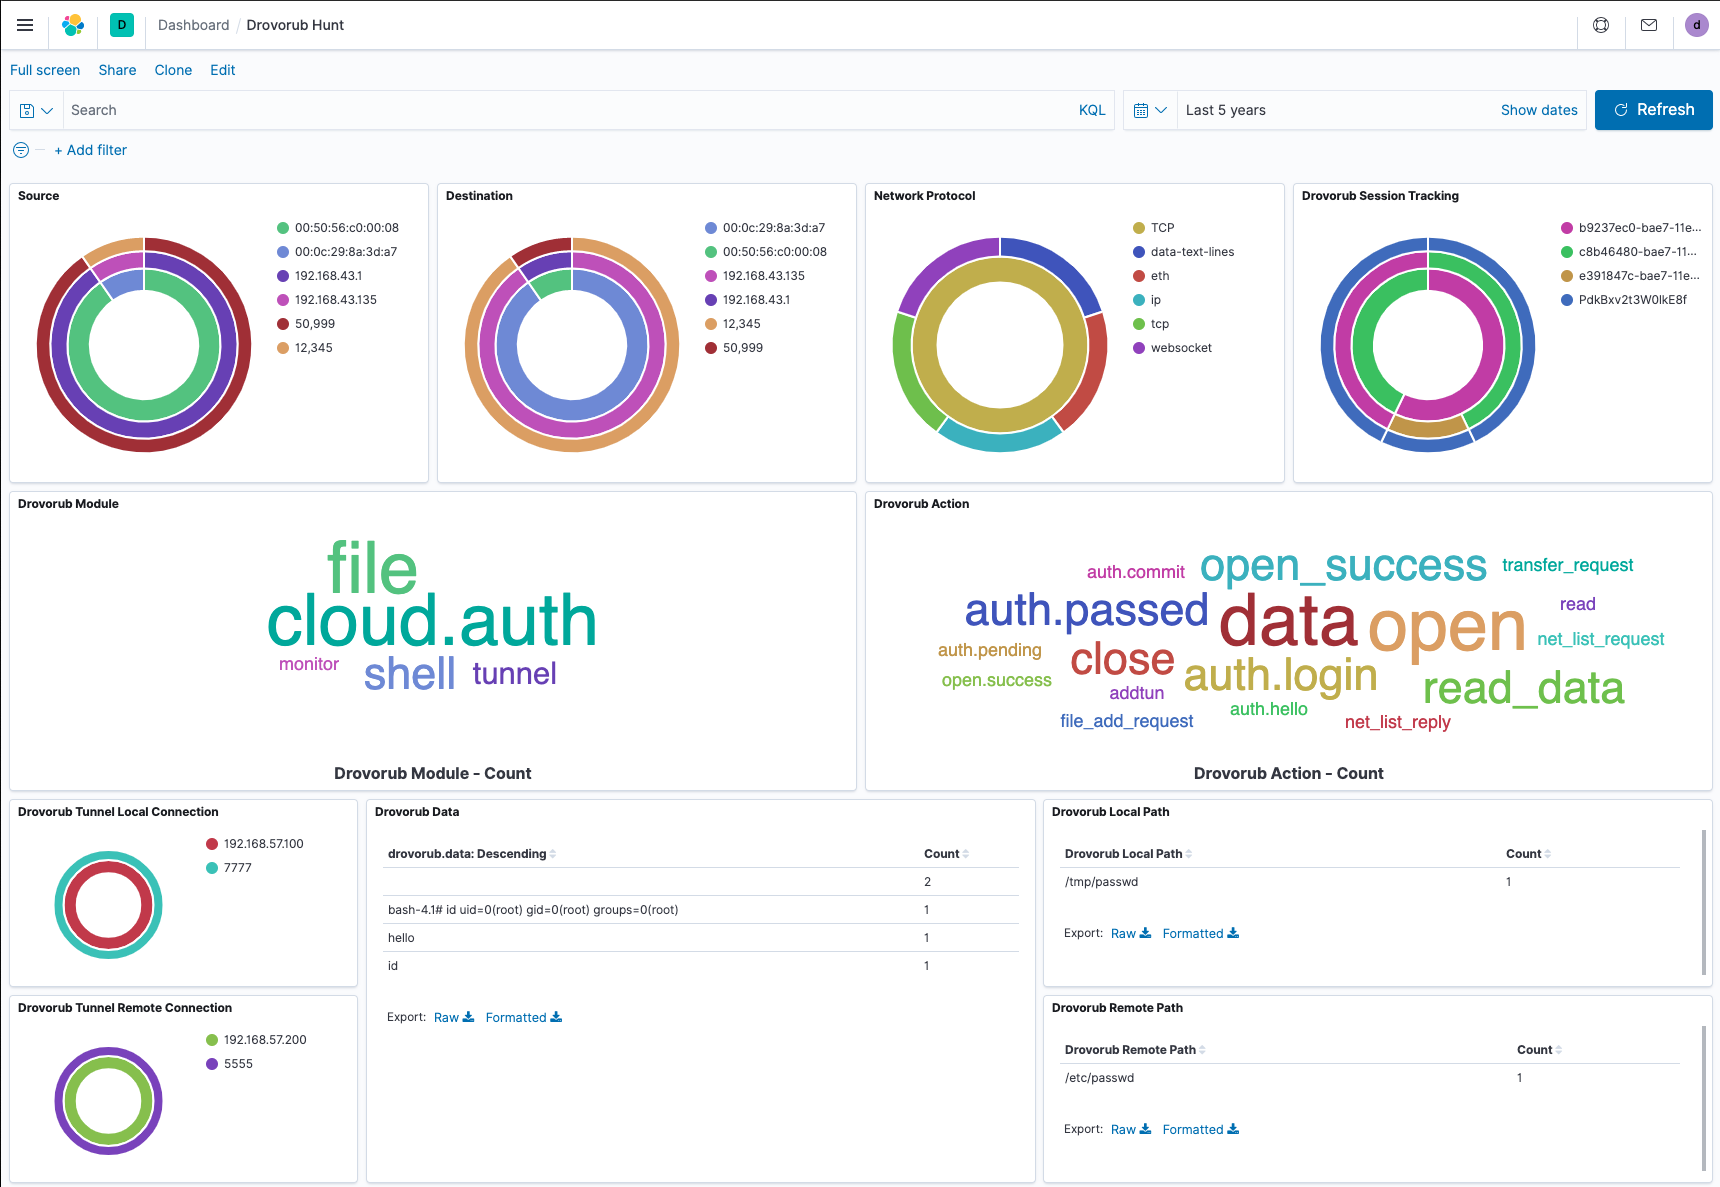 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis