

zeek-spicy-stun
 corelight/zeek-spicy-stun
A Zeek STUN protocol analyzer based on Spicy.
forensicsinformation-gatheringnetwork-forensics+2
5
corelight/zeek-spicy-stunA Zeek STUN protocol analyzer based on Spicy.
 abdom.seada/security-checks
linux security checks
 google/stenographer
Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those…
 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
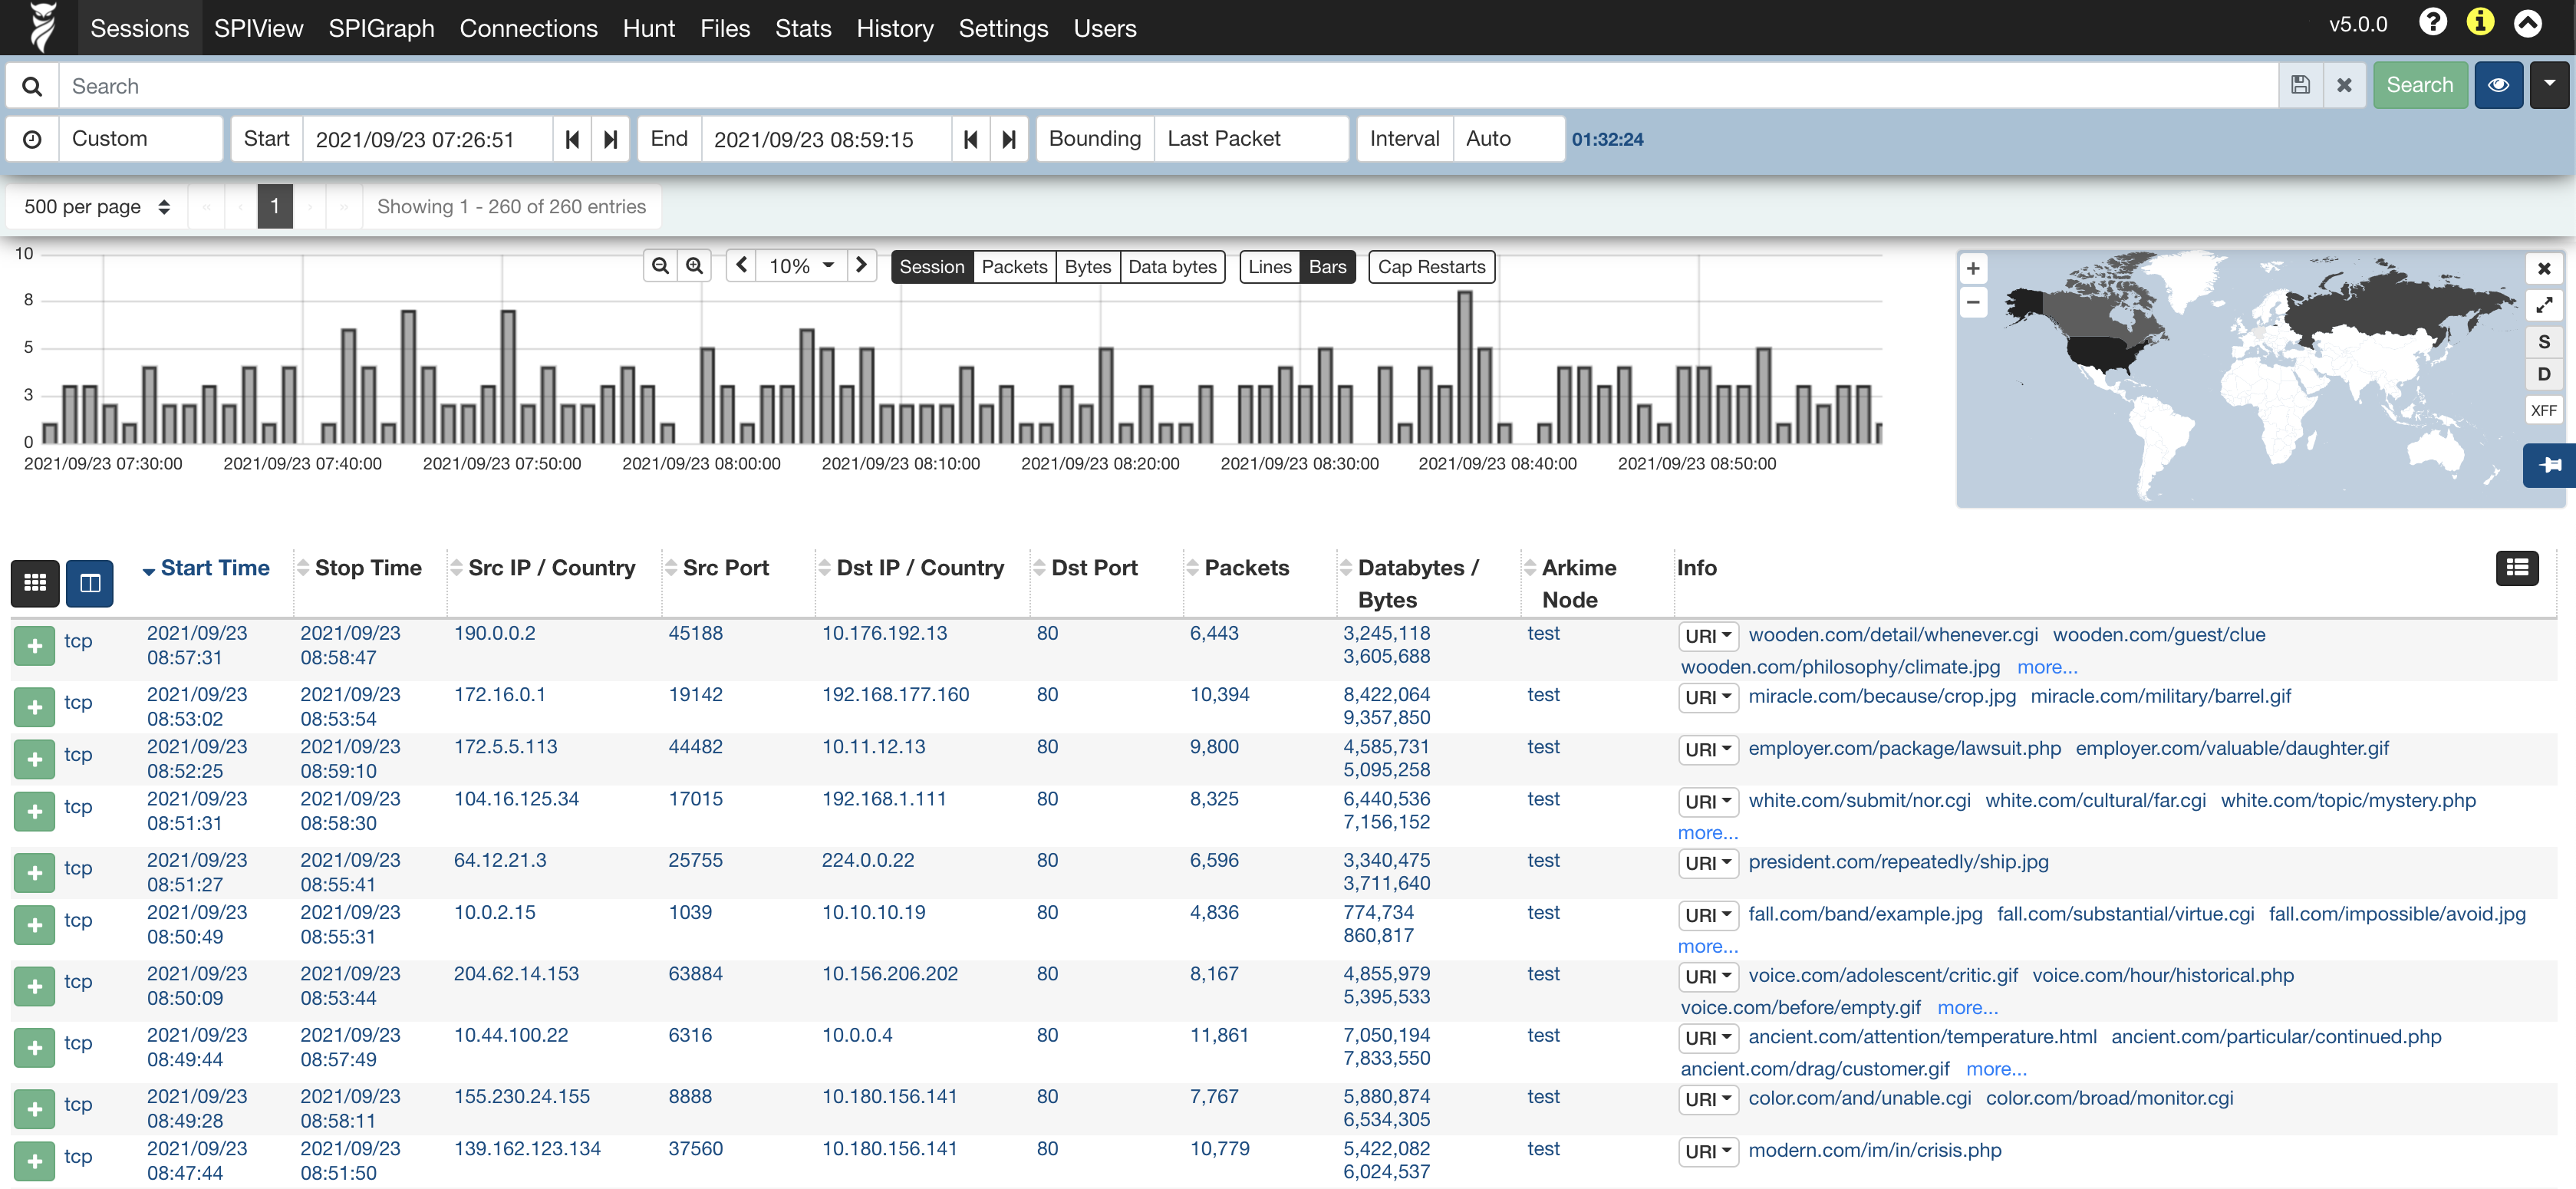 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
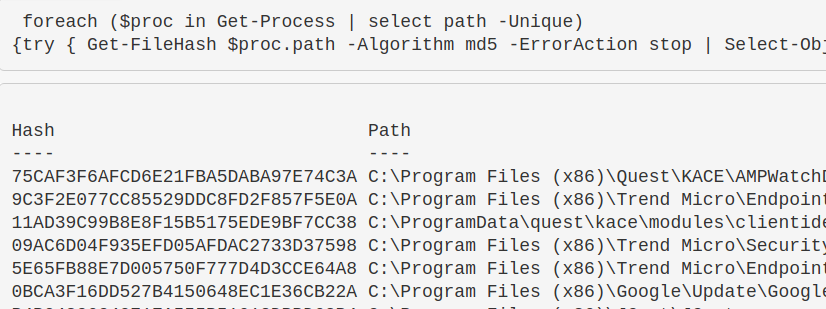 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
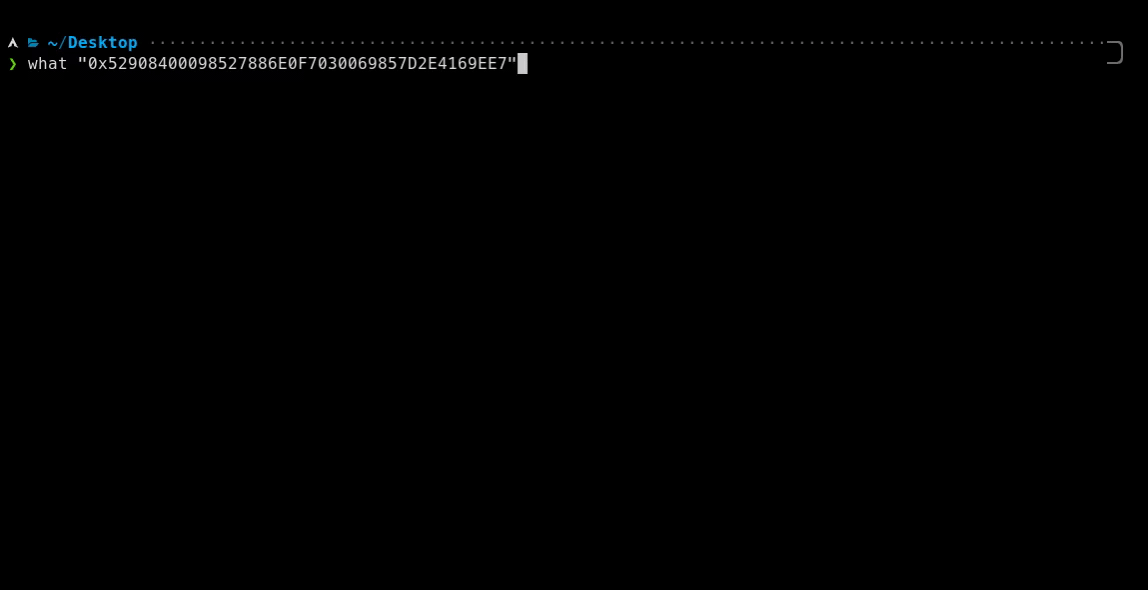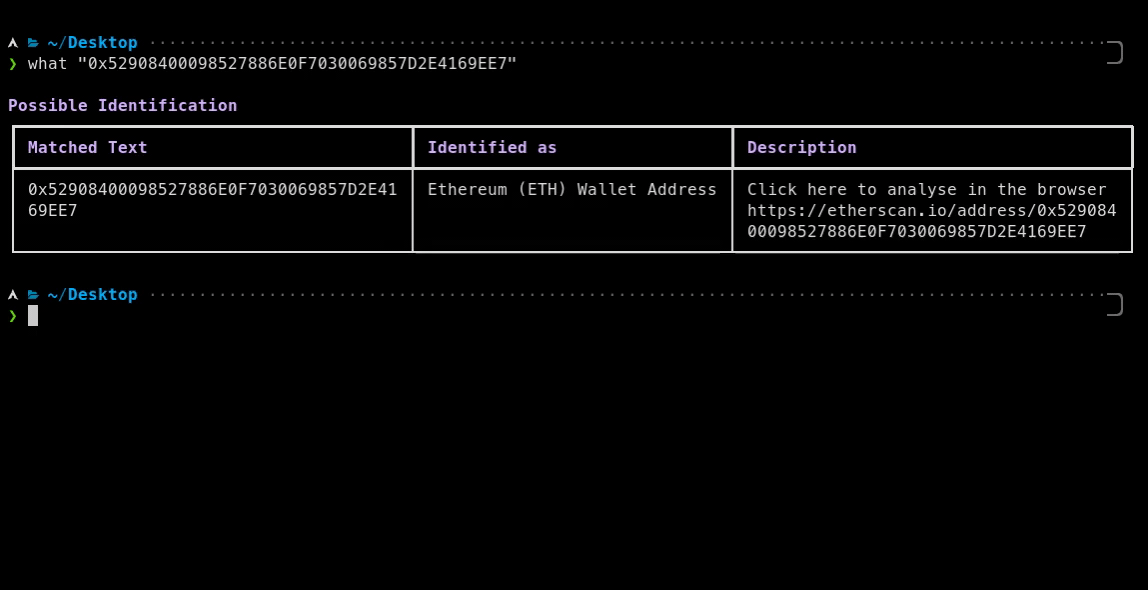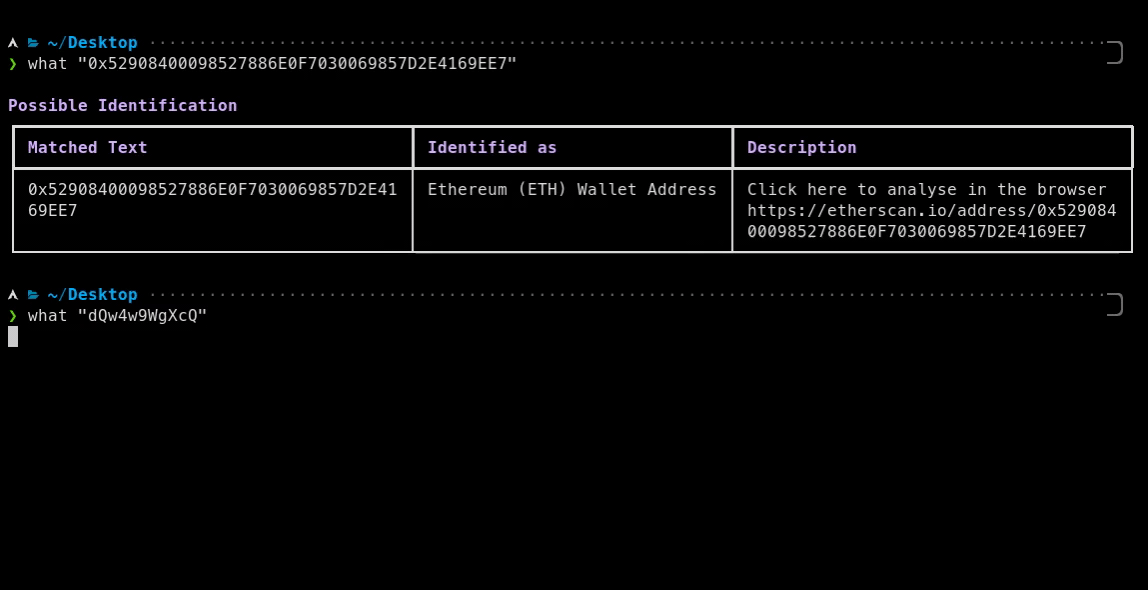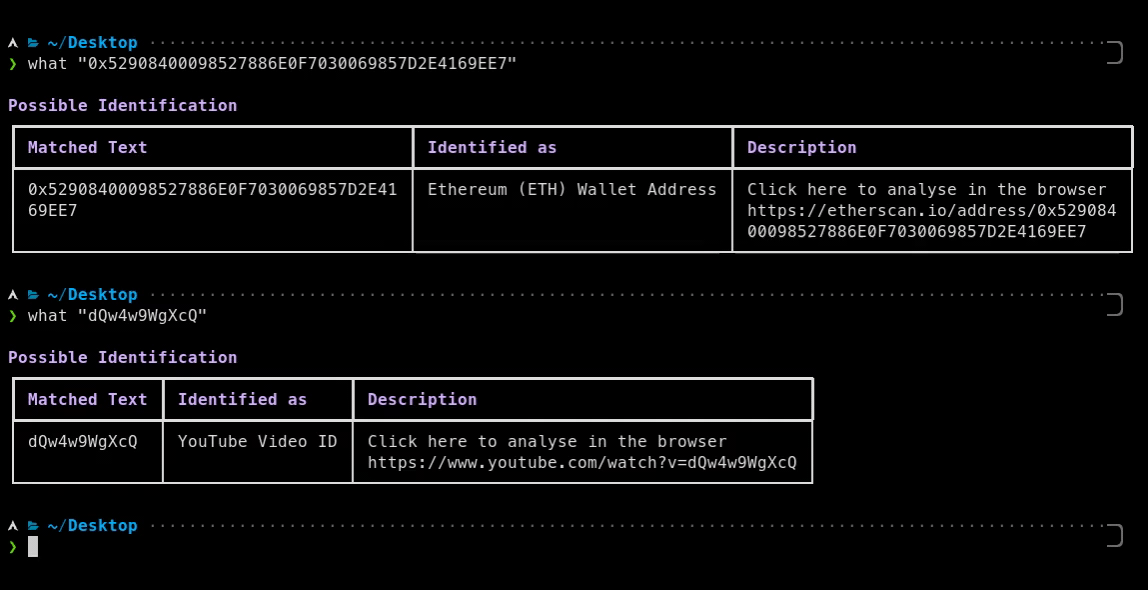 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 mattnotmax/cyberchef-recipes
A list of cyber-chef recipes and curated links
 simsong/tcpflow
TCP/IP packet demultiplexer. Download from:
 omriher/captipper
Malicious HTTP traffic explorer