
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
146 results
cyberchef-recipes preview

cyberchef-recipes

GitHubmattnotmax/cyberchef-recipes

A list of cyber-chef recipes and curated links

curated-resourcesdigital-forensicsdisk-forensics+8
2.2k
3 years ago
malware-samples preview

malware-samples

GitHubjstrosch/malware-samples

Malware samples, analysis exercises and other interesting resources.
binary-analysiscurated-resourceseducation+3
1.7k2 years ago
pyrdp preview

pyrdp

GitHubgosecure/pyrdp

RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact

ctfeducationexploitation+9
1.8k5 months ago
dissect preview

dissect

GitHubfox-it/dissect

Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
data-recoverydigital-forensicsdisk-forensics+5
1.1k3 days ago
PcapXray preview

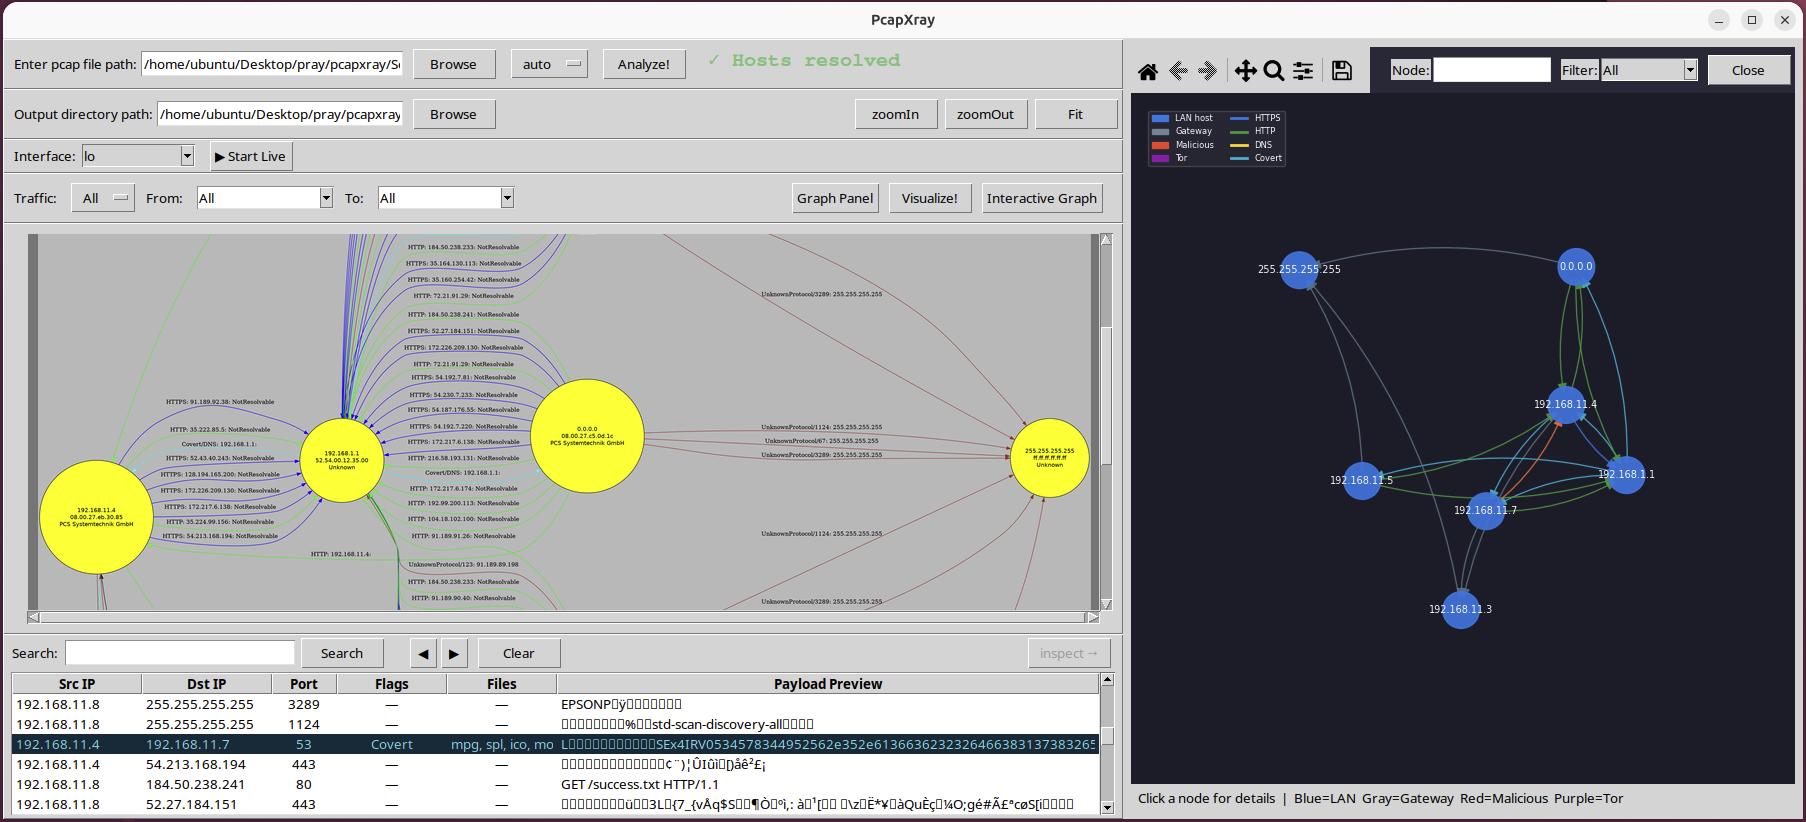
PcapXray

GitHubsrixivas/pcapxray

❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…

ctfdns-analysiseducation+7
1.9k6 months ago
joy preview

joy

GitHubcisco/joy

A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
anomaly-detectiondigital-forensicsdns-analysis+7
1.4k6 years ago
DFIR-LABS preview

DFIR-LABS

GitHubazr43lkn1ght/dfir-labs

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
ctfdigital-forensicsdisk-forensics+6
6711 month ago
StegoForge preview

StegoForge

GitHubnour833/stegoforge

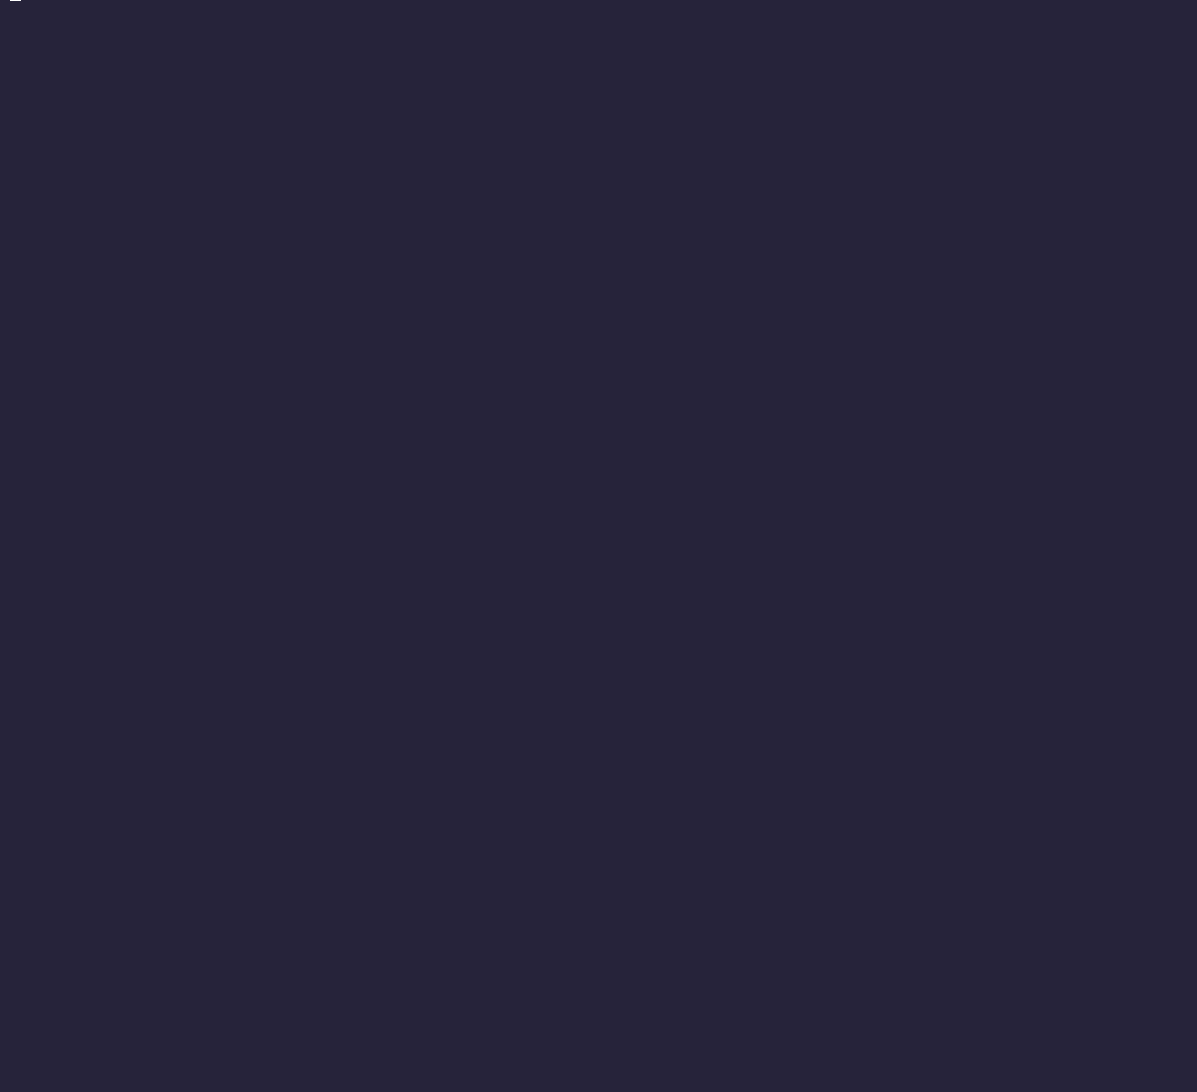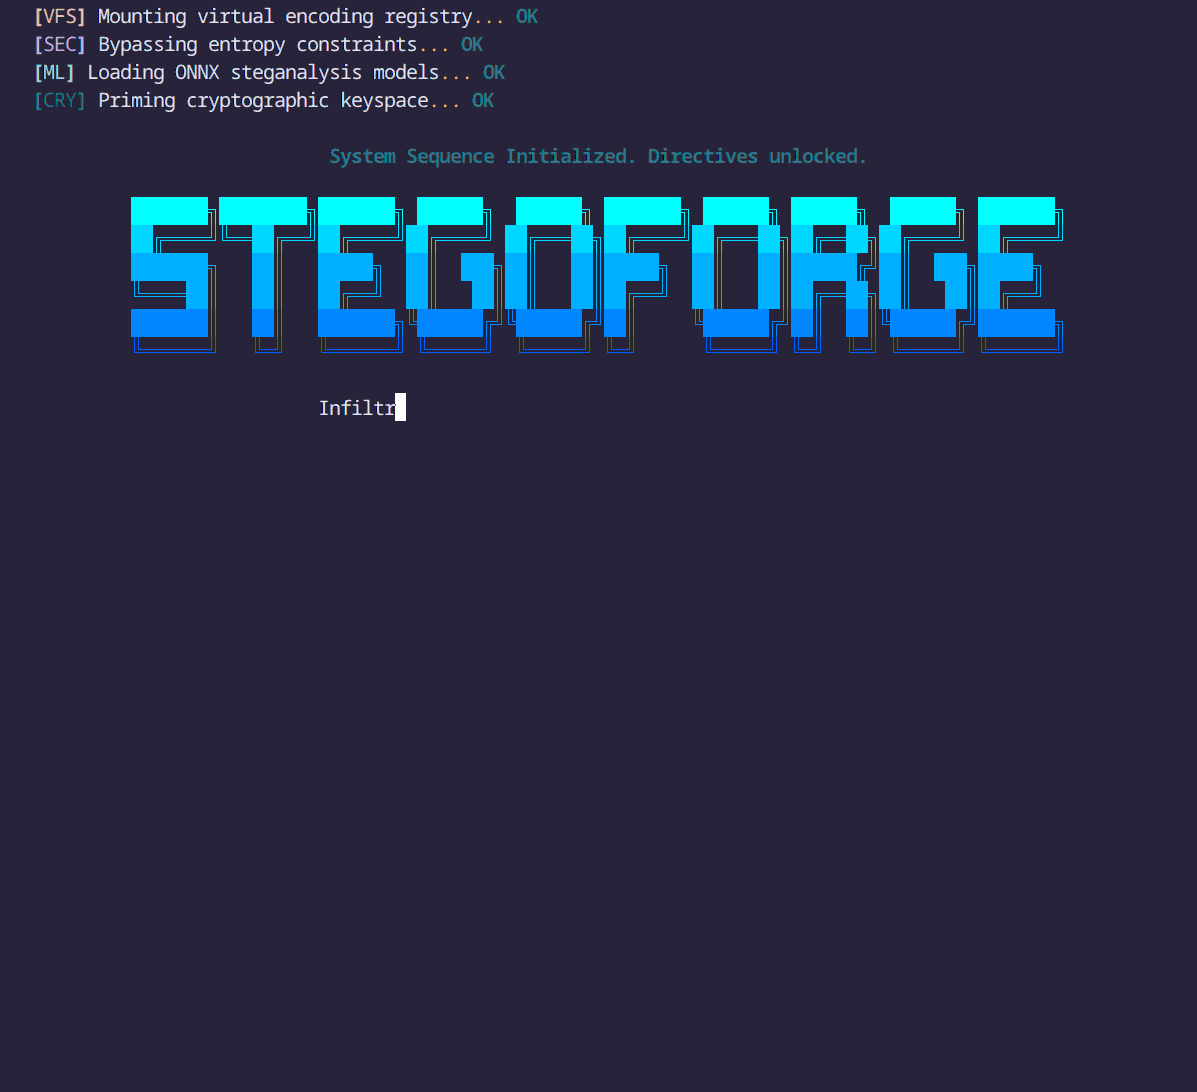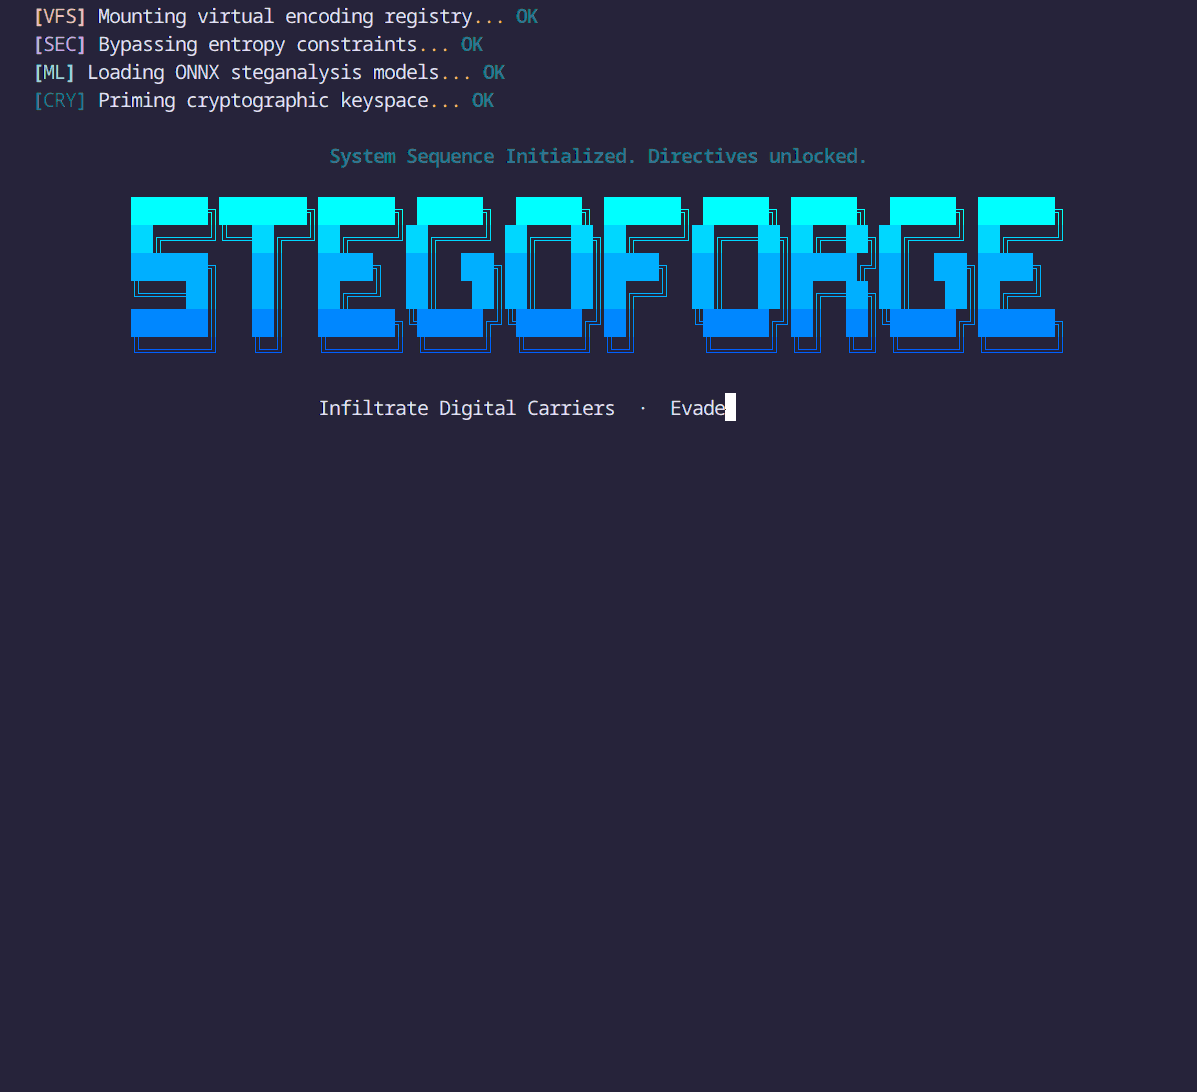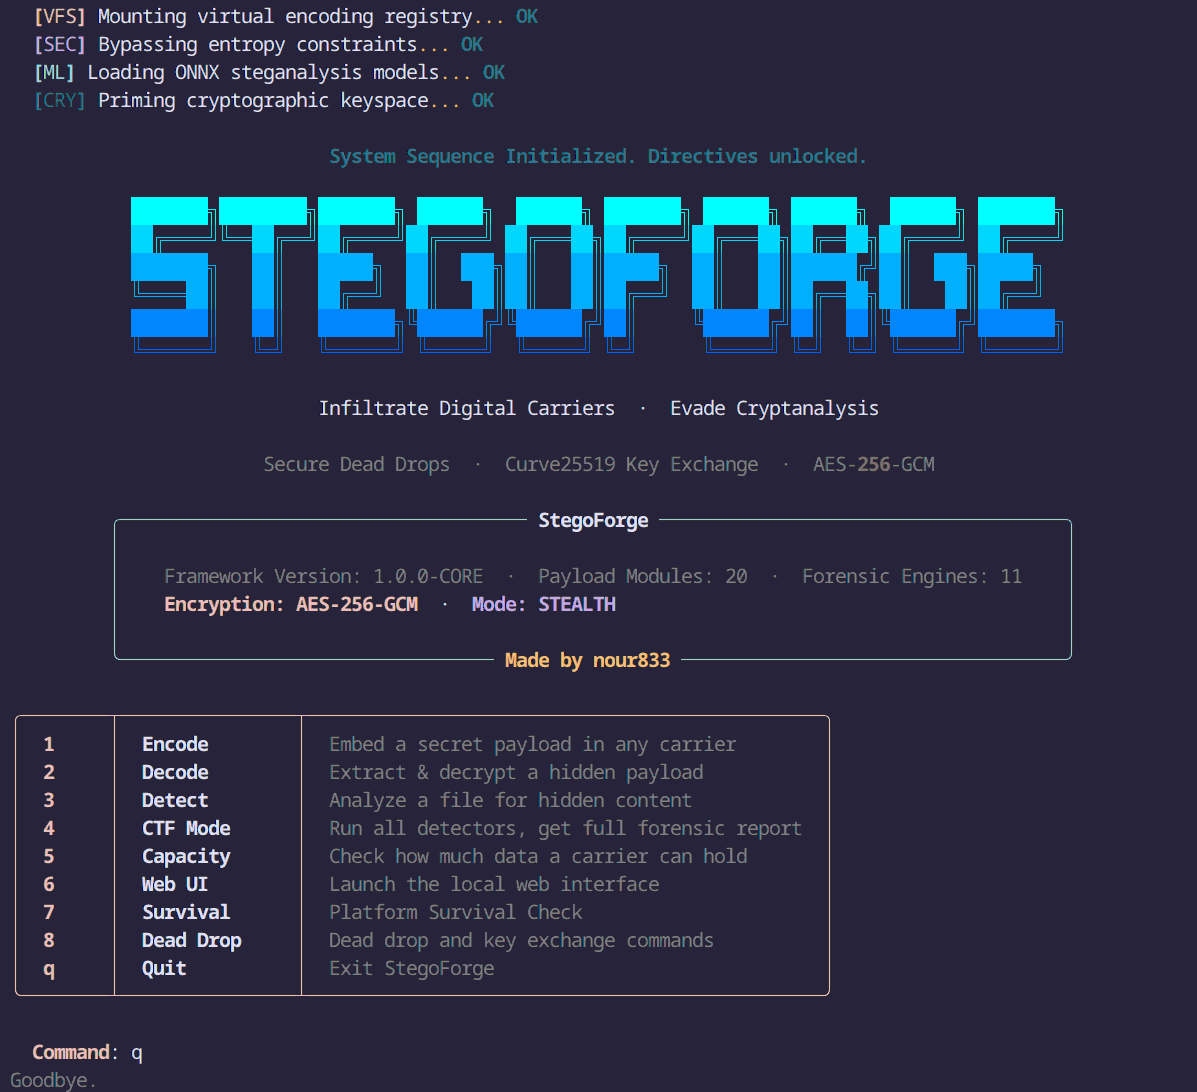
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…
cryptographyctfdata-exfiltration+8
57513 days ago
Malcolm preview

Malcolm

GitHubidaholab/malcolm

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
defensive-toolsdigital-forensicsforensics+8
4761 day ago
so-crates preview

so-crates

GitHubdougburks/so-crates

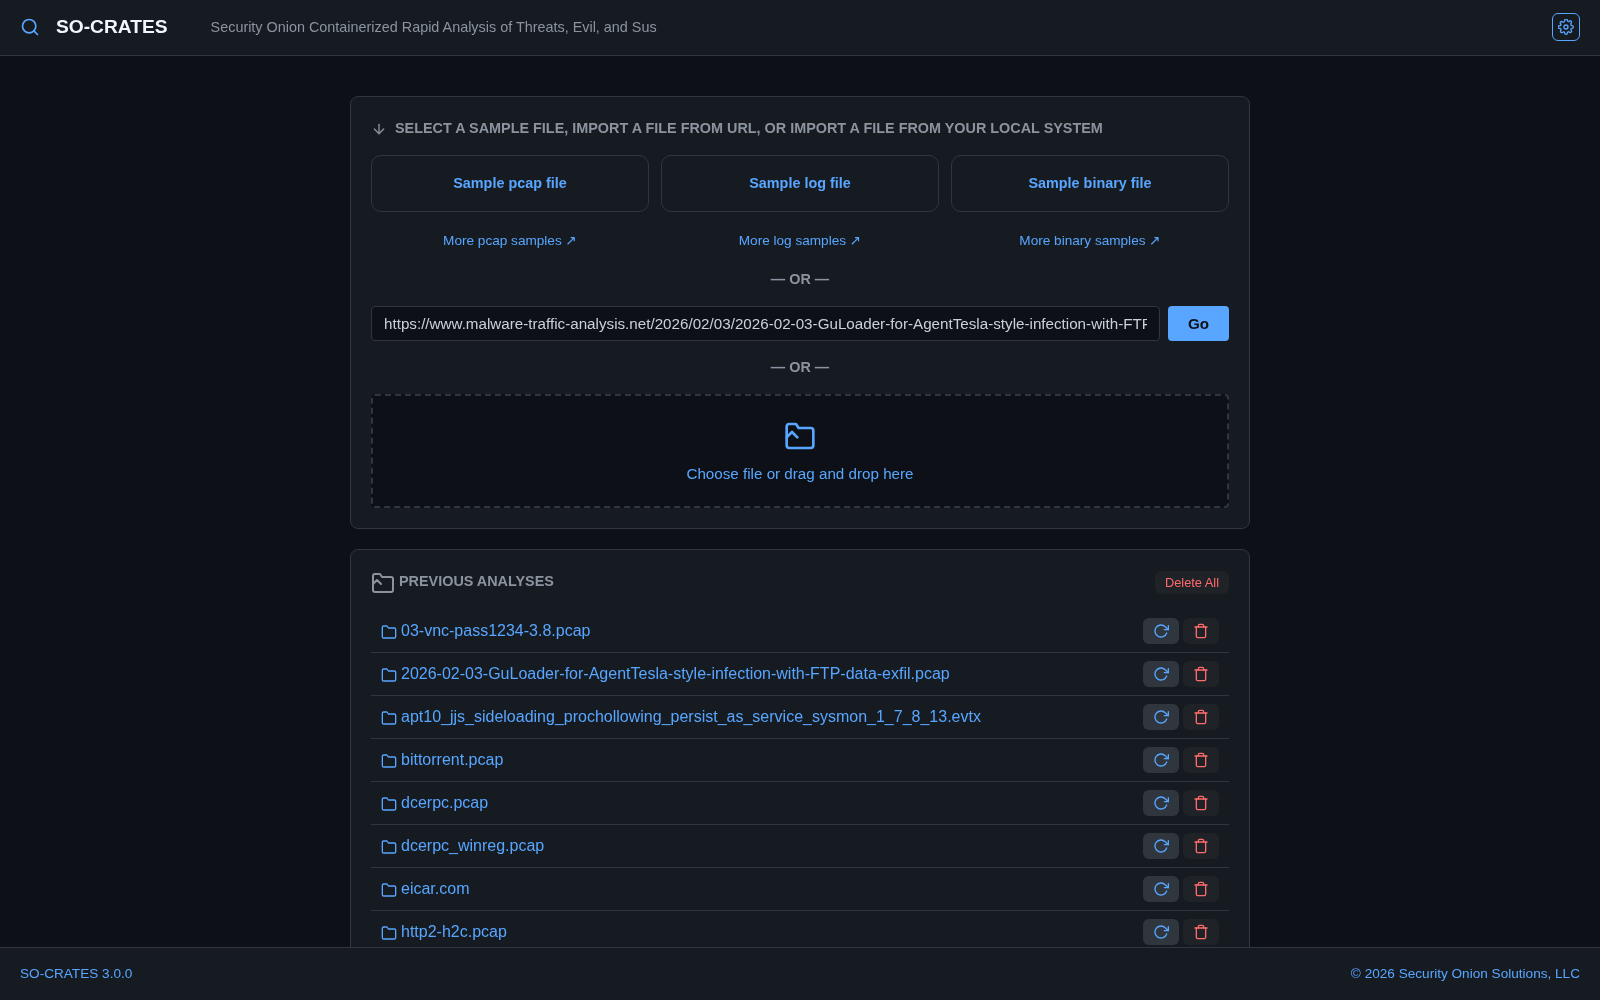
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
container-securitydigital-forensicseducation+8
5712 days ago
awesome-dfir-skills preview

awesome-dfir-skills

GitHubtsale/awesome-dfir-skills

A curated collection of DFIR skills and workflows for InfoSec practitioners.
curated-resourcesdigital-forensicseducation+7
3215 months ago
dissect.cobaltstrike preview

dissect.cobaltstrike

GitHubfox-it/dissect.cobaltstrike

Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
binary-analysiscommand-and-controldigital-forensics+4
19320 days ago
scripts preview

scripts

GitHubclausing/scripts

Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
digital-forensicsforensicsincident-response+5
868 days ago
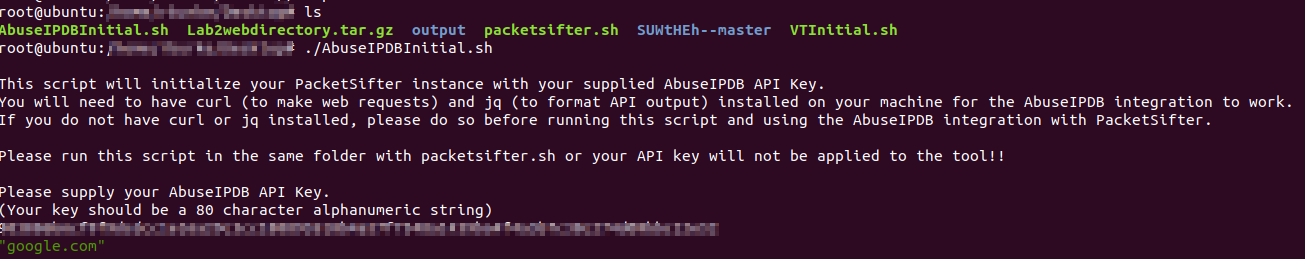
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
defensive-toolsdigital-forensicsforensics+5
935 years ago
wireshark-forensics-plugin preview

wireshark-forensics-plugin

GitHubrjbhide/wireshark-forensics-plugin

Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…

digital-forensicsforensicsnetwork-forensics+3
1024 years ago
honeypot-data preview

honeypot-data

GitHub0x4d31/honeypot-data

Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
incident-responseinformation-gatheringioc-management+4
449 days ago
CAPEsolo preview

CAPEsolo

GitHubcapesandbox/capesolo

Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
defensive-toolsdynamic-analysis-sandboxingforensics+7
611 month ago
HiddenNetworks-Python preview

HiddenNetworks-Python

GitHubtelefonica/hiddennetworks-python

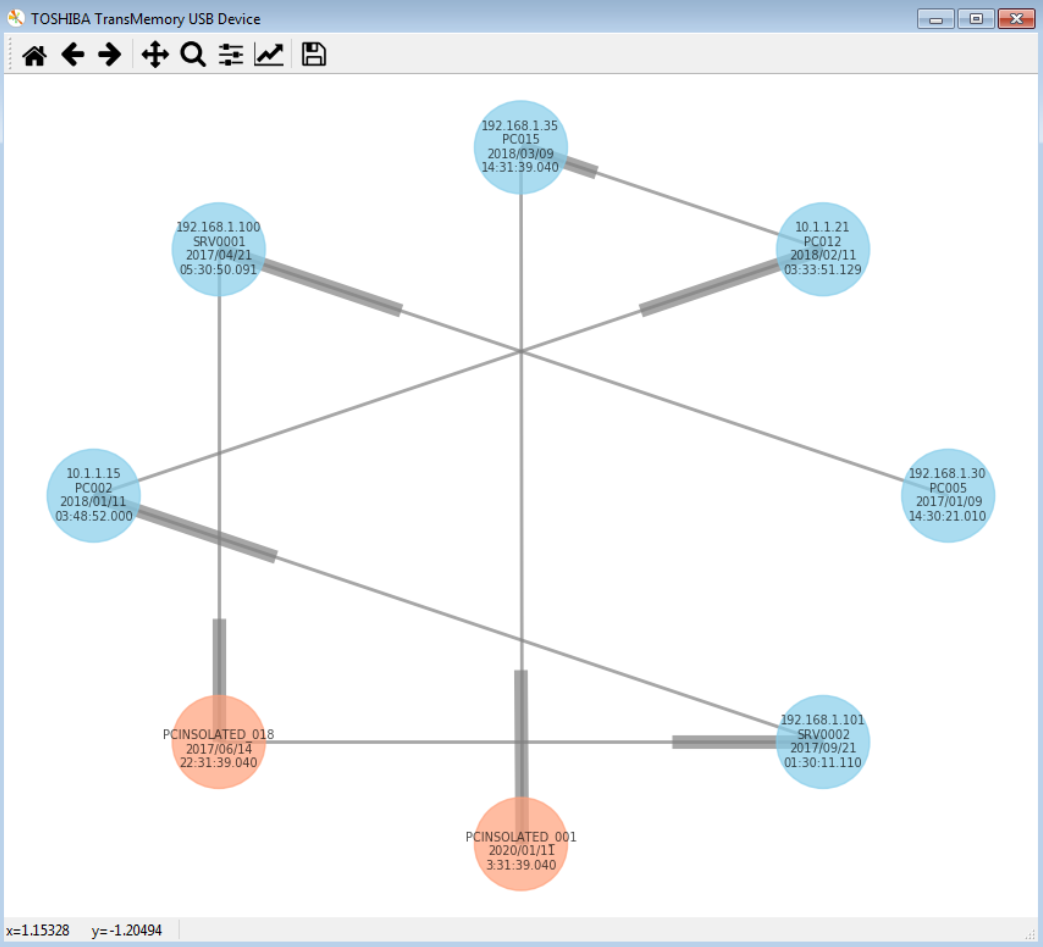
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…

digital-forensicsforensicsinformation-gathering+2
386 years ago
Previous1…345…9Next