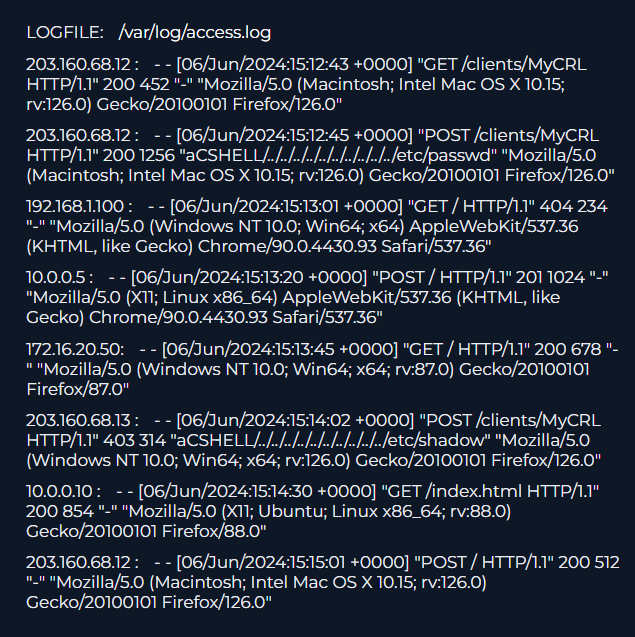
Incident-Analysis-Response-Check-Point-Security-Gateway-CVE-2024-24919-LFI-Exploitation

Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…

Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…

Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…

Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…

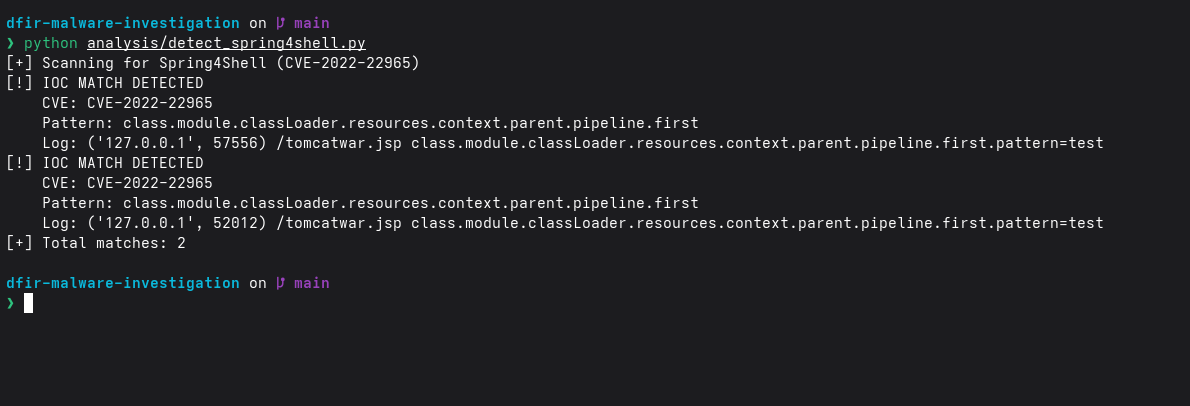
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.

Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management

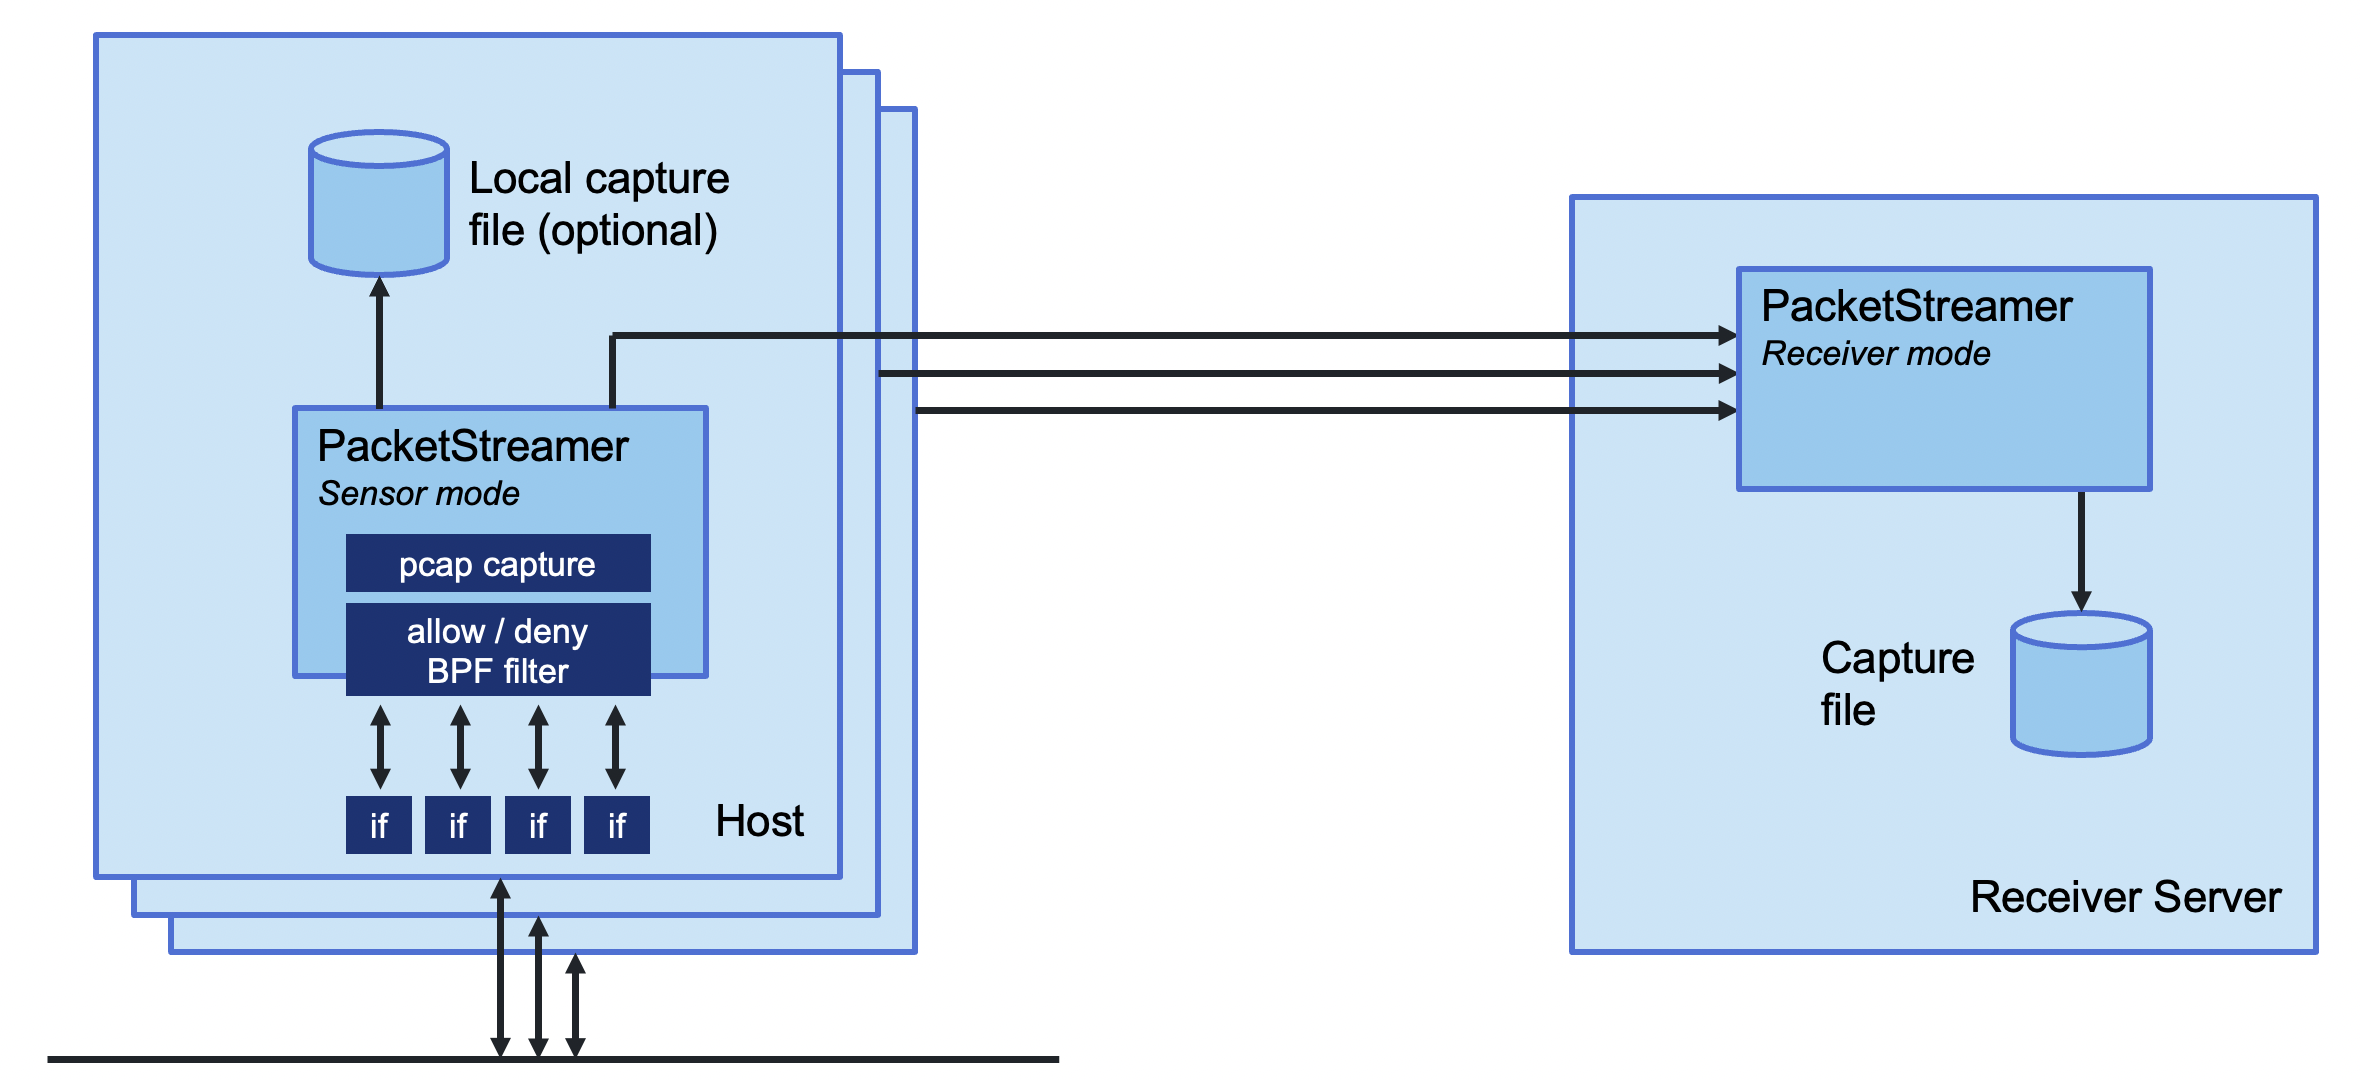
⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.


Malicious HTTP traffic explorer

Malcom - Malware Communications Analyzer

Collection of forensic tools

Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.

The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark

DFIR forensics companion server + capture extension

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

Parsing Ramnit's traffic