

termshark
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
network-forensicsnetwork-securitypacket-sniffing-analysis+1
gcla/termsharkA terminal UI for tshark, inspired by Wireshark
 simsong/tcpflow
TCP/IP packet demultiplexer. Download from:
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
 cyberhatcoil/acf
Android Connections Forensics
 orjanj/netscaler_threat_hunt_helper
NetScaler CTX697096 Threat Hunt Helper (IoC scanner) - CVE-2026-88771, CVE-2026-88772, CVE-2026-88779
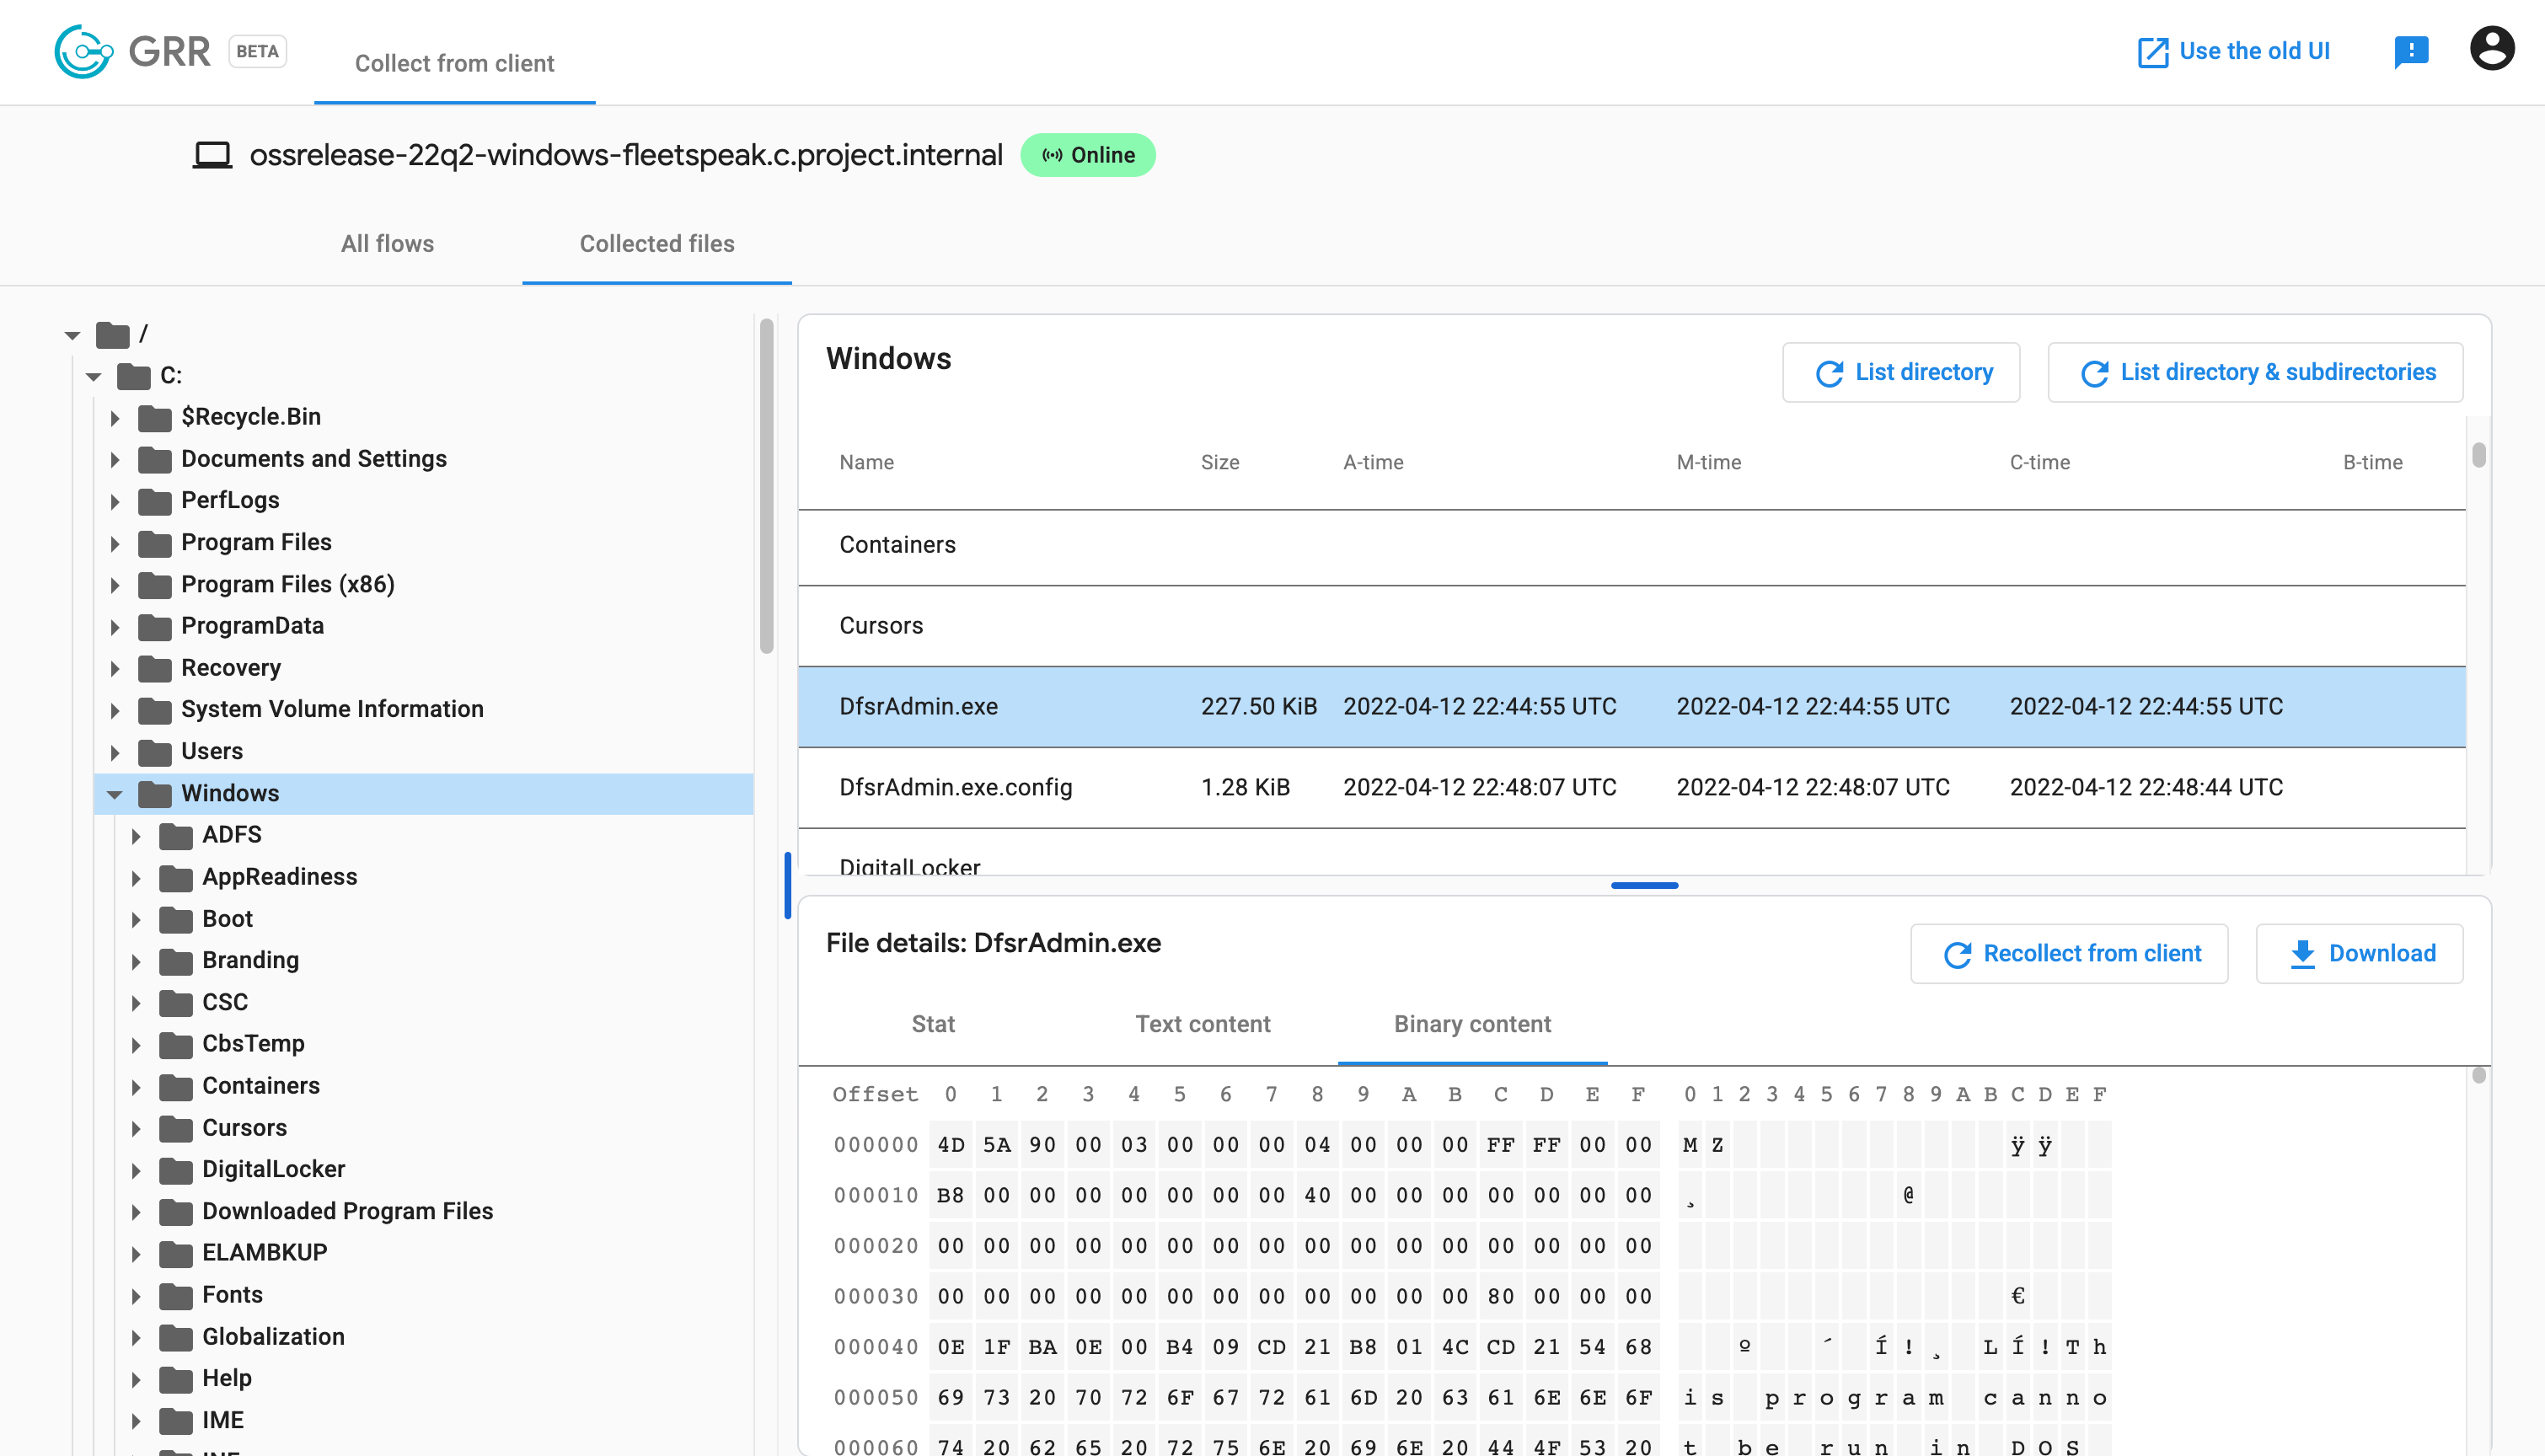 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
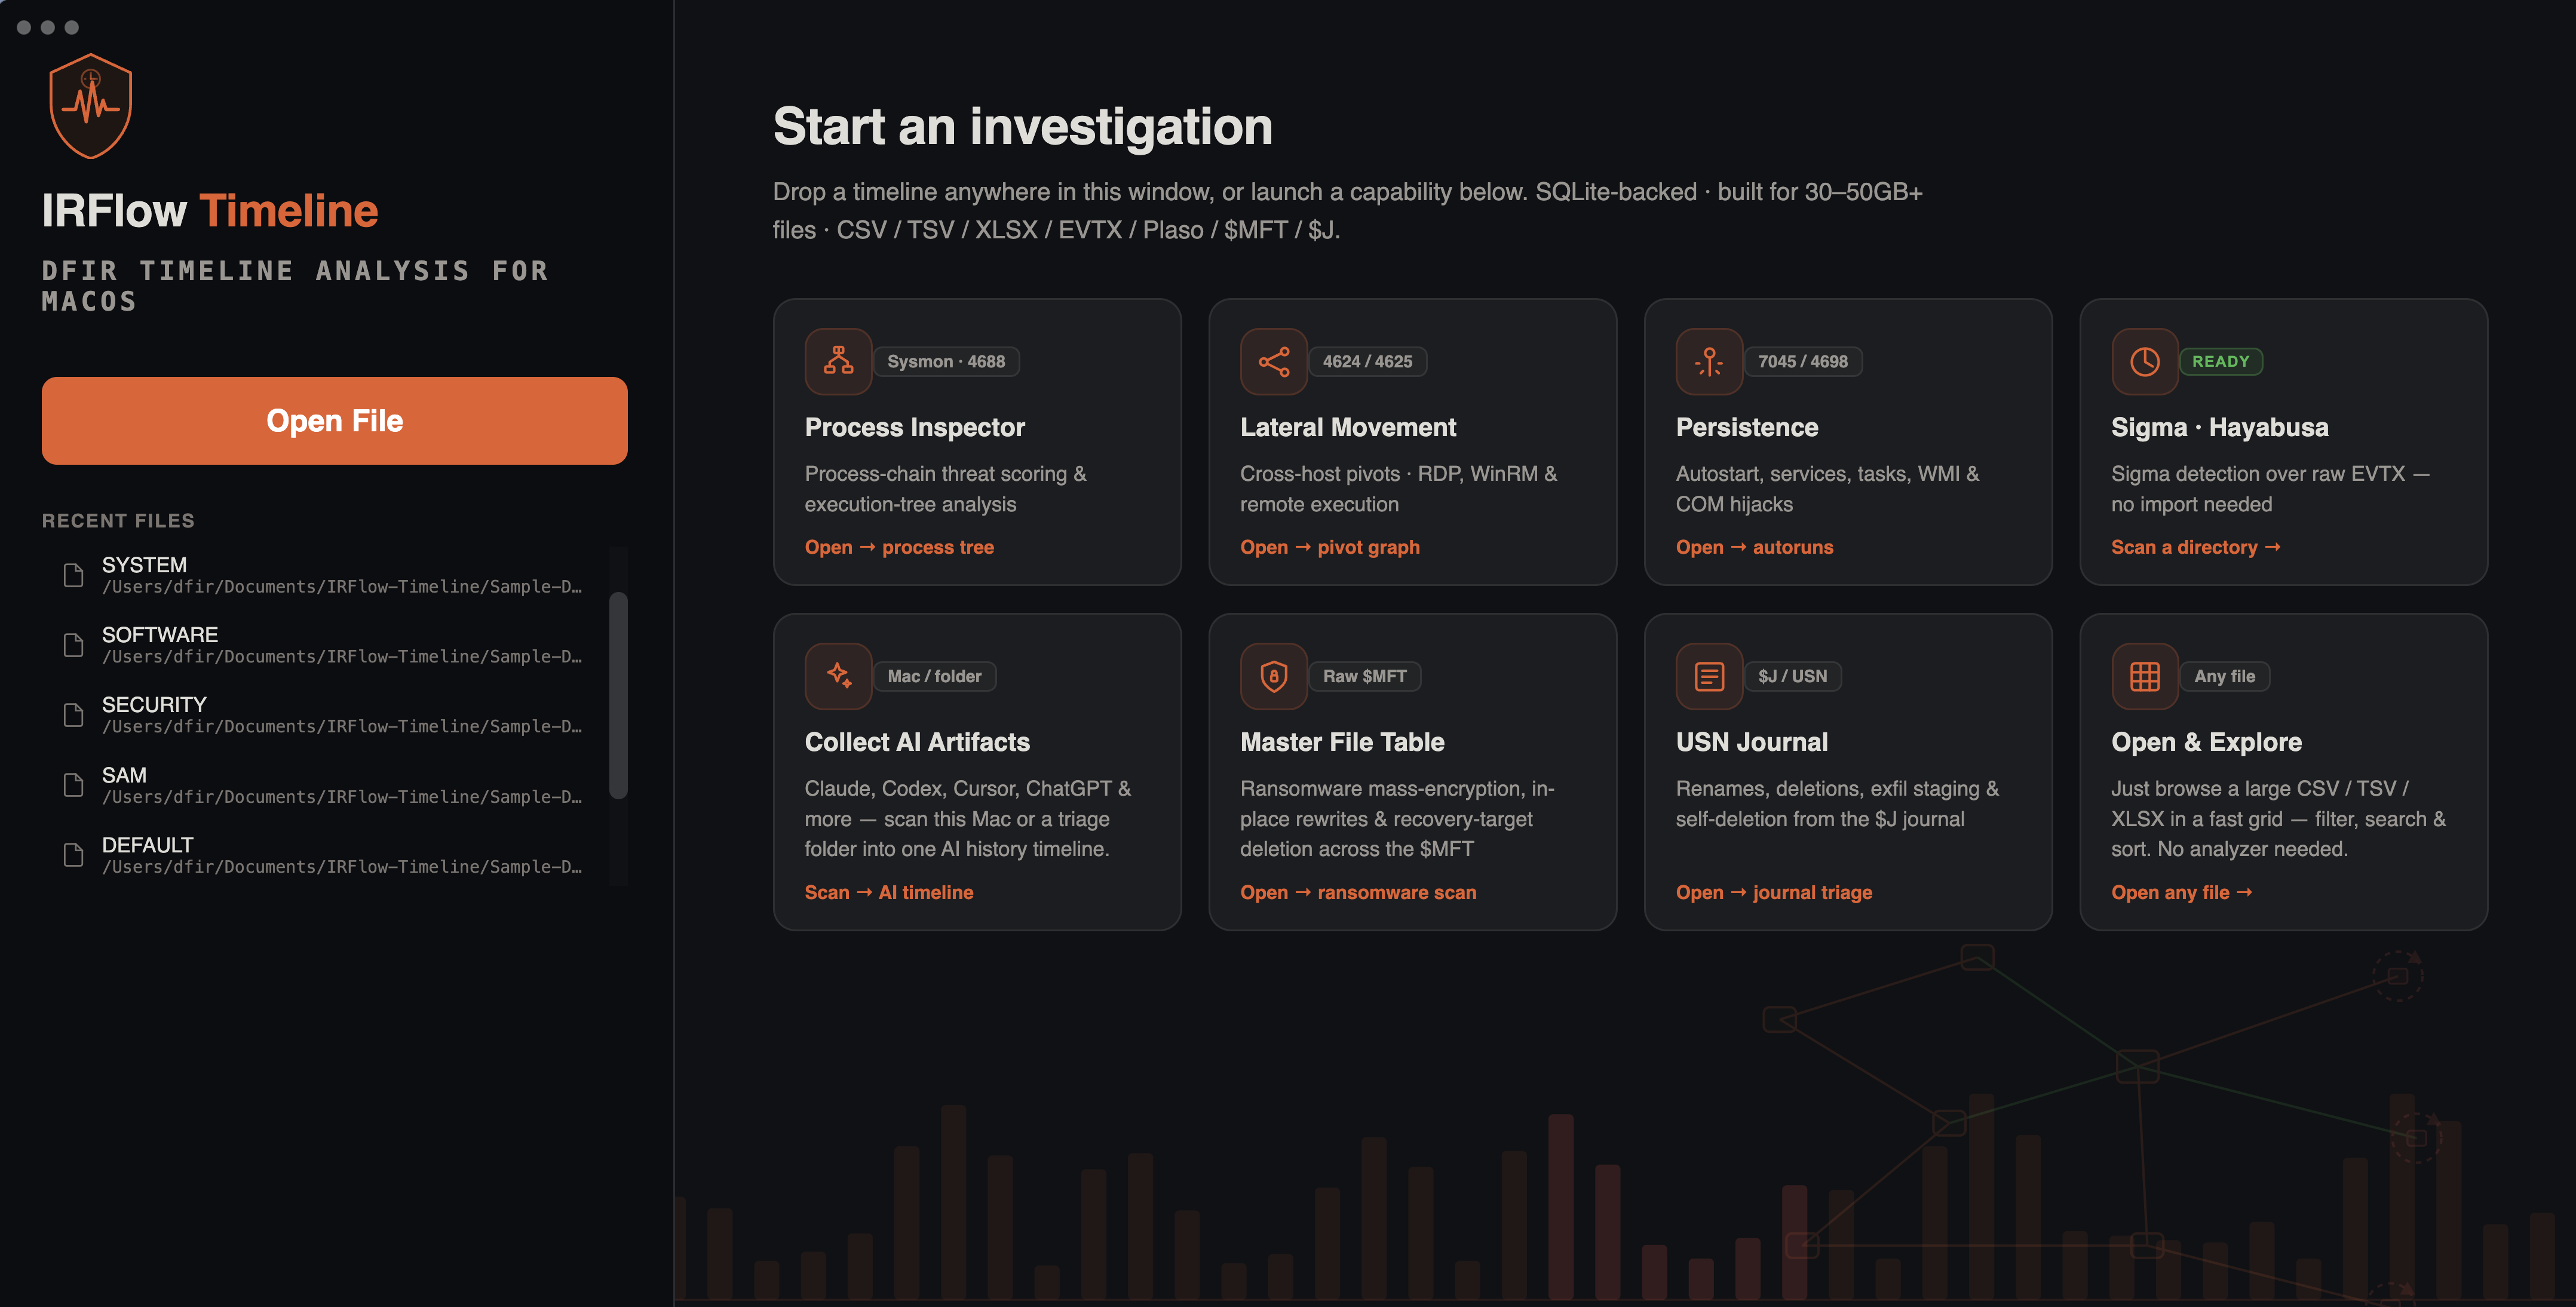 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…

 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
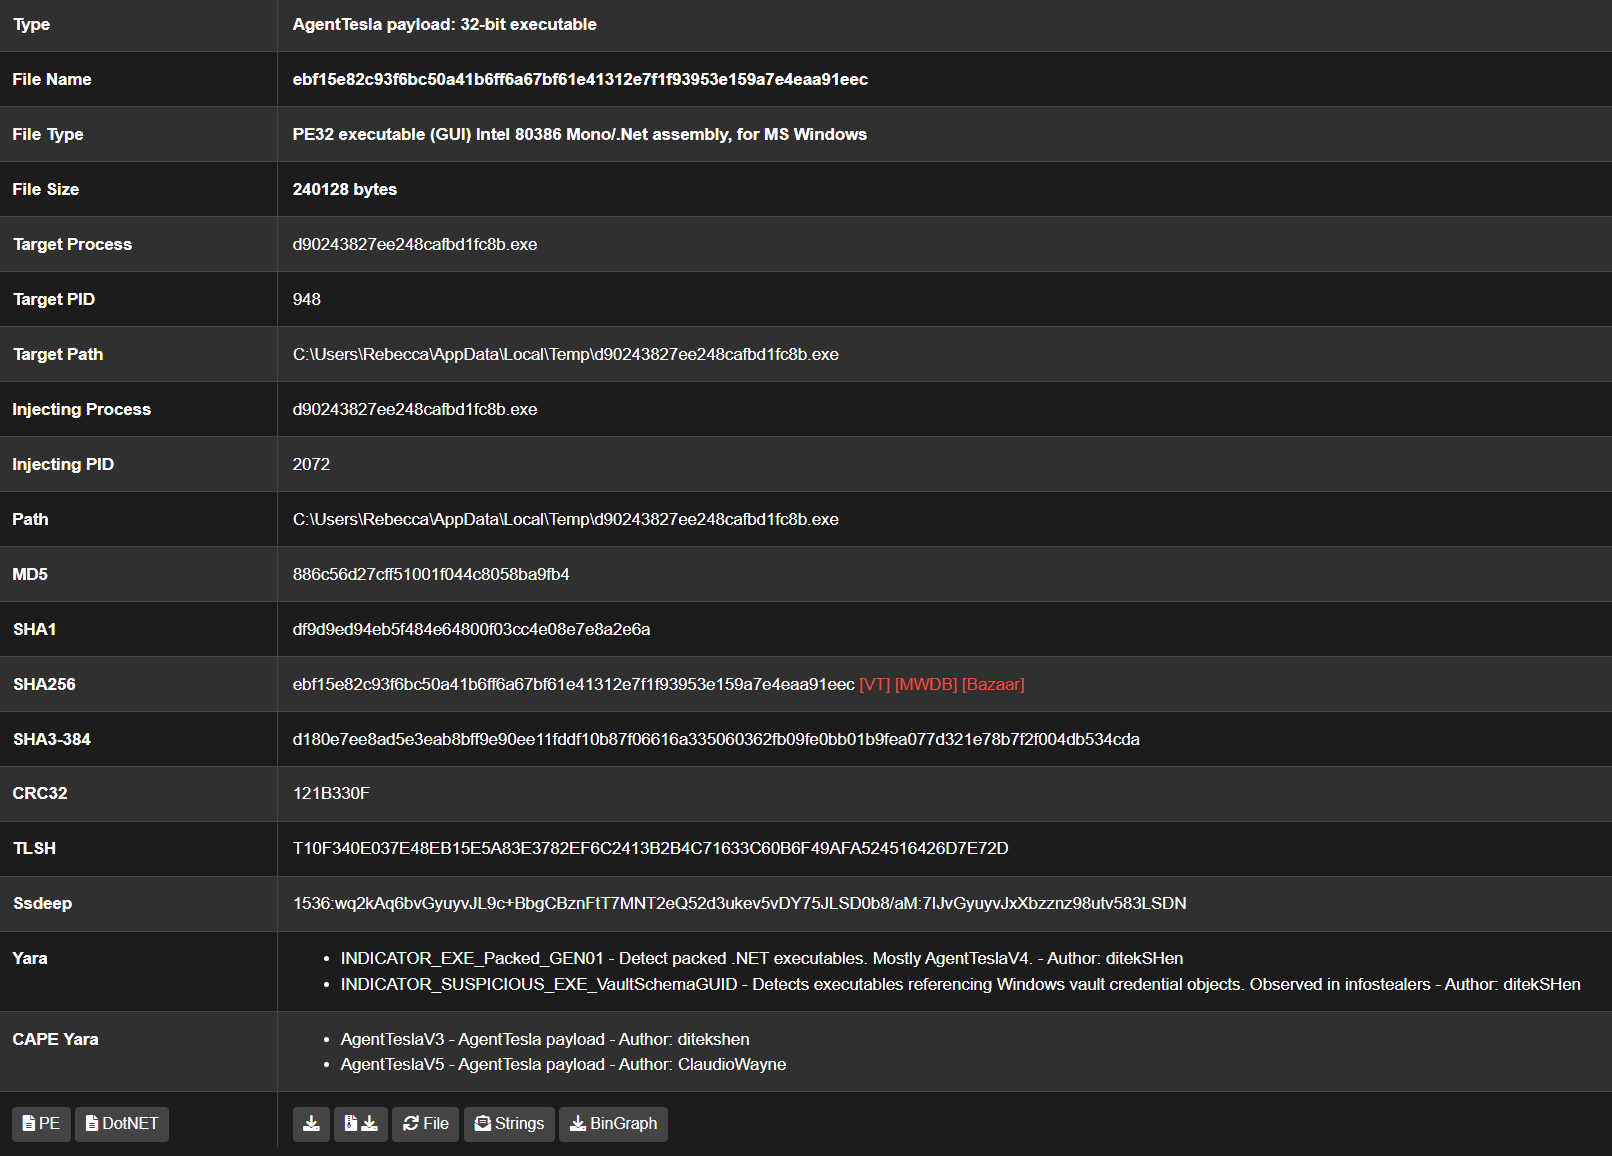 kevoreilly/capev2
Malware Configuration And Payload Extraction
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
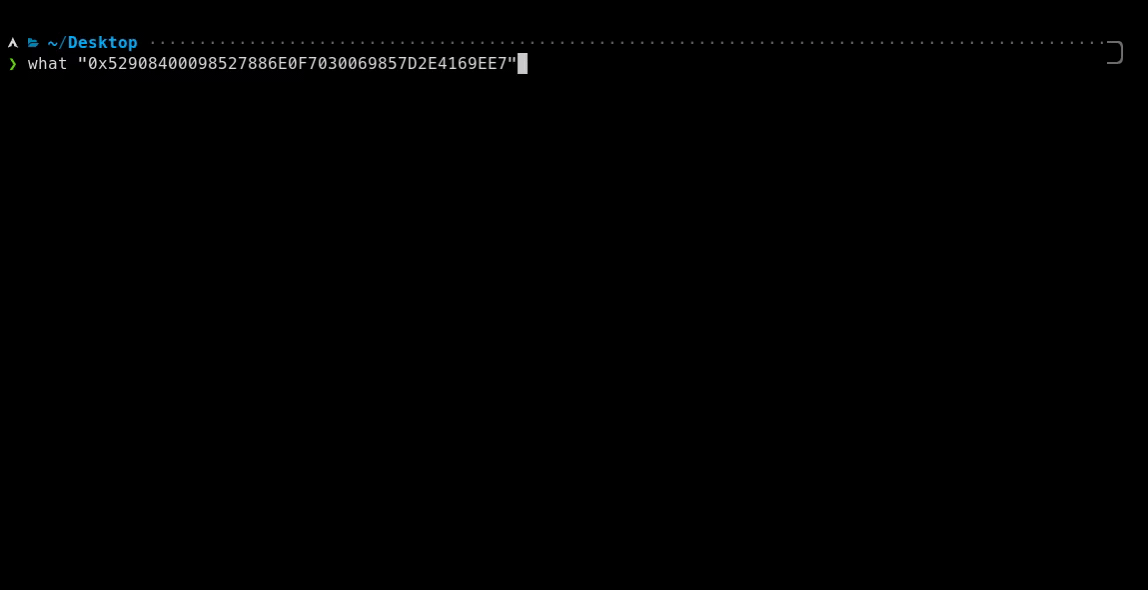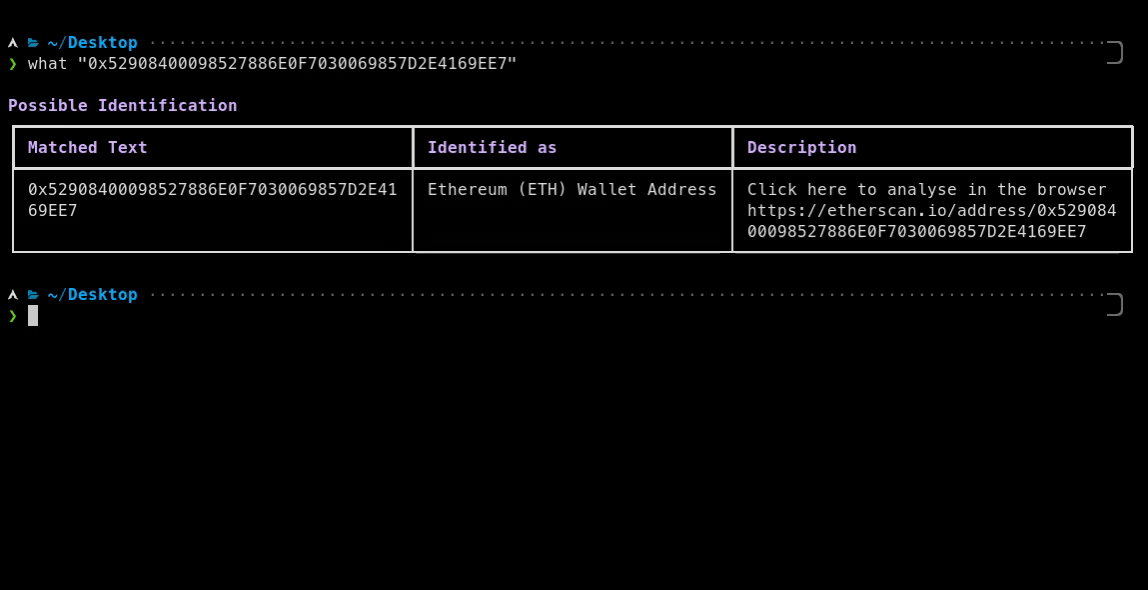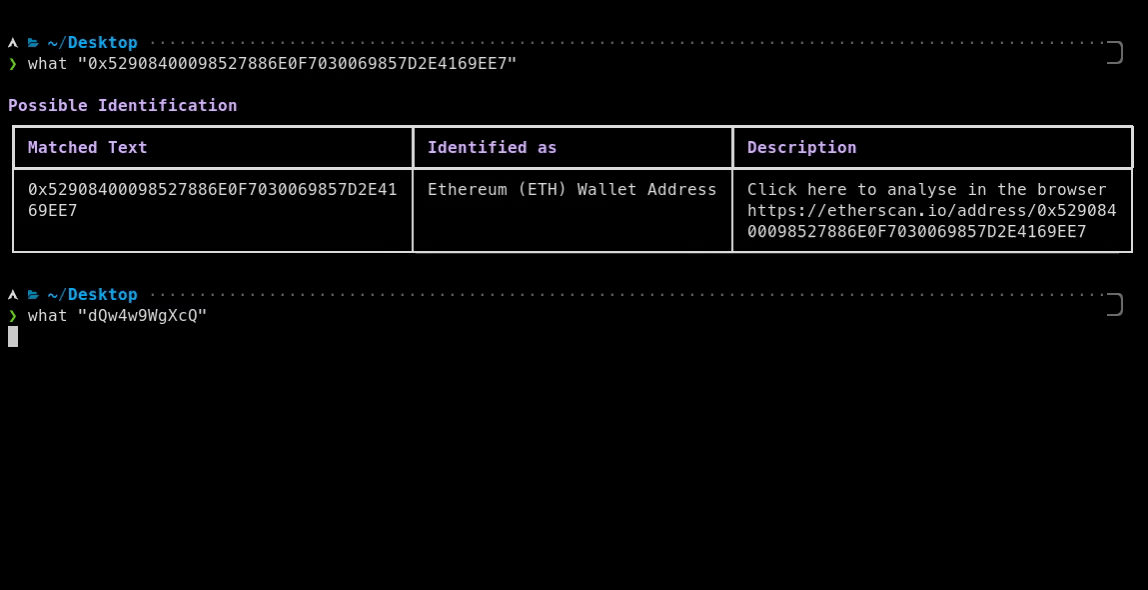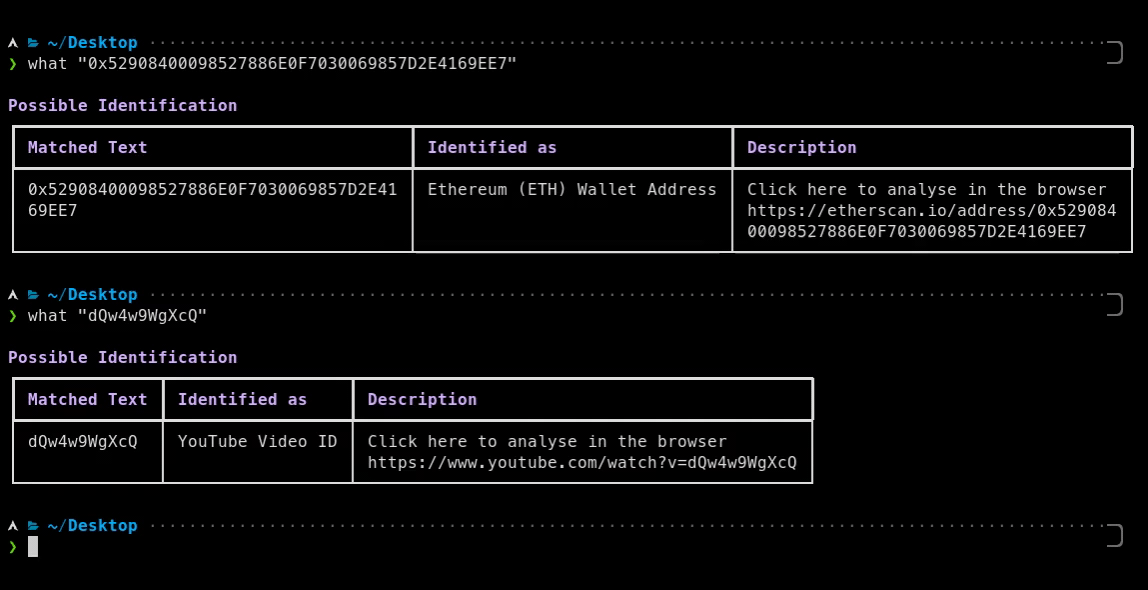 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
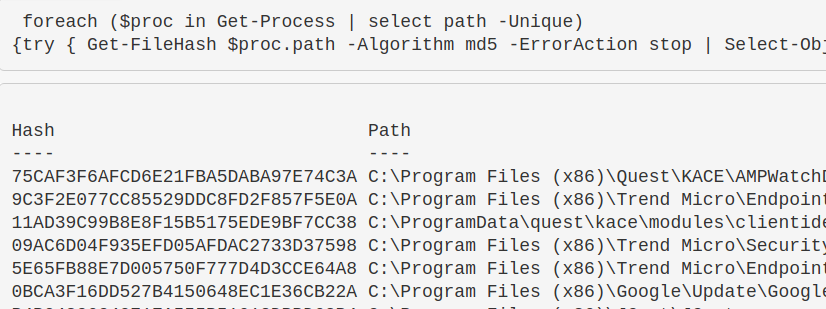 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…