Digital-Forensics-Guide

Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.

Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.

Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…

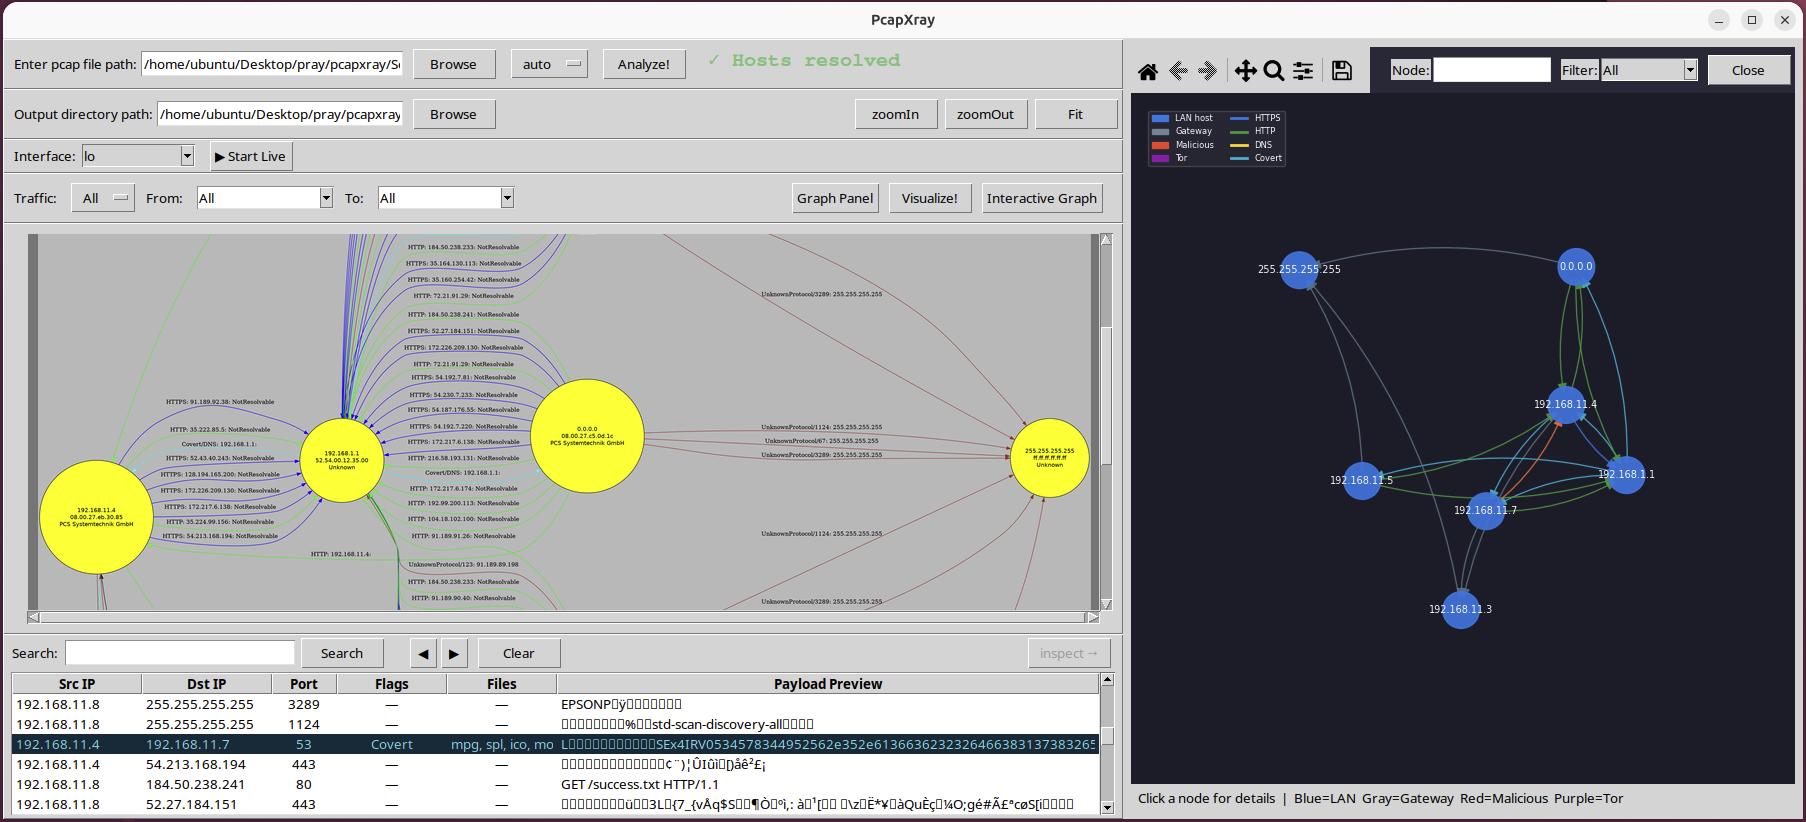
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…

A network sniffer that logs all DNS server replies for use in a passive DNS setup

FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…

The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…

NetworkAssessment: Network Compromise Assessment Tool

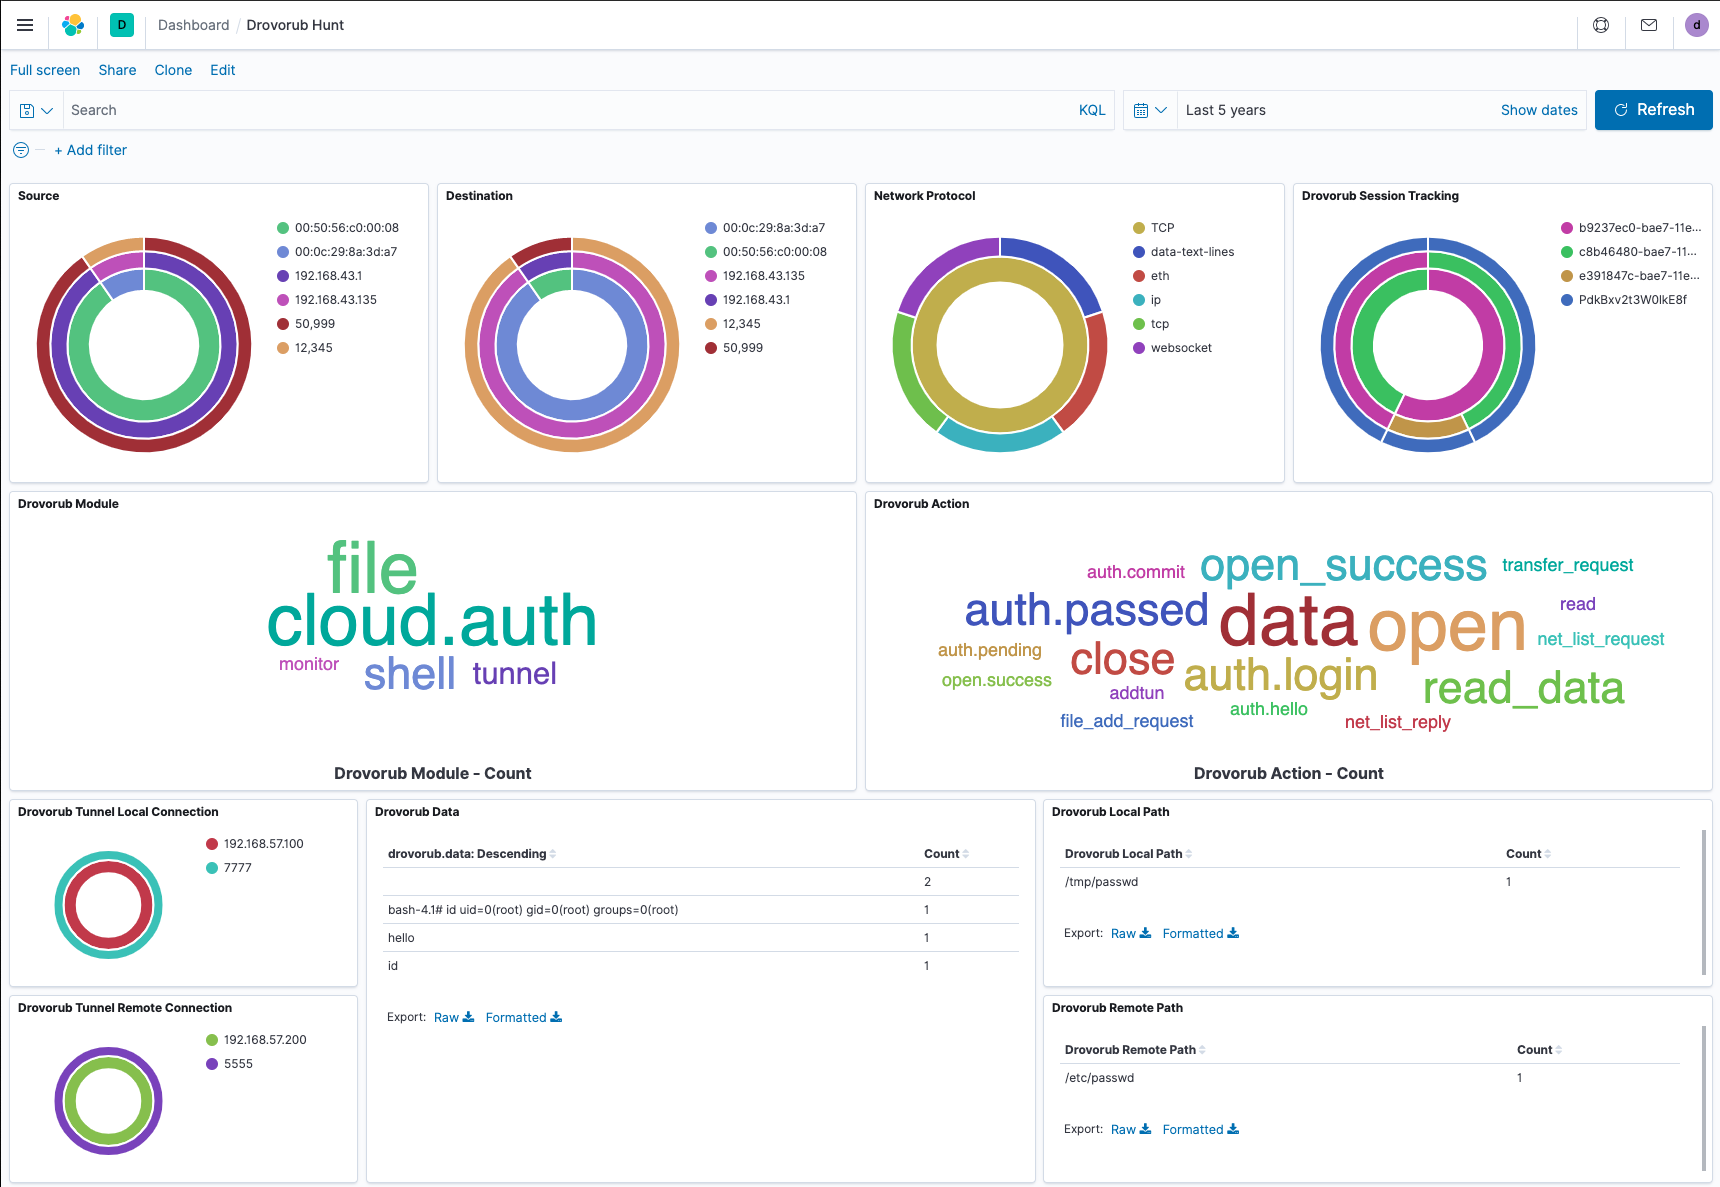
A tool to assist with network-based hunting for GRU's Drovorub malware c2

Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis

Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…

Web-based Traffic and Cybersecurity Network Traffic Monitoring

Free hands-on digital forensics labs for students and faculty


Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…

All-in-One malware analysis tool.

A terminal UI for tshark, inspired by Wireshark

Provides packet processing capabilities for Go